Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 2,629 advisories
Page 107 of 110
The Good, the Bad and the Ugly in Cybersecurity – Week 32 Moderate SentinelOne Threat Labs
2026-08-07 SentinelOne Threat Labs

The Good, the Bad and the Ugly in Cybersecurity – Week 32

The Good | Snowflake Hacker Pleads Guilty as Ransom Cartel Creator Draws 16 Years Connor Riley Moucka pleaded guilty in Seattle federal court this week to computer fraud, wire fraud, aggravated identity theft and conspiracy over the 2024 breaches of Snowflake customer accounts. The intrusions reached at least 165 organizations and exposed records tied to at …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
ChainDrop: Inside a Self-Propagating npm Worm Moderate Palo Alto Unit 42
2026-08-06 Palo Alto Unit 42

ChainDrop: Inside a Self-Propagating npm Worm

Analysis of ChainDrop, an npm supply chain worm extracting GitHub Actions runner secrets and using Ethereum smart contracts for C2 routing. The post ChainDrop: Inside a Self-Propagating npm Worm appeared first on Unit 42 .

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
When Agentic Glue Melts: Exploiting Cloudflare Code Mode and Workers Important Check Point Research
2026-08-06 Check Point Research

When Agentic Glue Melts: Exploiting Cloudflare Code Mode and Workers

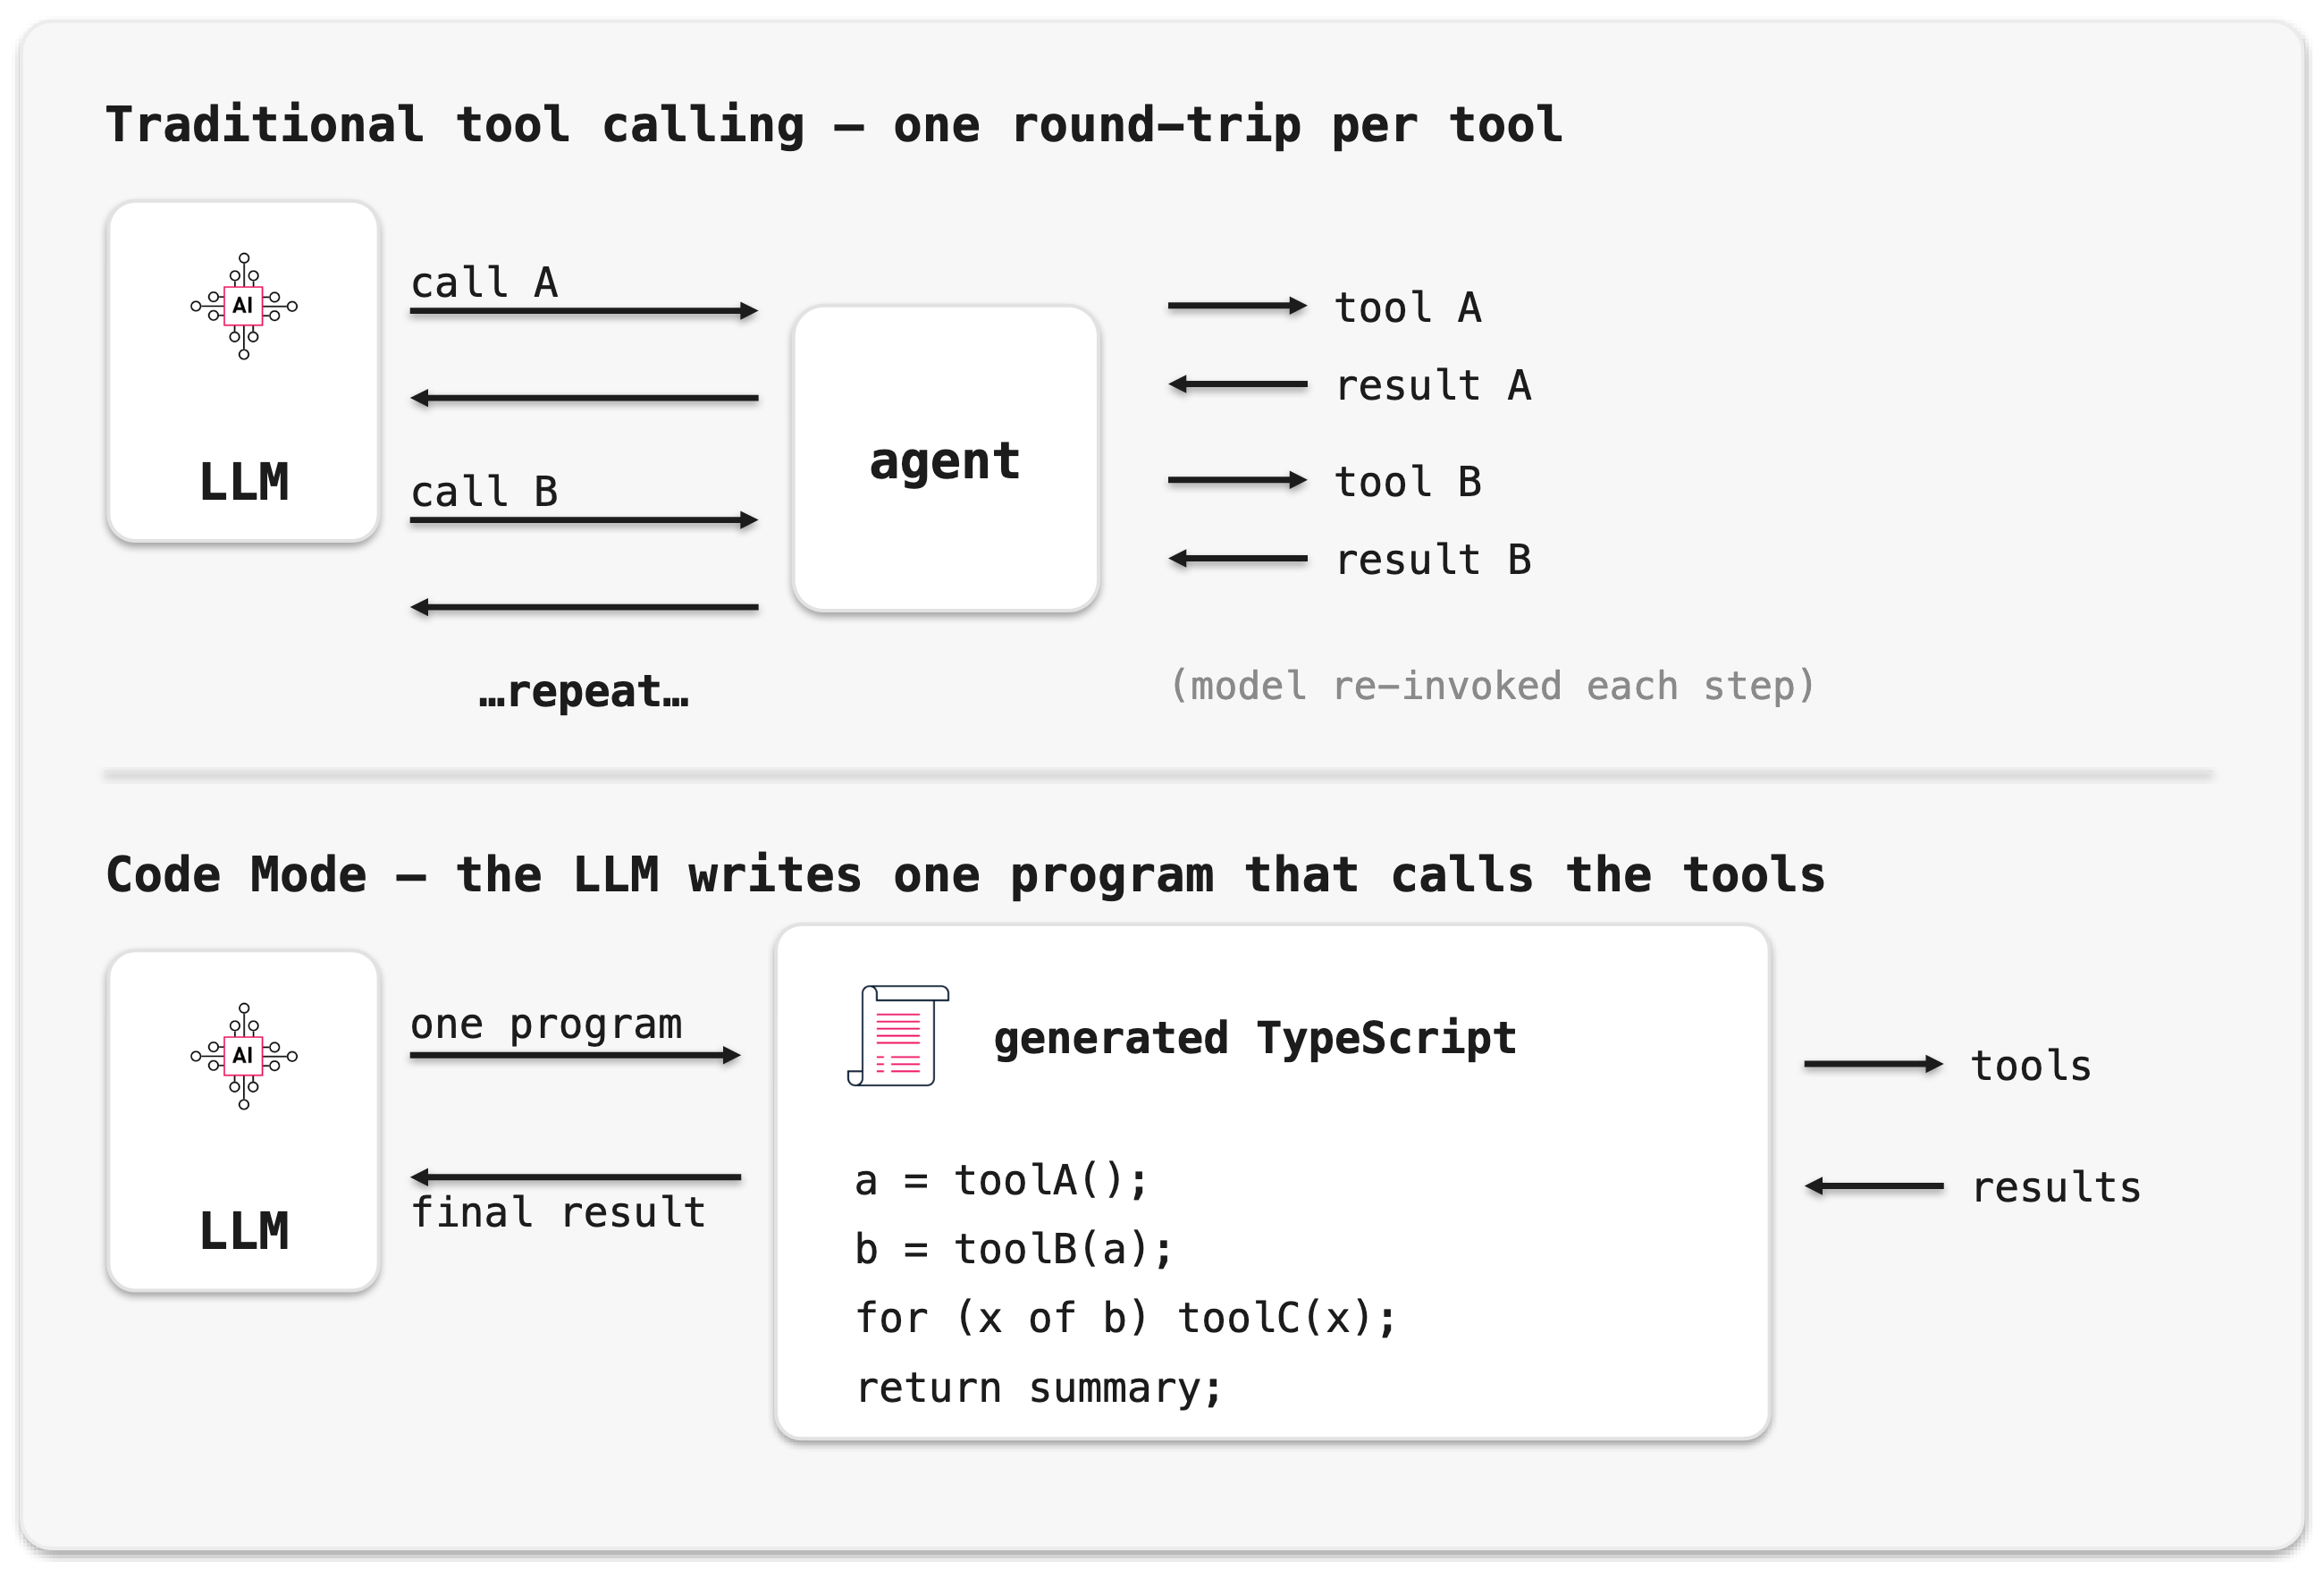
By Yarden Porat, Check Point Research Key Points Check Point Research analyzed Cloudflare Code Mode, a technique that changes how AI agents use MCP by turning tools into a TypeScript API the model can write code against. The research uncovered five vulnerabilities in workerd, the open-source runtime behind Code Mode and Cloudflare Workers. Two were rated Cri…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Canadian Man Pleads Guilty in Snowflake Extortions Moderate KrebsOnSecurity
2026-08-06 KrebsOnSecurity

Canadian Man Pleads Guilty in Snowflake Extortions

A 26-year-old Canadian man once described as one of the most consequential cybercrime threat actors of 2024 has pleaded guilty to computer fraud and conspiracy to hack and extort more than 165 organizations that used the cloud data storage provider Snowflake. Connor Riley Moucka, of Kitchener, Ontario, also admitted to stealing call and text history records of more than 100 million AT&T custo...

Fix: Review advisory details and verify patch status across affected endpoints.
How we took malware advisories beyond npm Important GitHub Security Blog
2026-08-06 GitHub Security Blog

How we took malware advisories beyond npm

A compromised package can steal credentials the moment you install it, and until recently, GitHub could only flag those in npm. Not anymore. This is the story of how the supply chain engineering team behind Dependabot expanded malware advisories to eight ecosystems by building on OpenSSF’s shared malicious packages data. Here’s where things stand: earlier th…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Apple’s bug bounty program is drowning in so much AI slop, it is in danger of missing serious exploits Important Graham Cluley Security
2026-08-06 Graham Cluley Security

Apple’s bug bounty program is drowning in so much AI slop, it is in danger of missing serious exploits

Apple has imposed strict new submission limits on its bug bounty portal after finding itself overwhelmed by low-quality, AI generated vulnerability reports - many of which were found to be describing security flaws that simply didn't exist. Read more in my article on the Hot for Security blog.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Token Jacking: Cybercriminals Could Be Stealing Your AI Resources Critical Palo Alto Unit 42
2026-08-06 Palo Alto Unit 42

Token Jacking: Cybercriminals Could Be Stealing Your AI Resources

Discover how attackers hijack AI tokens to fuel gray market transfer stations by stealing developer API keys. The post Token Jacking: Cybercriminals Could Be Stealing Your AI Resources appeared first on Unit 42 .

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Smashing Security podcast #479: How a fake police officer nearly stole Graham’s cryptocurrency Moderate Graham Cluley Security
2026-08-05 Graham Cluley Security

Smashing Security podcast #479: How a fake police officer nearly stole Graham’s cryptocurrency

Graham gets a phone call from the police. Well, someone who sounds convincingly like the police. There's just one small problem: what they really want is the 24-word seed key to Graham's cryptocurrency wallet. Meanwhile, if you've stayed in a hotel recently, the free Wi-Fi you connected to might have come with an unexpected extra: an all-you-can-eat buffet o…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

From Input to Impact: Secure AI Where It Runs Moderate SentinelOne Threat Labs
2026-08-04 SentinelOne Threat Labs

From Input to Impact: Secure AI Where It Runs

AI agents have made their way into virtually every layer of your environment. They run in the apps your employees adopt, on the endpoints where agents execute code, as users with access privileges those agents borrow, and in the cloud workloads that scale them. The platform that you trust to secure your endpoints is already already covering where AI operates…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
3rd August – Threat Intelligence Report Moderate CVE-2026-59726 Check Point Research
2026-08-03 Check Point Research

3rd August – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 27th July, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Minnesota IT Services has confirmed coordinated cyberattacks affecting more than 30 community water utilities across the state. The incidents briefly disrupted a treatment plant in Braham and affected industrial c…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The Good, the Bad and the Ugly in Cybersecurity – Week 31 Moderate SentinelOne Threat Labs
2026-07-31 SentinelOne Threat Labs

The Good, the Bad and the Ugly in Cybersecurity – Week 31

The Good | Authorities Disrupt “The Com”, Release Security Guidelines & Charge Telegram CEO Europol and law enforcement partners from nine countries have flagged over 4000 URLs for removal to disrupt the online ecosystem of The Com . Operating as a decentralized network, The Com targets and recruits vulnerable youth across social media and gaming platforms. …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Read This Before You Buy That TV Streaming Stick Moderate KrebsOnSecurity
2026-07-30 KrebsOnSecurity

Read This Before You Buy That TV Streaming Stick

Security experts have been sounding the alarm for years about the risks of using generic TV boxes that promise unlimited content streaming for a one-time fee, warning that they secretly rent the user's Internet connection out to strangers. But a groundbreaking new analysis finds these devices also routinely spoof themselves as mobile phones clicking ads on AI-generated websites as part of sprawlin...

Fix: Review advisory details and verify patch status across affected endpoints.
The July 2026 Apple Security Update Review Critical CVE-2026-43818 Trend Micro ZDI
2026-07-30 Trend Micro ZDI

The July 2026 Apple Security Update Review

Welcome to our monthly look at Apple security patches. This release shows that Apple is not immune to the bug apocalypse that is impacting other vendors. Last month, they released 37 unique CVEs compare to this month’s 210. Quite a jump. For July 2026, Apple released 210 unique CVEs across iOS/iPadOS 26.6, macOS Tahoe 26.6, macOS Sequoia 15.7.8, macOS Sonoma…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Tame Dependabot: Group your updates, slow the cadence, keep security fast Moderate GitHub Security Blog
2026-07-29 GitHub Security Blog

Tame Dependabot: Group your updates, slow the cadence, keep security fast

If you maintain an active repository, you know the feeling. You open your notifications on a Monday morning and there they are: five, 10, sometimes a dozen Dependabot pull requests, each bumping a single dependency by a single patch version. Individually, every one of them is helpful. Collectively, they’re noise. And noise is how important updates get ignore…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Disrupting supply chain attacks on npm and GitHub Actions Important GitHub Security Blog
2026-07-28 GitHub Security Blog

Disrupting supply chain attacks on npm and GitHub Actions

In the past year, there’s been a pattern of supply chain attacks that target weaknesses in package repositories and CI/CD systems to quickly spread malware to hundreds of open source projects. This malware seeks to exfiltrate credentials both to broadly spread the attack, as well as for later exploitation. We’ve written a few times about our plans for harden…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The Good, the Bad and the Ugly in Cybersecurity – Week 30 Moderate SentinelOne Threat Labs
2026-07-24 SentinelOne Threat Labs

The Good, the Bad and the Ugly in Cybersecurity – Week 30

The Good | Authorities Dismantle Kratos Phishing Network & Arrest Its Developer Kratos, a prominent phishing-as-a-service (PhaaS) platform, was dismantled from the inside out this week thanks to German and U.S. law enforcement agencies. During “Operation Olympus Blade”, authorities seized over 200 servers to render Kratos’ global network entirely inoperable …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Your Best Analyst Shouldn’t Be a Person. It Should Be a Capability Everyone Can Summon. Moderate SentinelOne Threat Labs
2026-07-24 SentinelOne Threat Labs

Your Best Analyst Shouldn’t Be a Person. It Should Be a Capability Everyone Can Summon.

For thirty years, we have measured security operations by the tools we buy. The next decade will measure us by the outcomes we deliver. That shift is already here, and it is being driven by something quietly radical: a repository of AI “skills” that turns the deep expertise of a principal analyst or engineer into a capability any team member can invoke on de…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The case for a cooldown: Why Dependabot now waits before issuing version updates Moderate GitHub Security Blog
2026-07-23 GitHub Security Blog

The case for a cooldown: Why Dependabot now waits before issuing version updates

In September 2025, an attacker phished the credentials of a single npm maintainer and published booby-trapped versions of chalk , debug , and around a dozen other packages that are together downloaded more than 2 billion times a week. The code rewrote cryptocurrency wallet addresses inside any browser app that loaded it. The poisoned versions were live for r…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Next chapter: Restructuring GitHub’s bug bounty program Moderate GitHub Security Blog
2026-07-22 GitHub Security Blog

Next chapter: Restructuring GitHub’s bug bounty program

The security research community makes GitHub safer for everyone. That’s the simple idea behind our bug bounty program. For more than a decade, researchers from around the world have helped us find and fix vulnerabilities before they could be exploited, and we’ve worked hard to be a program worth their time. Today, we’re sharing some meaningful changes to how…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
LG to Ban Residential Proxies from Smart TV Apps Moderate KrebsOnSecurity
2026-07-22 KrebsOnSecurity

LG to Ban Residential Proxies from Smart TV Apps

The home appliance giant LG Electronics USA said this week it plans to suspend any apps built for its smart TVs that turn one's television into an always-on residential proxy node. The move comes less than a month after researchers found that more than 42 percent of games and other apps available for download on LG's webOS store allow unknown third-parties to route their Internet traffic through a...

Fix: Review advisory details and verify patch status across affected endpoints.
Pwn2Own Ireland 2026 – New Targets and Categories Critical Trend Micro ZDI
2026-07-21 Trend Micro ZDI

Pwn2Own Ireland 2026 – New Targets and Categories

If you just want to read the rules, you can find them here . Pwn2Own Ireland returns for 2026, and it’s the third year for this event in the Emerald Isle. Despite the dreary Irish skies (and the threat of a random banshee ), we had an amazing event, even if we did end up in a jail at the end. With that in mind, we’re excited to return to Cork this fall for y…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft Patches a Record 570 Security Flaws Important KrebsOnSecurity
2026-07-14 KrebsOnSecurity

Microsoft Patches a Record 570 Security Flaws

Microsoft Corp. today released software updates to plug at least 570 security holes in its Windows operating systems and other software, almost triple the number of vulnerabilities the software giant fixed in its record-smashing Patch Tuesday release last month. Microsoft attributed the burgeoning patch counts to vulnerability discoveries aided by artificial intelligence.

Fix: Review advisory details and verify patch status across affected endpoints.
The July 2026 Security Update Review Critical CVE-2026-56155 Trend Micro ZDI
2026-07-14 Trend Micro ZDI

The July 2026 Security Update Review

Well folks. Here we are. The bug apocalypse has fully descended upon us. I’ll do my best to sort this out in some way meaningful, but this month’s release shows us the nay-sayers were right, and I’ve got to hand it to the nay-sayers here. Excellent call. Take an extended break from your regularly scheduled activities as we let’s take a look at the latest sec…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Lessons Learned from CISA’s Recent GitHub Leak Moderate KrebsOnSecurity
2026-07-13 KrebsOnSecurity

Lessons Learned from CISA’s Recent GitHub Leak

The Cybersecurity and Infrastructure Security Agency (CISA) has issued a postmortem on a data leak in which a contractor published dozens of internal CISA credentials -- including AWS Govcloud keys -- in a public GitHub repository for almost six months before being notified by KrebsOnSecurity. Experts say the gaps identified in the agency's initial response provide important lessons that all secur...

Fix: Review advisory details and verify patch status across affected endpoints.
Notification