
Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 2,629 advisories
Page 13 of 110
Drone program compliance: What a CTO says most agencies get wrong Moderate Help Net Security
2026-10-23 Help Net Security

Drone program compliance: What a CTO says most agencies get wrong

In this interview with Help Net Security, Nick Donarski, CTO at RotorLab, explains what councils, records clerks, insurers, and auditors expect from a public safety drone program, and where most programs fall short. He covers chain of custody for flight logs and video, how to publish drone activity without exposing sensitive operations, and common mistakes i…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
AI is taking cybersecurity jobs at junior and experienced levels alike Moderate Help Net Security
2026-10-23 Help Net Security

AI is taking cybersecurity jobs at junior and experienced levels alike

Organizations are cutting cybersecurity roles as they adopt AI, even while reporting shortages of the expertise needed to manage threats, according to Barracuda’s Cybersecurity Skills Gap Report. 56% have experienced professional workforce reductions linked to AI, evenly divided between entry-level and higher-level roles. The post AI is taking cybersecurity …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
New infosec products of the week: October 23, 2026 Moderate Help Net Security
2026-10-23 Help Net Security

New infosec products of the week: October 23, 2026

Here’s a look at the most interesting products from the past week, featuring releases from AppGate, IDENTOS, Sweet Security, and ThreatModeler. Sweet Security adds one-click protection for vulnerable cloud workloads Sweet Security has announced the release of Virtual Patching, a new capability that protects running cloud and AI applications from specific vul…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
State Bank of India Suffers a Customer PII Data Leak Moderate Dark Reading
2026-10-23 Dark Reading

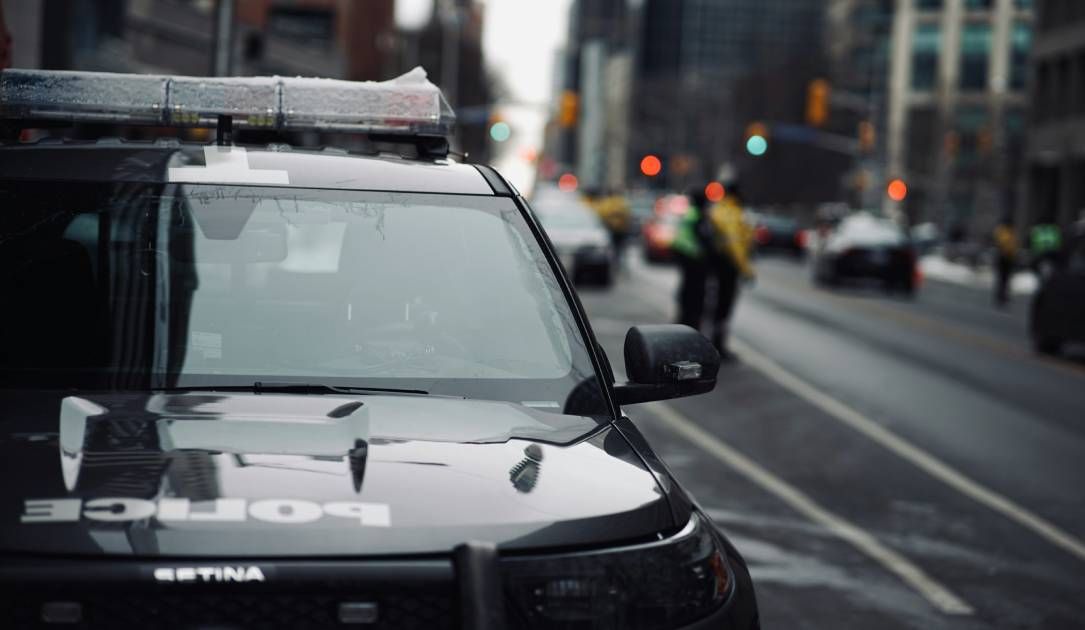
State Bank of India Suffers a Customer PII Data Leak

Relatively small data breaches in India can turn quite serious, thanks to a sophisticated underground market for trading PII.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Railway warns devs to rotate secrets after potential breach Critical BleepingComputer
2026-10-22 BleepingComputer

Railway warns devs to rotate secrets after potential breach

Cloud platform Railway published an urgent warning to users after detecting suspicious activity on its systems that store customer environment variables earlier this week. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Toronto crime tips org freezes operations after details of data breach come to light Critical The Record by Recorded Future
2026-10-22 The Record by Recorded Future

Toronto crime tips org freezes operations after details of data breach come to light

Late Wednesday night the Toronto chapter of Crime Stoppers broke ranks with the national association, revealing a timeline showing what it knew and when along with an announcement that it will pause operations.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft Links ConnectWise Breach to China-Linked Group Using AI Pentesting Tool ARTEX Critical SecurityAffairs
2026-10-22 SecurityAffairs

Microsoft Links ConnectWise Breach to China-Linked Group Using AI Pentesting Tool ARTEX

China-linked Storm-0940 used AI tool ARTEX to target 2,250 Microsoft 365 tenants, exploiting stolen ConnectWise credentials at machine speed. Microsoft published a detailed technical report naming Storm-0940, a China state-aligned group, as the actor behind the ConnectWise Cloud Backup supply chain compromise. The group used ARTEX, an open-source AI-driven p…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
What We Missed: Feds Lasso Texas Laptop Farms Moderate Dark Reading
2026-10-22 Dark Reading

What We Missed: Feds Lasso Texas Laptop Farms

In this video, Dark Reading editors discuss some of the news they didn't get a chance to cover, from busting up North Korea's stateside infrastructure in "Operation Lonestar Justice" to Staples' gift card bonanza.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Capcom confirms data breach affecting 11.7 million accounts Critical BleepingComputer
2026-10-22 BleepingComputer

Capcom confirms data breach affecting 11.7 million accounts

Japanese gaming giant Capcom has confirmed that hackers breached its membership service, CAPCOM ID, exposing more than 11.7 million customer email addresses and associated information. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

LiteLLM release pipeline hacked to distribute info-stealer malware Important BleepingComputer
2026-10-22 BleepingComputer

LiteLLM release pipeline hacked to distribute info-stealer malware

Hackers compromised the LiteLLM project's PyPI package and published malicious Docker images with a payload that steals credentials, secrets, and environment variables. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The AI Agent Nobody Owns: Watch Expert Webinar On Your Newest Insider Threat Moderate The Hacker News
2026-10-23 The Hacker News

The AI Agent Nobody Owns: Watch Expert Webinar On Your Newest Insider Threat

Right now, there is probably an AI agent running on a laptop somewhere in your network. It stores API keys and database passwords, can access your internal systems, and works without anyone watching. Nobody reviewed its access. Nobody owns it. If an employee had that much reach with that little oversight, you would call it an insider risk. So why do we still…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Arista Warns of Critical VeloCloud SQL Injection Zero-Day Exploited in Attacks Critical The Hacker News
2026-10-23 The Hacker News

Arista Warns of Critical VeloCloud SQL Injection Zero-Day Exploited in Attacks

Attackers are exploiting a zero-day SQL injection flaw in Arista's VeloCloud Orchestrator (VCO), the central management system for VeloCloud SD-WAN networks, the company said in an advisory on October 22. The flaw lets anyone who can log in to the orchestrator, even with a read-only customer account, gain operator privileges, the top level of control over it…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Indian tech company eMudhra announces withdrawal from certificate business after security incident Moderate The Record by Recorded Future
2026-10-22 The Record by Recorded Future

Indian tech company eMudhra announces withdrawal from certificate business after security incident

The issue was publicized by cybersecurity researcher Scott Helme, who published a blog saying that instead of a random 384-bit number, one of the company's private keys was just the number four.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Signal Vulnerability Could Keep Calls Alive After Users Hang Up Important CVE-2026-113380 SecurityAffairs
2026-10-22 SecurityAffairs

Signal Vulnerability Could Keep Calls Alive After Users Hang Up

A critical Signal flaw could keep calls active after hang-up, exposing microphone or camera. Update to a fixed version immediately. A critical vulnerability, tracked as CVE-2026-113380 (CVSS score 9.3 of 10), in Signal ’s calling library could allow a malicious caller to interfere with call termination, potentially leaving the victim’s microphone and camera …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
eMudhra to Exit Global SSL/TLS Business After 8 Intermediate CA Keys Found Easily Guessable Moderate The Hacker News
2026-10-22 The Hacker News

eMudhra to Exit Global SSL/TLS Business After 8 Intermediate CA Keys Found Easily Guessable

eMudhra, an Indian certificate authority (CA), will withdraw from its global SSL/TLS certificate business, its board decided on Thursday. The decision came five days after a researcher reported recovering the private keys of eight of its intermediate CA certificates. eMudhra said it will replace affected customers' certificates with free ones from partners, …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
I had plans for that second Critical Cisco Talos Intelligence
2026-10-22 Cisco Talos Intelligence

I had plans for that second

Welcome to this week’s edition of the Threat Source newsletter. Here for the latest on the PHP vulnerabilities? Head on down to ‘The One Big Thing’. Talos has published a blog to explain what we know so far, and details the Snort coverage available, including rules in the Community Ruleset. But if you want a bit of levity, here’s what I wrote before everythi…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
ThreatsDay: AI Secrets Leak, PingCAP Source Theft, Signal Hang-Up Flaw, Laravel Auth Bypass + 21 More Critical The Hacker News
2026-10-22 The Hacker News

ThreatsDay: AI Secrets Leak, PingCAP Source Theft, Signal Hang-Up Flaw, Laravel Auth Bypass + 21 More

This week has already been rough for cybersecurity. Critical PHP and GitLab RCE flaws, serious Linux security bugs, compromised eMudhra certificates, a Node.js RCE flaw, a hacked LiteLLM release, and hundreds of hijacked Tor relays. That's a lot to deal with in just a few days. And the week isn't even over yet. But those big headlines are only half the story…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

How bug bounty sharpens one researcher’s security skills Moderate GitHub Security Blog
2026-10-22 GitHub Security Blog

How bug bounty sharpens one researcher’s security skills

As Cybersecurity Awareness Month continues, the GitHub Bug Bounty team is excited to spotlight another top-performing security researcher from the GitHub Security Bug Bounty Program: @r31n ! As home to the world’s developers, GitHub is dedicated to the security and reliability of the code behind millions of projects, and our Bug Bounty Program remains a corn…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
EMudhra Intermediate CA Certificates Compromised Moderate Palo Alto Unit 42
2026-10-22 Palo Alto Unit 42

EMudhra Intermediate CA Certificates Compromised

Eight compromised eMudhra intermediate CA private keys risk unauthorized TLS signing and MitM interception. Read our analysis and containment guide. The post EMudhra Intermediate CA Certificates Compromised appeared first on Unit 42 .

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Two CVSS 9.0 Linux KSMBD RCE Flaws Disclosed on Public Mailing Lists Before Kernel Fixes Critical The Hacker News
2026-10-22 The Hacker News

Two CVSS 9.0 Linux KSMBD RCE Flaws Disclosed on Public Mailing Lists Before Kernel Fixes

Linux servers running KSMBD, the kernel's built-in SMB server, are exposed to two publicly reported remote code execution flaws rated 9.0 by Trend Micro's Zero Day Initiative, with no fix yet in the mainline kernel. One of them, ZDI-CAN-33774, can be triggered before any network authentication. The other, ZDI-CAN-33549, requires the SMB Direct transport and …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification
