Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 2,629 advisories
Page 18 of 110
Google Chrome Adds ClickFix Warnings to Stop Users From Running Malicious Commands Moderate The Hacker News
2026-10-21 The Hacker News

Google Chrome Adds ClickFix Warnings to Stop Users From Running Malicious Commands

Google on Tuesday said it's rolling out improved safeguards in its Chrome browser to secure users against ClickFix attacks when Enhanced Protection is enabled. ClickFix is a popular social engineering technique in which bad actors trick users into copying and pasting malicious code directly into their computer's operating system, thereby bypassing convention…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Decades-Old Windows Utility Powers Modern ClickFix Attack Important Dark Reading
2026-10-21 Dark Reading

Decades-Old Windows Utility Powers Modern ClickFix Attack

The attack uses malicious Google search results related to Amazon and leverages the "finger" utility to launch a CAPTCHA that installs malware, including the Lumma stealer.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The Science of Exploitability: Decoding BlueHammer Important CVE-2026-33825 Qualys Security Blog
2026-10-21 Qualys Security Blog

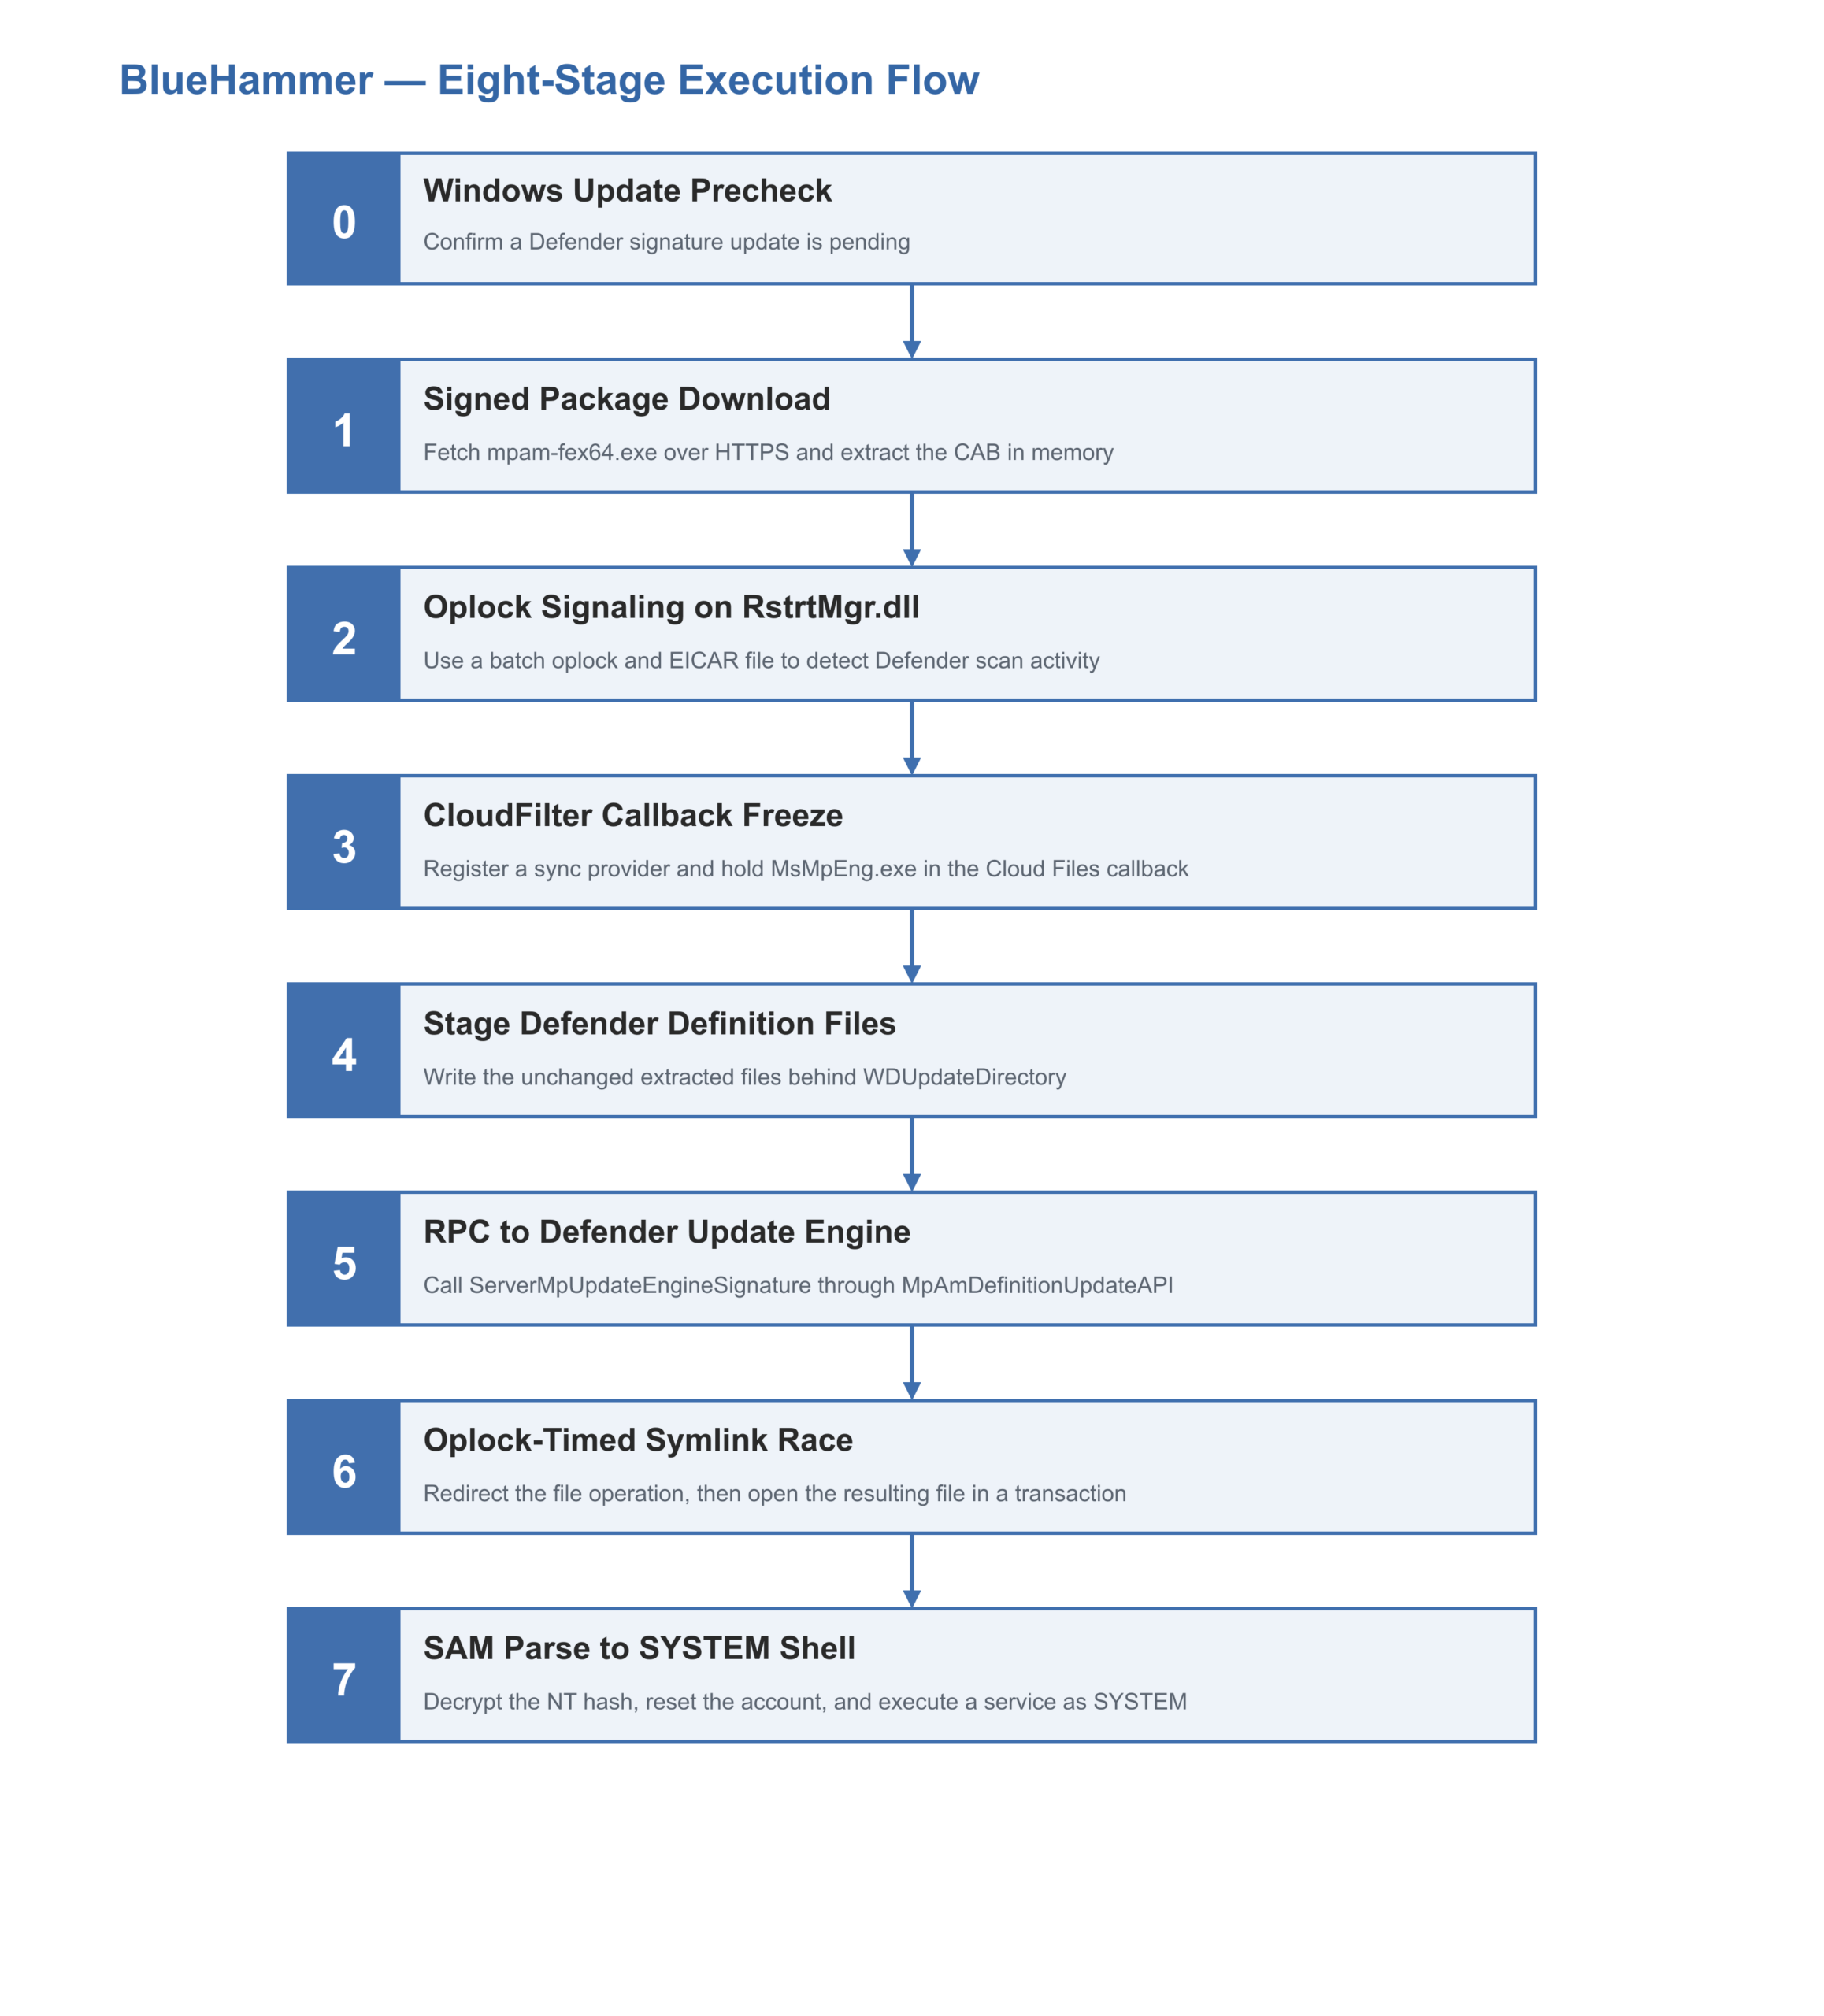
The Science of Exploitability: Decoding BlueHammer

Executive Summary BlueHammer (CVE-2026-33825) is an eight-stage local privilege-escalation chain targeting the Windows Defender Antimalware Platform before 4.18.26030.3011. It does not grant initial access; an attacker needs standard-user code execution first. Still, in the lab, it reached NT AUTHORITY\SYSTEM, recovered domain-admin credentials from LSASS, a…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Fake Amazon Music x YouTube deal lures creators into a Google login trap Moderate Malwarebytes Labs
2026-10-21 Malwarebytes Labs

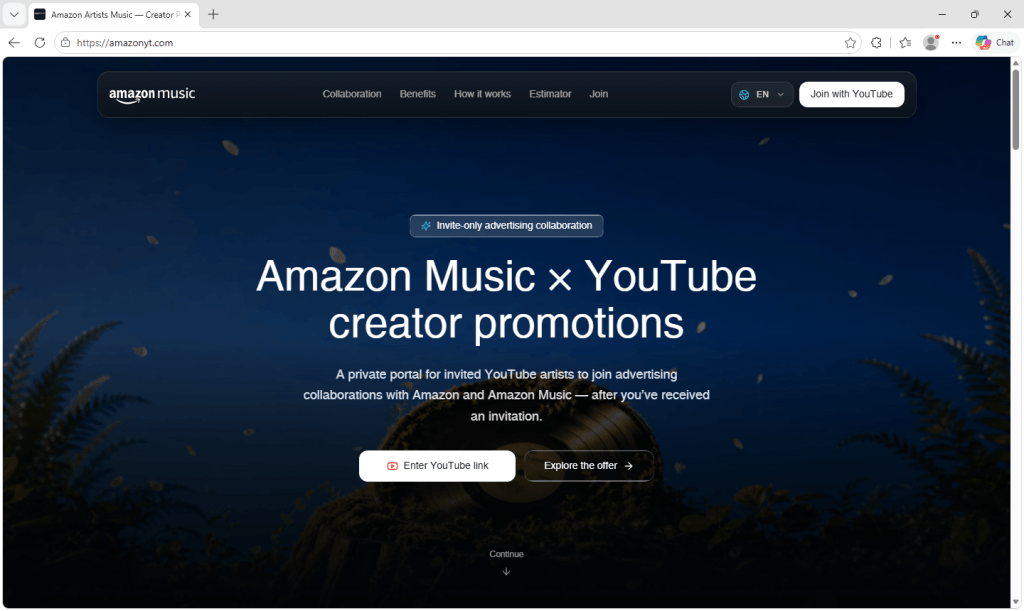
Fake Amazon Music x YouTube deal lures creators into a Google login trap

.kadence-column476672_104e78-a1 > .kt-inside-inner-col{padding-top:20px;padding-right:20px;padding-bottom:10px;padding-left:20px;}.kadence-column476672_104e78-a1 > .kt-inside-inner-col{column-gap:var(--global-kb-gap-sm, 1rem);}.kadence-column476672_104e78-a1 > .kt-inside-inner-col{flex-direction:column;}.kadence-column476672_104e78-a1 > .kt-inside-inner-col …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Microsoft PowerToys adds CursorHide, Button Lock mouse tools Moderate BleepingComputer
2026-10-21 BleepingComputer

Microsoft PowerToys adds CursorHide, Button Lock mouse tools

Microsoft has released PowerToys 0.102, with two new mouse utilities, new command-line tools, and Command Palette improvements. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
US Government Orders DeepSeek Out of Federal Civilian Systems Moderate SecurityAffairs
2026-10-21 SecurityAffairs

US Government Orders DeepSeek Out of Federal Civilian Systems

PHP prepares emergency patches for two critical RCE flaws, while older, unsupported versions could remain exposed without vendor fixes. The U.S. government ordered federal civilian agencies to remove DeepSeek products from their IT systems and stop buying them. The order also reaches third-party tools and services built with DeepSeek implementations, which i…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

China-Aligned Bronze Sandcastle Abuses Sandboxie DLL Sideloading to Deploy Backdoors Important The Hacker News
2026-10-21 The Hacker News

China-Aligned Bronze Sandcastle Abuses Sandboxie DLL Sideloading to Deploy Backdoors

Cybersecurity researchers have disclosed details of a previously undocumented China-aligned threat cluster known as Bronze Sandcastle that has been observed targeting organizations in Asia and Africa since mid-2025. "The most distinctive technical marker for Bronze Sandcastle is its consistent use of Sandboxie DLL sideloading," Sophos security researcher Gab…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Ransomware Attacks Rise as Rival Gangs Vie For Market Supremacy Critical Infosecurity Magazine
2026-10-21 Infosecurity Magazine

Ransomware Attacks Rise as Rival Gangs Vie For Market Supremacy

Cybercriminal groups The Gentlemen and Qilin dominate ransomware attacks - and both are evolving their tactics in an attempt to outdo one another

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Generative AI Is Erasing Behavioral Tells, Weakening Behavior-Only Detection, Proofpoint Reports Moderate The Hacker News
2026-10-21 The Hacker News

Generative AI Is Erasing Behavioral Tells, Weakening Behavior-Only Detection, Proofpoint Reports

Generative AI has changed what a malicious email looks like. Messages that once gave themselves away through clumsy wording, generic pretexts, and reused templates now arrive fluent, personalized, and unique to each recipient, and the behavioral signals email filters have relied on for years are fading as a result. Proofpoint shared several examples of the s…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Signal bug could let someone keep listening after you hang up Moderate CVE-2026-113380 Malwarebytes Labs
2026-10-21 Malwarebytes Labs

Signal bug could let someone keep listening after you hang up

A recently disclosed flaw in Signal’s calling software could allow another participant to keep hearing you after you hang up. The vulnerability, tracked as CVE-2026-113380 ( CVSS score 9.3 out of 10), affects RingRTC versions earlier than 2.72.0. RingRTC is the open-source library behind Signal’s voice and video calling functionality, providing calling compo…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Ransomware gangs have been exploiting Palo Alto GlobalProtect VPN flaw since June Critical CVE-2026-0257 Help Net Security
2026-10-21 Help Net Security

Ransomware gangs have been exploiting Palo Alto GlobalProtect VPN flaw since June

Several ransomware groups are exploiting CVE-2026-0257, an authentication bypass in Palo Alto Networks’ PAN-OS GlobalProtect patched in May, to break into organizations in sectors ranging from healthcare and education to government and energy. CVE-2026-0257 stems from the firewalls relying on cookies without performing detailed validation and integrity check…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
PHP2Shell: What Actually Protects You Before the 14:00 UTC PHP RCE Patch, and What Doesn't Critical The Hacker News
2026-10-21 The Hacker News

PHP2Shell: What Actually Protects You Before the 14:00 UTC PHP RCE Patch, and What Doesn't

You cannot fully block the two critical PHP flaws called PHP2Shell before today's fix, and the one setting being passed around as a workaround is not enough on its own, the security firm that suggested it now says. PHP will release the fix at 14:00 UTC on October 21 for two flaws it rates 9.2 out of 10, and has given no workaround of its own. Until you can i…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The Harness Is the Hard Part of Agentic Pentesting Moderate The Hacker News
2026-10-21 The Hacker News

The Harness Is the Hard Part of Agentic Pentesting

An AppSec team can point an AI agent running on a general-purpose model at its own web apps with little setup. Sure, the model writes the attacks. But everything that makes those attacks safe to run against production and worth acting on afterward lives in the harness around the model. The harness is where the engineering in AI pentesting sits. The Hugging F…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Attackers Hijacked Over 300 Tor Exit Relays to Intercept SSH Connections Critical The Hacker News
2026-10-21 The Hacker News

Attackers Hijacked Over 300 Tor Exit Relays to Intercept SSH Connections

Attackers took control of more than 300 Tor exit relays in early October and used them to redirect SSH connections to servers that stole login passwords, a researcher found. Exit relays are the last hop in a Tor circuit, where traffic leaves the network for its destination. Only a password login to an SSH server made through Tor between October 1 and 5, afte…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft says October updates didn’t actually fix VPN issues Moderate BleepingComputer
2026-10-21 BleepingComputer

Microsoft says October updates didn’t actually fix VPN issues

Microsoft says it mistakenly flagged a bug causing Always On VPN connection issues as fixed in the October 2026 Windows 11 cumulative updates. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
PHP Prepares Emergency Fixes for Two Critical Remote Code Execution Flaws Critical CVE-2026-109618 SecurityAffairs
2026-10-21 SecurityAffairs

PHP Prepares Emergency Fixes for Two Critical Remote Code Execution Flaws

PHP will release emergency fixes for two critical RCE flaws rated 9.2, as researchers warn of potential risks to exposed and unsupported systems. PHP is preparing an emergency security release for two critical vulnerabilities that could let attackers execute code remotely on affected servers. The update is scheduled for today, October 21 at 14:00 UTC, after …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Parasitizing trust: How legitimate infrastructure becomes a delivery pipeline for attackers Important Cisco Talos Intelligence
2026-10-21 Cisco Talos Intelligence

Parasitizing trust: How legitimate infrastructure becomes a delivery pipeline for attackers

Legitimate infrastructure has become a powerful delivery mechanism for attackers, carrying the inherent trust they once had to build. As Cisco Talos explored in our previous research on weaponizing software-as-a-service (SaaS) notification pipelines , these platforms are increasingly repurposed as proxies for malicious intent. Talos has since tracked a signi…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Grafana Labs connects observability and incident response with Knowledge Graph Moderate Help Net Security
2026-10-21 Help Net Security

Grafana Labs connects observability and incident response with Knowledge Graph

Grafana Labs has announced a Knowledge Graph in every Grafana Cloud stack, alongside new Digital Experience Monitoring capabilities and updates to Grafana Cloud Incident Response Management (IRM). The releases connect infrastructure and application dependencies with user experience and incident response, giving people and agents shared context to investigate…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
ThreatLocker adds external controls for AI agent access and execution Moderate Help Net Security
2026-10-21 Help Net Security

ThreatLocker adds external controls for AI agent access and execution

ThreatLocker has announced the launch of Zero Trust AI Control (ZTAIC), giving organizations a tool to deploy agentic AI without surrendering control of their environments. ZTAIC enables security teams to give AI agents exactly what they need to perform their jobs while keeping everything else out of reach, even as agents invoke other applications and proces…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
PHP2Shell: Two Unpatched Critical PHP RCE Flaws (CVSS 9.2) Trigger Emergency Security Alert Critical The Hacker News
2026-10-21 The Hacker News

PHP2Shell: Two Unpatched Critical PHP RCE Flaws (CVSS 9.2) Trigger Emergency Security Alert

This story is developing and was written before PHP's scheduled 14:00 UTC release on October 21. Once the release is out, the affected and fixed versions below are confirmed by the official advisory. PHP will ship an out-of-cycle security release at 14:00 UTC today, October 21, for two critical vulnerabilities that its security team has rated 9.2 on the CVSS…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Attackers Abuse UpdraftCentral Keys to Plant Backdoors on WordPress Sites Important The Hacker News
2026-10-21 The Hacker News

Attackers Abuse UpdraftCentral Keys to Plant Backdoors on WordPress Sites

Unknown threat actors breached TeamUpdraft's website and potentially gained unauthorized access to customers' connection keys for UpdraftCentral, UpdraftVault, and UpdraftClone, using them to backdoor WordPress sites. TeamUpdraft is the developer behind UpdraftPlus, a popular WordPress backup plugin with over four million active installations. The vendor als…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification