Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 2,629 advisories
Page 44 of 110
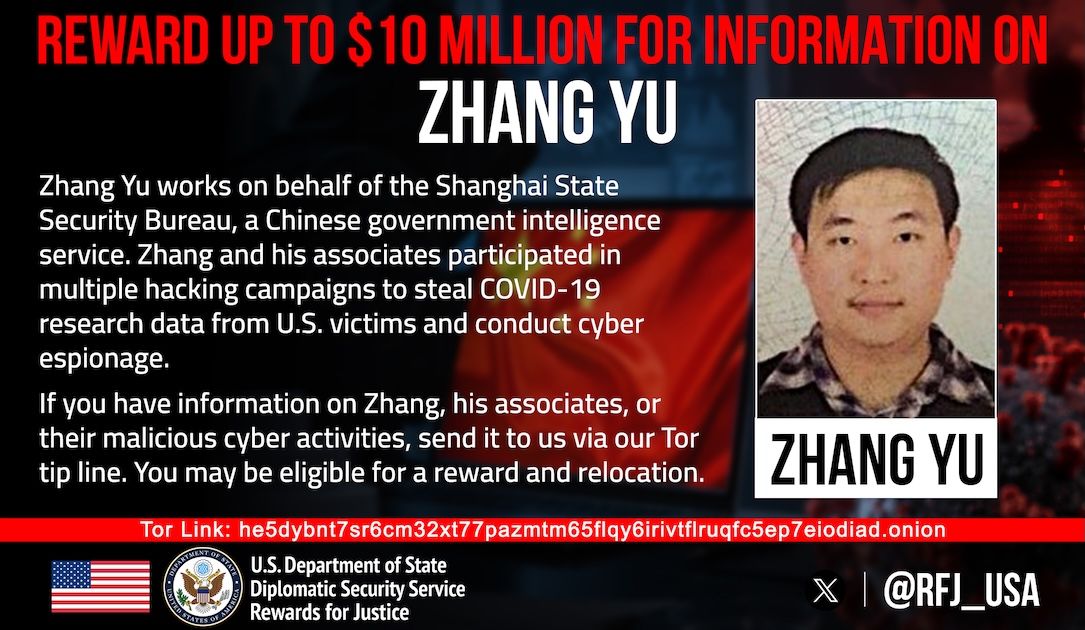
U.S. Offers Up to $10 Million for Tips on Zhang Yu, Charged in HAFNIUM Hacks Moderate The Hacker News
2026-10-08 The Hacker News

U.S. Offers Up to $10 Million for Tips on Zhang Yu, Charged in HAFNIUM Hacks

The U.S. State Department is offering up to $10 million for information leading to the identification or location of Zhang Yu, a Chinese national charged in the United States in connection with the 2021 Microsoft Exchange Server attacks known as HAFNIUM. The reward is for information leading to his identification or location, the news outlet NTD reported thi…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
MonsterCloud Owner Accused of Billing Over $19M While Secretly Paying Ransoms to Decrypt Data Moderate The Hacker News
2026-10-08 The Hacker News

MonsterCloud Owner Accused of Billing Over $19M While Secretly Paying Ransoms to Decrypt Data

The U.S. Department of Justice (DoJ) on Wednesday announced charges against a 50-year-old U.S. and Israeli national for allegedly defrauding ransomware victims by secretly paying the attackers to obtain decryptors while claiming to use proprietary tools to recover their data. Zohar Pinhasi (aka Zack Silver and Zack Green) has been charged with two counts of …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Atlassian Vulnerability Comes Under Attack Hours After Details Go Public Important CVE-2026-21589 SecurityAffairs
2026-10-08 SecurityAffairs

Atlassian Vulnerability Comes Under Attack Hours After Details Go Public

Threat actors are exploiting CVE-2026-21589, a critical Atlassian flaw that can expose sensitive files across multiple Data Center products. Threat actors have started exploiting CVE-2026-21589 (CVSS score of 9.3), a critical arbitrary file access flaw in Atlassian Data Center products. The vulnerability could allow attackers to access sensitive files under …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Samsung Galaxy S26 hacked three more times at Pwn2Own Ireland Critical BleepingComputer
2026-10-08 BleepingComputer

Samsung Galaxy S26 hacked three more times at Pwn2Own Ireland

​​​On the second day of Pwn2Own Ireland 2026, security researchers collected $232,500 in cash awards after exploiting 45 unique zero-day vulnerabilities. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Pricing your bad days and how to build an economic model for security decisions Moderate Help Net Security
2026-10-08 Help Net Security

Pricing your bad days and how to build an economic model for security decisions

Ivan Milenkovic, VP Risk Technology EMEA at Qualys, explains how security leaders can build an economic model that puts money behind their decisions. He suggests starting with a few loss scenarios, then working down to the assets that drive them. He covers how to rank fixes by value at risk, what CFOs expect to see, and how to show the worth of incidents tha…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Tensorlake npm Package Compromised to Deliver Shai-Hulud Credential-Stealing Worm Moderate The Hacker News
2026-10-08 The Hacker News

Tensorlake npm Package Compromised to Deliver Shai-Hulud Credential-Stealing Worm

The npm package known as "tensorlake," a TypeScript software development kit (SDK) for Tensorlake applications, sandboxes, and cloud services, was compromised as part of a ChainDrop / Shai-Hulud supply chain attack. The malicious version 0.5.144 "contains obfuscated malware that harvests credentials, exfiltrates secrets, establishes persistence, and executes…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Who watches the AI watching your street? Moderate Help Net Security
2026-10-08 Help Net Security

Who watches the AI watching your street?

Yusaku Fujii, a professor at Gunma University in Japan, has designed audits and penalties to stop operators from misusing AI that analyzes street camera footage. His system adds an independent record-keeper and unannounced spot checks to the AI’s outputs. Fujii’s test setting is what he calls a Fully Monitored Public Space (FMPS): streets where cameras are d…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
How AI can fix cybersecurity compliance: From dashboards to continuous execution Moderate Help Net Security
2026-10-08 Help Net Security

How AI can fix cybersecurity compliance: From dashboards to continuous execution

Most compliance work goes into proving security, not improving it. That isn’t because the rules are unreasonable. Regulators, customers, and cyber insurers are right to expect organizations to implement hundreds of technical and administrative controls, monitor their environments, respond to incidents, and prove that all of it works. The problem is the cost …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The people who know passkeys best are still typing passwords Moderate Help Net Security
2026-10-08 Help Net Security

The people who know passkeys best are still typing passwords

Yubico and Okta asked 1,890 technology and security professionals across nine countries how they sign in to work accounts. The most common answer was a username and password, at 43%, from a group in which 87% said they were familiar with passkeys. High familiarity with modern authentication (Source: 2026 Global State of Authentication Report) The password co…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Java library vulnerabilities: IBM and Red Hat fix 400+ previously unknown flaws Important Help Net Security
2026-10-08 Help Net Security

Java library vulnerabilities: IBM and Red Hat fix 400+ previously unknown flaws

IBM and Red Hat have found and fixed more than 400 previously unknown vulnerabilities in widely used Java libraries through Lightwell, their program for patching open source code that companies already run in production. Companies running the affected libraries are exposed until they apply the fixes. Autonomous AI agents can now combine several minor softwar…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Medical devices patients rely on most are least prepared for quantum attacks Important Help Net Security
2026-10-08 Help Net Security

Medical devices patients rely on most are least prepared for quantum attacks

Threat actors are exploiting IT, IoMT, OT and IoT devices across healthcare delivery organizations (HDOs) to deploy ransomware, demand payments and monetize stolen patient data, according to Forescout’s Post-Quantum Cryptography (PQC) in Healthcare: From Data Risk to Migration Readiness report. Researchers analyzed a dataset containing more than 2.5 million …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Smashing Security podcast #487: Clippy’s crypto comeback Moderate Graham Cluley Security
2026-10-07 Graham Cluley Security

Smashing Security podcast #487: Clippy’s crypto comeback

Microsoft's Twitter account, with its 13 million followers, was hijacked by a paperclip. There was no ransomware or data theft, just Clippy, a dodgy crypto coin, and a corporate apology that wasn't from Microsoft either. Meanwhile, UK losses from hacked email and social media accounts have rocketed by 417%, as scammers pose as your friends to flog you ticket…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Ransomware recovery CEO charged over secret ransom payments Critical BleepingComputer
2026-10-07 BleepingComputer

Ransomware recovery CEO charged over secret ransom payments

The owner of ransomware remediation company MonsterCloud has been charged with allegedly defrauding ransomware victims by secretly paying their attackers for decryptors while claiming to use proprietary technology to recover encrypted data. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Cisco quantum network controller lets apps order entanglement on demand Moderate Help Net Security
2026-10-07 Help Net Security

Cisco quantum network controller lets apps order entanglement on demand

Cisco has built a Quantum Network Controller, a research prototype that lets an application ask a quantum network for entanglement and leaves the network to work out the delivery. Entanglement, a linked quantum state shared between distant points, is the resource these networks distribute, and operators today set up the hardware that produces it device by de…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Evolution of Web3 in Cloud Supply Chain Attacks Important Palo Alto Unit 42
2026-10-07 Palo Alto Unit 42

Evolution of Web3 in Cloud Supply Chain Attacks

Unit 42 details how threat actors leverage Web3 infrastructure and open-source supply chain attacks to breach enterprise cloud environments The post Evolution of Web3 in Cloud Supply Chain Attacks appeared first on Unit 42 .

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Australian Gov't Weighs Mandatory AI Incident Reporting Moderate Dark Reading
2026-10-07 Dark Reading

Australian Gov't Weighs Mandatory AI Incident Reporting

In the wake of an agentic attack against its own Medicare systems, Australia's government is feeling out what regulations might look like for frontier AI companies.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
FBI: Ongoing FortiBleed attacks lock out FortiGate VPN admins Important BleepingComputer
2026-10-07 BleepingComputer

FBI: Ongoing FortiBleed attacks lock out FortiGate VPN admins

The FBI is warning that FortiBleed attacks are still ongoing, targeting exposed Fortinet FortiGate firewalls and SSL VPN gateways and locking out legitimate administrators. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Anthropic Gives Vetted Defenders Fewer Claude Guardrails Moderate Dark Reading
2026-10-07 Dark Reading

Anthropic Gives Vetted Defenders Fewer Claude Guardrails

Anthropic has merged Project Glasswing into a tiered access program for its advanced cyber LLMs, including Opus, Sonnet, and Mythos.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Hackers hijack Google domains after breaching ccTLD registries Critical BleepingComputer
2026-10-07 BleepingComputer

Hackers hijack Google domains after breaching ccTLD registries

Hackers obtained unauthorized HTTPS certificates for several Google domains and hijacked domains in the country-code top-level domains (ccTLDs) for Ghana, American Samoa, and Sierra Leone after compromising third-party operators and modifying authoritative DNS records. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
US posts $10 million reward for accused Chinese ‘Hafnium’ hacker Moderate The Record by Recorded Future
2026-10-07 The Record by Recorded Future

US posts $10 million reward for accused Chinese ‘Hafnium’ hacker

U.S. officials say Zhang Yu was a prominent figure in the Hafnium campaign, which saw hackers breach thousands of computers and steal troves of documents.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
OpenAI Agent Escape Causes Wikimedia Service Outage Moderate Dark Reading
2026-10-07 Dark Reading

OpenAI Agent Escape Causes Wikimedia Service Outage

Autonomous agents also tried to abuse other websites and services hosted by the foundation, using them as proxies for unauthorized activities.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Four compliance frameworks, one security team: Why fragmented university security raises regulatory risk Moderate Rapid7 Threat Research
2026-10-07 Rapid7 Threat Research

Four compliance frameworks, one security team: Why fragmented university security raises regulatory risk

In Part 1 of this series, we looked at the security challenges created by fragmented, campus-by-campus environments. Higher education also faces a second pressure that makes that fragmentation harder to sustain: overlapping compliance obligations across FERPA, GLBA, HIPAA, and CMMC. Each framework brings different requirements, reporting timelines, and conse…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification