
Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 2,629 advisories
Page 49 of 110
Atlassian urges immediate patching of critical Data Center file access vulnerability (CVE-2026-21589) Critical CVE-2026-21589 Help Net Security
2026-10-06 Help Net Security

Atlassian urges immediate patching of critical Data Center file access vulnerability (CVE-2026-21589)

Attackers who know where to look can read files from Atlassian Data Center installations without logging in, the company has warned. About CVE-2026-21589 CVE-2026-21589, a critical arbitrary file access vulnerability with a 9.3 CVSS score, affects all versions of Bitbucket Data Center, Confluence Data Center, Jira Service Management Data Center, Jira Softwar…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Critical Medical Devices Unable to Support PQC Transition Critical Infosecurity Magazine
2026-10-06 Infosecurity Magazine

Critical Medical Devices Unable to Support PQC Transition

Forescout found that just 6% of Internet of Medical Things (IoMT) and 16% of medical OT are capable of supporting post quantum cryptography

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Facebook Marketplace scam uses your name and number Moderate Malwarebytes Labs
2026-10-06 Malwarebytes Labs

Facebook Marketplace scam uses your name and number

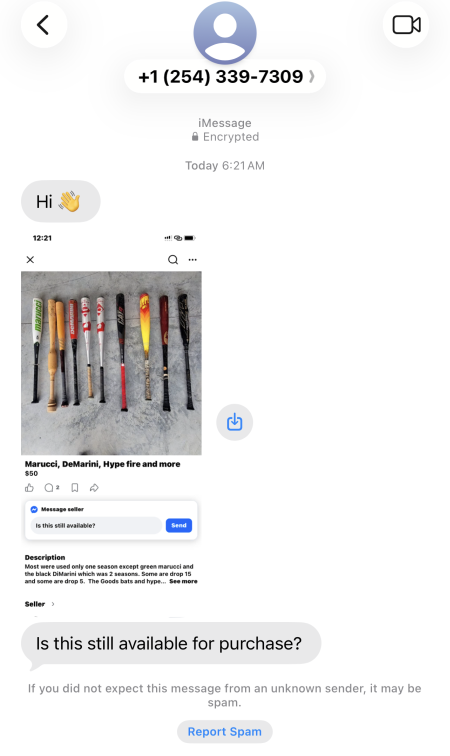
Facebook users are reporting receiving a message with a fake Facebook Marketplace listing that has their name as the seller. It works like this. You receive a message (in this case iMessage) asking “Is this still available for purchase?” Attached to the message is a fabricated Facebook Marketplace listing. Tapping on the picture, you might notice that the se…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
LibreOffice and OpenOffice Flaws Let Malicious Spreadsheets Run Code Without Macro Warnings Important The Hacker News
2026-10-06 The Hacker News

LibreOffice and OpenOffice Flaws Let Malicious Spreadsheets Run Code Without Macro Warnings

A malicious spreadsheet can make LibreOffice and Apache OpenOffice run an attacker's code as soon as the file is opened, security researchers have shown. There is no warning first, of the kind either program shows before it runs a macro. The attack works only when the program's Java support is enabled. So far, it has only been shown as a proof of concept, an…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Wikimedia: Rogue OpenAI agents behind unauthorized Wikipedia edits Moderate BleepingComputer
2026-10-06 BleepingComputer

Wikimedia: Rogue OpenAI agents behind unauthorized Wikipedia edits

The Wikimedia Foundation says rogue OpenAI agents made unauthorized Wikipedia edits and may have been partially responsible for a May outage. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Wikimedia Says OpenAI Agents Tried to Compromise Etherpad and Use Wiki Tools as Proxies Moderate The Hacker News
2026-10-06 The Hacker News

Wikimedia Says OpenAI Agents Tried to Compromise Etherpad and Use Wiki Tools as Proxies

The Wikimedia Foundation, which hosts Wikipedia, has confirmed that it has discovered activity by rogue OpenAI agents on its platforms, including unsuccessful efforts to compromise Etherpad, a public note-taking tool, and edit Wikipedia pages. "The unauthorized bot activities included edits to our wikis, some unsuccessful attempts to exploit a public note-ta…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Domino’s customers targeted in credential stuffing attacks Important Malwarebytes Labs
2026-10-06 Malwarebytes Labs

Domino’s customers targeted in credential stuffing attacks

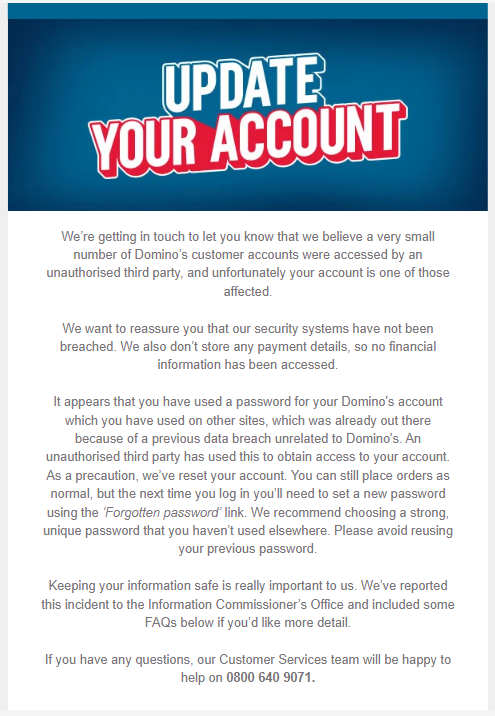
Domino’s Pizza customers tell us they have received emails saying they account has been accessed by a third party. Domino’s says its internal systems weren’t breached, but that individual accounts were logged into using a password and email combination stolen from another online account owned by the customer. This is known as credential stuffing. Here’s the …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Welcome to the Jungle: What We Found Inside 15,465 Public MCP Servers Moderate The Hacker News
2026-10-06 The Hacker News

Welcome to the Jungle: What We Found Inside 15,465 Public MCP Servers

In 2024, MCP (Model Context Protocol) set out to become the USB-C of AI: one standard for connecting models, agents, and IDEs to tools and data. The protocol delivered. Thousands of developers built servers, and enterprises plugged them into agent workflows. The ecosystem around it fell short. Earlier this year, our team at OX Security, traced critical vulne…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Dell System Update flaw allows attackers to gain root privileges (CVE-2026-86360) Important CVE-2026-86360 Help Net Security
2026-10-06 Help Net Security

Dell System Update flaw allows attackers to gain root privileges (CVE-2026-86360)

Dell is urging customers to patch a vulnerability (CVE-2026-86360) in Dell System Update (DSU) that could allow an unauthenticated remote attacker to execute arbitrary code with root privileges. DSU is a tool used by enterprise IT administrators to apply driver, BIOS, and firmware updates to Dell PowerEdge servers. About CVE-2026-86360 CVE-2026-86360 is a pa…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Ontinue extends ION MXDR with managed dark web monitoring Moderate Help Net Security
2026-10-06 Help Net Security

Ontinue extends ION MXDR with managed dark web monitoring

Ontinue has announced the launch of ION for Dark Web Monitoring (DWM), a new managed add-on service that extends ION MXDR to continuously identify exposed credentials, detect brand impersonation attempts, and uncover emerging external threats before attackers can exploit them. Compromised credentials are traded across criminal forums, lookalike domains are c…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Blinder Tunnel Campaign Targets Iraqi Infrastructure Moderate Palo Alto Unit 42
2026-10-06 Palo Alto Unit 42

Blinder Tunnel Campaign Targets Iraqi Infrastructure

Analysis of Blinder Tunnel, an Iran-nexus campaign using fake Dubai Airports recruitment lures and GitHub C2 malware to target critical infrastructure. The post Blinder Tunnel Campaign Targets Iraqi Infrastructure appeared first on Unit 42 .

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
GitHub’s ReviewBench puts AI code reviewers to the test Moderate Help Net Security
2026-10-06 Help Net Security

GitHub’s ReviewBench puts AI code reviewers to the test

GitHub’s ReviewBench measures how well AI code review tools detect problems before software is released. Available in research preview through its website, the benchmark lets users compare review agents and evaluate their own tools. Code review involves checking proposed changes for mistakes. ReviewBench measures AI reviewers’ ability to identify issues and …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Pwn2Own Ireland 2026 - Day One Results Critical Trend Micro ZDI
2026-10-06 Trend Micro ZDI

Pwn2Own Ireland 2026 - Day One Results

Welcome to Day One of Pwn2Own Ireland 2026! Today, 21 entries took the Pwn2Own stage to target multiple categories - including multiple Samsung attempts and our first Pixel entry. Follow the action live! We’ll be posting real-time updates and results throughout the competition on our blog and across social media. Stay up to date by following us on Twitter , …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
FBI Drops Accenture Contractor After Sensitive Data Breach Critical SecurityAffairs
2026-10-06 SecurityAffairs

FBI Drops Accenture Contractor After Sensitive Data Breach

Accenture lost an FBI contract after a missed security patch exposed sensitive employee data, raising serious concerns over operational security. The FBI pulled an Accenture contractor off its account on Monday, and the reason is almost mundane compared to the damage it caused. One update didn’t get installed on time. “The ‌Federal Bureau of Investigation re…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Nikkei discloses breaches of employees’ Microsoft, Google email accounts Critical BleepingComputer
2026-10-06 BleepingComputer

Nikkei discloses breaches of employees’ Microsoft, Google email accounts

Over the weekend, Japanese publishing giant Nikkei disclosed that unknown attackers recently breached two employee email accounts and used one to send thousands of phishing emails. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Google Pauses OSS Product Bug Bounty Rewards After Surge in Invalid Automated Reports Moderate The Hacker News
2026-10-06 The Hacker News

Google Pauses OSS Product Bug Bounty Rewards After Surge in Invalid Automated Reports

Google has stopped accepting product vulnerability reports through its bug bounty program for its open-source software. The change, in effect since October 1, means researchers can no longer submit security flaws in the code of projects such as Go, Angular, and Protocol Buffers there for a reward. Reports about supply chain compromises are still accepted, an…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Data breach at Denmark’s population register exposes 8.8 million people Critical Help Net Security
2026-10-06 Help Net Security

Data breach at Denmark’s population register exposes 8.8 million people

A data breach at Denmark’s Central Population Register (CPR) has exposed the personal information of 8.8 million people. These include people living in Denmark, deceased people and citizens who have moved abroad. The CPR is Denmark’s national register of residents, and the 10-digit CPR number it assigns to each person is used for everything from taxes and he…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Engineer sentenced for locking over 3,000 devices on employer network Moderate BleepingComputer
2026-10-06 BleepingComputer

Engineer sentenced for locking over 3,000 devices on employer network

A former core infrastructure engineer at an industrial company headquartered in New Jersey was sentenced to 32 months in prison for locking thousands of devices on his employer's network in a ransomware-style attack. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Dell Urges Customers to Patch Critical DSU Flaw That Can Give Attackers Root Access Critical CVE-2026-86360 SecurityAffairs
2026-10-06 SecurityAffairs

Dell Urges Customers to Patch Critical DSU Flaw That Can Give Attackers Root Access

Dell warns that a critical DSU flaw lets attackers run code as root. Customers should patch affected PowerEdge systems as soon as possible. Dell urged customers to patch a critical flaw, tracked as CVE-2026-86360 (CVSS score of 9.6), in its System Update (DSU) tool. The vulnerability is a path traversal issue that can let attackers execute code with root pri…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Critical Atlassian Flaw Lets Unauthenticated Attackers Read Known Files Across 8 Products Critical CVE-2026-21589 The Hacker News
2026-10-06 The Hacker News

Critical Atlassian Flaw Lets Unauthenticated Attackers Read Known Files Across 8 Products

A critical flaw in 8 Atlassian Data Center products, which customers host themselves, allows an attacker with no login access to read specific files in each product's web application root directory. The attacker must already know a file's exact name and path and cannot list what the directory holds. Atlassian disclosed the flaw, CVE-2026-21589, on October 5,…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification