
Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 2,629 advisories
Page 6 of 110
Hive ransomware affiliate jailed, years after FBI infiltrated the gang’s systems Critical Graham Cluley Security
2026-10-28 Graham Cluley Security

Hive ransomware affiliate jailed, years after FBI infiltrated the gang’s systems

A Ukrainian man who carried out ransomware attacks for both the Nefilim and Hive gangs, including attacks on law firms and a healthcare provider during the COVID-19 pandemic, has been sentenced to 70 months in a US prison. Read more in my article on the Hot for Security blog.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Banks are blocking AI agents from customer accounts Moderate Malwarebytes Labs
2026-10-28 Malwarebytes Labs

Banks are blocking AI agents from customer accounts

This week, Axios reported that major US banks were detecting third-party AI agents operating inside customer accounts. In many cases, customers have given the agents their usernames and passwords so they could act on their behalf. This kind of access can violate a bank’s rules. Bianco Research president Jim Bianco raised the question during Unchained’s Bits …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Chrome and Firefox updates fix serious security flaws. Install now Important Malwarebytes Labs
2026-10-28 Malwarebytes Labs

Chrome and Firefox updates fix serious security flaws. Install now

On October 27, Google issued a new Stable channel update for Chrome. Most users are on Chrome’s Stable channel. The desktop update brings Chrome to versions 156.0.8078.73/.74 for Windows and Mac and 156.0.8078.73 for Linux . The update includes 52 security fixes, including four rated Critical. On the same day, Mozilla issued Security Advisory 2026-118 , whic…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Millions of security cameras at risk: DoS vulnerability in Intelbras devices Important Kaspersky Securelist
2026-10-28 Kaspersky Securelist

Millions of security cameras at risk: DoS vulnerability in Intelbras devices

Background Network-connected surveillance cameras are now widespread in both home and enterprise environments, so securing them is essential to safeguarding physical spaces and sensitive assets. As these devices continue to gain new features and network connectivity capabilities, vulnerabilities in their implementation can have significant security implicati…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Waiting on a Node.js Upgrade? Build a Stopgap with the Controls You Own Critical CVE-2026-111497 Qualys Security Blog
2026-10-28 Qualys Security Blog

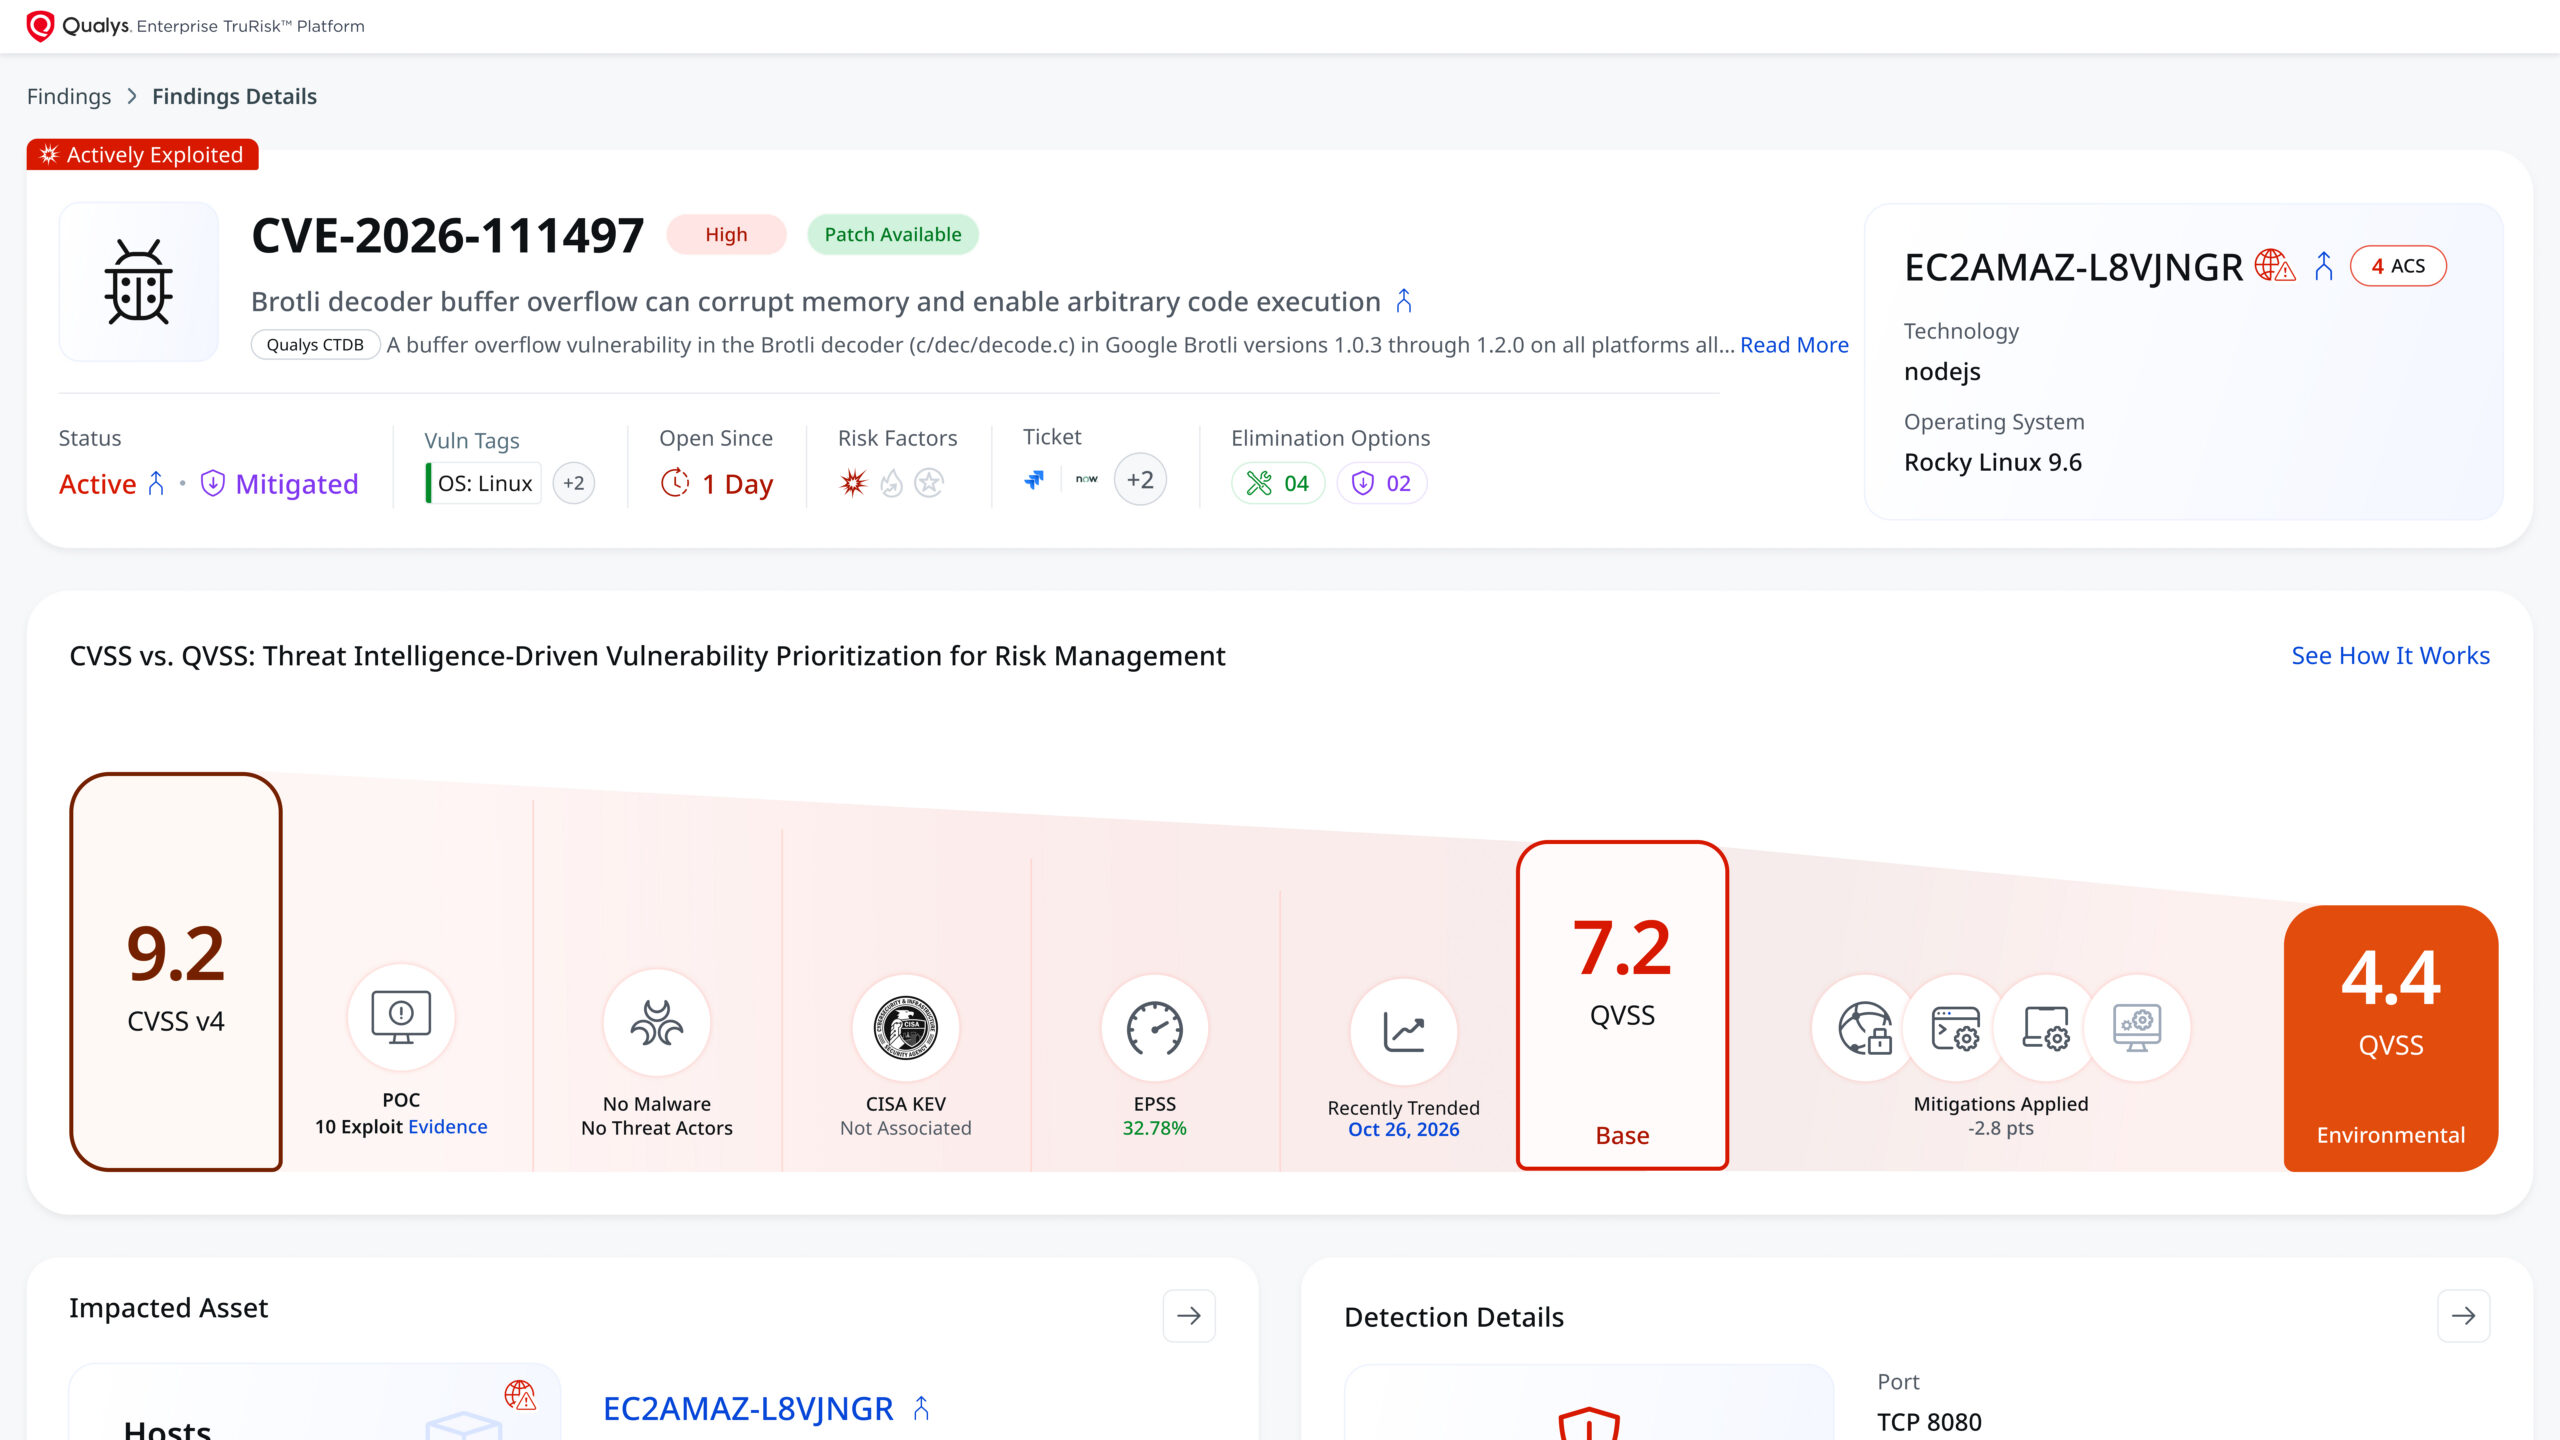
Waiting on a Node.js Upgrade? Build a Stopgap with the Controls You Own

Executive Summary Node.js has fixed CVE-2026-111497, a Brotli decoder flaw that can permit remote code execution, in 22.23.4, 24.22.1, and 26.12.1, but upgrading at scale is slow. In Qualys telemetry, only 42,000 of roughly 3 million Node.js installations have been patched, and 1.7 million run end-of-life lines that will never receive a fix. In the meantime,…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Third Serengeti Sweep Tops 1,400 Arrests as Investigations Mature Moderate Dark Reading
2026-10-28 Dark Reading

Third Serengeti Sweep Tops 1,400 Arrests as Investigations Mature

Interpol's annual Operation Serengeti, now in its third iteration, led to 1,462 arrests across 20 African countries and the US, recovering $105 million in stolen funds.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
External Teams Chats Anchor 15-Minute Malware Delivery Important Dark Reading
2026-10-27 Dark Reading

External Teams Chats Anchor 15-Minute Malware Delivery

Mail bombing is getting a new look with a wide-scale, ongoing social engineering campaign that might be tied to the Black Basta ransomware gang.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
SBOMs Alone Can't Reveal the Scope of a Supply Chain Attack Important Dark Reading
2026-10-27 Dark Reading

SBOMs Alone Can't Reveal the Scope of a Supply Chain Attack

A recent Shai-Hulud attack shows defenders need real-time visibility into production code and affected services to respond to supply chain compromises.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Beware the Slasher: AI Could Kill Off Cybersecurity Pros' Skills Moderate Dark Reading
2026-10-27 Dark Reading

Beware the Slasher: AI Could Kill Off Cybersecurity Pros' Skills

Nathan Hamiel outlines potential SecOps horror in the AI midst, as core technical capabilities go the way of reading an atlas or remembering phone numbers.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
'Aokigahara' Stealer Targets 'Developer Keyrings' & AI Assistants Moderate Dark Reading
2026-10-27 Dark Reading

'Aokigahara' Stealer Targets 'Developer Keyrings' & AI Assistants

The malware's focus on AI tools expands the traditional infostealer playbook to expose a forest of AI sessions, sensitive business data, and developer infrastructure from a single compromised endpoint.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CVE-2026-35273: SSRF to RCE in Oracle PeopleSoft Critical CVE-2026-35273 Trend Micro ZDI
2026-10-27 Trend Micro ZDI

CVE-2026-35273: SSRF to RCE in Oracle PeopleSoft

On September 25, 2026, Mandiant released a report regarding continued mass exploitation of CVE-2026-35273 by the ShinyHunters group. TrendAI’s Zero Day Initiative first reported this CVE to Oracle on June 10, 2026, following an investigation I conducted with Minh Giang and Lucas Miller of TrendAI Research. Although Oracle issued a patch under a single CVE, w…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
OpenAI Compaction Flaw Exposed AI Reasoning to Researchers Important Infosecurity Magazine
2026-10-27 Infosecurity Magazine

OpenAI Compaction Flaw Exposed AI Reasoning to Researchers

Researchers uncovered an OpenAI API flaw that exposed hidden AI reasoning traces, prompting a fix and a $6000 bug bounty reward

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Five election scams to watch out for Moderate Malwarebytes Labs
2026-10-27 Malwarebytes Labs

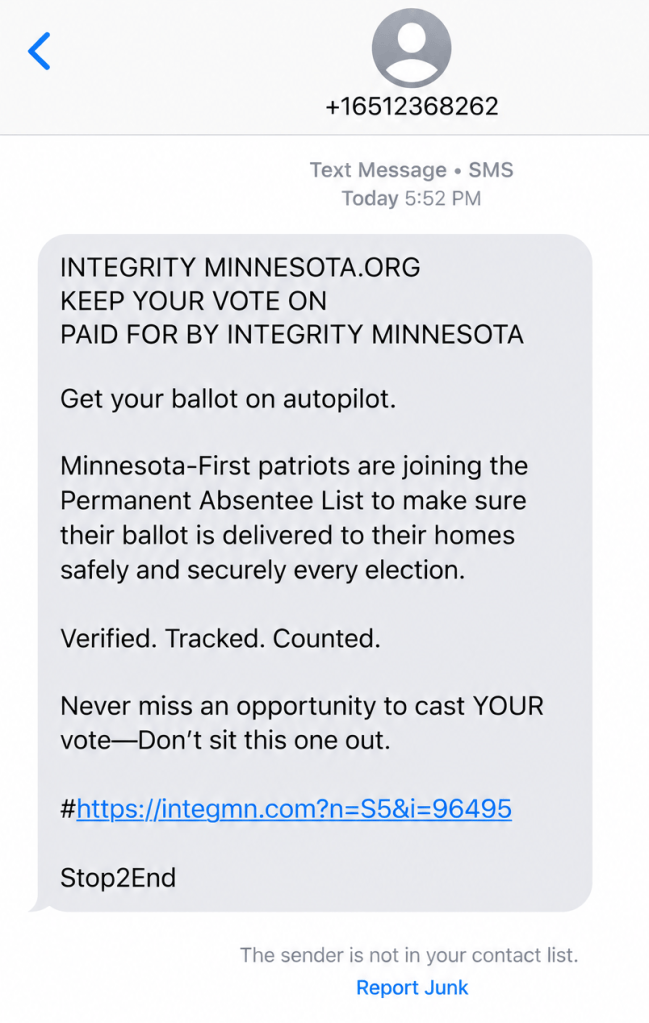
Five election scams to watch out for

Elections give scammers plenty to work with: urgent deadlines, familiar faces, passionate supporters, and messages asking people to take action. Some want you to “fix” your voter registration. Others want a donation, an answer to a survey, or payment for merchandise supposedly endorsed by your favorite politician. The details change, but the objective stays …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Tricks from the Past deployed via signed ChatGPT and Claude binaries Critical Check Point Research
2026-10-27 Check Point Research

Tricks from the Past deployed via signed ChatGPT and Claude binaries

Key Points Check Point Research discovered a campaign we track as Yoba where attackers abuse the popularity of AI tools such as ChatGPT and Claude, creating fake GitHub projects that pretend to be desktop applications like GPT-5.6 Sol , GPT-6 Astra , and Claude Opus . The malware is placed next to legitimate, signed executables from OpenAI and Anthropic so i…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Introducing the Cloudflare PHP Capture the Flag challenge Critical CVE-2026-109618 Cloudflare Security
2026-10-27 Cloudflare Security

Introducing the Cloudflare PHP Capture the Flag challenge

Update — October 30, 2026: Thank you to everyone who has participated in the PHP Capture the Flag challenge. We have received a strong response from the security research community, and the submissions have helped us harden our existing php2shell WAF protections and create new detections. Details of managed-rule changes are available in the Cloudflare WAF ch…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification