Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 2,629 advisories
Page 68 of 110
Elementor CSRF Flaw Lets Attackers Take Over Sites After Admin Clicks Crafted Link Important The Hacker News
2026-09-26 The Hacker News

Elementor CSRF Flaw Lets Attackers Take Over Sites After Admin Clicks Crafted Link

Details have emerged about a high-severity security flaw in the Elementor Website Builder WordPress plugin that could be exploited by an unauthenticated attacker to create rogue administrator accounts and take control of a site. The cross-site request forgery (CSRF) vulnerability, which has yet to be assigned a CVE identifier, carries a CVSS score of 8.8 out…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

SharePoint RCE and MikroTik RouterOS Flaws Actively Exploited in the Wild Critical CVE-2026-65660 The Hacker News
2026-09-26 The Hacker News

SharePoint RCE and MikroTik RouterOS Flaws Actively Exploited in the Wild

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added two security flaws impacting Microsoft SharePoint and Mikrotik RouterOS to its Known Exploited Vulnerabilities (KEV) catalog, citing evidence of active exploitation. The vulnerabilities in question are as follows - CVE-2026-65660 (CVSS score: 8.8) - A code injection vulnerabilit…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Kiteworks Urges Customers to Shut Down Systems for 9 Hours Over Possible Cyber Attack Important The Hacker News
2026-09-26 The Hacker News

Kiteworks Urges Customers to Shut Down Systems for 9 Hours Over Possible Cyber Attack

Kiteworks (formerly Accellion) is urging customers to shut down their systems as a precautionary measure for nine hours over the weekend after it received threat intelligence about an imminent cyber attack. "Kiteworks received credible threat intelligence from federal intelligence authorities indicating that a threat actor may attempt to target some Kitework…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog Important CVE-2026-87902 SecurityAffairs
2026-09-26 SecurityAffairs

U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog

U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds WordPress flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a WordPress Core flaw, tracked as CVE-2026-87902 (CVSS score of 9.2), to its Known Exploited Vulnerabilities (KEV) catalog . CVE-2026-87902 allows an unauthenti…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

3 Consulting Myths Debunked by Unit 42 Experts Moderate Palo Alto Unit 42
2026-09-25 Palo Alto Unit 42

3 Consulting Myths Debunked by Unit 42 Experts

Unit 42 security experts address critical cybersecurity misconceptions, offering practical insights to help your organization reinforce its enterprise defenses. The post 3 Consulting Myths Debunked by Unit 42 Experts appeared first on Unit 42 .

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Kiteworks urges 6-hour server shutdown over potential zero-day attacks Critical BleepingComputer
2026-09-25 BleepingComputer

Kiteworks urges 6-hour server shutdown over potential zero-day attacks

Secure file-sharing software company Kiteworks is urging customers worldwide to temporarily shut down their servers on Saturday for a six-hour window after receiving threat intelligence warning of a potentially imminent cyberattack. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
U.S. CISA adds Microsoft SharePoint and Mikrotik RouterOS flaws to its Known Exploited Vulnerabilities catalog Important CVE-2026-65660 SecurityAffairs
2026-09-25 SecurityAffairs

U.S. CISA adds Microsoft SharePoint and Mikrotik RouterOS flaws to its Known Exploited Vulnerabilities catalog

U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Microsoft SharePoint and Mikrotik RouterOS flaws flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog : CVE-2026-65660 (CVSS score of 8.8) …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
ShinyHunters hacked Clop leak site using Grav CMS path traversal flaw Important BleepingComputer
2026-09-25 BleepingComputer

ShinyHunters hacked Clop leak site using Grav CMS path traversal flaw

The Clop ransomware gang has moved its data leak site to a new Tor address after confirming its previous server was compromised and defaced through an unpatched Grav CMS flaw that BleepingComputer has learned is an unauthenticated path traversal vulnerability. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Why the CISO-CFO Relationship Is a Key to Cybersecurity Success Moderate Dark Reading
2026-09-25 Dark Reading

Why the CISO-CFO Relationship Is a Key to Cybersecurity Success

Organizations where CISOs and CFOs align on cybersecurity strategy to protect assets, manage risk, and enable business growth are better prepared to face today's threat landscape.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Kiteworks urges customers to stop using platform after warning from federal intelligence agencies Moderate The Record by Recorded Future
2026-09-25 The Record by Recorded Future

Kiteworks urges customers to stop using platform after warning from federal intelligence agencies

Frank Balonis, CISO at Kiteworks, told Recorded Future News that the company “received credible threat intelligence from federal intelligence authorities indicating that a threat actor may attempt to target some Kiteworks systems for customers.”

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Labcorp to overhaul data security practices, pay $2.3 million fine for cybersecurity failings Moderate The Record by Recorded Future
2026-09-25 The Record by Recorded Future

Labcorp to overhaul data security practices, pay $2.3 million fine for cybersecurity failings

Security changes include creating an incident response plan for vendor security failings, limiting how much data Labcorp shares with vendors and building an expansive risk management team charged with tracking vendors’ compliance with data security practices.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Elementor WordPress flaw lets attackers create admin accounts Important BleepingComputer
2026-09-25 BleepingComputer

Elementor WordPress flaw lets attackers create admin accounts

A cross-site request forgery (CSRF) vulnerability in the Elementor plugin for WordPress could allow an unauthenticated attacker to create administrator accounts. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Cryptocurrency exchange Bitget Says North Korea-Linked Hackers Stole $351.6 Million Important SecurityAffairs
2026-09-25 SecurityAffairs

Cryptocurrency exchange Bitget Says North Korea-Linked Hackers Stole $351.6 Million

Bitget says suspected North Korea-linked actors stole $351.6M from hot and warm wallets. Withdrawals were suspended while Mandiant investigates. Cryptocurrency exchange Bitget says suspected North Korea-linked threat actors stole $351.6 million from a limited number of hot and warm wallets. The company detected unauthorized transfers on September 24 and temp…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
What We Missed: Google Gemini Joins the AI Escape Party Moderate Dark Reading
2026-09-25 Dark Reading

What We Missed: Google Gemini Joins the AI Escape Party

In this video conversation, Dark Reading editors discuss some of the news they didn't get a chance to cover, from Google Gemini models breaking containment to ShinyHunters ratting on TeamPCP hackers.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CISA warns of Sharepoint, WSO2, Adobe Commerce flaws exploited in attacks Critical CVE-2026-5430 BleepingComputer
2026-09-25 BleepingComputer

CISA warns of Sharepoint, WSO2, Adobe Commerce flaws exploited in attacks

The Cybersecurity and Infrastructure Security Agency (CISA) warns that hackers are exploiting a critical authentication bypass vulnerability (CVE-2026-5430) affecting multiple products from enterprise software provider WSO2. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
LinkedIn adds new checks for fake profiles and work histories Moderate Malwarebytes Labs
2026-09-25 Malwarebytes Labs

LinkedIn adds new checks for fake profiles and work histories

LinkedIn is adding trust and verification features aimed at making fake professional identities, invented work histories, and company impersonation harder to pull off. The company is responding to an environment in which generative AI enables imposters to create an entirely made-up professional persona. It reduces the cost of creating convincing headshots, b…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Cyberattack hits Welsh police force, may have affected staff data Critical The Record by Recorded Future
2026-09-25 The Record by Recorded Future

Cyberattack hits Welsh police force, may have affected staff data

Dyfed-Powys Police in Wales said a cyberattack affecting the force disrupted some non-emergency systems and may have compromised staff information.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Kothamine malware uses Tailscale’s tailcat to evade network detection Important Malwarebytes Labs
2026-09-25 Malwarebytes Labs

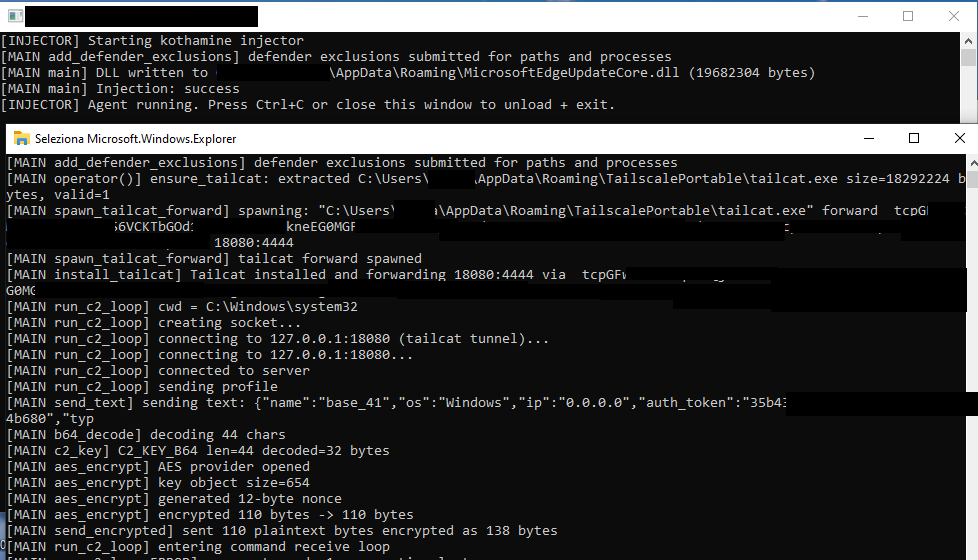
Kothamine malware uses Tailscale’s tailcat to evade network detection

We discovered an undocumented remote-access Trojan (RAT) called Kothamine Agent . It supports more than 30 commands and it gives attackers control of an infected Windows computer: they can run commands, read and change files, and add new capabilities. Some versions can also steal browser data and record through the camera and microphone. We found Kothamine l…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
OpenAI is preparing a $500 ChatGPT Pro Max plan with faster Codex Moderate BleepingComputer
2026-09-25 BleepingComputer

OpenAI is preparing a $500 ChatGPT Pro Max plan with faster Codex

OpenAI appears to be preparing a new ChatGPT Pro Max subscription that could cost $500 per month, but it's unclear when it'll begin rolling out. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
With the Rise of AI Agents, SOC 2 Should Adapt or Risk Irrelevance Moderate BleepingComputer
2026-09-25 BleepingComputer

With the Rise of AI Agents, SOC 2 Should Adapt or Risk Irrelevance

AI agents can operate through human credentials and take actions that existing SOC 2 controls may not distinguish from human activity. Token Security explains why SOC 2 needs to adapt to address the security gaps created by agent identities. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Stopping IT Worker Scams Requires Revamped HR Process Moderate Dark Reading
2026-09-25 Dark Reading

Stopping IT Worker Scams Requires Revamped HR Process

Training human-resource managers in the latest tactics and warning signs goes a long way toward blunting the threat, but automated analysis can help even more.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification