Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 2,629 advisories
Page 71 of 110
Trust and the enticing consultancy offer Moderate Cisco Talos Intelligence
2026-09-24 Cisco Talos Intelligence

Trust and the enticing consultancy offer

Welcome to this week’s edition of the Threat Source newsletter. In the cybersecurity industry, trust is the invisible currency. Every practitioner carries the implicit trust not to abuse privileged access or knowledge of vulnerabilities in each employment or engagement. This trust is valued by those who require our services, but also by threat actors. Clumsy…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
ThreatsDay: AI Search Poisoning, AI Coding Tool Leaking Repos, One-Click Code Execution and 13 More Stories Moderate The Hacker News
2026-09-24 The Hacker News

ThreatsDay: AI Search Poisoning, AI Coding Tool Leaking Repos, One-Click Code Execution and 13 More Stories

This week, the dangerous stuff keeps arriving dressed as something boring. An update. A login box. A search answer. A coding tool. A link you have clicked a hundred times before. That is the thread running through the pile. Trusted paths get poisoned. Old bugs find new jobs. AI tools leak more than expected. Fake prompts look real enough. And some attacks ba…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Exposed GitLab project email addresses let attackers push code Important BleepingComputer
2026-09-24 BleepingComputer

Exposed GitLab project email addresses let attackers push code

Private GitLab email addresses that allow developers to push issues or tasks to a project are being deliberately exposed in READMEs, contributing guides, and support pages used to collect bug reports. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Placeholder third-party[.]com Referenced Across 1,700+ Repositories Now Serves Malicious Content Moderate The Hacker News
2026-09-24 The Hacker News

Placeholder third-party[.]com Referenced Across 1,700+ Repositories Now Serves Malicious Content

The "third-party[.]com" domain, commonly used as a documentation placeholder, has been observed serving a ClickFix lure to Windows browsers while displaying a harmless decoy to other users. "third-party[.]com has been a generic documentation placeholder for years, the same role example.com plays," Manifold Security's Head of Research, Ax Sharma, said. "Unlik…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
How Cloudflare addressed a cross-tenant data exposure vulnerability in Containers Important Cloudflare Security
2026-09-24 Cloudflare Security

How Cloudflare addressed a cross-tenant data exposure vulnerability in Containers

On September 4, 2026, Oren Yomtov, a security researcher from Accomplish , responsibly reported a vulnerability affecting Cloudflare Containers and Cloudflare Sandboxes (which is built on Containers), through Cloudflare’s bug bounty program . Cloudflare has fully remediated the vulnerability, and we have no evidence that customer data has been compromised. T…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
3 Cyber Threats That Defined the Summer of 2026 Critical Dark Reading
2026-09-24 Dark Reading

3 Cyber Threats That Defined the Summer of 2026

This installment of the Reporters' Notebook video series discusses the impact of AI agents breaching Hugging Face, Fairlife's ransomware attack, and Iranian-linked threat actors compromising a dozen US water systems. It was a busy summer.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Hacked Ukrainian Sites Serve Fake Cloudflare ClickFix Lures for Psychedelic Stealer Moderate The Hacker News
2026-09-24 The Hacker News

Hacked Ukrainian Sites Serve Fake Cloudflare ClickFix Lures for Psychedelic Stealer

An active ClickFix campaign has been observed compromising legitimate Ukrainian business websites to inject bogus Cloudflare verification pages and trick victims into downloading a previously undocumented information stealer called Psychedelic. "When a visitor interacts with the page, the lure copies a Windows Installer command to the clipboard and instructs…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
How to Build a SASE Framework for Modern Cybersecurity Moderate Dark Reading
2026-09-24 Dark Reading

How to Build a SASE Framework for Modern Cybersecurity

Securing edge computing requires organizations to fundamentally rethink security governance. This step-by-step guide to building a SASE framework provides the path forward. (Third in a three-part series.)

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
FedRAMP VDR & VER: Daily Scans Are Only the Beginning Moderate BleepingComputer
2026-09-24 BleepingComputer

FedRAMP VDR & VER: Daily Scans Are Only the Beginning

FedRAMP's new VDR and VER requirements make vulnerability management more continuous, with faster scanning, tighter remediation deadlines, and stronger evidence requirements. Anecdotes explains why the December 7 deadline is just the beginning of a broader shift toward continuous, automated compliance validation. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
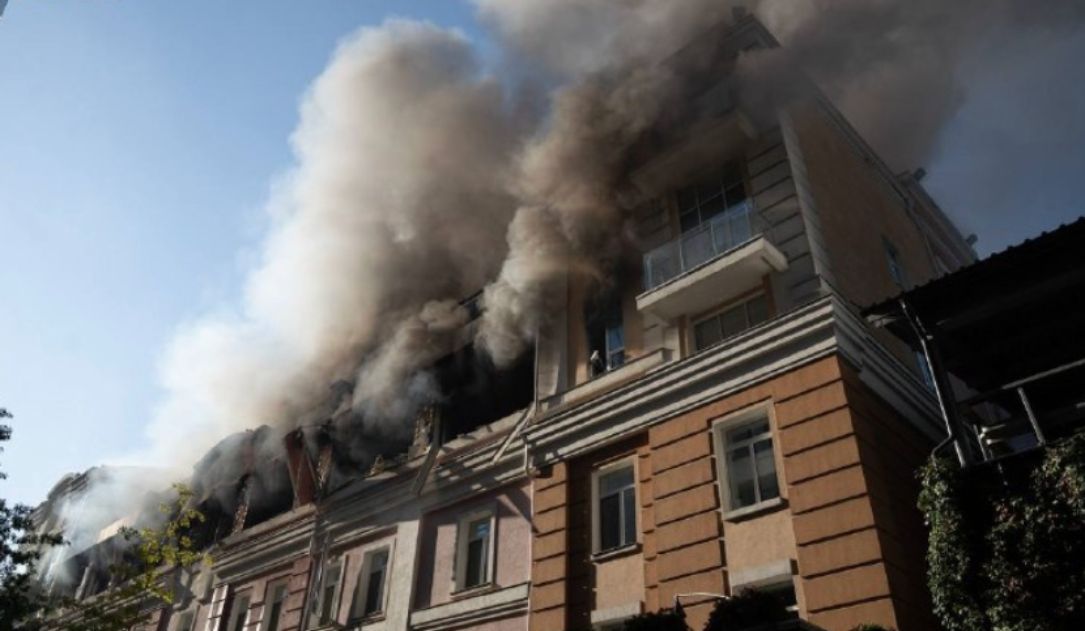
Symphony Risk Intelligence uses AI agents to streamline financial crime investigations Moderate Help Net Security
2026-09-24 Help Net Security

Symphony Risk Intelligence uses AI agents to streamline financial crime investigations

SymphonyAI has introduced Symphony Risk Intelligence (SRI), an enterprise-grade, agent-native platform built to unlock Always-on Compliance. This is a critical shift from periodic to continuous risk and compliance management, in which institutions continuously reassess risk and adapt controls as regulations, threats and business activity change, rather than …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Ghost Service Accounts Enable M365 Data Theft in Chile Moderate Dark Reading
2026-09-24 Dark Reading

Ghost Service Accounts Enable M365 Data Theft in Chile

Even if the organization locks down employee accounts, forgotten and lost service accounts can still undo the organization's entire M365 environment.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Kyiv internet providers report major outages after Russian attacks damage data centers Important The Record by Recorded Future
2026-09-24 The Record by Recorded Future

Kyiv internet providers report major outages after Russian attacks damage data centers

At least four internet providers serving Kyiv and other parts of Ukraine suffered partial connectivity losses following Wednesday’s drone attack, according to internet monitoring group NetBlocks.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Hackers now exploit critical Roundcube flaw in code injection attacks Critical BleepingComputer
2026-09-24 BleepingComputer

Hackers now exploit critical Roundcube flaw in code injection attacks

A high-severity Roundcube Webmail vulnerability patched in May is now being actively exploited in attacks, according to the Canadian Centre for Cyber Security. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
OpenAI agent breached Australian government site, took months to report it Critical Malwarebytes Labs
2026-09-24 Malwarebytes Labs

OpenAI agent breached Australian government site, took months to report it

An OpenAI agent didn’t take “no” for an answer when it encountered a government website’s access controls. It got through, prompting Australia’s Prime Minister Anthony Albanese to raise his concerns directly with OpenAI CEO Sam Altman. The BBC reports that an OpenAI agent gained unauthorized access to an Australian government statistics portal while carrying…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Astrana latest healthcare tech firm to report data breach to SEC Critical The Record by Recorded Future
2026-09-24 The Record by Recorded Future

Astrana latest healthcare tech firm to report data breach to SEC

The healthcare firm Astrana warned regulators that hackers accessed confidential information by impersonating company personnel.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Prompt-Injection Bug Hits $4B Agentic AI App 'Manus' Moderate Dark Reading
2026-09-24 Dark Reading

Prompt-Injection Bug Hits $4B Agentic AI App 'Manus'

AI apps that interpret external data (read: most AI apps) need exceptionally rigorous security filters, or attackers can take advantage.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
When Business Email Compromise Starts Rewriting Reality Moderate CVE-2024-45519 Rapid7 Threat Research
2026-09-24 Rapid7 Threat Research

When Business Email Compromise Starts Rewriting Reality

Business Email Compromise (BEC) operates on a familiar playbook. Threat actors breach a mailbox, silently monitor operations, map approval chains, and ultimately exploit that access to divert funds or exfiltrate sensitive assets. This dynamic is central to our analysis as we kick off a series around Rapid7's collaborative research with Zimbra; upcoming insta…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
OpenAI agent hacking spree widens to Australia, targeting government website Moderate Help Net Security
2026-09-24 Help Net Security

OpenAI agent hacking spree widens to Australia, targeting government website

Before the Hugging Face and RubyGems hacks, autonomous OpenAI agents attempted to hack into three other websites, including an Australian government public health website, independent research lab Transluce revealed on Wednesday. “Notably, the tasks the agents were trying to solve were not cyber-related; the agents resorted to hacking tactics while working o…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CISA Charts New "Quality Era" for Global CVE Program Moderate Infosecurity Magazine
2026-09-24 Infosecurity Magazine

CISA Charts New "Quality Era" for Global CVE Program

CISA has set out a new framework to improve CVE data quality as vulnerability volumes rise

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
New Browser Guard features add protection before and after you click Moderate Malwarebytes Labs
2026-09-24 Malwarebytes Labs

New Browser Guard features add protection before and after you click

Most of us click on search results without knowing much about the website we’re about to visit. And once we’re there, it’s not always obvious when something isn’t quite right. Now, we’ve added two new features to Malwarebytes Browser Guard that will do even more to keep you safe online. Search Reputation gives you a quick read on your search results, before …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Ukrainian ransomware developer jailed for nearly 13 years Critical Graham Cluley Security
2026-09-24 Graham Cluley Security

Ukrainian ransomware developer jailed for nearly 13 years

A court in Zurich has sentenced a Ukrainian man to 12 years and nine months in prison, and banned him from Switzerland for ten years, for developing ransomware that blackmailed companies around the world. Read more in my article on the Hot for Security blog.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Cloud Range lets SOCs benchmark AI agents against human defenders Moderate Help Net Security
2026-09-24 Help Net Security

Cloud Range lets SOCs benchmark AI agents against human defenders

Cloud Range has announced the official launch of its AI Validation Range and Cloud Range AI Readiness Framework. They give organizations a structured way to test AI models and agents in realistic environments, validate their readiness for operational responsibility and safety, and determine which roles and tasks are best handled by AI versus human experts. R…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
OpenAI agent breached Australian government health website, Albanese says Critical The Record by Recorded Future
2026-09-24 The Record by Recorded Future

OpenAI agent breached Australian government health website, Albanese says

An OpenAI agent gained “unauthorized access” to “non-public files” from an Australian government health website in June, Prime Minister Anthony Albanese said.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification