Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
How bug bounty sharpens one researcher’s security skills
Lead Cyber Advisory GitHub Security Blog Moderate

How bug bounty sharpens one researcher’s security skills

As Cybersecurity Awareness Month continues, the GitHub Bug Bounty team is excited to spotlight another top-performing security researcher from the GitHub Security Bug Bounty Program: @r31n ! As home to the world’s developers, GitHub is dedicated to the security and reliability of the code behind millions of projects, and our Bug Bounty Program remains a corn…

Vendor: GitHub Security Blog · Product: Open Source Supply Chain
View Advisory Details

Showing 15 of 15 advisories
Page 1 of 1
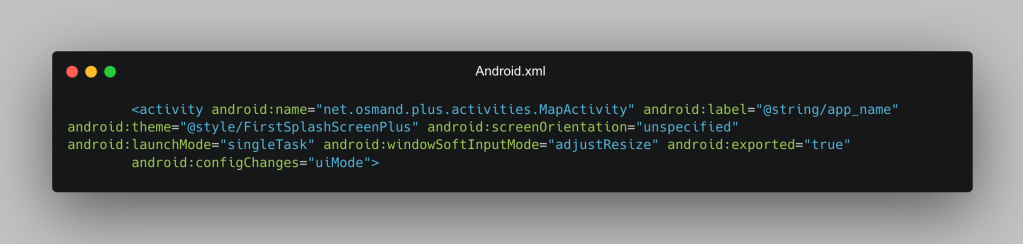
How we found 24 Android vulnerabilities using our open source AI security agent Critical GitHub Security Blog
2026-09-28 GitHub Security Blog

How we found 24 Android vulnerabilities using our open source AI security agent

With the rise of AI in the security space, our team created the GitHub Security Lab Taskflow Agent as a way for security researchers to easily automate, package, and share the AI prompts and workflows that they find effective for their work. In this blog post, I’ll share how I created auditing taskflows to find vulnerabilities in Android applications. While …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
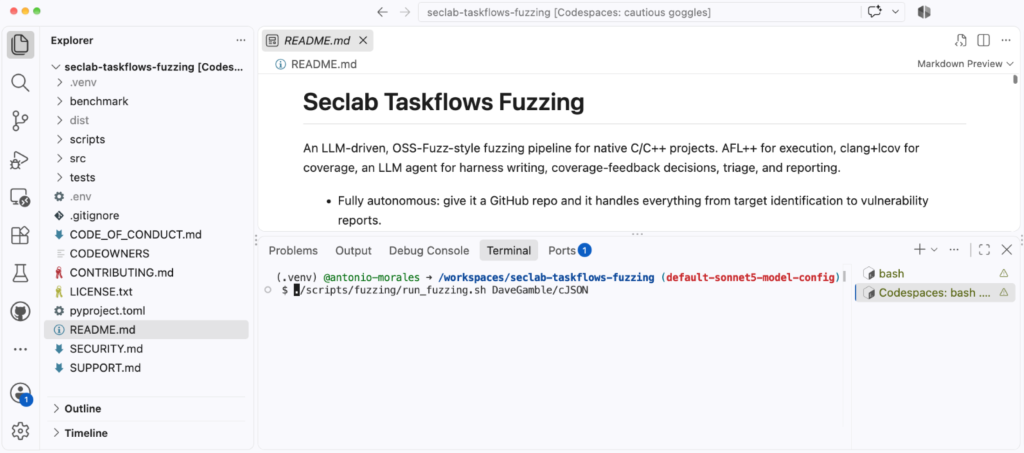
AI-powered fuzzing with the GitHub Security Lab Taskflow Agent Moderate GitHub Security Blog
2026-09-24 GitHub Security Blog

AI-powered fuzzing with the GitHub Security Lab Taskflow Agent

If you’re new to fuzzing and want to learn the fundamentals first, check out our Fuzzing 101 course at gh.io/fuzzing101 . Continuous fuzzing is not a magic solution that solves all your problems . Even projects that have been enrolled in OSS-Fuzz for years can still hide critical bugs, and the reason is almost always the same: someone needs to keep an eye on…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
OpenClaw went viral. Meet the maintainers building and securing it. Moderate GitHub Security Blog
2026-08-27 GitHub Security Blog

OpenClaw went viral. Meet the maintainers building and securing it.

What began as a personal experiment quickly became a global open source project with extraordinary momentum. OpenClaw is a personal AI assistant that runs on users’ devices and connects with the messaging channels they already use. Started by Peter Steinberger as a weekend project in November 2025, its GitHub repository has grown to approximately 388,000 sta…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
What 50 open source projects taught us about security in the AI era Critical GitHub Security Blog
2026-08-13 GitHub Security Blog

What 50 open source projects taught us about security in the AI era

AI is changing the pace of open source development and the security challenges that come with it. Maintainers are reviewing unfamiliar contributions, managing new attack surfaces, and responding to vulnerabilities with limited time and resources. Session 4 of the GitHub Secure Open Source Fund tested a practical response. The Secure Fund invested more than $…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
How we took malware advisories beyond npm Important GitHub Security Blog
2026-08-06 GitHub Security Blog

How we took malware advisories beyond npm

A compromised package can steal credentials the moment you install it, and until recently, GitHub could only flag those in npm. Not anymore. This is the story of how the supply chain engineering team behind Dependabot expanded malware advisories to eight ecosystems by building on OpenSSF’s shared malicious packages data. Here’s where things stand: earlier th…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Tame Dependabot: Group your updates, slow the cadence, keep security fast Moderate GitHub Security Blog
2026-07-29 GitHub Security Blog

Tame Dependabot: Group your updates, slow the cadence, keep security fast

If you maintain an active repository, you know the feeling. You open your notifications on a Monday morning and there they are: five, 10, sometimes a dozen Dependabot pull requests, each bumping a single dependency by a single patch version. Individually, every one of them is helpful. Collectively, they’re noise. And noise is how important updates get ignore…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Disrupting supply chain attacks on npm and GitHub Actions Important GitHub Security Blog
2026-07-28 GitHub Security Blog

Disrupting supply chain attacks on npm and GitHub Actions

In the past year, there’s been a pattern of supply chain attacks that target weaknesses in package repositories and CI/CD systems to quickly spread malware to hundreds of open source projects. This malware seeks to exfiltrate credentials both to broadly spread the attack, as well as for later exploitation. We’ve written a few times about our plans for harden…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The case for a cooldown: Why Dependabot now waits before issuing version updates Moderate GitHub Security Blog
2026-07-23 GitHub Security Blog

The case for a cooldown: Why Dependabot now waits before issuing version updates

In September 2025, an attacker phished the credentials of a single npm maintainer and published booby-trapped versions of chalk , debug , and around a dozen other packages that are together downloaded more than 2 billion times a week. The code rewrote cryptocurrency wallet addresses inside any browser app that loaded it. The poisoned versions were live for r…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Next chapter: Restructuring GitHub’s bug bounty program Moderate GitHub Security Blog
2026-07-22 GitHub Security Blog

Next chapter: Restructuring GitHub’s bug bounty program

The security research community makes GitHub safer for everyone. That’s the simple idea behind our bug bounty program. For more than a decade, researchers from around the world have helped us find and fix vulnerabilities before they could be exploited, and we’ve worked hard to be a program worth their time. Today, we’re sharing some meaningful changes to how…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
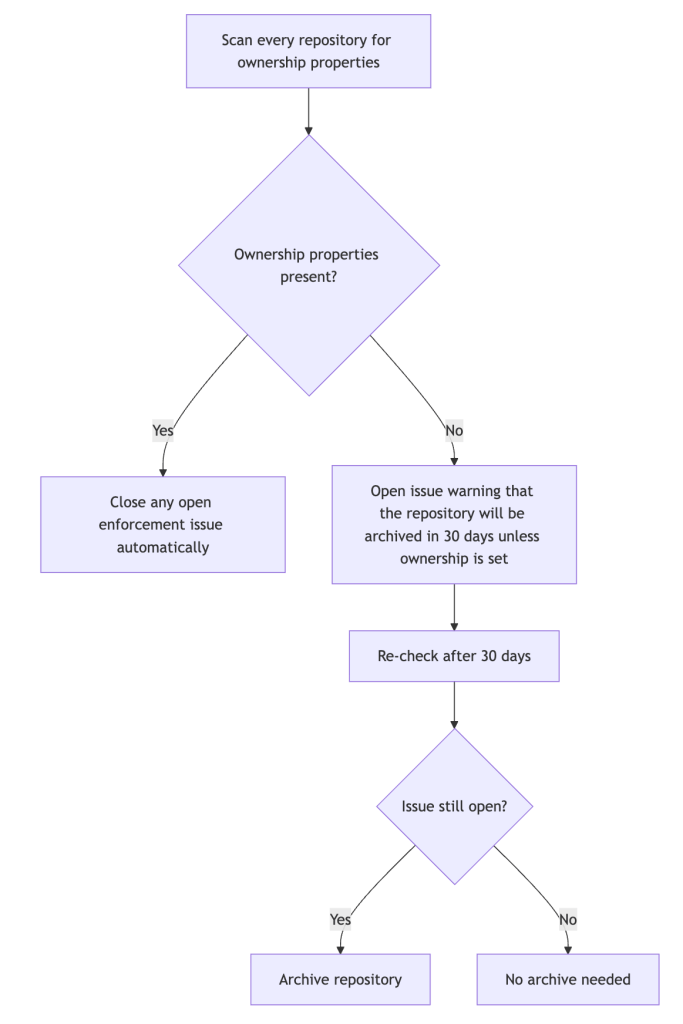
How GitHub gave every repository a durable owner Moderate GitHub Security Blog
2026-07-09 GitHub Security Blog

How GitHub gave every repository a durable owner

GitHub has over 14,000 repositories across our primary internal GitHub organization. As of early 2025, there were over 11,000 non-archived repositories, the vast majority of which with no clear owner. For repositories attached to production services, we have historically had robust durable ownership, but for repositories with no associated service, there was…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
How GitHub used secret scanning to reach inbox zero Moderate GitHub Security Blog
2026-07-02 GitHub Security Blog

How GitHub used secret scanning to reach inbox zero

Several years ago, GitHub Security launched an initiative to assess and improve our overall secrets hygiene. As part of that effort, we piloted the Secret Scanning capability that was under development at the time. That’s when we found more than 20,000 secrets spread across our 15,000+ repositories. The number was significantly higher than we anticipated, bu…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
6 security settings every GitHub maintainer should enable this week Moderate GitHub Security Blog
2026-07-01 GitHub Security Blog

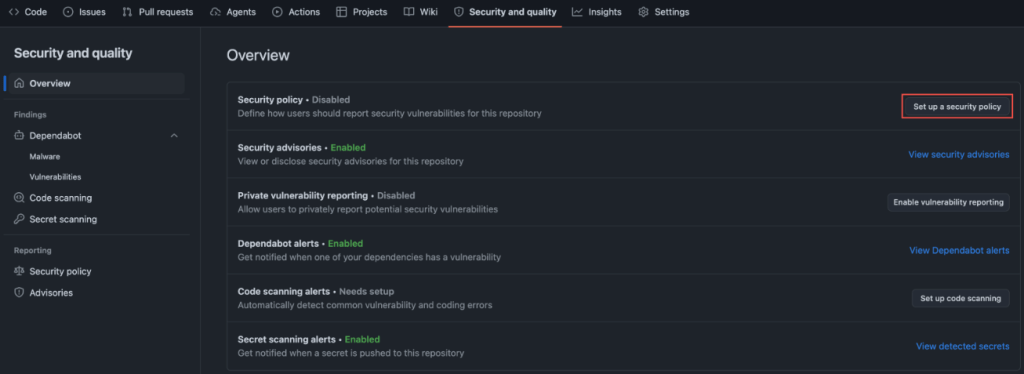
6 security settings every GitHub maintainer should enable this week

At GitHub Security Lab, we spend a lot of our week talking to maintainers. Some find the settings page dense and the docs sprawl. Most maintainers we talk to weren’t hired to be security engineers. While this is true, ignoring a project’s security settings completely will lead into leaving a lot in the table in terms of automation and scalability, leading in…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification