Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Operationalizing CISA AA26-194A: Automating Cisco Router Security Assessments with Qualys Policy Audit
Lead Cyber Advisory CVE-2018-0171 Moderate

Operationalizing CISA AA26-194A: Automating Cisco Router Security Assessments with Qualys Policy Audit

Key Takeaways CISA AA26-194A provides actionable guidance to improve the security of Internet-facing Cisco routers against real-world attack techniques. The advisory focuses on configuration hardening and security hygiene, rather than a single vulnerability or CVE. Manually validating advisory recommendations across enterprise networks is difficult, time-con…

Vendor: Qualys Security Blog · Product: Vulnerability Research & Audits
View Advisory Details
Showing 24 of 31 advisories
Page 1 of 2
How to Identify Compromised eMudhra Certificates With Qualys (CVE-2026-111943) Critical CVE-2026-111943 Qualys Security Blog
2026-10-24 Qualys Security Blog

How to Identify Compromised eMudhra Certificates With Qualys (CVE-2026-111943)

Executive Summary A critical certificate authority incident disclosed on October 17, 2026, impacts eight eMudhra intermediate CA certificates. A flaw in the key generation process could allow attackers to recover private keys and issue fraudulent TLS or code-signing certificates. The affected intermediates have been revoked and blocked by major platform vend…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Node.js Patches Brotli Remote Code Execution Flaw: Find Vulnerable Runtimes Before Attackers Do Critical CVE-2026-111497 Qualys Security Blog
2026-10-23 Qualys Security Blog

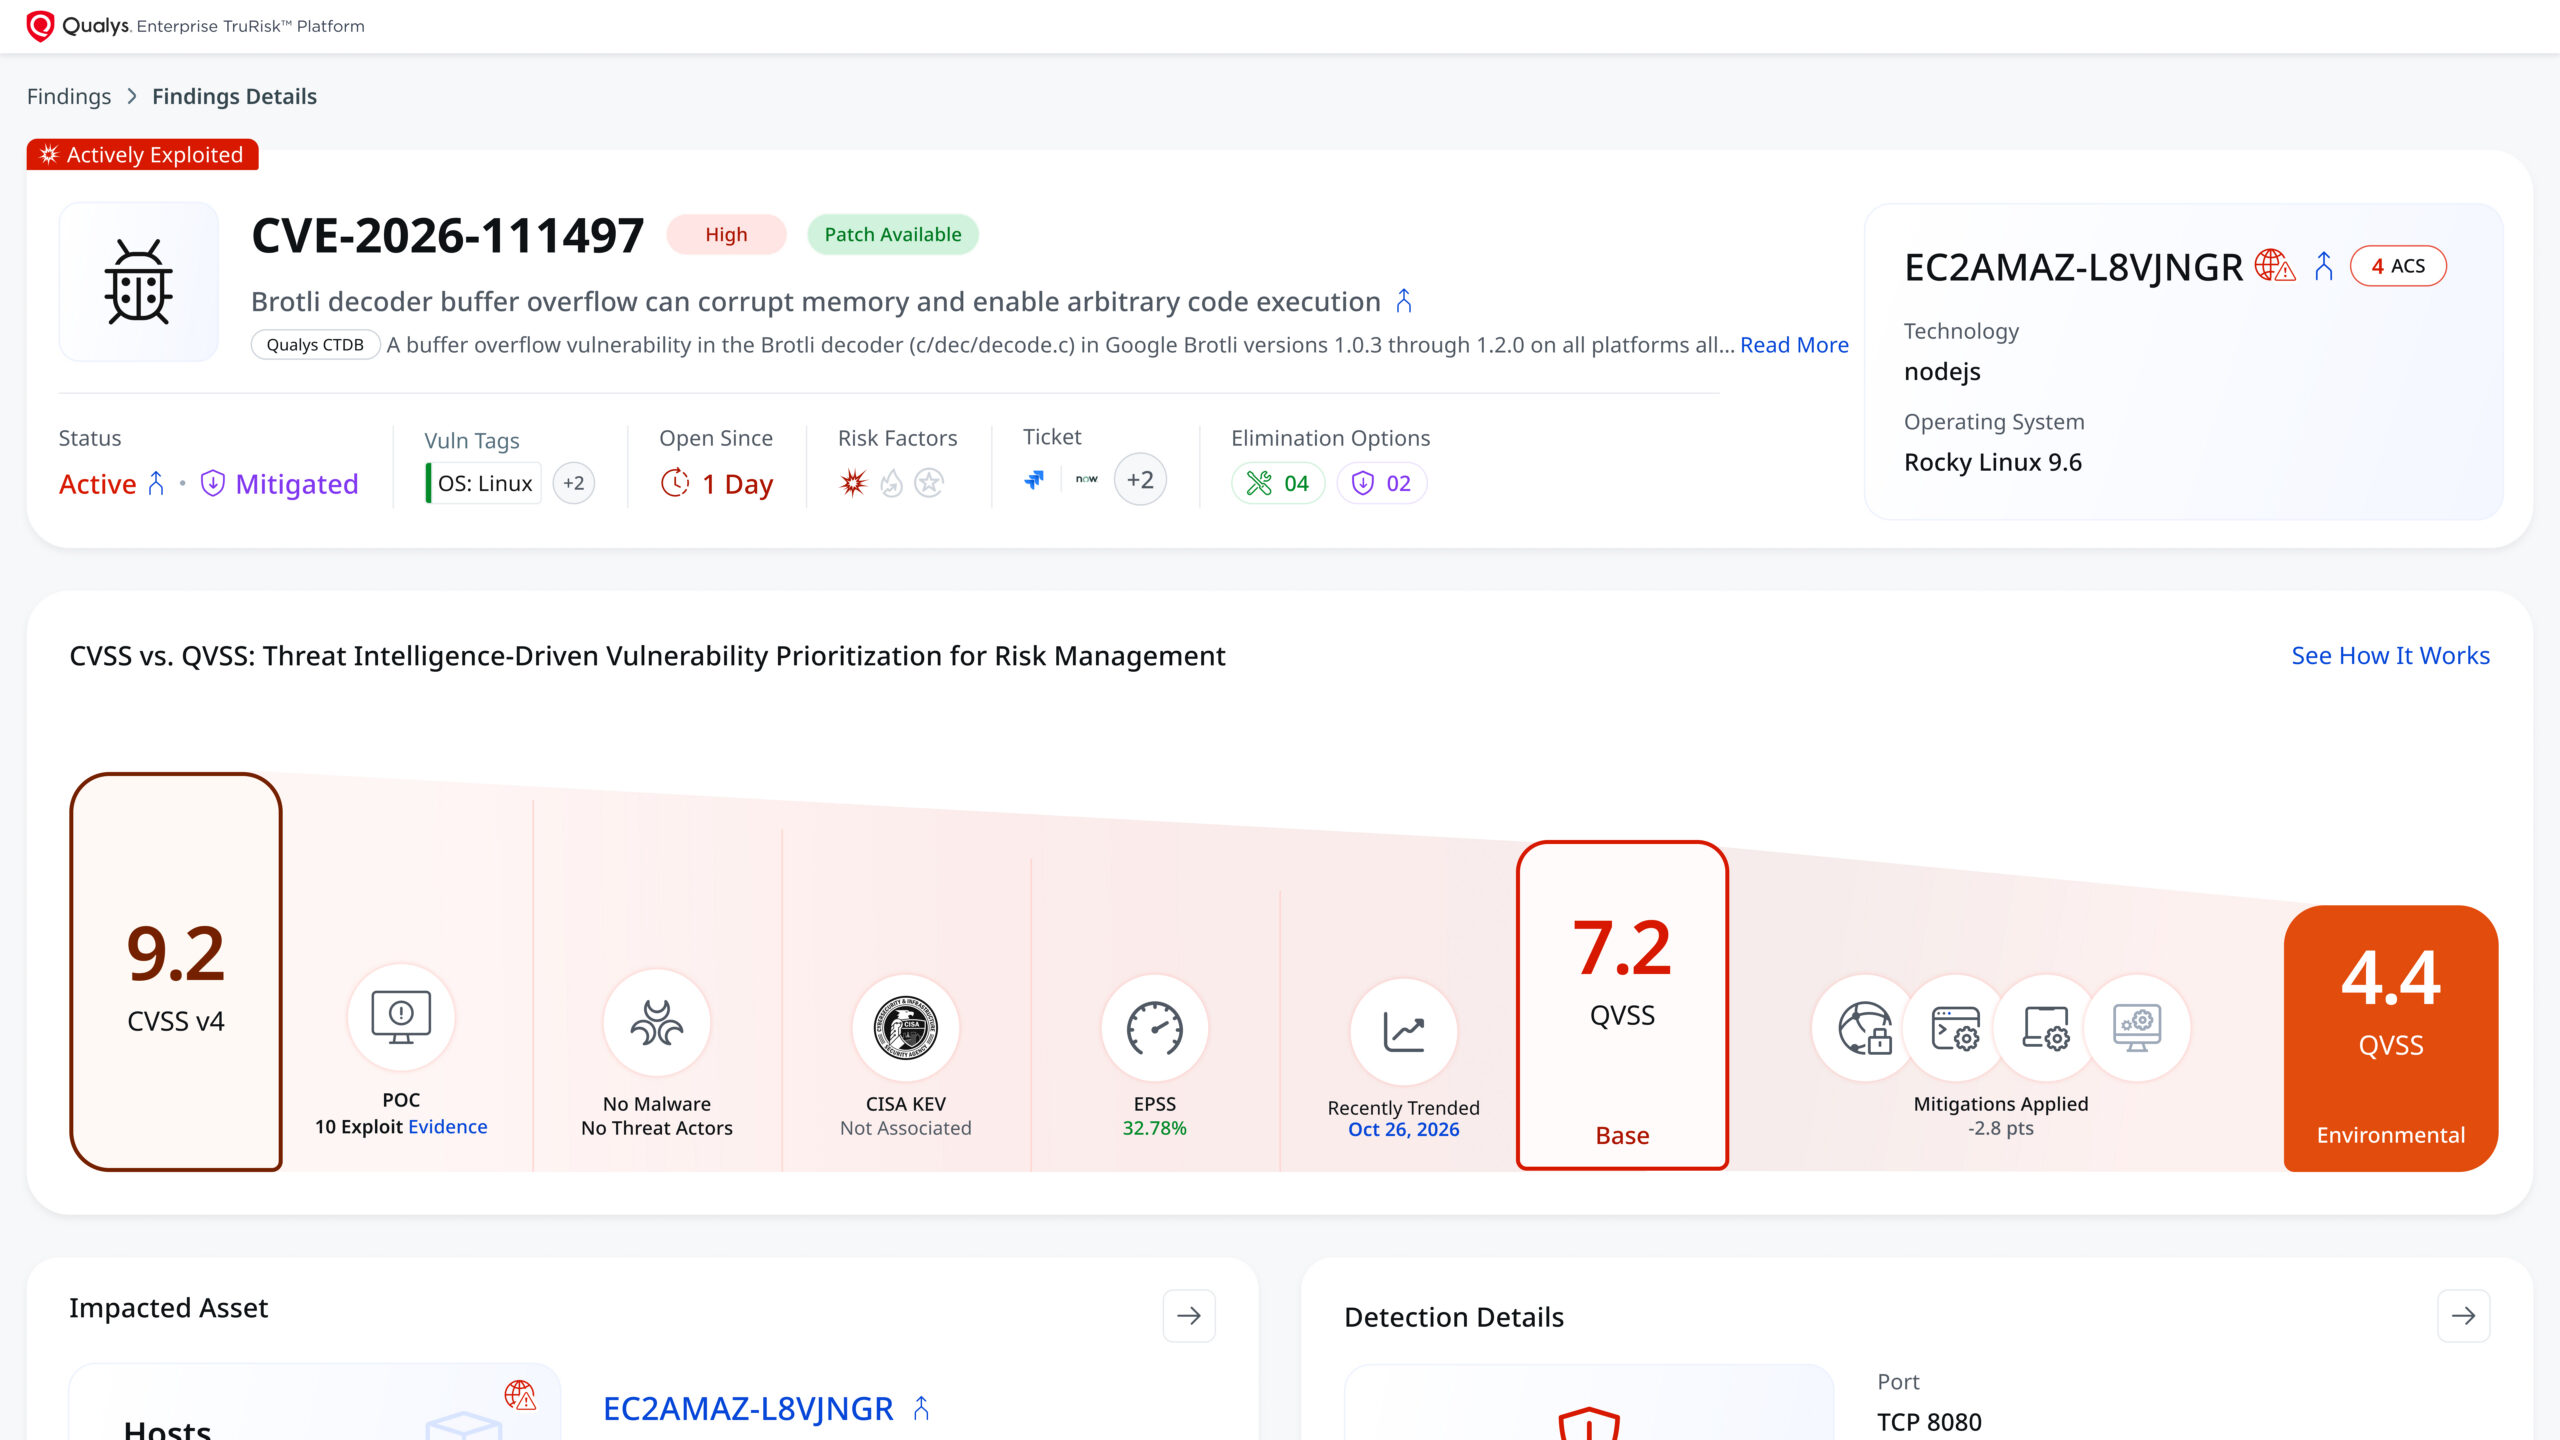
Node.js Patches Brotli Remote Code Execution Flaw: Find Vulnerable Runtimes Before Attackers Do

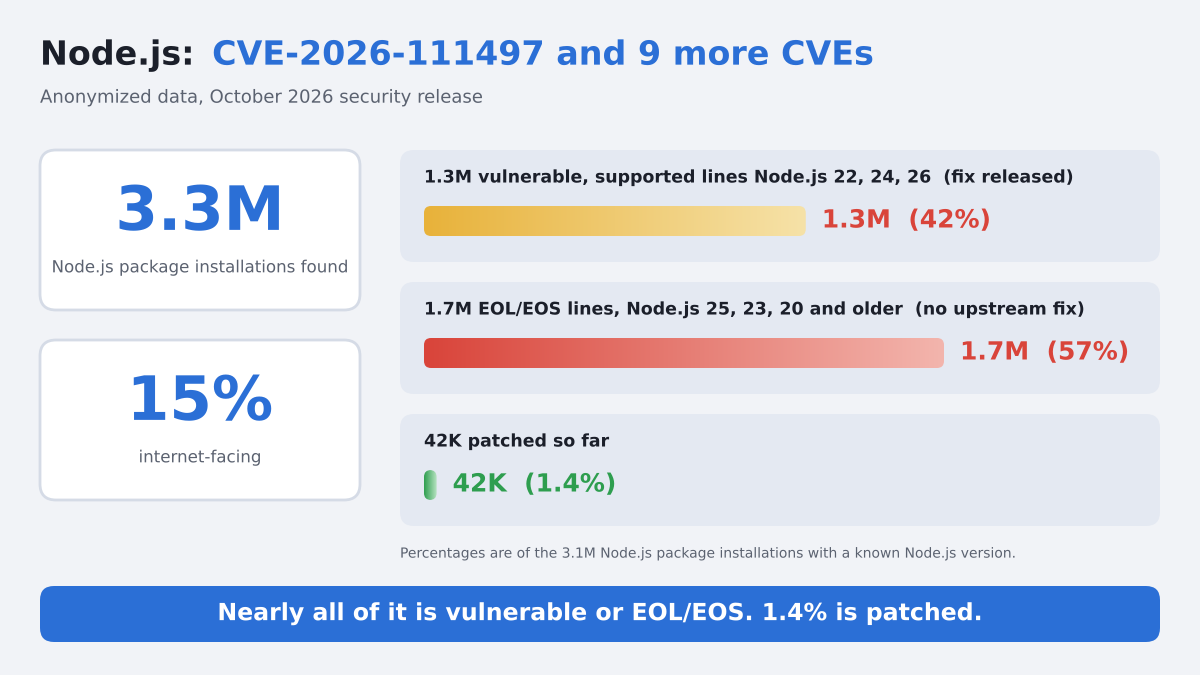
Executive Summary On October 21, 2026, Node.js released fixes for 10 vulnerabilities across its three supported release lines: 22.x, 24.x, and 26.x. Four are rated High. The most severe, CVE-2026-111497, is an out-of-bounds write in the bundled Brotli decoder that Node.js says permits remote code execution. These flaws live in the Node.js runtime itself, not…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The Science of Exploitability: Decoding BlueHammer Important CVE-2026-33825 Qualys Security Blog
2026-10-21 Qualys Security Blog

The Science of Exploitability: Decoding BlueHammer

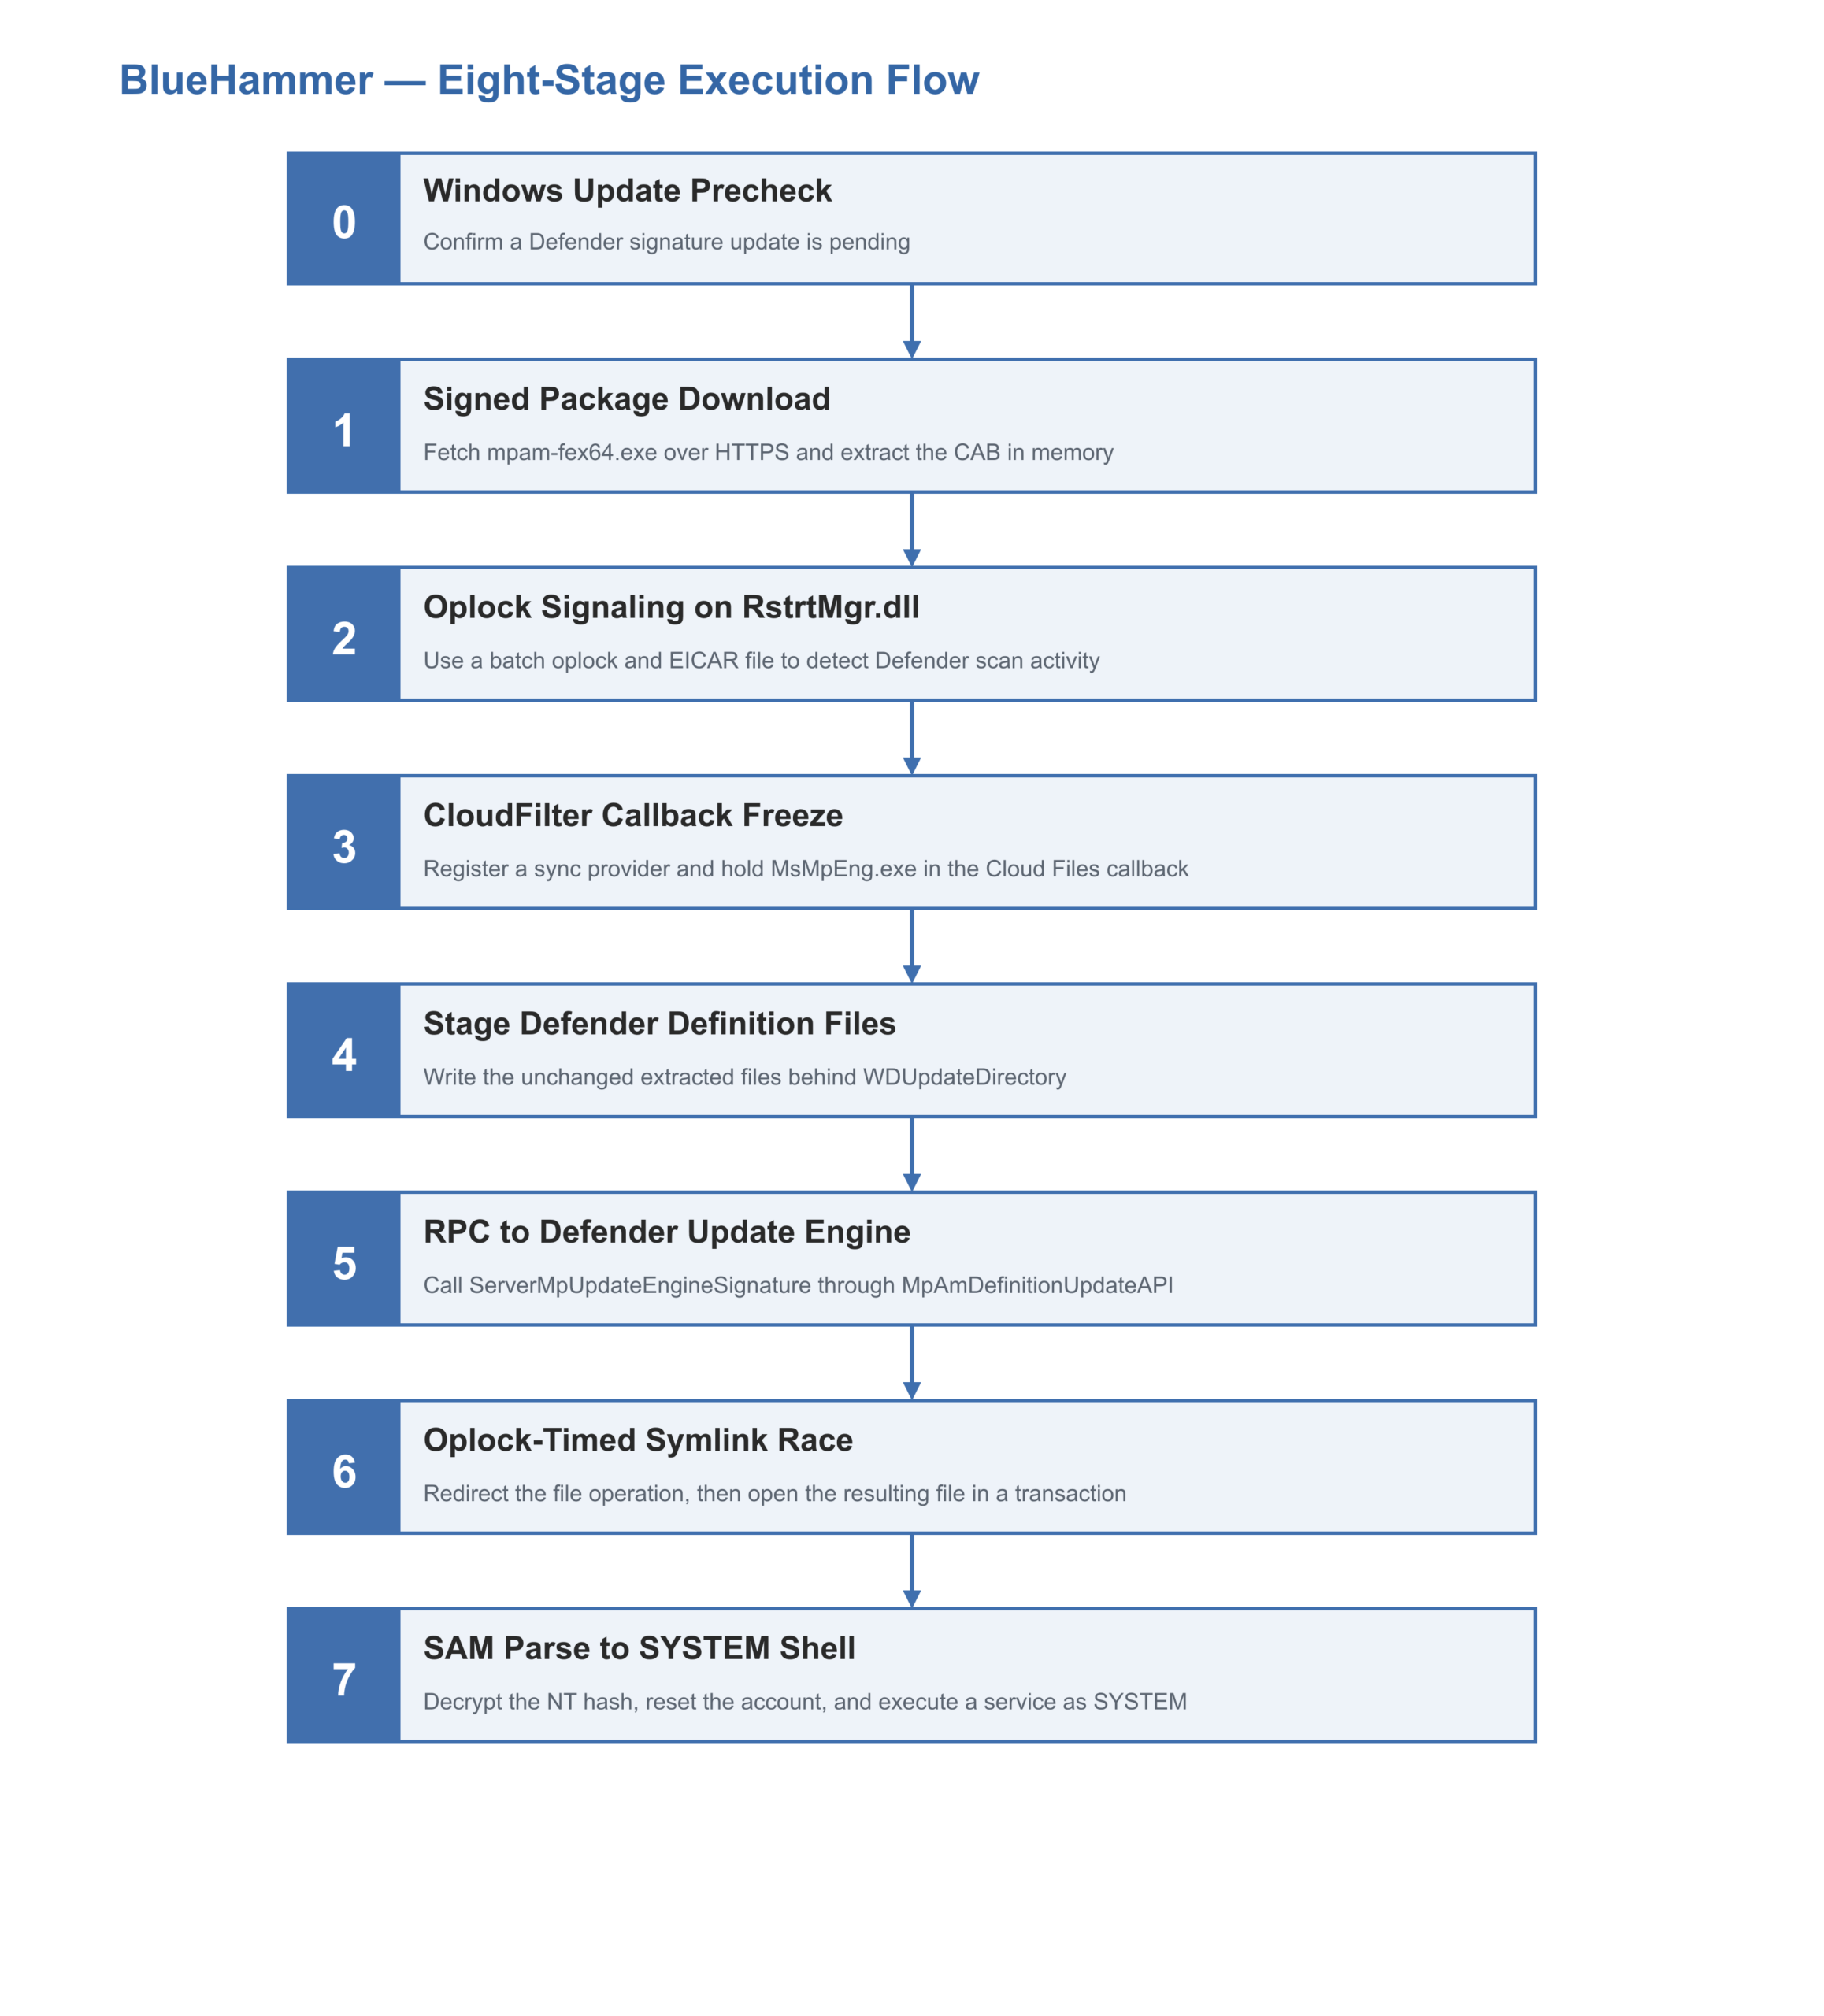
Executive Summary BlueHammer (CVE-2026-33825) is an eight-stage local privilege-escalation chain targeting the Windows Defender Antimalware Platform before 4.18.26030.3011. It does not grant initial access; an attacker needs standard-user code execution first. Still, in the lab, it reached NT AUTHORITY\SYSTEM, recovered domain-admin credentials from LSASS, a…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Two Critical PHP Flaws Could Hand Attackers Your Web Servers. Here’s How to Find, Mitigate, and Patch PHP2Shell Now Critical CVE-2026-109618 Qualys Security Blog
2026-10-21 Qualys Security Blog

Two Critical PHP Flaws Could Hand Attackers Your Web Servers. Here’s How to Find, Mitigate, and Patch PHP2Shell Now

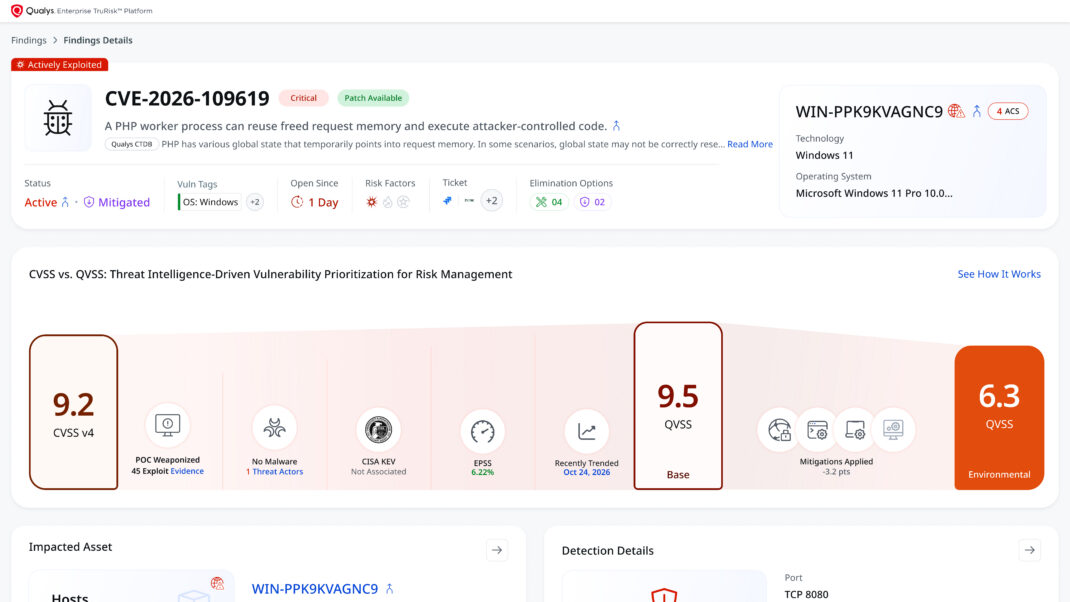
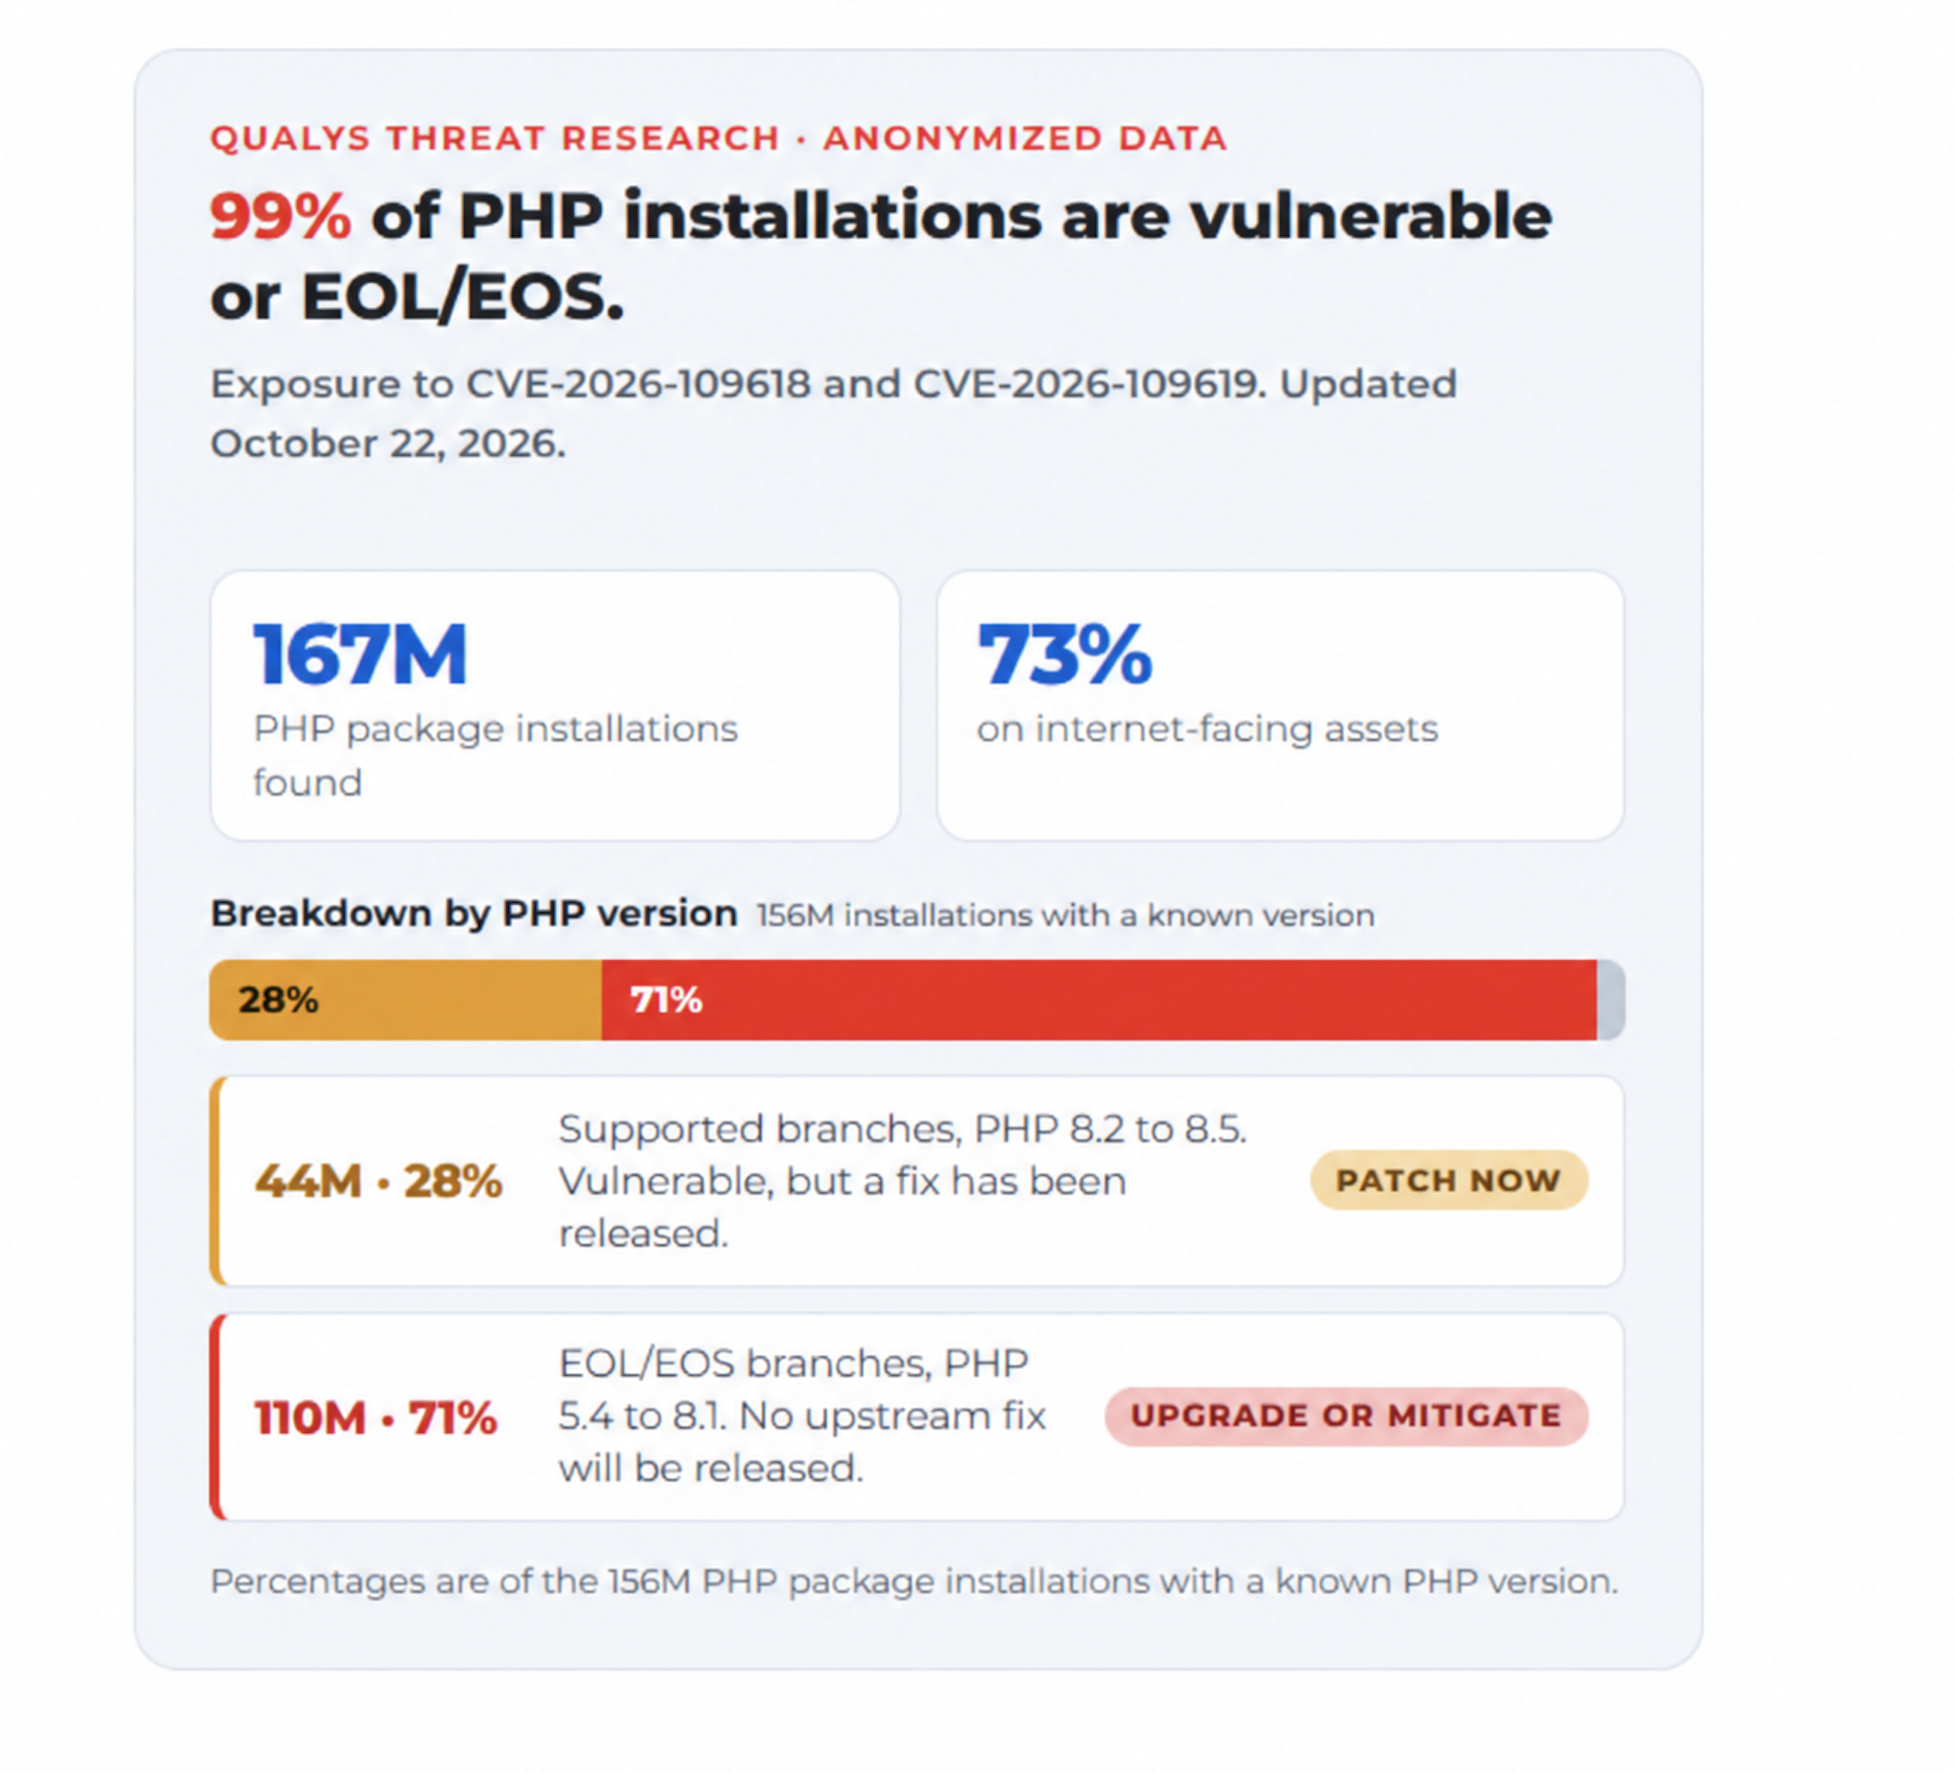
Executive Summary PHP2Shell refers to two critical vulnerabilities (CVE-2026-109618 and CVE-2026-109619), each with a CVSS v4.0 score of 9.2, that can allow unauthenticated remote code execution on PHP installations serving web requests. Researchers have also demonstrated unauthenticated disclosure of PHP worker memory, which can expose passwords, authentica…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The Real Jump Scare Isn’t the Attacker; It’s The Vulnerabilities You’re Focusing On Critical Qualys Security Blog
2026-10-20 Qualys Security Blog

The Real Jump Scare Isn’t the Attacker; It’s The Vulnerabilities You’re Focusing On

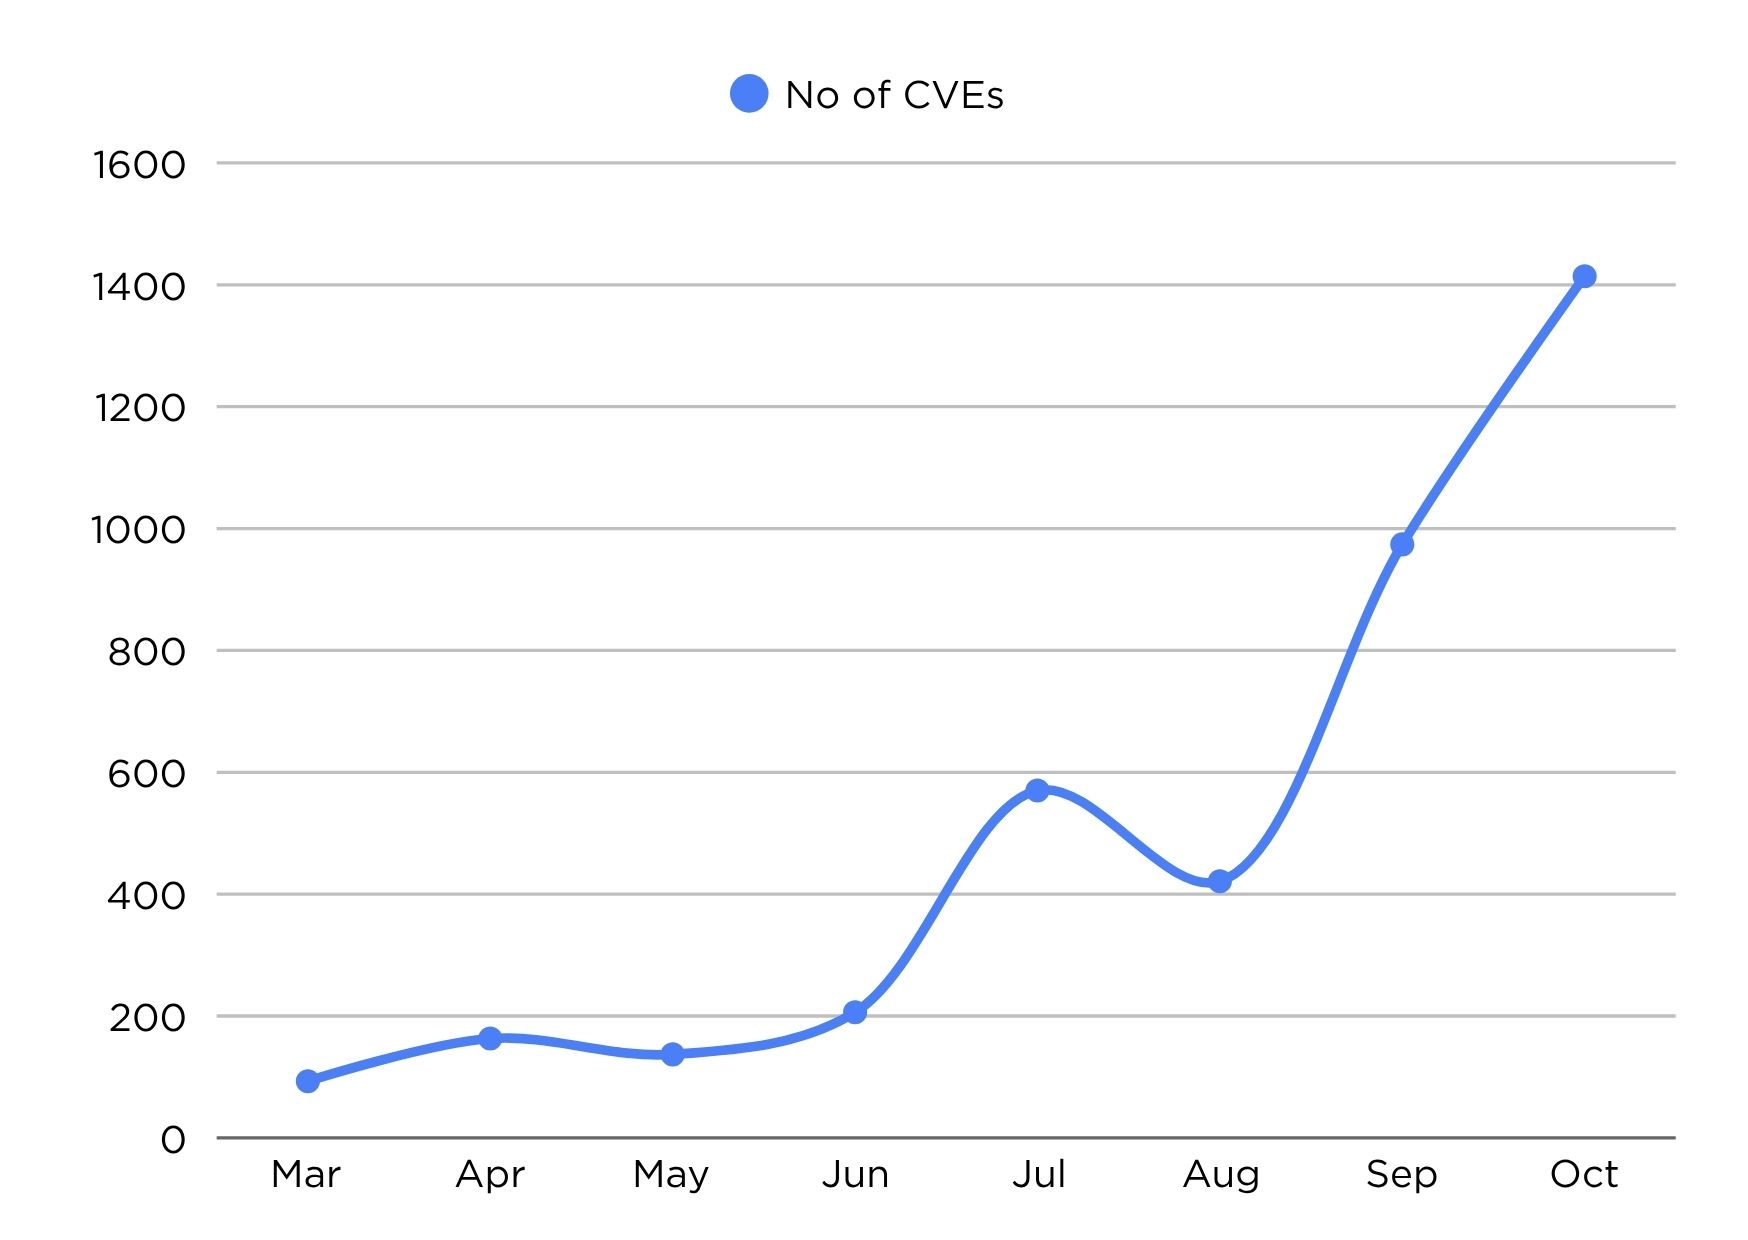
Key Takeaways Teams are remediating more than ever, but exposure from the vulnerabilities that matter is still rising faster than they can keep up with. Mean time to exploitation is about −7 days. Mean time to remediate sits around +30 days. Qualys research: closures rose from 73M (2022) to 473M (2025) – 6× – while critical findings still open at day seven r…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
TruConfidence: Why Your Patch Automation Can Finally Be Autonomous Critical Qualys Security Blog
2026-10-14 Qualys Security Blog

TruConfidence: Why Your Patch Automation Can Finally Be Autonomous

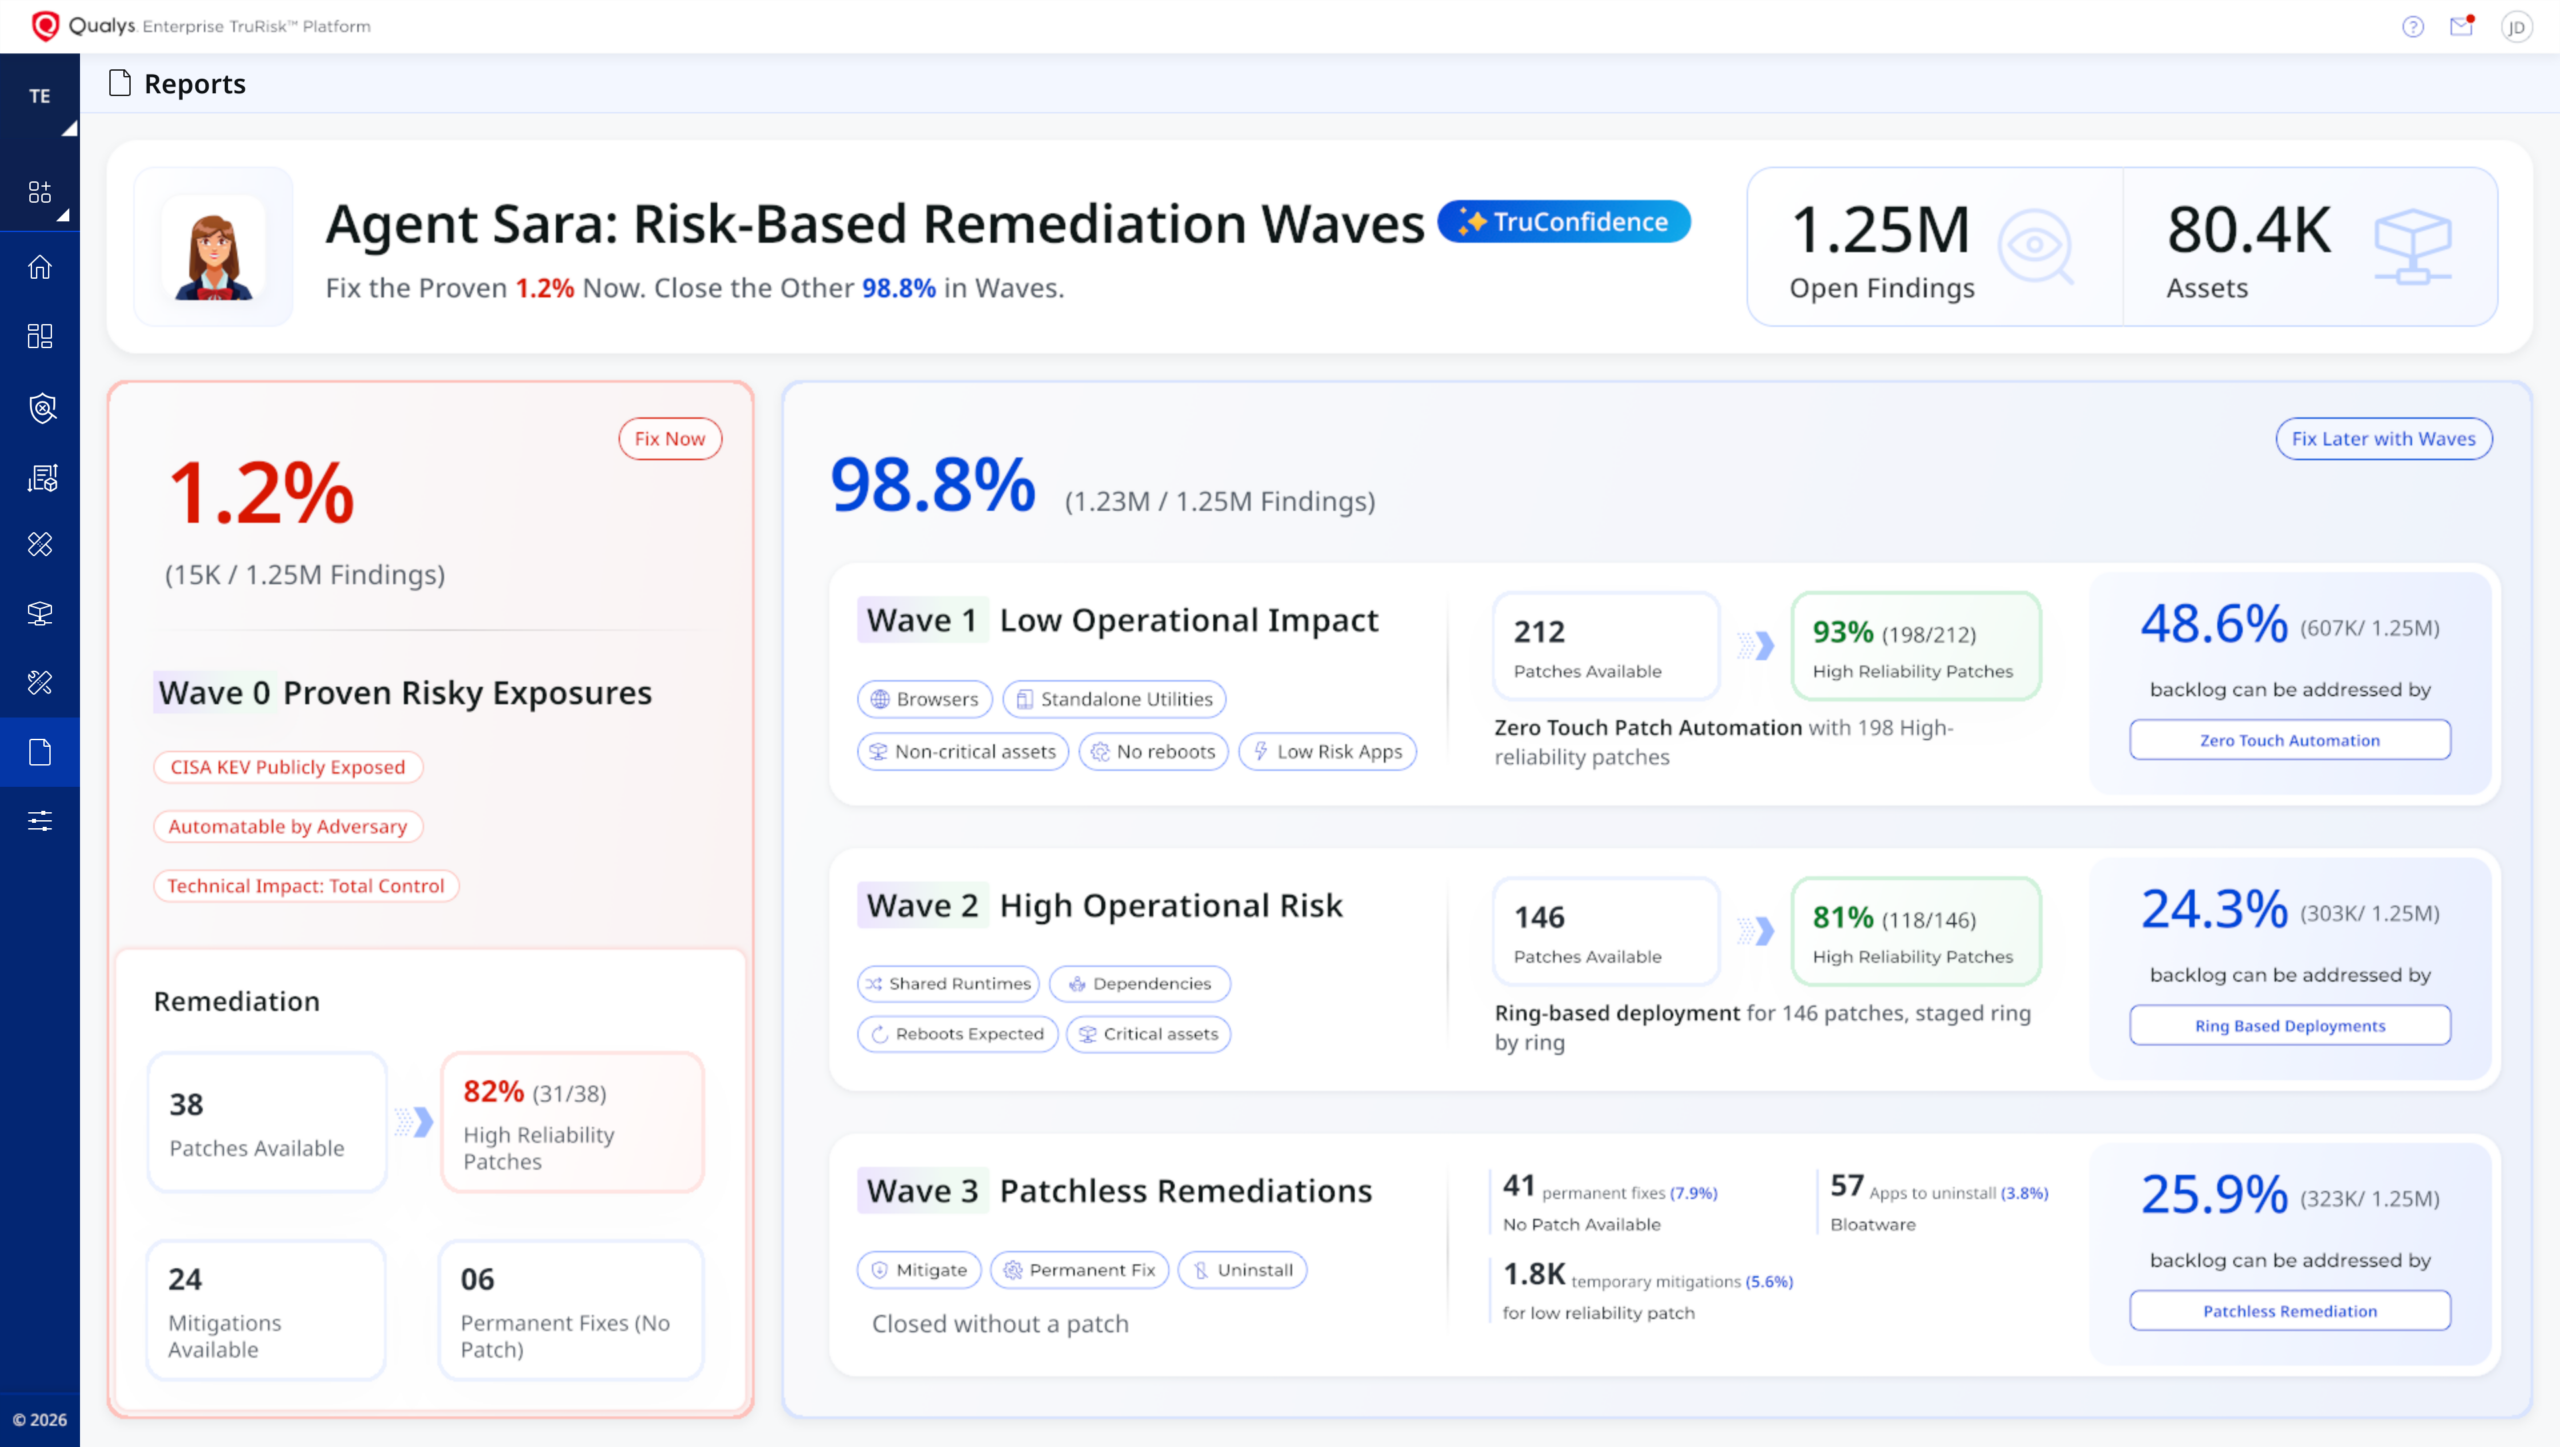
TruConfidence: The AI-Powered Remediation Intelligence & Orchestration engine powering TruRisk Eliminate 2.0 delivers autonomous remediation at scale with proof at every step. Executive Summary Vulnerabilities are now discovered faster than enterprises can remediate them. Patch automation has been around for years, but vulnerability backlogs are still growin…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft Patch Tuesday, October 2026 Security Update Review Critical CVE-2026-96951 Qualys Security Blog
2026-10-13 Qualys Security Blog

Microsoft Patch Tuesday, October 2026 Security Update Review

Microsoft has released its October 2026 Patch Tuesday security updates, addressing vulnerabilities across its products and services. As organizations continue to navigate an evolving threat landscape, applying security patches promptly remains critical to reducing exposure and strengthening security posture. This month’s updates highlight the importance of i…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Exploitability Needs Runtime Evidence: Understanding Runtime Vulnerability Reachability for Containers Important Qualys Security Blog
2026-10-12 Qualys Security Blog

Exploitability Needs Runtime Evidence: Understanding Runtime Vulnerability Reachability for Containers

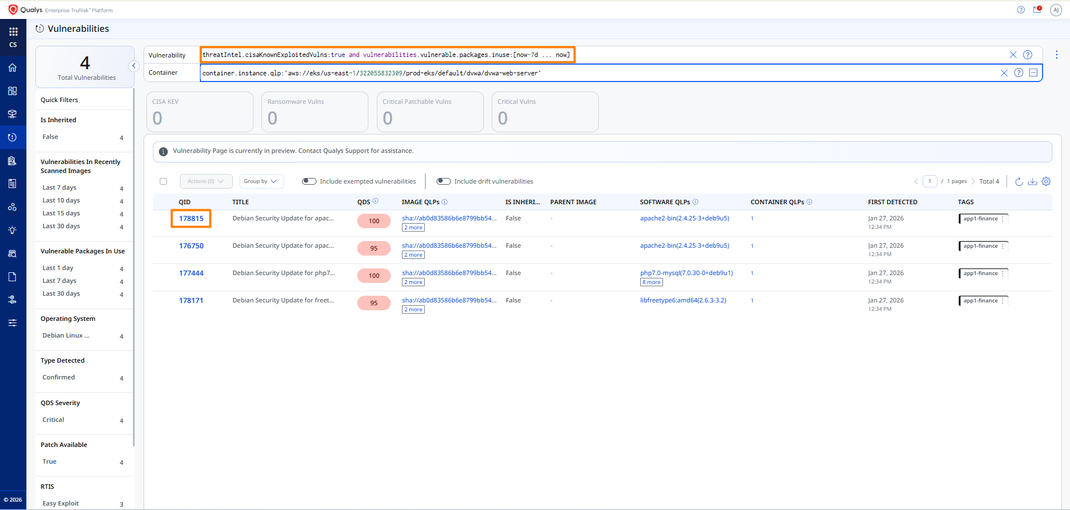
Key Takeaways Qualys Runtime Vulnerability Reachability for Containers brings runtime evidence directly into vulnerability prioritization. Package presence in a container image does not mean the vulnerable software is actually part of the workload’s live execution. Runtime reachability answers whether the vulnerable software is relevant to a running workload…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Secure Your Mission-Critical Application Estate: Qualys TotalAppSec is Now FedRAMP High Authorized (FedRAMP Certified Class D) Critical Qualys Security Blog
2026-10-05 Qualys Security Blog

Secure Your Mission-Critical Application Estate: Qualys TotalAppSec is Now FedRAMP High Authorized (FedRAMP Certified Class D)

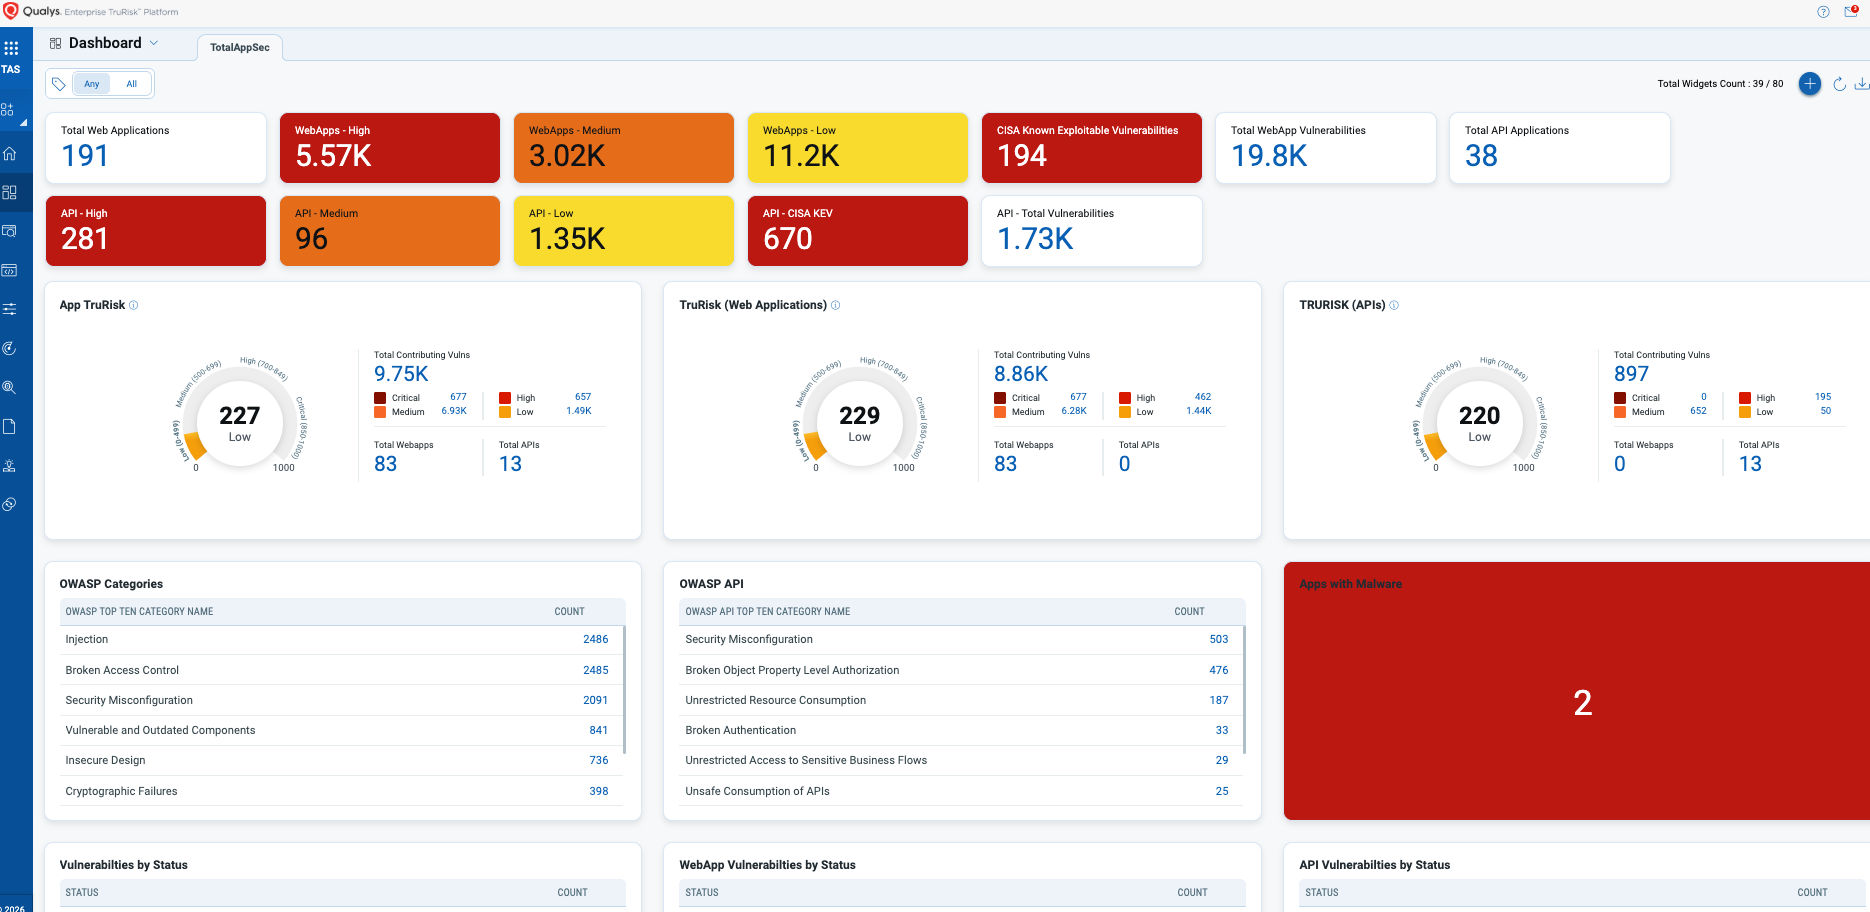
Key Takeaways Qualys TotalAppSec is now FedRAMP High Authorized on the Qualys Government Platform (FedRAMP Certified Class D, package FR2231052341). Federal AI use cases more than doubled in a year (3,611 use cases across 56 agencies), and most AI interactions are delivered through APIs; expanding an estate traditional IP-based inventory was never designed t…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Autonomous Remediation Is Already Running at Enterprise Scale Moderate Qualys Security Blog
2026-09-29 Qualys Security Blog

Autonomous Remediation Is Already Running at Enterprise Scale

The following is a guest blog by ITSPmagazine, based on their interview of Qualys President & CEO Sumedh Thakar at Black Hat USA 2026. Sumedh Thakar has watched the same clock compress for 23 years. He joined Qualys as an early software engineer on the scanner, when organizations scanned once every 90 days and gave themselves another 90 days to fix what turn…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Lessons from Microsoft Patch KB5002907: Two Layers of Patch Control in Qualys TruRisk Eliminate Moderate Qualys Security Blog
2026-09-29 Qualys Security Blog

Lessons from Microsoft Patch KB5002907: Two Layers of Patch Control in Qualys TruRisk Eliminate

How reliability scoring keeps risky patches out of zero-touch jobs, and how one blocking rule stops a paused update across your environment. Executive Summary Microsoft has paused the rollout of KB5002907, an optional Microsoft 365 Apps update that left some Office 2016 and Office 2019 installations unlicensed or removed. When an update runs into trouble aft…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
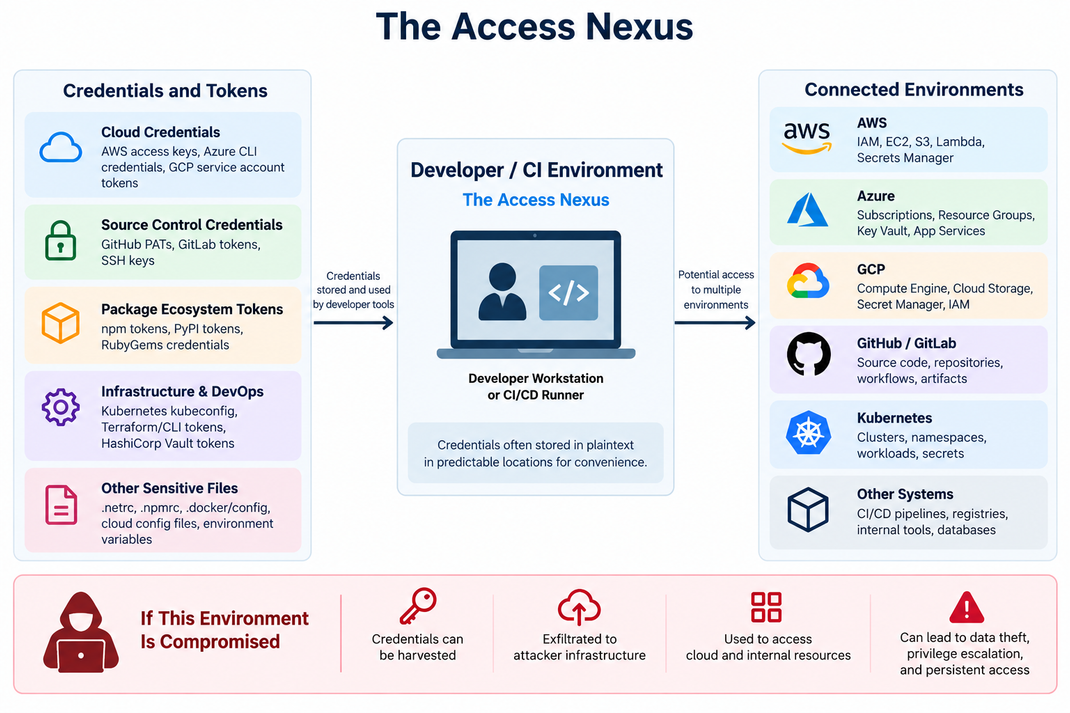
The Developer is the New Perimeter: How Supply Chain Attacks Are Becoming Cloud Breaches Critical Qualys Security Blog
2026-09-28 Qualys Security Blog

The Developer is the New Perimeter: How Supply Chain Attacks Are Becoming Cloud Breaches

Key Takeaways Malicious packages can steal cloud credentials during installation, before applications run. Stolen credentials turn developer workstations and CI/CD pipelines into gateways to cloud resources. Restrict installation scripts, minimize credential privileges, protect metadata access, and monitor cloud activity. Containment requires revoking expose…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CISA BOD 26-04 Timelines for Three Linux Kernel CVEs Critical CVE-2025-39682 Qualys Security Blog
2026-09-23 Qualys Security Blog

CISA BOD 26-04 Timelines for Three Linux Kernel CVEs

Executive Summary CISA added three actively exploited Linux kernel vulnerabilities: CVE-2025-39682, CVE-2026-53266, and CVE-2025-39964 to its KEV Catalog on September 18, 2026, triggering a 3-day remediation deadline that passed on September 21. Under CISA BOD 26-04, a 3-day window applies to CVE-2025-39682 across all assets, and for the other two, the deadl…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The End of Point-in-Time Compliance: Why Continuous Audit Readiness Matters to You in the AI Era Moderate Qualys Security Blog
2026-09-17 Qualys Security Blog

The End of Point-in-Time Compliance: Why Continuous Audit Readiness Matters to You in the AI Era

Key Takeaways Periodic audits provide a point-in-time assessment, but they cannot demonstrate whether controls remain effective between audit cycles. Qualys platform data shows 10.5 billion configuration findings across customer environments but only 1.6% represent meaningful exposure and under 1% are prioritized, business-critical findings. Verizon’s 2026 D…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The Autonomous Engine Behind Remediation, and What Finally Makes It Safe Moderate Qualys Security Blog
2026-09-17 Qualys Security Blog

The Autonomous Engine Behind Remediation, and What Finally Makes It Safe

Executive Summary Vulnerability exploitation now happens at a speed that manual, ticket-based remediation can’t match. Qualys’s Enterprise TruRisk Management Platform closes that gap with autonomous remediation: exposures are prioritized by threat, business, and environmental context, then validated by TruConfirm and Agent Val before any resource is committe…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Oracle Critical Security Patch Update, September 2026 Review Critical CVE-2026-83327 Qualys Security Blog
2026-09-16 Qualys Security Blog

Oracle Critical Security Patch Update, September 2026 Review

Oracle released its September edition of Critical Security Patch Update. The update received patches for 673 security vulnerabilities. Some of the vulnerabilities addressed in this update impact more than one product. These patches address vulnerabilities in various product families, including third-party components in Oracle products. Out of the 673 securit…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Before You Patch. Why Patch Reliability Matters for Confident Deployment Moderate Qualys Security Blog
2026-09-15 Qualys Security Blog

Before You Patch. Why Patch Reliability Matters for Confident Deployment

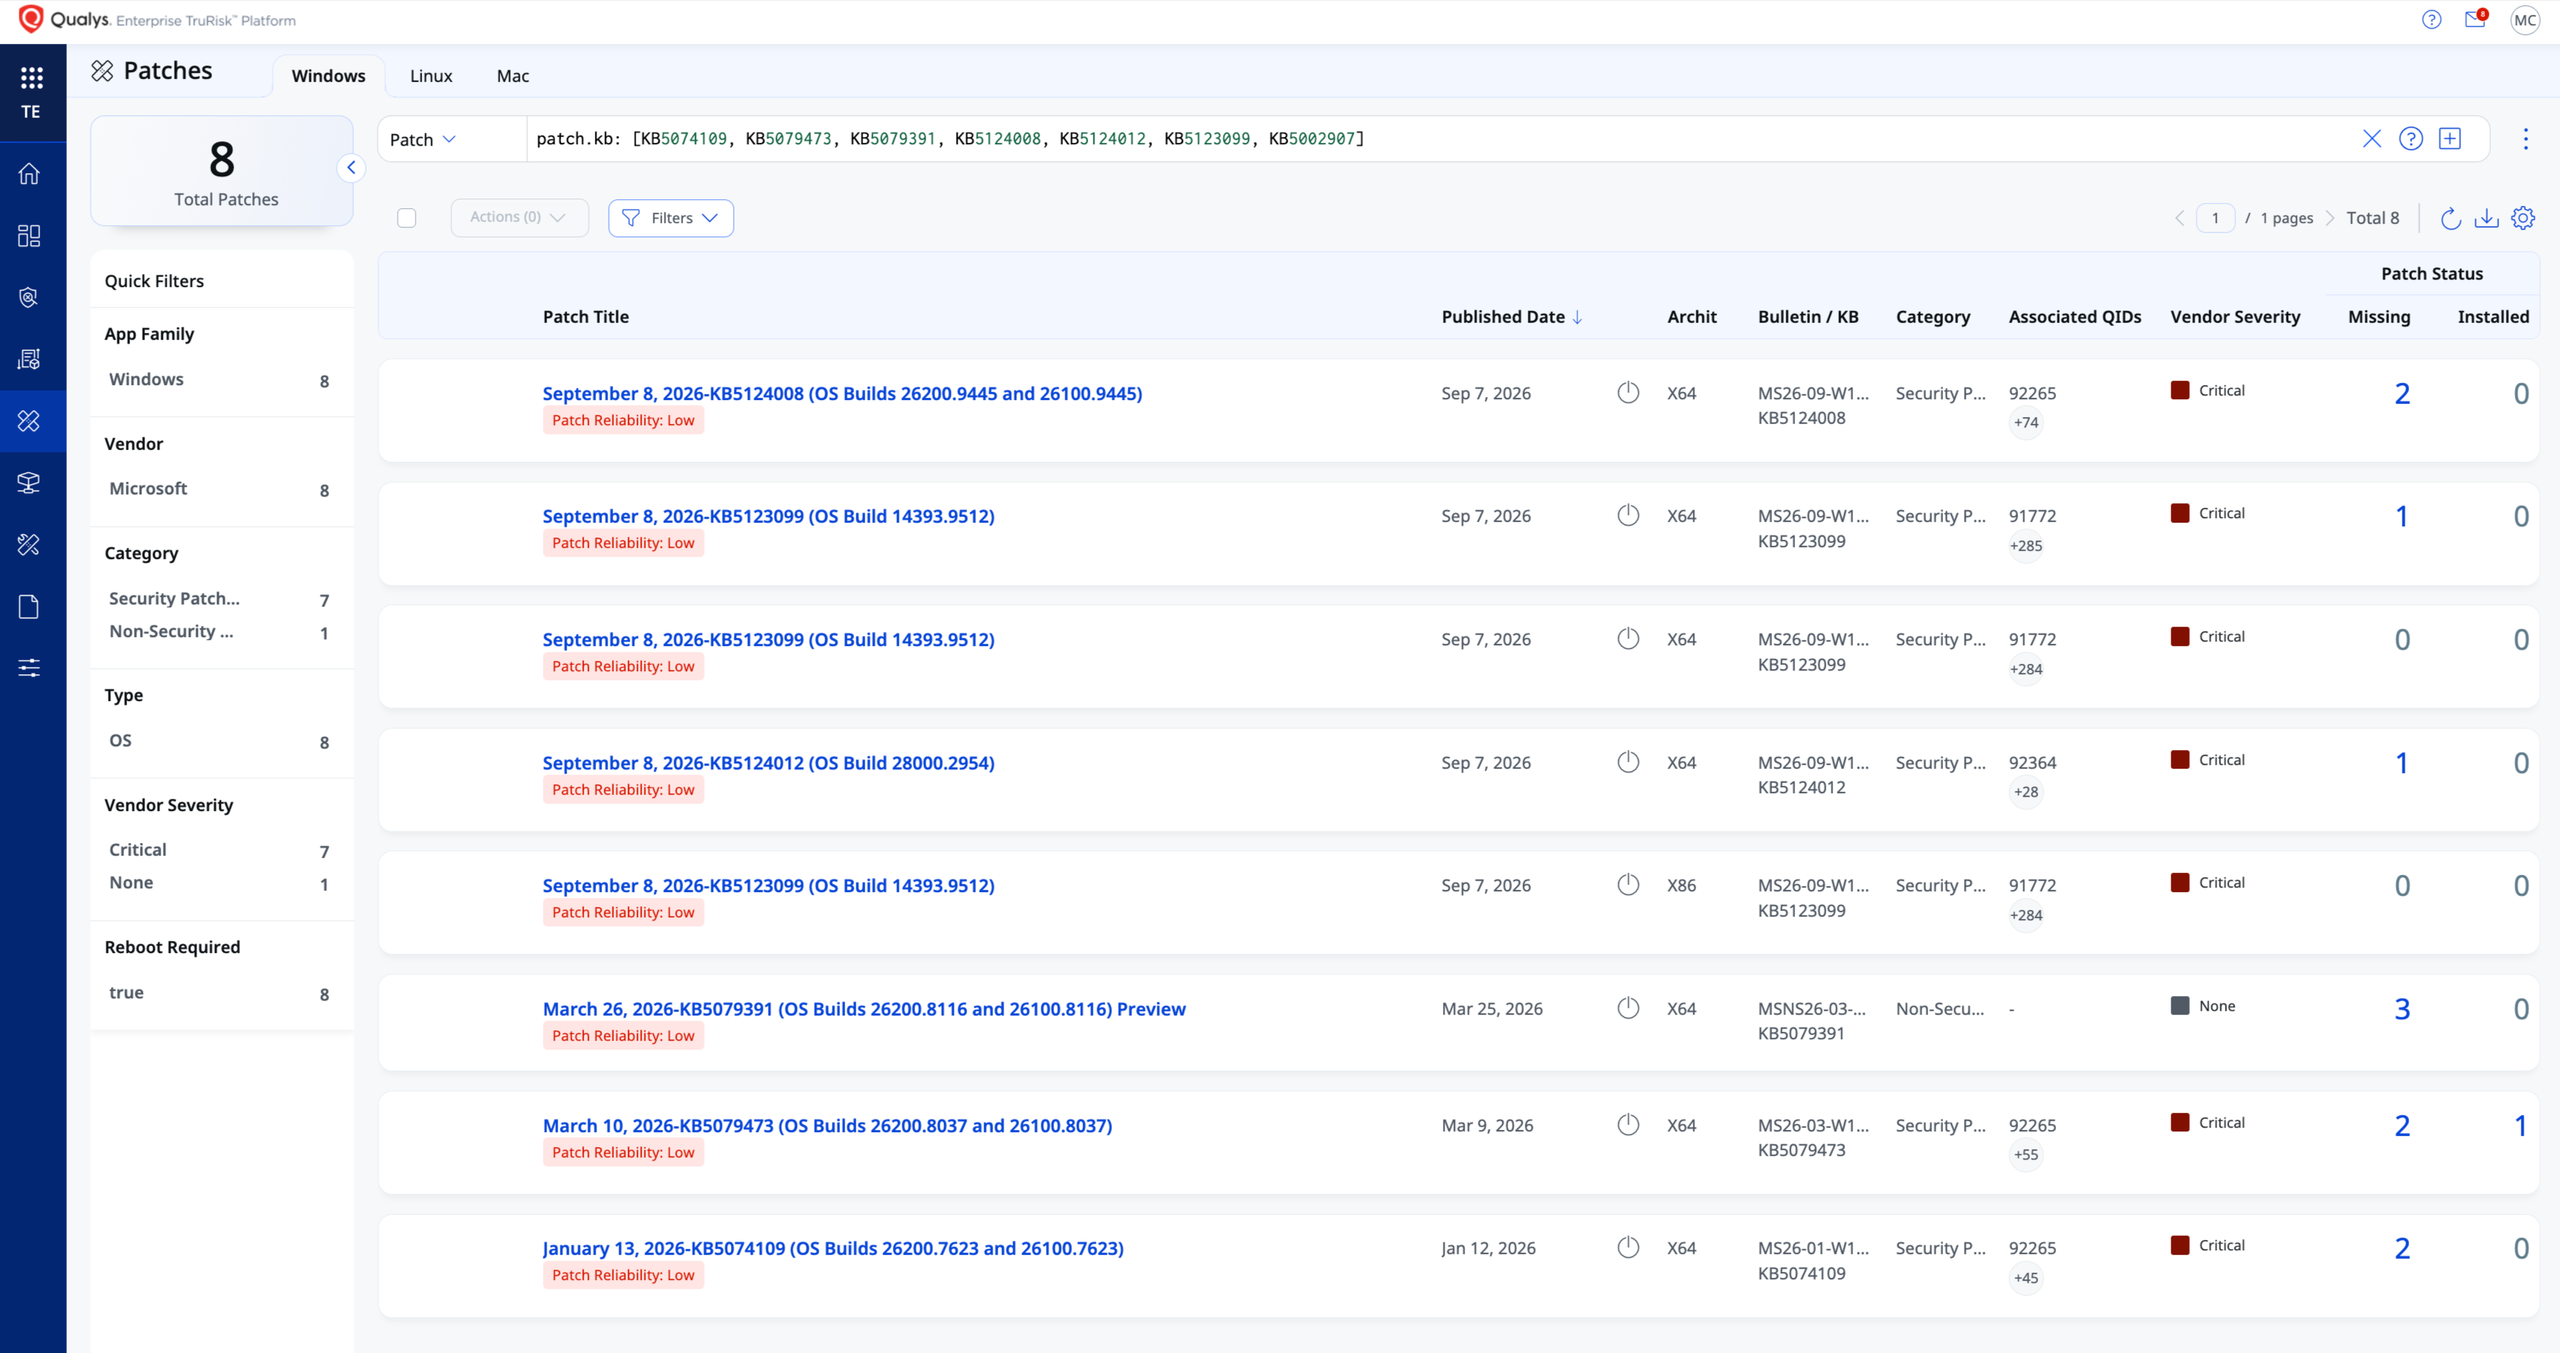
Executive Summary Microsoft’s September 2026 security updates – KB5124008 , KB5124012 , and KB5123099 have been linked to significant issues, underscoring the operational risks associated with security patching. Five known problems emerged after deployment: domain-joined devices losing their secure trust relationship with the domain, USB audio devices failin…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Automate Asset Isolation: Your Last Resort to Meet Remediation Deadlines Moderate Qualys Security Blog
2026-09-15 Qualys Security Blog

Automate Asset Isolation: Your Last Resort to Meet Remediation Deadlines

Executive Summary Remediation deadlines slip for reasons outside your control: a patch does not exist yet, a patch is delayed, or a remediation attempt fails. The outcome is the same either way: the host stays unpatched and stays on the network. TruRisk Eliminate closes that window by isolating the host automatically the moment your deadline passes, executed…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
What Is ISPM? How It Differs from IAM, PAM, IGA, and IDaaS Moderate Qualys Security Blog
2026-09-10 Qualys Security Blog

What Is ISPM? How It Differs from IAM, PAM, IGA, and IDaaS

Key Takeaways Identity Security Posture Management (ISPM) is the continuous risk and posture layer of the identity stack not a replacement for Identity and Access Management (IAM), Privileged Access Management (PAM), Identity Governance and Administration (IGA), or Identity-as-a-Service (IDaaS), but the layer that continuously assesses the exposure those sys…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The Models That Found 10,000 Zero-Days Broke Into Three Companies Using Weak Passwords Critical Qualys Security Blog
2026-09-09 Qualys Security Blog

The Models That Found 10,000 Zero-Days Broke Into Three Companies Using Weak Passwords

The question of whether a Frontier AI model could find vulnerabilities that no human researcher had found was settled in April. Claude Mythos Preview identified thousands of previously unknown flaws across every major operating system and browser, including a 27-year-old denial-of-service condition in OpenBSD, and within a month Anthropic and its Project Gla…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft and Adobe Patch Tuesday, September 2026 Security Update Review Moderate CVE-2026-81963 Qualys Security Blog
2026-09-08 Qualys Security Blog

Microsoft and Adobe Patch Tuesday, September 2026 Security Update Review

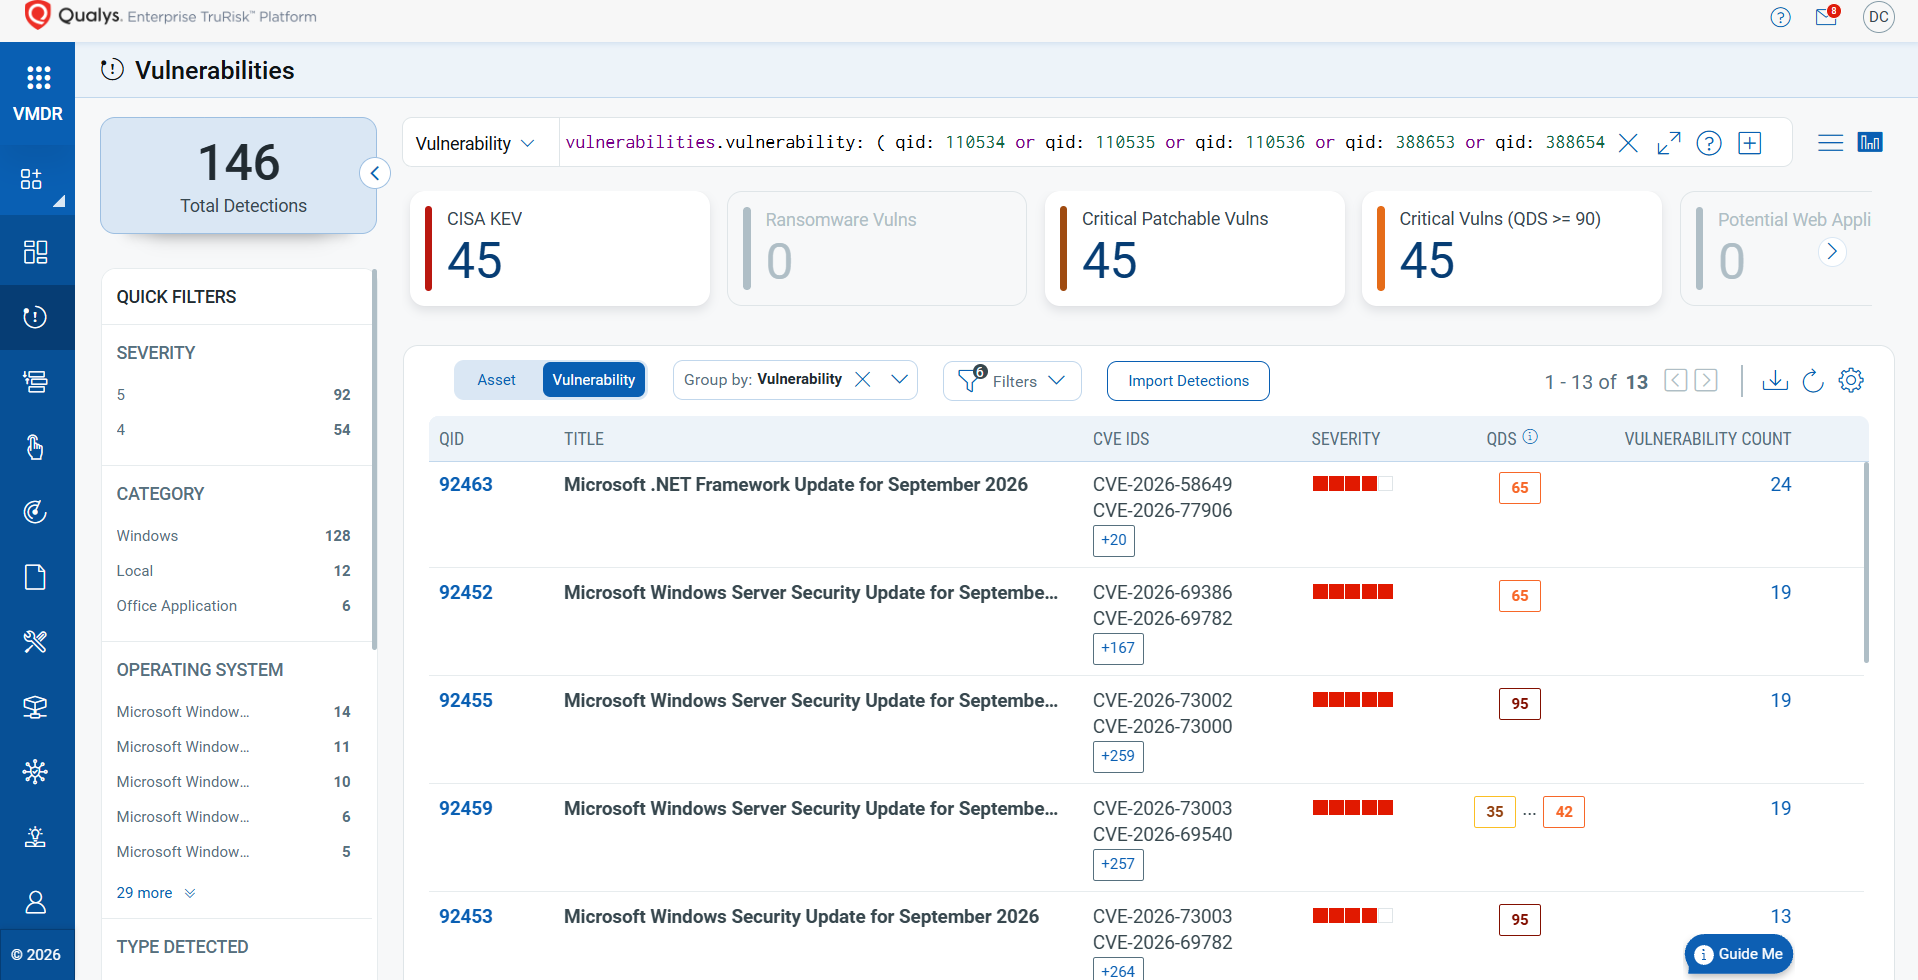
Microsoft kicks off September with its monthly Patch Tuesday release, delivering fixes for security vulnerabilities affecting its products. The security updates are packed with security fixes, providing organizations with important updates to help protect their environments from emerging threats. This Patch Tuesday is Microsoft’s largest security update ever…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification