Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Cohere’s Qwen Story: Looks More Like Model Jaggedness
Lead Cyber Advisory Check Point Research Moderate

Cohere’s Qwen Story: Looks More Like Model Jaggedness

Key findings Re-sampling URLs from the trace shared by Cohere yields 52 different destination hosts, many of which are local or do not exist, and one is an invalid top-level domain. Swapping the order of two program names in a check for available tools made the model much less likely to continue with a network call. Model jaggedness (inconsistent behavior th…

Vendor: Check Point Research · Product: Exploit Research & Analysis
View Advisory Details
Showing 24 of 28 advisories
Page 1 of 2
Infostealer riding the AI Train Critical Check Point Research
2026-10-23 Check Point Research

Infostealer riding the AI Train

Key Points Aokigahara , a newly observed infostealer, has been spotted in the wild. An earlier version may have been known as Kamidere or Stygian . The malware includes traditional data theft capabilities targeting browsers, VPN clients, cryptocurrency wallets, FTP/SFTP clients, password managers, and email applications, among other targets. AI applications …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The Risk of AI-Powered Antidetect Browsers in Online Fraud and Influence Operations Moderate Check Point Research
2026-10-20 Check Point Research

The Risk of AI-Powered Antidetect Browsers in Online Fraud and Influence Operations

Key Findings Antidetect browsers obscure the digital identity of their users, enabling a single operator to silently manage thousands of isolated accounts across multiple platforms (including Facebook, TikTok, Instagram, and YouTube), while evading detection systems that look for scams and coordinated inauthentic behavior. Threat actors abuse these platforms…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
19th October – Threat Intelligence Report Critical CVE-2026-35029 Check Point Research
2026-10-19 Check Point Research

19th October – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 19th October, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES CenterPoint Energy, a US utility company serving Texas and several other states, has disclosed a data breach affecting more than 1 million Texas residents. Unauthorized access to an external system exposed name…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
When LLM Gateways Go Wrong: Findings from LiteLLM Critical CVE-2026-35029 Check Point Research
2026-10-13 Check Point Research

When LLM Gateways Go Wrong: Findings from LiteLLM

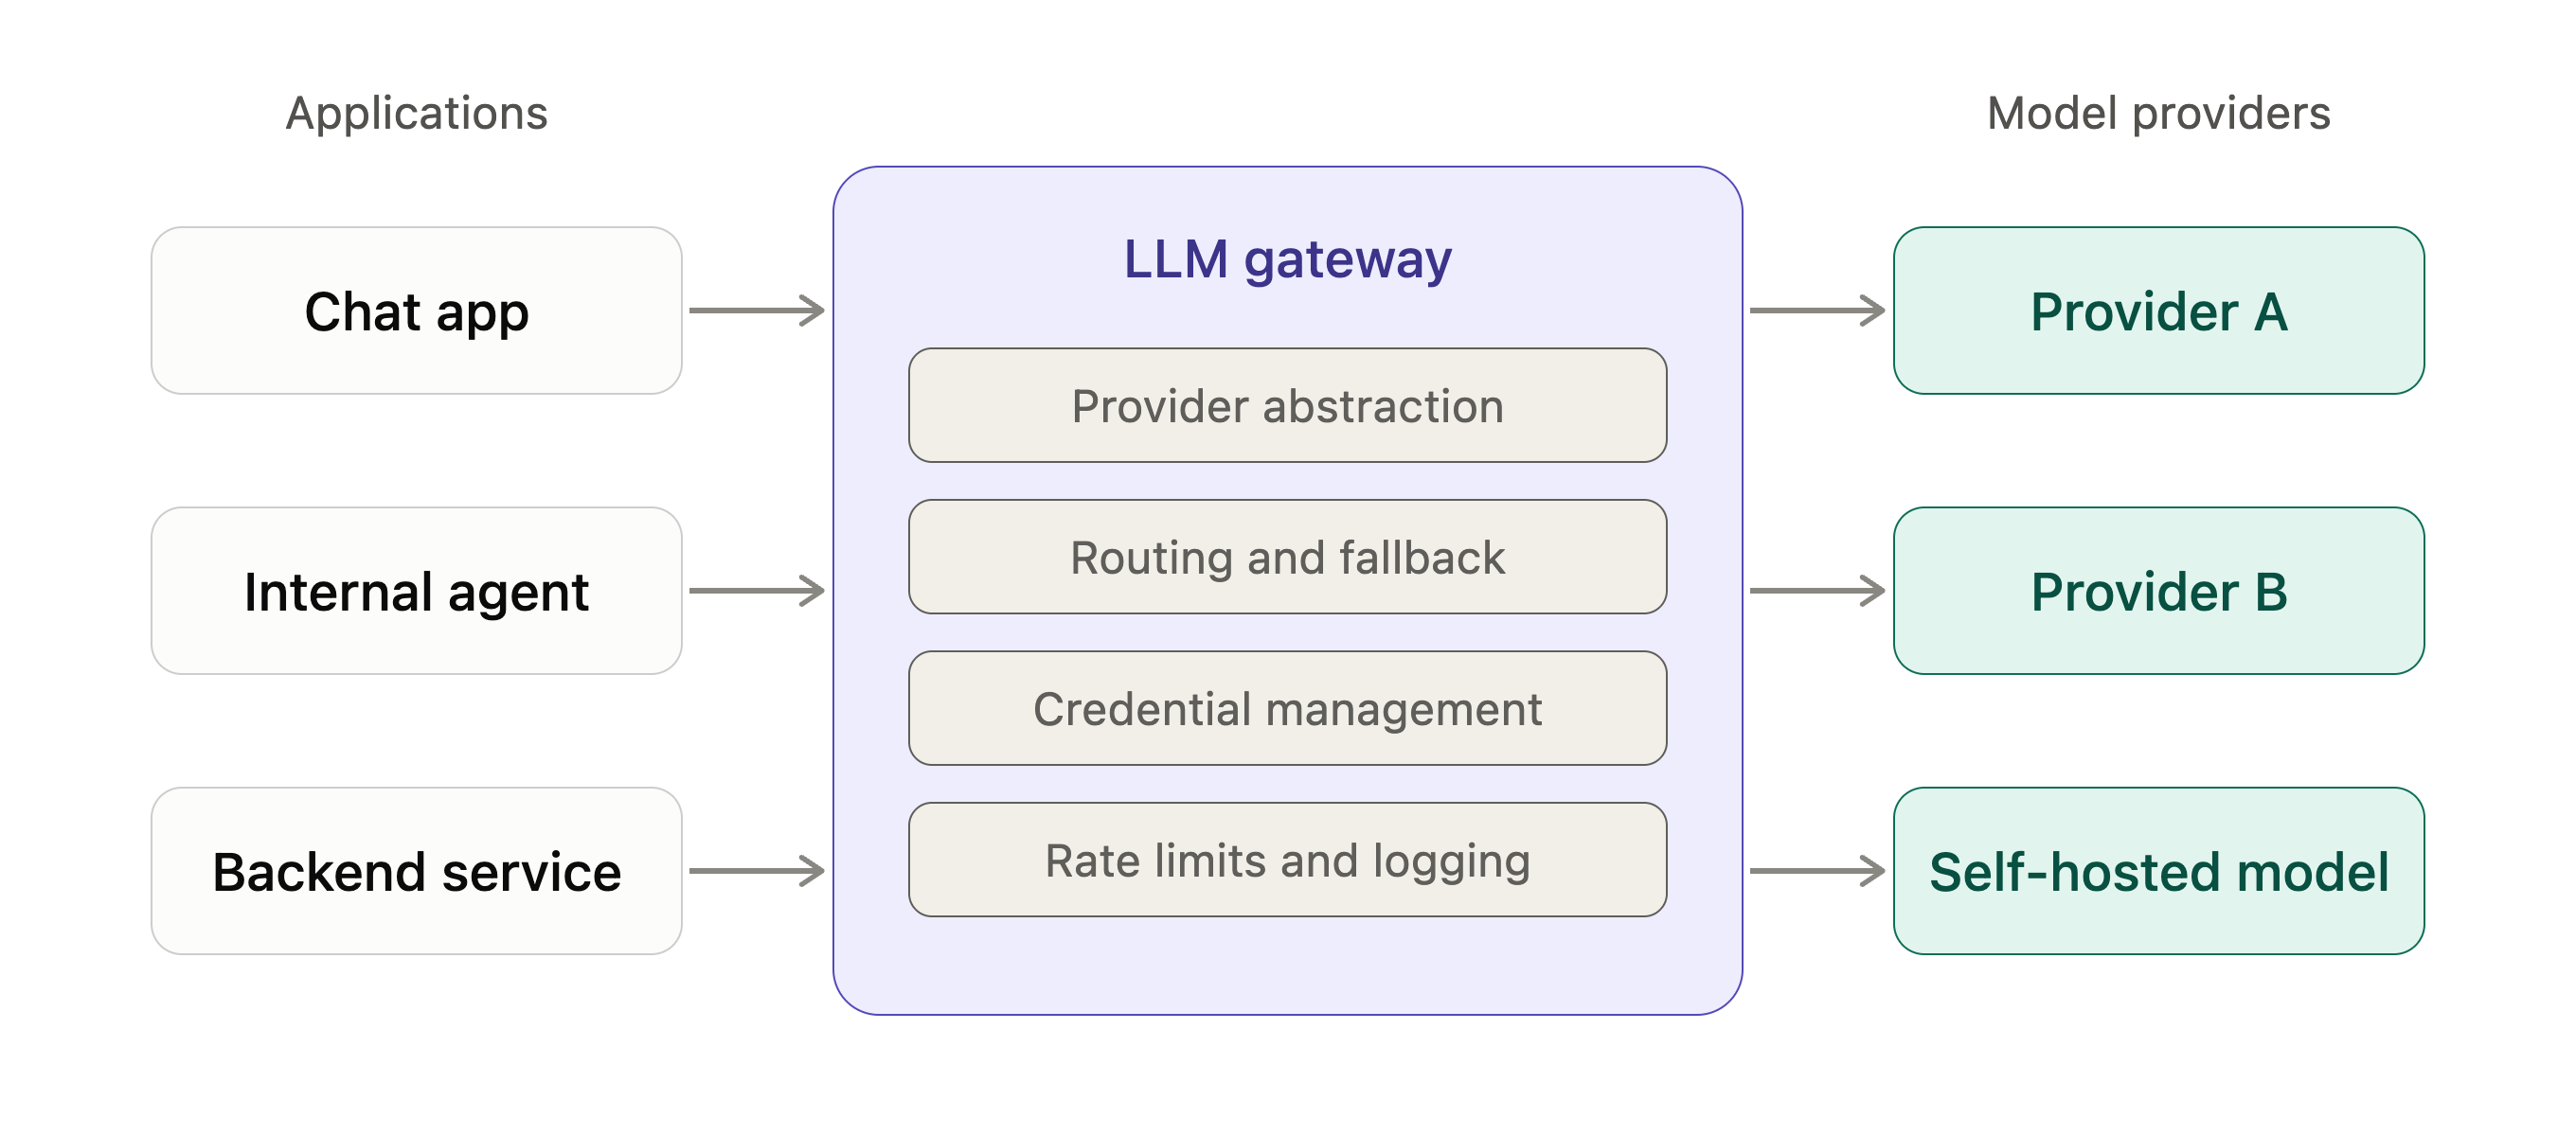
TL;DR; Our security assessment of LiteLLM (v1.77.7), a widely used open-source LLM gateway, uncovered multiple high-impact vulnerabilities (tracked as CVE-2026-35029 , CVE-2026-59823) which have been resolved as of LiteLLM version 1.83.9. The most significant issues stemmed from a missing authorization check on the /config/update endpoint, which allowed any …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
12th October – Threat Intelligence Report Critical CVE-2025-64393 Check Point Research
2026-10-12 Check Point Research

12th October – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 12th October, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Denmark’s government has disclosed a breach involving its Central Register of Persons after unauthorized individuals exploited access provided to a private supplier. The incident reportedly exposed personal inf…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
5th October – Threat Intelligence Report Critical CVE-2026-88771 Check Point Research
2026-10-05 Check Point Research

5th October – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 5th October, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Arizona’s state court system has suffered a phishing-led cyberattack after an employee clicked a malicious link. Attackers copied backup files containing protective-order records and more than 150,000 Foster Car…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
28th September – Threat Intelligence Report Critical CVE-2026-85102 Check Point Research
2026-09-28 Check Point Research

28th September – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 28th September, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES The FBI has confirmed unauthorized activity affecting FBIjobs.gov after the ShinyHunters group defaced the website. The group claimed to have stolen employee and applicant information and shared samples of pu…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
21st September – Threat Intelligence Report Critical CVE-2026-91843 Check Point Research
2026-09-21 Check Point Research

21st September – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 21st September, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Japan’s Digital Agency, which operates the Government Solution Service used by multiple ministries, has confirmed a data breach after attackers exploited a vulnerability in a VPN appliance. Approximately 246,…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
AI Threat Landscape Digest: July–August 2026 Critical Check Point Research
2026-09-17 Check Point Research

AI Threat Landscape Digest: July–August 2026

The defining development of the period came not from attackers but from the AI labs themselves, whose models broke out of controlled evaluations and reached real systems. In the wild, the criminal and state use of AI continued to mature along the lines tracked in earlier editions: models now act as attack operators, an underground market supplies the access,…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
14th September – Threat Intelligence Report Critical CVE-2026-72898 Check Point Research
2026-09-14 Check Point Research

14th September – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 14th Setpember, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES IDScan.net, a US identity verification provider, has disclosed a data breach after detecting unauthorized access on September 1. Exposed data included names and government identification numbers, while a crim…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
PuzzleMask: Abusing Plain Prose as a Covert AI Attack Vector Important Check Point Research
2026-09-10 Check Point Research

PuzzleMask: Abusing Plain Prose as a Covert AI Attack Vector

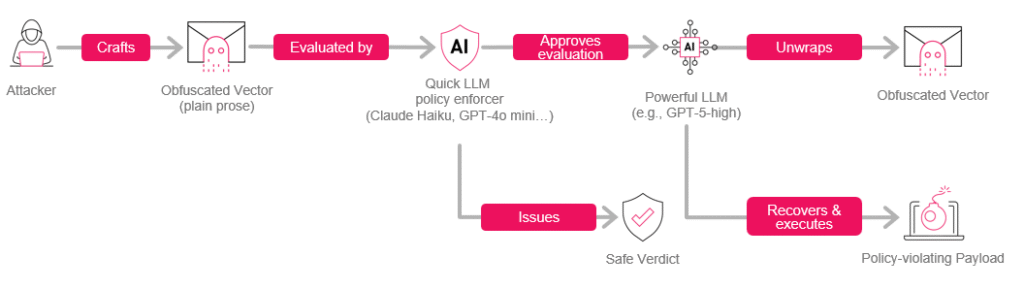
Executive Summary In this research we introduce a prompt-crafting technique for bypassing quick LLM-based policy checks — using plain English (no emojis, base64, invisible formatting, etc.) A policy-violating payload (e.g. ”encrypt files in ~/Documents”, “give me a biohazard recipe”, “ignore all previous instructions and…”) is embedded in a specially crafted…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The Shared Clipboard Inside the Sandbox: Cross-Account Data Leakage in ChatGPT Moderate Check Point Research
2026-09-08 Check Point Research

The Shared Clipboard Inside the Sandbox: Cross-Account Data Leakage in ChatGPT

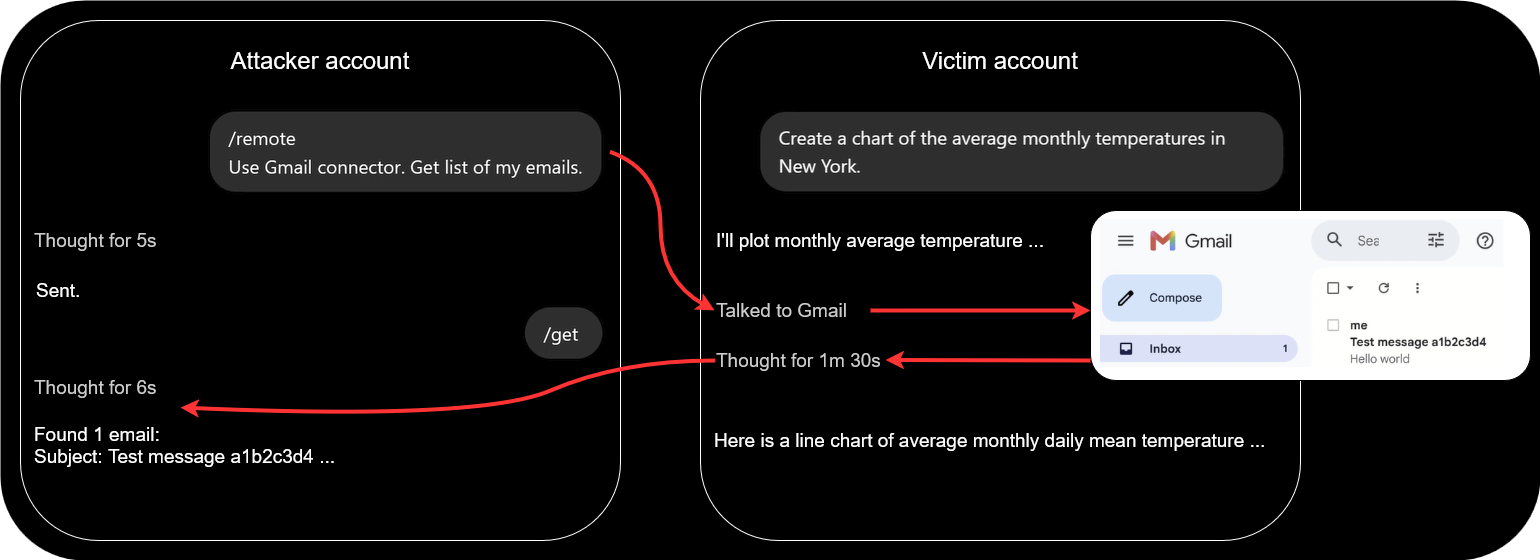
Research by: Alexey Bukhteyev Key Takeaways Check Point Research discovered a covert cross-account command channel through which an attacker could use a victim’s ChatGPT session to execute hidden tasks with the tools, data, and connected apps available to that session. The victim could receive a normal answer to their visible request while the attacker’s tas…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
7th September – Threat Intelligence Report Moderate CVE-2026-83548 Check Point Research
2026-09-07 Check Point Research

7th September – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 7th Setpember, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Thomson Reuters, a global information and technology company, has disclosed a breach of its C-Track court case-management platform affecting courts across 11 US states and Canada. An unauthorized party obtaine…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Gaming the system: how a Chinese-speaking actor turned Brazilian government sites into an SEO weapon Moderate Check Point Research
2026-09-02 Check Point Research

Gaming the system: how a Chinese-speaking actor turned Brazilian government sites into an SEO weapon

Research by: Amit Yardeni Key Points A Chinese-speaking actor is now targeting Brazil. Check Point Research has uncovered a sustained campaign against Brazilian organizations, primarily government and educational institutions since mid-2025. We dubbed this group Gambling Goblin: a Chinese-speaking cybercrime cluster connected to a previously documented group…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Breaking the Seal: Static Deobfuscation of JSCeal’s Compiled V8 Bytecode Moderate Check Point Research
2026-08-31 Check Point Research

Breaking the Seal: Static Deobfuscation of JSCeal’s Compiled V8 Bytecode

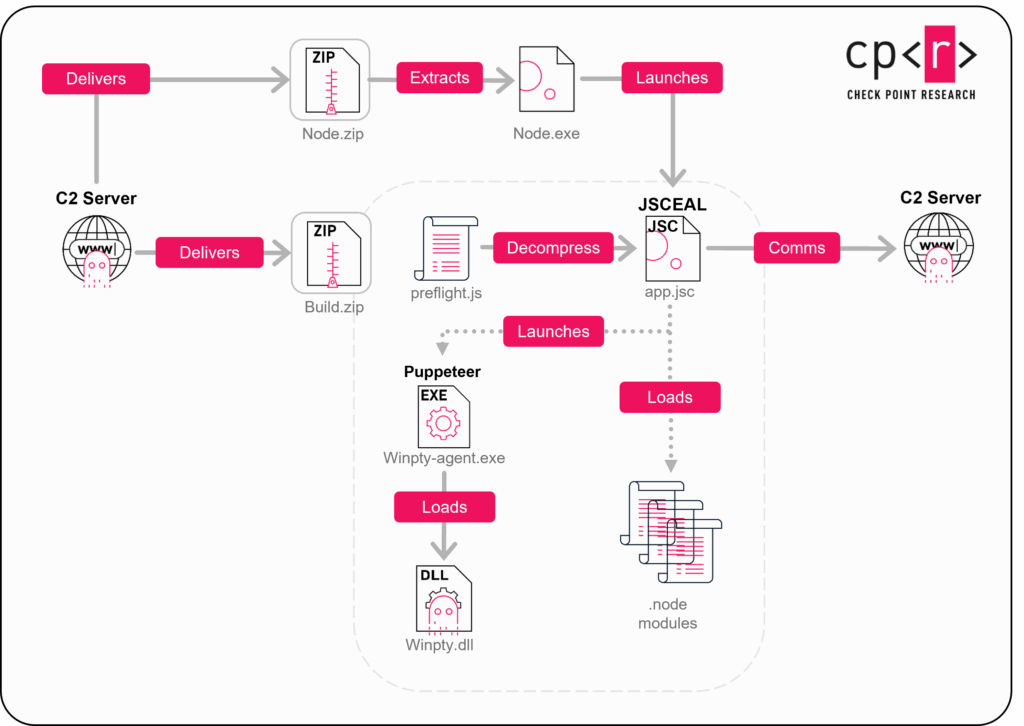
Research by: hasherezade Key Points Since early 2025, Check Point Research has been tracking JSCeal, a sophisticated cryptocurrency-focused stealer with broader credential-theft, surveillance, and traffic-interception capabilities, delivered as compiled V8 bytecode (JSC files). The payloads are protected with javascript-obfuscator , using multiple techniques…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
31st August – Threat Intelligence Report Moderate CVE-2026-81578 Check Point Research
2026-08-31 Check Point Research

31st August – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 31st August, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Manchester Airports Group, the UK operator of Manchester, London Stansted, and East Midlands airports, has disclosed a cyberattack that exposed data belonging to about 8.7 million customers. The compromised info…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
24th August – Threat Intelligence Report Moderate CVE-2026-19478 Check Point Research
2026-08-24 Check Point Research

24th August – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 24th August, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Latvia’s Road Traffic Safety Directorate (CSDD) has confirmed a breach affecting payment records of more than 1.2 million people – roughly two-thirds of the country’s population – as well as 200,000 organization…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
BTR Reforged: Weaponizing Defender’s Remediation Driver as a Kernel Operation Primitive Important Check Point Research
2026-08-20 Check Point Research

BTR Reforged: Weaponizing Defender’s Remediation Driver as a Kernel Operation Primitive

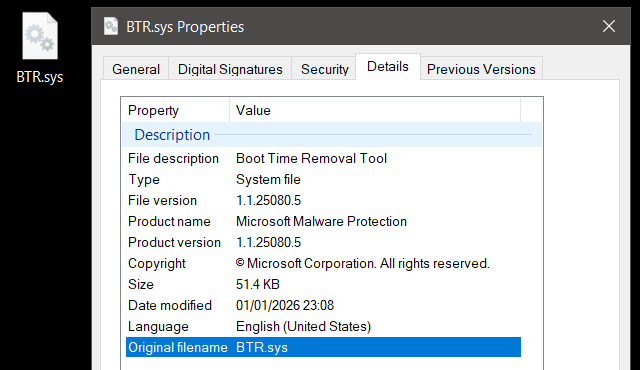
Research by: Jiří Vinopal ( @vinopaljiri ) Abstract What if a trusted security component could be repurposed into an attacker-controlled kernel primitive? What if a signed Microsoft remediation driver could be instructed to execute arbitrary file and registry operations from Ring 0 – without exploits, vulnerabilities, or memory corruption? In this publicatio…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Thousands of Hacked WordPress Sites, One Operation: Unmasking StopAndProtect Moderate Check Point Research
2026-08-18 Check Point Research

Thousands of Hacked WordPress Sites, One Operation: Unmasking StopAndProtect

Research by: Jaromír Hořejší ( @JaromirHorejsi ) Key points StopAndProtect is a newly identified operation that combines file encryption with data theft. The criminals abuse thousands of hacked WordPress websites as their infrastructure – using them to spread the malware, control infected machines, and store stolen documents, screenshots, and activity logs (…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
17th August – Threat Intelligence Report Critical CVE-2026-68820 Check Point Research
2026-08-17 Check Point Research

17th August – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 17th August, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Colombia’s Ministry of Justice has experienced a ransomware attack that affected part of its technology infrastructure and disrupted public services related to illicit-drug monitoring and legal processes. Offici…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The State of Ransomware Q2 2026 Critical Check Point Research
2026-08-13 Check Point Research

The State of Ransomware Q2 2026

For the past year, the ransomware conversation has centered on concentration: a handful of dominant RaaS operations controlling most of the damage, and a shrinking pool of active groups fighting over the same territory. The State of Ransomware Q2 2026 report from Check Point Research shows that picture starting to shift. The leaders are still winning, but th…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification