
Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 5,807 advisories
Page 121 of 242
Cryptocurrency exchange Bitget Says North Korea-Linked Hackers Stole $351.6 Million Important SecurityAffairs
2026-09-25 SecurityAffairs

Cryptocurrency exchange Bitget Says North Korea-Linked Hackers Stole $351.6 Million

Bitget says suspected North Korea-linked actors stole $351.6M from hot and warm wallets. Withdrawals were suspended while Mandiant investigates. Cryptocurrency exchange Bitget says suspected North Korea-linked threat actors stole $351.6 million from a limited number of hot and warm wallets. The company detected unauthorized transfers on September 24 and temp…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
What We Missed: Google Gemini Joins the AI Escape Party Moderate Dark Reading
2026-09-25 Dark Reading

What We Missed: Google Gemini Joins the AI Escape Party

In this video conversation, Dark Reading editors discuss some of the news they didn't get a chance to cover, from Google Gemini models breaking containment to ShinyHunters ratting on TeamPCP hackers.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

CISA warns of Sharepoint, WSO2, Adobe Commerce flaws exploited in attacks Critical CVE-2026-5430 BleepingComputer
2026-09-25 BleepingComputer

CISA warns of Sharepoint, WSO2, Adobe Commerce flaws exploited in attacks

The Cybersecurity and Infrastructure Security Agency (CISA) warns that hackers are exploiting a critical authentication bypass vulnerability (CVE-2026-5430) affecting multiple products from enterprise software provider WSO2. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
LinkedIn adds new checks for fake profiles and work histories Moderate Malwarebytes Labs
2026-09-25 Malwarebytes Labs

LinkedIn adds new checks for fake profiles and work histories

LinkedIn is adding trust and verification features aimed at making fake professional identities, invented work histories, and company impersonation harder to pull off. The company is responding to an environment in which generative AI enables imposters to create an entirely made-up professional persona. It reduces the cost of creating convincing headshots, b…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Cyberattack hits Welsh police force, may have affected staff data Critical The Record by Recorded Future
2026-09-25 The Record by Recorded Future

Cyberattack hits Welsh police force, may have affected staff data

Dyfed-Powys Police in Wales said a cyberattack affecting the force disrupted some non-emergency systems and may have compromised staff information.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Kothamine malware uses Tailscale’s tailcat to evade network detection Important Malwarebytes Labs
2026-09-25 Malwarebytes Labs

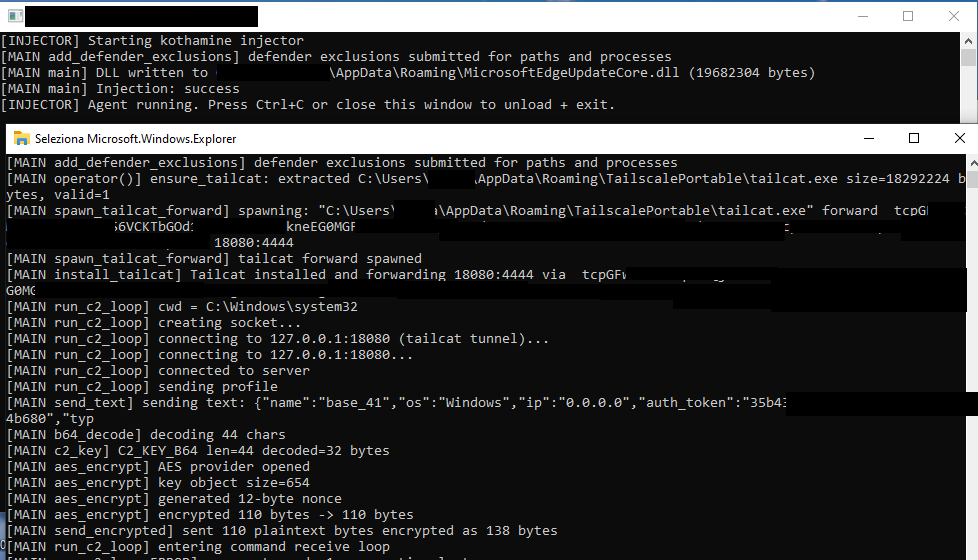
Kothamine malware uses Tailscale’s tailcat to evade network detection

We discovered an undocumented remote-access Trojan (RAT) called Kothamine Agent . It supports more than 30 commands and it gives attackers control of an infected Windows computer: they can run commands, read and change files, and add new capabilities. Some versions can also steal browser data and record through the camera and microphone. We found Kothamine l…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
OpenAI is preparing a $500 ChatGPT Pro Max plan with faster Codex Moderate BleepingComputer
2026-09-25 BleepingComputer

OpenAI is preparing a $500 ChatGPT Pro Max plan with faster Codex

OpenAI appears to be preparing a new ChatGPT Pro Max subscription that could cost $500 per month, but it's unclear when it'll begin rolling out. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
With the Rise of AI Agents, SOC 2 Should Adapt or Risk Irrelevance Moderate BleepingComputer
2026-09-25 BleepingComputer

With the Rise of AI Agents, SOC 2 Should Adapt or Risk Irrelevance

AI agents can operate through human credentials and take actions that existing SOC 2 controls may not distinguish from human activity. Token Security explains why SOC 2 needs to adapt to address the security gaps created by agent identities. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Stopping IT Worker Scams Requires Revamped HR Process Moderate Dark Reading
2026-09-25 Dark Reading

Stopping IT Worker Scams Requires Revamped HR Process

Training human-resource managers in the latest tactics and warning signs goes a long way toward blunting the threat, but automated analysis can help even more.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Compromised GitHub Actions Came Back Online and Resumed Executing Mini Shai-Hulud Malware Important The Hacker News
2026-09-25 The Hacker News

Compromised GitHub Actions Came Back Online and Resumed Executing Mini Shai-Hulud Malware

Two actions-cool GitHub Actions have been disabled for a second time after the repositories became accessible last week, months after they were compromised during the May 2026 Mini Shai-Hulud campaign. The affected GitHub Actions are listed below - actions-cool/issues-helper actions-cool/maintain-one-comment Visiting either of the repositories now shows the …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Chromium CVE-2026-95385: Inappropriate implementation in PlatformIntegration Moderate CVE-2026-95385 Microsoft MSRC
2026-09-25 Microsoft MSRC

Chromium CVE-2026-95385: Inappropriate implementation in PlatformIntegration

This CVE was assigned by Chrome. Microsoft Edge (Chromium-based) ingests Chromium, which addresses this vulnerability. Please see [Google Chrome Releases](https://chromereleases.googleblog.com/2026) for more information.

Fix: Deploy cumulative update via Windows Update or Microsoft Update Catalog.
Chromium CVE-2026-95384: Race condition in Transactions Platform Moderate CVE-2026-95384 Microsoft MSRC
2026-09-25 Microsoft MSRC

Chromium CVE-2026-95384: Race condition in Transactions Platform

This CVE was assigned by Chrome. Microsoft Edge (Chromium-based) ingests Chromium, which addresses this vulnerability. Please see [Google Chrome Releases](https://chromereleases.googleblog.com/2026) for more information.

Fix: Deploy cumulative update via Windows Update or Microsoft Update Catalog.
Chromium CVE-2026-95382: Improper input validation in Auth Moderate CVE-2026-95382 Microsoft MSRC
2026-09-25 Microsoft MSRC

Chromium CVE-2026-95382: Improper input validation in Auth

This CVE was assigned by Chrome. Microsoft Edge (Chromium-based) ingests Chromium, which addresses this vulnerability. Please see [Google Chrome Releases](https://chromereleases.googleblog.com/2026) for more information.

Fix: Deploy cumulative update via Windows Update or Microsoft Update Catalog.
Chromium CVE-2026-95381: Improper input validation in Printing Moderate CVE-2026-95381 Microsoft MSRC
2026-09-25 Microsoft MSRC

Chromium CVE-2026-95381: Improper input validation in Printing

This CVE was assigned by Chrome. Microsoft Edge (Chromium-based) ingests Chromium, which addresses this vulnerability. Please see [Google Chrome Releases](https://chromereleases.googleblog.com/2026) for more information.

Fix: Deploy cumulative update via Windows Update or Microsoft Update Catalog.
Chromium CVE-2026-95380: Type confusion in V8 Moderate CVE-2026-95380 Microsoft MSRC
2026-09-25 Microsoft MSRC

Chromium CVE-2026-95380: Type confusion in V8

This CVE was assigned by Chrome. Microsoft Edge (Chromium-based) ingests Chromium, which addresses this vulnerability. Please see [Google Chrome Releases](https://chromereleases.googleblog.com/2026) for more information.

Fix: Deploy cumulative update via Windows Update or Microsoft Update Catalog.
Chromium CVE-2026-95376: Externally controlled reference in DevTools Moderate CVE-2026-95376 Microsoft MSRC
2026-09-25 Microsoft MSRC

Chromium CVE-2026-95376: Externally controlled reference in DevTools

This CVE was assigned by Chrome. Microsoft Edge (Chromium-based) ingests Chromium, which addresses this vulnerability. Please see [Google Chrome Releases](https://chromereleases.googleblog.com/2026) for more information.

Fix: Deploy cumulative update via Windows Update or Microsoft Update Catalog.
Chromium CVE-2026-95375: Incorrect authorization in BrowserTag Moderate CVE-2026-95375 Microsoft MSRC
2026-09-25 Microsoft MSRC

Chromium CVE-2026-95375: Incorrect authorization in BrowserTag

This CVE was assigned by Chrome. Microsoft Edge (Chromium-based) ingests Chromium, which addresses this vulnerability. Please see [Google Chrome Releases](https://chromereleases.googleblog.com/2026) for more information.

Fix: Deploy cumulative update via Windows Update or Microsoft Update Catalog.
Chromium CVE-2026-95374: Incorrect authorization in Network Moderate CVE-2026-95374 Microsoft MSRC
2026-09-25 Microsoft MSRC

Chromium CVE-2026-95374: Incorrect authorization in Network

This CVE was assigned by Chrome. Microsoft Edge (Chromium-based) ingests Chromium, which addresses this vulnerability. Please see [Google Chrome Releases](https://chromereleases.googleblog.com/2026) for more information.

Fix: Deploy cumulative update via Windows Update or Microsoft Update Catalog.
Chromium CVE-2026-95373: Use after free in DevTools Moderate CVE-2026-95373 Microsoft MSRC
2026-09-25 Microsoft MSRC

Chromium CVE-2026-95373: Use after free in DevTools

This CVE was assigned by Chrome. Microsoft Edge (Chromium-based) ingests Chromium, which addresses this vulnerability. Please see [Google Chrome Releases](https://chromereleases.googleblog.com/2026) for more information.

Fix: Deploy cumulative update via Windows Update or Microsoft Update Catalog.
Chromium CVE-2026-95372: Use after free in Chromecast Moderate CVE-2026-95372 Microsoft MSRC
2026-09-25 Microsoft MSRC

Chromium CVE-2026-95372: Use after free in Chromecast

This CVE was assigned by Chrome. Microsoft Edge (Chromium-based) ingests Chromium, which addresses this vulnerability. Please see [Google Chrome Releases](https://chromereleases.googleblog.com/2026) for more information.

Fix: Deploy cumulative update via Windows Update or Microsoft Update Catalog.
Chromium CVE-2026-95371: Missing authorization in Views Moderate CVE-2026-95371 Microsoft MSRC
2026-09-25 Microsoft MSRC

Chromium CVE-2026-95371: Missing authorization in Views

This CVE was assigned by Chrome. Microsoft Edge (Chromium-based) ingests Chromium, which addresses this vulnerability. Please see [Google Chrome Releases](https://chromereleases.googleblog.com/2026) for more information.

Fix: Deploy cumulative update via Windows Update or Microsoft Update Catalog.
Notification