Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 5,807 advisories
Page 136 of 242
Critical Bifrost AI Gateway Flaw Lets Attackers Run Commands Without Credentials Critical CVE-2026-90898 The Hacker News
2026-09-22 The Hacker News

Critical Bifrost AI Gateway Flaw Lets Attackers Run Commands Without Credentials

A critical vulnerability in Bifrost, an open-source AI gateway that routes requests to more than 20 LLM providers, allows an unauthenticated attacker to run arbitrary commands on the gateway server with a single HTTP request. The flaw, tracked as CVE-2026-90898 (CVSS score: 9.8), affects all versions of the Bifrost HTTP transport before 2.1.0 when management…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Check Point warns of Management Server zero-day exploited in attacks Critical BleepingComputer
2026-09-22 BleepingComputer

Check Point warns of Management Server zero-day exploited in attacks

Check Point Software released emergency hotfixes to address a critical Security Management Server vulnerability that could let attackers run arbitrary scripts. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Researcher Drops BigDiskBuster Zero-Day PoC That Blocks Microsoft Defender Updates Critical The Hacker News
2026-09-22 The Hacker News

Researcher Drops BigDiskBuster Zero-Day PoC That Blocks Microsoft Defender Updates

A zero-day proof-of-concept tool that stops Microsoft Defender from installing platform and signature updates by filling all available disk space was published on GitHub on September 19. The tool, called BigDiskBuster, has no patch, no CVE, and no Microsoft advisory. Its author, Abdelhamid Naceri, is a former Microsoft security researcher whose earlier Defen…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Two arrested in UK after Microsoft takedown of ‘Eviltokens’ AI-chatbot for cybercriminals Moderate The Record by Recorded Future
2026-09-22 The Record by Recorded Future

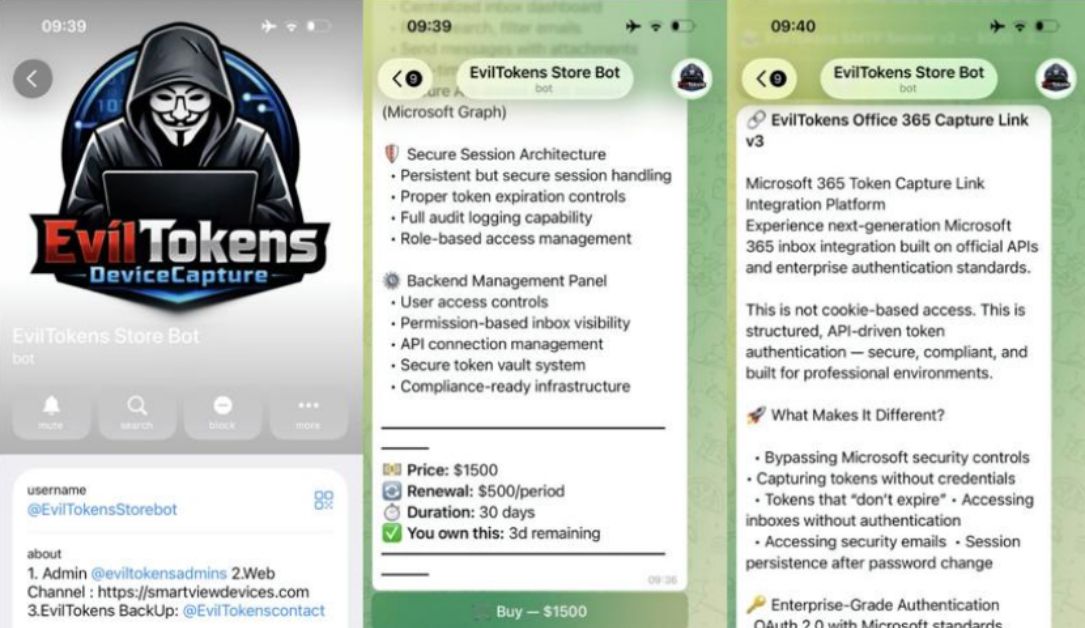
Two arrested in UK after Microsoft takedown of ‘Eviltokens’ AI-chatbot for cybercriminals

Available on Telegram for a $1,500 initiation fee and a recurring monthly $500 subscription, EvilTokens provided cybercriminals with artificial intelligence tools enabling them to compromise accounts, analyze breached inboxes and find the best methods for monetizing their access through fraud.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Some cheap smart glasses are a security disaster Moderate Malwarebytes Labs
2026-09-22 Malwarebytes Labs

Some cheap smart glasses are a security disaster

Apart from the privacy concerns around smart glasses , researchers have found that some cheap brands come with barely any security at all. ABC Australia reports that researchers from NSB Cyber and Abstract Shield tested two inexpensive pairs, costing A$60 and A$110 (around US$42 and US$78), and found more than a dozen flaws across the smart glasses themselve…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

EvilTokens PhaaS disrupted after compromising 12,000 Microsoft accounts Moderate BleepingComputer
2026-09-22 BleepingComputer

EvilTokens PhaaS disrupted after compromising 12,000 Microsoft accounts

The EvilTokens platform that compromised more than 12,000 Microsoft accounts at over 10,000 organizations has been disrupted in an effort led by Microsoft's Digital Crimes Unit (DCU). [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Chaotic Eclipse Released BigDiskBuster, A PoC For Windows Defender Update DoS Zero-Day Critical SecurityAffairs
2026-09-22 SecurityAffairs

Chaotic Eclipse Released BigDiskBuster, A PoC For Windows Defender Update DoS Zero-Day

The researcher Chaotic Eclipse released BigDiskBuster, a PoC exploit for a Windows Defender Update DoS Zero-Day vulnerability. Security researcher Chaotic Eclipse , also known as INFINITE NIGHTMARE, MSNightmare and Nightmare-Eclipse, released a new zero-day exploit targeting Microsoft Defender. The researcher named the exploit BigDiskBuster, it triggers a De…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Researchers uncover malware that uses AI to choose its next move Important Help Net Security
2026-09-22 Help Net Security

Researchers uncover malware that uses AI to choose its next move

To help security practitioners catch malware that leans on AI, researchers from Cisco Talos shared an open-source framework that they hope will be used to classify and analyze the threat. The tool, called CAIRN, works entirely from metadata pulled off files. No downloading the malware, no running it. CAIRN explorer connects malware binaries by metadata attri…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Brief hijack makes Elsevier domains redirect to LAPSUS$ “Chapter II” page Important Help Net Security
2026-09-22 Help Net Security

Brief hijack makes Elsevier domains redirect to LAPSUS$ “Chapter II” page

Three domains / web portals belonging to Dutch academic publishing company Elsevier have been redirecting users to a page branded “LAPSUS$ GROUP, Chapter II,” carrying a signed statement that taunted the FBI and counted down to a future victim. According to Cloudskope researchers, the redirect ran for at least 78 minutes, from roughly 7:49pm CT until it was …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
LausivLoader analysis, or how to pass data between malware stages, (Thu, Sep 17th) Important SANS Internet Storm Center
2026-09-22 SANS Internet Storm Center

LausivLoader analysis, or how to pass data between malware stages, (Thu, Sep 17th)

At the end of August, a malspam message was caught in the quarantine of a mail gateway operated by one of my customers. The message was not especially remarkable – it asked the recipient to review some attached requirements and provide a price quotation for a fiber optic system and appeared to impersonate an employee of a legitimate company.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
AI is set to help cyber attackers much more than defenders, says UK official Important The Record by Recorded Future
2026-09-22 The Record by Recorded Future

AI is set to help cyber attackers much more than defenders, says UK official

Dave Chismon, the NCSC’s chief technology officer for architecture, said in a blog post that the imbalance in AI means cyberattacks would likely grow as automated defenses struggle to keep pace.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Russia's internet shutdowns disrupt warnings about incoming drone attacks Important The Record by Recorded Future
2026-09-22 The Record by Recorded Future

Russia's internet shutdowns disrupt warnings about incoming drone attacks

Russia’s growing restrictions on mobile internet and cellular service are making it harder for people to receive warnings about incoming Ukrainian drone and missile attacks.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Webinar tomorrow: Inside real-world Google Workspace breaches Critical BleepingComputer
2026-09-22 BleepingComputer

Webinar tomorrow: Inside real-world Google Workspace breaches

Tomorrow's webinar examines real Google Workspace breaches involving social engineering and malicious OAuth applications, from initial access through the critical first hours of incident response. Learn which security controls and response decisions can make the greatest difference. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
D-Link warns of max severity zero-day bug in DIR-822A routers Critical CVE-2026-86296 BleepingComputer
2026-09-22 BleepingComputer

D-Link warns of max severity zero-day bug in DIR-822A routers

D-Link warned customers of a maximum-severity vulnerability (CVE-2026-86296) with public proof-of-concept (PoC) exploit code and no patch, affecting legacy DIR-822A dual-band Wi-Fi routers. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
AI Agents Are Rewriting the Rules of Lateral Movement Moderate The Hacker News
2026-09-22 The Hacker News

AI Agents Are Rewriting the Rules of Lateral Movement

Security teams have spent decades asking whether an identity has too much access. AI agents raise a harder question: how can we determine which paths an autonomous system can discover, given the access it already has? A person may try several ways to complete a task. A deterministic application follows the flow its developer wrote. But an AI agent is relentl…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification