Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 5,807 advisories
Page 140 of 242
ChainScript: the RAT that hides its command server inside a blockchain contract Moderate SecurityAffairs
2026-09-21 SecurityAffairs

ChainScript: the RAT that hides its command server inside a blockchain contract

Blackpoint uncovers ChainScript, a Node.js RAT that queries a Polygon smart contract to find and rotate its command server. Blackpoint’s Adversary Pursuit Group was chasing a ClickFix campaign spreading an unknown RAT namend ChainScript. The malicious code is a previously undocumented Node.js remote access trojan that hides its command server on a public blo…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft reminds admins to migrate Entra ID users to passkeys Moderate BleepingComputer
2026-09-21 BleepingComputer

Microsoft reminds admins to migrate Entra ID users to passkeys

Microsoft has reminded admins to migrate Entra ID users to phishing-resistant authentication methods to avoid sign-in disruptions after it retires SMS first-factor sign-in starting in February 2027. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
LinkedIn wins court order blocking mass scraping of user data Moderate The Record by Recorded Future
2026-09-21 The Record by Recorded Future

LinkedIn wins court order blocking mass scraping of user data

The agreement between LinkedIn, ProAPIs and joint business operator Netswift also requires the firms to stop selling and transferring the data, no longer access LinkedIn through fake accounts and delete the data that was scraped, according to a senior LinkedIn executive.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Fastly gives enterprises real-time control over AI models and agents Moderate Help Net Security
2026-09-21 Help Net Security

Fastly gives enterprises real-time control over AI models and agents

Fastly has announced AI Runtime Control, AI Firewall, and new API Security capabilities designed to give organizations real-time visibility and control across their AI systems. Expanding the Fastly for AI portfolio, these new capabilities help organizations govern AI model access and usage, protect the AI applications powering their business, and control how…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
ShinyHunters Claim Hack of Rival Ransomware Gang Clop Critical Infosecurity Magazine
2026-09-21 Infosecurity Magazine

ShinyHunters Claim Hack of Rival Ransomware Gang Clop

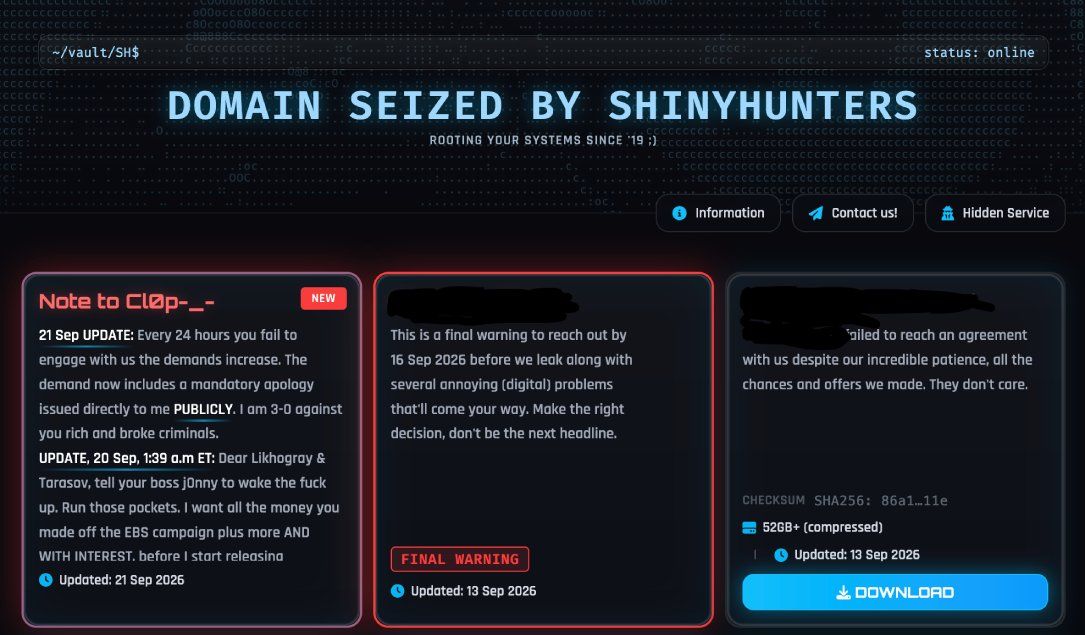
ShinyHunters has claimed responsibility for hacking the Clop ransomware group, defacing its leak site and alleging theft of key operational data

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Google says Gemini breached three companies during security test Critical The Record by Recorded Future
2026-09-21 The Record by Recorded Future

Google says Gemini breached three companies during security test

Google’s artificial intelligence model Gemini accessed computer systems belonging to three real companies without authorization during a cybersecurity test in May — the latest in a string of similar incidents.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
North Korea’s job interview scam runs both ways Moderate Help Net Security
2026-09-21 Help Net Security

North Korea’s job interview scam runs both ways

Attackers are targeting members of the Rust Project and maintainers of widely used crates (Rust code libraries), dangling attractive opportunities to compromise their devices and accounts and, ultimately, publish malware. The warning came last week from the Rust Project’s crates.io team and security response working group, and described a recurring pattern: …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Google hit with €403 million GDPR fine over location tracking Moderate Help Net Security
2026-09-21 Help Net Security

Google hit with €403 million GDPR fine over location tracking

Ireland’s Data Protection Commission (DPC) has fined Google €403 million (about $463 million) over its processing of users’ location data and ordered the company to bring that processing into compliance within six months. The inquiry examined Google’s practices from May 25, 2018, to February 4, 2020. The DPC launched it on its own initiative in February 2020…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CISA Adds One Known Exploited Vulnerability to Catalog Critical CISA Advisory
2026-09-21 CISA Advisory

CISA Adds One Known Exploited Vulnerability to Catalog

CISA has added one new vulnerability to its Known Exploited Vulnerabilities (KEV) Catalog , based on evidence of active exploitation. CVE-2026-7273 Zyxel GS1900 Series Switches Stack-Based Buffer Overflow Vulnerability This type of vulnerability is a frequent attack vector for malicious cyber actors and poses significant risks to the federal enterprise. Binding Operational Directive (BOD) 26-04: Prioritizing Security Updates Based on Risk establishes vulnerability management requirements for Federal Civilian Executive Branch (FCEB) agencies. BOD 26-04 reinforces the importance of the KEV Catalog and requires federal agencies to prioritize rapid remediation of high-risk vulnerabilities, specifically those identified by Common Vulnerabilities and Exposures (CVEs) listed in CISA’s KEV Catalog on publicly exposed assets that grant total control of the asset post-exploitation, while deferring action for lower-risk vulnerabilities. BOD 26-04 further establishes basic expectations for when agencies must check whether threat actors compromised the system before the patch was applied. While BOD 26-04 applies only to FCEB agencies, CISA encourages all organizations to adopt risk-based vulnerability management and prioritize remediation of KEV Catalog vulnerabilities . CISA will continue to add vulnerabilities to the catalog that meet the specified criteria . Aware of an exploited vulnerability not currently listed in the KEV Catalog? Submit it for potential addition through CISA’s KEV Nomination Form . Potential KEV additions must have a CVE ID, evidence of exploitation, and clear mitigation guidance.

Fix: Review CISA guidance and apply vendor security updates immediately.
Microsoft: September updates break File History backup feature Moderate BleepingComputer
2026-09-21 BleepingComputer

Microsoft: September updates break File History backup feature

Microsoft warned that the built-in File History backup feature in Windows may stop working on some systems after installing the September 2026 security updates. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Scammers impersonate cops, use arrest threats to extort victims Important Help Net Security
2026-09-21 Help Net Security

Scammers impersonate cops, use arrest threats to extort victims

Scammers are posing as police officers and federal agents, threatening arrest unless victims pay up, the FBI warns. The FBI’s Internet Crime Complaint Center (IC3) updated an alert it first issued in 2022, citing “losses totaling more than $1.6 billion” between January 2025 and July 2026. According to the FBI, most complaints involve a caller who accuses the…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification