
Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 5,807 advisories
Page 193 of 242
Smashing Security podcast #480: This is the AI service you should never sign up to Moderate Graham Cluley Security
2026-08-12 Graham Cluley Security

Smashing Security podcast #480: This is the AI service you should never sign up to

Would you like access to Anthropic's Claude at 90% off the normal price? All you have to do is redirect your traffic to a mysterious service called "Poison Claude". Only problem is that it's run by fraudsters... Meanwhile, a phishing-as-a-service platform called "Greatness" has come up with something rather nasty: a phishing attack that doesn't need a fake w…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
AI is Working in the SOC. So Why are Security Executives More Worried Than Ever? Moderate Rapid7 Threat Research
2026-08-12 Rapid7 Threat Research

AI is Working in the SOC. So Why are Security Executives More Worried Than Ever?

Something shifted in security operations over the last two years: AI stopped being a pilot program and became the plan. And if you survey 500 security professionals on whether that's going well – as Omdia did, commissioned by Rapid7 – you get a remarkable level of consensus: 97% report positive outcomes, 98% say AI reduces alert fatigue, and 95% say it's hel…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Microsoft Plugs Nearly 400 Security Holes Critical KrebsOnSecurity
2026-08-11 KrebsOnSecurity

Microsoft Plugs Nearly 400 Security Holes

Microsoft today released updates to remedy at least 398 security vulnerabilities in its Windows operating systems and supported software, including one weakness that is already being actively exploited and two others that were publicly detailed prior to today.

Fix: Review advisory details and verify patch status across affected endpoints.
Patch Tuesday - August 2026 Moderate CVE-2026-63520 Rapid7 Threat Research
2026-08-11 Rapid7 Threat Research

Patch Tuesday - August 2026

Microsoft is publishing 421 vulnerabilities on August 2026 Patch Tuesday , including 236 vulnerabilities in Windows. This is lower volume than last month’s record-breaking behemoth, but still one of the largest Patch Tuesday totals ever. There is no reason to suppose that Patch Tuesday will ever return to the lower volumes we saw prior to 2026. Microsoft is …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The August 2026 Security Update Review Critical CVE-2026-68820 Trend Micro ZDI
2026-08-11 Trend Micro ZDI

The August 2026 Security Update Review

I’ve successfully survived Hacker Summer Camp, and I have returned with a new outlook on patch density. When even Linus Torvalds says that huge updates are the “ new normal ”, it’s time to readjust what we consider a true bug apocalypse. This month’s release is thankfully smaller than last months, but still huge by historical standards. Take a break from you…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Shattering the Dream – When a Job Offer Becomes a Zero-Day Attack Critical CVE-2026-68820 Check Point Research
2026-08-11 Check Point Research

Shattering the Dream – When a Job Offer Becomes a Zero-Day Attack

Key Points Check Point Research is tracking a long‑running campaign called Operation Dream Job , targeting organizations worldwide, with a particular focus on the defense sector. The campaign is affiliated to DPRK-linked Lazarus group and its latest wave focuses on the defense sector in Europe and India. In the latest variant of the Operation Dream Job campa…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CVE-2026-63520: Microsoft SharePoint Remote Code Execution (FIXED) Critical CVE-2026-63520 Rapid7 Threat Research
2026-08-11 Rapid7 Threat Research

CVE-2026-63520: Microsoft SharePoint Remote Code Execution (FIXED)

Overview Rapid7 Labs conducted a zero-day research project against Microsoft SharePoint, resulting in the discovery of two new vulnerabilities that, when chained together, achieve unauthenticated remote code execution (RCE) against a vulnerable SharePoint server. Today, both Rapid7 and Microsoft are disclosing the second vulnerability in this chain, the RCE …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Head Mare APT is exploiting vulnerabilities in an unpatched TrueConf server to deliver PhantomCore and PhantomGraph to video conference participants Important Kaspersky Securelist
2026-08-11 Kaspersky Securelist

Head Mare APT is exploiting vulnerabilities in an unpatched TrueConf server to deliver PhantomCore and PhantomGraph to video conference participants

Overview of the attack In July 2026, Kaspersky experts detected a new attack by the Head Mare group. Previously, we classified them as hacktivists, but now we define them as an APT group due to the sophistication of their TTPs and the absence of destructive activity (encryption, wiping) in the targeted infrastructures. In this latest campaign, the attackers …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Project CAV3RN continues: Google Apps Script as C2 relay and DNS-based C2 channel selection Moderate Kaspersky Securelist
2026-08-11 Kaspersky Securelist

Project CAV3RN continues: Google Apps Script as C2 relay and DNS-based C2 channel selection

Project CAV3RN is a modular espionage framework used against targets in Israel. This report expands on two earlier publications: the first was published in June 2026 as part of our Kaspersky Threat Intelligence Reporting service , and the second was published on Securelist the following month, further documenting the framework’s evolving architecture and C2 …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Kimwolf v7: An Evolution of the Kimwolf Botnet Important Palo Alto Unit 42
2026-08-11 Palo Alto Unit 42

Kimwolf v7: An Evolution of the Kimwolf Botnet

Discover how Kimwolf v7 targets Android IoT devices with HTTP/2 DDoS fingerprinting, Ethereum ENS C2 resolution and Tor backup routing. The post Kimwolf v7: An Evolution of the Kimwolf Botnet appeared first on Unit 42 .

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The Permanent Threat: Analyzing Aeternum’s Blockchain-Based C2 Operations and Communications Moderate Palo Alto Unit 42
2026-08-10 Palo Alto Unit 42

The Permanent Threat: Analyzing Aeternum’s Blockchain-Based C2 Operations and Communications

Analysis of the Aeternum botnet loader, a threat leveraging Polygon blockchain smart contracts for decentralized C2 infrastructure and payload execution. The post The Permanent Threat: Analyzing Aeternum’s Blockchain-Based C2 Operations and Communications appeared first on Unit 42 .

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
10th August – Threat Intelligence Report Moderate CVE-2026-12537 Check Point Research
2026-08-10 Check Point Research

10th August – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 10th August, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES North Carolina Ports, the US authority operating the ports of Wilmington, Morehead City and others, has suffered a cyberattack that forced some operations onto manual processes. The authority claims it has conta…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Inside the Modern SOC: The Identity Front Door Moderate Palo Alto Unit 42
2026-08-07 Palo Alto Unit 42

Inside the Modern SOC: The Identity Front Door

Identity-based attacks drive 90% of incidents. Learn how modern attackers exploit identities and what SOC leaders can do to respond. The post Inside the Modern SOC: The Identity Front Door appeared first on Unit 42 .

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Beware cut-price AI services that read your every word Moderate Graham Cluley Security
2026-08-07 Graham Cluley Security

Beware cut-price AI services that read your every word

f someone offered you 90% off the official price to access Claude, the powerful AI model from Anthropic, would you be tempted? It turns out that around 900 people were, and they may be regretting their decision. Read more in my article on the Fortra blog.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The Good, the Bad and the Ugly in Cybersecurity – Week 32 Moderate SentinelOne Threat Labs
2026-08-07 SentinelOne Threat Labs

The Good, the Bad and the Ugly in Cybersecurity – Week 32

The Good | Snowflake Hacker Pleads Guilty as Ransom Cartel Creator Draws 16 Years Connor Riley Moucka pleaded guilty in Seattle federal court this week to computer fraud, wire fraud, aggravated identity theft and conspiracy over the 2024 breaches of Snowflake customer accounts. The intrusions reached at least 165 organizations and exposed records tied to at …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
ChainDrop: Inside a Self-Propagating npm Worm Moderate Palo Alto Unit 42
2026-08-06 Palo Alto Unit 42

ChainDrop: Inside a Self-Propagating npm Worm

Analysis of ChainDrop, an npm supply chain worm extracting GitHub Actions runner secrets and using Ethereum smart contracts for C2 routing. The post ChainDrop: Inside a Self-Propagating npm Worm appeared first on Unit 42 .

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
When Agentic Glue Melts: Exploiting Cloudflare Code Mode and Workers Important Check Point Research
2026-08-06 Check Point Research

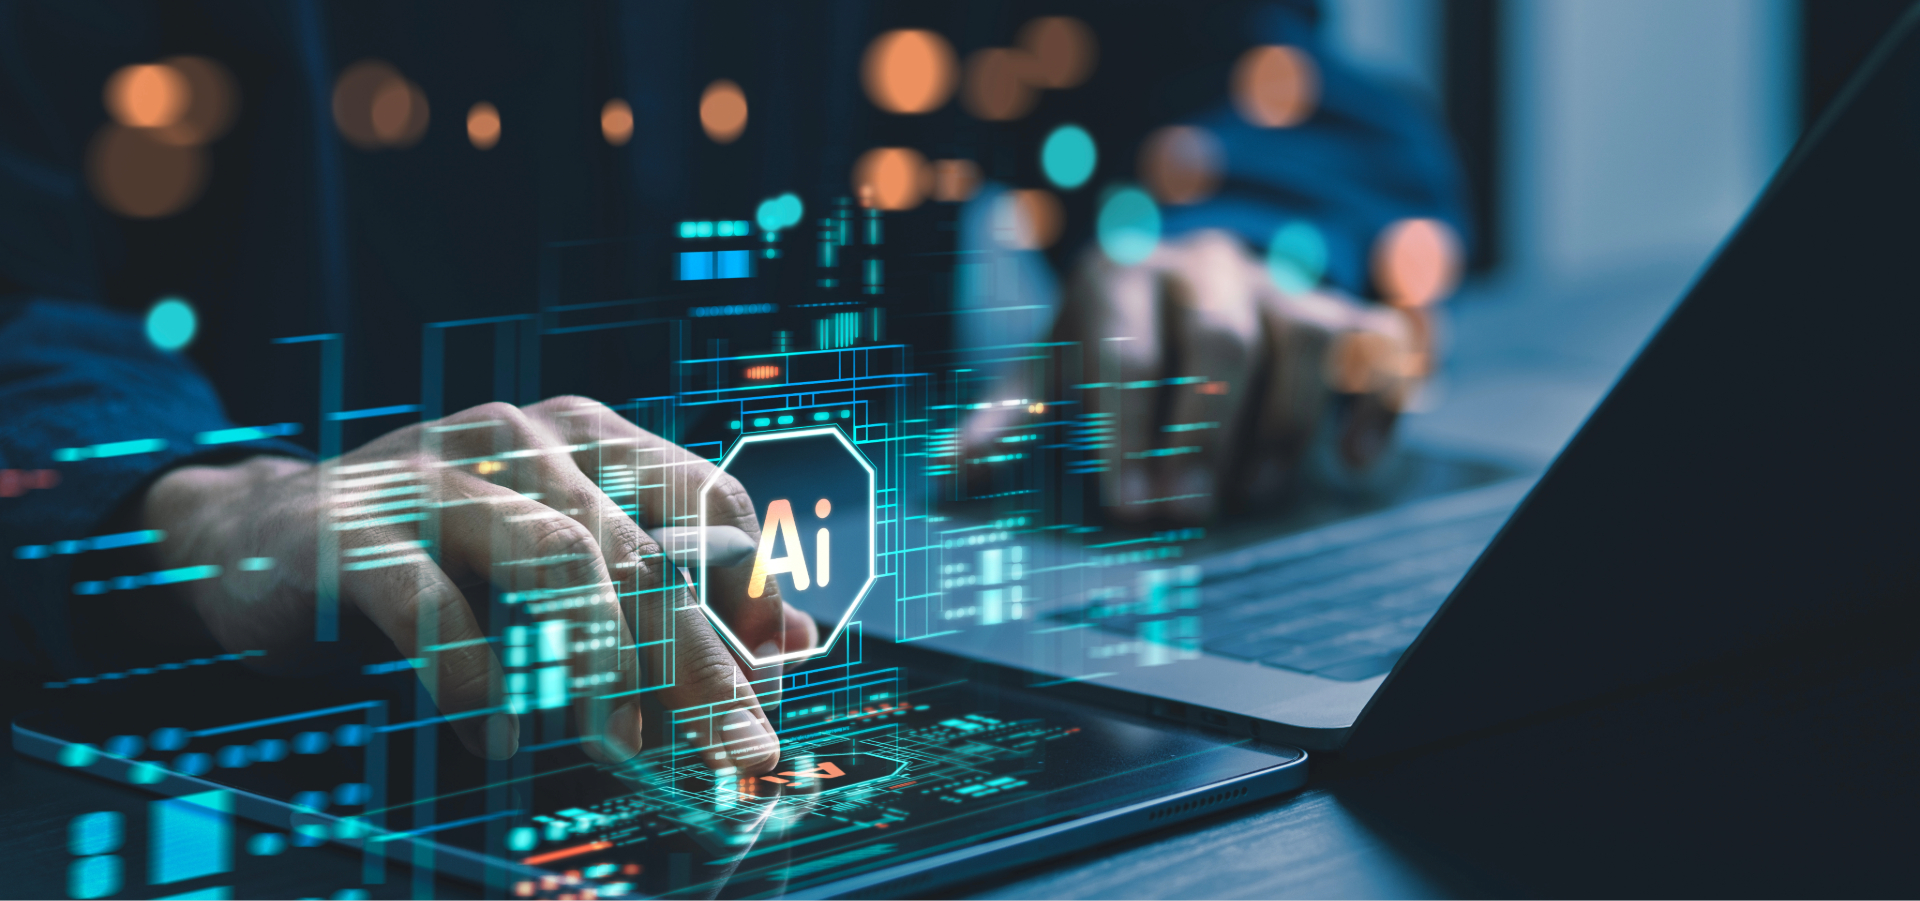
When Agentic Glue Melts: Exploiting Cloudflare Code Mode and Workers

By Yarden Porat, Check Point Research Key Points Check Point Research analyzed Cloudflare Code Mode, a technique that changes how AI agents use MCP by turning tools into a TypeScript API the model can write code against. The research uncovered five vulnerabilities in workerd, the open-source runtime behind Code Mode and Cloudflare Workers. Two were rated Cri…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Canadian Man Pleads Guilty in Snowflake Extortions Moderate KrebsOnSecurity
2026-08-06 KrebsOnSecurity

Canadian Man Pleads Guilty in Snowflake Extortions

A 26-year-old Canadian man once described as one of the most consequential cybercrime threat actors of 2024 has pleaded guilty to computer fraud and conspiracy to hack and extort more than 165 organizations that used the cloud data storage provider Snowflake. Connor Riley Moucka, of Kitchener, Ontario, also admitted to stealing call and text history records of more than 100 million AT&T custo...

Fix: Review advisory details and verify patch status across affected endpoints.
How we took malware advisories beyond npm Important GitHub Security Blog
2026-08-06 GitHub Security Blog

How we took malware advisories beyond npm

A compromised package can steal credentials the moment you install it, and until recently, GitHub could only flag those in npm. Not anymore. This is the story of how the supply chain engineering team behind Dependabot expanded malware advisories to eight ecosystems by building on OpenSSF’s shared malicious packages data. Here’s where things stand: earlier th…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Apple’s bug bounty program is drowning in so much AI slop, it is in danger of missing serious exploits Important Graham Cluley Security
2026-08-06 Graham Cluley Security

Apple’s bug bounty program is drowning in so much AI slop, it is in danger of missing serious exploits

Apple has imposed strict new submission limits on its bug bounty portal after finding itself overwhelmed by low-quality, AI generated vulnerability reports - many of which were found to be describing security flaws that simply didn't exist. Read more in my article on the Hot for Security blog.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Token Jacking: Cybercriminals Could Be Stealing Your AI Resources Critical Palo Alto Unit 42
2026-08-06 Palo Alto Unit 42

Token Jacking: Cybercriminals Could Be Stealing Your AI Resources

Discover how attackers hijack AI tokens to fuel gray market transfer stations by stealing developer API keys. The post Token Jacking: Cybercriminals Could Be Stealing Your AI Resources appeared first on Unit 42 .

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Smashing Security podcast #479: How a fake police officer nearly stole Graham’s cryptocurrency Moderate Graham Cluley Security
2026-08-05 Graham Cluley Security

Smashing Security podcast #479: How a fake police officer nearly stole Graham’s cryptocurrency

Graham gets a phone call from the police. Well, someone who sounds convincingly like the police. There's just one small problem: what they really want is the 24-word seed key to Graham's cryptocurrency wallet. Meanwhile, if you've stayed in a hotel recently, the free Wi-Fi you connected to might have come with an unexpected extra: an all-you-can-eat buffet o…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
From Input to Impact: Secure AI Where It Runs Moderate SentinelOne Threat Labs
2026-08-04 SentinelOne Threat Labs

From Input to Impact: Secure AI Where It Runs

AI agents have made their way into virtually every layer of your environment. They run in the apps your employees adopt, on the endpoints where agents execute code, as users with access privileges those agents borrow, and in the cloud workloads that scale them. The platform that you trust to secure your endpoints is already already covering where AI operates…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification