Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 5,807 advisories
Page 20 of 242
EPICS Base Important CISA Advisory
2026-10-27 CISA Advisory

EPICS Base

View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to cause a denial-of-service condition, corrupt memory, disclose sensitive information, or potentially execute arbitrary code. The following versions of EPICS Base are affected: EPICS Base release CVSS Vendor Equipment v3 9.8 The EPICS Community EPICS Base release 3 Vulnerabilities Integer Overflow or Wraparound, Improper Handling of Length Parameter Inconsistency, Access of Resource Using Incompatible Type ('Type Confusion') Background Critical Infrastructure Sectors: Critical Manufacturing Countries/Areas Deployed: Worldwide Company Headquarters Location: Global Vulnerabilities Expand All + CVE-2026-114595 In EPICS Base release 7.0.10 and prior, an integer overflow in network request processing can cause memory to be allocated with an incorrect size. Subsequent handling of attacker supplied data may result in memory corruption, denial of service, or potential remote code execution. Read More 1 Affected Product The EPICS Community EPICS Base release: Product Status: known_affected Remediations Mitigation The EPICS Community has made available updates to the epics-base GitHub repositories. Affected users should update to the 7.0.11 release. For more information, users should contact the EPICS Controls team https://epics-controls.org/support/. Mitigation https://github.com/epics-base/epics-base/pull/934 Mitigation https://github.com/epics-base/epics-base/pull/937 Mitigation https://github.com/epics-base/pvDataCPP/pull/109 Additional Metrics Relevant CWE: CWE-190 Integer Overflow or Wraparound CVSS Version Base Score Base Severity Vector String 3.1 9.8 CRITICAL CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H 4.0 9.3 CRITICAL CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N View CVE Details CVE-2026-114596 In EPICS Base release 7.0.10 and prior, an improper validation of message length values during protocol parsing can trigger an integer overflow, resulting in an out-of-bounds memory write. Successful exploitation can cause process instability or denial of service. Read More 2 Affected Products The EPICS Community EPICS Base release: Product Status: known_affected Remediations Mitigation The EPICS Community has made available updates to the epics-base GitHub repositories. Affected users should update to the 7.0.11 release. For more information, users should contact the EPICS Controls team https://epics-controls.org/support/. Mitigation https://github.com/epics-base/epics-base/pull/934 Mitigation https://github.com/epics-base/epics-base/pull/937 Mitigation https://github.com/epics-base/pvDataCPP/pull/109 The EPICS Community EPICS Base release: Product Status: known_affected Remediations Mitigation The EPICS Community has made available updates to the epics-base GitHub repositories. Affected users should update to the 7.0.11 release. For more information, users should contact the EPICS Controls team https://epics-controls.org/support/. Mitigation https://github.com/epics-base/epics-base/pull/934 Mitigation https://github.com/epics-base/epics-base/pull/937 Mitigation https://github.com/epics-base/pvDataCPP/pull/109 Additional Metrics Relevant CWE: CWE-190 Integer Overflow or Wraparound CVSS Version Base Score Base Severity Vector String 3.1 8.2 HIGH CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:L/A:H 4.0 8.8 HIGH CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:N/VI:L/VA:H/SC:N/SI:N/SA:N View CVE Details CVE-2026-114597 In EPICS Base release 7.0.10 and prior, an insufficient validation of element or length values in a network message can cause the application to read beyond the bounds of an allocated buffer. This may lead to denial of service and could expose adjacent memory contents. Read More 3 Affected Products The EPICS Community EPICS Base release: Product Status: known_affected Remediations Mitigation The EPICS Community has made available updates to the epics-base GitHub repositories. Affected users should update to the 7.0.11 release. For more information, users should contact the EPICS Controls team https://epics-controls.org/support/. Mitigation https://github.com/epics-base/epics-base/pull/934 Mitigation https://github.com/epics-base/epics-base/pull/937 Mitigation https://github.com/epics-base/pvDataCPP/pull/109 The EPICS Community EPICS Base release: Product Status: known_affected Remediations Mitigation The EPICS Community has made available updates to the epics-base GitHub repositories. Affected users should update to the 7.0.11 release. For more information, users should contact the EPICS Controls team https://epics-controls.org/support/. Mitigation https://github.com/epics-base/epics-base/pull/934 Mitigation https://github.com/epics-base/epics-base/pull/937 Mitigation https://github.com/epics-base/pvDataCPP/pull/109 The EPICS Community EPICS Base release: Product Status: known_affected Remediations Mitigation The EPICS Community has made available updates to the epics-base GitHub repositories. Affected users should update to the 7.0.11 release. For more information, users should contact the EPICS Controls team https://epics-controls.org/support/. Mitigation https://github.com/epics-base/epics-base/pull/934 Mitigation https://github.com/epics-base/epics-base/pull/937 Mitigation https://github.com/epics-base/pvDataCPP/pull/109 Additional Metrics Relevant CWE: CWE-130 Improper Handling of Length Parameter Inconsistency CVSS Version Base Score Base Severity Vector String 3.1 7.5 HIGH CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:H 4.0 8.7 HIGH CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:N/VI:N/VA:H/SC:N/SI:N/SA:N View CVE Details CVE-2026-114598 In EPICS Base release 7.0.10 and prior, an insufficient validation of element or length values in a network message can cause the application to read beyond the bounds of an allocated buffer. This may lead to denial of service and could expose adjacent memory contents. Read More 4 Affected Products The EPICS Community EPICS Base release: Product Status: known_affected Remediations Mitigation The EPICS Community has made available updates to the epics-base GitHub repositories. Affected users should update to the 7.0.11 release. For more information, users should contact the EPICS Controls team https://epics-controls.org/support/. Mitigation https://github.com/epics-base/epics-base/pull/934 Mitigation https://github.com/epics-base/epics-base/pull/937 Mitigation https://github.com/epics-base/pvDataCPP/pull/109 The EPICS Community EPICS Base release: Product Status: known_affected Remediations Mitigation The EPICS Community has made available updates to the epics-base GitHub repositories. Affected users should update to the 7.0.11 release. For more information, users should contact the EPICS Controls team https://epics-controls.org/support/. Mitigation https://github.com/epics-base/epics-base/pull/934 Mitigation https://github.com/epics-base/epics-base/pull/937 Mitigation https://github.com/epics-base/pvDataCPP/pull/109 The EPICS Community EPICS Base release: Product Status: known_affected Remediations Mitigation The EPICS Community has made available updates to the epics-base GitHub repositories. Affected users should update to the 7.0.11 release. For more information, users should contact the EPICS Controls team https://epics-controls.org/support/. Mitigation https://github.com/epics-base/epics-base/pull/934 Mitigation https://github.com/epics-base/epics-base/pull/937 Mitigation https://github.com/epics-base/pvDataCPP/pull/109 The EPICS Community EPICS Base release: Product Status: known_affected Remediations Mitigation The EPICS Community has made available updates to the epics-base GitHub repositories. Affected users should update to the 7.0.11 release. For more information, users should contact the EPICS Controls team https://epics-controls.org/support/. Mitigation https://github.com/epics-base/epics-base/pull/934 Mitigation https://github.com/epics-base/epics-base/pull/937 Mitigation https://github.com/epics-base/pvDataCPP/pull/109 Additional Metrics Relevant CWE: CWE-843 Access of Resource Using Incompatible Type ('Type Confusion') CVSS Version Base Score Base Severity Vector String 3.1 7.5 HIGH CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:H 4.0 8.7 HIGH CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:N/VI:N/VA:H/SC:N/SI:N/SA:N View CVE Details Acknowledgments Shubham Raj of Cipher / Causal Security reported these vulnerabilities to CISA. Recommended Practices CISA recommends users take defensive measures to minimize the risk of exploitation of these vulnerabilities. Minimize network exposure for all control system devices and/or systems, ensuring they are not accessible from the internet . Locate control system networks and remote devices behind firewalls and isolating them from business networks. When remote access is required, use more secure methods, such as Virtual Private Networks (VPNs), recognizing VPNs may have vulnerabilities and should be updated to the most current version available. Also recognize VPN is only as secure as the connected devices. CISA reminds organizations to perform proper impact analysis and risk assessment prior to deploying defensive measures. CISA also provides a section for control systems security recommended practices on the ICS webpage on cisa.gov/ics . Several CISA products detailing cyber defense best practices are available for reading and download, including Improving Industrial Control Systems Cybersecurity with Defense-in-Depth Strategies . CISA encourages organizations to implement recommended cybersecurity strategies for proactive defense of ICS assets . Additional mitigation guidance and recommended practices are publicly available on the ICS webpage at cisa.gov/ics in the technical information paper, ICS-TIP-12-146-01B--Targeted Cyber Intrusion Detection and Mitigation Strategies . Organizations observing suspected malicious activity should follow established internal procedures and report findings to CISA for tracking and correlation against other incidents. CISA also recommends users take the following measures to protect themselves from social engineering attacks: Do not click web links or open attachments in unsolicited email messages. Refer to Recognizing and Avoiding Email Scams for more information on avoiding email scams. Refer to Avoiding Social Engineering and Phishing Attacks for more information on social engineering attacks. No known public exploitation specifically targeting these vulnerabilities has been reported to CISA at this time. Revision History Initial Release Date: 2026-10-27 Date Revision Summary 2026-10-27 1 Initial Publication Legal Notice and Terms of Use

Fix: Review CISA guidance and apply vendor security updates immediately.
Samsung TVs without mics may listen through soundbars, researcher says Moderate Malwarebytes Labs
2026-10-27 Malwarebytes Labs

Samsung TVs without mics may listen through soundbars, researcher says

A reverse engineer claims that their Samsung smart TV has been collecting audio without their consent. The researcher, who calls themselves “log4j,” said in an X thread that their 2025 Samsung TV was delivering ads that seemed suspiciously relevant to them. Investigating, they claim to have found a package called “always on voice,” which uses the TV’s built-…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
From federal SOCs to Talos: Ryan Fetterman on practical security research Moderate Cisco Talos Intelligence
2026-10-27 Cisco Talos Intelligence

From federal SOCs to Talos: Ryan Fetterman on practical security research

What does it mean to be "blue collar" for the blue team? Amy sat down with security researcher Ryan Fetterman to discuss his journey from federal agency work to his new role at Talos. He shares the realities of detection engineering — including the creative, often frustrating ways attackers evolve their tactics to stay one step ahead of traditional defenses.…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Watchdog Urges Police and Fire Service to Improve Cybersecurity Moderate Infosecurity Magazine
2026-10-27 Infosecurity Magazine

Watchdog Urges Police and Fire Service to Improve Cybersecurity

UK police forces and fire and rescue services have been urged to strengthen cybersecurity as rising cyber threats outpace current defenses

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
So Many AI Security Benchmarks, but None Tell the Whole Story Moderate Dark Reading
2026-10-27 Dark Reading

So Many AI Security Benchmarks, but None Tell the Whole Story

Measuring artificial intelligence model security gets complex, fast, thanks to a growing patchwork of benchmarks targeting different variables in the equation. But none replace testing against your own code and workflows.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Apple Patches for October 2026, (Mon, Oct 26th) Moderate SANS Internet Storm Center
2026-10-26 SANS Internet Storm Center

Apple Patches for October 2026, (Mon, Oct 26th)

Apple today released patches for 304 vulnerabilties. This number is still in line with prior Apple updates, and comes just about a month after the last apple update.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
University of Copenhagen data breach exposes data of 525,000 people Critical BleepingComputer
2026-10-26 BleepingComputer

University of Copenhagen data breach exposes data of 525,000 people

The University of Copenhagen in Denmark confirmed that hackers accessed one of its test environments containing personal data belonging to 525,000 people. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Cross-request KV cache exposure in the GLM-5.3 Workers AI model, and our remediation with SGLang Moderate Cloudflare Security
2026-10-26 Cloudflare Security

Cross-request KV cache exposure in the GLM-5.3 Workers AI model, and our remediation with SGLang

On September 8, 2026, we were alerted by a security researcher, Gadi Evron from Knostic , to a tenant isolation issue affecting the GLM-5.3 Workers AI model ( @cf/zai-org/glm-5.3 ) starting on August 27, 2026. We have remediated the issue, and we restored the model on September 9. We have confirmed that no other model hosted on Workers AI was affected. Betwe…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Risks & Rewards: How AI Is Redefining the CISO's Role Moderate Dark Reading
2026-10-26 Dark Reading

Risks & Rewards: How AI Is Redefining the CISO's Role

Nvidia security executive Mark Weatherford says CISOs must help business leaders weigh AI's pros and cons, and ensure those deploying it own the risks.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Former pentester used ARTEX AI to steal 8.2 million data records Moderate BleepingComputer
2026-10-26 BleepingComputer

Former pentester used ARTEX AI to steal 8.2 million data records

South Korean police identified seven suspects linked to a cybercrime operation that breached more than 90 organizations in the country, with ARTEX AI pentesting framework used in most of the attacks. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
In-the-Wild Attack Abuses AI Agents' Trust in Markdown Important Dark Reading
2026-10-26 Dark Reading

In-the-Wild Attack Abuses AI Agents' Trust in Markdown

A new AI agent prompt injection technique exploits how coding assistants consume local instruction files, blurring the line between text documents and executable actions.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
OpenAI launches GPT-6.1 Terra with 3x faster AI agents, 50% lower pricing Moderate BleepingComputer
2026-10-26 BleepingComputer

OpenAI launches GPT-6.1 Terra with 3x faster AI agents, 50% lower pricing

OpenAI has launched GPT-6.1 Terra, a new model focused on computer use, visual reasoning, coding, and everyday work, while costing significantly less than its larger models. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Magento Campaign Infects 953 Online Stores Across Five Domains Moderate CVE-2026-48356 SecurityAffairs
2026-10-26 SecurityAffairs

Magento Campaign Infects 953 Online Stores Across Five Domains

Sansec tracks a Magento skimmer campaign that infected 953 stores, using five domains, bot filtering and malicious code hidden in CMS blocks. A criminal group has infected 953 online stores since July 2025, mostly Magento shops, according to Sansec researchers. The attackers add a small piece of code to store pages. When someone visits a shop, their browser …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
DreamHost forces password resets in ongoing "incident" Critical BleepingComputer
2026-10-26 BleepingComputer

DreamHost forces password resets in ongoing "incident"

DreamHost has forced password resets for email and FTP/SFTP users following an incident that disrupted connections to the File Manager interface. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Hackers Infect 953 Online Stores With Scanner-Evading JavaScript, Mostly on Magento Important The Hacker News
2026-10-26 The Hacker News

Hackers Infect 953 Online Stores With Scanner-Evading JavaScript, Mostly on Magento

An unknown threat actor has infected 953 online stores, most of them running Magento, as part of a long-running campaign active since July 2025. According to Dutch e-commerce security company Sansec, the activity is designed to add a small piece of code to the store's pages that, when visited by unsuspecting users, serves malicious JavaScript loader code thr…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
PHP Issues Second Windows Security Update in Five Days to Fix Brotli Code Execution Flaw Important CVE-2026-111497 The Hacker News
2026-10-26 The Hacker News

PHP Issues Second Windows Security Update in Five Days to Fix Brotli Code Execution Flaw

PHP has rebuilt its official Windows packages for PHP 8.2 through 8.5 to fix CVE-2026-111497, a flaw in the Brotli compression library that the packages include. The flaw can let an attacker corrupt memory and potentially run code. PHP says the flaw can be reached through the cURL extension when the extension decompresses HTTP responses automatically. cURL l…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
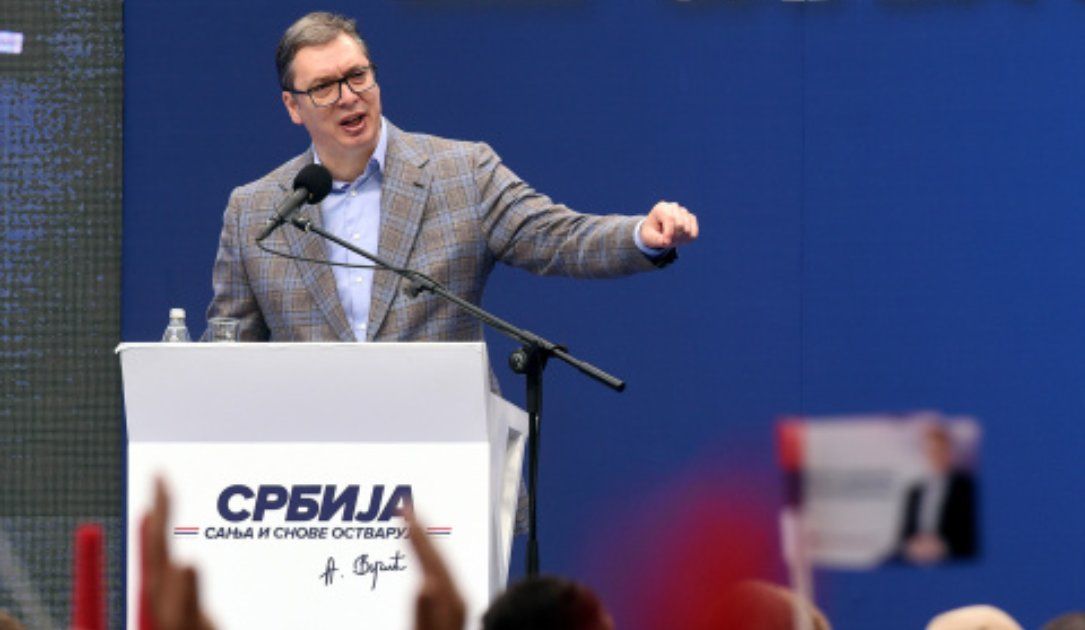
Serbian autocrat loses election following widespread reports of digital repression Moderate The Record by Recorded Future
2026-10-26 The Record by Recorded Future

Serbian autocrat loses election following widespread reports of digital repression

Serbian strongman leader Aleksandar Vučić on Sunday admitted defeat in his race for prime minister, a loss that follows a series of incidents of digital repression that galvanized the opposition.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification