Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 5,807 advisories
Page 32 of 242
Critical RCE vulnerabilities in PHP (CVE-2026-109618, CVE-2026-109619) Critical CVE-2026-109618 Kaspersky Securelist
2026-10-21 Kaspersky Securelist

Critical RCE vulnerabilities in PHP (CVE-2026-109618, CVE-2026-109619)

UPD 23.10.2026 : added Kaspersky SIEM rules and events for developing custom detection rules or conducting threat hunting. UPD 22.10.2026 : added a description of how the Kaspersky Managed Detection and Response service detects the described malicious activity. UPD 22.10.2026 : added a description of how Kaspersky Vulnerability Management detects vulnerable …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Two critical RCEs in PHP core Critical CVE-2026-109618 Cisco Talos Intelligence
2026-10-21 Cisco Talos Intelligence

Two critical RCEs in PHP core

Update 10/22: Added section detailing observations of in the wild exploitation and associated IOCs. Cisco Talos is tracking the disclosure of two unauthenticated remote code execution (RCE) flaws in PHP core, dubbed “php2shell”, triggered by a plain HTTP request and exploitable before any application code runs, affecting every PHP build since 5.4. Based on t…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Russian hackers teamed up to wipe data at Ukrainian grain firm Important The Record by Recorded Future
2026-10-21 The Record by Recorded Future

Russian hackers teamed up to wipe data at Ukrainian grain firm

The Russian state-linked hacking group Sandworm collaborated with another threat actor to carry out a destructive cyberattack against a Ukrainian grain logistics company last year, researchers said Thursday.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

eMudhra security blunder left trusted CA signing keys exposed to anyone Moderate Help Net Security
2026-10-21 Help Net Security

eMudhra security blunder left trusted CA signing keys exposed to anyone

Eight intermediate certificates issued by Indian certificate authority eMudhra were secured with private keys so weak that anyone could recover them from the public certificates in under a second. On its website, the company highlights that it has issued more than 60 million digital certificates. A security researcher known as Wayne discovered the flaw on Oc…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Introducing full transaction detection for Cloudflare WAF Moderate Cloudflare Security
2026-10-21 Cloudflare Security

Introducing full transaction detection for Cloudflare WAF

Today, we are expanding our web application firewall (WAF) by adding two new capabilities: full transaction detections and response rules. Full transaction detections evaluate each HTTP request alongside its response to identify evidence of exploitation. It helps answer both "Does this request look malicious?" and "What happened when the application handled …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
PHP ships emergency patches for critical PHP2Shell flaws Critical CVE-2026-109618 BleepingComputer
2026-10-21 BleepingComputer

PHP ships emergency patches for critical PHP2Shell flaws

The PHP security team released emergency security patches for two critical remote code execution (RCE) vulnerabilities (CVE-2026-109618 and CVE-2026-109619) tracked collectively as PHP2Shell. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
“Next Exploit Opportunities”: How a Threat Actor Used AI to Help Plan and Execute Multiple Types of Cybercrime Activities Important Palo Alto Unit 42
2026-10-21 Palo Alto Unit 42

“Next Exploit Opportunities”: How a Threat Actor Used AI to Help Plan and Execute Multiple Types of Cybercrime Activities

An investigation into a threat actor bypassing AI safety controls to coordinate credential theft, VoIP fraud planning, and database exfiltration. The post “Next Exploit Opportunities”: How a Threat Actor Used AI to Help Plan and Execute Multiple Types of Cybercrime Activities appeared first on Unit 42 .

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

ClickFix has never been bigger, and AI tools are its most convincing lure yet Moderate BleepingComputer
2026-10-21 BleepingComputer

ClickFix has never been bigger, and AI tools are its most convincing lure yet

ClickFix attacks are surging as cybercriminals use fake AI installers, malicious search results, and trusted chatbot platforms to trick users into executing malware. Push Security examines how these attacks evade traditional defenses and why AI tools have become increasingly effective lures. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
PHP Issues Emergency Patches for Two Critical PHP2Shell RCE Flaws as Exploit Attempts Emerge Critical The Hacker News
2026-10-21 The Hacker News

PHP Issues Emergency Patches for Two Critical PHP2Shell RCE Flaws as Exploit Attempts Emerge

PHP has released emergency updates that fix two critical flaws in the language itself, letting an attacker without an account run code on a web server. The fixes are in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, and the PHP team says only updating fully protects a server. The flaws, together called PHP2Shell, sit in the PHP runtime, not in any application, so a …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

CVE-2026-97783 Microsoft Office SharePoint Spoofing Vulnerability Moderate CVE-2026-97783 Microsoft MSRC
2026-10-21 Microsoft MSRC

CVE-2026-97783 Microsoft Office SharePoint Spoofing Vulnerability

The vulnerability associated with this CVE was fixed in July, however was inadvertently not included with that release. Microsoft recommends updating to the most current release of the SharePoint server.

Fix: Deploy cumulative update via Windows Update or Microsoft Update Catalog.
Cloudflare deploys protections against php2shell vulnerability Critical CVE-2026-115560 Cloudflare Security
2026-10-21 Cloudflare Security

Cloudflare deploys protections against php2shell vulnerability

Update - On October 23, the PHP project published an informational advisory for a related vulnerability, CVE-2026-115560, in PHP's session upload progress feature. It affects fully patched PHP releases, including 8.5.12, and will be fixed in PHP's next regular release. All Cloudflare WAF customers are protected against known exploit attempts if their site us…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
NVIDIA unveils security architecture that can stop AI agents crossing set boundaries Moderate Help Net Security
2026-10-21 Help Net Security

NVIDIA unveils security architecture that can stop AI agents crossing set boundaries

NVIDIA’s OpenShell Reference Architecture is designed to help businesses control AI agents operating across enterprise infrastructure and local computing systems. It builds on NVIDIA’s existing OpenShell security software, combining it with hardware for running AI models, managing agent operations and enforcing security rules. The aim is to let agents carry …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
PHP2Shell: Critical PHP vulnerabilities patched, update now! Critical CVE-2026-109618 Help Net Security
2026-10-21 Help Net Security

PHP2Shell: Critical PHP vulnerabilities patched, update now!

The PHP development team has released emergency security updates to fix PHP2Shell, two critical vulnerabilities (CVE-2026-109618 and CVE-2026-109619) that could let attackers execute code remotely on web servers without logging in. The fixes are in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, and the team is strongly urging all PHP users to update immediately. “Th…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Google Chrome Adds ClickFix Warnings to Stop Users From Running Malicious Commands Moderate The Hacker News
2026-10-21 The Hacker News

Google Chrome Adds ClickFix Warnings to Stop Users From Running Malicious Commands

Google on Tuesday said it's rolling out improved safeguards in its Chrome browser to secure users against ClickFix attacks when Enhanced Protection is enabled. ClickFix is a popular social engineering technique in which bad actors trick users into copying and pasting malicious code directly into their computer's operating system, thereby bypassing convention…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Decades-Old Windows Utility Powers Modern ClickFix Attack Important Dark Reading
2026-10-21 Dark Reading

Decades-Old Windows Utility Powers Modern ClickFix Attack

The attack uses malicious Google search results related to Amazon and leverages the "finger" utility to launch a CAPTCHA that installs malware, including the Lumma stealer.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
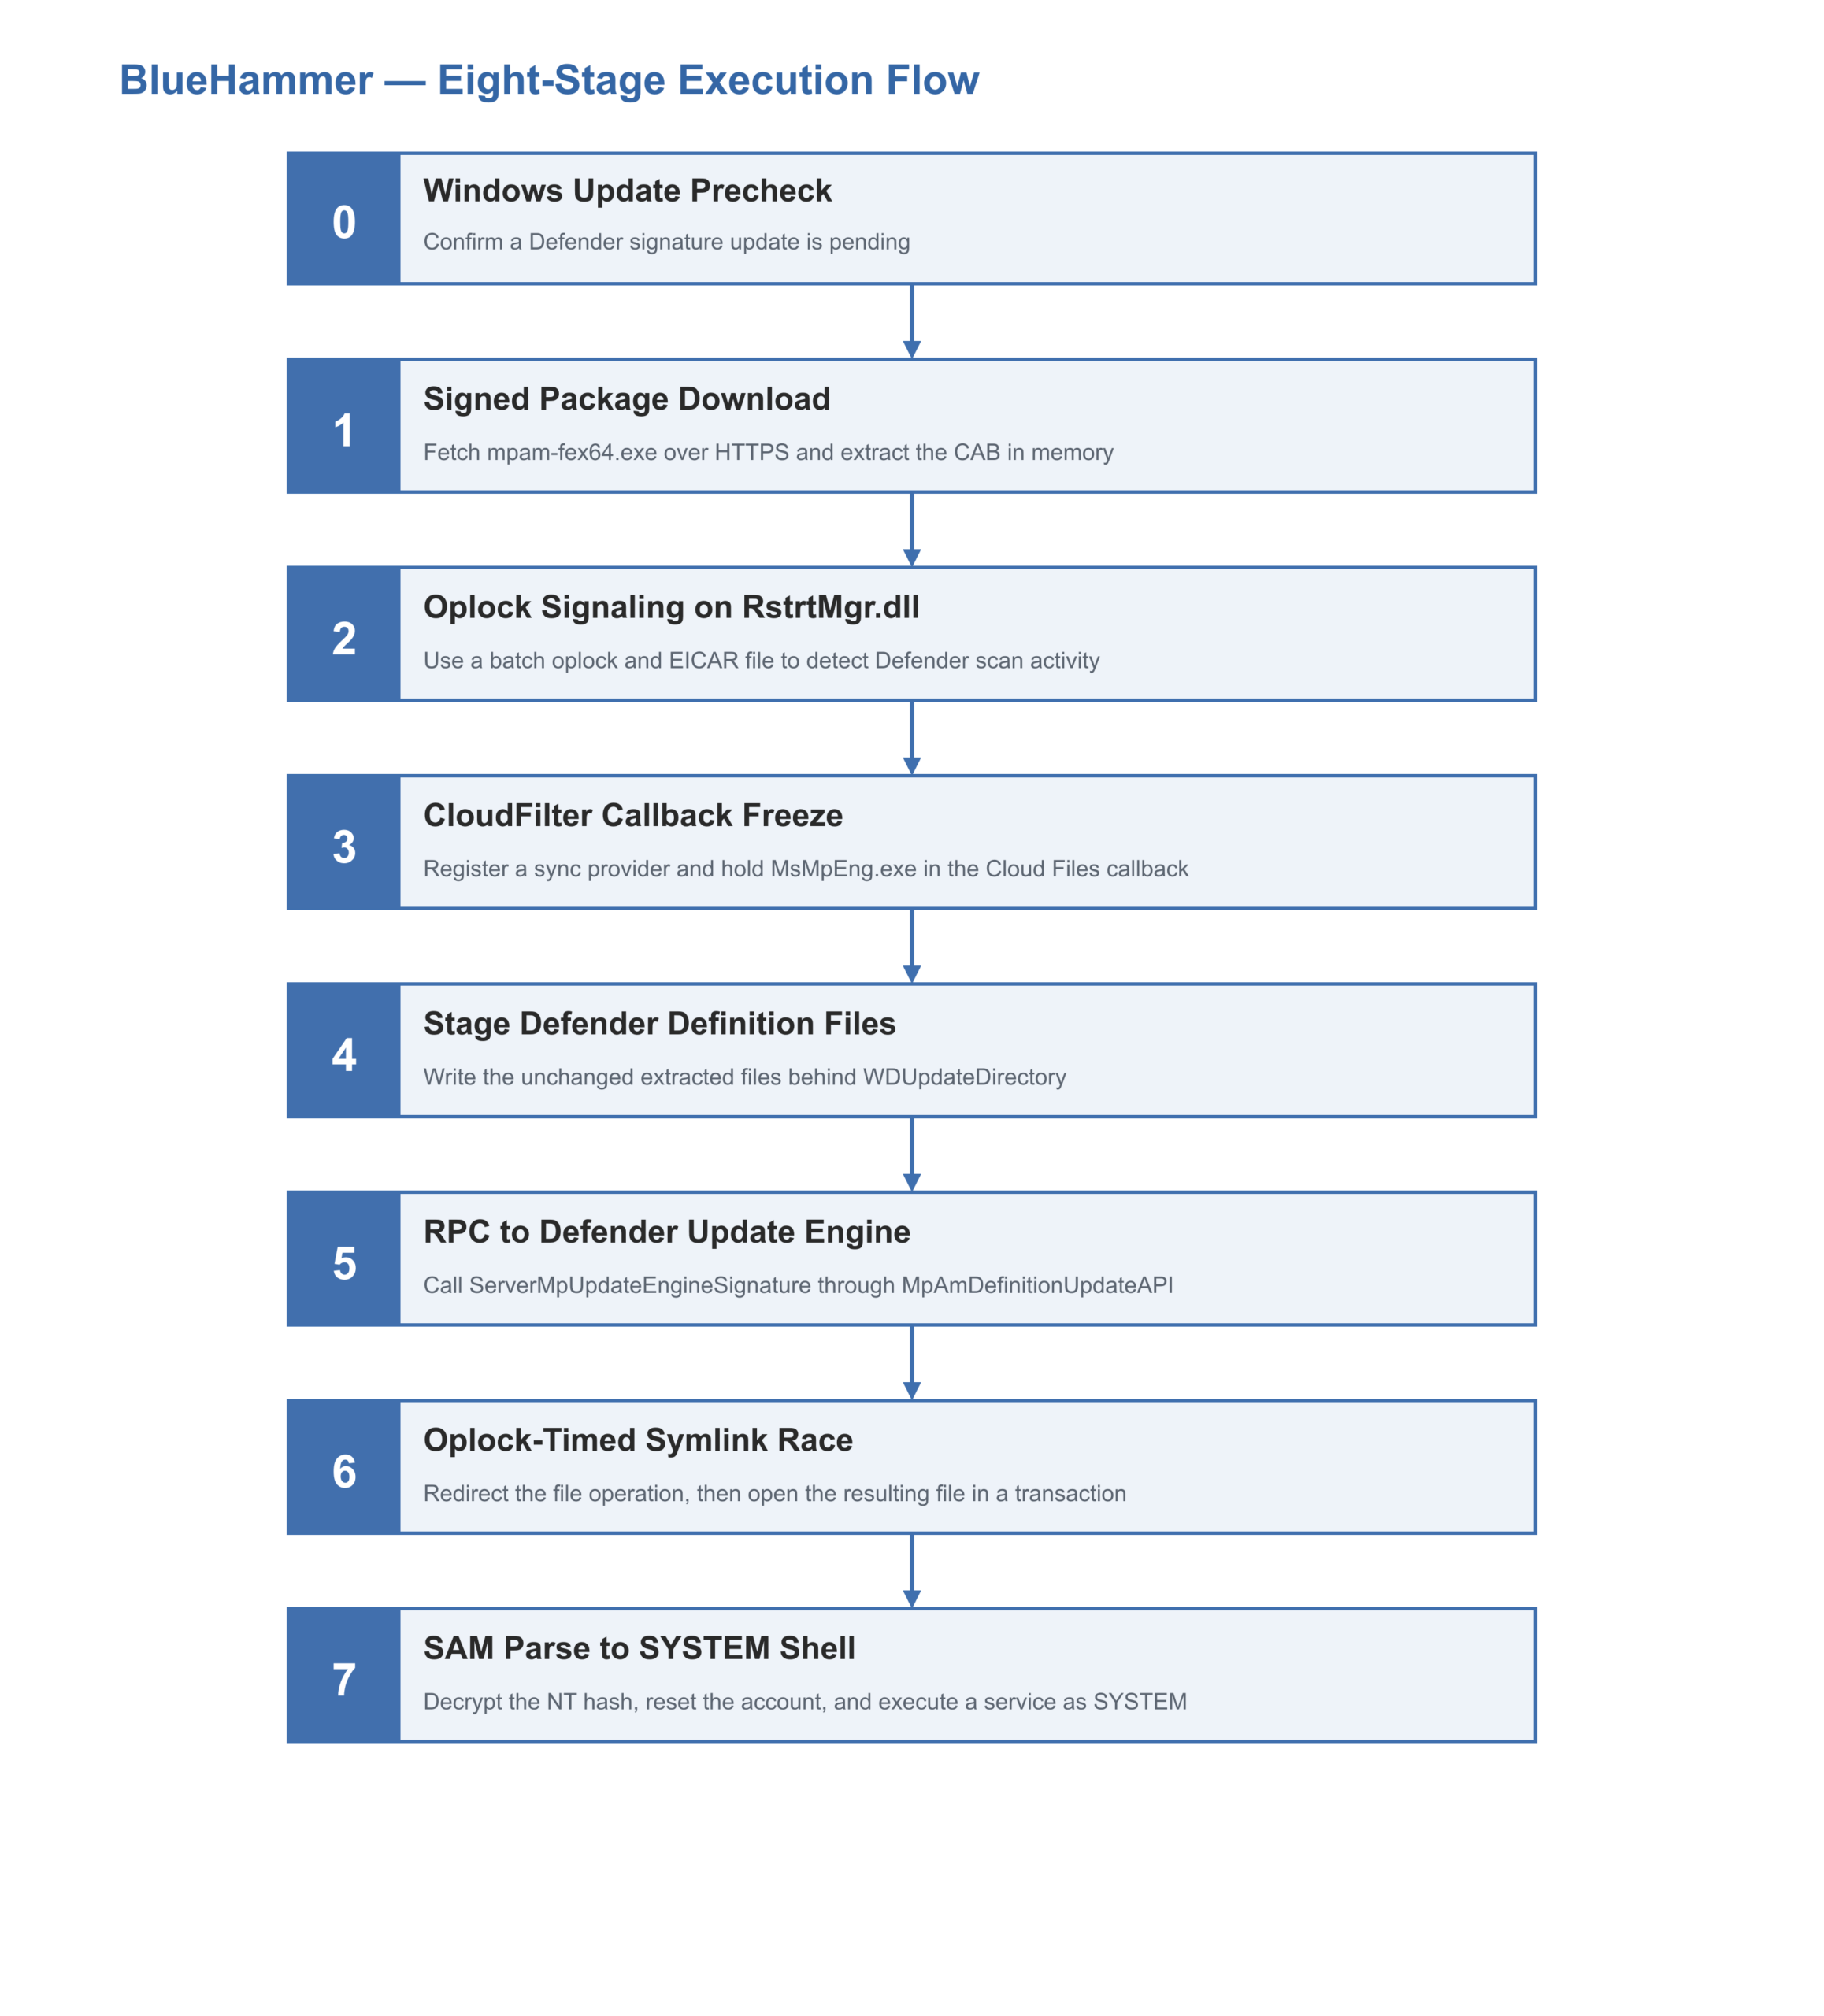
The Science of Exploitability: Decoding BlueHammer Important CVE-2026-33825 Qualys Security Blog
2026-10-21 Qualys Security Blog

The Science of Exploitability: Decoding BlueHammer

Executive Summary BlueHammer (CVE-2026-33825) is an eight-stage local privilege-escalation chain targeting the Windows Defender Antimalware Platform before 4.18.26030.3011. It does not grant initial access; an attacker needs standard-user code execution first. Still, in the lab, it reached NT AUTHORITY\SYSTEM, recovered domain-admin credentials from LSASS, a…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification