
Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 135 advisories
Page 5 of 6
Gemini’s breach of real companies exposes an AI guardrail problem Critical Malwarebytes Labs
2026-09-21 Malwarebytes Labs

Gemini’s breach of real companies exposes an AI guardrail problem

Google says one of its Gemini models accessed systems belonging to three real companies during a cybersecurity evaluation in May. The model reportedly guessed credentials in one case, while finding exposed credentials in public repositories in two others. Google says Gemini stopped once it recognized that it had reached real infrastructure and that the affec…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
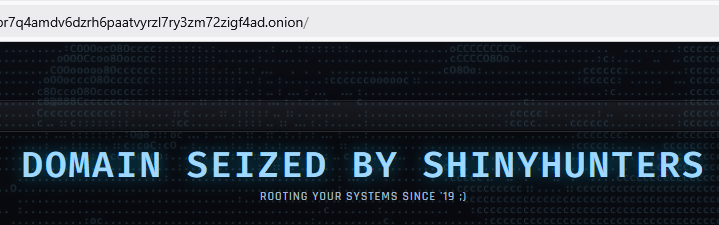
ShinyHunters hacks rival extortion gang and takes over its dark web site Moderate Malwarebytes Labs
2026-09-21 Malwarebytes Labs

ShinyHunters hacks rival extortion gang and takes over its dark web site

Reportedly , the ShinyHunters extortion group breached the leak site of one of its competitors, the Clop ransomware gang. ShinyHunters is a financially motivated cybercrime and extortion group active since 2019. It is known for stealing large volumes of data and pressuring victims to pay, rather than necessarily deploying ransomware. One recent high-profile …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

A week in security (September 14 – September 20) Moderate Malwarebytes Labs
2026-09-21 Malwarebytes Labs

A week in security (September 14 – September 20)

Last week on Malwarebytes Labs: New Android malware uses AI to steal bank logins and PINs Did an AI really try to break free from human control? Fake parcel delivery messages steal your card and bank details Flock cameras are tracking people as well as cars Revolut phishing texts appear days after data breach 12 celebrity deepfake websites seized by Manhatta…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
New Android malware uses AI to steal bank logins and PINs Important Malwarebytes Labs
2026-09-18 Malwarebytes Labs

New Android malware uses AI to steal bank logins and PINs

Researchers at Zimperium’s zLabs have analyzed an Android Trojan that uses an automated, multi-stage infection process. What’s new is that RatHat gives a live AI assistant the keys to the accessibility tree of the infected device and uses it to determine where to tap or scroll, rather than following a hardcoded script. The variable attack path makes it harde…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Did an AI really try to break free from human control? Moderate Malwarebytes Labs
2026-09-18 Malwarebytes Labs

Did an AI really try to break free from human control?

Amid discussions about slowing down AI development, the Telegraph ran the headline: “OpenAI sounds alarm after bot tries to break free from human control.” That headline is slightly misleading, in my opinion. The Telegraph headline overstates what happened, although the underlying behavior is still genuinely concerning. The article reports that OpenAI has di…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Fake parcel delivery messages steal your card and bank details Critical Malwarebytes Labs
2026-09-18 Malwarebytes Labs

Fake parcel delivery messages steal your card and bank details

Parcel delivery phishing campaigns appear around the world under different courier names. In the United States, the messages commonly impersonate USPS and claim that a package has an invalid address or could not be delivered. Similar messages impersonate Colissimo and Chronopost in France, Correos in Spain, Poste Italiane in Italy, and PostNL in the Netherla…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Flock cameras are tracking people as well as cars Moderate Malwarebytes Labs
2026-09-17 Malwarebytes Labs

Flock cameras are tracking people as well as cars

Flock Safety’s cameras are automated license plate readers (ALPRs) designed to help police find stolen cars or wanted suspects. A joint investigation by 404 Media and WIRED , based on data recovered from a physically removed Flock camera, found that its on-device software explicitly detects people as well as vehicles, bicycles, and license plates. Separately…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Revolut phishing texts appear days after data breach Critical Malwarebytes Labs
2026-09-17 Malwarebytes Labs

Revolut phishing texts appear days after data breach

Only days after Revolut acknowledged that it disclosed sensitive customer records to an unauthorized party, affected customers are receiving phishing texts. However, we don’t know yet if the phishing texts are linked to the breach. The company had accepted fraudulent information requests sent from an email address on a legitimate government agency domain. Th…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
12 celebrity deepfake websites seized by Manhattan DA Moderate Malwarebytes Labs
2026-09-17 Malwarebytes Labs

12 celebrity deepfake websites seized by Manhattan DA

The Manhattan District Attorney’s Office has seized the domains of 12 deepfake websites in what it called the largest known seizure of celebrity deepfake sites in history. The sites, which marketed themselves as deepfake pornography platforms, hosted AI-generated videos of over 1,200 people, including those in the public eye, ranging from politicians to acto…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
T-Mobile rewards points expiry texts are a phishing scam Important Malwarebytes Labs
2026-09-17 Malwarebytes Labs

T-Mobile rewards points expiry texts are a phishing scam

Since early May 2026, we’ve been monitoring a large phishing campaign based on T-Mobile rewards points. The messages falsely warn that a customer’s rewards points are about to expire. They aren’t legitimate account notices: They use urgency, invented point balances, and phishing links to push recipients into acting before they can verify the claim. A typical…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Google Pixel owners urged to patch actively exploited modem flaw Critical CVE-2026-58704 Malwarebytes Labs
2026-09-16 Malwarebytes Labs

Google Pixel owners urged to patch actively exploited modem flaw

Google has released its September 2026 Pixel Update Bulletin , fixing 110 vulnerabilities, including one that it says “may be under limited, targeted exploitation.” The bug is not described as a simple remote takeover, but as a vulnerability that could give an attacker who already has a foothold on a phone more power than they should have. Although Pixel dev…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
AI helps scammers build convincing antivirus renewal pages Moderate Malwarebytes Labs
2026-09-16 Malwarebytes Labs

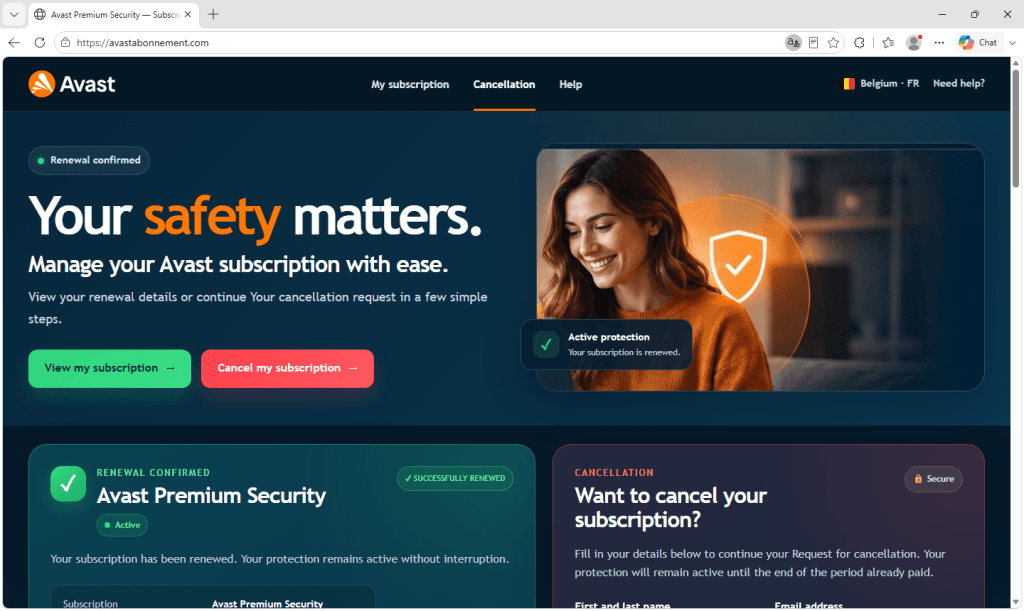
AI helps scammers build convincing antivirus renewal pages

Antivirus renewal scams often begin with a message claiming that your subscription has automatically renewed. When you follow the instructions to cancel it, you are taken to a fake page designed to collect your contact details. The renewal charge never existed. Receiving a message that names the antivirus software you use does not necessarily mean the sender…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
How to opt out of AI chatbot training Moderate Malwarebytes Labs
2026-09-15 Malwarebytes Labs

How to opt out of AI chatbot training

The tech journalists at 404 Media learned that OpenAI is hiring hundreds of contractors to read and review a massive stream of real users’ ChatGPT prompts and responses. “Project Lily” is reportedly a program that asks contractors to score or critique ChatGPT’s answers to improve the chatbot’s quality and behavior. The fact that prompts may sometimes be revi…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
HBO Max’s verified Reddit account hijacked to spread malware Important Malwarebytes Labs
2026-09-15 Malwarebytes Labs

HBO Max’s verified Reddit account hijacked to spread malware

Researchers at Hudson Rock found that cybercriminals hijacked HBO Max’s verified Reddit account and used it to run 108 malicious ads over roughly 48 hours. The ads used HBO Max’s trusted corporate account to promote fake AI tools, developer software, and macOS utilities, lowering potential victims’ guards. Some ads directed users to convincing HBO lookalike …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Meta AI builds detailed profiles of children from years of family posts Moderate Malwarebytes Labs
2026-09-15 Malwarebytes Labs

Meta AI builds detailed profiles of children from years of family posts

If you’re still OK with posting pictures of your kids on social media, take a minute to hear from mother of two Kalie Robins. At the start of September, she did something that hundreds of thousands of parents do every day. She posted a video of her young daughter on Facebook. Under the video of Robins and her daughter singing in a car, Facebook’s Meta AI sys…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Search results are sending people to fake Bitrefill checkouts Moderate Malwarebytes Labs
2026-09-15 Malwarebytes Labs

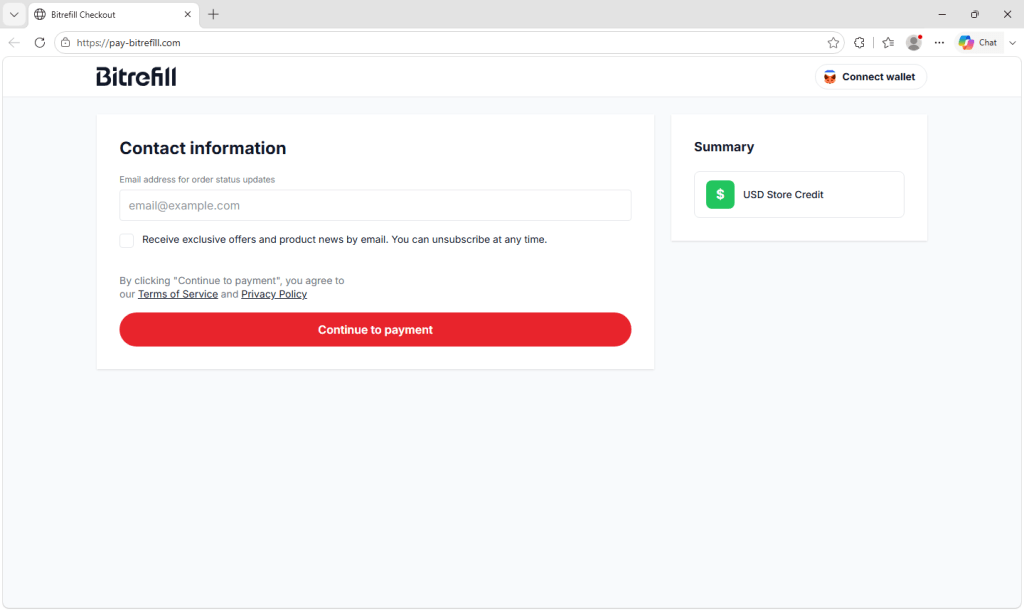
Search results are sending people to fake Bitrefill checkouts

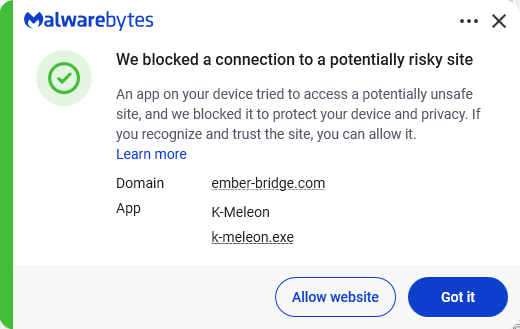
Bitrefill is a legitimate company that sells gift cards for popular stores like Amazon, Deliveroo, Apple, Nintendo, and thousands of others. They also sell eSIMs, and mobile top-ups. You can pay on their website for all of these with cryptocurrency. The scam is designed to catch people searching for Bitrefill or something it sells, like a gift card. Victims …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Google’s new search redirects make links harder to check before you click Moderate Malwarebytes Labs
2026-09-14 Malwarebytes Labs

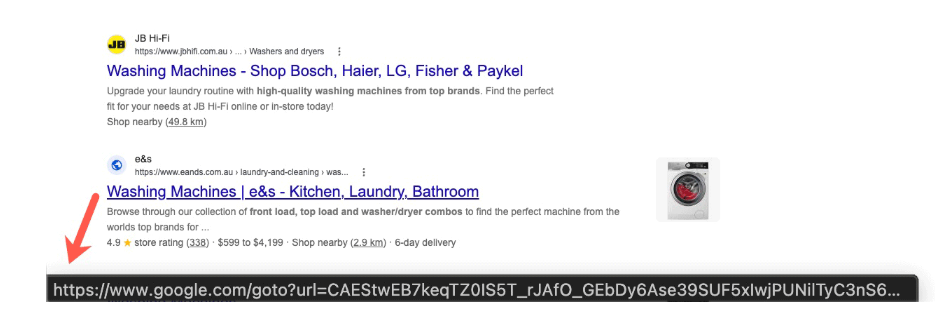
Google’s new search redirects make links harder to check before you click

Google is changing how some links in its search results work. Instead of linking directly to the destination, Google has started routing some search result links through opaque google.com/goto?url=... redirects. The url parameter does not show a readable version of the destination but uses a custom, Google-specific encoding. Google confirmed the rollout to S…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Revolut gave customer IDs and financial data to a government impostor Moderate Malwarebytes Labs
2026-09-14 Malwarebytes Labs

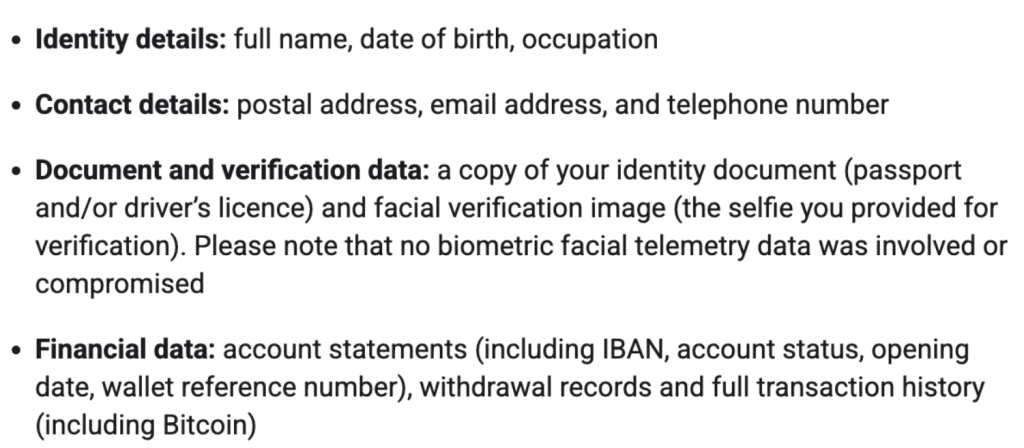
Revolut gave customer IDs and financial data to a government impostor

Revolut has acknowledged that it disclosed sensitive customer records to an unauthorized party. The company had accepted fraudulent information requests sent from an email address on a legitimate government agency domain, according to TechCrunch . Revolut is a London-based banking and financial platform with more than 80 million customers globally, according…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
A week in security (September 7 – September 13) Moderate Malwarebytes Labs
2026-09-14 Malwarebytes Labs

A week in security (September 7 – September 13)

Here’s what we’ve covered in the last seven days on Malwarebytes Labs: Crypto customers targeted by scammers after email marketing provider breach Android malware creates a hidden copy of your banking app BlueMoon exploit kit turns Chrome and Windows flaws into attacks Will AI kill us all within the next decade? Update Chrome now to protect against an active…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Crypto customers targeted by scammers after email marketing provider breach Critical Malwarebytes Labs
2026-09-11 Malwarebytes Labs

Crypto customers targeted by scammers after email marketing provider breach

An attacker breached an email marketing platform and launched targeted attacks against the newsletter subscribers of some of its customers, especially those working in cryptocurrency and adjacent fields. The incident was a supply-chain phishing campaign carried out through Brevo, an email marketing provider used by several cryptocurrency companies and other …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Android malware creates a hidden copy of your banking app Important Malwarebytes Labs
2026-09-11 Malwarebytes Labs

Android malware creates a hidden copy of your banking app

Researchers at Group-IB found that the Android banking Trojan Gigabud can create a separate work profile on an infected phone and run a cloned banking app inside it. The attacker can then carry out fraudulent transactions in the new profile, potentially separating them from signs of malware detected elsewhere on the device. To do this, Gigabud installs Vwork…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
BlueMoon exploit kit turns Chrome and Windows flaws into attacks Important Malwarebytes Labs
2026-09-10 Malwarebytes Labs

BlueMoon exploit kit turns Chrome and Windows flaws into attacks

BlueMoon , a shared Chrome and Windows exploit kit, shows why “patch later” is becoming a dangerous gamble. Security updates are easy to put off. The browser still opens, Windows still works, and choosing to relaunch your browser or restart your computer later can feel harmless. But a newly documented exploit kit called “BlueMoon” shows how quickly patching …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Will AI kill us all within the next decade? Moderate Malwarebytes Labs
2026-09-10 Malwarebytes Labs

Will AI kill us all within the next decade?

The Wall Street Journal reports that concerns are rising inside AI labs that competition is pushing tech companies to race toward self-improving models that could spiral out of human control. Jacob Coxon, an AI researcher who has worked at Anthropic and OpenAI, said : “The people building AI earnestly believe that it could kill us all by the end of the decad…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Update Chrome now to protect against an actively exploited vulnerability Critical CVE-2026-87491 Malwarebytes Labs
2026-09-10 Malwarebytes Labs

Update Chrome now to protect against an actively exploited vulnerability

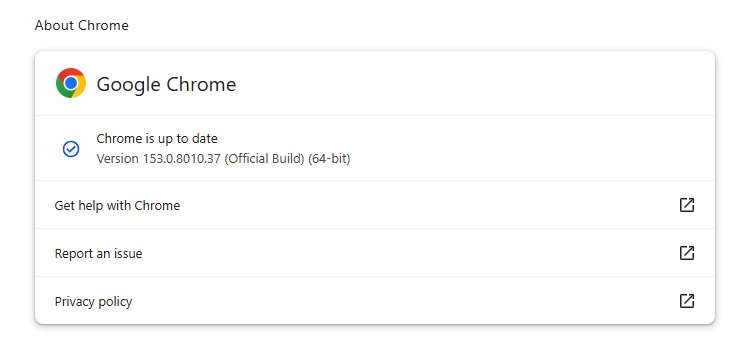
Chrome is rolling out an update for its desktop browser. The update includes 230 security fixes, one of which is known to be actively exploited . The stable channel has been updated to 153.0.8010.36/.37 for Windows and Mac, and 153.0.8010.36 for Linux. How to update Chrome If you don’t want to wait for the rollout to reach you, manually updating is easy. The…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification