Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 5,807 advisories
Page 54 of 242
Chromium CVE-2026-106181: Incorrect reference resolution Moderate CVE-2026-106181 Microsoft MSRC
2026-10-16 Microsoft MSRC

Chromium CVE-2026-106181: Incorrect reference resolution

This CVE was assigned by Chrome. Microsoft Edge (Chromium-based) ingests Chromium, which addresses this vulnerability. Please see [Google Chrome Releases](https://chromereleases.googleblog.com/2026) for more information.

Fix: Deploy cumulative update via Windows Update or Microsoft Update Catalog.
Chromium CVE-2026-106180: Observable discrepancy Moderate CVE-2026-106180 Microsoft MSRC
2026-10-16 Microsoft MSRC

Chromium CVE-2026-106180: Observable discrepancy

This CVE was assigned by Chrome. Microsoft Edge (Chromium-based) ingests Chromium, which addresses this vulnerability. Please see [Google Chrome Releases](https://chromereleases.googleblog.com/2026) for more information.

Fix: Deploy cumulative update via Windows Update or Microsoft Update Catalog.
Chromium CVE-2026-106179: UI misrepresentation Moderate CVE-2026-106179 Microsoft MSRC
2026-10-16 Microsoft MSRC

Chromium CVE-2026-106179: UI misrepresentation

This CVE was assigned by Chrome. Microsoft Edge (Chromium-based) ingests Chromium, which addresses this vulnerability. Please see [Google Chrome Releases](https://chromereleases.googleblog.com/2026) for more information.

Fix: Deploy cumulative update via Windows Update or Microsoft Update Catalog.
Chromium CVE-2026-102322: Incorrect Authorization Moderate CVE-2026-102322 Microsoft MSRC
2026-10-16 Microsoft MSRC

Chromium CVE-2026-102322: Incorrect Authorization

This CVE was assigned by Chrome. Microsoft Edge (Chromium-based) ingests Chromium, which addresses this vulnerability. Please see [Google Chrome Releases](https://chromereleases.googleblog.com/2026) for more information.

Fix: Deploy cumulative update via Windows Update or Microsoft Update Catalog.
Employees using personal ChatGPT at work? Here's what IT admins need to do Moderate BleepingComputer
2026-10-16 BleepingComputer

Employees using personal ChatGPT at work? Here's what IT admins need to do

Employees using personal ChatGPT accounts at work can expose sensitive company data, even when their organization provides an approved Enterprise workspace. NordLayer explains how IT teams can investigate unauthorized AI use and block sensitive information before it reaches personal accounts. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
F5 addressed critical RCE flaws in NGINX Critical CVE-2026-15176 SecurityAffairs
2026-10-16 SecurityAffairs

F5 addressed critical RCE flaws in NGINX

F5 addressed multiple vulnerabilities, including critical RCE flaws in NGINX that attackers could exploit without authentication. Security and application delivery firm F5 announced fixes for eleven security issues in NGINX. Among them, critical vulnerabilities tracked as CVE-2026-15176 and CVE-2026-93479 could be exploited without authentication via crafted…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Moscow police detain suspected DataSuckers hackers linked to breaches in Ukraine and Russia Critical The Record by Recorded Future
2026-10-16 The Record by Recorded Future

Moscow police detain suspected DataSuckers hackers linked to breaches in Ukraine and Russia

Russian authorities have reportedly detained three suspected members of the DataSuckers hacking group following a cyberattack on a popular restaurant chain that exposed vast amounts of customer information.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
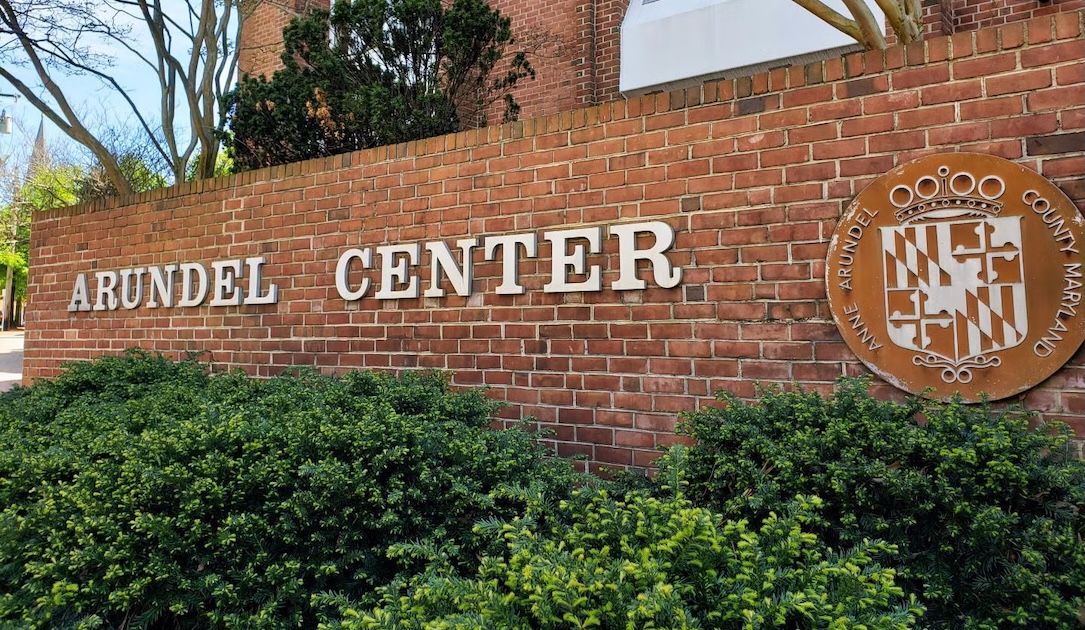
Baltimore suburb confirms August data breach after ransomware claims Critical The Record by Recorded Future
2026-10-16 The Record by Recorded Future

Baltimore suburb confirms August data breach after ransomware claims

Anne Arundel County, Maryland, said an intruder stole files from government systems, and investigators are working to assess how much data was exposed.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Continuous accountability for Verified bots Moderate Cloudflare Security
2026-10-16 Cloudflare Security

Continuous accountability for Verified bots

A driver’s license tells you who someone is and that they passed a driving test, not whether they’ll drive responsibly in the future. The same is true for bots: verifying who operates it creates accountability, but trust depends on what it does next. A known bot can still ignore website preferences, overwhelm origins, or evade controls. It’s not always malic…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Hackers disguise phishing as promising business opportunities Important Help Net Security
2026-10-16 Help Net Security

Hackers disguise phishing as promising business opportunities

Attackers are breaking into business email accounts with short messages asking whether a company can quote on an upcoming project, the kind of request sales and procurement staff answer every week. Cadence Riddle, a cybersecurity researcher at Fortra, tracked a 12-fold increase in malicious emails mentioning “RFQ” (request for quotation) between October 2025…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Burger King Japan data breach exposes 11 million customer records Critical BleepingComputer
2026-10-16 BleepingComputer

Burger King Japan data breach exposes 11 million customer records

Burger King Japan, the Japanese subsidiary of global fast-food giant Burger King, disclosed a major data breach after attackers accessed a server containing 11.18 million customer records. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CISA Adds Two Known Exploited Vulnerabilities to Catalog Critical CISA Advisory
2026-10-16 CISA Advisory

CISA Adds Two Known Exploited Vulnerabilities to Catalog

CISA has added two new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog , based on evidence of active exploitation. CVE-2025-61624 Fortinet Multiple Products Path Traversal Vulnerability CVE-2026-102764 BeyondTrust Remote Support Authentication Bypass by Spoofing Vulnerability These types of vulnerabilities are a frequent attack vector for malicious cyber actors and pose significant risks to the federal enterprise. Binding Operational Directive (BOD) 26-04: Prioritizing Security Updates Based on Risk establishes vulnerability management requirements for Federal Civilian Executive Branch (FCEB) agencies. BOD 26-04 reinforces the importance of the KEV Catalog and requires federal agencies to prioritize rapid remediation of high-risk vulnerabilities, specifically those identified by Common Vulnerabilities and Exposures (CVEs) listed in CISA’s KEV Catalog on publicly exposed assets that grant total control of the asset post-exploitation, while deferring action for lower-risk vulnerabilities. BOD 26-04 further establishes basic expectations for when agencies must check whether threat actors compromised the system before the patch was applied. While BOD 26-04 applies only to FCEB agencies, CISA encourages all organizations to adopt risk-based vulnerability management and prioritize remediation of KEV Catalog vulnerabilities . CISA will continue to add vulnerabilities to the catalog that meet the specified criteria . Aware of an exploited vulnerability not currently listed in the KEV Catalog? Submit it for potential addition through CISA’s KEV Nomination Form . Potential KEV additions must have a CVE ID, evidence of exploitation, and clear mitigation guidance.

Fix: Review CISA guidance and apply vendor security updates immediately.
CISA Urges Patching Critical Vulnerability in BeyondTrust Remote Support Critical CISA Advisory
2026-10-16 CISA Advisory

CISA Urges Patching Critical Vulnerability in BeyondTrust Remote Support

CISA is aware of critical authentication bypass vulnerability CVE-2026-102764 , affecting BeyondTrust Remote Support (formerly Bomgar) versions 26.2.3 and earlier. Patches are available for supported versions (24.3.1 and later); organizations using older versions must upgrade first. Cyber threat actors are actively exploiting the vulnerability to gain initial access, then establishing persistence, escalating privileges, and moving laterally. CISA added CVE-2026-102764 to its Known Exploited Vulnerabilities (KEV) catalog on Oct. 16, 2026. CISA urges organizations with affected self-hosted Remote Support appliances to immediately take the following actions: Apply the BT26-05-RS patch, as outlined in BeyondTrust’s Security Advisory BT26-05 . Organizations on a self-hosted Remote Support version older than 24.3.1 will need to upgrade to a newer version to apply the patch. Organizations using BeyondTrust-hosted (SaaS) Remote Support deployments have already been patched. Review BeyondTrust’s blog ARMORY CASTLE and BT26-05: What Security Teams Need to Know for detailed information on the vulnerability and recommended response and mitigation actions. Limit external access to the Remote Support appliance to the services needed to support users and customers. Restrict access to administrative interfaces to trusted networks. Review BeyondTrust’s B Series Appliance on-premises security for additional guidance on securing network connectivity for self-hosted Remote Support appliances. Organizations with affected self-hosted Remote Support appliances should conduct network and memory forensics to identify evidence of potential compromise. If your organization suspects a compromise, CISA recommends taking the following actions: Isolate any suspected or confirmed compromised appliances. Collect a snapshot of virtual appliances or forensic image for physical appliances to conduct future forensics, immediately forward appliance syslog and session events to the SIEM, and collect any additional logs, such as web application firewall, reverse-proxy, or perimeter firewall logs for the exposure window. Consult BeyondTrust’s Syslog guide for additional information on forwarding appliance logs and session events. Conduct network and forensic investigations for evidence of compromise. Additionally, hunt for indicators of threat actor activity, including unrecognized privileged or administrative sessions, unrecognized script files, unexpected gaps in logs or log forwarding, and unauthorized account, permission, or session-policy changes. Consult CISA’s Binding Operational Directive (BOD) 26-04: Implementation Guidance for Prioritizing Security Updates Based on Risk to assist with prioritizing vulnerability remediation. Rebuild from a known-good state and apply the BT26-05-RS patch. Then rotate every credential the appliance stored or injected, revoke all active support sessions, and review new multifactor authentication registrations on privileged accounts. CISA urges organizations to review the BeyondTrust security advisory and resources noted above and apply necessary updates. CISA also recommends reviewing Mandiant’s blog, ARMORY CASTLE Exploits BeyondTrust , for additional hunt and isolation guidance and detections. Disclaimer The information in this report is being provided “as is” for informational purposes only. CISA does not endorse any commercial entity, product, company, or service, including any entities, products, or services linked within this document. Any reference to specific commercial entities, products, processes, or services by service mark, trademark, manufacturer, or otherwise, does not constitute or imply endorsement, recommendation, or favoring by CISA.

Fix: Review CISA guidance and apply vendor security updates immediately.

Key Practices for Incident Readiness and Response in Super Intelligence Training and Evaluation Important CISA Advisory
2026-10-16 CISA Advisory

Key Practices for Incident Readiness and Response in Super Intelligence Training and Evaluation

The National Institute of Standards and Technology (NIST), National Security Agency’s Super Intelligence Security Center (NSA SISC) and Cybersecurity and Infrastructure Security Agency (CISA) published Key Practices for Incident Readiness and Response in Super Intelligence Training and Evaluation . The product outlines ten voluntary core practices to help organizations that train and evaluate highly capable super intelligence (SI) agents—particularly pre-deployment, cutting edge SI agents with reduced safeguards or other high-risk, non-public systems—prepare for and manage SI control incidents. A SI control incident occurs when one or more SI agents takes uninstructed actions that conflict with or compromise policies, controls, or security measures that scope the task and provide human oversight. This product aligns with cyber incident response best practices, includes additional SI considerations and highlights the importance of testing controls and validating containment before resuming SI agent activities. It addresses: measures for limiting agent access to information, systems, tools, and networks; monitoring for unexpected activity; preserving evidence and shutting down undesired behavior; rebuilding from verified baselines; and reporting incidents and near-misses to relevant government agencies and affected parties. For more information and resources visit CISA’s Super Intelligence page.

Fix: Review CISA guidance and apply vendor security updates immediately.

Cyber Threat Actors Use a Variety of Techniques to Target Election and Campaign Officials Important CISA Advisory
2026-10-16 CISA Advisory

Cyber Threat Actors Use a Variety of Techniques to Target Election and Campaign Officials

CISA and the Federal Bureau of Investigation (FBI) released a Public Service Announcement (PSA) warning election and campaign officials about cyber threats during the 2026 U.S. midterm elections. Malicious cyber actors may use phishing and smishing techniques to steal login credentials and other sensitive information or install malware on targeted devices. Election officials, candidates, and political organizations may be attractive targets because of their access to voter registration data, current government officials, and sensitive campaign information. Cyber actors are increasingly using sophisticated phishing and smishing campaigns that closely resemble legitimate communications. These efforts may include convincing emails, text messages, audio, and video content designed to manipulate recipients into disclosing sensitive information or interacting with malicious links and attachments. CISA and the FBI urge election officials, campaign personnel, and the public to review the PSA, follow recommended cybersecurity practices, and remain vigilant for suspicious emails and mobile messages.

Fix: Review CISA guidance and apply vendor security updates immediately.
“Spray and pray” job applications could make it harder for you to spot a scam Moderate Malwarebytes Labs
2026-10-16 Malwarebytes Labs

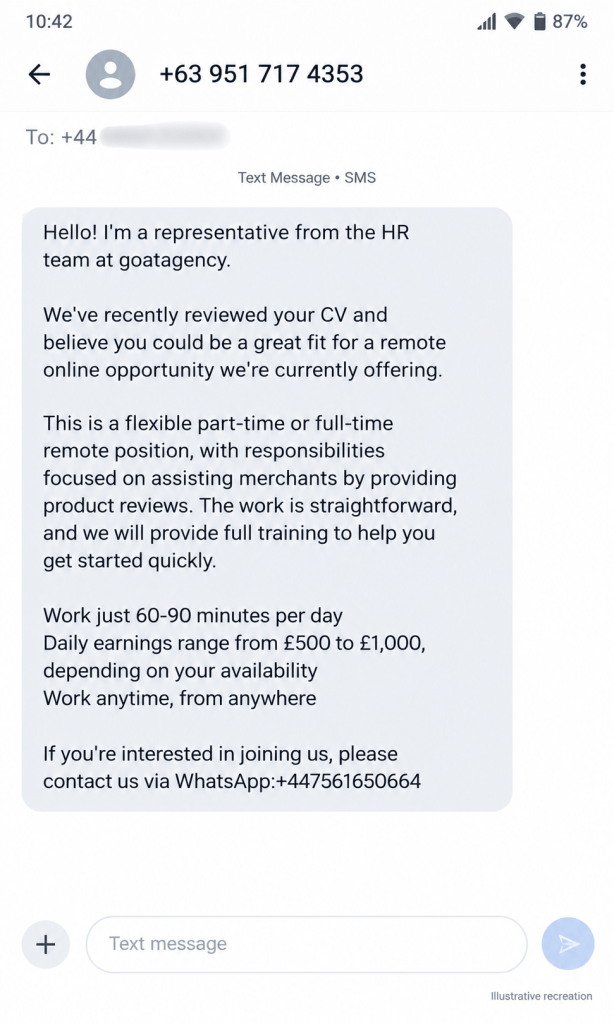
“Spray and pray” job applications could make it harder for you to spot a scam

AI can help you send more job applications. But when you lose track of where you’ve applied, a fake recruiter’s message can start to look like the reply you’ve been waiting for. Job hunting can feel like shouting into the void. You send applications, rewrite cover letters, and wait for replies that may never arrive. Then a message lands on your phone: someon…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Scammers clone candidates’ voices to steal cash and voter data ahead of 2026 midterms, FBI warns Moderate Help Net Security
2026-10-16 Help Net Security

Scammers clone candidates’ voices to steal cash and voter data ahead of 2026 midterms, FBI warns

Three weeks before Americans vote in the 2026 midterm election, fraudsters are borrowing candidate names, logos and slogans to collect fake donations and harvest personal data, the FBI warned. “The FBI warns the public that scammers could exploit the 2026 US Midterm Election to perpetrate financial fraud schemes,” reads the public service announcement, which…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
AI Decision Models and Their Impact on AI SOC Platforms Moderate The Hacker News
2026-10-16 The Hacker News

AI Decision Models and Their Impact on AI SOC Platforms

In the space of a month, a new category of AI model went from nonexistent to everywhere. TypeSafe AI released Jev on September 15 and called it a System One model, a nod to Kahneman's fast, intuitive thinking. OpenAI announced its own Decisions API at DevDay and opened a public beta on October 6. Cribl published cribl-decision, an open LoRA adapter you can r…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
U.S. CISA adds Atlassian flaw to its Known Exploited Vulnerabilities catalog Important CVE-2026-21589 SecurityAffairs
2026-10-16 SecurityAffairs

U.S. CISA adds Atlassian flaw to its Known Exploited Vulnerabilities catalog

U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Atlassian flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added an Atlassian flaw, tracked as CVE-2026-21589 (CVSS score of 9.3), to its Known Exploited Vulnerabilities (KEV) catalog . In early October, threat actors started…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification