Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 2,629 advisories
Page 54 of 110
N0n ransomware: what you need to know Critical Graham Cluley Security
2026-10-03 Graham Cluley Security

N0n ransomware: what you need to know

N0n is a newly-emerged cyber extortion gang. The group was first spotted in the middle of September 2026, and within days it had published on its dark web leak site details of what it claimed to be around a dozen victims. Since then, the tally has continued to grow. Read more in my article on the Fortra blog.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
U.S. CISA adds Zammad GmbH Zammad flaws to its Known Exploited Vulnerabilities catalog Important CVE-2026-102489 SecurityAffairs
2026-10-02 SecurityAffairs

U.S. CISA adds Zammad GmbH Zammad flaws to its Known Exploited Vulnerabilities catalog

U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Zammad GmbH Zammad flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog : CVE-2026-102489 (CVSS score of 9.4) Zammad GmbH Zammad Session Fi…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Judge dismisses spyware case brought by Salvadoran journalists targeted with Pegasus Important The Record by Recorded Future
2026-10-02 The Record by Recorded Future

Judge dismisses spyware case brought by Salvadoran journalists targeted with Pegasus

The plaintiffs, who all worked for the independent and Salvadoran news outlet El Faro, failed to convince the court that their case had jurisdiction in California, according to the judge’s order.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Bipartisan backlash to ALPRs grows as two high-profile bills are introduced Moderate The Record by Recorded Future
2026-10-02 The Record by Recorded Future

Bipartisan backlash to ALPRs grows as two high-profile bills are introduced

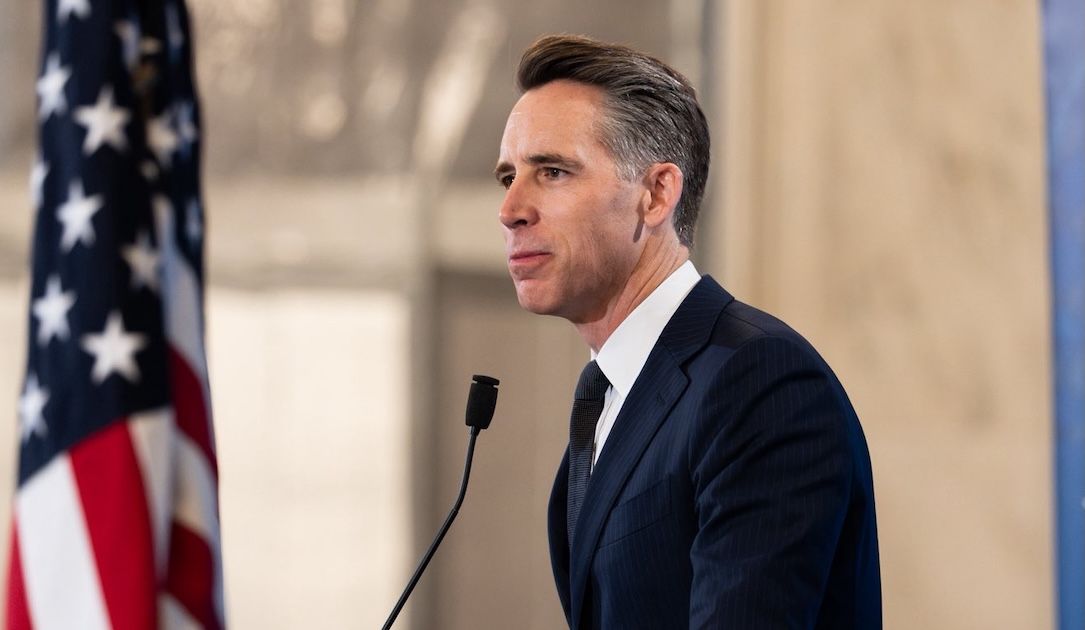
Republican Sen. Josh Hawley has new legislation on limiting automated license plate readers (ALPRs), while Democratic Sens. Bernie Sanders and Jeff Merkley, with Rep. Alexandria Ocasio-Cortez, have teed up a broader bill.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Frontline Education breach exposes school district employee data Critical BleepingComputer
2026-10-02 BleepingComputer

Frontline Education breach exposes school district employee data

Frontline Education is notifying school districts of a data breach after attackers exploited a vulnerability in third-party software to gain unauthorized access to its systems and steal employee information, including Social Security numbers. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Warlock ransomware breach SharePoint in water, telecom operator attacks Critical BleepingComputer
2026-10-02 BleepingComputer

Warlock ransomware breach SharePoint in water, telecom operator attacks

The China-linked ransomware group Warlock targeted a water utility, a telecom provider, a regional government body, and a university by exploiting SharePoint vulnerabilities to gain initial access. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
GitLab Patches Critical 9.9 AI Gateway Flaw Allowing Command Execution on Self-Hosted Servers Critical The Hacker News
2026-10-02 The Hacker News

GitLab Patches Critical 9.9 AI Gateway Flaw Allowing Command Execution on Self-Hosted Servers

A critical flaw in GitLab's AI Gateway could let a logged-in user with Duo Agent Platform access run commands on the gateway under certain conditions, GitLab said in an advisory. The gateway is the service that connects a GitLab instance to AI models, and only organizations that host their own gateway need to act. The flaw is fixed in gateway versions 19.2.4…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Antino Backdoor Uses Outlook and OneDrive for C2 in China-Nexus Espionage Campaign Important The Hacker News
2026-10-02 The Hacker News

Antino Backdoor Uses Outlook and OneDrive for C2 in China-Nexus Espionage Campaign

Government and policy organizations across Asia have become the target of a new campaign orchestrated by a China-nexus threat actor. The activity, which has targeted government and policy organizations in Taiwan, India, the Philippines, Cambodia, Pakistan, Thailand, and Myanmar, involves the deployment of a previously undocumented backdoor codenamed Antino. …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Dell CSM Flaws Enable Unauthenticated Admin Access and Root on Kubernetes Nodes Critical CVE-2026-63688 The Hacker News
2026-10-02 The Hacker News

Dell CSM Flaws Enable Unauthenticated Admin Access and Root on Kubernetes Nodes

Dell has released security updates to address multiple critical security flaws in Dell Container Storage Modules (CSM) that could be exploited by bad actors to take over susceptible systems. The vulnerabilities are listed below - CVE-2026-63688 (CVSS score: 10.0) - A missing authentication for critical function vulnerability in the csm-authorization-storage …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Kiteworks & Citrix Incidents Show Challenges of Zero-Day Response Critical Dark Reading
2026-10-02 Dark Reading

Kiteworks & Citrix Incidents Show Challenges of Zero-Day Response

One company told customers to power down its data-protection platform during a nine-hour window, while the other remained mum on reported attacks prior to releasing a patch for its product.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
GitLab warns of critical RCE vulnerability in AI Gateway service Critical BleepingComputer
2026-10-02 BleepingComputer

GitLab warns of critical RCE vulnerability in AI Gateway service

GitLab warned customers today to immediately patch a critical AI Gateway vulnerability that could let attackers run arbitrary commands on vulnerable instances. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Is Your Organization Ready for 2027's AI Accountability Era? Moderate Dark Reading
2026-10-02 Dark Reading

Is Your Organization Ready for 2027's AI Accountability Era?

Organizations may face an artificial intelligence (AI) reckoning over the next year. Omdia and Gartner weigh in on how to tackle the governance, security, and value challenges ahead.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Is It Fair to Blame 'Rogue' AI for Security Failures? Moderate Dark Reading
2026-10-02 Dark Reading

Is It Fair to Blame 'Rogue' AI for Security Failures?

"Rogue AI" terminology anthropomorphizes LLMs and shifts risk responsibility from vendors. Defenders should treat agents as untrusted, nondeterministic software systems, not sentient beings with malicious intent.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
US sanctions Tren de Aragua gang members in ATM hacks crackdown Moderate BleepingComputer
2026-10-02 BleepingComputer

US sanctions Tren de Aragua gang members in ATM hacks crackdown

The U.S. Treasury Department has sanctioned eight members of the Venezuelan gang Tren de Aragua (TdA) for their role in the theft of millions of dollars in ATM jackpotting attacks across the United States. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
AI Agents Attempt SQL Injection While Searching Government Data Moderate SecurityAffairs
2026-10-02 SecurityAffairs

AI Agents Attempt SQL Injection While Searching Government Data

AI agents probing US and Canadian government sites made SQL injection attempts while seeking data, but investigators found no evidence of compromise. Autonomous AI agents, working on what looks like ordinary data retrieval tasks, ended up throwing basic hacking attempts at a U.S. Department of Education site and Library and Archives Canada. Nobody told them …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft: AI Cuts Post-Compromise Attack Time to Minutes Important Infosecurity Magazine
2026-10-02 Infosecurity Magazine

Microsoft: AI Cuts Post-Compromise Attack Time to Minutes

Microsoft has warned that threat actors have gained the advantage over defenders by using AI to enhance the speed and scale of attacks

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Mississippi mayor says ransomware incident led city to shut down systems Critical The Record by Recorded Future
2026-10-02 The Record by Recorded Future

Mississippi mayor says ransomware incident led city to shut down systems

Government services were temporarily disrupted by ransomware in Vicksburg, Mississippi. Mayor Willis Thompson said the FBI and other authorities are investigating.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The EDR blind spot: 3 ways browser attacks evade endpoint telemetry Important BleepingComputer
2026-10-02 BleepingComputer

The EDR blind spot: 3 ways browser attacks evade endpoint telemetry

Browser-based attacks can steal sessions, abuse extensions, or manipulate users without creating the endpoint artifacts EDR is designed to detect. NordLayer explains three ways attacks can evade endpoint telemetry and why browser-level controls can help close the gap. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Vulnerability Backlogs Are an Ownership Problem Important Dark Reading
2026-10-02 Dark Reading

Vulnerability Backlogs Are an Ownership Problem

Organizations don't need better vulnerability scanners; they need to know who owns their assets, and who has the authority and capacity to actually fix them.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Follow the thread: a new dashboard to investigate account abuse Moderate Cloudflare Security
2026-10-02 Cloudflare Security

Follow the thread: a new dashboard to investigate account abuse

Traditionally, preventing online fraud relied on point-in-time proof of identity: enter the correct password, complete a biometric verification, or pass a liveness check, and gain access. To defeat these controls, fraudsters had to steal credentials and other identity evidence from a real user, which was difficult to execute and scale. Today, widespread acce…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Protected Quick Tunnels: simple accountless authentication for your next dev project Moderate Cloudflare Security
2026-10-02 Cloudflare Security

Protected Quick Tunnels: simple accountless authentication for your next dev project

We launched Quick Tunnels in 2021 to give developers an easy way to share their latest service, application, or project running in their local development environment. A lot has changed since then, but the core use case remains the same. Your coding agent has just finished the feature. The dev server is up on localhost:5173 , and before you ask, the agent of…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification