Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 2,629 advisories
Page 56 of 110
Iranian accused of hacking American universities extradited from Montenegro Moderate The Record by Recorded Future
2026-10-01 The Record by Recorded Future

Iranian accused of hacking American universities extradited from Montenegro

An Iranian national accused by the U.S. of taking part in dozens of breaches involving the theft of academic data and intellectual property has been extradited from Montenegro.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Microsoft says threat actors are ahead in the early AI race Moderate BleepingComputer
2026-10-01 BleepingComputer

Microsoft says threat actors are ahead in the early AI race

Microsoft says cyberattackers are currently benefiting from artificial intelligence faster than defenders, allowing threat actors to speed up vulnerability discovery, malware development, and post-compromise activity while security teams struggle to keep pace. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Operation KillSwitch: Police Dismantle KillSec Ransomware Group Critical SecurityAffairs
2026-10-01 SecurityAffairs

Operation KillSwitch: Police Dismantle KillSec Ransomware Group

Operation KillSwitch: Europol says the KillSec ransomware group, allegedly led by a 16-year-old, was dismantled after attacks on about 1,000 victims. Law enforcement seized control of KillSec ‘s dark web leak site, the Tor website the group used to threaten victims with publishing stolen files unless they paid up. That single action locked down more than 110…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Give yourself room to be human Moderate Cisco Talos Intelligence
2026-10-01 Cisco Talos Intelligence

Give yourself room to be human

Welcome to this week’s edition of the Threat Source newsletter. Fall is officially here in Maryland, and I can’t be more relieved. I flourish in 50 degree weather, where it feels natural to burrow under blankets, knit sweaters, and listen to an audiobook. Beyond that, though, can I say that I’m glad fall is here because the end of summer has been a bit of a …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Fake xStocks, Pendle, and other sites bait crypto users with rewards votes Moderate Malwarebytes Labs
2026-10-01 Malwarebytes Labs

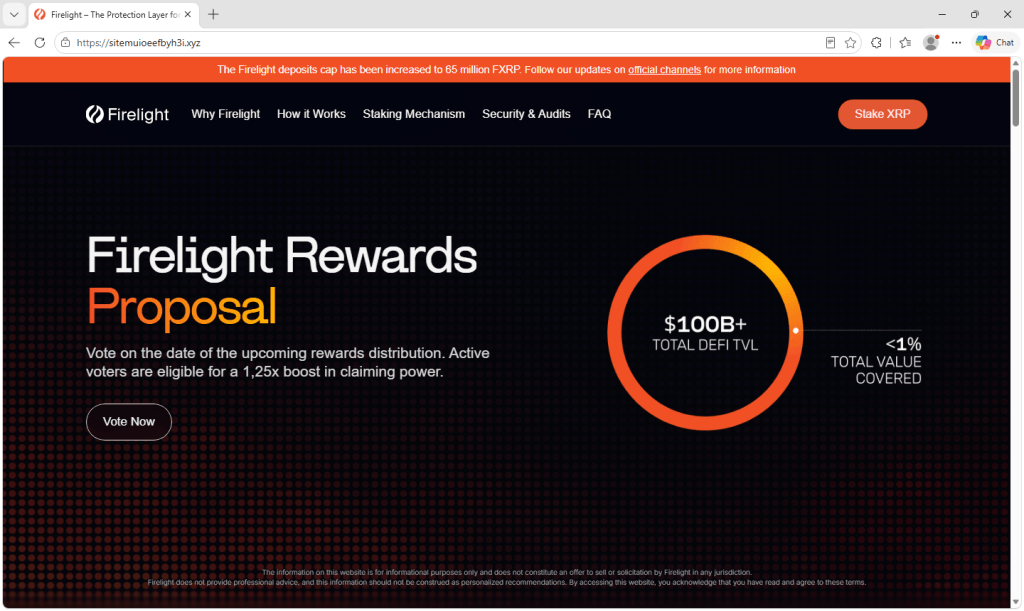
Fake xStocks, Pendle, and other sites bait crypto users with rewards votes

We found 70 websites that impersonate legitimate crypto projects that invite visitors to vote on the date of an upcoming rewards distribution. The pages copy the look of the real sites closely, and on most of them the offer is small and believable: Cast a vote, and as an active voter you get a 1.25x boost when the rewards are paid out. However, the vote is f…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Police Arrest 16-Year-Old Suspected of Running KillSec, Seize Ransomware Leak Site and Servers Critical The Hacker News
2026-10-01 The Hacker News

Police Arrest 16-Year-Old Suspected of Running KillSec, Seize Ransomware Leak Site and Servers

Police in Spain have arrested a 16-year-old whom investigators suspect of running the KillSec ransomware group. KillSec is accused of stealing data from organizations and threatening to publish it on its leak site unless they paid. The 16-year-old was one of 3 people arrested on September 30, when police also took control of that site. Investigators identifi…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
ThreatsDay: AI-Powered Zero-Day Chain, 543K Live Secrets, Model Inspection RCE and 13 More Stories Critical The Hacker News
2026-10-01 The Hacker News

ThreatsDay: AI-Powered Zero-Day Chain, 543K Live Secrets, Model Inspection RCE and 13 More Stories

This week, the useful words are boring ones: inspect, cache, compile, store, trust. Each sounds harmless. Each can become an attack path when a system does a little more than people expect. A model check can run code. A cache can mix up requests. A public secret can stay useful for years. That is the lesson running through the list. Attackers do not always n…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Police disrupt KillSec ransomware, arrest suspected teenage leader Critical The Record by Recorded Future
2026-10-01 The Record by Recorded Future

Police disrupt KillSec ransomware, arrest suspected teenage leader

European police said raids against the KillSec ransomware-as-a-service operation included the arrest of a high-profile teen suspect.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
WordPress Backdoor Rebuilds Itself After Cleanup Using Files, Database, and Shared Memory Important The Hacker News
2026-10-01 The Hacker News

WordPress Backdoor Rebuilds Itself After Cleanup Using Files, Database, and Shared Memory

Cybersecurity researchers have shed light on a WordPress compromise in which threat actors deployed multiple persistence mechanisms to ensure that the final payload kept returning without having to infect the site again. The backdoor has been codenamed SC after the "SC_" markers present in the injected content. Sucuri has described the malware as a "self-hea…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Police dismantle KillSec ransomware gang allegedly led by 16-year-old Critical BleepingComputer
2026-10-01 BleepingComputer

Police dismantle KillSec ransomware gang allegedly led by 16-year-old

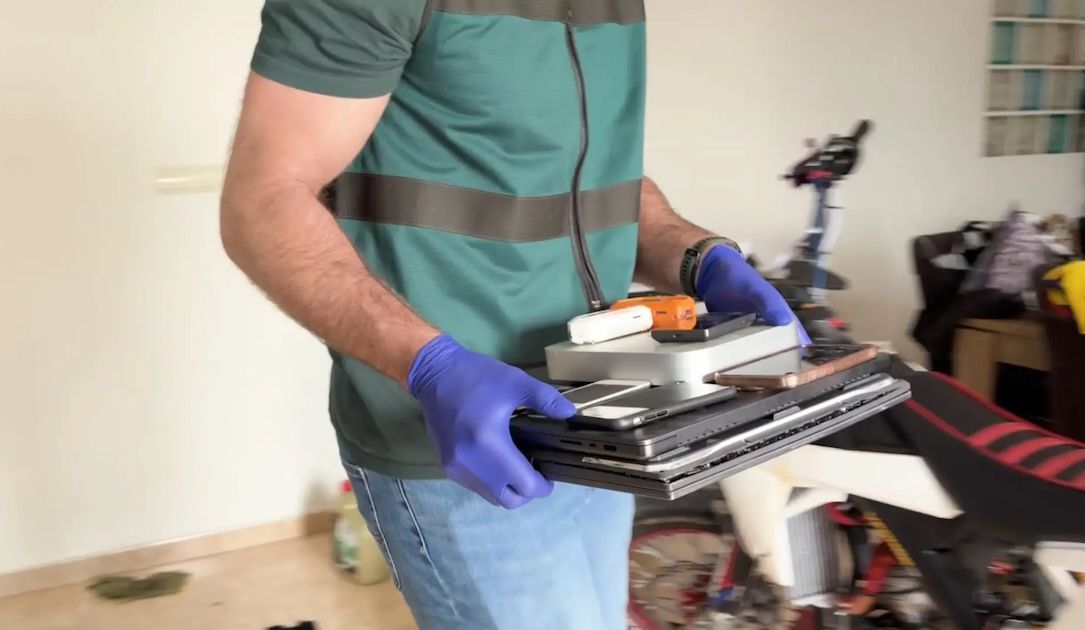
An international law enforcement operation dubbed "Operation KillSwitch" seized the KillSec ransomware gang's data leak site and servers, led to three arrests, and identified a 16-year-old as the group's alleged administrator. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Shadow AI explained: The work shortcut that could leak your company’s secrets Moderate Malwarebytes Labs
2026-10-01 Malwarebytes Labs

Shadow AI explained: The work shortcut that could leak your company’s secrets

Using an AI chatbot, assistant, or browser to speed up your work is tempting, but doing it without your employer’s knowledge can put sensitive data at risk. You’re swamped, so you paste a long email thread into a free chatbot and ask for a summary. It works, it saves an hour, and nobody notices. But the thread may contain customer details or confidential pla…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

The Day-One Hole in Zero Trust Architecture Moderate BleepingComputer
2026-10-01 BleepingComputer

The Day-One Hole in Zero Trust Architecture

Zero Trust can verify users once they are established, but onboarding creates a gap where organizations must decide who to trust before strong authentication exists. Specops explains why identity verification should begin before credentials, MFA methods, and access are issued. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

16-year-old suspected leader of KillSec ransomware group arrested Critical Help Net Security
2026-10-01 Help Net Security

16-year-old suspected leader of KillSec ransomware group arrested

A 16-year-old is suspected of being the main operator of KillSec, a ransomware group that Eurojust says is responsible for almost 1,000 attacks worldwide. Seizure notice (Source: Eurojust) According to Eurojust, KillSec has been active since 2024. The group got into organizations’ systems by exploiting poorly secured access, particularly access linked to clo…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
DeepKeep’s AI Lens flags coding agent data leaks and routes destructive commands for approval Moderate Help Net Security
2026-10-01 Help Net Security

DeepKeep’s AI Lens flags coding agent data leaks and routes destructive commands for approval

DeepKeep has announced AI Lens for Developers, a new extension to the company’s AI usage control and runtime protection modules to secure software developers and their coding agents that can write, modify, and execute code on their behalf. The capability gives security teams policy enforcement, audit visibility, and runtime security over coding agents such a…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Kiteworks patches max severity code injection vulnerability Important BleepingComputer
2026-10-01 BleepingComputer

Kiteworks patches max severity code injection vulnerability

Secure file-sharing software company Kiteworks has released security updates to address 126 vulnerabilities, including a max-severity flaw affecting its Email Protection Gateway (EPG) security solution. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Exabeam brings AI-assisted security investigations to data that must stay on-premises Moderate Help Net Security
2026-10-01 Help Net Security

Exabeam brings AI-assisted security investigations to data that must stay on-premises

Exabeam has introduced a new wave of capabilities that bring the Agentic SOC to life in the cloud and on-premises environments, combining AI-driven investigation, execution, and governance. Analyst workflows alone can’t keep pace with machine-speed threats or the growing complexity of goal-driven AI agents and autonomous workflows. The future of the SOC is a…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
RadarFirst helps teams investigate AI bias, data exposure and unintended actions Moderate Help Net Security
2026-10-01 Help Net Security

RadarFirst helps teams investigate AI bias, data exposure and unintended actions

RadarFirst has announced the general availability of Radar AI Incident Management, a purpose-built solution that helps organizations investigate, manage, and document AI-related incidents. As organizations deploy AI across customer experiences, employee workflows, business operations, and decision-making processes, adverse events can create risks that span p…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Inside Gemini 4 Argon, the model Google is testing on its own infrastructure first Moderate SecurityAffairs
2026-10-01 SecurityAffairs

Inside Gemini 4 Argon, the model Google is testing on its own infrastructure first

Google unveils Gemini 4 Argon, a frontier AI model built for coding, enterprise work, and autonomous cybersecurity defense, rolling out to trusted testers. Google announced Gemini 4 Argon, and it’s not going straight to the public. It’s rolling out first to a set of trusted cyber defenders through what Google calls the Fairwind Program, which tells you somet…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Inside Gemini 4 Argon, the model Google is testing on its own infrastructure first Moderate SecurityAffairs
2026-10-01 SecurityAffairs

Inside Gemini 4 Argon, the model Google is testing on its own infrastructure first

Google unveils Gemini 4 Argon, a frontier AI model built for coding, enterprise work, and autonomous cybersecurity defense, rolling out to trusted testers. Google announced Gemini 4 Argon, and it’s not going straight to the public. It’s rolling out first to a set of trusted cyber defenders through what Google calls the Fairwind Program, which tells you somet…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification