
Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 2,629 advisories
Page 57 of 110
Sophos uses agentic AI to show businesses which security fixes deserve funding Moderate Help Net Security
2026-10-01 Help Net Security

Sophos uses agentic AI to show businesses which security fixes deserve funding

Sophos has launched Sophos CISO Advantage, an agentic AI-enabled solution that connects security operations to security strategy. The solution gives organizations a picture of their cyber risk, a prioritized plan to reduce it, and measurable proof of progress, in plain language that business leaders can understand, fund, and act on. Sophos CISO Advantage def…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

AI agent used Zammad zero-days to breach Dutch vulnerability disclosure non-profit Critical Help Net Security
2026-10-01 Help Net Security

AI agent used Zammad zero-days to breach Dutch vulnerability disclosure non-profit

An agentic AI-powered attack that hit the Dutch Institute for Vulnerability Disclosure (DIVD) on September 21 exploited two zero-day vulnerabilities in Zammad, an open-source helpdesk and customer support ticketing system. “Used together, [the two flaws] allowed the attackers to hijack sessions, run code remotely and escalate privileges from the Zammad user …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Legit Security extends automated fixes to vulnerable open-source dependencies Critical Help Net Security
2026-10-01 Help Net Security

Legit Security extends automated fixes to vulnerable open-source dependencies

Legit Security has announced an expansion of its Agentic Remediation capability to cover vulnerabilities found in open-source dependencies, not just first-party code, enabling development teams to move from vulnerability detection to a verified fix without manual triage. The expansion addresses a growing gap in application security: as AI-generated code acce…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
One year later: Sovereign AI and the fight for choice Moderate Cloudflare Security
2026-10-01 Cloudflare Security

One year later: Sovereign AI and the fight for choice

It's Birthday Week, when we traditionally ship presents to the Internet. This year, two of them come from Europe: EuroLLM, which covers all 24 official EU languages, and Apertus, Switzerland's fully open model, trained on more than 1,500 languages. Both were built by public universities and research institutions. Both are coming to Workers AI, and you can re…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Warlock Ransomware Hits Large Spanish, Portuguese Orgs Critical Dark Reading
2026-10-01 Dark Reading

Warlock Ransomware Hits Large Spanish, Portuguese Orgs

A year-old Chinese threat actor looks like a cybercrime gang, acts like a state-associated APT, and attacks organizations in unexpected places.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
How AI Is Changing the Roles Required in the Security Operations Center Moderate Rapid7 Threat Research
2026-10-01 Rapid7 Threat Research

How AI Is Changing the Roles Required in the Security Operations Center

As AI takes on more of the enrichment, correlation, and initial assessment inside the SOC, roles, skills, and KPIs still require deliberate redesign. Security leaders need to decide where automation is dependable, where human judgment should remain decisive, and how teams should be measured when alert handling is no longer the center of the operating model T…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Cyberattack on major Polish invoicing platform exposes customer data Important The Record by Recorded Future
2026-10-01 The Record by Recorded Future

Cyberattack on major Polish invoicing platform exposes customer data

One of Poland’s major online invoicing platforms suffered a data breach that may have exposed information belonging to its users, their customers and business partners.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Pentagon breach exposes personal data of more than 3 million people Critical Help Net Security
2026-10-01 Help Net Security

Pentagon breach exposes personal data of more than 3 million people

The Pentagon’s Defense Manpower Data Center (DMDC) is notifying millions of people that hackers gained access to their personal data. The breach affects 2.76 million living individuals, a group that can include current and former defense personnel and their dependents, along with 294,000 deceased individuals, a Defense Department official told CNN. Establish…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Public PoC Released for Apple CoreGraphics Zero-Day CVE-2026-86950 Critical CVE-2026-86950 SecurityAffairs
2026-10-01 SecurityAffairs

Public PoC Released for Apple CoreGraphics Zero-Day CVE-2026-86950

Apple patched a CoreGraphics zero-day that may have been exploited in targeted attacks. A public PoC for the flaw is now available. Apple patched a zero-day vulnerability, tracked as CVE-2026-86950 , in CoreGraphics that attackers may have exploited to target specific individuals. The flaw is an out-of-bounds write that can lead to arbitrary code execution w…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

How Financial Services Companies Can Modernize Their Software Supply Chain Moderate The Hacker News
2026-10-01 The Hacker News

How Financial Services Companies Can Modernize Their Software Supply Chain

Every security leader at a bank, insurer, or asset manager has had a version of this conversation: Security wants to eliminate a class of vulnerabilities. Engineering explains what it would take to upgrade the platform where they live. Somebody prices out the regression testing. Somebody else raises the change-freeze calendar. The finding gets an exception, …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Convincing Free Mobile phishing emails appear after data breach Critical Malwarebytes Labs
2026-10-01 Malwarebytes Labs

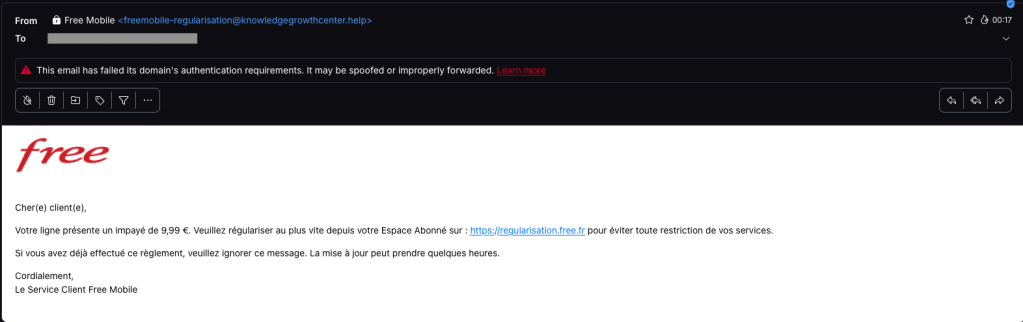
Convincing Free Mobile phishing emails appear after data breach

Free Mobile, one of France’s main cellular providers, was fined €27 million by France’s data protection regulator, the CNIL, in January over failures to protect customer data. The October 2024 breach allowed an unauthorized party to access sensitive customer records, including bank account details and login information. Since the breach, we’ve seen many poor…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Armadin raises $255.5 million to expand AI offensive security platform Moderate Help Net Security
2026-10-01 Help Net Security

Armadin raises $255.5 million to expand AI offensive security platform

Armadin has raised $255.5 million in Series B funding co-led by Andreessen Horowitz (a16z) and Accel that brings the company’s valuation to over $2.5 billion. The round includes participation from new investors Bain Capital Ventures (BCV) and Redpoint. Existing investors 8VC, Ballistic Ventures, Google Ventures, In-Q-Tel, Kleiner Perkins, and Menlo Ventures …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft enables Windows settings backup by default for orgs Moderate BleepingComputer
2026-10-01 BleepingComputer

Microsoft enables Windows settings backup by default for orgs

Microsoft announced that Windows settings backup and restore is now enabled by default on all Microsoft Entra-joined or Microsoft Entra hybrid-joined enterprise systems upgraded to Windows 11 26H2. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
FBI tells ShinyHunters members to turn themselves in, after arrest of alleged leader Moderate Graham Cluley Security
2026-10-01 Graham Cluley Security

FBI tells ShinyHunters members to turn themselves in, after arrest of alleged leader

The FBI has a very simple message for the ShinyHunters gang: give yourselves up. On Tuesday, FBI cyber division assistant director Brett Leatherman released a video, thanking the Dutch police for arresting a 24-year-old man they believe to be a member of the group, and and who is separately suspected of attempting to arrange two murders. Read more in my arti…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
ShinyHunters suspect arrested, and is now investigated over alleged murder plots Moderate Graham Cluley Security
2026-10-01 Graham Cluley Security

ShinyHunters suspect arrested, and is now investigated over alleged murder plots

An alleged key figure in the ShinyHunters cybercrime group has been arrested in the Netherlands, and - in a sinister twist - the 24-year-old suspect is also being investigated for attempting to arrange two murders. Read more in my article on the Hot for Security blog.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Malwarebytes earns another Top Product award in independent testing Important Malwarebytes Labs
2026-10-01 Malwarebytes Labs

Malwarebytes earns another Top Product award in independent testing

Every few months, Malwarebytes gets a chance to test its mettle against real-world threats in an independent laboratory setting. And the latest round of results gives us plenty to celebrate. Malwarebytes earned a perfect 18 out of 18 and received another Top Product award from AV-TEST. We also achieved Level 1 Certification from MRG Effitas, and we stopped 1…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Pentagon breach exposes Social Security numbers and military records of millions Critical Malwarebytes Labs
2026-10-01 Malwarebytes Labs

Pentagon breach exposes Social Security numbers and military records of millions

The US government is alerting millions of people that their personal information was stolen during a breach of the Pentagon’s personnel records at the Defense Manpower Data Center (DMDC). The DMDC is a central US Department of Defense (DoD) organization that manages personnel records, ID credentials, and benefit entitlements for military and civilian staff, …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
OpenAI Disrupts Reasoning Extraction Campaign Linked to Moonshot AI Associates Moderate The Hacker News
2026-10-01 The Hacker News

OpenAI Disrupts Reasoning Extraction Campaign Linked to Moonshot AI Associates

OpenAI on Wednesday said it identified and disrupted a coordinated distillation campaign that was designed to illicitly extract protected reasoning from its artificial intelligence (AI) models. A "core cluster of the activity," going back to the first week of July, has been attributed to individuals associated with Moonshot AI, a Chinese AI company based in …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CISA Adds Exploited Cisco Catalyst SD-WAN Manager Auth Bypass to KEV Critical CVE-2026-76504 The Hacker News
2026-10-01 The Hacker News

CISA Adds Exploited Cisco Catalyst SD-WAN Manager Auth Bypass to KEV

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added a critical authentication bypass flaw impacting Cisco Catalyst SD-WAN Manager to its Known Exploited Vulnerabilities (KEV), following reports of active exploitation. The vulnerability, tracked as CVE-2026-76504 (CVSS score: 9.8), could allow an unauthenticated, remote attacke…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
New Cisco SD-WAN zero-day exploited in-the-wild (CVE-2026-76504) Critical CVE-2026-76504 Help Net Security
2026-10-01 Help Net Security

New Cisco SD-WAN zero-day exploited in-the-wild (CVE-2026-76504)

For the fifth time this year, Cisco revealed attackers have exploited a vulnerability (CVE-2026-76504) in its SD-WAN solution in zero-day attacks. The vendor’s incident responders became aware of active exploitation of this vulnerability in September 2026, after getting pinged and resolving a Cisco Technical Assistance Center (TAC) support case. Cisco has ye…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The Fine Art of Frustrating the Adversary Moderate Cisco Talos Intelligence
2026-10-01 Cisco Talos Intelligence

The Fine Art of Frustrating the Adversary

For Cybersecurity Awareness Month, eight Cisco Talos researchers share practical ways defenders can frustrate adversaries at different stages of an operation. Deception techniques such as honeypot accounts, false infrastructure, and tarpits can slow adversaries down while giving defenders earlier opportunities to detect their activity. Behavioral detections,…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Hackers stole Pentagon personnel records of over 3 million people Important BleepingComputer
2026-10-01 BleepingComputer

Hackers stole Pentagon personnel records of over 3 million people

The Pentagon's Defense Manpower Data Center (DMDC) is notifying millions of military service members that hackers stole their data after breaching the Pentagon's human resources management system in October 2025. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Losing gamblers pushed to bet more by DraftKings’ AI, report says Moderate Malwarebytes Labs
2026-10-01 Malwarebytes Labs

Losing gamblers pushed to bet more by DraftKings’ AI, report says

Two separate investigations have raised concerns about betting site DraftKings’ marketing to target problem gamblers, including its use of AI. On September 19, the New York Times reported that the company’s machine learning model targeted people who were more likely to respond to betting promotions by gambling and losing more money. The model crunched data o…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification