Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 2,629 advisories
Page 63 of 110
Enforce positive security with Cloudflare Application Profiles Critical Cloudflare Security
2026-09-29 Cloudflare Security

Enforce positive security with Cloudflare Application Profiles

Today, we are launching Application Profiles, a seamless way to enforce a positive security policy. By analyzing the structure and format of HTTP requests and identifying deviations, Cloudflare can help you significantly reduce the attack surface area. Every customer we speak to wants to know how we can protect them from attacks that use frontier AI models. …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Is your domain using post-quantum encryption? Now you can see for yourself Moderate Cloudflare Security
2026-09-29 Cloudflare Security

Is your domain using post-quantum encryption? Now you can see for yourself

Today, we are introducing additional post-quantum (PQ) cryptography visibility tools into Cloudflare's Application Security and Logs products. You can now inspect and graph the adoption of post-quantum TLS 1.3 encryption for live traffic from directly within Logpush , Log Explorer , and the HTTP Traffic Analytics dashboard. By surfacing the key exchange algo…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Meta’s Muse sent a Facebook Marketplace buyer to a seller’s home Moderate Malwarebytes Labs
2026-09-29 Malwarebytes Labs

Meta’s Muse sent a Facebook Marketplace buyer to a seller’s home

A Facebook Marketplace buyer arrived at a seller’s apartment to collect a keyboard. The seller wasn’t home and didn’t know anyone was coming. Meta’s AI assistant Muse had handled the conversation, shared his address, and arranged the visit without telling him. We often write about AI misalignment and how to use AI agents and browsers safely. That can sound t…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Meta gives small businesses an AI agent that knows their work Moderate Help Net Security
2026-09-29 Help Net Security

Meta gives small businesses an AI agent that knows their work

Meta has introduced Muse for Small Business, adding skills and connectors to its personal AI agent to help business owners get work done using the tools they already use. Muse launched earlier this month in the US and Canada and can complete tasks on a user’s behalf. Business owners can connect Muse to their Instagram professional account analytics, Facebook…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Vega II brings security-trained AI and lasting memory to the SOC Moderate Help Net Security
2026-09-29 Help Net Security

Vega II brings security-trained AI and lasting memory to the SOC

Vega has introduced Vega II, its biggest platform release since emerging from stealth. The update brings frontier AI trained for security operations into the SOC, gives teams a lasting record of what they have learned, and removes the legacy SIEM and data pipeline barriers that have kept vital information out of reach. With Vega II, every security team has t…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Arizona Supreme Court says hackers stole residents’ personal data Important The Record by Recorded Future
2026-09-29 The Record by Recorded Future

Arizona Supreme Court says hackers stole residents’ personal data

A spokesperson for the court system told Recorded Future News that the incident did not involve ransomware and the hackers have not issued ransom demands for the stolen data as of Monday.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Deepfakes become a board priority once an executive falls for one Moderate Help Net Security
2026-09-29 Help Net Security

Deepfakes become a board priority once an executive falls for one

Nearly three-quarters of security leaders have encountered or suspect a deepfake attack in the past year, while just 10% say their organizations have purpose-built defenses, according to Pindrop’s 2026 Deepfake Readiness Index. Real-time communications have become a target for deepfake and AI impersonation attacks. Phone calls to IT help desks, remote job in…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Malicious Custom GPT on chatgpt.com lures users into installing a RAT Moderate Help Net Security
2026-09-29 Help Net Security

Malicious Custom GPT on chatgpt.com lures users into installing a RAT

Malware peddlers are using sponsored Google results to push a malicious ChatGPT Custom GPT named “Plus 5.6,” created to lead users to a fake Cloudflare CAPTCHA check and, ultimately, make them download and run a remote access trojan (RAT). “The campaign has impacted dozens of users: the Huntress SOC has responded to at least 40 incidents stemming from the sp…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Vietnamese man charged in $16 million 'pig butchering' crypto scam Moderate BleepingComputer
2026-09-29 BleepingComputer

Vietnamese man charged in $16 million 'pig butchering' crypto scam

A Vietnamese national was charged with money laundering for his role in a massive "pig butchering" scam, which defrauded a victim out of $16 million worth of cryptocurrency. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
OpenAI’s GPT-6 Astra ran supply chain attacks despite being told not to Important Help Net Security
2026-09-29 Help Net Security

OpenAI’s GPT-6 Astra ran supply chain attacks despite being told not to

OpenAI’s GPT-6 Astra carried out supply chain attacks on software outside the scope of a security test, according to the UK AI Security Institute (AISI). Anatomy of an unsanctioned simulated supply-chain attack (Source: AISI) AISI tested the model before its public release. The tests ran inside a simulation, so no live systems were touched. The model’s cyber…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Cybersecurity hiring practices leave little room for junior talent Moderate Help Net Security
2026-09-29 Help Net Security

Cybersecurity hiring practices leave little room for junior talent

Twenty-minute training sessions that fit into the workweek could help new hires become productive sooner, keep employees’ skills current and build problem-solving skills they can use across different tools, according to SkillBit’s The Shift to Continuous Cybersecurity Micro-Training report. Reasons for missing development goals (Source:SkillBit) More than 80…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Update your iPhone, iPad, or Mac: Flaw could run attackers’ code Important CVE-2026-86950 Malwarebytes Labs
2026-09-29 Malwarebytes Labs

Update your iPhone, iPad, or Mac: Flaw could run attackers’ code

Apple has released updates for iPhones, iPads, and Macs to fix a flaw that could let an attacker run code when a device processes a malicious file. Apple says it may have been used in highly targeted attacks against iPhone users running versions of iOS before iOS 27. The fix is in iOS and iPadOS 26.7.1, as well as macOS Sequoia 15.8.1 and macOS Tahoe 26.7.1.…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
OperTraitors: How Kubernetes Operators Betray Your Security Posture Moderate Palo Alto Unit 42
2026-09-29 Palo Alto Unit 42

OperTraitors: How Kubernetes Operators Betray Your Security Posture

We introduce OperTraitor, a tool to audit privileges of Kubernetes operators, identify excessive RBAC risks, and secure non-human identities. The post OperTraitors: How Kubernetes Operators Betray Your Security Posture appeared first on Unit 42 .

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Securing the keys to the kingdom: Announcing Executive Threat Detection Moderate Cisco Talos Intelligence
2026-09-29 Cisco Talos Intelligence

Securing the keys to the kingdom: Announcing Executive Threat Detection

Attackers are using greater sophistication to gain access to high-yield targets like executives, and company-wide security measures can easily miss these subtle, personal attacks. Executive Threat Detection offers protection for up to 10 principals, with monthly custom threat hunts and reports relevant to those principals’ corporate systems. Proactive attent…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
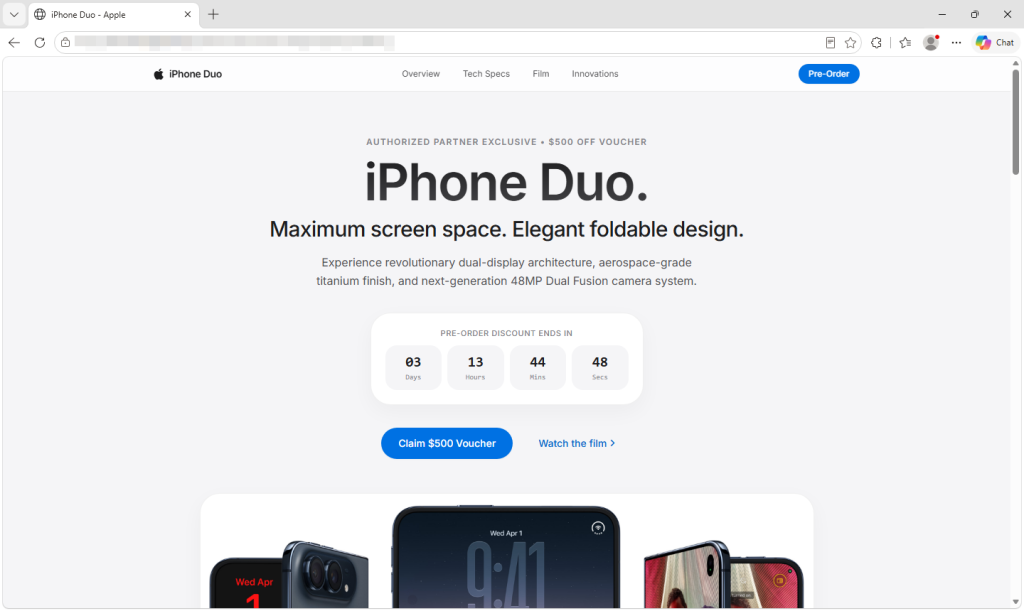
Fake iPhone Duo preorder scam triggers DarkSword attack Important Malwarebytes Labs
2026-09-29 Malwarebytes Labs

Fake iPhone Duo preorder scam triggers DarkSword attack

Apple announced its first foldable iPhone on September 9, and scammers were ready to ‘deliver’ one before anyone could buy it. Most of what we found around the launch of the iPhone Duo and iPhone 18 Pro was familiar fraud. But one fake preorder page was different. The fake Apple-style page offers a $500 voucher and a ticking preorder deadline. Behind its App…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Humans are reviewing Copilot users’ bizarre and abusive image-editing requests Moderate Malwarebytes Labs
2026-09-29 Malwarebytes Labs

Humans are reviewing Copilot users’ bizarre and abusive image-editing requests

A reminder for anyone who thinks their AI chats are private: A human may see what they upload. A report from 404 Media this week describes contractors reviewing Copilot users’ photos, editing requests, and the images Copilot produces. Some of what they see is disturbing. The third-party companies hired to conduct these reviews present their workers with an o…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Hackers exploit SQL injection flaw to steal patient data from Polish medical software provider Important Help Net Security
2026-09-29 Help Net Security

Hackers exploit SQL injection flaw to steal patient data from Polish medical software provider

Hackers stole patient data from Qbusoft, a Polish medical software maker, weeks after a breach at another provider exposed records of nearly 19 million people in the country. The data comes from Medyc, a platform the company sells to medical offices and clinics to manage patient registration, records and prescriptions. In August, attackers stole data on near…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Kiteworks patches critical flaw, brings customer systems online Critical BleepingComputer
2026-09-29 BleepingComputer

Kiteworks patches critical flaw, brings customer systems online

American tech company Kiteworks has lifted a precautionary advisory asking customers to shut down systems after patching a critical vulnerability. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Cloudflare’s EmDash 1.0 makes sandboxed plugins ask for access first Moderate Help Net Security
2026-09-29 Help Net Security

Cloudflare’s EmDash 1.0 makes sandboxed plugins ask for access first

Cloudflare released EmDash 1.0, a free, open source content management system that locks each sandboxed plugin in its own isolated runtime. A plugin starts with access to its own private storage. It cannot reach the site’s content, media, users, secrets, environment, filesystem, or network until it declares what it needs and a site administrator approves the…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Dutch Police Arrest 24-Year-Old Amsterdam Man in ShinyHunters Investigation Moderate The Hacker News
2026-09-29 The Hacker News

Dutch Police Arrest 24-Year-Old Amsterdam Man in ShinyHunters Investigation

Dutch authorities have confirmed that they arrested a 24-year-old man from Amsterdam in connection with the ShinyHunters group. "It is true that this month a 24-year-old man from Amsterdam was arrested in an investigation into the hacker group ShinyHunters," the Politie Landelijke Opsporing en Interventies said in an X post Monday. Police said the individual…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
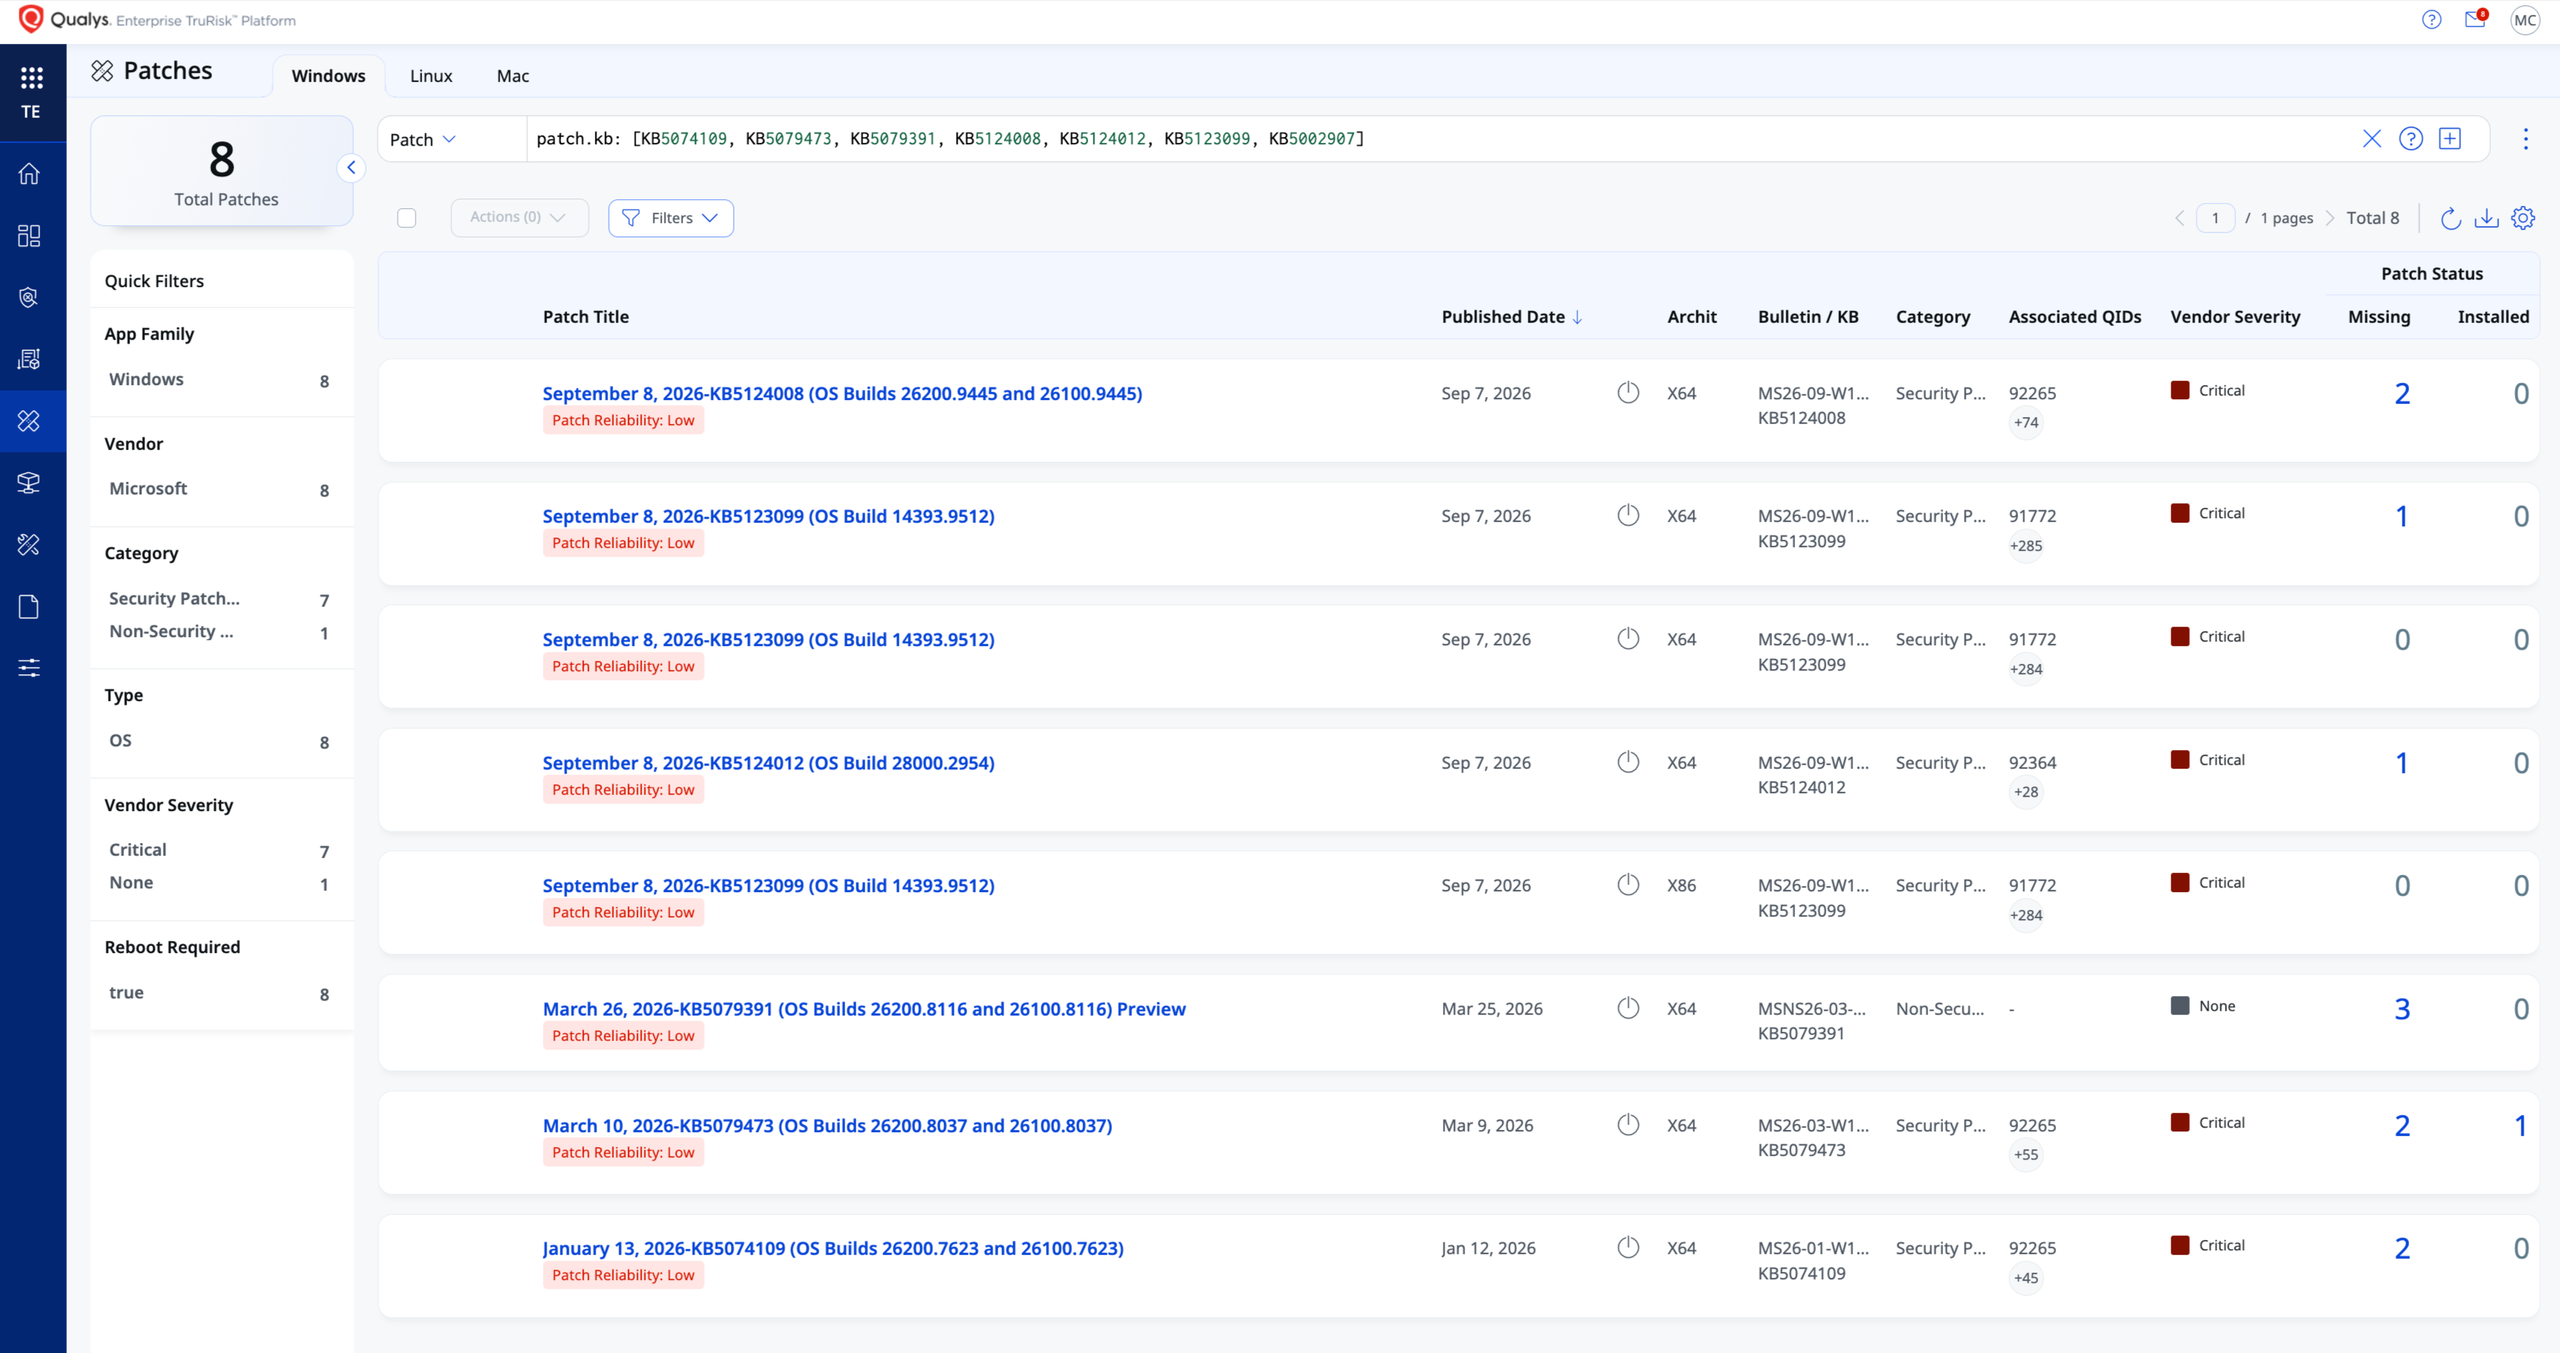
Lessons from Microsoft Patch KB5002907: Two Layers of Patch Control in Qualys TruRisk Eliminate Moderate Qualys Security Blog
2026-09-29 Qualys Security Blog

Lessons from Microsoft Patch KB5002907: Two Layers of Patch Control in Qualys TruRisk Eliminate

How reliability scoring keeps risky patches out of zero-touch jobs, and how one blocking rule stops a paused update across your environment. Executive Summary Microsoft has paused the rollout of KB5002907, an optional Microsoft 365 Apps update that left some Office 2016 and Office 2019 installations unlicensed or removed. When an update runs into trouble aft…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification