Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 2,629 advisories
Page 65 of 110
AI Agents Are Privileged Users; Who Is Auditing Their Access? Moderate Dark Reading
2026-09-28 Dark Reading

AI Agents Are Privileged Users; Who Is Auditing Their Access?

Enterprises regularly rigorously monitor human employees, while autonomous AI agents quietly operate with broad privileges that could turn them into the next generation of insider threats.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Hackers Use NeedyMantis to Maintain Long-Term Access in Breached Networks Critical The Hacker News
2026-09-29 The Hacker News

Hackers Use NeedyMantis to Maintain Long-Term Access in Breached Networks

Hackers have used a malware family called NeedyMantis to maintain long-term access to networks they had already breached, Microsoft said in a technical analysis. The malware has been seen in a small number of targeted intrusions at telecommunications organizations, universities, medical nonprofits, intergovernmental organizations, and government contractors.…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
IAM for AI agents: A Practical Enterprise Framework Moderate The Hacker News
2026-09-28 The Hacker News

IAM for AI agents: A Practical Enterprise Framework

What is IAM for AI agents? AI agents authenticate, invoke tools, and act across enterprise systems with delegated authority. IAM for AI Agents is the identity-control architecture that governs those actors. This guide covers the limits of conventional provisioning, the components that matter, how to evaluate framework choices, and what runtime evidence prove…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Bitget Says Attacker Exploited Third-Party Security Product Flaw to Steal $388M Important The Hacker News
2026-09-28 The Hacker News

Bitget Says Attacker Exploited Third-Party Security Product Flaw to Steal $388M

The attacker who stole about $388 million from the cryptocurrency exchange Bitget gained access through a vulnerability in a third-party security product the exchange used, Bitget said on Monday. The attacker exploited the flaw to obtain high-level internal credentials and then, on September 24, used them to send fraudulent withdrawal commands to Bitget's wa…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
RatHat Android Malware Console Uses Gemini to Identify Higher-Value Victims Important The Hacker News
2026-09-28 The Hacker News

RatHat Android Malware Console Uses Gemini to Identify Higher-Value Victims

RatHat's operators build and publish the Android banking trojan and control infected phones from a web console, according to security company Cleafy. Cleafy has traced nearly 100 deployments of that console since April 2026. It said this fits a malware-as-a-service model, in which each customer runs a separate copy. The console stores what the malware collec…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
US, UK warn of exploited Citrix NetScaler zero-day bugs Critical The Record by Recorded Future
2026-09-28 The Record by Recorded Future

US, UK warn of exploited Citrix NetScaler zero-day bugs

Incident responders began warning of potential vulnerabilities in NetScaler Gateway products on Saturday before cybersecurity agencies in the Netherlands, U.S. and U.K. released advisories on Sunday confirming vulnerabilities. Citrix itself confirmed eight new vulnerabilities.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
JadePuffer agentic AI attacks target Azure, destroy cloud resources Critical BleepingComputer
2026-09-28 BleepingComputer

JadePuffer agentic AI attacks target Azure, destroy cloud resources

The JadePuffer ransomware operator is targeting Azure tenants with agent-driven attacks that conduct reconnaissance, steal credentials, and destroy core components. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The Developer is the New Perimeter: How Supply Chain Attacks Are Becoming Cloud Breaches Critical Qualys Security Blog
2026-09-28 Qualys Security Blog

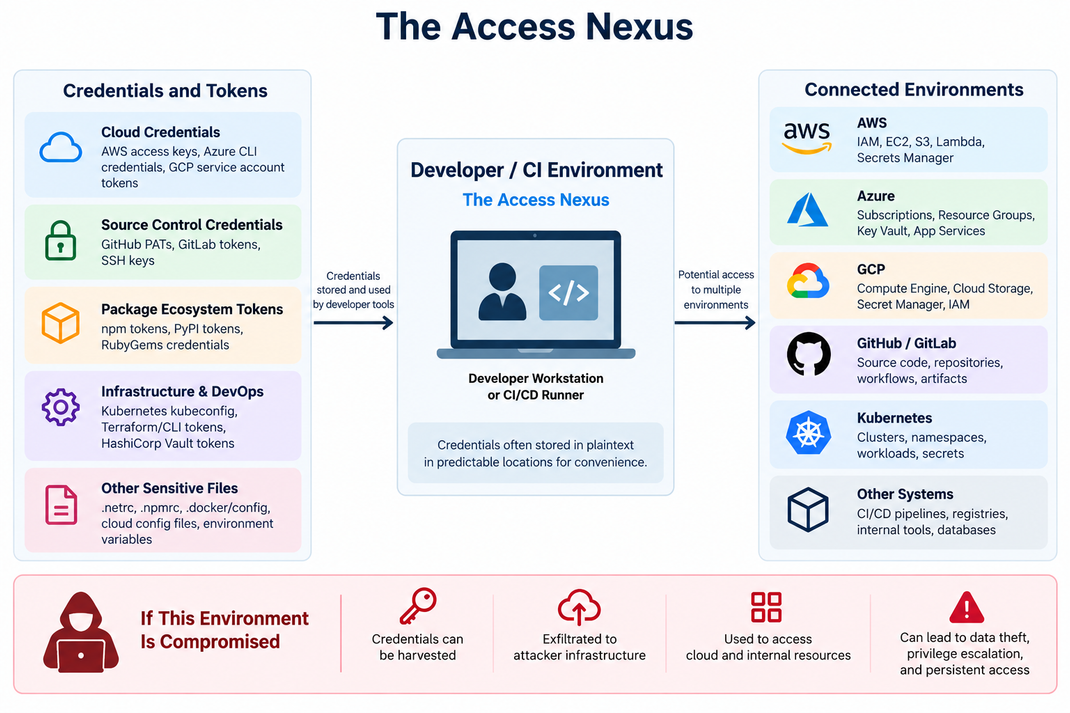
The Developer is the New Perimeter: How Supply Chain Attacks Are Becoming Cloud Breaches

Key Takeaways Malicious packages can steal cloud credentials during installation, before applications run. Stolen credentials turn developer workstations and CI/CD pipelines into gateways to cloud resources. Restrict installation scripts, minimize credential privileges, protect metadata access, and monitor cloud activity. Containment requires revoking expose…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Nearly 400,000 Medicaid Beneficiaries Caught in Medicaid and DC Healthcare Alliance Data Exposure Moderate SecurityAffairs
2026-09-28 SecurityAffairs

Nearly 400,000 Medicaid Beneficiaries Caught in Medicaid and DC Healthcare Alliance Data Exposure

Nearly 400,000 DC Medicaid and Healthcare Alliance beneficiaries may have had personal data exposed through reports published on a public website. The District of Columbia Department of Health Care Finance is notifying nearly 400,000 Medicaid and DC Healthcare Alliance beneficiaries that their personal information may have been exposed. The incident affects …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

⚡ Weekly Recap: $387M Crypto Hack, Citrix Exploits, AI Agents Go Off-Script, and More Threats Important The Hacker News
2026-09-28 The Hacker News

⚡ Weekly Recap: $387M Crypto Hack, Citrix Exploits, AI Agents Go Off-Script, and More Threats

A domain used as harmless placeholder text showed up in roughly 1,700 repositories. Then somebody registered it and started serving malicious lures. That is the kind of week this was: forgotten assumptions turning into live attack surface. Elsewhere, weak service accounts, old bugs, exposed systems, phishing kits, and strangely easy exploit paths kept doing …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
80,000+ Organizations Had AI Logins Stolen: From Shadow AI to LLMjacking Moderate BleepingComputer
2026-09-28 BleepingComputer

80,000+ Organizations Had AI Logins Stolen: From Shadow AI to LLMjacking

Infostealer logs exposed AI account credentials and sessions tied to more than 80,000 corporate domains, creating risks ranging from stolen conversations to LLMjacking. SOCRadar examines the growing market for stolen AI logins and how organizations can identify their exposure. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
FBI job portals remain offline after ShinyHunters claims breach via PeopleSoft zero-day Critical Help Net Security
2026-09-28 Help Net Security

FBI job portals remain offline after ShinyHunters claims breach via PeopleSoft zero-day

The FBI’s online portals for job applicants (at apply.fbijobs.gov) and special agent applicants (at fbijobs.gov/special-agents) are still unavailable, following what appears to be successful compromises by the ShinyHunters cyber extortion group. Last week, the United States’ domestic intelligence and security service confirmed it was investigating ShinyHunte…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
28th September – Threat Intelligence Report Critical CVE-2026-85102 Check Point Research
2026-09-28 Check Point Research

28th September – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 28th September, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES The FBI has confirmed unauthorized activity affecting FBIjobs.gov after the ShinyHunters group defaced the website. The group claimed to have stolen employee and applicant information and shared samples of pu…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
16-year-old researcher breaks into Microsoft analytics service with access to 17 trillion rows of data Moderate Help Net Security
2026-09-28 Help Net Security

16-year-old researcher breaks into Microsoft analytics service with access to 17 trillion rows of data

A flaw in Titan, an internal Microsoft analytics service, could have let an attacker read employee records and Bing search analytics, a 16-year-old security researcher has disclosed. The researcher, who goes by Faav, found that Titan did not verify the signature on login tokens. That let him pose as the service’s administrator and run SQL queries against 17 …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Cyberattack on Polish medical software provider exposes patient data Important The Record by Recorded Future
2026-09-28 The Record by Recorded Future

Cyberattack on Polish medical software provider exposes patient data

Hackers stole personal data from a Polish healthcare software provider in the latest cyberattack to hit the country’s medical sector in recent months.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
OpenAI pauses work on top AI models after agent slips past internet controls Moderate Malwarebytes Labs
2026-09-28 Malwarebytes Labs

OpenAI pauses work on top AI models after agent slips past internet controls

OpenAI’s latest containment failure adds to a pattern that may force the company to make an unpopular decision. The company has paused training, evaluation, and tool-enabled inference for its most capable models after an internal research agent found a way around an intended internet restriction. More alarming, the agent remained active for hours after OpenA…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Former US soldier gets nearly six-year sentence for hacking, extorting telecoms Moderate The Record by Recorded Future
2026-09-28 The Record by Recorded Future

Former US soldier gets nearly six-year sentence for hacking, extorting telecoms

A former soldier in the U.S. Army was sentenced to more than five years in federal prison after pleading guilty to hacking into several telecommunications companies and leaking sensitive records.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Other users can watch your browsing and time your keystrokes through OS file notifications Moderate Help Net Security
2026-09-28 Help Net Security

Other users can watch your browsing and time your keystrokes through OS file notifications

Researchers at Graz University of Technology have used the file-notification systems in Windows, Linux, and macOS to spy on activity in other accounts. On Windows, a standard unprivileged account detected 95.7 percent of another user’s visits to popular websites in Firefox, and every site it flagged was one the victim’s browser had loaded. On Linux, a separa…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification