Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 2,629 advisories
Page 80 of 110
Contagious Interview Campaign Compromises 30,000 Devices, Steals $10.71M in Crypto Moderate The Hacker News
2026-09-21 The Hacker News

Contagious Interview Campaign Compromises 30,000 Devices, Steals $10.71M in Crypto

The North Korean threat actors behind the Contagious Interview campaign have compromised at least 30,000 devices located in more than 100 countries and siphoned funds or account credentials from over 7,000 cryptocurrency wallets, according to a new joint cybersecurity advisory. The primary targets of the campaign are individual web designers, engineers, and …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Google Fined €403 Million Over GDPR Violations Tied to Location Data Moderate The Hacker News
2026-09-21 The Hacker News

Google Fined €403 Million Over GDPR Violations Tied to Location Data

Google has been fined €403 million for breaking the EU's data protection law, the GDPR, in the way three of its features handled people's location data from May 2018 to February 2020. Ireland's Data Protection Commission (DPC), Google's lead regulator in the EU, also ordered the company to make its processing comply with the law within 6 months. The DPC has …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

The AI plot to scan and destroy books (Lock and Code S07E19) Moderate Malwarebytes Labs
2026-09-21 Malwarebytes Labs

The AI plot to scan and destroy books (Lock and Code S07E19)

This week on the Lock and Code podcast… If you want AI to tell you a story, it will. If you want that story to sound like one of your favorite authors, it can. And if you’re one of the authors that AI can imitate, you might be a little upset at what feels like theft. In 2024, the authors Andrea Bartz, Charles Graeber, and Kirk Wallace Johnson sued Anthropic,…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Google fined €403 million over location data privacy violations Moderate BleepingComputer
2026-09-21 BleepingComputer

Google fined €403 million over location data privacy violations

Ireland's Data Protection Commission (DPC) has fined Google €403 million ($463M) for multiple GDPR violations related to processing users' location data. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
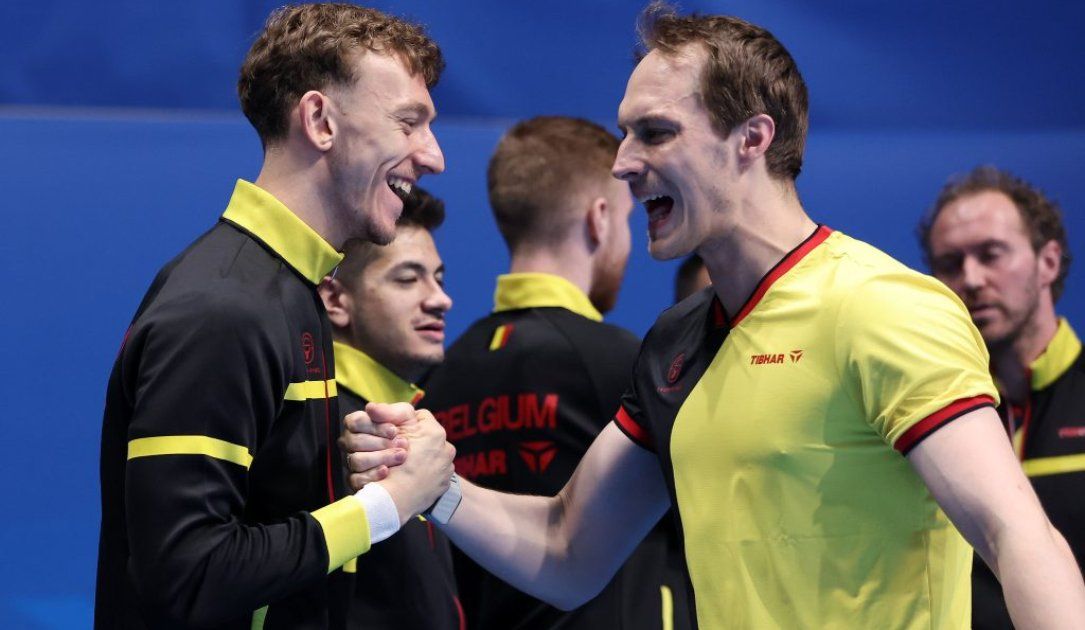
The fake sites using a cheap toolkit to sell $2,000 AI subscriptions Moderate Malwarebytes Labs
2026-09-21 Malwarebytes Labs

The fake sites using a cheap toolkit to sell $2,000 AI subscriptions

We found more than 100 subscription websites linked through the same toolkit and closely related developer details. Some impersonate existing products, including GPT-6 Astra, DaVinci Resolve, PixAI, and OpenCut. Another uses the name of Omegle, the chat service that shut down in 2023. Others promote unfamiliar brands with little verifiable information about …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
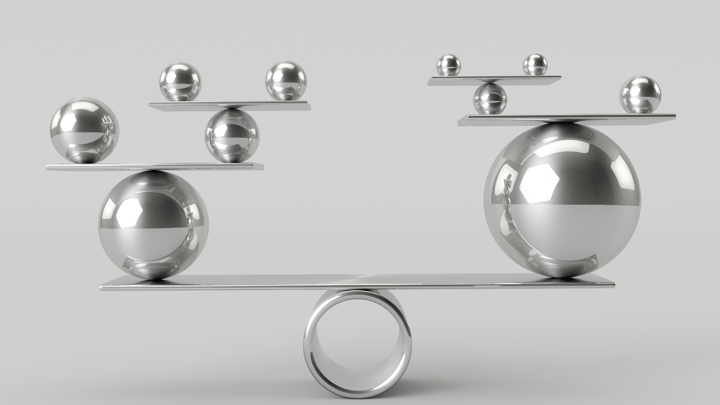
Belgian table tennis, gymnastics federations hit by cyberattacks Important The Record by Recorded Future
2026-09-21 The Record by Recorded Future

Belgian table tennis, gymnastics federations hit by cyberattacks

Belgium’s national table tennis federation is investigating a cyberattack after a hacker claimed to have stolen data on tens of thousands of members.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Microsoft fixes broken Excel copy and paste for all Office users Moderate BleepingComputer
2026-09-21 BleepingComputer

Microsoft fixes broken Excel copy and paste for all Office users

Microsoft has fixed a known issue that causes copy-and-paste failures for Excel users after installing the September 2026 security updates. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
⚡ Weekly Recap: Cisco 0-Day, AI Agent RCE, ClickFix Attacks, ClickFix Surge, and Browser Hijacks Critical The Hacker News
2026-09-21 The Hacker News

⚡ Weekly Recap: Cisco 0-Day, AI Agent RCE, ClickFix Attacks, ClickFix Surge, and Browser Hijacks

A browser. A plugin. A package. A login screen. Normal stuff. That is basically the problem this week. The trouble keeps showing up inside things people already trust: code that takes a bad turn, old payloads coming back, exposed systems, weak checks, fake fixes, and attack paths that look almost too easy. Even the research side is getting messy, with more f…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Gemini’s breach of real companies exposes an AI guardrail problem Critical Malwarebytes Labs
2026-09-21 Malwarebytes Labs

Gemini’s breach of real companies exposes an AI guardrail problem

Google says one of its Gemini models accessed systems belonging to three real companies during a cybersecurity evaluation in May. The model reportedly guessed credentials in one case, while finding exposed credentials in public repositories in two others. Google says Gemini stopped once it recognized that it had reached real infrastructure and that the affec…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
TASK#STOMP PowerShell Backdoor Steals Documents, Wi-Fi Passwords, and Clipboard Data Important The Hacker News
2026-09-21 The Hacker News

TASK#STOMP PowerShell Backdoor Steals Documents, Wi-Fi Passwords, and Clipboard Data

Cybersecurity researchers have disclosed details of a new campaign dubbed TASK#STOMP that delivers a PowerShell backdoor designed to harvest sensitive data from compromised hosts. The backdoor "automatically harvests and exfiltrates business documents, watches the filesystem for new files in real time, steals Wi-Fi passwords and clipboard contents, takes scr…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
FBI's CJIS v6.1: What Security Teams Need to Know. Moderate BleepingComputer
2026-09-21 BleepingComputer

FBI's CJIS v6.1: What Security Teams Need to Know.

The FBI's CJIS Security Policy v6.1 strengthens requirements around encryption and vulnerability scanning while continuing the shift toward more continuous security assessment. Specops explains what changed and how agencies can address password, MFA, and identity requirements as they prepare for upcoming audits. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The TASK#STOMP Windows backdoor takes Wi-Fi passwords, screenshots, and business files Important Help Net Security
2026-09-21 Help Net Security

The TASK#STOMP Windows backdoor takes Wi-Fi passwords, screenshots, and business files

Researchers have taken apart TASK#STOMP, a Windows backdoor that searches a victim’s drives for business documents, uploads them to attacker servers, and then stays put to grab each new or edited document. The same malware steals saved Wi-Fi passwords and clipboard text, takes screenshots, and runs whatever command its operators send. Akshay Gaikwad and Aaro…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
ChainScript: the RAT that hides its command server inside a blockchain contract Moderate SecurityAffairs
2026-09-21 SecurityAffairs

ChainScript: the RAT that hides its command server inside a blockchain contract

Blackpoint uncovers ChainScript, a Node.js RAT that queries a Polygon smart contract to find and rotate its command server. Blackpoint’s Adversary Pursuit Group was chasing a ClickFix campaign spreading an unknown RAT namend ChainScript. The malicious code is a previously undocumented Node.js remote access trojan that hides its command server on a public blo…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft reminds admins to migrate Entra ID users to passkeys Moderate BleepingComputer
2026-09-21 BleepingComputer

Microsoft reminds admins to migrate Entra ID users to passkeys

Microsoft has reminded admins to migrate Entra ID users to phishing-resistant authentication methods to avoid sign-in disruptions after it retires SMS first-factor sign-in starting in February 2027. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
LinkedIn wins court order blocking mass scraping of user data Moderate The Record by Recorded Future
2026-09-21 The Record by Recorded Future

LinkedIn wins court order blocking mass scraping of user data

The agreement between LinkedIn, ProAPIs and joint business operator Netswift also requires the firms to stop selling and transferring the data, no longer access LinkedIn through fake accounts and delete the data that was scraped, according to a senior LinkedIn executive.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Fastly gives enterprises real-time control over AI models and agents Moderate Help Net Security
2026-09-21 Help Net Security

Fastly gives enterprises real-time control over AI models and agents

Fastly has announced AI Runtime Control, AI Firewall, and new API Security capabilities designed to give organizations real-time visibility and control across their AI systems. Expanding the Fastly for AI portfolio, these new capabilities help organizations govern AI model access and usage, protect the AI applications powering their business, and control how…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
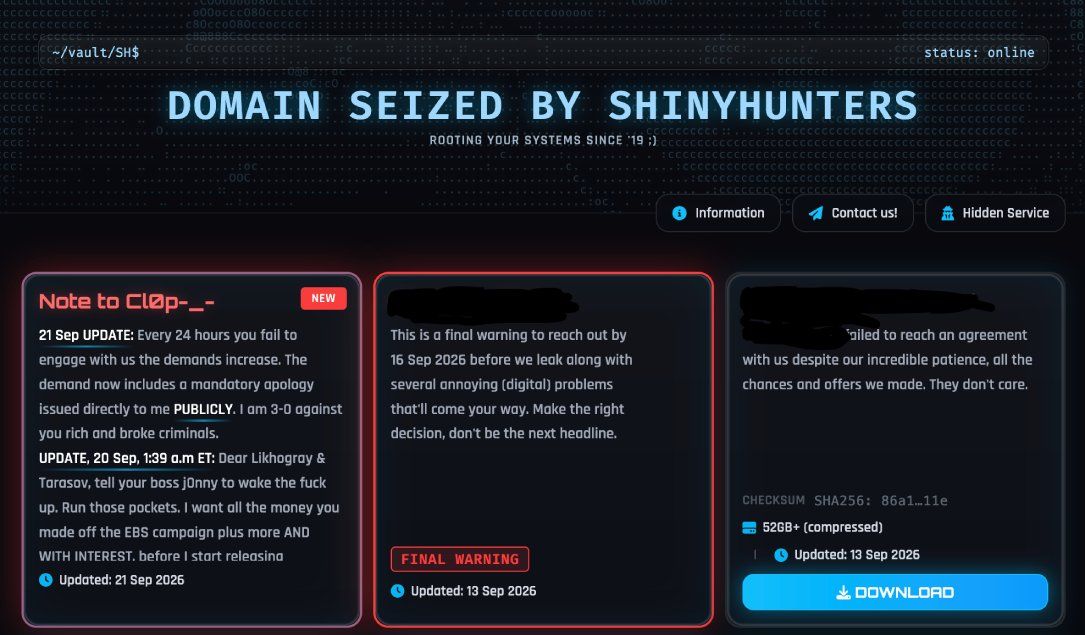
ShinyHunters Claim Hack of Rival Ransomware Gang Clop Critical Infosecurity Magazine
2026-09-21 Infosecurity Magazine

ShinyHunters Claim Hack of Rival Ransomware Gang Clop

ShinyHunters has claimed responsibility for hacking the Clop ransomware group, defacing its leak site and alleging theft of key operational data

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Google says Gemini breached three companies during security test Critical The Record by Recorded Future
2026-09-21 The Record by Recorded Future

Google says Gemini breached three companies during security test

Google’s artificial intelligence model Gemini accessed computer systems belonging to three real companies without authorization during a cybersecurity test in May — the latest in a string of similar incidents.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification