
Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 2,629 advisories
Page 81 of 110
North Korea’s job interview scam runs both ways Moderate Help Net Security
2026-09-21 Help Net Security

North Korea’s job interview scam runs both ways

Attackers are targeting members of the Rust Project and maintainers of widely used crates (Rust code libraries), dangling attractive opportunities to compromise their devices and accounts and, ultimately, publish malware. The warning came last week from the Rust Project’s crates.io team and security response working group, and described a recurring pattern: …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Google hit with €403 million GDPR fine over location tracking Moderate Help Net Security
2026-09-21 Help Net Security

Google hit with €403 million GDPR fine over location tracking

Ireland’s Data Protection Commission (DPC) has fined Google €403 million (about $463 million) over its processing of users’ location data and ordered the company to bring that processing into compliance within six months. The inquiry examined Google’s practices from May 25, 2018, to February 4, 2020. The DPC launched it on its own initiative in February 2020…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft: September updates break File History backup feature Moderate BleepingComputer
2026-09-21 BleepingComputer

Microsoft: September updates break File History backup feature

Microsoft warned that the built-in File History backup feature in Windows may stop working on some systems after installing the September 2026 security updates. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Scammers impersonate cops, use arrest threats to extort victims Important Help Net Security
2026-09-21 Help Net Security

Scammers impersonate cops, use arrest threats to extort victims

Scammers are posing as police officers and federal agents, threatening arrest unless victims pay up, the FBI warns. The FBI’s Internet Crime Complaint Center (IC3) updated an alert it first issued in 2022, citing “losses totaling more than $1.6 billion” between January 2025 and July 2026. According to the FBI, most complaints involve a caller who accuses the…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
TerminalFix: PNG Steganography, (Mon, Sep 21st) Moderate SANS Internet Storm Center
2026-09-21 SANS Internet Storm Center

TerminalFix: PNG Steganography, (Mon, Sep 21st)

Microsoft Security Research published an interesting blog post "TerminalFix campaign deploys a reverse tunnel through multistage intrusion" about a malware campaign. The aspect that I want to take a closer look at, is the fact that the threat actors used PNG files with steganography. I reached out to the researchers and they kindly shared the IOCs for the PN…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
A BYD Shark 6 Hack Shows the Risks of Connected Cars Moderate SecurityAffairs
2026-09-21 SecurityAffairs

A BYD Shark 6 Hack Shows the Risks of Connected Cars

A BYD Shark 6 was remotely hacked, exposing vehicle controls, location tracking and cabin audio, raising serious connected-car security concerns. A journalist drove a BYD Shark 6 down a country road outside Canberra while a hacker sitting on the shoulder killed the headlights with a keystroke. That’s not a hypothetical. It’s what happened during a two week t…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

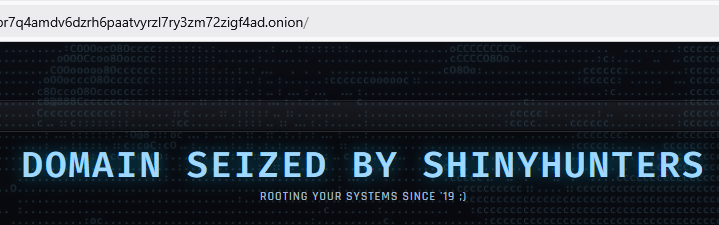
ShinyHunters hacks rival extortion gang and takes over its dark web site Moderate Malwarebytes Labs
2026-09-21 Malwarebytes Labs

ShinyHunters hacks rival extortion gang and takes over its dark web site

Reportedly , the ShinyHunters extortion group breached the leak site of one of its competitors, the Clop ransomware gang. ShinyHunters is a financially motivated cybercrime and extortion group active since 2019. It is known for stealing large volumes of data and pressuring victims to pay, rather than necessarily deploying ransomware. One recent high-profile …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Group Policy hijacked: PAYLOAD ransomware weaponizes Active Directory GPO Critical Kaspersky Securelist
2026-09-21 Kaspersky Securelist

Group Policy hijacked: PAYLOAD ransomware weaponizes Active Directory GPO

Executive summary In April 2026, we at Kaspersky’s Global Emergency Response Team (GERT) responded to a security incident at a manufacturing organization in the Middle East. The threat actor obtained domain admin-equivalent control of the organization’s Active Directory environment and authored a malicious Group Policy Object (GPO) named PAYLOAD, linking it …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
From Exposure to Lockdown: How AWS Neutralizes Compromised IAM Credentials through Managed Policies Moderate Palo Alto Unit 42
2026-09-21 Palo Alto Unit 42

From Exposure to Lockdown: How AWS Neutralizes Compromised IAM Credentials through Managed Policies

We explore how AWS neutralizes exposed IAM credentials using managed policies, detailing GitHub secret scanning and CloudTrail monitoring strategies. The post From Exposure to Lockdown: How AWS Neutralizes Compromised IAM Credentials through Managed Policies appeared first on Unit 42 .

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Siemba brings continuous IDOR testing to production APIs Moderate Help Net Security
2026-09-21 Help Net Security

Siemba brings continuous IDOR testing to production APIs

Siemba has announced automated testing for insecure direct object reference (IDOR) as part of its API Security Testing capability, which tests REST, GraphQL and SOAP APIs for the vulnerability classes most likely to expose customer data. A 200-endpoint API collection can be tested for IDOR in under an hour. The same coverage has typically taken a human teste…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Hackers exploit Gyazo server flaw to steal 23.6 million user records Important Help Net Security
2026-09-21 Help Net Security

Hackers exploit Gyazo server flaw to steal 23.6 million user records

Japanese software company Helpfeel has confirmed a data breach on its screenshot-sharing platform Gyazo, in which attackers exploited a vulnerability in its image upload server, stealing approximately 23.62 million user records and metadata tied to hundreds of millions of images. Gyazo is a cloud-based screenshot and screen-recording service that uploads use…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
ClickFix Lures Deploy ChainScript RAT Using Polygon to Rotate C2 Infrastructure Moderate The Hacker News
2026-09-21 The Hacker News

ClickFix Lures Deploy ChainScript RAT Using Polygon to Rotate C2 Infrastructure

Threat actors are leveraging ClickFix-like lures to deliver a previously undocumented remote access trojan (RAT) called ChainScript. "ChainScript has appeared under multiple build names, including ComponentTask33, UpdateDigital, HostShared, and OrchidViolet66, while presenting itself as Spotify, Zoom Workplace, and Microsoft Teams software," Blackpoint Adver…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The Target Is No Longer the Model. It’s the Agent. Moderate CVE-2025-32711 SecurityAffairs
2026-09-21 SecurityAffairs

The Target Is No Longer the Model. It’s the Agent.

AI agents are becoming the new attack surface, exposed to poisoned skills, prompt injection, jailbreaks and attacks through connected tools. I read the AI security research published in a single month, February 2026, and when you put it all together, it’s not a list of curiosities. It’s a field guide to a new attack surface. In my previous piece, I explained…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
UK Police Data Faces Long-Standing Microsoft Cloud Security Concerns Moderate SecurityAffairs
2026-09-21 SecurityAffairs

UK Police Data Faces Long-Standing Microsoft Cloud Security Concerns

A 2017 UK assessment warned that police data on Microsoft Azure could face foreign access risks. The risks may still exist. A Guardian investigation has surfaced a 2017 document signed off by then City of London police commissioner Ian Dyson, who also held the title of senior information risk owner for the entire country. That document reviewed 15 risks tied…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
A week in security (September 14 – September 20) Moderate Malwarebytes Labs
2026-09-21 Malwarebytes Labs

A week in security (September 14 – September 20)

Last week on Malwarebytes Labs: New Android malware uses AI to steal bank logins and PINs Did an AI really try to break free from human control? Fake parcel delivery messages steal your card and bank details Flock cameras are tracking people as well as cars Revolut phishing texts appear days after data breach 12 celebrity deepfake websites seized by Manhatta…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Jade Sleet Linked to Indian IT Provider Breach With FLATROOF and ROOFDECK Backdoors Critical The Hacker News
2026-09-21 The Hacker News

Jade Sleet Linked to Indian IT Provider Breach With FLATROOF and ROOFDECK Backdoors

The North Korean threat actor known as Jade Sleet has been attributed to the compromise of an India-based "much smaller organization" in the information technology (IT) services industry, once again highlighting how the adversary continues to target developers to breach target networks. Cybersecurity company SentinelOne, which disclosed details of the activi…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Know what was tested before your SAP ECC migration goes live Moderate Help Net Security
2026-09-21 Help Net Security

Know what was tested before your SAP ECC migration goes live

In this Help Net Security interview, Guilherme Joventino, COO of MIGNOW, explains why some large companies plan to stay on ECC past the 2027 deadline and pay SAP for extended support until 2030. The interview covers what that choice may cost, why fear of disruption stalls projects more often than budget, and what the first ninety days of a phased migration i…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Product showcase: Helmit alerts parents when online conversations show signs of trouble Moderate Help Net Security
2026-09-21 Help Net Security

Product showcase: Helmit alerts parents when online conversations show signs of trouble

Helmit is a parental control app that combines AI-powered social media monitoring with screen time management, web filtering, location tracking, and safety alerts. It identifies potentially concerning interactions and surface the messages associated with an alert. Helmit is available on iOS, Android, macOS, and Windows. Parents can create profiles for their …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Gopass: Open-source command-line password manager for teams Critical Help Net Security
2026-09-21 Help Net Security

Gopass: Open-source command-line password manager for teams

Gopass is a free, open-source password manager that stores credentials in an encrypted store and runs from the command line. Its maintainers built it as a drop-in replacement for pass, the standard Unix password manager. Out of the box, Gopass encrypts each secret with GPG and keeps the store in a git repository. Git gives a team a record of every change and…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Intent injection attacks are a new worry for AI-native 6G networks Important Help Net Security
2026-09-21 Help Net Security

Intent injection attacks are a new worry for AI-native 6G networks

Intent-based networking (IBN) lets operators state the outcome they want and leaves its translation into network policy to software, an approach AI-native 6G designs have moved to the forefront. Researchers at the University of Ottawa and Nokia Bell Labs argue that this abstraction gives attackers new openings, and it tests two machine-learning detectors aga…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
AI compliance issues hit 2 in 5 large companies, and legacy workflows are a big factor Moderate Help Net Security
2026-09-21 Help Net Security

AI compliance issues hit 2 in 5 large companies, and legacy workflows are a big factor

Forty percent of large companies had an AI-related compliance or governance issue in the past 12 months, according to 1,000 senior IT, operations, and transformation leaders surveyed by Sapio Research. Those leaders said process-related problems contributed to 84 percent of the incidents. The researchers trace the exposure to workflows designed around people…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification