No Identity, No Recovery: Cyber Resilience Starts With IAM
The proliferation of enterprise apps and the centrality of cloud identity providers requires an identity security rethink.
Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.
The proliferation of enterprise apps and the centrality of cloud identity providers requires an identity security rethink.
Ledger has confirmed that some of its devices distributed through Southeast Asian reseller CryptoBilis were compromised with a hardware implant that drained users' cryptocurrency wallets. [...]
European food retailers have been affected by two separate disruptive cyberattacks: In France, several supermarket chains have had their freezers tampered with and chilled/frozen products destroyed, while in the Netherlands and Belgium workers at stores owned by Dutch multinational Ahold Delhaize have been dealing with disruption resulting from an unspecifie…
Attackers remotely defrosted refrigerators at multiple French supermarket chains overnight in a cyberattack that reportedly targeted Danfoss refrigeration controllers. [...]
Some meetings last longer than it took attackers to jump on a newly disclosed security flaw this week. Within hours, they were already testing it. That's not much time to read the warning, let alone do something about it. But speed is only part of the problem. A secure connection didn't always mean a safe destination. People offering to fix a ransomware mess…
Leaked documents suggest a multi-pronged operation, with social engineering and more technical attackers working together to manipulate a single target
Key Takeaways Qualys Runtime Vulnerability Reachability for Containers brings runtime evidence directly into vulnerability prioritization. Package presence in a container image does not mean the vulnerable software is actually part of the workload’s live execution. Runtime reachability answers whether the vulnerable software is relevant to a running workload…
For the latest discoveries in cyber research for the week of 12th October, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Denmark’s government has disclosed a breach involving its Central Register of Persons after unauthorized individuals exploited access provided to a private supplier. The incident reportedly exposed personal inf…
A new Windows malware loader called AvisLoader uses encrypted peer-to-peer communications to make command-and-control infrastructure harder to disrupt. Varonis researchers explain how the malware uses ClickFix delivery, shortcut-based persistence, and remote command execution capabilities. [...]
Retail giant Ahold Delhaize, one of the world's largest food retail chains, confirmed today that it had to take some systems offline in response to a "cybersecurity incident" affecting its network. [...]
Attackers are exploiting SonicWall SMA 1000 vulnerability, tracked as CVE-2026-102255 (CVSS score of 10.0), just days after its public disclosure. Attackers have begun exploiting a critical flaw in SonicWall SMA 1000 appliances, tracked as CVE-2026-102255 (CVSS score of 10.0), just days after public disclosure. The vulnerability is a server-side request forg…
GitLab warned users today to immediately patch a maximum-severity vulnerability in the CI/CD Regular Expression Compiler that could let remote attackers run arbitrary code on targeted instances. [...]
An attacker reportedly used a leaked password to abuse a company’s legitimate access to Denmark’s population register (CPR). The weak password is remarkable, but the failure to spot millions of unusual searches made the breach worse. The CPR administration states it identified a serious security incident. By abusing a Danish company’s authorized access to th…
Fahmida Y. Rashid will keep the momentum going as she leads Dark Reading.
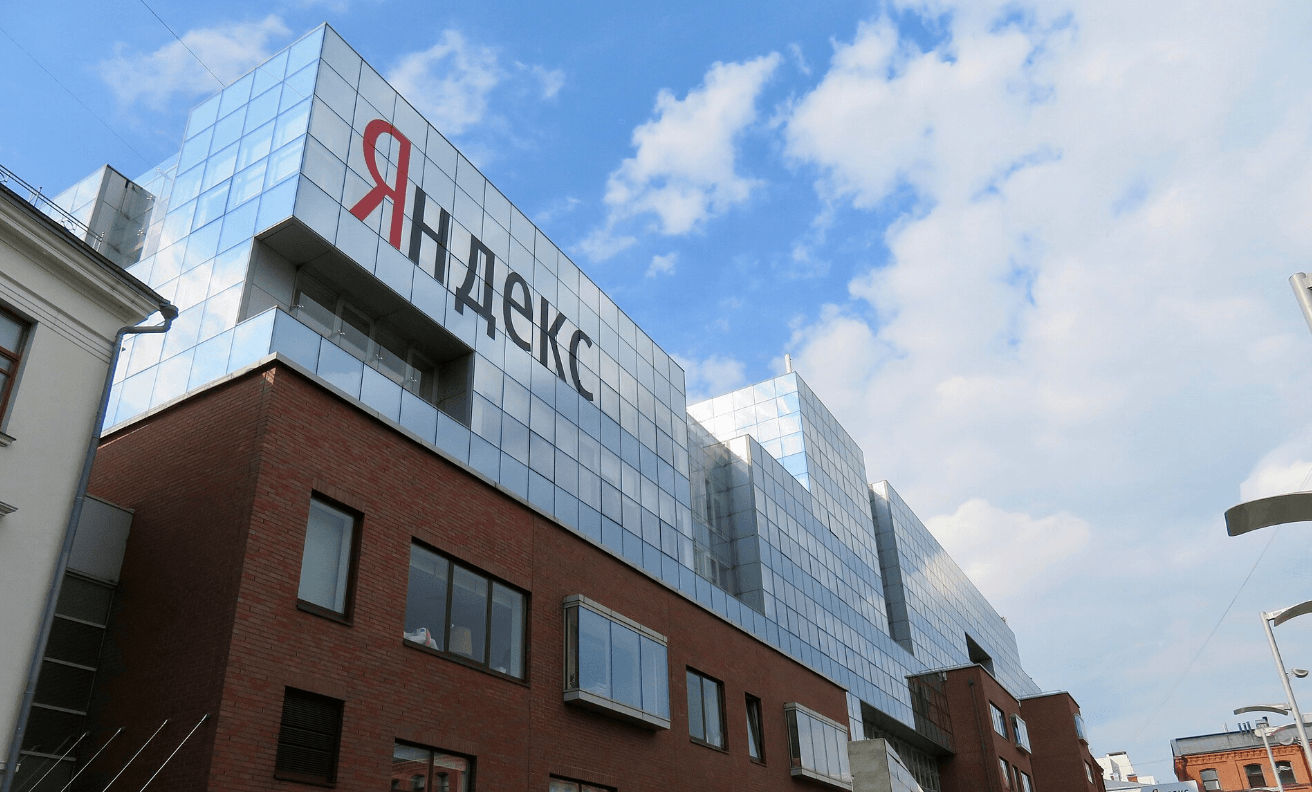
A third Yandex data center in Russia was hit by Ukrainian drones over the weekend, forcing it to shut down and causing further disruptions to cloud services, payments, deliveries and other online services across the country.
Microsoft has reminded customers that systems running Windows 11 23H2 Enterprise, Education, and IoT Enterprise editions will stop receiving security updates next month. [...]
The CEO of Cooperative U confirmed a cyber-attack affected the food stock in several stores from October 11
The personal AI agents rollout is going about as smoothly as expected: Amazon now blocks Meta's Muse because it doesn't identify itself as a bot while browsing; Instinct keeps raising privacy concerns; and the horror stories from pretty much every personal AI agent keep piling up. Regardless, the tech world is mesmerized by the capabilities and potential of …
Cryptocurrency hardware maker Ledger has temporarily paused sales of its products via CryptoBilis following reports of stolen funds linked to devices sold by the reseller. On Friday, the company said it was investigating reports of loss of funds from users in Southeast Asia who had purchased products from CryptoBilis. The incident is said to have resulted in…
Microsoft-Decision-1 is a small decision-scoring model. Given a situation, a question and a fixed set of answer options, it returns a calibrated probability for each option. “This model is designed for routing, classification, prioritization, verification, and workflow control, making it easier to incorporate decision intelligence into existing applications,…
You ignored the suspicious email. You didn’t open the attachment, click the link, or reply to the sender. Then you asked your AI assistant to summarize your inbox. Could the message you wisely avoided find its way back onto your to-do list—only this time presented as an urgent recommendation from a tool you trust? That’s the risk behind phishing emails conta…
People who buy low-cost Android phones from online marketplaces may be carrying malware that was placed on the device before it reached them, Bitdefender has found. The campaign, dubbed Midnight Mimosa, runs on budget Android devices from different brands built on MediaTek platforms. The malware ships in the device firmware, is present before the owner switc…
Threat actors have been observed exploiting a recently disclosed critical security flaw in SonicWall Secure Mobile Access (SMA) 1000 appliances within days of public disclosure. The vulnerability, tracked as CVE-2026-102255 (CVSS score: 10.0), is a case of pre-authenticated server-side request forgery (SSRF) that could allow a remote attacker "to direct the …
The FBI has arrested a Canadian cybersecurity executive as it continues its crackdown on ShinyHunters