
Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 2,629 advisories
Page 86 of 110
Windows 11 24H2 Home and Pro reach end of support in October Moderate BleepingComputer
2026-09-17 BleepingComputer

Windows 11 24H2 Home and Pro reach end of support in October

Microsoft reminded customers this week that devices running Windows 11 24H2 Home and Pro editions will stop receiving updates next month. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

A fake ChatGPT billing email is after your OpenAI password Moderate Help Net Security
2026-09-17 Help Net Security

A fake ChatGPT billing email is after your OpenAI password

A fake ChatGPT billing email is steering users to a copy of the OpenAI login page that keeps whatever username and password they type. Josh Varden of Cofense’s Phishing Defense Center traced the email’s payment button through a Google redirect to the attacker’s page. The lure targets ChatGPT users on work and personal accounts alike, and it copies the kind o…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The Odyssey and Trojans again: MovieReaper attacks users in multiple countries through compromised torrents Important Kaspersky Securelist
2026-09-17 Kaspersky Securelist

The Odyssey and Trojans again: MovieReaper attacks users in multiple countries through compromised torrents

Introduction Torrent trackers have long been abused for distributing malicious software, disguised as popular films, games, and other content. Our previous research has shown that cybercriminals repeatedly turn to torrents as an initial infection vector, using trojanized cracks and installers to reach a large number of users. Installation guides for pirated …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Download: The IT leader’s guide to AI code sprawl Moderate Help Net Security
2026-09-17 Help Net Security

Download: The IT leader’s guide to AI code sprawl

AI hasn’t just made building faster, it’s made everyone a builder. Across every department, employees are shipping apps, agents and automations using AI tools, often without knowing they’ve created something that needs governing at all. The result: AI code sprawl is taking root, increasing risk, compromising compliance, and wasting resources. The usual respo…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CISA wants critical infrastructure orgs and smaller security teams to start using cyber decoys Critical Help Net Security
2026-09-17 Help Net Security

CISA wants critical infrastructure orgs and smaller security teams to start using cyber decoys

Cyber deception has long been the domain of well-resourced security teams, but CISA’s latest guidance, titled “Using Cyber Decoys to Strengthen Detection and Response”, is an attempt to try and change that. Why decoys, and why now The core problem CISA is attempting to address is that many organizations are incapable of detecting adversaries who use legitima…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Critical Unbound DNSSEC Validator Flaw Could Allow RCE via a Malicious DNS Zone Critical CVE-2026-81642 The Hacker News
2026-09-17 The Hacker News

Critical Unbound DNSSEC Validator Flaw Could Allow RCE via a Malicious DNS Zone

Every release of the Unbound DNS resolver before 1.26.1 has a critical heap overflow in its DNSSEC validator, maintainer NLnet Labs said in an advisory on Wednesday. An attacker who controls a malicious zone and queries a vulnerable resolver can trigger it, enabling remote code execution. Unbound 1.26.1, released the same day, fixes the bug, tracked as CVE-2…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Druva expands identity resilience with ransomware detection Critical Help Net Security
2026-09-17 Help Net Security

Druva expands identity resilience with ransomware detection

Druva has announced new capabilities for Druva Identity Resilience alongside the launch of Ransomware Detection, a new feature fueled by a proprietary AI threat pipeline. Powered by Dru MetaGraph, the new offerings use behavioral intelligence and built-in validation to turn suspicious behavior into actionable evidence, definitively confirm impact, and accele…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Israeli contractor BlackCore trained Angolan officials in online influence operations Moderate The Record by Recorded Future
2026-09-17 The Record by Recorded Future

Israeli contractor BlackCore trained Angolan officials in online influence operations

An Israeli influence-for-hire company trained Angolan government officials to run online influence operations, including by creating fake social media personas and media outlets, researchers found.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Google’s new agent security system detects tool misuse, loops and rogue behavior Moderate Help Net Security
2026-09-17 Help Net Security

Google’s new agent security system detects tool misuse, loops and rogue behavior

Google’s Agent Anomaly Detection is a reasoning-based oversight and audit layer for autonomous agents deployed on Agent Runtime in the Gemini Enterprise Agent Platform and built with the Agent Development Kit (ADK) for Python 1.2 or later. Google recommends ADK 2.1.0 or later. It is available in Private Preview. What Agent Anomaly Detection monitors Agent An…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
FBI takes down one of the longest-running DDoS-for-hire services Moderate Help Net Security
2026-09-17 Help Net Security

FBI takes down one of the longest-running DDoS-for-hire services

The FBI has seized the domains behind NightmareStresser, a DDoS-for-hire service officials call one of the longest running “booter” operations in existence. The domain seizure notice (Source: US Department of Justice) “Booter services such as those named in this action allegedly facilitate attacks on a wide array of victims in the United States and abroad, i…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
NightmareStresser Goes Offline in Global DDoS-for-Hire Crackdown Moderate SecurityAffairs
2026-09-17 SecurityAffairs

NightmareStresser Goes Offline in Global DDoS-for-Hire Crackdown

The DOJ seized domains behind NightmareStresser, a DDoS-for-hire service tied to hundreds of thousands of attacks since 2022, as part of Operation PowerOFF. Renting a DDoS attack used to be as easy as renting a movie. Pick a target, pay a few dollars, watch the site go dark. The Justice Department just made that a little harder by seizing the domains behind …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
US takes down NightmareStresser DDoS-for-hire platform Moderate BleepingComputer
2026-09-17 BleepingComputer

US takes down NightmareStresser DDoS-for-hire platform

The U.S. Federal Bureau of Investigation (FBI) seized the domains used by NightmareStresser, one of the world's longest-running distributed denial-of-service (DDoS) platforms. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
12 celebrity deepfake websites seized by Manhattan DA Moderate Malwarebytes Labs
2026-09-17 Malwarebytes Labs

12 celebrity deepfake websites seized by Manhattan DA

The Manhattan District Attorney’s Office has seized the domains of 12 deepfake websites in what it called the largest known seizure of celebrity deepfake sites in history. The sites, which marketed themselves as deepfake pornography platforms, hosted AI-generated videos of over 1,200 people, including those in the public eye, ranging from politicians to acto…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Cisco Warns of Active Exploitation of Critical ISE Flaw Critical Infosecurity Magazine
2026-09-17 Infosecurity Magazine

Cisco Warns of Active Exploitation of Critical ISE Flaw

Cisco urged ISE customers to apply a software update, as well as check for signs of exploitation

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

CISO's Expert Guide to Agentic Pentesting for Websites Moderate The Hacker News
2026-09-17 The Hacker News

CISO's Expert Guide to Agentic Pentesting for Websites

Attackers now weaponize new vulnerabilities in about five days (Mandiant, part of Google Cloud). The median organization takes 43 days to patch one (Verizon DBIR 2026). A new free guide explains how autonomous AI agents are closing that gap, and what security leaders must demand before pointing one at production. TL;DR Exploitation is now the front door. It …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
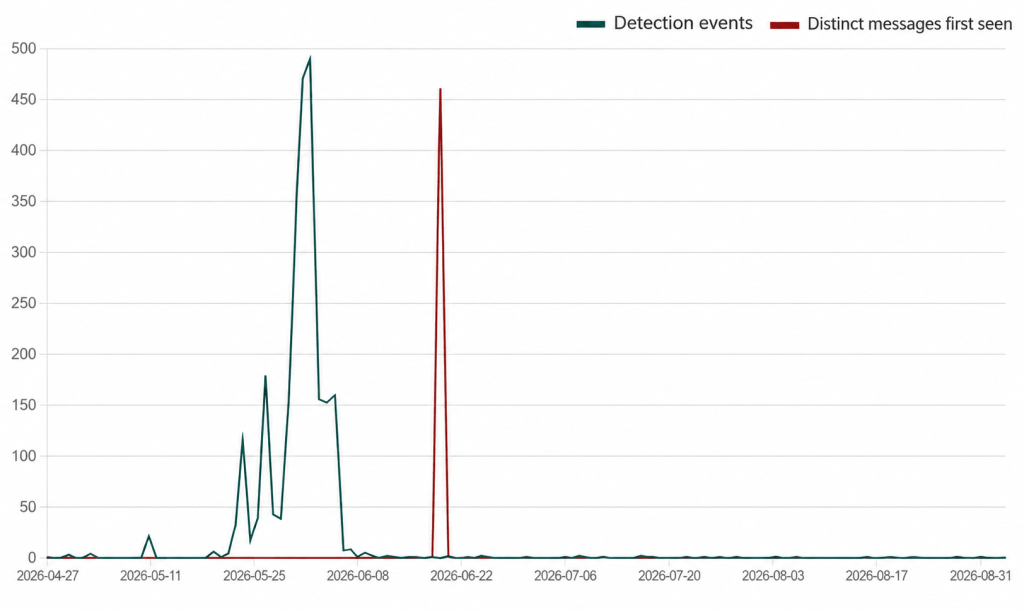
T-Mobile rewards points expiry texts are a phishing scam Important Malwarebytes Labs
2026-09-17 Malwarebytes Labs

T-Mobile rewards points expiry texts are a phishing scam

Since early May 2026, we’ve been monitoring a large phishing campaign based on T-Mobile rewards points. The messages falsely warn that a customer’s rewards points are about to expire. They aren’t legitimate account notices: They use urgency, invented point balances, and phishing links to push recipients into acting before they can verify the claim. A typical…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Unauthenticated attackers are bypassing Cisco ISE’s management interface (CVE-2026-76460) Critical CVE-2026-76460 Help Net Security
2026-09-17 Help Net Security

Unauthenticated attackers are bypassing Cisco ISE’s management interface (CVE-2026-76460)

Two days after it warned customers about an actively exploited email gateway zero-day, Cisco confirmed one more flaw is being targeted: CVE-2026-76460, an authentication bypass bug in an API of Cisco Identity Services Engine (ISE). About CVE-2026-76460 Cisco ISE is an identity-based network access control and policy platform. It checks connecting users’ iden…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Scammers leave AI fingerprints all over fake antivirus renewal page Moderate Help Net Security
2026-09-17 Help Net Security

Scammers leave AI fingerprints all over fake antivirus renewal page

AI appears to be helping scammers with little web development skill build convincing fake antivirus-renewal pages, Malwarebytes found. The researchers came across a scam page impersonating Avast, aimed at users in Belgium, that was more polished than most sites of its kind. The page told visitors their Avast Premium Security subscription had renewed for €129…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
China-Aligned FamousSparrow Deploys SparroWocky Backdoor Across Latin America Important The Hacker News
2026-09-17 The Hacker News

China-Aligned FamousSparrow Deploys SparroWocky Backdoor Across Latin America

The China-aligned state-sponsored threat actor known as FamousSparrow has been observed deploying a previously unreported backdoor called SparroWocky in attacks targeting multiple countries in Latin America since at least August 2025. "SparroWocky is a modular, C++ backdoor," ESET security researchers Alexandre Côté Cyr and Romain Dumont said in a technical …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Ransomware incidents in Japan in the first half of 2026: Investigation of The Gentlemen’s infrastructure and evidence of Qilin's AI use Critical CVE-2025-2479 Cisco Talos Intelligence
2026-09-17 Cisco Talos Intelligence

Ransomware incidents in Japan in the first half of 2026: Investigation of The Gentlemen’s infrastructure and evidence of Qilin's AI use

Compared with the same period last year, ransomware incidents in Japan increased slightly by approximately 4.7%, indicating that ransomware continues to pose a significant threat. In Japan, The Gentlemen was the most active ransomware group in the first half of 2026. Attackers continue to primarily target small- and medium-sized enterprises, with organizatio…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
OpenAI Reveals Six Model Incidents Involving Hidden Failures and Unauthorized Uploads Moderate The Hacker News
2026-09-17 The Hacker News

OpenAI Reveals Six Model Incidents Involving Hidden Failures and Unauthorized Uploads

OpenAI on Wednesday disclosed six new instances of "unexpected or concerning model behavior" that took place over the past six months, while sharing a new framework for reporting, tracking, investigating, and disclosing model misalignment in a bid to improve transparency. "As AI systems grow more advanced and more widely deployed, we need to build a broader …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
U.S. CISA adds Acronis Backup, Cisco ISE, and Google Pixel flaws to its Known Exploited Vulnerabilities catalog Important CVE-2026-76460 SecurityAffairs
2026-09-17 SecurityAffairs

U.S. CISA adds Acronis Backup, Cisco ISE, and Google Pixel flaws to its Known Exploited Vulnerabilities catalog

U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Acronis Backup, Cisco ISE, and Google Pixel flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added [ 1 , 2 ] the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog : CVE-2026-76460 (CVSS score of …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification