Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 2,629 advisories
Page 87 of 110
Chinese hackers use SparroWocky malware in govt espionage attacks Important BleepingComputer
2026-09-17 BleepingComputer

Chinese hackers use SparroWocky malware in govt espionage attacks

The China-linked espionage group FamousSparrow has been using a new backdoor named SparroWocky in attacks on government organizations in Latin America. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Spain reports first data breach involving autonomous AI agent Critical Help Net Security
2026-09-17 Help Net Security

Spain reports first data breach involving autonomous AI agent

Spain’s data protection authority (AEPD) has reported its first data breach blamed on an AI agent acting on its own, after the system reportedly logged into a company’s network, found a way to alter personal records, and pulled invoice data. “Before drawing any conclusions, it should be noted that the available information comes from the notification submitt…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
AI Agent Carries Out Multi-Stage Data Theft Attack Important Infosecurity Magazine
2026-09-17 Infosecurity Magazine

AI Agent Carries Out Multi-Stage Data Theft Attack

Spanish data protection agency AEPD reveals the country’s first AI-powered data breach

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft shares workaround for Windows domain login issues Moderate BleepingComputer
2026-09-17 BleepingComputer

Microsoft shares workaround for Windows domain login issues

Microsoft shared a temporary fix on Wednesday for a known issue that prevents Windows 11 users from logging in with valid domain credentials after installing the September 2026 security updates. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
BIND 9 Update Fixes 14 Flaws, Including an Unauthenticated Crash Over DNS-over-HTTPS Important The Hacker News
2026-09-17 The Hacker News

BIND 9 Update Fixes 14 Flaws, Including an Unauthenticated Crash Over DNS-over-HTTPS

The Internet Systems Consortium (ISC) has released BIND 9.20.29 and 9.21.26 to fix fourteen security flaws it disclosed on 16 September in BIND 9, its open-source DNS server software. One of them affects any BIND server that answers DNS-over-HTTPS (DoH). A sender with no credentials can crash the server process, named, with a single request that carries an i…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Fake AI trading agent steals crypto wallet passwords Moderate Help Net Security
2026-09-17 Help Net Security

Fake AI trading agent steals crypto wallet passwords

Attackers built a website for a fake AI crypto trading agent and used it to install Needle Stealer, malware that replaces a victim’s browser wallet with a copy that sends the wallet password to the attacker. HP caught the campaign between April and June 2026. The Needle campaign targets people who download AI agents from search results or ads, and users of s…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Gyazo Breach Exposes 23.62 Million User Records and 490 Million Image Metadata Records Critical The Hacker News
2026-09-17 The Hacker News

Gyazo Breach Exposes 23.62 Million User Records and 490 Million Image Metadata Records

A security breach at Gyazo, Helpfeel's image-sharing service, exposed about 23.62 million user records, including email addresses and password hashes, the Kyoto-based company said in a notice published Wednesday. It also exposed about 490 million image metadata records, mostly for images from January 2019 or earlier, including the IDs that make up Gyazo imag…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Chosen Brick, Iran’s Surveillance Malware Important SecurityAffairs
2026-09-17 SecurityAffairs

Chosen Brick, Iran’s Surveillance Malware

UK, US, and Dutch agencies expose Chosen Brick, Iranian malware used to track and harass dissidents, journalists, and activists via Telegram. The UK, the US, and the Netherlands published a joint advisory warning about a Windows malware family, dubbed Chosen Brick, that Iran’s intelligence services use to track down dissidents, journalists, and activists, an…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Cisco warns of max severity ISE zero-day exploited in attacks Critical BleepingComputer
2026-09-17 BleepingComputer

Cisco warns of max severity ISE zero-day exploited in attacks

Cisco has released security updates to address a maximum-severity Identity Services Engine vulnerability that attackers are actively exploiting in the wild. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Cisco Warns of New Zero-Day ISE Auth Bypass (CVSS 10.0) Exploited in Active Attacks Critical CVE-2026-76460 The Hacker News
2026-09-17 The Hacker News

Cisco Warns of New Zero-Day ISE Auth Bypass (CVSS 10.0) Exploited in Active Attacks

Cisco has warned of a fresh maximum-severity security flaw impacting Identity Services Engine (ISE) that has come under active exploitation. The vulnerability, tracked as CVE-2026-76460 (CVSS score: 10.0), could allow an unauthenticated, remote attacker to bypass authentication. "This vulnerability is due to insufficient authentication control on an API endp…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Riverbed NPM 360 uses AI to predict and prevent network disruptions Moderate Help Net Security
2026-09-17 Help Net Security

Riverbed NPM 360 uses AI to predict and prevent network disruptions

Riverbed has announced new Riverbed intelligent network observability solutions that combine 360-degree network visibility with agentic AI to help network operations teams accelerate troubleshooting, identify root causes, predict emerging issues and increasingly prevent disruptions before they impact users. The new Riverbed Network 360 offerings natively int…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Tuskira Vector brings autonomous red teaming to attack surface validation Important Help Net Security
2026-09-17 Help Net Security

Tuskira Vector brings autonomous red teaming to attack surface validation

Tuskira has announced Vector, its autonomous red teaming agentic capability, which identifies an organization’s exploitable attack surface by simulating what an attacker can do from outside it. Tuskira validates every external finding against the organization’s deployed compensating controls, the internal risks already reported by its security tools, and the…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The AI security question leaders should be asking instead Moderate Help Net Security
2026-09-17 Help Net Security

The AI security question leaders should be asking instead

In this Help Net Security interview, Frederic Bull, Security Officer at Gremlin, talks about what AI means for security teams. The conversation covers why asking what data a model was trained on is only part of the picture, and why least privilege and access controls still matter for AI agents. It also looks at how AI has narrowed the skill gap between attac…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
U.S. Seizes NightmareStresser Domains Linked to Hundreds of Thousands of DDoS Attacks Important The Hacker News
2026-09-17 The Hacker News

U.S. Seizes NightmareStresser Domains Linked to Hundreds of Thousands of DDoS Attacks

The U.S. Department of Justice (DoJ) on Tuesday announced the court-authorized seizure of internet domains associated with a distributed denial-of-service (DDoS)-for-hire service known as NightmareStresser. The domains in question are: nightmare-stresser[.]com and nightmarestresser[.]org. Visitors to the site are now greeted by a seizure banner that states -…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
A flat cybersecurity budget doesn’t have to mean weaker coverage Moderate Help Net Security
2026-09-17 Help Net Security

A flat cybersecurity budget doesn’t have to mean weaker coverage

Cheri Hotman, Managing Partner of Hotman Group, works as a vCISO and vGRC leader. In this Help Net Security video, she talks about holding coverage steady when the CFO asks for a flat budget or a 12% cut. Her advice is to stop trimming every line by the same percentage. Instead, sort each security expense into four buckets: what works and protects something …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
AWS’s new sign-up gives accounts spend caps, email invites, and agent-set permissions Moderate Help Net Security
2026-09-17 Help Net Security

AWS’s new sign-up gives accounts spend caps, email invites, and agent-set permissions

New AWS customers can now sign up with a Google, GitHub, or Apple login, start with $100 in Free Tier credits, and build inside a “project” where AWS and coding agents set up permissions automatically. Paid projects get a monthly spend limit, starting at $20, and a project that reaches its limit is halted instead of running up more charges. Owners who later …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
GNOME 51 adds passkey logins, offline maps and drawn PDF signatures Moderate Help Net Security
2026-09-17 Help Net Security

GNOME 51 adds passkey logins, offline maps and drawn PDF signatures

GNOME 51, the new version of the Linux desktop, came out on September 16 under the codename A Coruña. The release adds offline maps and live transit information to Maps, new login options at the login screen, hand-drawn signatures in the Papers document viewer, and smoother animations when the system is under load. Fedora 45 and Ubuntu 26.10 will ship it. Th…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
AI is adding to the review load on open-source projects, many of them thinly funded Critical Help Net Security
2026-09-17 Help Net Security

AI is adding to the review load on open-source projects, many of them thinly funded

AI coding tools are making open source software harder to maintain and secure, according to six authors writing for the Association for Computing Machinery’s Technology Policy Council, among them Simson Garfinkel and Josiah Dykstra. The tools write code and find security flaws quickly. The maintainers who decide what enters a project’s official release still…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The world must establish red lines for autonomous AI weapons Moderate Help Net Security
2026-09-17 Help Net Security

The world must establish red lines for autonomous AI weapons

AI is transforming warfare and international conflict. Autonomous weapon systems pose a genuine threat to civilians. The war in Ukraine has become a proving ground for weapons that can navigate, identify targets, resist electronic countermeasures, and pursue and engage targets autonomously without the need for human control. That evolution should concern tec…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Anthropic wants Claude to analyze your bank account and financial data Moderate BleepingComputer
2026-09-16 BleepingComputer

Anthropic wants Claude to analyze your bank account and financial data

Anthropic is testing a new personal finance feature called "Claude Money" that will allow you to connect your bank accounts directly to Claude and "understand your money." [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Smashing Security podcast #485: These researchers got drunk to hack an LG TV Moderate Graham Cluley Security
2026-09-16 Graham Cluley Security

Smashing Security podcast #485: These researchers got drunk to hack an LG TV

Researchers wanted to test if LG's smart TVs come with any security risks - but their lawyers noticed a snag: the terms and conditions would forbid it. So they came up with a solution. They got plastered before setting up the TV, on the reasoning that you can't be legally bound to a contract you agreed to while drunk. What they discovered will make you look …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Key lawmaker suggests action on AI safety legislation will wait until 2027 Moderate The Record by Recorded Future
2026-09-16 The Record by Recorded Future

Key lawmaker suggests action on AI safety legislation will wait until 2027

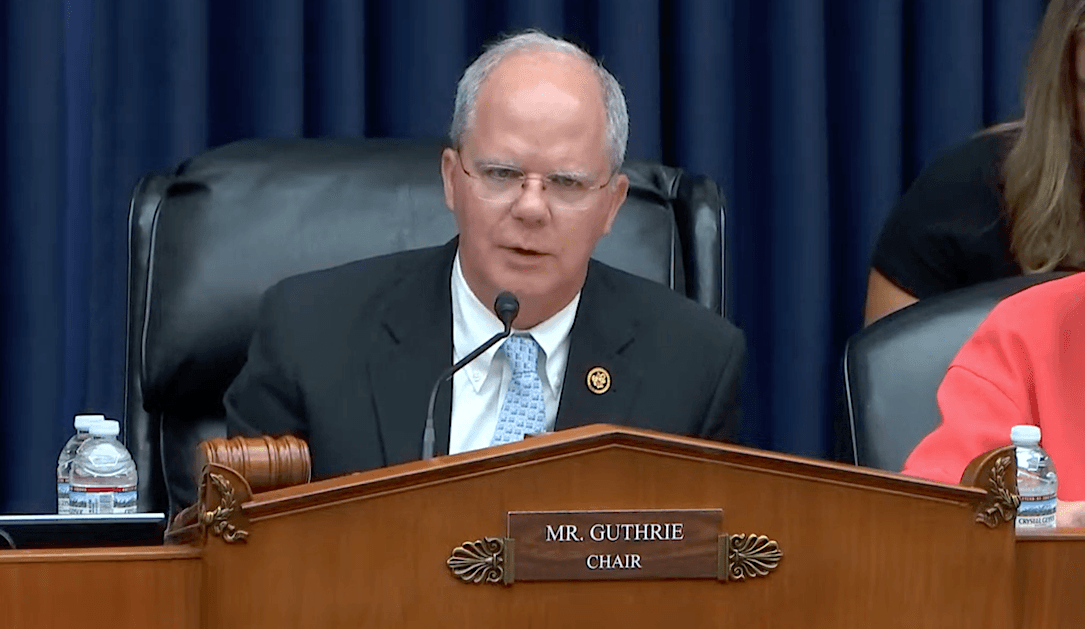
“It's really complicated, and I wouldn't want to do something in a lame duck session to do it quickly and not get it right,” said House Energy and Commerce Chairman Brett Guthrie about the FRONTIER Act.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification