Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 2,629 advisories
Page 89 of 110
EU chief wants joint response to cyberattacks, sabotage Important The Record by Recorded Future
2026-09-16 The Record by Recorded Future

EU chief wants joint response to cyberattacks, sabotage

Delivering her annual State of the Union address in Strasbourg, Ursula von der Leyen said threats were “mounting on our soil,” pointing to recent incidents in Denmark, Lithuania and Poland and an attempted drone attack in Leipzig.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Revolut Data Leak May Trace Back to Compromised Italian Government Accounts Moderate SecurityAffairs
2026-09-16 SecurityAffairs

Revolut Data Leak May Trace Back to Compromised Italian Government Accounts

A suspected compromise of an Italian government PEC account may have allowed threat actors to impersonate law enforcement and obtain sensitive data from hundreds of Revolut customers. The Revolut data exposure may be part of a much broader cyber incident involving compromised Italian government infrastructure. Revolut has confirmed that its systems were not …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Ukraine moves to crack down on scam call centers after corruption scandal Moderate The Record by Recorded Future
2026-09-16 The Record by Recorded Future

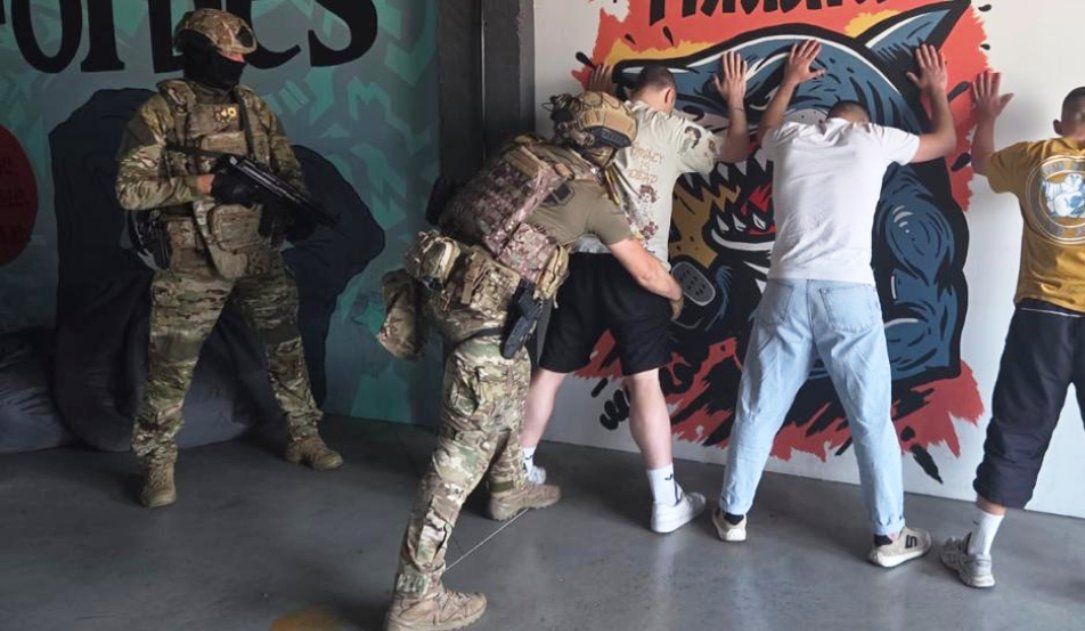
Ukraine moves to crack down on scam call centers after corruption scandal

Ukraine’s parliament has approved tougher criminal penalties for involvement in fraudulent call centers and the theft of personal data, following a corruption scandal in which prosecutors were accused of taking bribes to protect scam operations.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Parallels Desktop flaw hands any local user root on a Mac (CVE-2026-90894) Important CVE-2026-90894 Help Net Security
2026-09-16 Help Net Security

Parallels Desktop flaw hands any local user root on a Mac (CVE-2026-90894)

A newly disclosed vulnerability in Parallels Desktop, tracked as CVE-2026-90894 and dubbed “ParaShells,” can allow any local user on a Mac to gain root privileges on the host system. ParaShells PoC in action (Source: JFrog) The danger is highest on developer laptops, where a single poisoned Homebrew formula or malicious npm preinstall script can go from loca…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Microsoft says Copilot buttons still missing in classic Outlook Moderate BleepingComputer
2026-09-16 BleepingComputer

Microsoft says Copilot buttons still missing in classic Outlook

Microsoft says it's still investigating a known issue that causes the Copilot and Copilot Chat buttons in Classic Outlook to disappear for some Windows users. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Webinar: What happens in the first hours of a Google Workspace breach Critical BleepingComputer
2026-09-16 BleepingComputer

Webinar: What happens in the first hours of a Google Workspace breach

The first hours after discovering a Google Workspace breach can determine how an incident unfolds. This webinar examines real-world breaches to show which early response decisions can limit the impact and which can make matters worse. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

N0va Phishkit Targets US and EU Businesses: A New Challenge for Identity Security Moderate The Hacker News
2026-09-16 The Hacker News

N0va Phishkit Targets US and EU Businesses: A New Challenge for Identity Security

N0va is targeting organizations across North America and Europe with phishing campaigns that impersonate trusted services and abuse legitimate authentication flows. Successful attacks can give threat actors access to valid accounts without relying on obvious malware activity. From there, a single compromised identity can open the door to sensitive data, busi…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Self-improving AI should slow down, von der Leyen tells EU lawmakers Moderate Help Net Security
2026-09-16 Help Net Security

Self-improving AI should slow down, von der Leyen tells EU lawmakers

European Commission President Ursula von der Leyen wants frontier AI development slowed, and said on Wednesday that she will invite the leading AI labs to discuss how the EU can support their own efforts to do that. In her State of the Union address to the European Parliament in Strasbourg, she also committed the EU to joint work with Canada, the U.K. and ot…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Google Patches Pixel Modem Flaw Amid Signs of Limited Targeted Exploitation Critical CVE-2026-58704 The Hacker News
2026-09-16 The Hacker News

Google Patches Pixel Modem Flaw Amid Signs of Limited Targeted Exploitation

Google has disclosed that a high-severity security flaw in its Pixel Cellular Modem has come under exploitation in the wild. The vulnerability, tracked as CVE-2026-58704 (CVSS score: 8.0), is a privilege escalation flaw. "In Cellular Modem, there is a possible permission bypass due to a logic error in the code," according to a description of the bug in the N…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Threat Intelligence Alone Won't Close the Exploitation Gap Important The Hacker News
2026-09-16 The Hacker News

Threat Intelligence Alone Won't Close the Exploitation Gap

A leaked credential shows up in a criminal marketplace, or a vulnerability gets a disclosure advisory, and either one can be weaponized against a real target before most security teams have triaged the alert. Attackers are combining that kind of intelligence with AI-assisted exploitation to accelerate the path from exposure to breach faster than most securit…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Critical ScreenConnect flaw now actively exploited in attacks Critical BleepingComputer
2026-09-16 BleepingComputer

Critical ScreenConnect flaw now actively exploited in attacks

Attackers now exploit a critical-severity ConnectWise ScreenConnect vulnerability in the wild, according to the U.S. Cybersecurity and Infrastructure Security Agency (CISA). [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Acronis cPanel Backup Plugin Vulnerability Exploited in Targeted Attacks Critical CVE-2026-87886 The Hacker News
2026-09-16 The Hacker News

Acronis cPanel Backup Plugin Vulnerability Exploited in Targeted Attacks

Acronis has warned that a high-severity security flaw in its Backup plugin for cPanel and Web Host Manager (WHM) deployments has been exploited in the wild. The vulnerability, tracked as CVE-2026-87886 (CVSS score: 7.8), is described as a case of local privilege escalation due to insecure file permissions. It affects the following versions - Acronis Backup p…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Cyber-Attacks Cost Organizations $52,000 on Average Important Infosecurity Magazine
2026-09-16 Infosecurity Magazine

Cyber-Attacks Cost Organizations $52,000 on Average

Hiscox highlighted the huge financial and operational costs of cyber-attacks, with the average cost of an incident at $52,000

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Cohesity adds recovery capabilities for AI agents and the data they manage Moderate Help Net Security
2026-09-16 Help Net Security

Cohesity adds recovery capabilities for AI agents and the data they manage

Cohesity has introduced Cohesity Agent Resilience. This new Cohesity Data Cloud capability will discover, protect, and recover the infrastructure behind enterprise AI agents. A unified view of an agent and the state it depends on. (Source: Cohesity) The company outlined its vision for Autonomous Cyber Resilience, which uses agentic workflows to automate its …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Rubrik MCP gives AI agents controlled access to security intelligence Moderate Help Net Security
2026-09-16 Help Net Security

Rubrik MCP gives AI agents controlled access to security intelligence

Rubrik has announced Rubrik MCP (Model Context Protocol), giving an organization’s AI agents a secure, programmable path to Rubrik’s data, identity, and application intelligence. Support for MCP expands Rubrik AI, which is now trusted by one-third of its global customers, and unites Anthropic’s frontier models with Rubrik’s domain expertise and security guar…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Google Pixel owners urged to patch actively exploited modem flaw Critical CVE-2026-58704 Malwarebytes Labs
2026-09-16 Malwarebytes Labs

Google Pixel owners urged to patch actively exploited modem flaw

Google has released its September 2026 Pixel Update Bulletin , fixing 110 vulnerabilities, including one that it says “may be under limited, targeted exploitation.” The bug is not described as a simple remote takeover, but as a vulnerability that could give an attacker who already has a foothold on a phone more power than they should have. Although Pixel dev…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CenterPoint Energy confirms data breach following claims on hacking forum Critical Help Net Security
2026-09-16 Help Net Security

CenterPoint Energy confirms data breach following claims on hacking forum

CenterPoint Energy disclosed that an unauthorized third party got into customer data through one of its external systems, after online claims by a hacker that millions of records had been stolen from the company. CenterPoint Energy is a Houston-based public utility company that provides electricity and natural gas services. It serves about 7 million customer…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Nozomi Compass helps industrial teams manage OT assets and vulnerabilities Important Help Net Security
2026-09-16 Help Net Security

Nozomi Compass helps industrial teams manage OT assets and vulnerabilities

Nozomi Networks announced Nozomi Compass, an OT asset and service management platform designed to help organizations manage industrial assets, vulnerabilities, and exposures. The platform brings asset data, remediation workflows, and operational processes together, reducing reliance on spreadsheets, IT ticketing systems, and manual workflows that may not acc…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Citrix adds AI-powered browser activity analysis to SecurAccess Moderate Help Net Security
2026-09-16 Help Net Security

Citrix adds AI-powered browser activity analysis to SecurAccess

Citrix has announced Citrix Session Insights, a new AI-powered capability for Citrix SecurAccess with Chrome Enterprise that helps organizations capture, analyze and understand browser activity from users and autonomous agents. By combining visual session evidence, AI-powered risk analysis and recommendations, Citrix helps organizations investigate incidents…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Securing the unpatchable in an age of AI-driven vulnerabilities Important Cisco Talos Intelligence
2026-09-16 Cisco Talos Intelligence

Securing the unpatchable in an age of AI-driven vulnerabilities

AI is accelerating vulnerability discovery, leaving unpatchable operational technology (OT) systems at risk. Hoping for the best is not a viable anti-exploitation strategy. Deploying next-generation firewalls directly upstream allows for virtual patching through deep packet inspection. These systems scan incoming traffic to detect and block exploit attempts …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
NightEagle targets Russian companies Moderate CVE-2020-0688 Kaspersky Securelist
2026-09-16 Kaspersky Securelist

NightEagle targets Russian companies

Over the past year, our Global Emergency Response Team (GERT) has investigated several incidents involving the NightEagle group (also tracked as APT-Q-95) . This group has been active since at least 2023 and originally focused on organizations in Asia. We have now identified attacks by the group targeting businesses in Russia. This post examines both known a…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Atomic macOS (AMOS) Stealer Activity Moderate Palo Alto Unit 42
2026-09-16 Palo Alto Unit 42

Atomic macOS (AMOS) Stealer Activity

Modern macOS malware uses deceptive setup guides to steal credentials and sensitive user data. Learn how to identify and block these threats. The post Atomic macOS (AMOS) Stealer Activity appeared first on Unit 42 .

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
One runaway AI agent racked up a $50,000 cloud bill Moderate Help Net Security
2026-09-16 Help Net Security

One runaway AI agent racked up a $50,000 cloud bill

Organizations are deploying autonomous AI systems that execute API calls, optimize production configurations, and analyze telemetry across hybrid cloud environments. At the same time, attacks are expanding from direct prompts to indirect prompt injection and AI supply chain compromises, blurring security boundaries. Mandiant’s latest AI Risk and Resilience r…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification