
Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 2,629 advisories
Page 90 of 110
Acronis backup plugin flaw exploited in targeted attacks (CVE-2026-87886) Critical CVE-2026-87886 Help Net Security
2026-09-16 Help Net Security

Acronis backup plugin flaw exploited in targeted attacks (CVE-2026-87886)

A Linux privilege escalation vulnerability (CVE-2026-87886) affecting Acronis’ backup extensions for cPanel, WebHost Manager (WHM), and Plesk, is being leveraged by attackers, the backup and recovery company warns. “Exploitation of this vulnerability has been detected in the wild in limited, targeted attacks against Acronis Backup plugin for cPanel & WHM dep…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Windows Server 2022 reaches end of mainstream support next month Moderate BleepingComputer
2026-09-16 BleepingComputer

Windows Server 2022 reaches end of mainstream support next month

Microsoft has reminded customers that Windows Server 2022 will reach the end of mainstream support next month and enter extended support until October 2031. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Iranian hackers use CHOSEN BRICK data-stealing malware to spy on dissidents and journalists Important Help Net Security
2026-09-16 Help Net Security

Iranian hackers use CHOSEN BRICK data-stealing malware to spy on dissidents and journalists

Iranian state cyber actors are deploying malware called CHOSEN BRICK against individuals they see as a threat to the regime, reaching victims through social messaging apps and infecting their Windows devices, three Western intelligence agencies warned. The UK’s National Cyber Security Centre, the FBI and the Netherlands’ AIVD said the campaign has targeted d…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
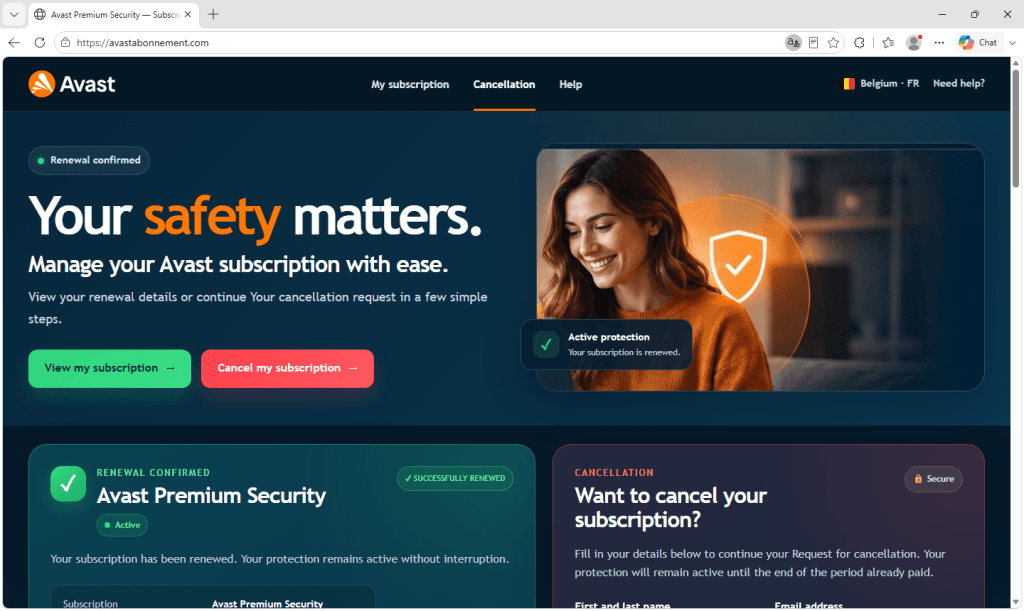
AI helps scammers build convincing antivirus renewal pages Moderate Malwarebytes Labs
2026-09-16 Malwarebytes Labs

AI helps scammers build convincing antivirus renewal pages

Antivirus renewal scams often begin with a message claiming that your subscription has automatically renewed. When you follow the instructions to cancel it, you are taken to a fake page designed to collect your contact details. The renewal charge never existed. Receiving a message that names the antivirus software you use does not necessarily mean the sender…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
NCSC and Allies Warn of Iranian Spyware Campaign Important Infosecurity Magazine
2026-09-16 Infosecurity Magazine

NCSC and Allies Warn of Iranian Spyware Campaign

The UK’s National Cyber Security Centre says Iranian Chosen Brick spyware is designed to snoop on dissidents

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Texas Utility CenterPoint Energy Confirms Data Breach After Hacker Claims 7.49M Records Stolen Critical SecurityAffairs
2026-09-16 SecurityAffairs

Texas Utility CenterPoint Energy Confirms Data Breach After Hacker Claims 7.49M Records Stolen

CenterPoint Energy confirmed a customer data breach after a hacker claimed to leak 7.49M records, including personal and billing information. CenterPoint Energy admitted on Monday that an intruder stole personal information belonging to some of its customers. The Houston-based utility, which supplies electricity and gas to about 7 million accounts across Tex…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
NIST and CISA finalize playbook to stop token theft and forgery Moderate Help Net Security
2026-09-16 Help Net Security

NIST and CISA finalize playbook to stop token theft and forgery

NIST and CISA have finalized guidelines to help federal agencies and cloud service providers (CSPs) protect identity and access tokens from forgery, theft, and misuse. The guidance, Protecting Tokens and Assertions from Forgery, Theft, and Misuse (NIST IR 8587), explains how agencies and cloud providers can strengthen key management, token verification, and …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Google fixes actively exploited Android zero-day on Pixel devices Critical BleepingComputer
2026-09-16 BleepingComputer

Google fixes actively exploited Android zero-day on Pixel devices

Google has released the September 2026 security patches to address 110 vulnerabilities affecting its Pixel devices, including one zero-day flaw actively exploited in targeted attacks. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
What happens when AI agent governance is missing at scale Moderate Help Net Security
2026-09-16 Help Net Security

What happens when AI agent governance is missing at scale

In this interview with Help Net Security, Gourab Basu, Global Head of Engineering at meshIQ, discusses governance in AI agent systems. He argues that instructions written into a prompt are not enough to control what an agent does, since agents can change their own path as they work. Real control means checking proposed actions before they reach production sy…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Attackers Exploit WooCommerce Wholesale Lead Capture Flaw to Plant PHP Web Shells Critical The Hacker News
2026-09-16 The Hacker News

Attackers Exploit WooCommerce Wholesale Lead Capture Flaw to Plant PHP Web Shells

Threat actors are exploiting a critical security flaw in WooCommerce Wholesale Lead Capture, a premium WordPress plugin that has more than 6,000 active installs. "This vulnerability can be leveraged by unauthenticated attackers to upload arbitrary files, including PHP backdoors, and achieve remote code execution," Wordfence said. The WordPress security compa…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
DeepZero: Open-source hunting for vulnerable Windows drivers Critical Help Net Security
2026-09-16 Help Net Security

DeepZero: Open-source hunting for vulnerable Windows drivers

DeepZero is an open-source engine that automates the search for exploitable Windows kernel drivers. You point it at a folder of binaries and it parses them, pulls them apart, scans them, throws most of them away, and asks a language model whether what survives can be attacked. Pipelines are written in YAML, the code is Python 3.11 and up. Rehman Ahmadzai, wh…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Active Exploitation Attempts Target WSO2 API Manager JWT Bypass With Forged Admin Tokens Critical CVE-2026-5430 The Hacker News
2026-09-16 The Hacker News

Active Exploitation Attempts Target WSO2 API Manager JWT Bypass With Forged Admin Tokens

A critical security flaw in WSO2 API Manager has come under active exploitation in the wild, according to findings from watchTowr. The vulnerability, tracked as CVE-2026-5430 (CVSS score: 9.8/10.0), is a case of improper verification of a cryptographic signature that could result in account takeover. Hacktron Team has been credited with discovering and repor…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The modern attack chain: Rethinking Google Workspace security in the age of AI Important Help Net Security
2026-09-16 Help Net Security

The modern attack chain: Rethinking Google Workspace security in the age of AI

Over the past two months, I’ve written about the Vercel breach and the Composio breach separately. Both offer lessons to learn on their own. But reading them together, I keep coming back to the same observation: these aren’t isolated incidents. They’re the same attack, run twice, against different targets, where email was not the entry point into the workspa…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
MSPs say nearly half their customers rely on them for CISO services Moderate Help Net Security
2026-09-16 Help Net Security

MSPs say nearly half their customers rely on them for CISO services

MSPs estimate that 46% of their customers, on average, look to them to act as CISOs, according to Sophos. Most of those providers do that job without the full set of compliance services, and many spread the work across several tools. Most providers expect this work to grow. For many of those customers, the MSP is the closest thing they have to a security lea…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Cyber Op Targets South Korean Media & Automotive Sectors Moderate Dark Reading
2026-09-16 Dark Reading

Cyber Op Targets South Korean Media & Automotive Sectors

A likely North Korean advanced persistent threat (APT) group used a previously undocumented Linux espionage toolkit to compromise load balancers, gain access to communications, and further exploit networks.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Acronis warns of actively exploited flaw in its cPanel backup plugin Critical BleepingComputer
2026-09-15 BleepingComputer

Acronis warns of actively exploited flaw in its cPanel backup plugin

Acronis disclosed a high-severity Linux local privilege escalation vulnerability in its backup plugin for cPanel, WebHost Manager (WHM), and Plesk that may be exploited in the wild. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
U.S. CISA adds Cisco Secure Email Gateway flaw to its Known Exploited Vulnerabilities catalog Important CVE-2026-76461 SecurityAffairs
2026-09-15 SecurityAffairs

U.S. CISA adds Cisco Secure Email Gateway flaw to its Known Exploited Vulnerabilities catalog

U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Cisco Secure Email Gateway flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a Cisco Secure Email Gateway flaw, tracked as CVE-2026-76461 (CVSS score of 9,8), to its Known Exploited Vulnerabilities (KEV) catalog . Cisco …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Malcious Admin Menu Editor Pro plugin backdoors 1,500 WordPress sites Important BleepingComputer
2026-09-15 BleepingComputer

Malcious Admin Menu Editor Pro plugin backdoors 1,500 WordPress sites

Malicious versions of the Admin Menu Editor Pro plugin for WordPress have been distributed to more than 200 customers after a threat actor compromised the maintainer's website and pushed updates that created a hidden user account. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Norway announces investigations into telecom Telenor’s work with Myanmar junta Moderate The Record by Recorded Future
2026-09-15 The Record by Recorded Future

Norway announces investigations into telecom Telenor’s work with Myanmar junta

Oslo-based Telenor potentially enabled crimes against humanity and violated sanctions in its dealings with the military regime that took over Myanmar in 2021, Norwegian authorities said.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
KREMLIN Banking Malware Hijacks Chrome and Edge to Steal Credentials and Session Tokens Important The Hacker News
2026-09-16 The Hacker News

KREMLIN Banking Malware Hijacks Chrome and Edge to Steal Credentials and Session Tokens

Cybersecurity researchers have shed light on a previously undocumented Brazilian banking malware operation that delivers a toolkit called KREMLIN. Elastic Security Labs is tracking the activity under the moniker REF9334. Active since at least May 2025, the threat actor has used lures that impersonate a dozen Brazilian banks and install a malicious browser ex…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification