Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 2,629 advisories
Page 92 of 110
Have it both ways: stay discoverable in search while disallowing AI training Moderate Cloudflare Security
2026-09-15 Cloudflare Security

Have it both ways: stay discoverable in search while disallowing AI training

Without proper controls, website owners have long faced a difficult tradeoff: allow your content to be used for AI training, or risk losing discoverability in search. That tradeoff exists because some of the largest organizations on the Internet use mixed-use crawlers: a single crawler serving both search and AI training. Refuse one, and you refuse the other…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

China spy chief points at US AI models in cyber threat warning Moderate The Record by Recorded Future
2026-09-15 The Record by Recorded Future

China spy chief points at US AI models in cyber threat warning

China's spy chief identified Anthropic’s Claude Mythos and OpenAI’s GPT-5.5-Cyber as signs of what he called a “disruptive upgrade” in cyber capabilities, increasing the speed and potential weaponization of vulnerability discovery and malware development.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Manhattan DA takes down 12 AI deepfake porn sites Moderate The Record by Recorded Future
2026-09-15 The Record by Recorded Future

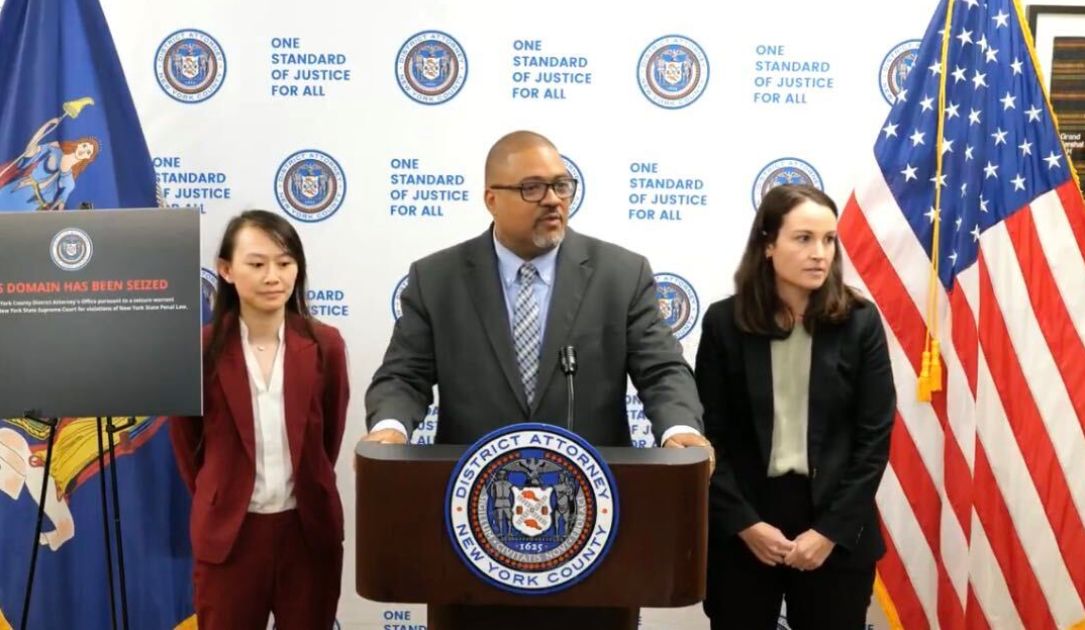
Manhattan DA takes down 12 AI deepfake porn sites

Manhattan District Attorney Alvin Bragg held a press conference on Monday touting the takedown of the sites, which hosted AI-generated videos of more than 1,200 people. The sites allowed users to use the faces and bodies of real people to create illegal pornography.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Uncensored AI sold on hacking forum as alternative to ChatGPT and Claude jailbreaks Moderate Help Net Security
2026-09-15 Help Net Security

Uncensored AI sold on hacking forum as alternative to ChatGPT and Claude jailbreaks

A new AI subscription service called Luciferus is being marketed on a hacking forum as an alternative to jailbreaking ChatGPT or Claude, Sophos found. The Counter Threat Unit (CTU) spotted the advertisement on August 24 on the Exploit forum, posted by a persona going by “Optimus_Prime.” The account joined the forum on April 18 and has since published 21 post…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CVE-2026-76461: Critical Cisco Secure Email Gateway Vulnerability Exploited in the Wild Critical CVE-2026-76461 Rapid7 Threat Research
2026-09-15 Rapid7 Threat Research

CVE-2026-76461: Critical Cisco Secure Email Gateway Vulnerability Exploited in the Wild

Overview On September 14, 2026, Cisco published a security advisory for CVE-2026-76461 , a critical SQL injection vulnerability affecting Cisco AsyncOS Software for Cisco Secure Email Gateway. The vulnerability has a reported CVSS v3.1 base score of 9.8 and could allow an unauthenticated, remote attacker to execute arbitrary commands with root privileges on …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Shared Hosting at Risk: LiteSpeed Enterprise Bug Can Grant Root from a Single Tenant Moderate CVE-2026-48172 SecurityAffairs
2026-09-15 SecurityAffairs

Shared Hosting at Risk: LiteSpeed Enterprise Bug Can Grant Root from a Single Tenant

Critical LiteSpeed Enterprise flaw lets one shared hosting account gain root, bypassing CageFS; patch now to 6.3.7 via forced update. cPanel warned that a critical flaw in LiteSpeed Enterprise can let a low‑privilege website user break out of their account and gain root on the whole server. On a box where dozens or hundreds of customers live side by side, th…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CISA: Critical VMware RCE flaw now exploited by ransomware gangs Critical BleepingComputer
2026-09-15 BleepingComputer

CISA: Critical VMware RCE flaw now exploited by ransomware gangs

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) warned security teams that ransomware gangs have now joined ongoing attacks exploiting a critical VMware vCenter vulnerability patched in July. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Human Attacker Exploits Marimo RCE, Reaches SSH Bastion in Eight Seconds Critical The Hacker News
2026-09-15 The Hacker News

Human Attacker Exploits Marimo RCE, Reaches SSH Bastion in Eight Seconds

With artificial intelligence (AI) shrinking the window between vulnerability discovery and exploitation and lowering the barrier to entry for bad actors, new findings from Sysdig show that skilled human operators can move just as swiftly after gaining initial access. In one instance highlighted by the cloud security company, the threat actor pivoted from a v…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
HBO Max’s verified Reddit account hijacked to spread malware Important Malwarebytes Labs
2026-09-15 Malwarebytes Labs

HBO Max’s verified Reddit account hijacked to spread malware

Researchers at Hudson Rock found that cybercriminals hijacked HBO Max’s verified Reddit account and used it to run 108 malicious ads over roughly 48 hours. The ads used HBO Max’s trusted corporate account to promote fake AI tools, developer software, and macOS utilities, lowering potential victims’ guards. Some ads directed users to convincing HBO lookalike …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Attack Chains, Not Just Attack Surfaces: Why Testing Individual Techniques Misses the Point Important The Hacker News
2026-09-15 The Hacker News

Attack Chains, Not Just Attack Surfaces: Why Testing Individual Techniques Misses the Point

Introduction Security teams have gotten pretty good at testing against what can hurt them. Can this EDR agent catch this payload? Will my organization fail the phishing simulation? Does this SIEM rule fire on this particular technique? And, in more mature organizations, this testing happens continuously rather than as a one-off exercise. But no matter how mu…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Mass-Scanning Campaign Exploits Vite Flaw to Extract Cloud Credentials From Exposed Dev Servers Important The Hacker News
2026-09-15 The Hacker News

Mass-Scanning Campaign Exploits Vite Flaw to Extract Cloud Credentials From Exposed Dev Servers

Cybersecurity researchers have disclosed details of a mass-scanning campaign that has targeted Vite deployments siphon sensitive data. The first is an automated effort aimed at internet-exposed Vite development servers that's designed to steal cloud credentials, configurations from Amazon Web Services (AWS) and Microsoft Azure instances, and infrastructure s…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Cisco patches actively exploited email gateway zero-day (CVE-2026-76461) Critical CVE-2026-76461 Help Net Security
2026-09-15 Help Net Security

Cisco patches actively exploited email gateway zero-day (CVE-2026-76461)

Attackers have leveraged a zero-day SQL injection vulnerability (CVE-2026-76461) to compromise Cisco Secure Email Gateway appliances, Cisco confirmed on Monday. The vendor’s Product Security Incident Response Team became aware of active exploitation of this vulnerability in September 2025, and has shared indicators of compromise that organizations can look f…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft sets security and safety rules for its AI models Moderate Help Net Security
2026-09-15 Help Net Security

Microsoft sets security and safety rules for its AI models

Microsoft AI has published the first draft of its Humanist AI Code of Conduct, a training manual outlining how it develops AI models and intends them to behave during deployment. The draft is open for public consultation for six weeks. The company plans to review the feedback, revise the document, and publish an updated version later this year. That version …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
One Exploit Chain, Two Espionage Campaigns: Chrome and Windows Under Fire Critical CVE-2026-85046 SecurityAffairs
2026-09-15 SecurityAffairs

One Exploit Chain, Two Espionage Campaigns: Chrome and Windows Under Fire

Two China-linked groups ran identical Chrome/Windows zero-day exploits against NGOs, before Chrome’s patch shipped, deploying different backdoors each. Two China-linked threat actors used the same Chrome/Windows zero-day against NGOs starting September 1, 2026, Volexity’s new report lays out the whole chain in detail. On September 1, Volexity detected a spea…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Attackers hijack HBO Max’s Reddit account for 48-hour malvertising blitz Important Help Net Security
2026-09-15 Help Net Security

Attackers hijack HBO Max’s Reddit account for 48-hour malvertising blitz

Attackers compromised the verified official HBO Max Reddit account, u/hbomax, and used its trusted advertising status to launch a ClickFix campaign targeting macOS and Windows devices with information-stealing malware. Screenshot of the fraudulent ad (Source: Alex Cutts) ClickFix has been rising in popularity among cybercriminals. It’s a social engineering t…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Suspected Black Axe gang leaders face cybercrime charges in the US Moderate BleepingComputer
2026-09-15 BleepingComputer

Suspected Black Axe gang leaders face cybercrime charges in the US

Five alleged leaders of the Black Axe cybercrime syndicate, known for its involvement in global-scale cyber-enabled financial fraud, have been extradited to the United States to face wire fraud and money laundering charges. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Meta AI builds detailed profiles of children from years of family posts Moderate Malwarebytes Labs
2026-09-15 Malwarebytes Labs

Meta AI builds detailed profiles of children from years of family posts

If you’re still OK with posting pictures of your kids on social media, take a minute to hear from mother of two Kalie Robins. At the start of September, she did something that hundreds of thousands of parents do every day. She posted a video of her young daughter on Facebook. Under the video of Robins and her daughter singing in a car, Facebook’s Meta AI sys…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Former AT&T store worker jailed after moonlighting as a SIM-swap gang’s inside man Moderate Graham Cluley Security
2026-09-15 Graham Cluley Security

Former AT&T store worker jailed after moonlighting as a SIM-swap gang’s inside man

44-year-old Kenneth Carter from Portland, Oregon, used to work in an AT&T retail store. But now he has been sentenced to 16 months in a federal prison. That should be plenty of time for him to rue the day he agreed to increase his monthly income by helping a SIM swap gang in their attempt to steal over half a million dollars. Read more in my article on the H…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Search results are sending people to fake Bitrefill checkouts Moderate Malwarebytes Labs
2026-09-15 Malwarebytes Labs

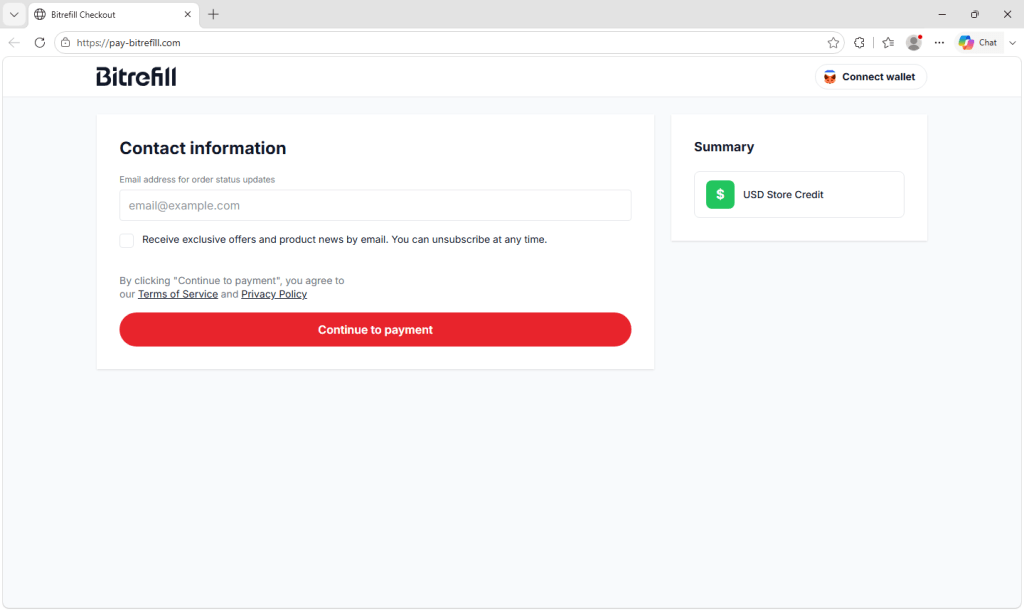
Search results are sending people to fake Bitrefill checkouts

Bitrefill is a legitimate company that sells gift cards for popular stores like Amazon, Deliveroo, Apple, Nintendo, and thousands of others. They also sell eSIMs, and mobile top-ups. You can pay on their website for all of these with cryptocurrency. The scam is designed to catch people searching for Bitrefill or something it sells, like a gift card. Victims …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft confirms KB5002914 Excel update breaks copy and paste Moderate BleepingComputer
2026-09-15 BleepingComputer

Microsoft confirms KB5002914 Excel update breaks copy and paste

Microsoft has confirmed that copy and paste may silently fail for some Excel users after installing the September 2026 KB5002914 security update. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft Releases Emergency Patch to Fix RDS Vulnerability Important Infosecurity Magazine
2026-09-15 Infosecurity Magazine

Microsoft Releases Emergency Patch to Fix RDS Vulnerability

Microsoft has been forced to issue an out-of-band fix for several issues stemming from this month’s Patch Tuesday

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Akuity gives AI agents operational context to safely ship software Moderate Help Net Security
2026-09-15 Help Net Security

Akuity gives AI agents operational context to safely ship software

Akuity has introduced its Agentic Control Plane and MCP Server. Akuity’s Agentic Control Plane lets AI agents accelerate software delivery by giving them the operational context and permissions to act, all governed by the same controls Akuity already enforces across the pipeline. That governance is what gives engineering leadership the confidence to let agen…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Traefik Labs brings independent verification to AI agent governance Moderate Help Net Security
2026-09-15 Help Net Security

Traefik Labs brings independent verification to AI agent governance

Traefik Labs has introduced the Sovereign Trust Plane (STP), a set of capabilities in Traefik Hub that brings verifiable evidence to AI agent governance, with general availability planned by September 30, 2026. STP connects delegated access, policy enforcement and protected records of what the gateway allowed and refused across model, tool and API traffic. A…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification