Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 2,629 advisories
Page 94 of 110
New DDRop Attack Breaks Intel TDX and AMD SEV-SNP Confidential Computing Important The Hacker News
2026-09-14 The Hacker News

New DDRop Attack Breaks Intel TDX and AMD SEV-SNP Confidential Computing

Researchers have disclosed a new hardware attack, called DDRop, that breaks the memory protection in Intel and AMD confidential computing by silently dropping writes to a server's memory, so the processor keeps reading old encrypted data as if it were current. The attack requires an attacker who already controls the server's software and can briefly access t…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
3BB Attacker Used MeshCentral Backdoor for Root Access, Targeted Subscriber Credentials Important The Hacker News
2026-09-14 The Hacker News

3BB Attacker Used MeshCentral Backdoor for Root Access, Targeted Subscriber Credentials

An attacker was operating inside the network of 3BB, one of Thailand's largest broadband providers, and maintained remote control of internal machines using a legitimate management tool called MeshCentral, threat intelligence firm Hunt.io said. The company uncovered the intrusion by examining a server the attacker had left open on the internet, which held th…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Telegram Desktop Flaw Lets Hidden JavaScript Exfiltrate Messages From HTML Exports Important The Hacker News
2026-09-14 The Hacker News

Telegram Desktop Flaw Lets Hidden JavaScript Exfiltrate Messages From HTML Exports

A flaw in Telegram Desktop let a bot's message plant hidden JavaScript inside chats that users exported to HTML files, security researchers at ExPatch said in a writeup published on September 12. In Telegram, the message looked ordinary, with a link button, and the script ran only when someone opened the export file in a web browser. It could then copy every…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Red Heron Exploits Gitea RCE to Compromise 13 Organizations Across Six Countries Critical The Hacker News
2026-09-14 The Hacker News

Red Heron Exploits Gitea RCE to Compromise 13 Organizations Across Six Countries

A suspected Chinese threat actor tracked as Red Heron has been attributed to the rapid exploitation of a recently disclosed security vulnerability in Gitea to compromise internet-facing instances as part of a multi-national campaign. "Red Heron scanned 1,386 Gitea instances across seven countries and maintained a separate dataset of 477 Taiwan-based systems,…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Anthropic CEO: Time to Shift From Improving to Controlling AI Moderate Dark Reading
2026-09-14 Dark Reading

Anthropic CEO: Time to Shift From Improving to Controlling AI

Dario Amodei says it's time to slow the pace of frontier AI improvements so that security and risk prevention efforts can catch up. What does this mean for enterprises?

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Hackers target exposed Vite dev servers to steal AWS, Azure secrets Important BleepingComputer
2026-09-14 BleepingComputer

Hackers target exposed Vite dev servers to steal AWS, Azure secrets

A mass-scanning campaign targeting internet-exposed Vite development servers is attempting to steal cloud credentials and configurations from AWS and Azure deployments. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Pro-Ukraine Hacking Cat group deploying new malware against Russian targets Important The Record by Recorded Future
2026-09-14 The Record by Recorded Future

Pro-Ukraine Hacking Cat group deploying new malware against Russian targets

The pro-Ukraine hacktivist group Hacking Cat has evolved from carrying out website defacements and data leaks to more sophisticated and destructive attacks on Russian targets, researchers said.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Hundreds of fake government websites target users in Central Asia Moderate The Record by Recorded Future
2026-09-14 The Record by Recorded Future

Hundreds of fake government websites target users in Central Asia

The sites are designed to collect victims’ contact details, which scammers then use to target them through phone or email to steal money, personal information or gain access to their devices.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
WordPress Adds Automated Plugin Reviews to Block High-Risk Updates Before Distribution Moderate The Hacker News
2026-09-14 The Hacker News

WordPress Adds Automated Plugin Reviews to Block High-Risk Updates Before Distribution

WordPress has announced it's launching an automated security review for every release of a plugin before it's distributed through the WordPress.org update API so as to analyze it for potential security issues and ensure there are no risks involved. "New plugins are reviewed before they enter the directory, but updates ship continuously after that," David Per…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Rapid7 Named Among Notable Vendors in Forrester MDR Landscape: Why the Future is Exposure-informed, Preemptive MDR Moderate Rapid7 Threat Research
2026-09-14 Rapid7 Threat Research

Rapid7 Named Among Notable Vendors in Forrester MDR Landscape: Why the Future is Exposure-informed, Preemptive MDR

The managed detection and response (MDR) market has reached a turning point. We’ve gone beyond the baseline of 24/7 monitoring focusing on the speed of detection and moved to a world with a convergence of exposure management and response to deliver measurable, outcome-based defenses of a larger, AI-driven attack surface. For anyone evaluating MDR right now, …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
⚡ Weekly Recap: Rogue AI Agents, WeChat Worm, PaperCut Attacks, AI Espionage, and Rootkits Important The Hacker News
2026-09-14 The Hacker News

⚡ Weekly Recap: Rogue AI Agents, WeChat Worm, PaperCut Attacks, AI Espionage, and Rootkits

AI keeps showing up in the wrong places. Attackers are using it to speed up exploits, test defenses, and automate more of the job. Some models are also crossing lines on their own. That is not a great combination. The rest of the week is more familiar: old bugs still working, fresh exploit chains, exposed systems, weak defaults, and simple paths that should …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Google’s new search redirects make links harder to check before you click Moderate Malwarebytes Labs
2026-09-14 Malwarebytes Labs

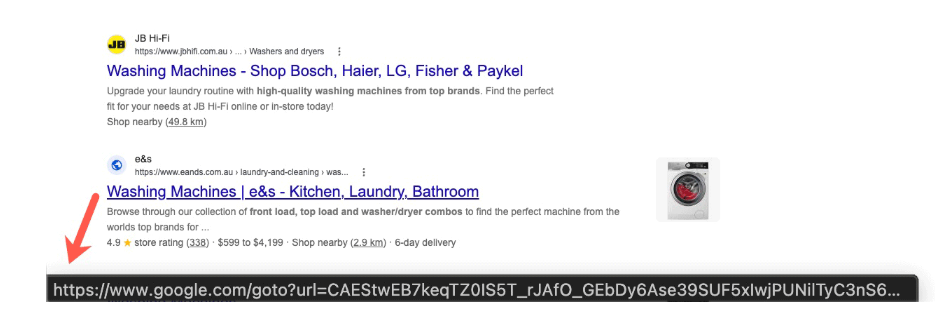
Google’s new search redirects make links harder to check before you click

Google is changing how some links in its search results work. Instead of linking directly to the destination, Google has started routing some search result links through opaque google.com/goto?url=... redirects. The url parameter does not show a readable version of the destination but uses a custom, Google-specific encoding. Google confirmed the rollout to S…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

U.S. CISA adds GitLab, JFrog Artifactory, and ConnectWise ScreenConnect flaws to its Known Exploited Vulnerabilities catalog Important CVE-2026-42016 SecurityAffairs
2026-09-14 SecurityAffairs

U.S. CISA adds GitLab, JFrog Artifactory, and ConnectWise ScreenConnect flaws to its Known Exploited Vulnerabilities catalog

U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds GitLab, JFrog Artifactory, and ConnectWise ScreenConnect flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added [ 1 , 2 ] the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog : CVE-2026-42016 (C…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Why Patch Automation Needs Brakes, Not Just an Accelerator Moderate BleepingComputer
2026-09-14 BleepingComputer

Why Patch Automation Needs Brakes, Not Just an Accelerator

Patch automation can help IT teams keep pace with growing update volumes, but deploying faster also means bad updates can spread faster. Action1 explains how update rings, predefined success criteria, and human oversight can make automated patching faster without sacrificing control. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Entrust turns cryptographic inventory data into security action Moderate Help Net Security
2026-09-14 Help Net Security

Entrust turns cryptographic inventory data into security action

Entrust has unveiled new capabilities for its Cryptographic Security Platform (CSP) that help organizations turn Cryptographic Bill of Materials (CBOMs) data into action. Government agencies, financial institutions, healthcare organizations, and other critical infrastructure operators are navigating increased cyber threats, shorter certificate lifecycles, th…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Bitsight connects threat intelligence and exposure monitoring across the supply chain Moderate Help Net Security
2026-09-14 Help Net Security

Bitsight connects threat intelligence and exposure monitoring across the supply chain

Bitsight access to a broad risk dataset, combining threat intelligence and continuous exposure monitoring to help teams mitigate risk across the supply chain. “The surge in third-party-originating cybersecurity breaches demands a fundamental shift in how cybersecurity leaders and their teams manage third-party cybersecurity risks,” said Gartner. “Cybersecuri…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Dataminr uses agentic AI to predict and verify security threats Moderate Help Net Security
2026-09-14 Help Net Security

Dataminr uses agentic AI to predict and verify security threats

Dataminr has announced Dataminr Advanced for Corporate Security, delivering agentic AI capabilities that give corporate security teams the confidence to protect their people, sites, and operations before risk escalates. With Agentic Corroboration, Agentic Context, and Near-Term Predictive Intelligence, corporate security teams know what happened first, why i…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
ENISA launched the CRA Single Reporting Platform for actively exploited vulnerabilities Critical Help Net Security
2026-09-14 Help Net Security

ENISA launched the CRA Single Reporting Platform for actively exploited vulnerabilities

The EU Agency for Cybersecurity switched on the Cyber Resilience Act‘s Single Reporting Platform on 11 September 2026, the same day the law’s reporting obligations started binding manufacturers. ENISA built the tool and runs its day-to-day operations, a job Article 16(1) of the CRA hands to the agency. Anyone placing a product with digital elements on the EU…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
14th September – Threat Intelligence Report Critical CVE-2026-72898 Check Point Research
2026-09-14 Check Point Research

14th September – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 14th Setpember, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES IDScan.net, a US identity verification provider, has disclosed a data breach after detecting unauthorized access on September 1. Exposed data included names and government identification numbers, while a crim…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Webinar: How malicious OAuth apps can lead to Google Workspace breaches Critical BleepingComputer
2026-09-14 BleepingComputer

Webinar: How malicious OAuth apps can lead to Google Workspace breaches

Attackers can combine social engineering with malicious OAuth applications to gain access to Google Workspace data without relying solely on stolen passwords. This webinar examines two attacks to show how these breaches unfold and which security controls can help stop them. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Revolut handed customer data to fraudsters using government email account Moderate The Record by Recorded Future
2026-09-14 The Record by Recorded Future

Revolut handed customer data to fraudsters using government email account

British fintech company Revolut confirmed disclosing sensitive customer data to fraudsters who submitted emergency data requests from a legitimate government email account.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification