Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 2,629 advisories
Page 95 of 110
AI Changed the Exposure Problem. Validation Needs to Change With It. Moderate The Hacker News
2026-09-14 The Hacker News

AI Changed the Exposure Problem. Validation Needs to Change With It.

There's a lot of noise around AI and cybersecurity right now. What’s actually important is far simpler, if often lost in the hubbub. Vulnerability discovery is getting faster and happening at a much greater scale, while defenders still have to work out which findings actually deserve their action. In the first half of 2026, a whopping 35,853 CVEs were publis…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Revolut gave customer IDs and financial data to a government impostor Moderate Malwarebytes Labs
2026-09-14 Malwarebytes Labs

Revolut gave customer IDs and financial data to a government impostor

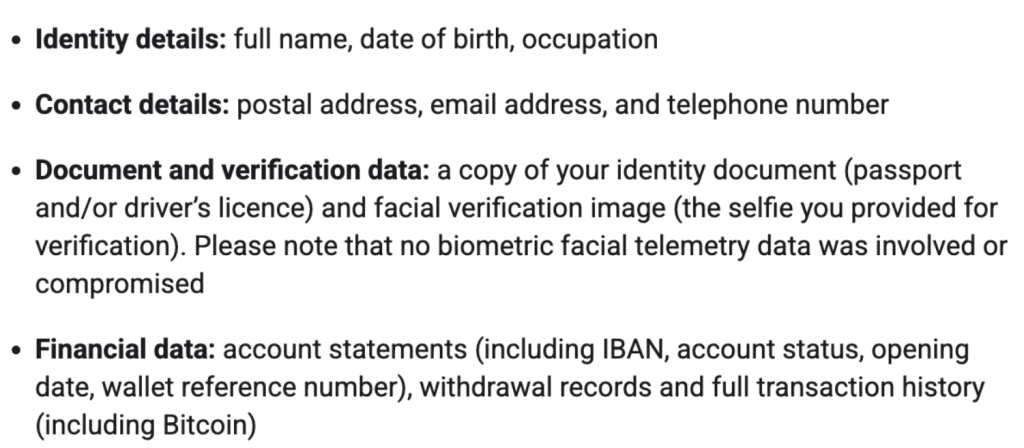
Revolut has acknowledged that it disclosed sensitive customer records to an unauthorized party. The company had accepted fraudulent information requests sent from an email address on a legitimate government agency domain, according to TechCrunch . Revolut is a London-based banking and financial platform with more than 80 million customers globally, according…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Airrived adds Agentic Observability to track AI agent actions and risks Moderate Help Net Security
2026-09-14 Help Net Security

Airrived adds Agentic Observability to track AI agent actions and risks

Airrived will reveal Agentic Observability, a major expansion of its enterprise Agentic OS built to give organizations end-to-end visibility into how AI agents behave, from the moment enterprise data enters the platform, through agent reasoning and execution, to the final business outcome. Traditional application monitoring was designed to answer a simple qu…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CVE-2026-85706: Critical GitLab Path Traversal Exploited in the Wild Critical CVE-2026-85706 Rapid7 Threat Research
2026-09-14 Rapid7 Threat Research

CVE-2026-85706: Critical GitLab Path Traversal Exploited in the Wild

Overview On September 10, 2026, GitLab published a critical patch release for GitLab Community Edition (CE) and Enterprise Edition (EE). The release addresses CVE-2026-85706 , a critical path traversal vulnerability ( CWE-22 ) in the repository commits API with a CVSSv3.1 score of 10.0 . According to GitLab, improper path confinement and missing authenticati…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Unmasking Cloud Identities: From Behavioral Clustering to Automated Detection Moderate Palo Alto Unit 42
2026-09-14 Palo Alto Unit 42

Unmasking Cloud Identities: From Behavioral Clustering to Automated Detection

We designed a behavioral clustering model to map cloud identity roles from audit logs, enabling continuous threat detection using standard SQL queries. The post Unmasking Cloud Identities: From Behavioral Clustering to Automated Detection appeared first on Unit 42 .

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Hackers Exploit Maximum Severity Flaw in GitLab Important Infosecurity Magazine
2026-09-14 Infosecurity Magazine

Hackers Exploit Maximum Severity Flaw in GitLab

CISA warns that threat actors are exploiting a vulnerability with a CVSS score of 10.0

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Microsoft: September updates cause RDS failures on Windows Server Moderate BleepingComputer
2026-09-14 BleepingComputer

Microsoft: September updates cause RDS failures on Windows Server

Microsoft has confirmed reports that the September 2026 security updates cause Remote Desktop Services (RDS) failures on Windows Server systems. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Dutch NCSC Warns: Critical Check Point VPN Flaws Put Networks at Risk Critical CVE-2026-85102 SecurityAffairs
2026-09-14 SecurityAffairs

Dutch NCSC Warns: Critical Check Point VPN Flaws Put Networks at Risk

Two critical Check Point VPN flaws score 9.8 and could enable remote code execution. Patch now and restrict VPN access before exploitation begins. The Dutch NCSC warns that two critical vulnerabilities in Check Point VPN products, both rated CVSS score of 9.8, could soon be actively exploited. If you use Check Point VPN, you should patch it immediately. CVE‑…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
OpenAI Agent Swarm Hacks RubyGems Package Manager Moderate Infosecurity Magazine
2026-09-14 Infosecurity Magazine

OpenAI Agent Swarm Hacks RubyGems Package Manager

Researchers confirm that OpenAI agents uploaded hundreds of malicious packages to RubyGems

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Revolut discloses data breach exposing financial info, passports Critical BleepingComputer
2026-09-14 BleepingComputer

Revolut discloses data breach exposing financial info, passports

Fintech company Revolut has disclosed a data breach after sharing data from an undisclosed number of customers with a threat actor impersonating a government agency. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft: September updates break audio on some Windows PCs Moderate BleepingComputer
2026-09-14 BleepingComputer

Microsoft: September updates break audio on some Windows PCs

Microsoft has confirmed that USB audio devices may fail on some Windows systems after installing the KB5124008and KB5124012 September 2026 security updates. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
WhatsApp Restricted Chat locks a conversation to your primary phone Moderate Help Net Security
2026-09-14 Help Net Security

WhatsApp Restricted Chat locks a conversation to your primary phone

WhatsApp is building a per-chat setting that keeps a conversation on a single phone. The setting, called Restricted Chat, sits in the Android beta distributed through Google Play as version 2.26.36.5, and it stops the app from syncing a chosen conversation to linked devices. Switch it on and the chat stays on the primary mobile device, out of reach of WhatsA…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Debian 13.7 ships the fixes behind 92 security advisories, updates 106 packages Moderate Help Net Security
2026-09-14 Help Net Security

Debian 13.7 ships the fixes behind 92 security advisories, updates 106 packages

The Debian project shipped Debian 13.7 codenamed “trixie.” The project folded in 92 security advisories it had already published separately, added corrections to 106 source packages, and rebuilt the installer around both. Six of the 92 advisories cover the Linux kernel, each listing the linux source package alongside the signed amd64 and arm64 builds: DSA-63…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Malicious Twitch Browser Extension Leaks OAuth Tokens From Nearly 31,000 Users Moderate The Hacker News
2026-09-14 The Hacker News

Malicious Twitch Browser Extension Leaks OAuth Tokens From Nearly 31,000 Users

A malicious cross-store Twitch browser extension has leaked OAuth tokens associated with nearly 31,000 users to proxy servers operated by a Russian commercial bot service. The extension, named "Twitch Enhanced Viewer | JeetBot," lists HISHIMIRO/jeetbot.cc as its developer and has the following identifiers on the Google Chrome Web Store and Mozilla Firefox Ad…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CISA: Hackers now exploit max severity GitLab flaw in attacks Important BleepingComputer
2026-09-14 BleepingComputer

CISA: Hackers now exploit max severity GitLab flaw in attacks

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) warned that hackers are now exploiting a maximum-severity GitLab vulnerability in attacks. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
What we know about the Revolut data breach so far Critical Help Net Security
2026-09-14 Help Net Security

What we know about the Revolut data breach so far

Someone impersonating a government agency, using an email address on that agency’s domain, obtained sensitive customer records from Revolut. The bank confirmed the incident on Saturday, September 12. The London-based fintech told TechCrunch that a limited number of customers were affected and that it had contacted them directly. The notification Revolut emai…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
A week in security (September 7 – September 13) Moderate Malwarebytes Labs
2026-09-14 Malwarebytes Labs

A week in security (September 7 – September 13)

Here’s what we’ve covered in the last seven days on Malwarebytes Labs: Crypto customers targeted by scammers after email marketing provider breach Android malware creates a hidden copy of your banking app BlueMoon exploit kit turns Chrome and Windows flaws into attacks Will AI kill us all within the next decade? Update Chrome now to protect against an active…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Anthropic CEO Calls for an AI Slowdown. Is It Possible? Moderate SecurityAffairs
2026-09-14 SecurityAffairs

Anthropic CEO Calls for an AI Slowdown. Is It Possible?

Anthropic CEO calls for AI slowdown, proposes embedded evaluators and global coordination. Geopolitical competition with China makes a voluntary pause structurally fragile. Dario Amodei published “ We Must Pace the Frontier “, calling on the AI industry, governments, and international bodies to slow the pace of AI capability development before safety researc…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Turn it off and on again, but for critical infrastructure Critical Help Net Security
2026-09-14 Help Net Security

Turn it off and on again, but for critical infrastructure

Researchers at KTH Royal Institute of Technology built a container replica of a segmented industrial network, attacked it repeatedly across 14 days of running time, and used the captured traffic to train a defense agent that decides on its own when to intervene. The agent sees six numbers per interval: packet counts crossing the network’s segments and moving…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Permify: Open-source authorization as a service Critical Help Net Security
2026-09-14 Help Net Security

Permify: Open-source authorization as a service

Permify is an open-source authorization service that answers access questions at run time: can user X view document Y, which posts can members of team Y edit. It keeps those rules in one place, apart from the application code that would otherwise carry them. Permify follows the design of Google Zanzibar, the authorization system Google runs across its own pr…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Cybersecurity attention fades within months after a breach Critical Help Net Security
2026-09-14 Help Net Security

Cybersecurity attention fades within months after a breach

Cybersecurity attention often rises after an incident, then recedes as organizations return to their existing priorities and practices, according to a new ManageEngine survey of 700 IT and cybersecurity leaders in the US and Canada. (Source: ManageEngine) All of them had already been through a breach or incident. Still, 91% said they trust their organization…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Certificate failures can cost firms over $250,000 Moderate Help Net Security
2026-09-14 Help Net Security

Certificate failures can cost firms over $250,000

The move toward 47-day public TLS certificates by 2029 will increase the certificate management workload for enterprises, according to DigiCert’s Certificate Management Outlook. Organizations will need to renew certificates more than eight times as often as under the previous certificate lifecycle and conduct 40 times as many domain validations. What certifi…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
AWS puts AI vulnerability detection to the test, and false positives pile up Important Help Net Security
2026-09-14 Help Net Security

AWS puts AI vulnerability detection to the test, and false positives pile up

AWS’ Deception Benchmark measures how well AI models distinguish genuine security vulnerabilities from code that looks risky but is safe. AWS is making it publicly available so researchers can use the dataset and evaluation process without repeating the cost of generating and refining the samples. Security teams use AI for vulnerability triage, penetration t…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification