
Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 5,807 advisories
Page 91 of 242
Attackers hijack country-code domains to impersonate Google and other services Important Malwarebytes Labs
2026-10-08 Malwarebytes Labs

Attackers hijack country-code domains to impersonate Google and other services

According to Google , attackers compromised infrastructure behind three country-code domain namespaces— .gh (Ghana), .sl (Sierra Leone), and .as (American Samoa)—and used it to obtain unauthorized HTTPS certificates for Google domains and other organizations. These domain endings aren’t limited to sites serving those countries, so the risk can extend to user…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Japan Sees Sharp Rise in Web Data Leaks Amid Mobile API Abuse and Metabase Attacks Important The Hacker News
2026-10-08 The Hacker News

Japan Sees Sharp Rise in Web Data Leaks Amid Mobile API Abuse and Metabase Attacks

Attackers behind a string of personal data leaks at Japanese organizations have abused APIs for mobile apps and targeted known software flaws, the JPCERT Coordination Center (JPCERT/CC) said. The Tokyo-based center, which takes incident reports, based its October 8, 2026 alert on those reports and other information. The alert names no attacker and no affecte…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Crypto thief who splurged on gold grills sentenced in London Moderate The Record by Recorded Future
2026-10-08 The Record by Recorded Future

Crypto thief who splurged on gold grills sentenced in London

A 25-year-old man who helped steal nearly $260,000 in cryptocurrency through a SIM-swapping fraud scheme was sentenced to two and a half years in prison at a London court.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
UAC-0099 Targets Ukrainian Government Personnel With ASHVEIN RAT Hiding Commands in HTML Moderate The Hacker News
2026-10-08 The Hacker News

UAC-0099 Targets Ukrainian Government Personnel With ASHVEIN RAT Hiding Commands in HTML

The Russia-aligned threat actor known as UAC-0099 has been attributed to a previously undocumented .NET infostealer and remote access trojan (RAT) codenamed ASHVEIN. According to TrendAI, the malware has been put to use in attacks targeting Ukrainian government personnel. The cybersecurity company is tracking the cluster under the name Earth Sirrush (previou…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Cisco warns of critical flaws allowing Nexus switch takeover Critical BleepingComputer
2026-10-08 BleepingComputer

Cisco warns of critical flaws allowing Nexus switch takeover

Cisco released security advisories for five critical vulnerabilities in its NX-OS data center network operating system that could be exploited to run arbitrary code with root privileges on Nexus switches. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Leaked chats show Russian extortion gang sending ‘agents’ into US law firms Moderate The Record by Recorded Future
2026-10-08 The Record by Recorded Future

Leaked chats show Russian extortion gang sending ‘agents’ into US law firms

In leaked chats, members track dozens of victims, haggle over multimillion-dollar payments and direct operatives based in the United States whom they call “agents.”

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
ARTEX AI Pentesting Tool Used in Data Theft Attacks on South Korean Financial Firms Important The Hacker News
2026-10-08 The Hacker News

ARTEX AI Pentesting Tool Used in Data Theft Attacks on South Korean Financial Firms

Cybersecurity researchers have disclosed details of a targeted campaign aimed at South Korean financial organizations that used an artificial intelligence (AI) pen testing tool named ARTEX to carry out the attacks. The activity, per CrowdStrike Intelligence, was active from late September to early October 2026, and resulted in data exfiltration from various …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

OAuth grants pile up faster than you can review them. Here's how to keep up. Moderate BleepingComputer
2026-10-08 BleepingComputer

OAuth grants pile up faster than you can review them. Here's how to keep up.

OAuth grants create data highways between SaaS apps, AI agents, and other tools. And, they are multiplying faster than any security team can review them. As the recent Klue breach showed, attackers are taking notice and exploiting forgotten OAuth grants to gain access to corporate data. This article covers why OAuth risks are so hard [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CVE-2026-83947 Azure Event Grid Spoofing Vulnerability Moderate CVE-2026-83947 Microsoft MSRC
2026-10-08 Microsoft MSRC

CVE-2026-83947 Azure Event Grid Spoofing Vulnerability

Missing authorization in Azure Event Grid allows an authorized attacker to perform spoofing over a network.

Fix: Deploy cumulative update via Windows Update or Microsoft Update Catalog.
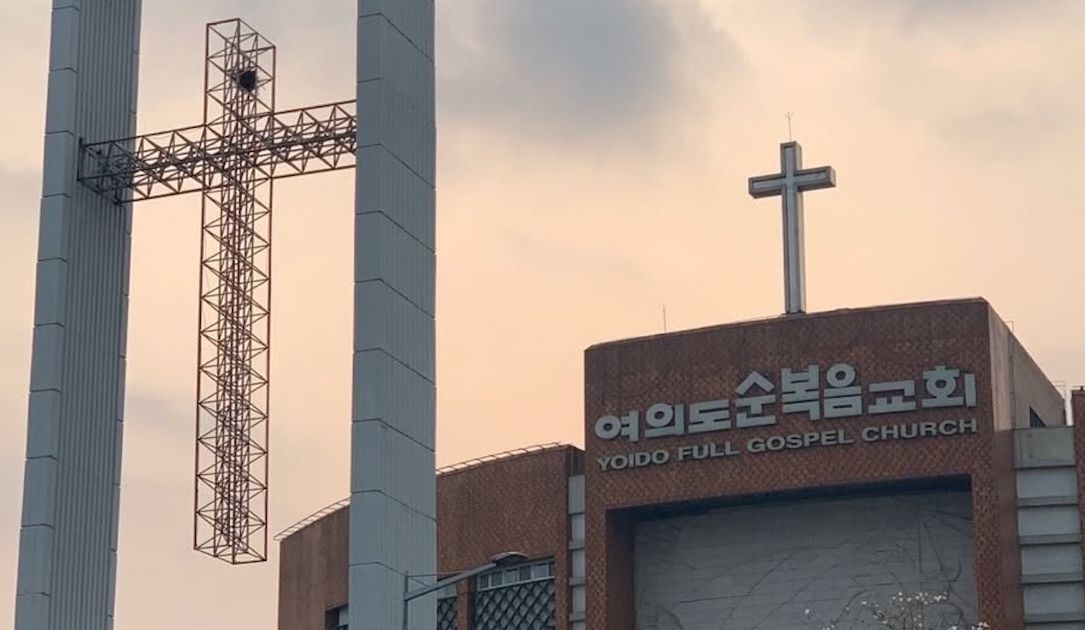
Hackers target two South Korean megachurches, potentially exposing congregant data Important The Record by Recorded Future
2026-10-08 The Record by Recorded Future

Hackers target two South Korean megachurches, potentially exposing congregant data

Two of South Korea's largest Protestant churches are investigating cyberattacks that may have exposed sensitive information about hundreds of thousands of members, including personal details, financial records and internal documents.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
MonsterCloud Owner Charged With Secretly Paying Ransomware Demands Critical SecurityAffairs
2026-10-08 SecurityAffairs

MonsterCloud Owner Charged With Secretly Paying Ransomware Demands

MonsterCloud owner Zohar Pinhasi allegedly paid ransomware demands behind clients’ backs, then charged them millions for the supposed recovery. Zohar Pinhasi, the owner of Florida-based MonsterCloud, was charged this week with wire fraud. Federal prosecutors say his clients were scammed twice during the same ransomware crisis. Pinhasi (50) also used the name…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Uranium crypto exchange hacker convicted for stealing $53 million Moderate BleepingComputer
2026-10-08 BleepingComputer

Uranium crypto exchange hacker convicted for stealing $53 million

A Maryland man was found guilty of stealing more than $53 million after hacking the decentralized crypto exchange Uranium Finance twice in April 2021. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification