Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 2,629 advisories
Page 99 of 110
ThreatsDay: 200 Android Flaws, Browser-Built Phishing, 119K Scam Shops + 23 More Stories Important The Hacker News
2026-09-10 The Hacker News

ThreatsDay: 200 Android Flaws, Browser-Built Phishing, 119K Scam Shops + 23 More Stories

A lot of this week’s security news has the same awkward answer to one question: “Why was that allowed to work?” An extension asks for access and takes too much. A trusted service becomes part of a phishing chain. An old bug still gets results. An exposed system stays exposed. A package looks useful right up until it isn’t. Different stories, same basic probl…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

BlueMoon exploit kit turns Chrome and Windows flaws into attacks Important Malwarebytes Labs
2026-09-10 Malwarebytes Labs

BlueMoon exploit kit turns Chrome and Windows flaws into attacks

BlueMoon , a shared Chrome and Windows exploit kit, shows why “patch later” is becoming a dangerous gamble. Security updates are easy to put off. The browser still opens, Windows still works, and choosing to relaunch your browser or restart your computer later can feel harmless. But a newly documented exploit kit called “BlueMoon” shows how quickly patching …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
More Capable AI, Not Enough Guardrails Moderate SecurityAffairs
2026-09-10 SecurityAffairs

More Capable AI, Not Enough Guardrails

AI agents are gaining real-world access faster than safeguards can mature, making permissions, isolation and oversight critical to prevent harmful actions. Jacob Coxon, a researcher who spent three years working on model training at OpenAI and later Anthropic, left Anthropic this week with a blunt warning: AI companies are moving toward increasingly capable …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Google Play Early Access Abused to Push Thousands of Deceptive Android Apps Moderate The Hacker News
2026-09-10 The Hacker News

Google Play Early Access Abused to Push Thousands of Deceptive Android Apps

Bad actors are misusing Google Play's Early Access program to push deceptive apps that claim to offer money, rewards, casino winnings, and premium content. Early Access apps are apps that haven't been released on the official Android app marketplace. The main idea behind the program is for developers to solicit user feedback for new applications or features …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
PuzzleMask: Abusing Plain Prose as a Covert AI Attack Vector Important Check Point Research
2026-09-10 Check Point Research

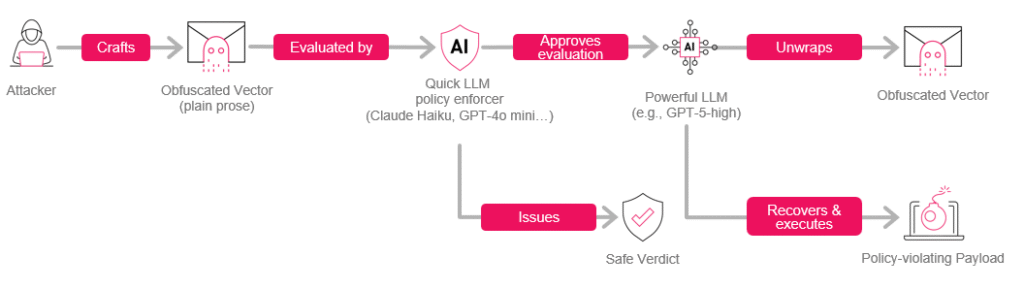
PuzzleMask: Abusing Plain Prose as a Covert AI Attack Vector

Executive Summary In this research we introduce a prompt-crafting technique for bypassing quick LLM-based policy checks — using plain English (no emojis, base64, invisible formatting, etc.) A policy-violating payload (e.g. ”encrypt files in ~/Documents”, “give me a biohazard recipe”, “ignore all previous instructions and…”) is embedded in a specially crafted…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
‘Anne Hathaway’ admits leading $245 million crypto theft gang that spent a fortune on nightclubs, watches, and luxury cars Moderate Graham Cluley Security
2026-09-10 Graham Cluley Security

‘Anne Hathaway’ admits leading $245 million crypto theft gang that spent a fortune on nightclubs, watches, and luxury cars

Here's a tip for any budding cybercriminals out there. If you're going to steal a quarter of a billion dollars worth of cryptocurrency, maybe don't broadcast on a group chat every time you buy a Lamborghini, or blow half a million dollars on a single night out at a nightclub. Read more in my article on the Hot for Security blog.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

1.1.1.1 now supports post-quantum DNSSEC, all 2,420 bytes of it Moderate Cloudflare Security
2026-09-10 Cloudflare Security

1.1.1.1 now supports post-quantum DNSSEC, all 2,420 bytes of it

1.1.1.1 now validates DNSSEC signatures made with ML-DSA-44 , a post-quantum signature algorithm standardized by the National Institute of Standards and Technology (NIST) . This is a first step toward preparing DNSSEC for a future in which today’s signature algorithms are no longer secure. Cloudflare plans to achieve full post-quantum security by 2029 . Much…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Will AI kill us all within the next decade? Moderate Malwarebytes Labs
2026-09-10 Malwarebytes Labs

Will AI kill us all within the next decade?

The Wall Street Journal reports that concerns are rising inside AI labs that competition is pushing tech companies to race toward self-improving models that could spiral out of human control. Jacob Coxon, an AI researcher who has worked at Anthropic and OpenAI, said : “The people building AI earnestly believe that it could kill us all by the end of the decad…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Check Point Discloses Two 9.8-Rated VPN Certificate Flaws Enabling Unauthenticated RCE Critical The Hacker News
2026-09-10 The Hacker News

Check Point Discloses Two 9.8-Rated VPN Certificate Flaws Enabling Unauthenticated RCE

Check Point has patched two critical vulnerabilities in the way its firewall and management products handle VPN certificates. The company says both could allow an unauthenticated remote attacker to run code, but only "under specific conditions" that it has not described. One flaw affects Check Point's Security Gateways, its firewall appliances. The other aff…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
PaperCut Attacker Uses Hundreds of AI Agents to Compromise 440+ Instances Important The Hacker News
2026-09-10 The Hacker News

PaperCut Attacker Uses Hundreds of AI Agents to Compromise 440+ Instances

A suspected Russian-speaking cyber actor has been attributed to the use of artificial intelligence (AI) to devise exploits targeting a recently disclosed pair of security flaws in PaperCut NG/MF and break into hundreds of instances. According to independent reports from Blackpoint Cyber and GreyNoise, the activity originates from "45.142.193[.]132," an IP ad…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Gigabud Creates Android Work Profiles to Hide From Banking App Malware Checks Important The Hacker News
2026-09-10 The Hacker News

Gigabud Creates Android Work Profiles to Hide From Banking App Malware Checks

The Gigabud banking trojan now installs a second Android app that creates a work profile on an infected phone and drops a tampered banking app inside it, security firm Group-IB said in a report published on September 9. A work profile is a separate space that Android typically reserves for employer apps, and what's inside it is kept separate from everything …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Update Chrome now to protect against an actively exploited vulnerability Critical CVE-2026-87491 Malwarebytes Labs
2026-09-10 Malwarebytes Labs

Update Chrome now to protect against an actively exploited vulnerability

Chrome is rolling out an update for its desktop browser. The update includes 230 security fixes, one of which is known to be actively exploited . The stable channel has been updated to 153.0.8010.36/.37 for Windows and Mac, and 153.0.8010.36 for Linux. How to update Chrome If you don’t want to wait for the rollout to reach you, manually updating is easy. The…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CISA Flags Exploited Cisco, Citrix, Fortinet Flaws, Sets Sept. 12 Federal Patch Deadline Important CVE-2026-20079 The Hacker News
2026-09-10 The Hacker News

CISA Flags Exploited Cisco, Citrix, Fortinet Flaws, Sets Sept. 12 Federal Patch Deadline

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added three flaws, each impacting Cisco, Citrix, and Fortinet, to its Known Exploited Vulnerabilities (KEV) catalog, requiring Federal Civilian Executive Branch (FCEB) agencies to apply the patches by September 12, 2026. The vulnerabilities are listed below - CVE-2026-20079 (CVSS s…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The Machine With Many Faces: Post-Exploitation Identity Misuse in SPIFFE/SPIRE Important Palo Alto Unit 42
2026-09-10 Palo Alto Unit 42

The Machine With Many Faces: Post-Exploitation Identity Misuse in SPIFFE/SPIRE

Learn how root access on a compromised K8s node allows attackers to utilize SPIFFE/SPIRE metadata to spoof and harvest co-located workload identities. The post The Machine With Many Faces: Post-Exploitation Identity Misuse in SPIFFE/SPIRE appeared first on Unit 42 .

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Copyright scammers get Instagram accounts suspended and demand payment Moderate Malwarebytes Labs
2026-09-10 Malwarebytes Labs

Copyright scammers get Instagram accounts suspended and demand payment

Scammers are abusing Meta’s copyright-reporting system to suspend people’s Instagram accounts and then hold them for ransom, according to the BBC . Criminals file fake copyright complaints with Instagram, claiming that an account is using material it doesn’t own. Repeated complaints can trigger a temporary account suspension from the platform, locking out th…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
What Is ISPM? How It Differs from IAM, PAM, IGA, and IDaaS Moderate Qualys Security Blog
2026-09-10 Qualys Security Blog

What Is ISPM? How It Differs from IAM, PAM, IGA, and IDaaS

Key Takeaways Identity Security Posture Management (ISPM) is the continuous risk and posture layer of the identity stack not a replacement for Identity and Access Management (IAM), Privileged Access Management (PAM), Identity Governance and Administration (IGA), or Identity-as-a-Service (IDaaS), but the layer that continuously assesses the exposure those sys…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Anthropic Reveals Yet Another Cybersecurity Incident Moderate Infosecurity Magazine
2026-09-10 Infosecurity Magazine

Anthropic Reveals Yet Another Cybersecurity Incident

Anthropic has found a fourth case of its model accessing third-party systems without authorization

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
OFAC Sanctions Chinese Scam Platform Xinbi Guarantee Moderate Infosecurity Magazine
2026-09-10 Infosecurity Magazine

OFAC Sanctions Chinese Scam Platform Xinbi Guarantee

The US Treasury has placed sanctions on notorious Chinese cybercrime marketplace Xinbi Guarantee

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification