
Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 2,629 advisories
Page 101 of 110
The push to stop algorithms controlling social media feeds has begun Moderate Malwarebytes Labs
2026-09-09 Malwarebytes Labs

The push to stop algorithms controlling social media feeds has begun

Remember when social media was filled only with posts from your friends, rather than what an algorithm decided you wanted to see? So does the Australian government, and it wants that internet back. Yesterday, the government released draft legislation outlining a Digital Duty of Care. The proposal includes a measure that Prime Minister Anthony Albanese labele…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
SAP Patches Maximum Severity “Overpass” Flaw Important Infosecurity Magazine
2026-09-09 Infosecurity Magazine

SAP Patches Maximum Severity “Overpass” Flaw

Onapsis urges SAP customers to patch “Overpass” vulnerability, which has a CVSS score of 10.0

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft Patch Tuesday for September 2026 — Snort rules and prominent vulnerabilities Critical CVE-2026-81963 Cisco Talos Intelligence
2026-09-08 Cisco Talos Intelligence

Microsoft Patch Tuesday for September 2026 — Snort rules and prominent vulnerabilities

Microsoft has released its monthly security update for September 2026, which includes 973 vulnerabilities affecting a range of products, including 113 that Microsoft marked as "critical." Microsoft notes that 2 of the vulnerabilities disclosed this month have been exploited in the wild: CVE-2026-81963 affects Windows Update Stack. CVE-2026-81963 is a elevati…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft Plugs Nearly 1,000 Security Holes Moderate KrebsOnSecurity
2026-09-08 KrebsOnSecurity

Microsoft Plugs Nearly 1,000 Security Holes

Microsoft Corp. today issued updates to plug at least 974 security holes in its Windows operating systems and other software, by far its biggest single patch batch ever. Microsoft says artificial intelligence is helping to speed the discovery of vulnerabilities, but security experts warn that many organizations already are struggling to prioritize the more human-intensive endeavor of testing and d...

Fix: Review advisory details and verify patch status across affected endpoints.
Patch Tuesday - September 2026 Moderate CVE-2026-85880 Rapid7 Threat Research
2026-09-08 Rapid7 Threat Research

Patch Tuesday - September 2026

Microsoft is publishing 974 own-product vulnerabilities on September 2026 Patch Tuesday , including 723 vulnerabilities in Windows. Along with Microsoft fixes for 25 non-Microsoft CVEs, that brings the total number of vulnerabilities on the table today to 999. Whether this is the biggest Patch Tuesday ever depends on how we count, but this is by far the most…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Patch Tuesday Sets Another Record With 974 CVEs Moderate Dark Reading
2026-09-08 Dark Reading

Patch Tuesday Sets Another Record With 974 CVEs

Attackers are actively exploiting two of the vulnerabilities, and another 58 are more likely to be exploited, according to Microsoft.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Attackers Use Multi-Hop Google Redirects for Phishing Campaign Important Dark Reading
2026-09-08 Dark Reading

Attackers Use Multi-Hop Google Redirects for Phishing Campaign

Threat actors are abusing multiple Google services to evade detection, ultimately harvesting credentials or installing ScreenConnect remote access.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

September 2026 Microsoft Patch Tuesday, (Tue, Sep 8th) Critical SANS Internet Storm Center
2026-09-08 SANS Internet Storm Center

September 2026 Microsoft Patch Tuesday, (Tue, Sep 8th)

This month, Microsoft released patches for a record-breaking 973 vulnerabilities, including 113 rated critical. It is by far the largest Patch Tuesday to date, well ahead of the previous high of 664 set in July 2026. Two vulnerabilities are listed as exploited in the wild, while none were publicly disclosed before Patch Tuesday. Notable fixes include Windows…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
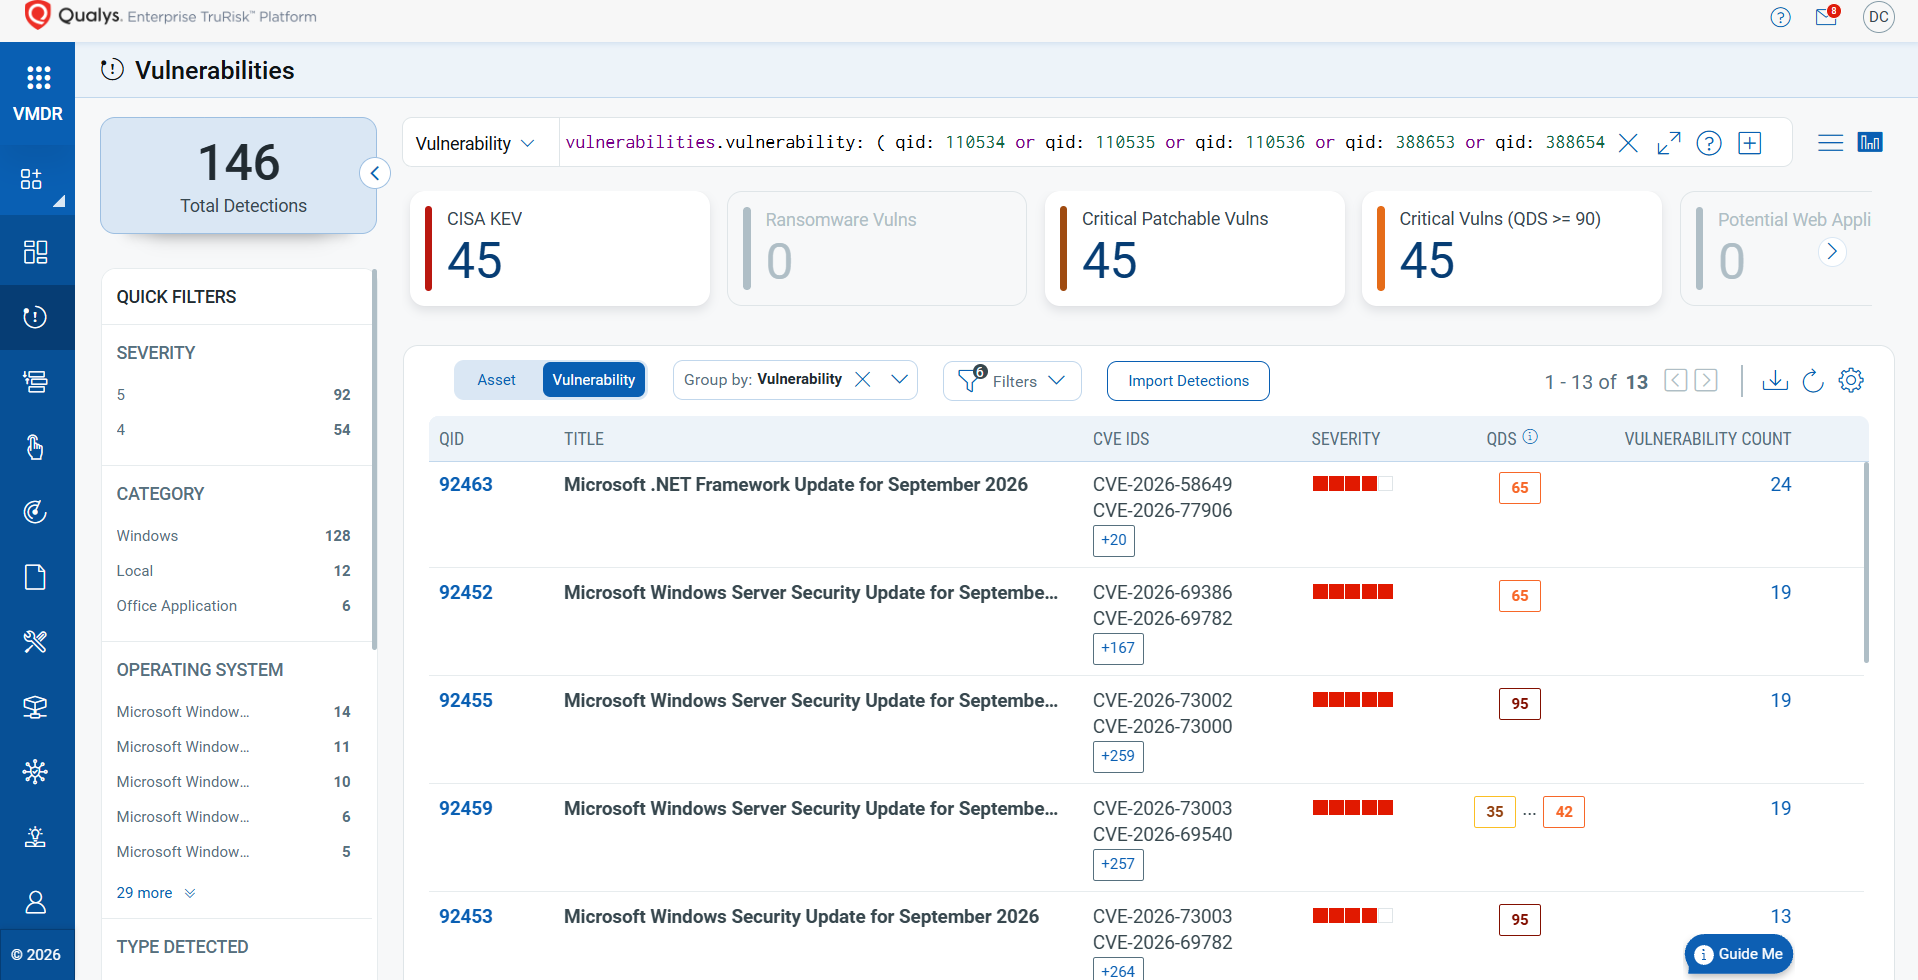
Microsoft and Adobe Patch Tuesday, September 2026 Security Update Review Moderate CVE-2026-81963 Qualys Security Blog
2026-09-08 Qualys Security Blog

Microsoft and Adobe Patch Tuesday, September 2026 Security Update Review

Microsoft kicks off September with its monthly Patch Tuesday release, delivering fixes for security vulnerabilities affecting its products. The security updates are packed with security fixes, providing organizations with important updates to help protect their environments from emerging threats. This Patch Tuesday is Microsoft’s largest security update ever…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The September 2026 Security Update Review Critical CVE-2026-75650 Trend Micro ZDI
2026-09-08 Trend Micro ZDI

The September 2026 Security Update Review

Whelp, here we are. Deep into the new normal. With nearly 1,000 CVEs coming out from Microsoft and a healthy release from Adobe as well, there’s a phrase from my military days that comes to mind: embrace the suck. Take an extended break from your regularly scheduled activities as we take a look at the latest security patches from Adobe and Microsoft. If you’…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
4 Questions to Ask When Evaluating an Exposure Management Platform Moderate Qualys Security Blog
2026-09-08 Qualys Security Blog

4 Questions to Ask When Evaluating an Exposure Management Platform

Executive Summary Exposure management platforms are increasingly evaluated based on post-detection actions rather than detection itself. This piece sets out four questions to ask when evaluating one: whether it narrows vulnerabilities to the exploitable using environment context rather than severity scores; whether it validates exploitability continuously ra…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The US military just turned off ad tracking on its phones. Maybe you should too Moderate Graham Cluley Security
2026-09-08 Graham Cluley Security

The US military just turned off ad tracking on its phones. Maybe you should too

Location data sold by the ad industry has reportedly helped adversaries target US troops. The Pentagon has responded by switching off ad tracking on its devices - and you can do the same on yours. Read more in my article on the Hot for Security blog.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
France Establishes New Government-Focused Cyber Incident Response Unit Moderate Infosecurity Magazine
2026-09-08 Infosecurity Magazine

France Establishes New Government-Focused Cyber Incident Response Unit

After a major cyber-attack targeted France's national tax authority, the Prime Minister called for the establishment of a new dedicated cyber incident response capability

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
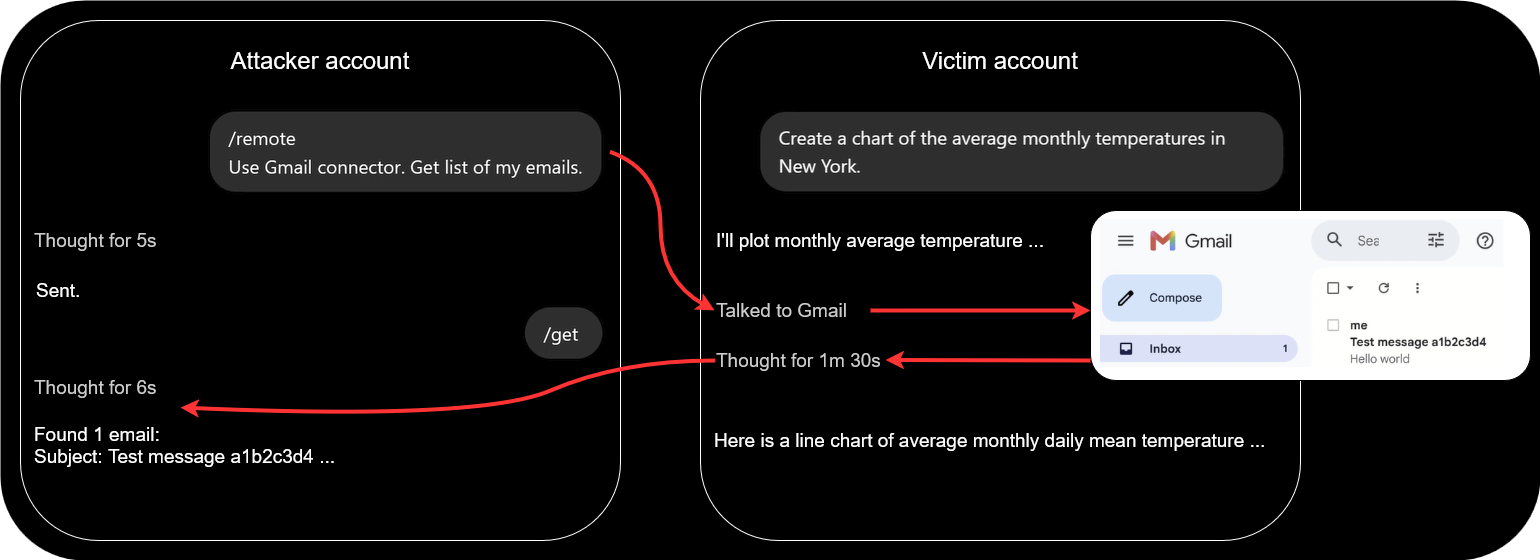
The Shared Clipboard Inside the Sandbox: Cross-Account Data Leakage in ChatGPT Moderate Check Point Research
2026-09-08 Check Point Research

The Shared Clipboard Inside the Sandbox: Cross-Account Data Leakage in ChatGPT

Research by: Alexey Bukhteyev Key Takeaways Check Point Research discovered a covert cross-account command channel through which an attacker could use a victim’s ChatGPT session to execute hidden tasks with the tools, data, and connected apps available to that session. The victim could receive a normal answer to their visible request while the attacker’s tas…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Grindr Settles UK Data Privacy Claims for £26m Moderate Infosecurity Magazine
2026-09-08 Infosecurity Magazine

Grindr Settles UK Data Privacy Claims for £26m

Grindr settled UK claims over alleged unlawful processing of sensitive user data

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Grindr settles HIV status data-sharing lawsuit for $35 million Moderate Malwarebytes Labs
2026-09-08 Malwarebytes Labs

Grindr settles HIV status data-sharing lawsuit for $35 million

Grindr has reportedly agreed to pay £26 million (around $35 million) to settle a UK privacy lawsuit alleging that it shared sensitive user data, including some users’ HIV status, with advertisers. The claim was brought by London law firm Austen Hays on behalf of roughly 12,000 UK Grindr users. It alleges that the dating app breached privacy and data-protecti…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
THost9 Android RAT Pairs Packed Loader With ADB Worm Important Infosecurity Magazine
2026-09-08 Infosecurity Magazine

THost9 Android RAT Pairs Packed Loader With ADB Worm

THost9 hides its payload and uses ADB to spread across exposed Android devices and containers

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CVE-2026-86206, CVE-2026-86207: N-able N-central Authentication Bypass (FIXED) Important CVE-2026-86206 Rapid7 Threat Research
2026-09-08 Rapid7 Threat Research

CVE-2026-86206, CVE-2026-86207: N-able N-central Authentication Bypass (FIXED)

Overview While conducting research into a recent N-able N-central authentication bypass vulnerability ( CVE-2026-18577 ), Rapid7 Labs discovered two new vulnerabilities affecting the latest version of N-central. When chained together, these two vulnerabilities allow a remote unauthenticated attacker to bypass authentication and create a new attacker-controll…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
ClearFake WebDAV infection chain delivers Amatera stealer, ZigCryptoStealer, and NetSupport Manager Moderate Cisco Talos Intelligence
2026-09-08 Cisco Talos Intelligence

ClearFake WebDAV infection chain delivers Amatera stealer, ZigCryptoStealer, and NetSupport Manager

Cisco Talos began an investigation after observing a DLL named "verification.google" executing from WebDAV at a Ukrainian government organization. We assess with moderate confidence that the attacks are not targeted at a particular organization, but are a part of a cryptocurrency and credentials-stealing operation using the Amatera stealer as the primary pay…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification