Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 2,629 advisories
Page 102 of 110
ClickFix moves into the browser: Cryptocurrency theft with Google-hosted C2 Moderate Cisco Talos Intelligence
2026-09-08 Cisco Talos Intelligence

ClickFix moves into the browser: Cryptocurrency theft with Google-hosted C2

Cisco Talos is tracking a cryptocurrency-stealing campaign that abuses the Google Visualization API for command and control (C2), retrieving obfuscated JavaScript from a publicly published Google Sheets document and injecting it into the victim's browser session. The actors use a variation on ClickFix social engineering. Instead of convincing targets to run …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

MikroTik router flaws allow takeover without a password Important CVE-2026-67276 Malwarebytes Labs
2026-09-08 Malwarebytes Labs

MikroTik router flaws allow takeover without a password

CERT Polska warns that attackers are actively exploiting a chain of critical MikroTik RouterOS flaws to seize control of routers exposed to the internet. Although the warning comes from Poland’s national cybersecurity response team, MikroTik routers are sold worldwide, including in the US. The vulnerabilities can affect users anywhere if their router is runn…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Trezor Supply Chain Breach Now Impacts 81,000 Customers Critical Infosecurity Magazine
2026-09-08 Infosecurity Magazine

Trezor Supply Chain Breach Now Impacts 81,000 Customers

Crypto wallet-maker Trezor says a data breach at supplier ShipMonk is far worse than originally thought

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Loyalty points fraud is funding hacker holidays (Lock and Code S07E18) Moderate Malwarebytes Labs
2026-09-07 Malwarebytes Labs

Loyalty points fraud is funding hacker holidays (Lock and Code S07E18)

This week on the Lock and Code podcast… Crooks are taking a holiday. They’re counting on you to fund it. For decades, cybercriminals have stolen roughly the same types of data. Biographical and personal details—like Social Security numbers, birthdates, addresses, and phone numbers—can be stolen to commit identity fraud. Credit card numbers, expiration dates,…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
7th September – Threat Intelligence Report Moderate CVE-2026-83548 Check Point Research
2026-09-07 Check Point Research

7th September – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 7th Setpember, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Thomson Reuters, a global information and technology company, has disclosed a breach of its C-Track court case-management platform affecting courts across 11 US states and Canada. An unauthorized party obtaine…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
NCSC Warns Shadow AI Creates New Security Risks Moderate Infosecurity Magazine
2026-09-07 Infosecurity Magazine

NCSC Warns Shadow AI Creates New Security Risks

NCSC warns unapproved AI tools can expose corporate data and create new security risks

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
LG TV flaws could let attackers listen in, even in standby mode Important Malwarebytes Labs
2026-09-07 Malwarebytes Labs

LG TV flaws could let attackers listen in, even in standby mode

Smart TVs are internet-connected computers with microphones, app stores, advertising systems, and access to the same home networks used by your family’s phones, laptops, printers, and smart-home devices. A major manufacturer in Smart TVs, LG, has come under the spotlight this week after an investigation by Gamers Nexus, carried out with Level1Techs and indep…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Flirty OnlyFans promoters on X may be using AI to appear human Moderate Malwarebytes Labs
2026-09-07 Malwarebytes Labs

Flirty OnlyFans promoters on X may be using AI to appear human

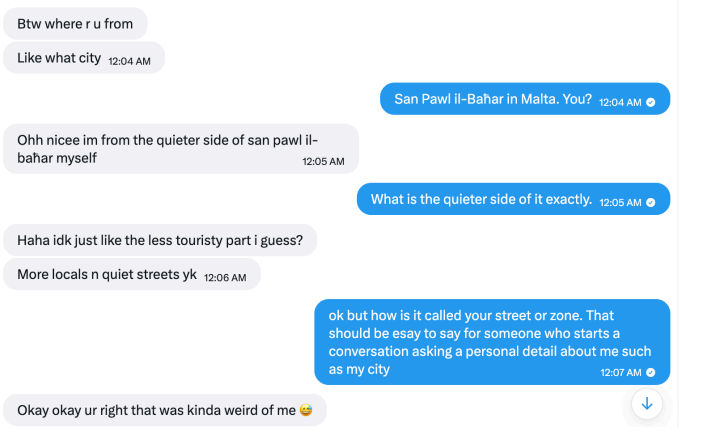
In a recent post, we looked at reports of League of Legends players receiving suspicious friend requests shortly after matches. The accounts quickly steered the conversation toward Discord, where they promoted paid adult-content pages. At the time, one unanswered question was how much of those conversations was automated. Were people working from scripts beh…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
North Korea’s Lazarus Operates Through Six Distinct Cyber Clusters Moderate Infosecurity Magazine
2026-09-07 Infosecurity Magazine

North Korea’s Lazarus Operates Through Six Distinct Cyber Clusters

Sekoia and Kudelski Security have observed that North Korea's Lazarus umbrella is split into six distinct clusters, focused on espionage, financial theft and sanctions evasion

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
How a hole in Lenovo’s login system let hackers walk into 5,000 Dropbox accounts Important Graham Cluley Security
2026-09-07 Graham Cluley Security

How a hole in Lenovo’s login system let hackers walk into 5,000 Dropbox accounts

If you ever linked your Dropbox account to a Lenovo ID - perhaps to make life easier when logging in via a Lenovo laptop - you might want to take heed. Read more in my article on the Hot for Security blog.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Multiple Class Action Lawsuits Filed Against IDScan Moderate Infosecurity Magazine
2026-09-07 Infosecurity Magazine

Multiple Class Action Lawsuits Filed Against IDScan

Several victims of a recent breach of driver’s license information have sued the company they believe responsible

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
A week in security (August 31 – September 6) Moderate Malwarebytes Labs
2026-09-07 Malwarebytes Labs

A week in security (August 31 – September 6)

Last week on Malwarebytes Labs: The hidden work of modernizing Malwarebytes X Money rollout linked to password-reset attacks Free streaming boxes may be routing criminal traffic through your home StreamRat Android malware spreads through Meta and TikTok ads Your phone or computer may soon ask how old you are Tech support scams look different now. Here’s what…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Critical MikroTik Vulnerability - Patch Now, (Sun, Sep 6th) Critical SANS Internet Storm Center
2026-09-06 SANS Internet Storm Center

Critical MikroTik Vulnerability - Patch Now, (Sun, Sep 6th)

Mikrotik released a patch late last week for an already-exploited vulnerability. The vulnerability allows an SSH authentication bypass and is already being exploited. At this point, assume compromise. Attackers have been adding new accounts to affected devices to maintain access after a patch is installed.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
numbat - AI agent observability, (Fri, Sep 4th) Moderate SANS Internet Storm Center
2026-09-05 SANS Internet Storm Center

numbat - AI agent observability, (Fri, Sep 4th)

Latest threat intelligence analysis from SANS Internet Storm Center: numbat - AI agent observability, (Fri, Sep 4th).

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The hidden work of modernizing Malwarebytes Important Malwarebytes Labs
2026-09-04 Malwarebytes Labs

The hidden work of modernizing Malwarebytes

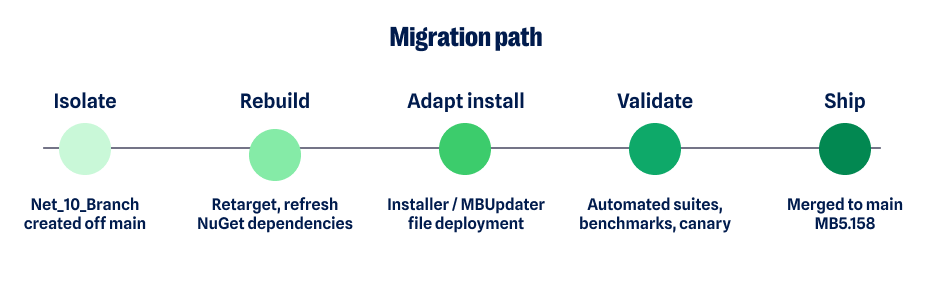
Most of the work that keeps a security product trustworthy is invisible. Users see a scan complete, a threat blocked, an update applied overnight. They don’t see the platform underneath. Runtimes, managed libraries, native drivers, and Windows requirements must all stay current and work together across millions of endpoints. Our migration to .NET 10 is one e…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Companies Have 6 Months to Prepare for Automated Attacks Important Dark Reading
2026-09-04 Dark Reading

Companies Have 6 Months to Prepare for Automated Attacks

Frontier AI models have already demonstrated they can autonomously — and in some cases, inadvertently — conduct end-to-end compromises, but researchers warn the situation will become more urgent very soon.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
X Money rollout linked to password-reset attacks Important Malwarebytes Labs
2026-09-04 Malwarebytes Labs

X Money rollout linked to password-reset attacks

X says attackers may be targeting accounts because its X Money payments service is now more widely available. The company is investigating a wave of unsolicited password-reset emails sent to users. While their arrival alongside the wider X Money rollout has fueled account-takeover concerns, X says it has found no evidence of a breach or successful account ta…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Insurers Search for Answers to Rein in Rogue AI Moderate Dark Reading
2026-09-04 Dark Reading

Insurers Search for Answers to Rein in Rogue AI

As incidents of unintended harm caused by rogue AI agents mount, CISOs and insurance firms are figuring out how to handle the fallout.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification