Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 2,629 advisories
Page 103 of 110
DPRK APTs: Ted backdoor and curlRAT target South Korean media and automotive sectors Important Rapid7 Threat Research
2026-09-04 Rapid7 Threat Research

DPRK APTs: Ted backdoor and curlRAT target South Korean media and automotive sectors

Overview A new Linux toolkit, identified by Rapid7 Labs, has been targeting organizations across South Korea’s automotive and media industries with minimal detection. The campaign made use of a HAProxy instance named “ted backdoor”, alongside trojanized versions of crond, agetty, atd, sshd, and polkitd. This previously undocumented framework enabled threat a…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Angry Birds: Toy Ghouls’ new toys Moderate Kaspersky Securelist
2026-09-04 Kaspersky Securelist

Angry Birds: Toy Ghouls’ new toys

Introduction We continue tracking the activity of Toy Ghouls (also known as Bearlyfy, Laboo.boo, and Feral Wolf), a financially motivated group that has been targeting Russian organizations since 2025. The attackers initially relied exclusively on tools pulled from public GitHub repositories along with leaked Babuk and LockBit ransomware builders, later shif…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Free streaming boxes may be routing criminal traffic through your home Moderate Malwarebytes Labs
2026-09-04 Malwarebytes Labs

Free streaming boxes may be routing criminal traffic through your home

“Free” movies and TV could cost you your privacy, bandwidth, and control of your home network. We’ve warned about illegal streaming and modded Amazon Fire TV Sticks in the past. Now, researchers have found that certain SuperBox devices and apps could quietly enroll a household connection into a proxy network, allowing third parties to route traffic through i…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Introducing context-aware vulnerability discovery and remediation with Cloudflare Managed Defense and OpenAI Daybreak models Important Cloudflare Security
2026-09-03 Cloudflare Security

Introducing context-aware vulnerability discovery and remediation with Cloudflare Managed Defense and OpenAI Daybreak models

Your scanner just flagged 4,000 new vulnerabilities, 78 of them critical. Which one do you fix first? To answer that question, Cloudflare is announcing early access to Vulnerability Discovery and Remediation, now part of Cloudflare Managed Defense . Vulnerability Discovery and Remediation is a new, invitation-only Cloudflare service that helps customers dete…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Large Enterprises Targeted in Fake Merger & Acquisition Scams Moderate Dark Reading
2026-09-03 Dark Reading

Large Enterprises Targeted in Fake Merger & Acquisition Scams

Threat actors behind the "Phantom Deal" campaign are studying companies in extreme detail, aiming to dupe midlevel employees into initiating large financial transfers.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
What We Missed: Did ShinyHunters 'Breach' ReliaQuest? Critical Dark Reading
2026-09-03 Dark Reading

What We Missed: Did ShinyHunters 'Breach' ReliaQuest?

In this video conversation, Dark Reading editors discuss some of the news they didn't get a chance to cover, from the latest antics of ShinyHunters to new research about the prevalence (or lack thereof) of AI-generated malware.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The story behind the intelligence Moderate Cisco Talos Intelligence
2026-09-03 Cisco Talos Intelligence

The story behind the intelligence

Welcome to this week’s edition of the Threat Source newsletter. Our goal is to get accurate threat intelligence to our audience as quickly as possible, with all the context you need to ask the right questions of your own environment: How at risk are we from this threat? Are we prepared for it? And what can we do about it? What you don’t often see is all the.…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
What the AI Warning Letter Completely Missed Moderate Dark Reading
2026-09-03 Dark Reading

What the AI Warning Letter Completely Missed

The recent open letter is right about the "window," but it omits naming who is coming through it or, critically, who will close it.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
StreamRat Android malware spreads through Meta and TikTok ads Important Malwarebytes Labs
2026-09-03 Malwarebytes Labs

StreamRat Android malware spreads through Meta and TikTok ads

A malicious advertising campaign promoting a fake free TV-streaming service reached roughly 570,000 Meta users. The researchers who discovered the campaign found that its streaming-themed ads were aimed at Spanish-speaking users, with most observed victims located in Spain. One Meta campaign ran from June 11 through July 3, 2026, and the same banners were al…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
AI 'Machine Speed' Cuts 2-Week Attack Down to 10 Hours Important Dark Reading
2026-09-03 Dark Reading

AI 'Machine Speed' Cuts 2-Week Attack Down to 10 Hours

The incident demonstrates how frontier AI agents can dramatically compress an attack timeline and coordinate a large-scale breach, according to researchers.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Attackers Expose Ongoing AI Tool Use Targeting Organizations in Latin America Important Palo Alto Unit 42
2026-09-03 Palo Alto Unit 42

Attackers Expose Ongoing AI Tool Use Targeting Organizations in Latin America

Explore how attackers targeting Latin American entities use AI for data exfiltration and how basic OpSec errors allow defenders to disrupt operations. The post Attackers Expose Ongoing AI Tool Use Targeting Organizations in Latin America appeared first on Unit 42 .

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Your phone or computer may soon ask how old you are Moderate Malwarebytes Labs
2026-09-03 Malwarebytes Labs

Your phone or computer may soon ask how old you are

First, the good news: If you use a Linux-based operating system, you may not be asked your age in a few months. The bad news is that Windows, macOS, iOS, and Android users in California will be. California has passed a law that requires a range of operating systems to start collecting your age when you first set them up. Under the state’s Digital Age Assuran…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Smashing Security podcast #483: This AI helps thieves steal your iPhone Moderate Graham Cluley Security
2026-09-02 Graham Cluley Security

Smashing Security podcast #483: This AI helps thieves steal your iPhone

You've had your iPhone stolen. A day later, you get a text from Apple saying they've found it, and a very helpful woman called Alice from Apple Support calls to walk you through recovering it. She's polite. She's professional. But she is not from Apple. She's not even human. And she's about to break into your iPhone. Meanwhile, OpenAI, Anthropic, and Meta ha…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Critical SonicWall SMA1000 Vulnerabilities CVE-2026-83548, CVE-2026-83549 Exploited in the Wild Critical CVE-2026-83548 Rapid7 Threat Research
2026-09-02 Rapid7 Threat Research

Critical SonicWall SMA1000 Vulnerabilities CVE-2026-83548, CVE-2026-83549 Exploited in the Wild

Overview On September 1, 2026, SonicWall disclosed two vulnerabilities affecting SonicWall SMA1000 appliances that the vendor says are being actively exploited in the wild. The vulnerabilities, CVE-2026-83548 and CVE-2026-83549 , can be chained to achieve unauthenticated remote code execution (RCE) on affected appliances. CVE-2026-83548 is a critical pre-aut…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

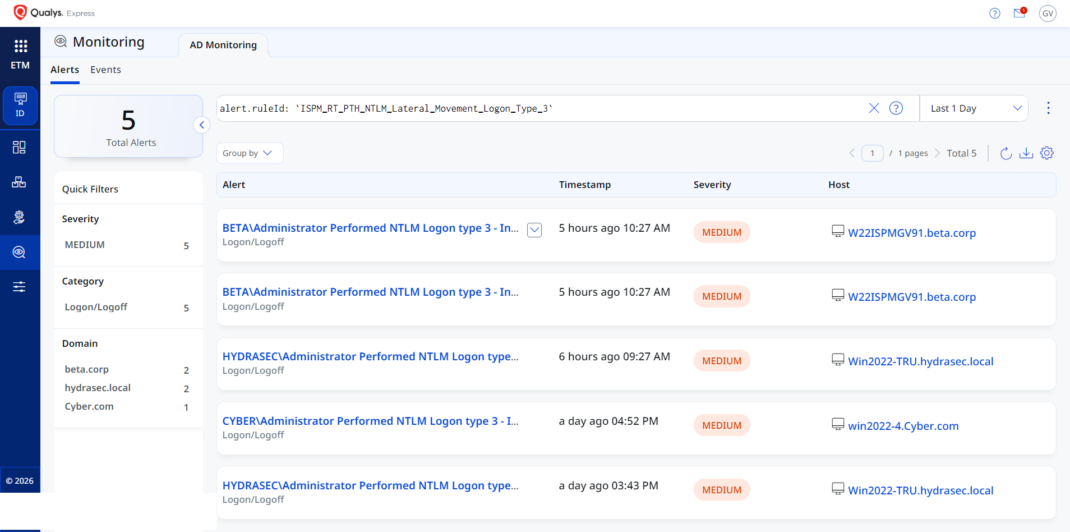
Anatomy of a Silent Domain Takeover Important Qualys Security Blog
2026-09-02 Qualys Security Blog

Anatomy of a Silent Domain Takeover

Key Takeaways Modern AD attacks use legitimate protocols end-to-end, no malware, no exploit, nothing for signature tools to fingerprint. The evidence is already in the logs; what is missing is the narrative linking five benign-looking Windows events into a single attack. A full domain takeover can be completed in 54 minutes, from the first password spray to …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Revolut scam wave steals £180,000 from Jersey residents in just four weeks Moderate Graham Cluley Security
2026-09-02 Graham Cluley Security

Revolut scam wave steals £180,000 from Jersey residents in just four weeks

If you live in Jersey and bank with Revolut, you should be on your guard against scam phone calls. Because local police on the largest of the Channel Islands have warned that over a single four-week period, an astonishing 75% of all scam crime reports they have received have involved Revolut accounts Read more in my article on the Hot for Security blog.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Gaming the system: how a Chinese-speaking actor turned Brazilian government sites into an SEO weapon Moderate Check Point Research
2026-09-02 Check Point Research

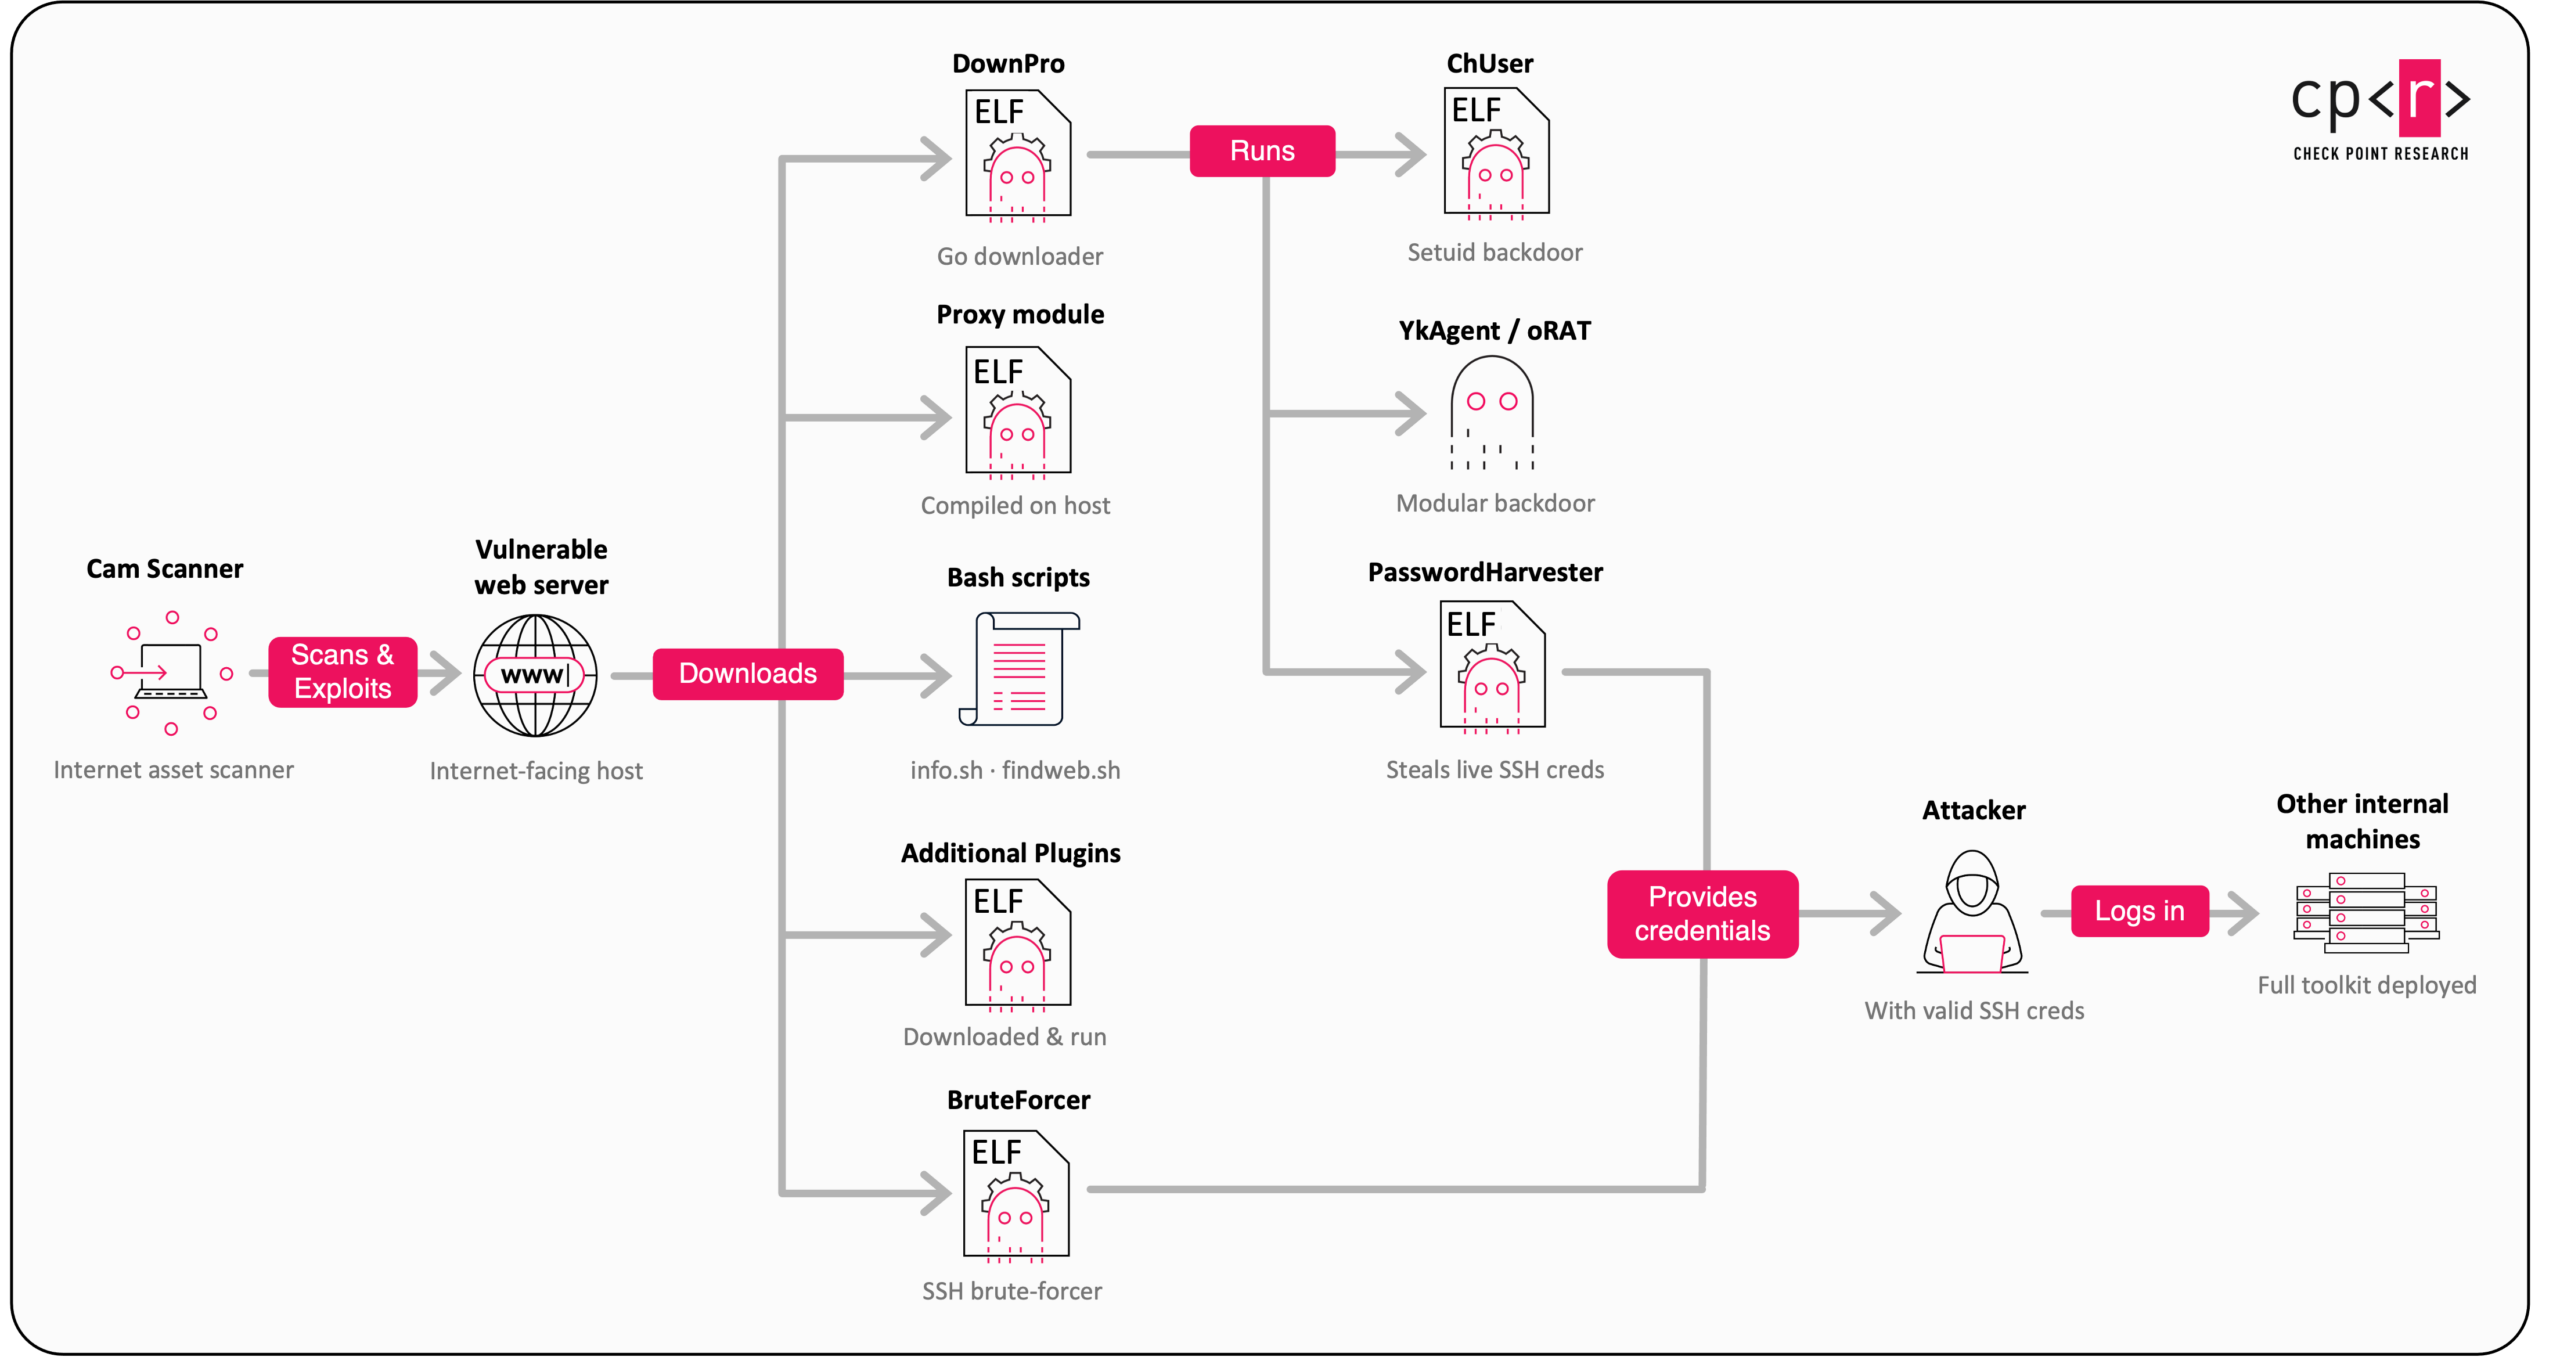
Gaming the system: how a Chinese-speaking actor turned Brazilian government sites into an SEO weapon

Research by: Amit Yardeni Key Points A Chinese-speaking actor is now targeting Brazil. Check Point Research has uncovered a sustained campaign against Brazilian organizations, primarily government and educational institutions since mid-2025. We dubbed this group Gambling Goblin: a Chinese-speaking cybercrime cluster connected to a previously documented group…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
An AI-Assisted Cyber Attack: Inside a Unit 42 Investigation Important Palo Alto Unit 42
2026-09-02 Palo Alto Unit 42

An AI-Assisted Cyber Attack: Inside a Unit 42 Investigation

Using autonomous AI agents, an attacker breached an enterprise network in a matter of hours. Understand how to address and defend against agentic attacks. The post An AI-Assisted Cyber Attack: Inside a Unit 42 Investigation appeared first on Unit 42 .

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
FBI Probes Service Selling 153M+ Drivers Licenses Moderate KrebsOnSecurity
2026-09-01 KrebsOnSecurity

FBI Probes Service Selling 153M+ Drivers Licenses

A new identity theft service launched on the dark web this week is selling digital scans of more than 153 million drivers licenses from people in the United States and Canada. Based on interviews with individuals whose licenses are available for purchase on this service, it appears to be siphoning images collected by a widely-used identity verification company based in Louisiana. KrebsOnSecurity a...

Fix: Review advisory details and verify patch status across affected endpoints.
Mirage Kitten targeting aviation and FinTech sectors across the Middle East and Africa with a new malware set Important Kaspersky Securelist
2026-09-01 Kaspersky Securelist

Mirage Kitten targeting aviation and FinTech sectors across the Middle East and Africa with a new malware set

While monitoring Mirage Kitten activity, we uncovered a previously undocumented malware family that we dubbed NodeRabbit. We identified the first sample on a system in Afghanistan. Further threat hunting revealed two additional, more advanced, variants: one on a system in Egypt and another on a system in Ethiopia. NodeRabbit is a cross-platform remote access…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Breaking the Seal: Static Deobfuscation of JSCeal’s Compiled V8 Bytecode Moderate Check Point Research
2026-08-31 Check Point Research

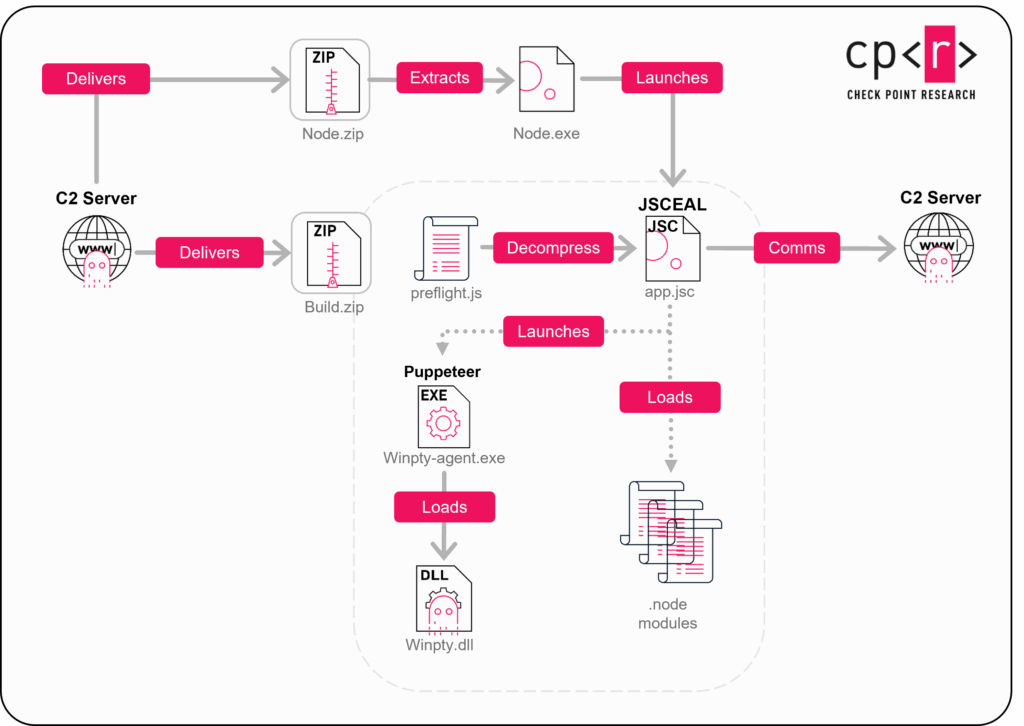
Breaking the Seal: Static Deobfuscation of JSCeal’s Compiled V8 Bytecode

Research by: hasherezade Key Points Since early 2025, Check Point Research has been tracking JSCeal, a sophisticated cryptocurrency-focused stealer with broader credential-theft, surveillance, and traffic-interception capabilities, delivered as compiled V8 bytecode (JSC files). The payloads are protected with javascript-obfuscator , using multiple techniques…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
31st August – Threat Intelligence Report Moderate CVE-2026-81578 Check Point Research
2026-08-31 Check Point Research

31st August – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 31st August, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Manchester Airports Group, the UK operator of Manchester, London Stansted, and East Midlands airports, has disclosed a cyberattack that exposed data belonging to about 8.7 million customers. The compromised info…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Spring Ring: An Inside Look at Voice Phishing Campaigns in Microsoft Teams Important Palo Alto Unit 42
2026-08-31 Palo Alto Unit 42

Spring Ring: An Inside Look at Voice Phishing Campaigns in Microsoft Teams

Learn how the Spring Ring campaign abuses Microsoft Teams and voice phishing to deploy malware and target enterprise domain controllers. The post Spring Ring: An Inside Look at Voice Phishing Campaigns in Microsoft Teams appeared first on Unit 42 .

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification