Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Tricks from the Past deployed via signed ChatGPT and Claude binaries
Lead Cyber Advisory Check Point Research Critical

Tricks from the Past deployed via signed ChatGPT and Claude binaries

Key Points Check Point Research discovered a campaign we track as Yoba where attackers abuse the popularity of AI tools such as ChatGPT and Claude, creating fake GitHub projects that pretend to be desktop applications like GPT-5.6 Sol , GPT-6 Astra , and Claude Opus . The malware is placed next to legitimate, signed executables from OpenAI and Anthropic so i…

Vendor: Check Point Research · Product: Exploit Research & Analysis
View Advisory Details

Showing 13 of 13 advisories
Page 1 of 1
5th October – Threat Intelligence Report Critical CVE-2026-88771 Check Point Research
2026-10-05 Check Point Research

5th October – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 5th October, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Arizona’s state court system has suffered a phishing-led cyberattack after an employee clicked a malicious link. Attackers copied backup files containing protective-order records and more than 150,000 Foster Car…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
28th September – Threat Intelligence Report Critical CVE-2026-85102 Check Point Research
2026-09-28 Check Point Research

28th September – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 28th September, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES The FBI has confirmed unauthorized activity affecting FBIjobs.gov after the ShinyHunters group defaced the website. The group claimed to have stolen employee and applicant information and shared samples of pu…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
AI Threat Landscape Digest: July–August 2026 Critical Check Point Research
2026-09-17 Check Point Research

AI Threat Landscape Digest: July–August 2026

The defining development of the period came not from attackers but from the AI labs themselves, whose models broke out of controlled evaluations and reached real systems. In the wild, the criminal and state use of AI continued to mature along the lines tracked in earlier editions: models now act as attack operators, an underground market supplies the access,…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
14th September – Threat Intelligence Report Critical CVE-2026-72898 Check Point Research
2026-09-14 Check Point Research

14th September – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 14th Setpember, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES IDScan.net, a US identity verification provider, has disclosed a data breach after detecting unauthorized access on September 1. Exposed data included names and government identification numbers, while a crim…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
7th September – Threat Intelligence Report Moderate CVE-2026-83548 Check Point Research
2026-09-07 Check Point Research

7th September – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 7th Setpember, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Thomson Reuters, a global information and technology company, has disclosed a breach of its C-Track court case-management platform affecting courts across 11 US states and Canada. An unauthorized party obtaine…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
31st August – Threat Intelligence Report Moderate CVE-2026-81578 Check Point Research
2026-08-31 Check Point Research

31st August – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 31st August, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Manchester Airports Group, the UK operator of Manchester, London Stansted, and East Midlands airports, has disclosed a cyberattack that exposed data belonging to about 8.7 million customers. The compromised info…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
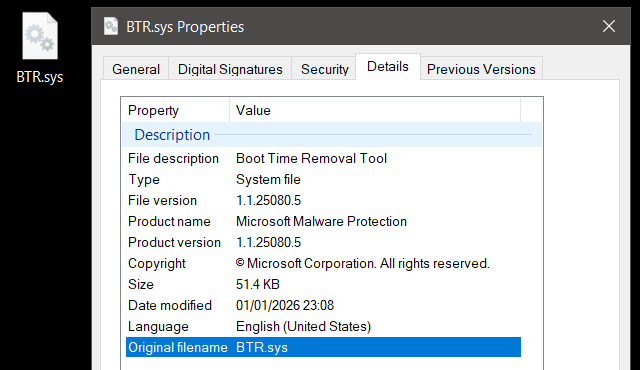
BTR Reforged: Weaponizing Defender’s Remediation Driver as a Kernel Operation Primitive Important Check Point Research
2026-08-20 Check Point Research

BTR Reforged: Weaponizing Defender’s Remediation Driver as a Kernel Operation Primitive

Research by: Jiří Vinopal ( @vinopaljiri ) Abstract What if a trusted security component could be repurposed into an attacker-controlled kernel primitive? What if a signed Microsoft remediation driver could be instructed to execute arbitrary file and registry operations from Ring 0 – without exploits, vulnerabilities, or memory corruption? In this publicatio…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
17th August – Threat Intelligence Report Critical CVE-2026-68820 Check Point Research
2026-08-17 Check Point Research

17th August – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 17th August, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Colombia’s Ministry of Justice has experienced a ransomware attack that affected part of its technology infrastructure and disrupted public services related to illicit-drug monitoring and legal processes. Offici…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Shattering the Dream – When a Job Offer Becomes a Zero-Day Attack Critical CVE-2026-68820 Check Point Research
2026-08-11 Check Point Research

Shattering the Dream – When a Job Offer Becomes a Zero-Day Attack

Key Points Check Point Research is tracking a long‑running campaign called Operation Dream Job , targeting organizations worldwide, with a particular focus on the defense sector. The campaign is affiliated to DPRK-linked Lazarus group and its latest wave focuses on the defense sector in Europe and India. In the latest variant of the Operation Dream Job campa…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
3rd August – Threat Intelligence Report Moderate CVE-2026-59726 Check Point Research
2026-08-03 Check Point Research

3rd August – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 27th July, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Minnesota IT Services has confirmed coordinated cyberattacks affecting more than 30 community water utilities across the state. The incidents briefly disrupted a treatment plant in Braham and affected industrial c…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification