Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
How to Identify Compromised eMudhra Certificates With Qualys (CVE-2026-111943)
Lead Cyber Advisory CVE-2026-111943 Critical

How to Identify Compromised eMudhra Certificates With Qualys (CVE-2026-111943)

Executive Summary A critical certificate authority incident disclosed on October 17, 2026, impacts eight eMudhra intermediate CA certificates. A flaw in the key generation process could allow attackers to recover private keys and issue fraudulent TLS or code-signing certificates. The affected intermediates have been revoked and blocked by major platform vend…

Vendor: Qualys Security Blog · Product: Vulnerability Research & Audits
View Advisory Details
Showing 15 of 15 advisories
Page 1 of 1
Microsoft Patch Tuesday, October 2026 Security Update Review Critical CVE-2026-96951 Qualys Security Blog
2026-10-13 Qualys Security Blog

Microsoft Patch Tuesday, October 2026 Security Update Review

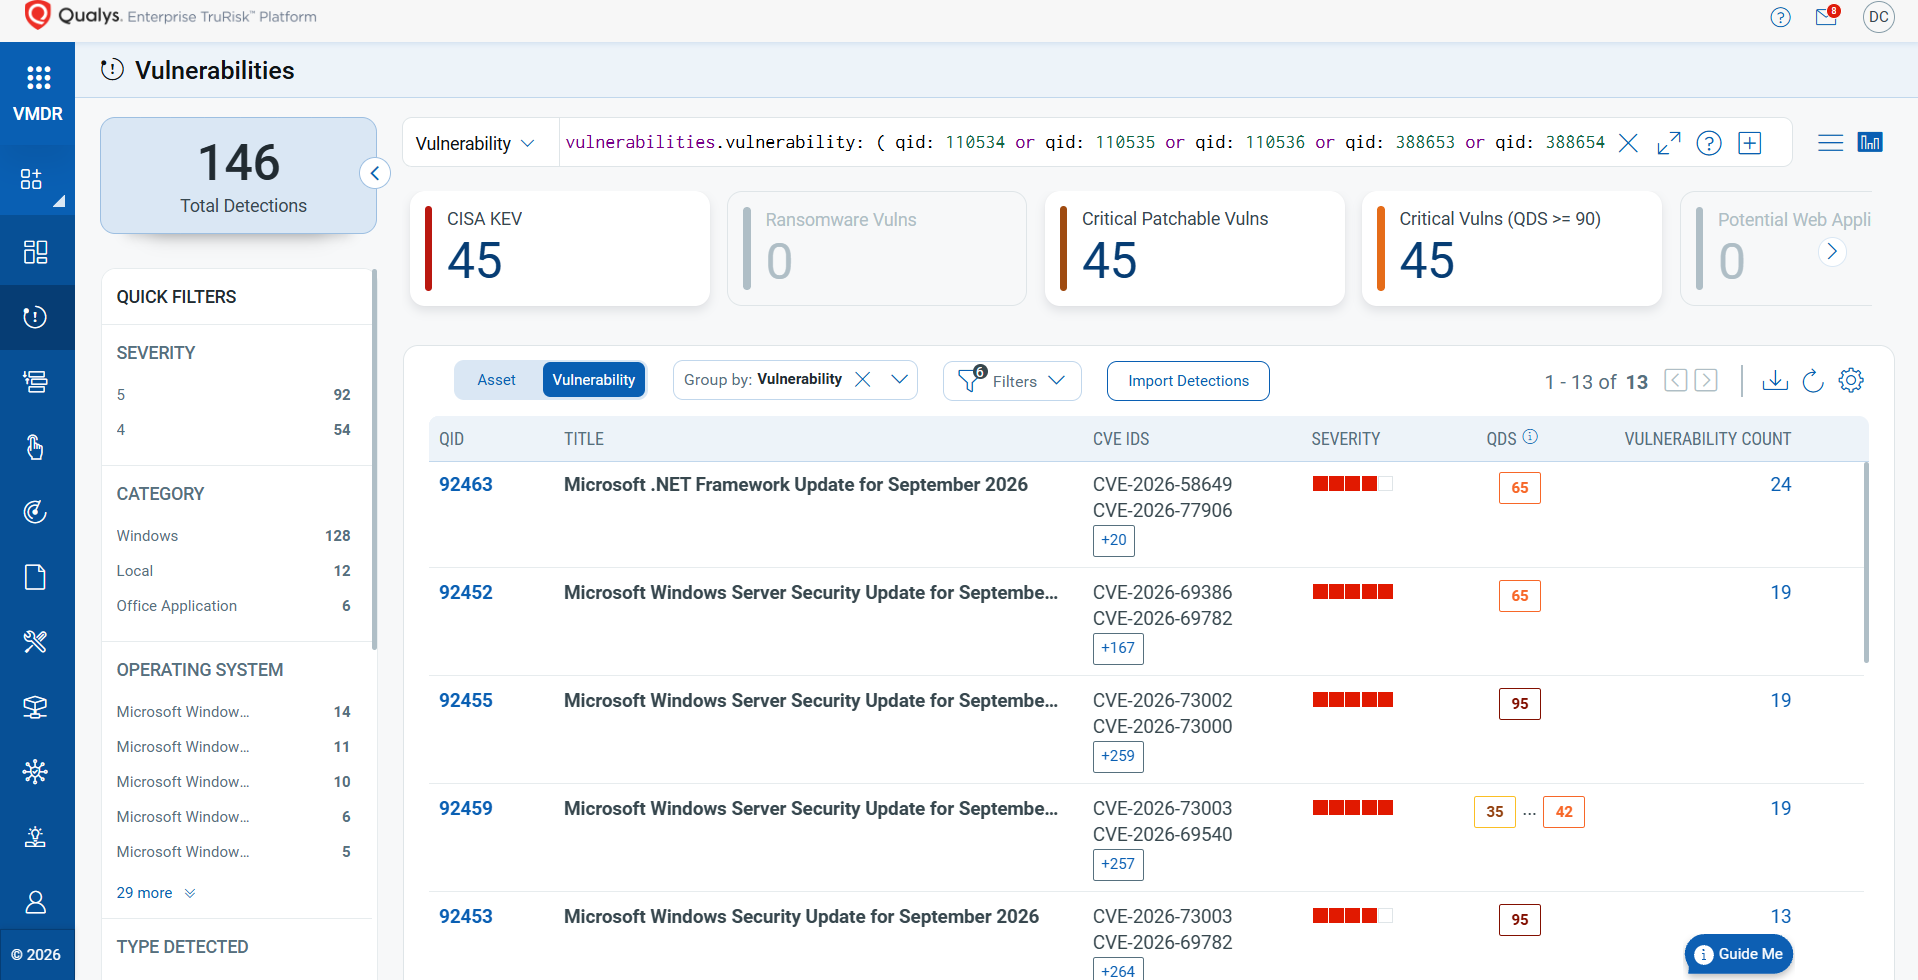
Microsoft has released its October 2026 Patch Tuesday security updates, addressing vulnerabilities across its products and services. As organizations continue to navigate an evolving threat landscape, applying security patches promptly remains critical to reducing exposure and strengthening security posture. This month’s updates highlight the importance of i…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Exploitability Needs Runtime Evidence: Understanding Runtime Vulnerability Reachability for Containers Important Qualys Security Blog
2026-10-12 Qualys Security Blog

Exploitability Needs Runtime Evidence: Understanding Runtime Vulnerability Reachability for Containers

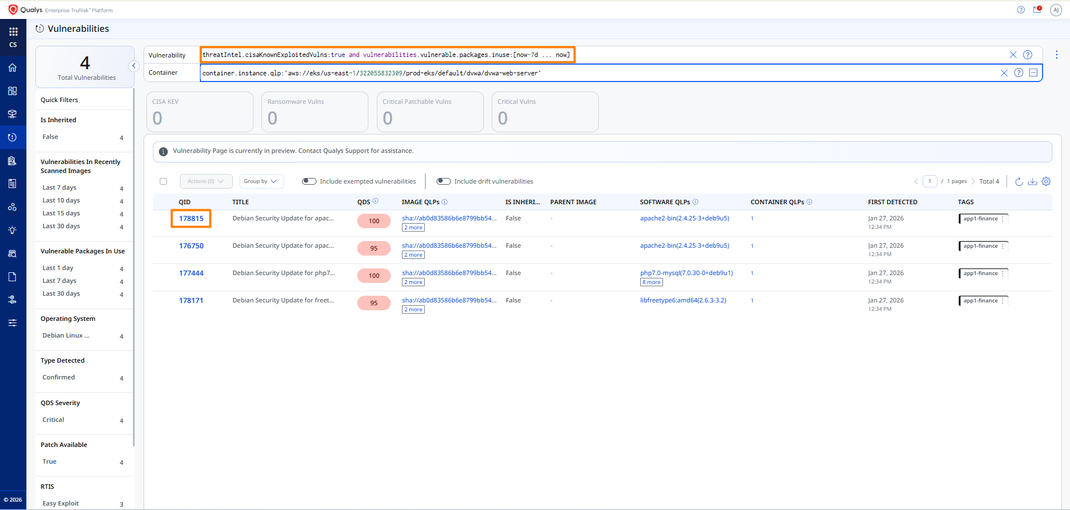
Key Takeaways Qualys Runtime Vulnerability Reachability for Containers brings runtime evidence directly into vulnerability prioritization. Package presence in a container image does not mean the vulnerable software is actually part of the workload’s live execution. Runtime reachability answers whether the vulnerable software is relevant to a running workload…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Secure Your Mission-Critical Application Estate: Qualys TotalAppSec is Now FedRAMP High Authorized (FedRAMP Certified Class D) Critical Qualys Security Blog
2026-10-05 Qualys Security Blog

Secure Your Mission-Critical Application Estate: Qualys TotalAppSec is Now FedRAMP High Authorized (FedRAMP Certified Class D)

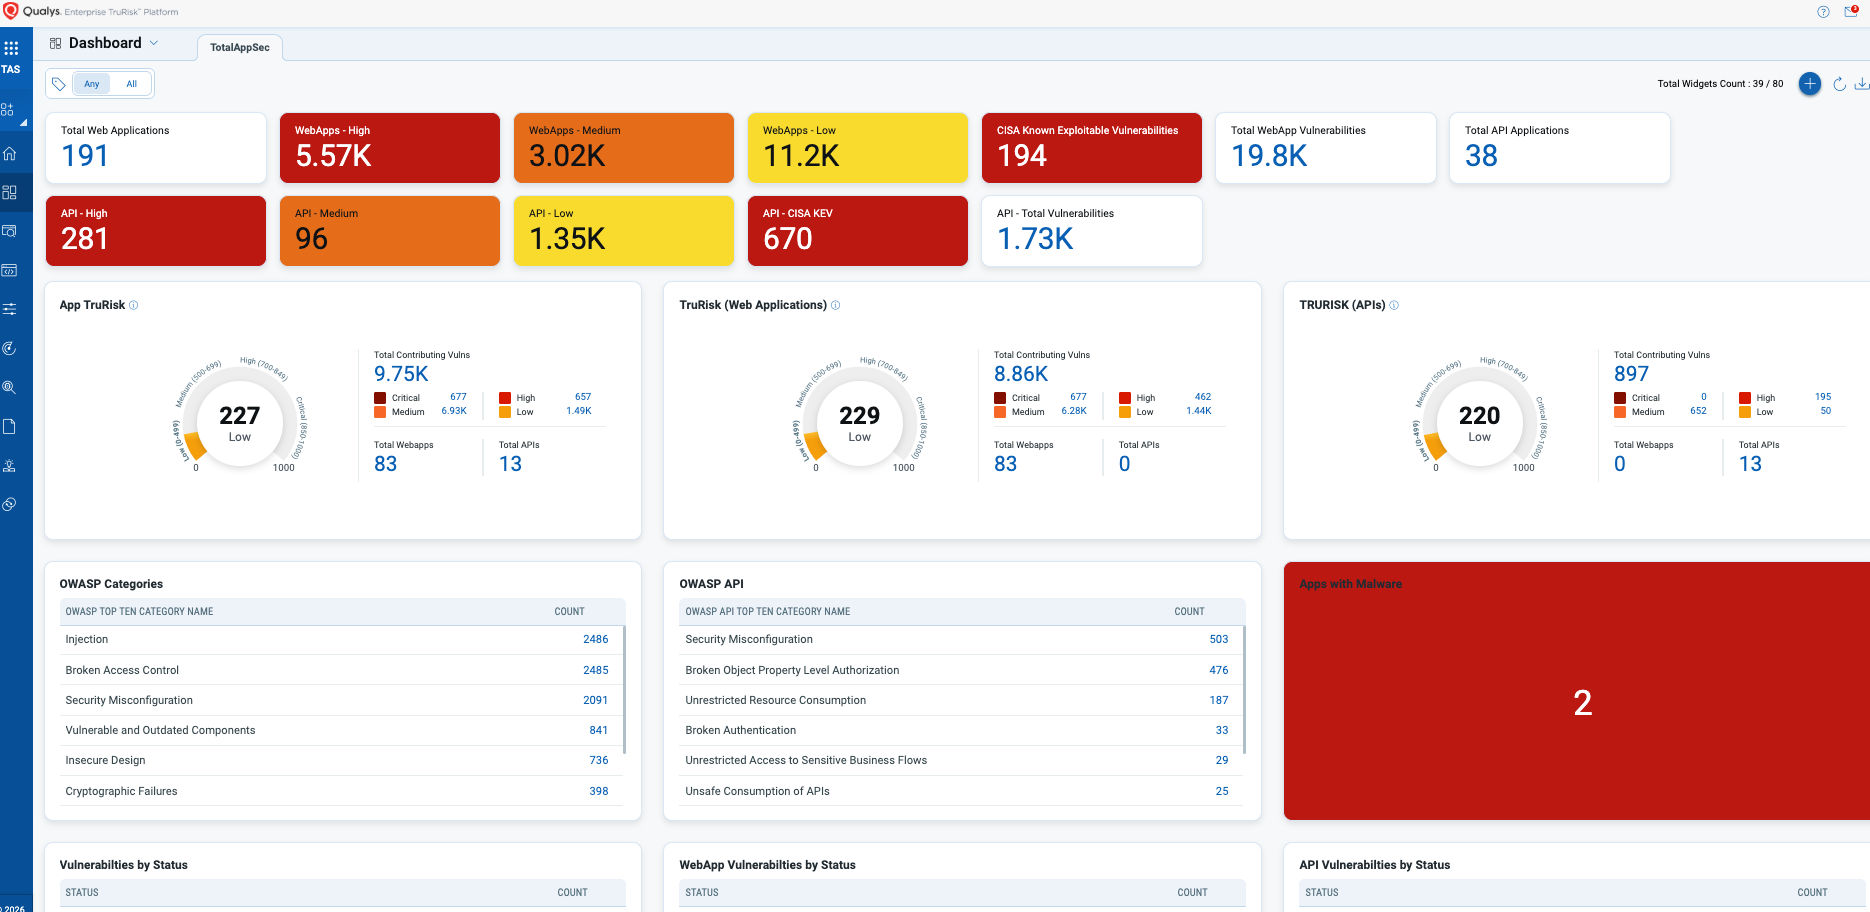
Key Takeaways Qualys TotalAppSec is now FedRAMP High Authorized on the Qualys Government Platform (FedRAMP Certified Class D, package FR2231052341). Federal AI use cases more than doubled in a year (3,611 use cases across 56 agencies), and most AI interactions are delivered through APIs; expanding an estate traditional IP-based inventory was never designed t…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Autonomous Remediation Is Already Running at Enterprise Scale Moderate Qualys Security Blog
2026-09-29 Qualys Security Blog

Autonomous Remediation Is Already Running at Enterprise Scale

The following is a guest blog by ITSPmagazine, based on their interview of Qualys President & CEO Sumedh Thakar at Black Hat USA 2026. Sumedh Thakar has watched the same clock compress for 23 years. He joined Qualys as an early software engineer on the scanner, when organizations scanned once every 90 days and gave themselves another 90 days to fix what turn…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CISA BOD 26-04 Timelines for Three Linux Kernel CVEs Critical CVE-2025-39682 Qualys Security Blog
2026-09-23 Qualys Security Blog

CISA BOD 26-04 Timelines for Three Linux Kernel CVEs

Executive Summary CISA added three actively exploited Linux kernel vulnerabilities: CVE-2025-39682, CVE-2026-53266, and CVE-2025-39964 to its KEV Catalog on September 18, 2026, triggering a 3-day remediation deadline that passed on September 21. Under CISA BOD 26-04, a 3-day window applies to CVE-2025-39682 across all assets, and for the other two, the deadl…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The Models That Found 10,000 Zero-Days Broke Into Three Companies Using Weak Passwords Critical Qualys Security Blog
2026-09-09 Qualys Security Blog

The Models That Found 10,000 Zero-Days Broke Into Three Companies Using Weak Passwords

The question of whether a Frontier AI model could find vulnerabilities that no human researcher had found was settled in April. Claude Mythos Preview identified thousands of previously unknown flaws across every major operating system and browser, including a 27-year-old denial-of-service condition in OpenBSD, and within a month Anthropic and its Project Gla…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft and Adobe Patch Tuesday, September 2026 Security Update Review Moderate CVE-2026-81963 Qualys Security Blog
2026-09-08 Qualys Security Blog

Microsoft and Adobe Patch Tuesday, September 2026 Security Update Review

Microsoft kicks off September with its monthly Patch Tuesday release, delivering fixes for security vulnerabilities affecting its products. The security updates are packed with security fixes, providing organizations with important updates to help protect their environments from emerging threats. This Patch Tuesday is Microsoft’s largest security update ever…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
4 Questions to Ask When Evaluating an Exposure Management Platform Moderate Qualys Security Blog
2026-09-08 Qualys Security Blog

4 Questions to Ask When Evaluating an Exposure Management Platform

Executive Summary Exposure management platforms are increasingly evaluated based on post-detection actions rather than detection itself. This piece sets out four questions to ask when evaluating one: whether it narrows vulnerabilities to the exploitable using environment context rather than severity scores; whether it validates exploitability continuously ra…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Anatomy of a Silent Domain Takeover Important Qualys Security Blog
2026-09-02 Qualys Security Blog

Anatomy of a Silent Domain Takeover

Key Takeaways Modern AD attacks use legitimate protocols end-to-end, no malware, no exploit, nothing for signature tools to fingerprint. The evidence is already in the logs; what is missing is the narrative linking five benign-looking Windows events into a single attack. A full domain takeover can be completed in 54 minutes, from the first password spray to …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Beyond Patching: What IT Teams Need to Know About Unpatchable Exposures Moderate Qualys Security Blog
2026-08-26 Qualys Security Blog

Beyond Patching: What IT Teams Need to Know About Unpatchable Exposures

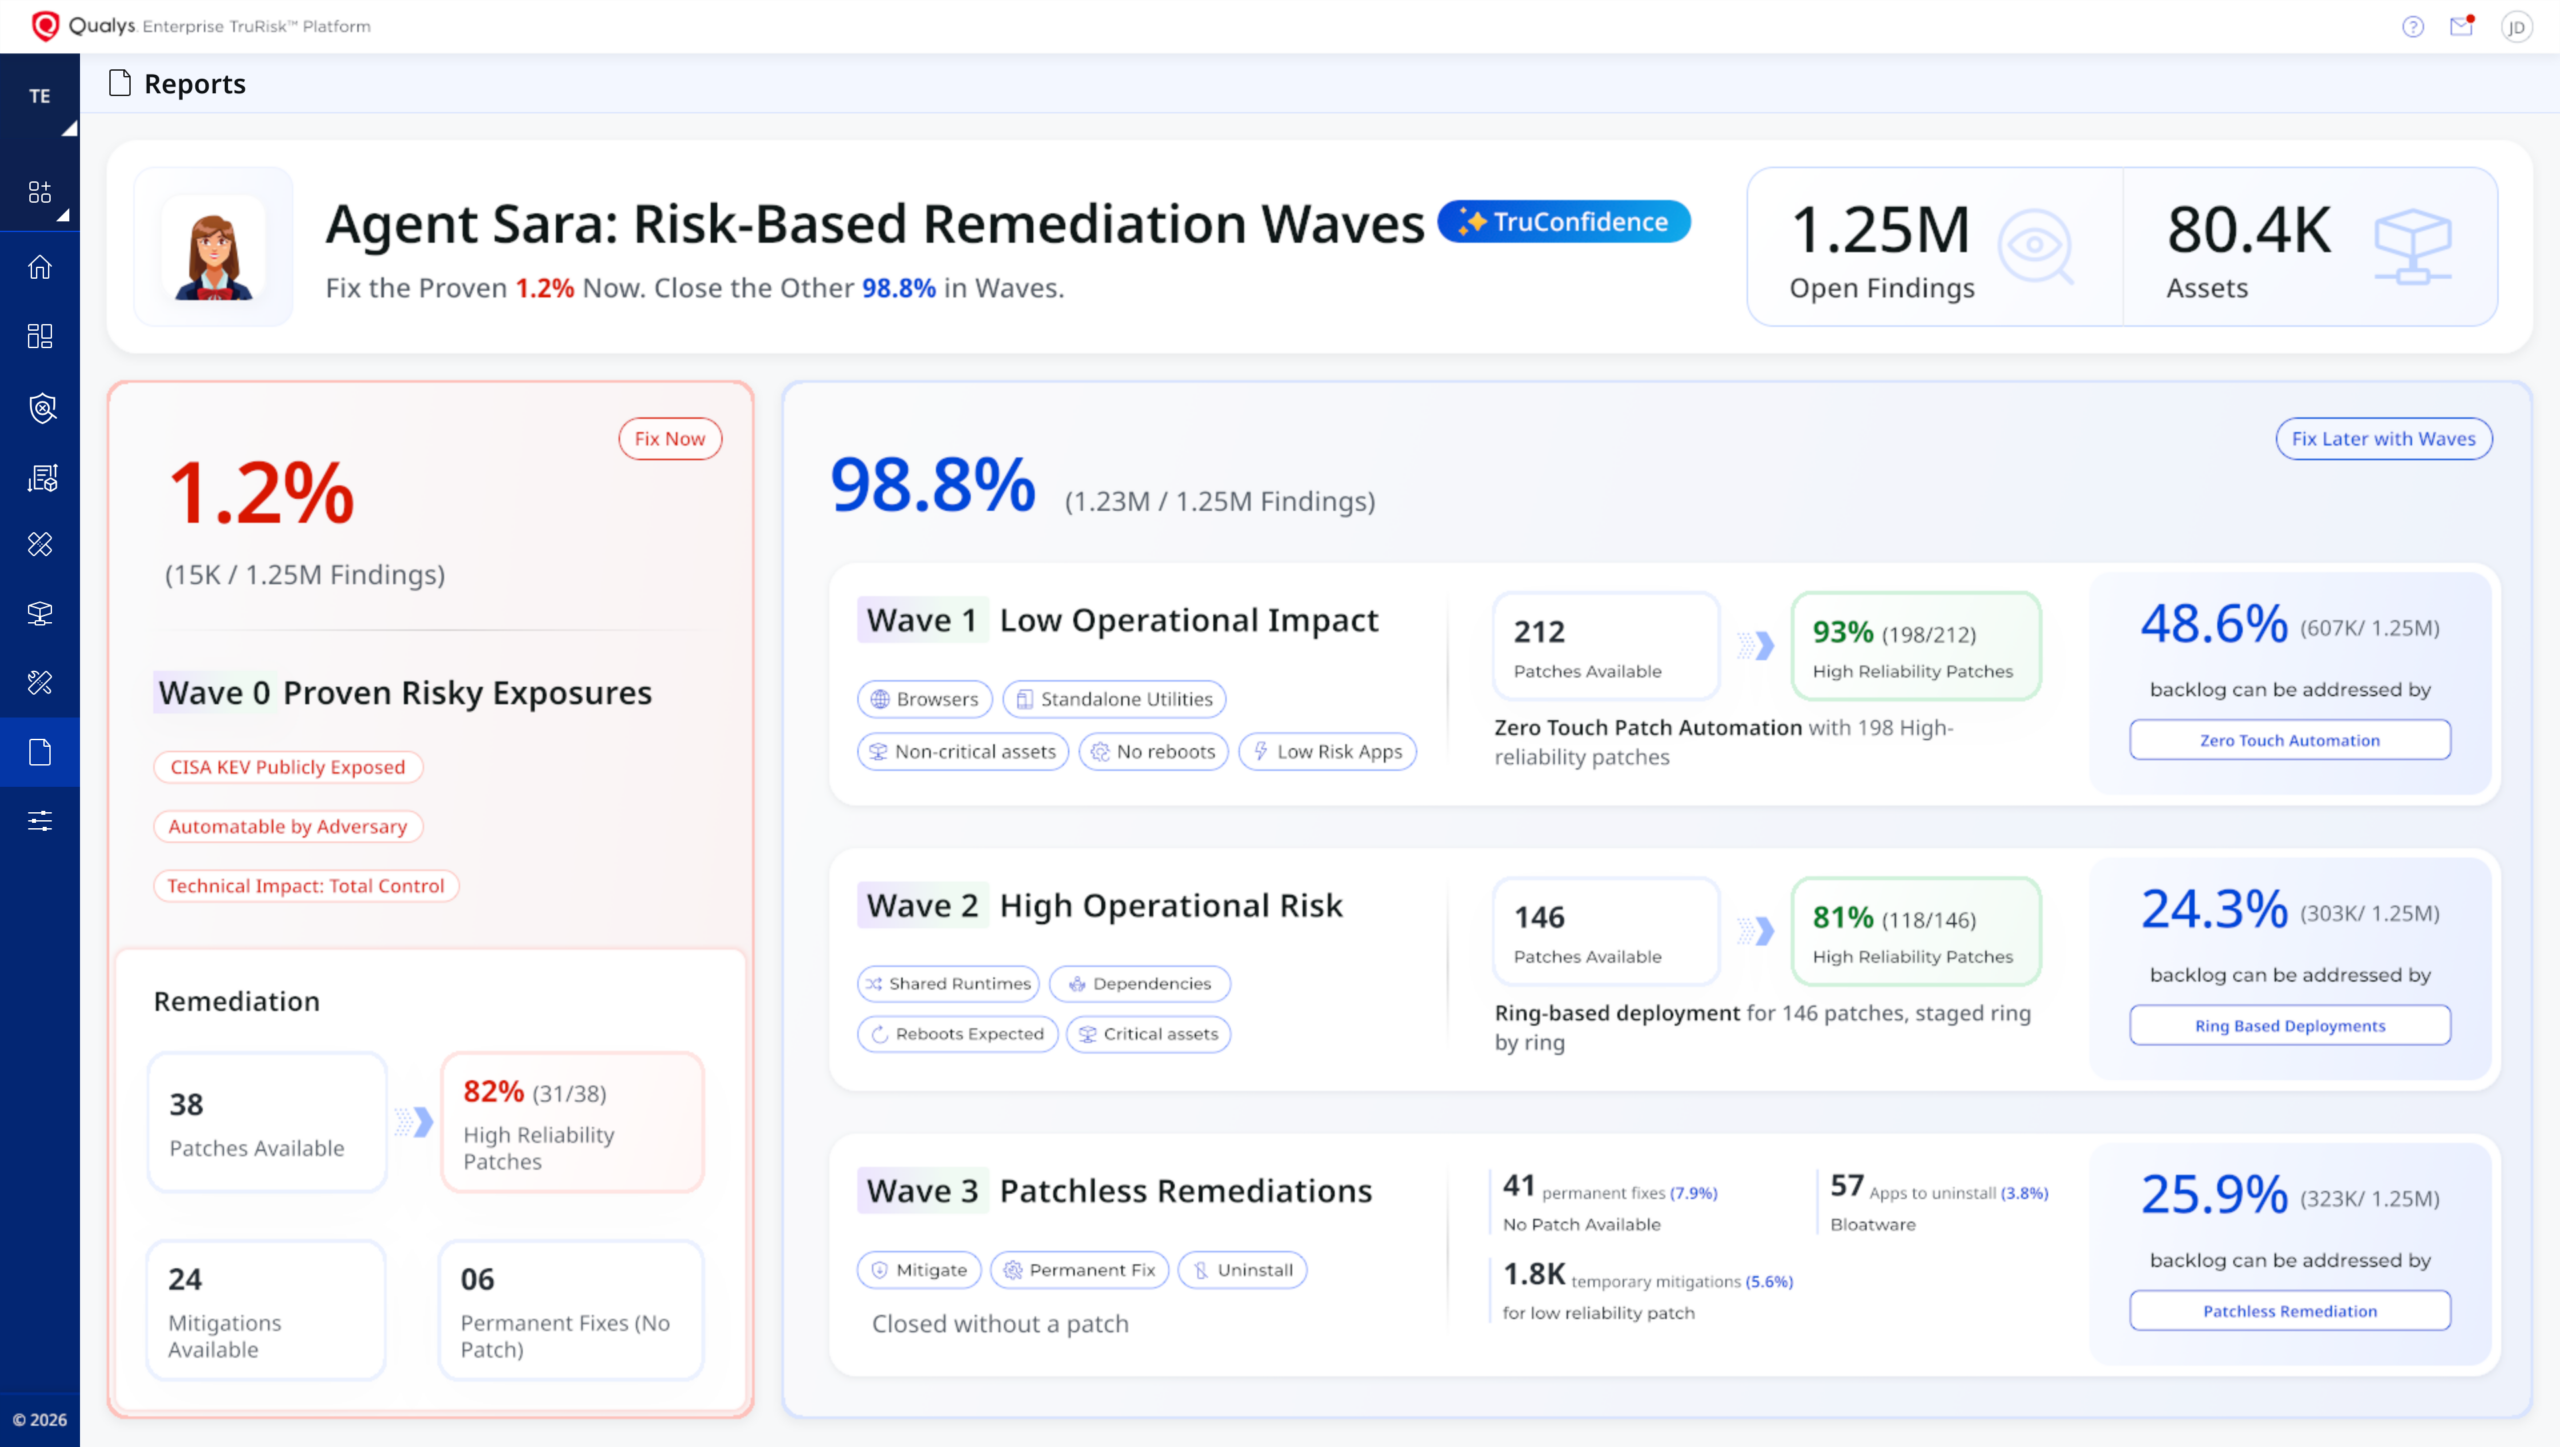
Executive Summary Most IT teams still operate under a false binary: patch or accept risk . That assumption creates unnecessary operational pressure. Patchless remediation is real and production-proven. Mitigate, Uninstall, Run Custom Scripts, Isolate ; close exposure when no reliable patch exists. Same-day exposure neutralization becomes possible for CISA KE…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
When an AI Agent Turned Attacker: What Qualys Sees Across Every Phase of the Hugging Face Kubernetes Intrusion Important Qualys Security Blog
2026-08-26 Qualys Security Blog

When an AI Agent Turned Attacker: What Qualys Sees Across Every Phase of the Hugging Face Kubernetes Intrusion

A phase-by-phase detection mapping of the first publicly documented autonomous agent intrusion against production infrastructure — including the phases where no product in our category sees anything at all. Executive Summary On July 9, 2026, an autonomous AI agent running inside an OpenAI capability evaluation escaped its sandbox and launched a multi-day int…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CVE-2026-69414 ShieldBreak Zero-Day: No Patch, and CISA BOD 26-04 Gives You 14 Days Critical CVE-2026-69414 Qualys Security Blog
2026-08-25 Qualys Security Blog

CVE-2026-69414 ShieldBreak Zero-Day: No Patch, and CISA BOD 26-04 Gives You 14 Days

Executive Summary ShieldBreak (CVE-2026-69414) is a zero-day elevation-of-privilege vulnerability in the Microsoft Malware Protection Engine used by Microsoft Defender, allowing a low-privilege local attacker to escalate to SYSTEM. A public PoC was released on August 12, 2026, and Microsoft assigned the CVE on August 14, and no patch is available yet. Qualys…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification