Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 5,807 advisories
Page 117 of 242
Times Car confirms data breach affecting 6.6 million user accounts Critical BleepingComputer
2026-09-28 BleepingComputer

Times Car confirms data breach affecting 6.6 million user accounts

Japanese car-sharing service Times Car has confirmed that approximately 6.6 million user accounts were compromised in a cyberattack disclosed late last week. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Carbonato Botnet Puts an AI Agent on Hacked Docker Hosts Important Dark Reading
2026-09-28 Dark Reading

Carbonato Botnet Puts an AI Agent on Hacked Docker Hosts

The botnet uses the open source Hermes Agent AI framework to execute commands via Telegram and steal AI API keys from exposed Docker hosts.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

AI Accounts Are Becoming the New Target for Infostealers Important SecurityAffairs
2026-09-28 SecurityAffairs

AI Accounts Are Becoming the New Target for Infostealers

Infostealers are exposing corporate AI accounts, sessions and API keys, giving attackers access to sensitive data, compute and connected systems. SOCRadar analyzed stealer log data from the last 90 days and found 482 companies with exposed AI accounts and credentials. Of those, 295 appeared in active logs during that period, suggesting the exposure is recent…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Dutch police confirm arrest in ShinyHunters hacking investigation Moderate BleepingComputer
2026-09-28 BleepingComputer

Dutch police confirm arrest in ShinyHunters hacking investigation

Dutch police have confirmed that a 24-year-old Amsterdam man arrested earlier this month was detained as part of an investigation into the ShinyHunters hacking group. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
ShinyHunters exploiting workarounds for Oracle PeopleSoft bug, Mandiant warns Important The Record by Recorded Future
2026-09-28 The Record by Recorded Future

ShinyHunters exploiting workarounds for Oracle PeopleSoft bug, Mandiant warns

A vulnerability in a popular line of products from Oracle is being used in a new campaign by the prolific ShinyHunters hacking group, which recently claimed credit for an attack on the FBI’s jobs site.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Apple Patches CoreGraphics Flaw Possibly Exploited in Targeted Attacks Critical CVE-2026-86950 The Hacker News
2026-09-29 The Hacker News

Apple Patches CoreGraphics Flaw Possibly Exploited in Targeted Attacks

Apple has released security updates to address a vulnerability in older versions of iOS, iPadOS, and macOS that it said may have been exploited in targeted attacks. The vulnerability, tracked as CVE-2026-86950, refers to an out-of-bounds write impacting the CoreGraphics component that could lead to arbitrary code execution when processing a maliciously craft…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
How we found 24 Android vulnerabilities using our open source AI security agent Critical GitHub Security Blog
2026-09-28 GitHub Security Blog

How we found 24 Android vulnerabilities using our open source AI security agent

With the rise of AI in the security space, our team created the GitHub Security Lab Taskflow Agent as a way for security researchers to easily automate, package, and share the AI prompts and workflows that they find effective for their work. In this blog post, I’ll share how I created auditing taskflows to find vulnerabilities in Android applications. While …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Over 16,000 Supabase databases expose PII, passwords, auth tokens Moderate BleepingComputer
2026-09-28 BleepingComputer

Over 16,000 Supabase databases expose PII, passwords, auth tokens

Researchers found more than 16,000 misconfigured Supabase databases exposing readable tables with personally identifiable information, passwords, or authentication tokens. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
AI Agents Are Privileged Users; Who Is Auditing Their Access? Moderate Dark Reading
2026-09-28 Dark Reading

AI Agents Are Privileged Users; Who Is Auditing Their Access?

Enterprises regularly rigorously monitor human employees, while autonomous AI agents quietly operate with broad privileges that could turn them into the next generation of insider threats.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Hackers Use NeedyMantis to Maintain Long-Term Access in Breached Networks Critical The Hacker News
2026-09-29 The Hacker News

Hackers Use NeedyMantis to Maintain Long-Term Access in Breached Networks

Hackers have used a malware family called NeedyMantis to maintain long-term access to networks they had already breached, Microsoft said in a technical analysis. The malware has been seen in a small number of targeted intrusions at telecommunications organizations, universities, medical nonprofits, intergovernmental organizations, and government contractors.…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
IAM for AI agents: A Practical Enterprise Framework Moderate The Hacker News
2026-09-28 The Hacker News

IAM for AI agents: A Practical Enterprise Framework

What is IAM for AI agents? AI agents authenticate, invoke tools, and act across enterprise systems with delegated authority. IAM for AI Agents is the identity-control architecture that governs those actors. This guide covers the limits of conventional provisioning, the components that matter, how to evaluate framework choices, and what runtime evidence prove…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Bitget Says Attacker Exploited Third-Party Security Product Flaw to Steal $388M Important The Hacker News
2026-09-28 The Hacker News

Bitget Says Attacker Exploited Third-Party Security Product Flaw to Steal $388M

The attacker who stole about $388 million from the cryptocurrency exchange Bitget gained access through a vulnerability in a third-party security product the exchange used, Bitget said on Monday. The attacker exploited the flaw to obtain high-level internal credentials and then, on September 24, used them to send fraudulent withdrawal commands to Bitget's wa…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
RatHat Android Malware Console Uses Gemini to Identify Higher-Value Victims Important The Hacker News
2026-09-28 The Hacker News

RatHat Android Malware Console Uses Gemini to Identify Higher-Value Victims

RatHat's operators build and publish the Android banking trojan and control infected phones from a web console, according to security company Cleafy. Cleafy has traced nearly 100 deployments of that console since April 2026. It said this fits a malware-as-a-service model, in which each customer runs a separate copy. The console stores what the malware collec…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
US, UK warn of exploited Citrix NetScaler zero-day bugs Critical The Record by Recorded Future
2026-09-28 The Record by Recorded Future

US, UK warn of exploited Citrix NetScaler zero-day bugs

Incident responders began warning of potential vulnerabilities in NetScaler Gateway products on Saturday before cybersecurity agencies in the Netherlands, U.S. and U.K. released advisories on Sunday confirming vulnerabilities. Citrix itself confirmed eight new vulnerabilities.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
JadePuffer agentic AI attacks target Azure, destroy cloud resources Critical BleepingComputer
2026-09-28 BleepingComputer

JadePuffer agentic AI attacks target Azure, destroy cloud resources

The JadePuffer ransomware operator is targeting Azure tenants with agent-driven attacks that conduct reconnaissance, steal credentials, and destroy core components. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The Developer is the New Perimeter: How Supply Chain Attacks Are Becoming Cloud Breaches Critical Qualys Security Blog
2026-09-28 Qualys Security Blog

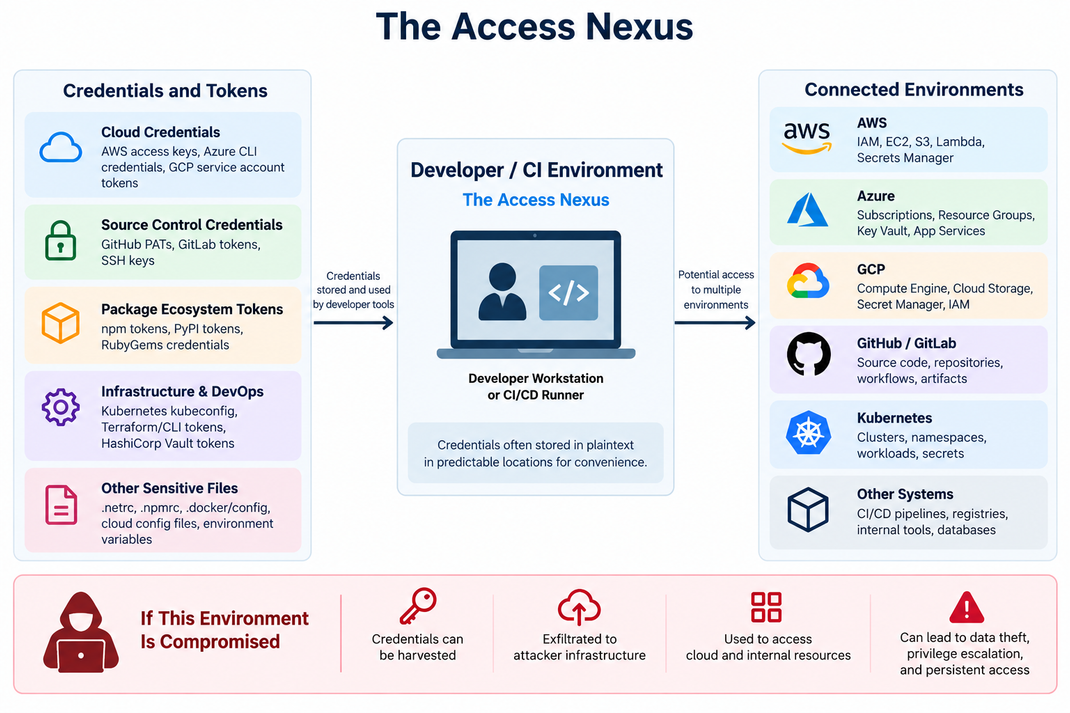
The Developer is the New Perimeter: How Supply Chain Attacks Are Becoming Cloud Breaches

Key Takeaways Malicious packages can steal cloud credentials during installation, before applications run. Stolen credentials turn developer workstations and CI/CD pipelines into gateways to cloud resources. Restrict installation scripts, minimize credential privileges, protect metadata access, and monitor cloud activity. Containment requires revoking expose…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Nearly 400,000 Medicaid Beneficiaries Caught in Medicaid and DC Healthcare Alliance Data Exposure Moderate SecurityAffairs
2026-09-28 SecurityAffairs

Nearly 400,000 Medicaid Beneficiaries Caught in Medicaid and DC Healthcare Alliance Data Exposure

Nearly 400,000 DC Medicaid and Healthcare Alliance beneficiaries may have had personal data exposed through reports published on a public website. The District of Columbia Department of Health Care Finance is notifying nearly 400,000 Medicaid and DC Healthcare Alliance beneficiaries that their personal information may have been exposed. The incident affects …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
⚡ Weekly Recap: $387M Crypto Hack, Citrix Exploits, AI Agents Go Off-Script, and More Threats Important The Hacker News
2026-09-28 The Hacker News

⚡ Weekly Recap: $387M Crypto Hack, Citrix Exploits, AI Agents Go Off-Script, and More Threats

A domain used as harmless placeholder text showed up in roughly 1,700 repositories. Then somebody registered it and started serving malicious lures. That is the kind of week this was: forgotten assumptions turning into live attack surface. Elsewhere, weak service accounts, old bugs, exposed systems, phishing kits, and strangely easy exploit paths kept doing …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
80,000+ Organizations Had AI Logins Stolen: From Shadow AI to LLMjacking Moderate BleepingComputer
2026-09-28 BleepingComputer

80,000+ Organizations Had AI Logins Stolen: From Shadow AI to LLMjacking

Infostealer logs exposed AI account credentials and sessions tied to more than 80,000 corporate domains, creating risks ranging from stolen conversations to LLMjacking. SOCRadar examines the growing market for stolen AI logins and how organizations can identify their exposure. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification