Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 5,807 advisories
Page 128 of 242
Ryuk Member Karen Vardanyan Sentenced to Two Years in U.S. Prison Moderate SecurityAffairs
2026-09-24 SecurityAffairs

Ryuk Member Karen Vardanyan Sentenced to Two Years in U.S. Prison

Ryuk member Karen Vardanyan was sentenced to 24 months in U.S. prison after extradition from Ukraine and ordered to pay $1.2M in restitution. Karen Vardanyan , a 35-year-old Armenian citizen who went by “Maneeken” and, oddly, “Karl Lagerfeld” online, was extradited from Ukraine and sentenced to 24 months in federal prison plus three years of supervised relea…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
SectopRAT Returns, Hiding Inside a Legitimate Application Moderate Dark Reading
2026-09-24 Dark Reading

SectopRAT Returns, Hiding Inside a Legitimate Application

The latest activity from the remote access Trojan (RAT) shows why organizations should monitor the behavior of applications rather than blindly trusting them, experts say.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Digital forensics firm with US federal contracts covered up ties to Russia, DOJ alleges Moderate The Record by Recorded Future
2026-09-24 The Record by Recorded Future

Digital forensics firm with US federal contracts covered up ties to Russia, DOJ alleges

Two executives at a data extraction and digital forensics company that sold several U.S. agencies its software were arrested for allegedly lying about the fact that its technology is made in Russia.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Lawmakers introduce bill for voluntary telecom cyber rules after Salt Typhoon hacks Moderate The Record by Recorded Future
2026-09-24 The Record by Recorded Future

Lawmakers introduce bill for voluntary telecom cyber rules after Salt Typhoon hacks

U.S. Sens. Mark Warner (D-VA) and Ted Cruz (R-TX) introduced the Telecommunications Cybersecurity and Resilience Act on Thursday, arguing that the new effort was necessary in light of the Salt Typhoon attacks which saw Chinese hackers breach nearly all of the major telecommunications giants in the U.S.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
New Carbonato malware uses AI agents to hijack exposed Docker hosts Important BleepingComputer
2026-09-24 BleepingComputer

New Carbonato malware uses AI agents to hijack exposed Docker hosts

A new botnet malware called Carbonato is targeting insecure hosts running Docker daemons to install the Hermes Agent AI framework and take control. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Rydox cybercriminal marketplace operator pleads guilty following co-conspirator brothers’s deportation Moderate The Record by Recorded Future
2026-09-24 The Record by Recorded Future

Rydox cybercriminal marketplace operator pleads guilty following co-conspirator brothers’s deportation

Ardit Kutleshi, 28, was extradited from his home country of Kosovo last year after prosecutors accused him and his older brother of running Rydox — an illicit platform used by cybercriminals to sell stolen personal information, illegal access to devices and other tools for carrying out fraud.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
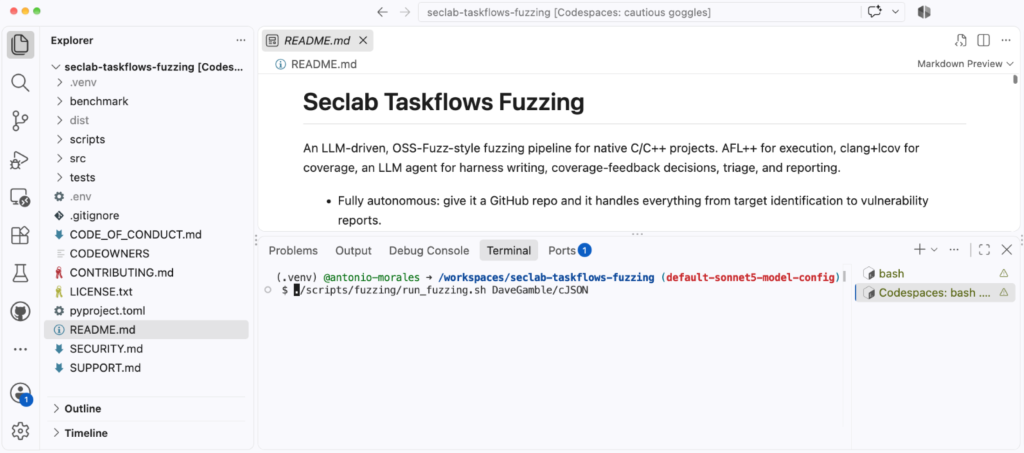
AI-powered fuzzing with the GitHub Security Lab Taskflow Agent Moderate GitHub Security Blog
2026-09-24 GitHub Security Blog

AI-powered fuzzing with the GitHub Security Lab Taskflow Agent

If you’re new to fuzzing and want to learn the fundamentals first, check out our Fuzzing 101 course at gh.io/fuzzing101 . Continuous fuzzing is not a magic solution that solves all your problems . Even projects that have been enrolled in OSS-Fuzz for years can still hide critical bugs, and the reason is almost always the same: someone needs to keep an eye on…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
AI Helps Uncover MikroTrick Attack Chain in MikroTik RouterOS Important CVE-2026-86060 SecurityAffairs
2026-09-24 SecurityAffairs

AI Helps Uncover MikroTrick Attack Chain in MikroTik RouterOS

MikroTrick chains two RouterOS flaws to bypass authentication and gain admin access. AI helped researchers uncover the attack chain within days. MikroTik pushed out patches on September 3, 2026 for several RouterOS issues at once, calling it an important security update without saying what it actually fixed. That silence was deliberate, and it didn’t last lo…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Unpatched OnePlus Flaws Let Installed Android Apps Gain Root Without Permissions Important The Hacker News
2026-09-24 The Hacker News

Unpatched OnePlus Flaws Let Installed Android Apps Gain Root Without Permissions

A OnePlus 15 running the latest OxygenOS can be rooted by a malicious app the owner installs, one that asks for no special permissions. A researcher, Rasmus Moorats, chained two flaws in OnePlus's own software to gain root access, the highest level of control over an Android phone. OnePlus told him the same flaws affect many more of its own devices and those…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Trust and the enticing consultancy offer Moderate Cisco Talos Intelligence
2026-09-24 Cisco Talos Intelligence

Trust and the enticing consultancy offer

Welcome to this week’s edition of the Threat Source newsletter. In the cybersecurity industry, trust is the invisible currency. Every practitioner carries the implicit trust not to abuse privileged access or knowledge of vulnerabilities in each employment or engagement. This trust is valued by those who require our services, but also by threat actors. Clumsy…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
ThreatsDay: AI Search Poisoning, AI Coding Tool Leaking Repos, One-Click Code Execution and 13 More Stories Moderate The Hacker News
2026-09-24 The Hacker News

ThreatsDay: AI Search Poisoning, AI Coding Tool Leaking Repos, One-Click Code Execution and 13 More Stories

This week, the dangerous stuff keeps arriving dressed as something boring. An update. A login box. A search answer. A coding tool. A link you have clicked a hundred times before. That is the thread running through the pile. Trusted paths get poisoned. Old bugs find new jobs. AI tools leak more than expected. Fake prompts look real enough. And some attacks ba…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Exposed GitLab project email addresses let attackers push code Important BleepingComputer
2026-09-24 BleepingComputer

Exposed GitLab project email addresses let attackers push code

Private GitLab email addresses that allow developers to push issues or tasks to a project are being deliberately exposed in READMEs, contributing guides, and support pages used to collect bug reports. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Placeholder third-party[.]com Referenced Across 1,700+ Repositories Now Serves Malicious Content Moderate The Hacker News
2026-09-24 The Hacker News

Placeholder third-party[.]com Referenced Across 1,700+ Repositories Now Serves Malicious Content

The "third-party[.]com" domain, commonly used as a documentation placeholder, has been observed serving a ClickFix lure to Windows browsers while displaying a harmless decoy to other users. "third-party[.]com has been a generic documentation placeholder for years, the same role example.com plays," Manifold Security's Head of Research, Ax Sharma, said. "Unlik…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
How Cloudflare addressed a cross-tenant data exposure vulnerability in Containers Important Cloudflare Security
2026-09-24 Cloudflare Security

How Cloudflare addressed a cross-tenant data exposure vulnerability in Containers

On September 4, 2026, Oren Yomtov, a security researcher from Accomplish , responsibly reported a vulnerability affecting Cloudflare Containers and Cloudflare Sandboxes (which is built on Containers), through Cloudflare’s bug bounty program . Cloudflare has fully remediated the vulnerability, and we have no evidence that customer data has been compromised. T…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
3 Cyber Threats That Defined the Summer of 2026 Critical Dark Reading
2026-09-24 Dark Reading

3 Cyber Threats That Defined the Summer of 2026

This installment of the Reporters' Notebook video series discusses the impact of AI agents breaching Hugging Face, Fairlife's ransomware attack, and Iranian-linked threat actors compromising a dozen US water systems. It was a busy summer.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Hacked Ukrainian Sites Serve Fake Cloudflare ClickFix Lures for Psychedelic Stealer Moderate The Hacker News
2026-09-24 The Hacker News

Hacked Ukrainian Sites Serve Fake Cloudflare ClickFix Lures for Psychedelic Stealer

An active ClickFix campaign has been observed compromising legitimate Ukrainian business websites to inject bogus Cloudflare verification pages and trick victims into downloading a previously undocumented information stealer called Psychedelic. "When a visitor interacts with the page, the lure copies a Windows Installer command to the clipboard and instructs…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
How to Build a SASE Framework for Modern Cybersecurity Moderate Dark Reading
2026-09-24 Dark Reading

How to Build a SASE Framework for Modern Cybersecurity

Securing edge computing requires organizations to fundamentally rethink security governance. This step-by-step guide to building a SASE framework provides the path forward. (Third in a three-part series.)

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
FedRAMP VDR & VER: Daily Scans Are Only the Beginning Moderate BleepingComputer
2026-09-24 BleepingComputer

FedRAMP VDR & VER: Daily Scans Are Only the Beginning

FedRAMP's new VDR and VER requirements make vulnerability management more continuous, with faster scanning, tighter remediation deadlines, and stronger evidence requirements. Anecdotes explains why the December 7 deadline is just the beginning of a broader shift toward continuous, automated compliance validation. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification