Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 5,807 advisories
Page 150 of 242
CVE-2026-56176 Windows Win32k Elevation of Privilege Vulnerability Important CVE-2026-56176 Microsoft MSRC
2026-09-17 Microsoft MSRC

CVE-2026-56176 Windows Win32k Elevation of Privilege Vulnerability

Added Office software to the Security Updates table. Customers that are running supported version of Office are encouraged to update to the indicated version to be protected from this vulnerability.

Fix: Deploy cumulative update via Windows Update or Microsoft Update Catalog.
CVE-2026-55946 Microsoft Copilot Information Disclosure Vulnerability Moderate CVE-2026-55946 Microsoft MSRC
2026-09-17 Microsoft MSRC

CVE-2026-55946 Microsoft Copilot Information Disclosure Vulnerability

Improper neutralization of special elements used in a command ('command injection') in Microsoft Copilot allows an unauthorized attacker to disclose information over a network.

Fix: Deploy cumulative update via Windows Update or Microsoft Update Catalog.
Hackers claim breach of Russian election systems days before parliamentary vote Critical The Record by Recorded Future
2026-09-17 The Record by Recorded Future

Hackers claim breach of Russian election systems days before parliamentary vote

An anonymous hacking group claimed to have broken into computer systems connected to Russia’s election infrastructure just days before the country begins voting for a new parliament.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Congress eyes new support for Cyber Command after recent suicide deaths Moderate The Record by Recorded Future
2026-09-17 The Record by Recorded Future

Congress eyes new support for Cyber Command after recent suicide deaths

Congressional sources say they view the deaths of U.S. Cyber Command personnel as an inflection point, especially as the Pentagon’s appetite for cyber capabilities grows following successful contributions to high-profile missions against Iran and Venezuela.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Iranian strikes on AWS facilities left customer data beyond recovery in Bahrain, UAE Moderate Help Net Security
2026-09-17 Help Net Security

Iranian strikes on AWS facilities left customer data beyond recovery in Bahrain, UAE

Six months after Iranian drone strikes tore through its Middle East infrastructure, Amazon Web Services (AWS) has acknowledged the permanent loss of customer data in Bahrain and the UAE. In two updates posted September 15, AWS said it can no longer recover customer data and resources stored in its Middle East (Bahrain) region, known as me-south-1, or in one …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Windows 11 24H2 Home and Pro reach end of support in October Moderate BleepingComputer
2026-09-17 BleepingComputer

Windows 11 24H2 Home and Pro reach end of support in October

Microsoft reminded customers this week that devices running Windows 11 24H2 Home and Pro editions will stop receiving updates next month. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
A fake ChatGPT billing email is after your OpenAI password Moderate Help Net Security
2026-09-17 Help Net Security

A fake ChatGPT billing email is after your OpenAI password

A fake ChatGPT billing email is steering users to a copy of the OpenAI login page that keeps whatever username and password they type. Josh Varden of Cofense’s Phishing Defense Center traced the email’s payment button through a Google redirect to the attacker’s page. The lure targets ChatGPT users on work and personal accounts alike, and it copies the kind o…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The Odyssey and Trojans again: MovieReaper attacks users in multiple countries through compromised torrents Important Kaspersky Securelist
2026-09-17 Kaspersky Securelist

The Odyssey and Trojans again: MovieReaper attacks users in multiple countries through compromised torrents

Introduction Torrent trackers have long been abused for distributing malicious software, disguised as popular films, games, and other content. Our previous research has shown that cybercriminals repeatedly turn to torrents as an initial infection vector, using trojanized cracks and installers to reach a large number of users. Installation guides for pirated …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Download: The IT leader’s guide to AI code sprawl Moderate Help Net Security
2026-09-17 Help Net Security

Download: The IT leader’s guide to AI code sprawl

AI hasn’t just made building faster, it’s made everyone a builder. Across every department, employees are shipping apps, agents and automations using AI tools, often without knowing they’ve created something that needs governing at all. The result: AI code sprawl is taking root, increasing risk, compromising compliance, and wasting resources. The usual respo…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CISA wants critical infrastructure orgs and smaller security teams to start using cyber decoys Critical Help Net Security
2026-09-17 Help Net Security

CISA wants critical infrastructure orgs and smaller security teams to start using cyber decoys

Cyber deception has long been the domain of well-resourced security teams, but CISA’s latest guidance, titled “Using Cyber Decoys to Strengthen Detection and Response”, is an attempt to try and change that. Why decoys, and why now The core problem CISA is attempting to address is that many organizations are incapable of detecting adversaries who use legitima…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Critical Unbound DNSSEC Validator Flaw Could Allow RCE via a Malicious DNS Zone Critical CVE-2026-81642 The Hacker News
2026-09-17 The Hacker News

Critical Unbound DNSSEC Validator Flaw Could Allow RCE via a Malicious DNS Zone

Every release of the Unbound DNS resolver before 1.26.1 has a critical heap overflow in its DNSSEC validator, maintainer NLnet Labs said in an advisory on Wednesday. An attacker who controls a malicious zone and queries a vulnerable resolver can trigger it, enabling remote code execution. Unbound 1.26.1, released the same day, fixes the bug, tracked as CVE-2…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Druva expands identity resilience with ransomware detection Critical Help Net Security
2026-09-17 Help Net Security

Druva expands identity resilience with ransomware detection

Druva has announced new capabilities for Druva Identity Resilience alongside the launch of Ransomware Detection, a new feature fueled by a proprietary AI threat pipeline. Powered by Dru MetaGraph, the new offerings use behavioral intelligence and built-in validation to turn suspicious behavior into actionable evidence, definitively confirm impact, and accele…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
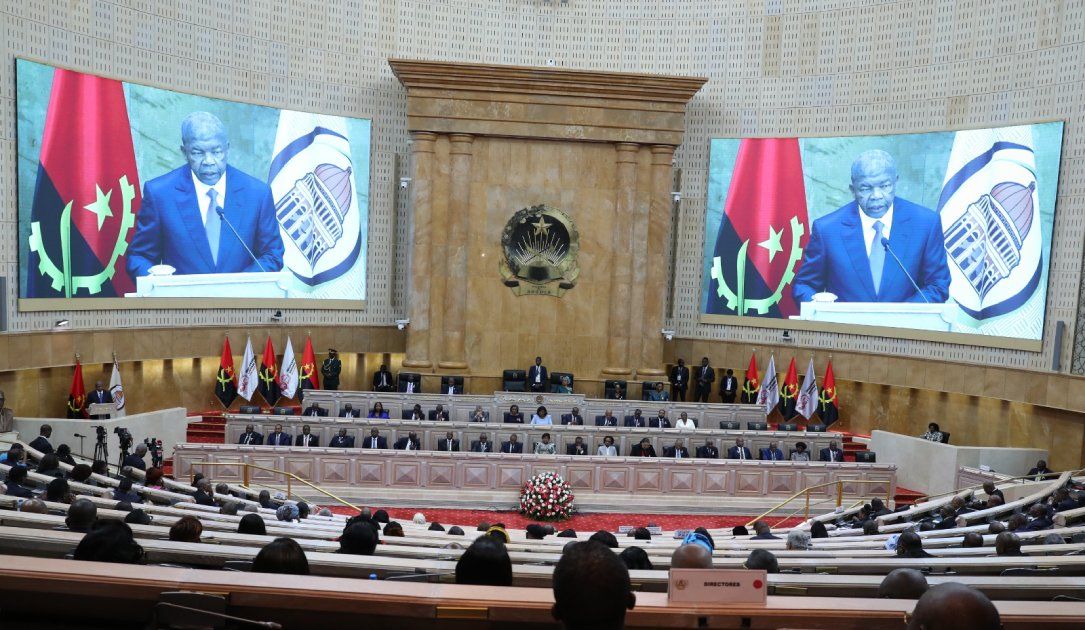
Israeli contractor BlackCore trained Angolan officials in online influence operations Moderate The Record by Recorded Future
2026-09-17 The Record by Recorded Future

Israeli contractor BlackCore trained Angolan officials in online influence operations

An Israeli influence-for-hire company trained Angolan government officials to run online influence operations, including by creating fake social media personas and media outlets, researchers found.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Schneider Electric NetBotz 5 750/755 Important CISA Advisory
2026-09-17 CISA Advisory

Schneider Electric NetBotz 5 750/755

View CSAF Summary Schneider Electric is aware of multiple vulnerabilities in its NetBotz 5 – 750/755 products.The NetBotz 5 – 750/755 products are security and environmental monitors providing temperature, humidity, leak, smoke, vibration, door contact, and video monitoring capabilities. Failure to apply the remediation provided below may risk arbitrary or remote code execution over the local network, which could result in device manipulation and unauthorized data access. The following versions of Schneider Electric NetBotz 5 750/755 are affected: NetBotz 5 750 vers:intdot/ NetBotz 5 755 vers:intdot/ CVSS Vendor Equipment Vulnerabilities v3 6.4 Schneider Electric Schneider Electric NetBotz 5 750/755 Improper Neutralization of Special Elements used in an OS Command ('OS Command Injection'), SQL Injection: Hibernate Background Critical Infrastructure Sectors: Commercial Facilities, Critical Manufacturing, Information Technology Countries/Areas Deployed: Worldwide Company Headquarters Location: France Vulnerabilities Expand All + CVE-2026-13336 CWE-78: Improper Neutralization of Special Elements used in an OS Command ('OS Command Injection') vulnerability exists that could cause execution of Linux Operating system commands when a system back up is restored that has been maliciously modified. View CVE Details Affected Products Schneider Electric NetBotz 5 750/755 Vendor: Schneider Electric Product Version: NetBotz 5 750 versions 5.5.2 and prior, NetBotz 5 755 Versions 5.5.2 and prior Product Status: fixed, known_affected Remediations Vendor fix Version 5.6.0 of NetBotz 5 750/755 includes a fix for these vulnerabilities and is available for download here: https://www.se.com/ww/en/product-range/61830-netbotz/#software-and-firmware Reboot needed: Upon install, the offer will automatically restart. A customer can validate a successful install by logging into the GUI and selecting the ‘About NetBotz’ option. This will indicate the installed version. For more information see the associated Schneider Electric security advisory Multiple Vulnerabilities on NetBotz 5 750/755 Products - SEVD-2026-223-02 CSAF Version , Multiple Vulnerabilities on NetBotz 5 750/755 Products - SEVD-2026-223-02 PDF Version . Relevant CWE: CWE-78 Improper Neutralization of Special Elements used in an OS Command ('OS Command Injection') Metrics CVSS Version Base Score Base Severity Vector String 3.1 6.4 MEDIUM CVSS:3.1/AV:A/AC:H/PR:H/UI:N/S:U/C:H/I:H/A:H CVE-2026-13337 CWE-564:SQL Injection: Hibernate vulnerability exists that could allow the injection of a malicious HQL query in the NetBotz database when a malicious user is logged into the NetBotz via the web-service interface or web-ui. View CVE Details Affected Products Schneider Electric NetBotz 5 750/755 Vendor: Schneider Electric Product Version: NetBotz 5 750 versions 5.5.2 and prior, NetBotz 5 755 Versions 5.5.2 and prior Product Status: fixed, known_affected Remediations Vendor fix Version 5.6.0 of NetBotz 5 750/755 includes a fix for these vulnerabilities and is available for download here: https://www.se.com/ww/en/product-range/61830-netbotz/#software-and-firmware Reboot needed: Upon install, the offer will automatically restart. A customer can validate a successful install by logging into the GUI and selecting the ‘About NetBotz’ option. This will indicate the installed version. For more information see the associated Schneider Electric security advisory Multiple Vulnerabilities on NetBotz 5 750/755 Products - SEVD-2026-223-02 CSAF Version , Multiple Vulnerabilities on NetBotz 5 750/755 Products - SEVD-2026-223-02 PDF Version . Relevant CWE: CWE-564 SQL Injection: Hibernate Metrics CVSS Version Base Score Base Severity Vector String 3.1 4.6 MEDIUM CVSS:3.1/AV:A/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:N Acknowledgments Schneider Electric CPCERT reported these vulnerabilities to CISA. General Security Recommendations Schneider Electric strongly recommends the following industry cybersecurity best practices. Locate control and safety system networks and remote devices behind firewalls and isolate them from the business network. Install physical controls so no unauthorized personnel can access your industrial control and safety systems, components, peripheral equipment, and networks. Place all controllers in locked cabinets and never leave them in the “Program” mode. Never connect programming software to any network other than the network intended for that device. Scan all methods of mobile data exchange with the isolated network such as CDs, USB drives, etc. before use in the terminals or any node connected to these networks. Never allow mobile devices that have connected to any other network besides the intended network to connect to the safety or control networks without proper sanitation. Minimize network exposure for all control system devices and systems and ensure that they are not accessible from the Internet. * When remote access is required, use secure methods, such as Virtual Private Networks (VPNs). Recognize that VPNs may have vulnerabilities and should be updated to the most current version available. Also, understand that VPNs are only as secure as the connected devices. For more information refer to the Schneider Electric Recommended Cybersecurity Best Practices document . For More Information This document provides an overview of the identified vulnerability or vulnerabilities and actions required to mitigate. For more details and assistance on how to protect your installation, contact your local Schneider Electric representative or Schneider Electric Industrial Cybersecurity Services: https://www.se.com/ww/en/work/solutions/cybersecurity/ . These organizations will be fully aware of this situation and can support you through the process. For further information related to cybersecurity in Schneider Electric’s products, visit the company’s cybersecurity support portal page: https://www.se.com/ww/en/work/support/cybersecurity/overview.jsp LEGAL DISCLAIMER THIS NOTIFICATION DOCUMENT, THE INFORMATION CONTAINED HEREIN, AND ANY MATERIALS LINKED FROM IT (COLLECTIVELY, THIS “NOTIFICATION”) ARE INTENDED TO HELP PROVIDE AN OVERVIEW OF THE IDENTIFIED SITUATION AND SUGGESTED MITIGATION ACTIONS, REMEDIATION, FIX, AND/OR GENERAL SECURITY RECOMMENDATIONS AND IS PROVIDED ON AN “AS-IS” BASIS WITHOUT WARRANTY OR GUARANTEE OF ANY KIND. SCHNEIDER ELECTRIC DISCLAIMS ALL WARRANTIES RELATING TO THIS NOTIFICATION, EITHER EXPRESS OR IMPLIED, INCLUDING WARRANTIES OF MERCHANTABILITY OR FITNESS FOR A PARTICULAR PURPOSE. SCHNEIDER ELECTRIC MAKES NO WARRANTY THAT THE NOTIFICATION WILL RESOLVE THE IDENTIFIED SITUATION. IN NO EVENT SHALL SCHNEIDER ELECTRIC BE LIABLE FOR ANY DAMAGES OR LOSSES WHATSOEVER IN CONNECTION WITH THIS NOTIFICATION, INCLUDING DIRECT, INDIRECT, INCIDENTAL, CONSEQUENTIAL, LOSS OF BUSINESS PROFITS OR SPECIAL DAMAGES, EVEN IF SCHNEIDER ELECTRIC HAS BEEN ADVISED OF THE POSSIBILITY OF SUCH DAMAGES. YOUR USE OF THIS NOTIFICATION IS AT YOUR OWN RISK, AND YOU ARE SOLELY LIABLE FOR ANY DAMAGES TO YOUR SYSTEMS OR ASSETS OR OTHER LOSSES THAT MAY RESULT FROM YOUR USE OF THIS NOTIFICATION. SCHNEIDER ELECTRIC RESERVES THE RIGHT TO UPDATE OR CHANGE THIS NOTIFICATION AT ANY TIME AND IN ITS SOLE DISCRETION About Schneider Electric Schneider's purpose is to create Impact by empowering all to make the most of our energy and resources, bridging progress and sustainability for all. We call this Life Is On. Our mission is to be the trusted partner in Sustainability and Efficiency. We are a global industrial technology leader bringing world-leading expertise in electrification, automation and digitization to smart industries, resilient infrastructure, future-proof data centers, intelligent buildings, and intuitive homes. Anchored by our deep domain expertise, we provide integrated end-to-end lifecycle AI enabled Industrial IoT solutions with connected products, automation, software and services, delivering digital twins to enable profitable growth for our customers. We are a people company with an ecosystem of 150,000 colleagues and more than a million partners operating in over 100 countries to ensure proximity to our customers and stakeholders. We embrace diversity and inclusion in everything we do, guided by our meaningful purpose of a sustainable future for all. www.se.com Legal Notice and Terms of Use This product is provided subject to this Notification ( https://www.cisa.gov/notification ) and this Privacy & Use policy ( https://www.cisa.gov/privacy-policy ). Recommended Practices CISA recommends users take defensive measures to minimize the exploitation risk of this vulnerability. Minimize network exposure for all control system devices and/or systems, and ensure they are not accessible from the internet. Locate control system networks and remote devices behind firewalls and isolate them from business networks. When remote access is required, use more secure methods, such as Virtual Private Networks (VPNs), recognizing VPNs may have vulnerabilities and should be updated to the most recent version available. Also recognize VPN is only as secure as its connected devices. CISA reminds organizations to perform proper impact analysis and risk assessment prior to deploying defensive measures. CISA also provides a section for control systems security recommended practices on the ICS webpage on cisa.gov. Several CISA products detailing cyber defense best practices are available for reading and download, including Improving Industrial Control Systems Cybersecurity with Defense-in-Depth Strategies. CISA encourages organizations to implement recommended cybersecurity strategies for proactive defense of ICS assets. Additional mitigation guidance and recommended practices are publicly available on the ICS webpage at cisa.gov in the technical information paper, ICS-TIP-12-146-01B--Targeted Cyber Intrusion Detection and Mitigation Strategies. Organizations observing suspected malicious activity should follow established internal procedures and report findings to CISA for tracking and correlation against other incidents. Advisory Conversion Disclaimer This ICSA is a verbatim republication of Schneider Electric CPCERT SEVD-2026-223-02 from a direct conversion of the vendor's Common Security Advisory Framework (CSAF) advisory. This is republished to CISA's website as a means of increasing visibility and is provided "as-is" for informational purposes only. CISA is not responsible for the editorial or technical accuracy of republished advisories and provides no warranties of any kind regarding any information contained within this advisory. Further, CISA does not endorse any commercial product or service. Please contact Schneider Electric CPCERT directly for any questions regarding this advisory. Revision History Initial Release Date: 2026-08-11 Date Revision Summary 2026-08-11 1 Original Release 2026-09-17 2 Initial CISA Republication of Schneider Electric CPCERT SEVD-2026-223-02 advisory Legal Notice and Terms of Use

Fix: Review CISA guidance and apply vendor security updates immediately.

Mitsubishi Electric CC-Link IE TSN Communication Protocol (Update A) Important CISA Advisory
2026-09-17 CISA Advisory

Mitsubishi Electric CC-Link IE TSN Communication Protocol (Update A)

View CSAF Summary Successful exploitation of this vulnerability could allow an attacker with access to the same network segment to tamper with communication data in the affected product by sending specially crafted packets under specific timing conditions. This could allow the attacker to cause a denial-of-service (DoS) condition in the affected product by interfering with its control function or causing it to operate incorrectly. The following versions of Mitsubishi Electric CC-Link IE TSN Communication Protocol (Update A) are affected: Mitsubishi Electric MELSEC MX Controller MX-R model MXR300-16 vers:all/* (CVE-2026-13584) Mitsubishi Electric MELSEC MX Controller MX-R model MXR300-32 vers:all/* (CVE-2026-13584) Mitsubishi Electric MELSEC MX Controller MX-R model MXR300-64 vers:all/* (CVE-2026-13584) Mitsubishi Electric MELSEC MX Controller MX-R model MXR500-128 vers:all/* (CVE-2026-13584) Mitsubishi Electric MELSEC MX Controller MX-R model MXR500-256 vers:all/* (CVE-2026-13584) Mitsubishi Electric MELSEC MX Controller MX-F model MXF100-8-N32 vers:all/* (CVE-2026-13584) Mitsubishi Electric MELSEC MX Controller MX-F model MXF100-8-P32 vers:all/* (CVE-2026-13584) Mitsubishi Electric MELSEC MX Controller MX-F model MXF100-16-N32 vers:all/* (CVE-2026-13584) Mitsubishi Electric MELSEC MX Controller MX-F model MXF100-16-P32 vers:all/* (CVE-2026-13584) Mitsubishi Electric MELSEC MX Controller MX-F model MXF100S-N32 vers:all/* (CVE-2026-13584) Mitsubishi Electric MELSEC MX Controller MX-F model MXF100S-P32 vers:all/* (CVE-2026-13584) Mitsubishi Electric MELSEC MX Controller MX-F model MXF100S-8-N32 vers:all/* (CVE-2026-13584) Mitsubishi Electric MELSEC MX Controller MX-F model MXF100S-8-P32 vers:all/* (CVE-2026-13584) Mitsubishi Electric MELSEC MX Controller MX-F model MXF100S-16-N32 vers:all/* (CVE-2026-13584) Mitsubishi Electric MELSEC MX Controller MX-F model MXF100S-16-P32 vers:all/* (CVE-2026-13584) Mitsubishi Electric Master/local module RJ71GN11-T2 vers:all/* (CVE-2026-13584) Mitsubishi Electric Master/local module RJ71GN11-SX vers:all/* (CVE-2026-13584) Mitsubishi Electric Master/local module RJ71GN11-EIP vers:all/* (CVE-2026-13584) Mitsubishi Electric Master/local module FX5-CCLGN-MS vers:all/* (CVE-2026-13584) Mitsubishi Electric CC-Link IE TSN interface board NZ81GN11-SX vers:all/* (CVE-2026-13584) Mitsubishi Electric CC-Link IE TSN interface board NZ81GN11-T2 vers:all/* (CVE-2026-13584) Mitsubishi Electric Motion module RD78G4 vers:all/* (CVE-2026-13584) Mitsubishi Electric Motion module RD78G8 vers:all/* (CVE-2026-13584) Mitsubishi Electric Motion module RD78G16 vers:all/* (CVE-2026-13584) Mitsubishi Electric Motion module RD78G64 vers:all/* (CVE-2026-13584) Mitsubishi Electric Motion module RD78GHV vers:all/* (CVE-2026-13584) Mitsubishi Electric Motion module RD78GHW vers:all/* (CVE-2026-13584) Mitsubishi Electric Motion module FX5-40SSC-G vers:all/* (CVE-2026-13584) Mitsubishi Electric Motion module FX5-80SSC-G vers:all/* (CVE-2026-13584) Mitsubishi Electric MELSEC iQ-L Series Motion Module LD78G4 vers:all/* (CVE-2026-13584) Mitsubishi Electric MELSEC iQ-L Series Motion Module LD78G16 vers:all/* (CVE-2026-13584) Mitsubishi Electric Motion Control Board MR-EM441G vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module NZ2GN2S1-32D vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module NZ2GN2S1-32T vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module NZ2GN2S1-32TE vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module NZ2GN2S1-32DT vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module NZ2GN2S1-32DTE vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module NZ2GN2B1-32D vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module NZ2GN2B1-32T vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module NZ2GN2B1-32TE vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module NZ2GN2B1-32DT vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module NZ2GN2B1-32DTE vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module NZ2GNCF1-32D vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module NZ2GNCF1-32T vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module NZ2GNCE3-32D vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module NZ2GNCE3-32DT vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module NZ2GN12A4-16D vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module NZ2GN12A4-16DE vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module NZ2GN12A2-16T vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module NZ2GN12A2-16TE vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module NZ2GN12A42-16DT vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module NZ2GN12A42-16DTE vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module NZ2GN2S1-16D vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module NZ2GN2S1-16T vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module NZ2GN2S1-16TE vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module NZ2GN2B1-16D vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module NZ2GN2B1-16T vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module NZ2GN2B1-16TE vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module with safety functions NZ2GNSS2-8D vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module with safety functions NZ2GNSS2-8D-K vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module with safety functions NZ2GNSS2-8TE vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module with safety functions NZ2GNSS2-8TE-K vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module with safety functions NZ2GNSS2-16DTE vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module with safety functions NZ2GNSS2-16DTE-K vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module with safety functions NZ2GNS12A2-14DT vers:all/* (CVE-2026-13584) Mitsubishi Electric Block-type remote module with safety functions NZ2GNS12A2-16DTE vers:all/* (CVE-2026-13584) Mitsubishi Electric Analog-Digital converter module NZ2GN2S-60AD4 vers:all/* (CVE-2026-13584) Mitsubishi Electric Analog-Digital converter module NZ2GN2B-60AD4 vers:all/* (CVE-2026-13584) Mitsubishi Electric Digital-Analog converter module NZ2GN2S-60DA4 vers:all/* (CVE-2026-13584) Mitsubishi Electric Digital-Analog converter module NZ2GN2B-60DA4 vers:all/* (CVE-2026-13584) Mitsubishi Electric CC-Link IE TSN compatible coupler NZ2FT-GN vers:all/* (CVE-2026-13584) Mitsubishi Electric FPGA module NZ2GN2S-D41P01 vers:all/* (CVE-2026-13584) Mitsubishi Electric FPGA module NZ2GN2S-D41D01 vers:all/* (CVE-2026-13584) Mitsubishi Electric FPGA module NZ2GN2S-D41PD02 vers:all/* (CVE-2026-13584) Mitsubishi Electric Tension meter LM7-1LG vers:all/* (CVE-2026-13584) Mitsubishi Electric Tension meter LM7-2LG vers:all/* (CVE-2026-13584) Mitsubishi Electric AC Servo MELSERVO-J5 MR-J5-G vers:all/* (CVE-2026-13584) Mitsubishi Electric AC Servo MELSERVO-J5 MR-J5W-G vers:all/* (CVE-2026-13584) Mitsubishi Electric AC Servo MELSERVO-J5 MR-J5-G-HS vers:all/* (CVE-2026-13584) Mitsubishi Electric AC Servo MELSERVO-J5 MR-J5-G-RJ vers:all/* (CVE-2026-13584) Mitsubishi Electric AC Servo MELSERVO-J5 MR-J5-G-LL vers:all/* (CVE-2026-13584) Mitsubishi Electric AC Servo MELSERVO-J5 MR-J5D-G4 vers:all/* (CVE-2026-13584) Mitsubishi Electric AC Servo MELSERVO-J5 MR-MD333G vers:all/* (CVE-2026-13584) Mitsubishi Electric AC Servo MELSERVO-JET MR-JET-G vers:all/* (CVE-2026-13584) Mitsubishi Electric AC Servo MELSERVO-JET MR-JET-G4-HS vers:all/* (CVE-2026-13584) Mitsubishi Electric Liner Track System MTR-S series Linear track control module MTR-SCU00-4G vers:all/* (CVE-2026-13584) Mitsubishi Electric Liner Track System MTR-S series Linear track control module MTR-SCU00-PG vers:all/* (CVE-2026-13584) Mitsubishi Electric Inverter FR-A800/F800/E800 Series FR-A8NCG vers:all/* (CVE-2026-13584) Mitsubishi Electric Inverter FR-A800/F800/E800 Series FR-A8NCG-S vers:all/* (CVE-2026-13584) Mitsubishi Electric Inverter FR-A800/F800/E800 Series FR-A800-GN vers:all/* (CVE-2026-13584) Mitsubishi Electric Inverter FR-A800/F800/E800 Series FR-E800-E vers:all/* (CVE-2026-13584) Mitsubishi Electric Inverter FR-A800/F800/E800 Series FR-E800-SCE vers:all/* (CVE-2026-13584) Mitsubishi Electric Industrial Robot CR800-D series controller Network Base Card 2F-DQ535-TSN vers:all/* (CVE-2026-13584) Mitsubishi Electric CC-Link IE TSN expansion unit FCU8-EX569 vers:all/* (CVE-2026-13584) Mitsubishi Electric CC-Link IE TSN-CC-Link IE Field Network bridge module NZ2GN-GFB vers:all/* (CVE-2026-13584) Mitsubishi Electric CC-Link IE TSN-AnyWireASLINK bridge module NZ2AW1GNAL vers:all/* (CVE-2026-13584) Mitsubishi Electric Energy Measuring Unit CC-Link IE TSN Communication Unit EMU4-CM-TSN vers:all/* (CVE-2026-13584) Mitsubishi Electric GOT3000 Series GT3715-FHCBD vers:all/* (CVE-2026-13584) Mitsubishi Electric GOT3000 Series GT3712-WXCBD vers:all/* (CVE-2026-13584) Mitsubishi Electric GOT3000 Series GT3715-XRBA vers:all/* (CVE-2026-13584) Mitsubishi Electric GOT3000 Series GT3715-XRBD vers:all/* (CVE-2026-13584) Mitsubishi Electric GOT3000 Series GT3712-XRBA vers:all/* (CVE-2026-13584) Mitsubishi Electric GOT3000 Series GT3712-XRBD vers:all/* (CVE-2026-13584) Mitsubishi Electric GOT3000 Series GT3710-XRBA vers:all/* (CVE-2026-13584) Mitsubishi Electric GOT3000 Series GT3710-XRBD vers:all/* (CVE-2026-13584) Mitsubishi Electric GOT3000 Series GT3708-XRBA vers:all/* (CVE-2026-13584) Mitsubishi Electric GOT3000 Series GT3708-XRBD vers:all/* (CVE-2026-13584) Mitsubishi Electric CC-Link IE TSN Communication Unit GT25-J71GN13-T2 vers:all/* (CVE-2026-13584) Mitsubishi Electric Motion Control Software SWM-G vers:all/* (CVE-2026-13584) Mitsubishi Electric Motion Control Software SWM-G-N1 vers:all/* (CVE-2026-13584) Mitsubishi Electric CC-Link IE TSN Communication Software for Windows SW1DND-CCIETCT-M vers:all/* (CVE-2026-13584) Mitsubishi Electric Analysis Support Software MELSOFT VIMA SW1DNN-VIMA-M vers:all/* (CVE-2026-13584) Mitsubishi Electric Master/Local module Designated communication LSI DeviceKit NZ2KT-NPETNG51 vers:all/* (CVE-2026-13584) Mitsubishi Electric Remote Station Communication LSI with GbE-PHY NZ2GACP620-60 vers:all/* (CVE-2026-13584) Mitsubishi Electric Remote Station Communication LSI with GbE-PHY NZ2GACP620-300 vers:all/* (CVE-2026-13584) Mitsubishi Electric Remote Station Communication LSI with GbE-PHY NZ2GACP621-90 vers:all/* (CVE-2026-13584) Mitsubishi Electric Remote Station Communication LSI with GbE-PHY NZ2GACP621-720 vers:all/* (CVE-2026-13584) Mitsubishi Electric CC-Link IE TSN Master/Local module Designated communication LSI SDK SW1DNN-GN610SRC-M vers:all/* (CVE-2026-13584) Mitsubishi Electric Remote station software development kit SW1DNC-GNSDK1S-M vers:all/* (CVE-2026-13584) Mitsubishi Electric Remote station software development kit SW1DNC-GNSDK2S-M vers:all/* (CVE-2026-13584) CVSS Vendor Equipment Vulnerabilities v3 7.1 Mitsubishi Electric Mitsubishi Electric CC-Link IE TSN Communication Protocol (Update A) Improper Enforcement of Message Integrity During Transmission in a Communication Channel Background Critical Infrastructure Sectors: Critical Manufacturing Countries/Areas Deployed: Worldwide Company Headquarters Location: Japan Vulnerabilities Expand All + CVE-2026-13584 Improper Enforcement of Message Integrity During Transmission in a Communication Channel (CWE-924) vulnerability exists in the CC-Link IE TSN communication protocol. This vulnerability could allow an attacker with access to the same network segment to tamper with communication data, such as control input and output values, by sending specially crafted packets under specific timing conditions. This could allow the attacker to cause a denial-of-service (DoS) condition in the affected product by interfering with its control function or causing it to operate incorrectly. View CVE Details Affected Products Mitsubishi Electric CC-Link IE TSN Communication Protocol (Update A) Vendor: Mitsubishi Electric Product Version: Mitsubishi Electric MELSEC MX Controller MX-R model MXR300-16: vers:all/*, Mitsubishi Electric MELSEC MX Controller MX-R model MXR300-32: vers:all/*, Mitsubishi Electric MELSEC MX Controller MX-R model MXR300-64: vers:all/*, Mitsubishi Electric MELSEC MX Controller MX-R model MXR500-128: vers:all/*, Mitsubishi Electric MELSEC MX Controller MX-R model MXR500-256: vers:all/*, Mitsubishi Electric MELSEC MX Controller MX-F model MXF100-8-N32: vers:all/*, Mitsubishi Electric MELSEC MX Controller MX-F model MXF100-8-P32: vers:all/*, Mitsubishi Electric MELSEC MX Controller MX-F model MXF100-16-N32: vers:all/*, Mitsubishi Electric MELSEC MX Controller MX-F model MXF100-16-P32: vers:all/*, Mitsubishi Electric MELSEC MX Controller MX-F model MXF100S-N32: vers:all/*, Mitsubishi Electric MELSEC MX Controller MX-F model MXF100S-P32: vers:all/*, Mitsubishi Electric MELSEC MX Controller MX-F model MXF100S-8-N32: vers:all/*, Mitsubishi Electric MELSEC MX Controller MX-F model MXF100S-8-P32: vers:all/*, Mitsubishi Electric MELSEC MX Controller MX-F model MXF100S-16-N32: vers:all/*, Mitsubishi Electric MELSEC MX Controller MX-F model MXF100S-16-P32: vers:all/*, Mitsubishi Electric Master/local module RJ71GN11-T2: vers:all/*, Mitsubishi Electric Master/local module RJ71GN11-SX: vers:all/*, Mitsubishi Electric Master/local module RJ71GN11-EIP: vers:all/*, Mitsubishi Electric Master/local module FX5-CCLGN-MS: vers:all/*, Mitsubishi Electric CC-Link IE TSN interface board NZ81GN11-SX: vers:all/*, Mitsubishi Electric CC-Link IE TSN interface board NZ81GN11-T2: vers:all/*, Mitsubishi Electric Motion module RD78G4: vers:all/*, Mitsubishi Electric Motion module RD78G8: vers:all/*, Mitsubishi Electric Motion module RD78G16: vers:all/*, Mitsubishi Electric Motion module RD78G64: vers:all/*, Mitsubishi Electric Motion module RD78GHV: vers:all/*, Mitsubishi Electric Motion module RD78GHW: vers:all/*, Mitsubishi Electric Motion module FX5-40SSC-G: vers:all/*, Mitsubishi Electric Motion module FX5-80SSC-G: vers:all/*, Mitsubishi Electric MELSEC iQ-L Series Motion Module LD78G4: vers:all/*, Mitsubishi Electric MELSEC iQ-L Series Motion Module LD78G16: vers:all/*, Mitsubishi Electric Motion Control Board MR-EM441G: vers:all/*, Mitsubishi Electric Block-type remote module NZ2GN2S1-32D: vers:all/*, Mitsubishi Electric Block-type remote module NZ2GN2S1-32T: vers:all/*, Mitsubishi Electric Block-type remote module NZ2GN2S1-32TE: vers:all/*, Mitsubishi Electric Block-type remote module NZ2GN2S1-32DT: vers:all/*, Mitsubishi Electric Block-type remote module NZ2GN2S1-32DTE: vers:all/*, Mitsubishi Electric Block-type remote module NZ2GN2B1-32D: vers:all/*, Mitsubishi Electric Block-type remote module NZ2GN2B1-32T: vers:all/*, Mitsubishi Electric Block-type remote module NZ2GN2B1-32TE: vers:all/*, Mitsubishi Electric Block-type remote module NZ2GN2B1-32DT: vers:all/*, Mitsubishi Electric Block-type remote module NZ2GN2B1-32DTE: vers:all/*, Mitsubishi Electric Block-type remote module NZ2GNCF1-32D: vers:all/*, Mitsubishi Electric Block-type remote module NZ2GNCF1-32T: vers:all/*, Mitsubishi Electric Block-type remote module NZ2GNCE3-32D: vers:all/*, Mitsubishi Electric Block-type remote module NZ2GNCE3-32DT: vers:all/*, Mitsubishi Electric Block-type remote module NZ2GN12A4-16D: vers:all/*, Mitsubishi Electric Block-type remote module NZ2GN12A4-16DE: vers:all/*, Mitsubishi Electric Block-type remote module NZ2GN12A2-16T: vers:all/*, Mitsubishi Electric Block-type remote module NZ2GN12A2-16TE: vers:all/*, Mitsubishi Electric Block-type remote module NZ2GN12A42-16DT: vers:all/*, Mitsubishi Electric Block-type remote module NZ2GN12A42-16DTE: vers:all/*, Mitsubishi Electric Block-type remote module NZ2GN2S1-16D: vers:all/*, Mitsubishi Electric Block-type remote module NZ2GN2S1-16T: vers:all/*, Mitsubishi Electric Block-type remote module NZ2GN2S1-16TE: vers:all/*, Mitsubishi Electric Block-type remote module NZ2GN2B1-16D: vers:all/*, Mitsubishi Electric Block-type remote module NZ2GN2B1-16T: vers:all/*, Mitsubishi Electric Block-type remote module NZ2GN2B1-16TE: vers:all/*, Mitsubishi Electric Block-type remote module with safety functions NZ2GNSS2-8D: vers:all/*, Mitsubishi Electric Block-type remote module with safety functions NZ2GNSS2-8D-K: vers:all/*, Mitsubishi Electric Block-type remote module with safety functions NZ2GNSS2-8TE: vers:all/*, Mitsubishi Electric Block-type remote module with safety functions NZ2GNSS2-8TE-K: vers:all/*, Mitsubishi Electric Block-type remote module with safety functions NZ2GNSS2-16DTE: vers:all/*, Mitsubishi Electric Block-type remote module with safety functions NZ2GNSS2-16DTE-K: vers:all/*, Mitsubishi Electric Block-type remote module with safety functions NZ2GNS12A2-14DT: vers:all/*, Mitsubishi Electric Block-type remote module with safety functions NZ2GNS12A2-16DTE: vers:all/*, Mitsubishi Electric Analog-Digital converter module NZ2GN2S-60AD4: vers:all/*, Mitsubishi Electric Analog-Digital converter module NZ2GN2B-60AD4: vers:all/*, Mitsubishi Electric Digital-Analog converter module NZ2GN2S-60DA4: vers:all/*, Mitsubishi Electric Digital-Analog converter module NZ2GN2B-60DA4: vers:all/*, Mitsubishi Electric CC-Link IE TSN compatible coupler NZ2FT-GN: vers:all/*, Mitsubishi Electric FPGA module NZ2GN2S-D41P01: vers:all/*, Mitsubishi Electric FPGA module NZ2GN2S-D41D01: vers:all/*, Mitsubishi Electric FPGA module NZ2GN2S-D41PD02: vers:all/*, Mitsubishi Electric Tension meter LM7-1LG: vers:all/*, Mitsubishi Electric Tension meter LM7-2LG: vers:all/*, Mitsubishi Electric AC Servo MELSERVO-J5 MR-J5-G: vers:all/*, Mitsubishi Electric AC Servo MELSERVO-J5 MR-J5W-G: vers:all/*, Mitsubishi Electric AC Servo MELSERVO-J5 MR-J5-G-HS: vers:all/*, Mitsubishi Electric AC Servo MELSERVO-J5 MR-J5-G-RJ: vers:all/*, Mitsubishi Electric AC Servo MELSERVO-J5 MR-J5-G-LL: vers:all/*, Mitsubishi Electric AC Servo MELSERVO-J5 MR-J5D-G4 : vers:all/*, Mitsubishi Electric AC Servo MELSERVO-J5 MR-MD333G: vers:all/*, Mitsubishi Electric AC Servo MELSERVO-JET MR-JET-G: vers:all/*, Mitsubishi Electric AC Servo MELSERVO-JET MR-JET-G4-HS: vers:all/*, Mitsubishi Electric Liner Track System MTR-S series Linear track control module MTR-SCU00-4G: vers:all/*, Mitsubishi Electric Liner Track System MTR-S series Linear track control module MTR-SCU00-PG: vers:all/*, Mitsubishi Electric Inverter FR-A800/F800/E800 Series FR-A8NCG: vers:all/*, Mitsubishi Electric Inverter FR-A800/F800/E800 Series FR-A8NCG-S: vers:all/*, Mitsubishi Electric Inverter FR-A800/F800/E800 Series FR-A800-GN: vers:all/*, Mitsubishi Electric Inverter FR-A800/F800/E800 Series FR-E800-E: vers:all/*, Mitsubishi Electric Inverter FR-A800/F800/E800 Series FR-E800-SCE: vers:all/*, Mitsubishi Electric Industrial Robot CR800-D series controller Network Base Card 2F-DQ535-TSN: vers:all/*, Mitsubishi Electric CC-Link IE TSN expansion unit FCU8-EX569: vers:all/*, Mitsubishi Electric CC-Link IE TSN-CC-Link IE Field Network bridge module NZ2GN-GFB: vers:all/*, Mitsubishi Electric CC-Link IE TSN-AnyWireASLINK bridge module NZ2AW1GNAL: vers:all/*, Mitsubishi Electric Energy Measuring Unit CC-Link IE TSN Communication Unit EMU4-CM-TSN: vers:all/*, Mitsubishi Electric GOT3000 Series GT3715-FHCBD: vers:all/*, Mitsubishi Electric GOT3000 Series GT3712-WXCBD: vers:all/*, Mitsubishi Electric GOT3000 Series GT3715-XRBA: vers:all/*, Mitsubishi Electric GOT3000 Series GT3715-XRBD: vers:all/*, Mitsubishi Electric GOT3000 Series GT3712-XRBA: vers:all/*, Mitsubishi Electric GOT3000 Series GT3712-XRBD: vers:all/*, Mitsubishi Electric GOT3000 Series GT3710-XRBA: vers:all/*, Mitsubishi Electric GOT3000 Series GT3710-XRBD: vers:all/*, Mitsubishi Electric GOT3000 Series GT3708-XRBA: vers:all/*, Mitsubishi Electric GOT3000 Series GT3708-XRBD: vers:all/*, Mitsubishi Electric CC-Link IE TSN Communication Unit GT25-J71GN13-T2: vers:all/*, Mitsubishi Electric Motion Control Software SWM-G: vers:all/*, Mitsubishi Electric Motion Control Software SWM-G-N1: vers:all/*, Mitsubishi Electric CC-Link IE TSN Communication Software for Windows SW1DND-CCIETCT-M: vers:all/*, Mitsubishi Electric Analysis Support Software MELSOFT VIMA SW1DNN-VIMA-M: vers:all/*, Mitsubishi Electric Master/Local module Designated communication LSI DeviceKit NZ2KT-NPETNG51: vers:all/*, Mitsubishi Electric Remote Station Communication LSI with GbE-PHY NZ2GACP620-60: vers:all/*, Mitsubishi Electric Remote Station Communication LSI with GbE-PHY NZ2GACP620-300: vers:all/*, Mitsubishi Electric Remote Station Communication LSI with GbE-PHY NZ2GACP621-90: vers:all/*, Mitsubishi Electric Remote Station Communication LSI with GbE-PHY NZ2GACP621-720: vers:all/*, Mitsubishi Electric CC-Link IE TSN Master/Local module Designated communication LSI SDK SW1DNN-GN610SRC-M: vers:all/*, Mitsubishi Electric Remote station software development kit SW1DNC-GNSDK1S-M: vers:all/*, Mitsubishi Electric Remote station software development kit SW1DNC-GNSDK2S-M: vers:all/* Product Status: known_affected Remediations No fix planned For customers using the affected products, please refer to Mitsubishi Electric's security advisory, " https://www.mitsubishielectric.com/psirt/vulnerability/pdf/2026-005_en.pdf " and take the measures described there. Mitigation For customers of the affected products, Mitsubishi Electric recommends restricting physical access to the affected products and the CC-Link IE TSN network to which the affected products are connected by taking measures such as the following: (a) managing access to and from the site where the affected products are installed, (b) locking the control panel in which the affected products and/or the network devices are installed, and (c) locking the Ethernet ports such as with port lock accessories, to minimize the risk of exploitation of this vulnerability. Mitigation For customers of the affected products, Mitsubishi Electric recommends using the affected products within a trusted network where communication with untrusted networks and hosts is blocked by a firewall or similar measures, to minimize the risk of exploitation of this vulnerability. Mitigation For customers of the affected products, Mitsubishi Electric recommends appropriately configuring credentials and access privileges for network devices installed at the boundary between trusted networks and external networks, to minimize the risk of exploitation of this vulnerability. Relevant CWE: CWE-924 Improper Enforcement of Message Integrity During Transmission in a Communication Channel Metrics CVSS Version Base Score Base Severity Vector String 3.1 7.1 HIGH CVSS:3.1/AV:A/AC:L/PR:N/UI:N/S:U/C:N/I:H/A:L 4.0 7.1 HIGH CVSS:4.0/AV:A/AC:L/AT:N/PR:N/UI:N/VC:N/VI:H/VA:L/SC:N/SI:N/SA:N Acknowledgments Alessandro Di Pinto, Giovanni Dini Gentilini, Luca Cremona, Gabriele Quagliarella of Nozomi Networks, Inc. reported this vulnerability to Mitsubishi Electric. Legal Notice and Terms of Use This product is provided subject to this Notification ( https://www.cisa.gov/notification ) and this Privacy & Use policy ( https://www.cisa.gov/privacy-policy ). Recommended Practices CISA recommends users take defensive measures to minimize the exploitation risk of these vulnerabilities. Minimize network exposure for all control system devices and/or systems, and ensure they are not accessible from the internet. Locate control system networks and remote devices behind firewalls and isolate them from business networks. When remote access is required, use more secure methods, such as Virtual Private Networks (VPNs), recognizing VPNs may have vulnerabilities and should be updated to the most recent version available. Also recognize VPN is only as secure as its connected devices. CISA reminds organizations to perform proper impact analysis and risk assessment prior to deploying defensive measures. CISA also provides a section for control systems security recommended practices on the ICS webpage on cisa.gov. Several CISA products detailing cyber defense best practices are available for reading and download, including Improving Industrial Control Systems Cybersecurity with Defense-in-Depth Strategies. CISA encourages organizations to implement recommended cybersecurity strategies for proactive defense of ICS assets. Additional mitigation guidance and recommended practices are publicly available on the ICS webpage at cisa.gov in the technical information paper, ICS-TIP-12-146-01B--Targeted Cyber Intrusion Detection and Mitigation Strategies. Organizations observing suspected malicious activity should follow established internal procedures and report findings to CISA for tracking and correlation against other incidents. Advisory Conversion Disclaimer This ICSA is a verbatim republication of Mitsubishi Electric 2026-005 from a direct conversion of the vendor's Common Security Advisory Framework (CSAF) advisory. This is republished to CISA's website as a means of increasing visibility and is provided "as-is" for informational purposes only. CISA is not responsible for the editorial or technical accuracy of republished advisories and provides no warranties of any kind regarding any information contained within this advisory. Further, CISA does not endorse any commercial product or service. Please contact Mitsubishi Electric directly for any questions regarding this advisory. Revision History Initial Release Date: 2026-07-30 Date Revision Summary 2026-07-30 1 Initial Publication 2026-07-30 2 CISA Republication - Initial CISA Republication of Mitsubishi Electric 2026-005 advisory 2026-09-17 3 MXF100S-N32, MXF100S-P32, MXF100S-8-N32, MXF100S-8-P32, MXF100S-16-N32, MXF100S-16-P32, LD78G4, and LD78G16 have been added as affected products and MI2532-W, MI2332-W, and NZ2GACP610-60 have been removed from affected products. 2026-09-17 4 CISA Republication update based on Mitsubishi Electric 2026-005 advisory Legal Notice and Terms of Use

Fix: Review CISA guidance and apply vendor security updates immediately.
ABB Ability Edgenius Important CISA Advisory
2026-09-17 CISA Advisory

ABB Ability Edgenius

View CSAF Summary ABB is aware of public reports of a vulnerability CVE‑2026‑31431 (Copy Fail) in the product versions listed as affected in the advisory. An update is available that resolves a publicly reported vulnerability. CVE‑2026‑31431 (Copy Fail) is a Linux kernel vulnerability that may allow a locally authenticated user or compromised container workload to gain elevated (root) privileges on affected systems. Once root access is obtained, the attacker can effectively gain complete control of the system The following versions of ABB Ability Edgenius are affected: Ability Edgenius >=3.2.0.0| CVSS Vendor Equipment Vulnerabilities v3 7.8 ABB ABB Ability Edgenius Incorrect Resource Transfer Between Spheres Background Critical Infrastructure Sectors: Critical Manufacturing, Energy, Water and Wastewater, Chemical Countries/Areas Deployed: Worldwide Company Headquarters Location: Switzerland Vulnerabilities Expand All + CVE-2026-31431 A Linux kernel vulnerability that may allow a locally authenticated user or compromised container workload to gain elevated (root) privileges on affected systems. The issue originates in the Linux kernel’s cryptographic subsystem and impacts kernels used by most major Linux distributions released since 2017.Successful exploitation requires local code execution, however, in shared, containerized, or multi‑tenant environments this may increase the security risk. View CVE Details Affected Products ABB Ability Edgenius Vendor: ABB Product Version: ABB Ability Edgenius >=3.2.0.0| Product Status: fixed, known_affected Remediations Vendor fix The problem is corrected in the following product versions: - Edgenius 3.2.4.1 ABB recommends that customers apply the update at earliest convenience. Mitigation Mitigating factors describe conditions and circumstances that make an attack that exploits the vulnerability difficult or less likely to succeed. Refer to section General security recommendations for further advise on how to keep your system secure. Recommended mitigation factors - Limit access to ssh or cockpit - By default, no additional lower privilege users are present on Edgenius installations. Mitigation For more information see the associated ABB PSIRT security advisory 7PAA024620 ABB CYBERSECURITY ADVISORY - PDF Version , ABB CYBERSECURITY ADVISORY - CSAF Version . Relevant CWE: CWE-669 Incorrect Resource Transfer Between Spheres Metrics CVSS Version Base Score Base Severity Vector String 3.1 7.8 HIGH CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H Acknowledgments ABB PSIRT reported this vulnerability to CISA. Notice The information in this document is subject to change without notice, and should not be construed as a commitment by ABB. ABB provides no warranty, express or implied, including warranties of merchantability and fitness for a particular purpose, for the information contained in this document, and assumes no responsibility for any errors that may appear in this document. In no event shall ABB or any of its suppliers be liable for direct, indirect, special, incidental or consequential damages of any nature or kind arising from the use of this document, or from the use of any hardware or software described in this document, even if ABB or its suppliers have been advised of the possibility of such damages. This document and parts hereof must not be reproduced or copied without written permission from ABB, and the contents hereof must not be imparted to a third party nor used for any unauthorized purpose. All rights to registrations and trademarks reside with their respective owners. Frequently Asked Questions What causes the vulnerability? - A flaw was found in the Linux kernel's algif_aead cryptographic algorithm interface. An incorrect 'in-place operation' was introduced, where the source and destination data mappings were different. This could lead to unexpected behavior or data integrity issues during cryptographic operations, potentially impacting the reliability of encrypted communications. What is Edgenius? - ABB Ability™ Edgenius is an edge computing platform that - Connects to control systems, devices, and equipment - Collects and contextualizes operational data - Hosts applications that deliver real-time insights and AI-driven recommendations What might an attacker use the vulnerability to do? - Successful exploitation could enable a local user attacker to gain administrative control of the system node, execute arbitrary code, or cause the node to become unavailable. How could an attacker exploit the vulnerability? - An attacker could exploit this vulnerability after obtaining local access to the system. By invoking the Linux kernel’s affected cryptographic interface (algif_aead), the attacker can trigger incorrect memory handling in the kernel. This allows the attacker to escalate privileges from a normal user to full administrative (root) access on the affected system node Could the vulnerability be exploited remotely? - No, to exploit this vulnerability an attacker would need to have local access (physical access or through valid SSH credentials) to an affected system node. What does the update do? - The update resolves the issue by incorporating the security update of the Linux kernel. When this security advisory was issued, had this vulnerability been publicly disclosed? - Yes, this vulnerability has been publicly disclosed. When this security advisory was issued, had ABB received any reports that this vulnerability was being exploited? - No, ABB had not received any information indicating that this vulnerability had been exploited for Edgenius when this security advisory was originally issued. Legal Notice and Terms of Use This product is provided subject to this Notification ( https://www.cisa.gov/notification ) and this Privacy & Use policy (https://www.cisa.gov/privacy-policy). Recommended Practices CISA recommends users take defensive measures to minimize the exploitation risk of these vulnerabilities. Minimize network exposure for all control system devices and/or systems, and ensure they are not accessible from the internet. Locate control system networks and remote devices behind firewalls and isolate them from business networks. When remote access is required, use more secure methods, such as Virtual Private Networks (VPNs), recognizing VPNs may have vulnerabilities and should be updated to the most recent version available. Also recognize VPN is only as secure as its connected devices. CISA reminds organizations to perform proper impact analysis and risk assessment prior to deploying defensive measures. CISA also provides a section for control systems security recommended practices on the ICS webpage on cisa.gov. Several CISA products detailing cyber defense best practices are available for reading and download, including Improving Industrial Control Systems Cybersecurity with Defense-in-Depth Strategies. CISA encourages organizations to implement recommended cybersecurity strategies for proactive defense of ICS assets. Additional mitigation guidance and recommended practices are publicly available on the ICS webpage at cisa.gov in the technical information paper, ICS-TIP-12-146-01B--Targeted Cyber Intrusion Detection and Mitigation Strategies. Organizations observing suspected malicious activity should follow established internal procedures and report findings to CISA for tracking and correlation against other incidents. Advisory Conversion Disclaimer This ICSA is a verbatim republication of ABB PSIRT 7PAA024620 from a direct conversion of the vendor's Common Security Advisory Framework (CSAF) advisory. This is republished to CISA's website as a means of increasing visibility and is provided "as-is" for informational purposes only. CISA is not responsible for the editorial or technical accuracy of republished advisories and provides no warranties of any kind regarding any information contained within this advisory. Further, CISA does not endorse any commercial product or service. Please contact ABB PSIRT directly for any questions regarding this advisory. Revision History Initial Release Date: 2026-06-25 Date Revision Summary 2026-06-25 1 Initial version. 2026-09-17 2 Initial CISA Republication of ABB PSIRT 7PAA024620 advisory Legal Notice and Terms of Use

Fix: Review CISA guidance and apply vendor security updates immediately.
Schneider Electric Modicon M340 Controller and Communication Modules Important CISA Advisory
2026-09-17 CISA Advisory

Schneider Electric Modicon M340 Controller and Communication Modules

View CSAF Summary Schneider Electric is aware of a vulnerability in its Modicon M340 https://www.se.com/ww/en/product-range/1468-modicon-m340-pac/ , BMXNOR0200H https://www.se.com/us/en/product/BMXNOR0200H/communication-module-modicon-m340-iec-608705101-104-dnp3-for-severe-environments/ : Modicon M340 X80 Ethernet Communication Modules, BMXNGD0100 https://www.se.com/us/en/product/BMXNGD0100/communication-module-modicon-m580-global-data-service/ : M580 Global Data module, BMXNOC0401 https://www.se.com/us/en/product/BMXNOC0401/network-module-modicon-m340-ethernet-ip-and-modbus-tcp-4-x-rj45/?pageType=product&sourceId=BMXNOC0401 : Modicon M340 X80 Ethernet Communication modules, BMXNOE0100 https://www.se.com/ww/en/product/BMXNOE0100/network-module-modicon-m340-modbus-tcp-1-x-rj45-flash-memory-card/?pageType=product&sourceId=BMXNOE0100 : Modbus/TCP Ethernet Modicon M340 module, BMXNOE0110 https://www.se.com/ww/en/product/BMXNOE0110/ethernet-tcp-ip-network-module-modicon-m340-automation-platform-flash-memory-card-internal-ram-16-mb-1-x-rj45-10-100/ : Modbus/TCP Ethernet Modicon M340 FactoryCast module product(s). Failure to apply the fix provided below may risk Denial Of Service attack, which could result in the unavailability of the devices. The following versions of Schneider Electric Modicon M340 Controller and Communication Modules are affected: Schneider Electric Ethernet/Serial RTU Module: vers:generic/ Schneider Electric M580 Global Data module: vers:all/* Schneider Electric Ethernet / Serial RTU Module: vers:all/* Schneider Electric Modbus/TCP Ethernet Modicon M340 module: vers:intdot/ Schneider Electric Modbus/TCP Ethernet Modicon M340 FactoryCast module: vers:intdot/ Schneider Electric Modicon M340 Firmware Versions prior to SV3.70 installed on Modicon M340 Controller: All versions CVSS Vendor Equipment Vulnerabilities v3 7.5 Schneider Electric Schneider Electric Modicon M340 Controller and Communication Modules Improper Input Validation Background Critical Infrastructure Sectors: Chemical, Commercial Facilities, Critical Manufacturing, Energy, Water and Wastewater Countries/Areas Deployed: Worldwide Company Headquarters Location: France Vulnerabilities Expand All + CVE-2025-6625 CWE-20: Improper Input Validation vulnerability exists that could cause a Denial Of Service when specific crafted FTP command is sent to the device. View CVE Details Affected Products Schneider Electric Modicon M340 Controller and Communication Modules Vendor: Schneider Electric Product Version: Ethernet / Serial RTU Module All versions, M580 Global Data module All versions, Modicon M340 X80 Ethernet Communication modules All versions, Modbus/TCP Ethernet Modicon M340 module Versions prior to 3.60, Modbus/TCP Ethernet Modicon M340 FactoryCast module Versions prior to 6.80 Product Status: fixed, known_affected Remediations Vendor fix Version 3.60 of BMXNOE0100 includes a fix for this vulnerability and is available for download here: https://www.se.com/ww/en/product/BMXNOE0100/network-module-modicon-m340-modbus-tcp-1-x-rj45-flash-memory-card/ Reboot is needed to complete the firmware upgrade Vendor fix Version 6.80 of BMXNOE0110 includes a fix for this vulnerability and is available for download here: https://www.se.com/ww/en/product/BMXNOE0110/ethernet-tcp-ip-network-module-modicon-m340-automation-platform-flash-memory-card-internal-ram-16-mb-1-x-rj45-10-100/ Reboot is needed to complete the firmware upgrade Vendor fix Version SV3.70 of Modicon M340 includes a fix for this vulnerability and is available for download here: https://www.se.com/ww/en/product-range/1468-modicon-m340/#software-and-firmware Vendor fix Version SV1.7 IR27 of BMXNOR0200H includes a fix for this vulnerability and is available for download here: https://www.se.com/ww/en/product/BMXNOR0200H/ethernet-serial-rtu-module-2-x-rj45/ Mitigation If customers choose not to apply the remediation provided above, they should immediately apply the following mitigations to reduce the risk of exploit: FTP service is disabled by default. Ensure to disable FTP service when not in use. Setup network segmentation and implement a firewall to block all unauthorized access to ports 21/FTP. Use VPN (Virtual Private Networks) tunnels if remote access is required. Mitigation Schneider Electric is establishing a remediation plan for all future versions of: Modicon M340 BMXNOR0200H BMXNGD0100 BMXNOC401 Schneider Electric will update this document when the remediation is available. Until then, customers should immediately apply the following mitigations to reduce the risk of exploit: FTP service is disabled by default. Ensure to disable FTP service when not in use. Setup network segmentation and implement a firewall to block all unauthorized access to ports 21/FTP. Use VPN (Virtual Private Networks) tunnels if remote access is required. Mitigation For more information see the associated Schneider Electric security advisory Modicon M340 Controller and Communication Modules - SEVD-2025-224-05 CSAF Version , Modicon M340 Controller and Communication Modules - SEVD-2025-224-05 PDF Version . Relevant CWE: CWE-20 Improper Input Validation Metrics CVSS Version Base Score Base Severity Vector String 3.1 7.5 HIGH CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:H Acknowledgments Schneider Electric CPCERT reported this vulnerability to CISA. General Security Recommendations We strongly recommend the following industry cybersecurity best practices. Locate control and safety system networks and remote devices behind firewalls and isolate them from the business network. Install physical controls so no unauthorized personnel can access your industrial control and safety systems, components, peripheral equipment, and networks. Place all controllers in locked cabinets and never leave them in the “Program” mode. Never connect programming software to any network other than the network intended for that device. Scan all methods of mobile data exchange with the isolated network such as CDs, USB drives, etc. before use in the terminals or any node connected to these networks. Never allow mobile devices that have connected to any other network besides the intended network to connect to the safety or control networks without proper sanitation. Minimize network exposure for all control system devices and systems and ensure that they are not accessible from the Internet. When remote access is required, use secure methods, such as Virtual Private Networks (VPNs). Recognize that VPNs may have vulnerabilities and should be updated to the most current version available. Also, understand that VPNs are only as secure as the connected devices. For more information refer to the Schneider Electric Recommended Cybersecurity Best Practices document. For More Information This document provides an overview of the identified vulnerability or vulnerabilities and actions required to mitigate. For more details and assistance on how to protect your installation, contact your local Schneider Electric representative or Schneider Electric Industrial Cybersecurity Services: https://www.se.com/ww/en/work/solutions/cybersecurity/ . These organizations will be fully aware of this situation and can support you through the process. For further information related to cybersecurity in Schneider Electric's products, visit the company's cybersecurity support portal page: https://www.se.com/ww/en/work/support/cybersecurity/overview.jsp LEGAL DISCLAIMER THIS NOTIFICATION DOCUMENT, THE INFORMATION CONTAINED HEREIN, AND ANY MATERIALS LINKED FROM IT (COLLECTIVELY, THIS “NOTIFICATION”) ARE INTENDED TO HELP PROVIDE AN OVERVIEW OF THE IDENTIFIED SITUATION AND SUGGESTED MITIGATION ACTIONS, REMEDIATION, FIX, AND/OR GENERAL SECURITY RECOMMENDATIONS AND IS PROVIDED ON AN “AS-IS” BASIS WITHOUT WARRANTY OR GUARANTEE OF ANY KIND. SCHNEIDER ELECTRIC DISCLAIMS ALL WARRANTIES RELATING TO THIS NOTIFICATION, EITHER EXPRESS OR IMPLIED, INCLUDING WARRANTIES OF MERCHANTABILITY OR FITNESS FOR A PARTICULAR PURPOSE. SCHNEIDER ELECTRIC MAKES NO WARRANTY THAT THE NOTIFICATION WILL RESOLVE THE IDENTIFIED SITUATION. IN NO EVENT SHALL SCHNEIDER ELECTRIC BE LIABLE FOR ANY DAMAGES OR LOSSES WHATSOEVER IN CONNECTION WITH THIS NOTIFICATION, INCLUDING DIRECT, INDIRECT, INCIDENTAL, CONSEQUENTIAL, LOSS OF BUSINESS PROFITS OR SPECIAL DAMAGES, EVEN IF SCHNEIDER ELECTRIC HAS BEEN ADVISED OF THE POSSIBILITY OF SUCH DAMAGES. YOUR USE OF THIS NOTIFICATION IS AT YOUR OWN RISK, AND YOU ARE SOLELY LIABLE FOR ANY DAMAGES TO YOUR SYSTEMS OR ASSETS OR OTHER LOSSES THAT MAY RESULT FROM YOUR USE OF THIS NOTIFICATION. SCHNEIDER ELECTRIC RESERVES THE RIGHT TO UPDATE OR CHANGE THIS NOTIFICATION AT ANY TIME AND IN ITS SOLE DISCRETION About Schneider Electric Schneider's purpose is to create Impact by empowering all to make the most of our energy and resources, bridging progress and sustainability for all. We call this Life Is On. Our mission is to be the trusted partner in Sustainability and Efficiency. We are a global industrial technology leader bringing world-leading expertise in electrification, automation and digitization to smart industries, resilient infrastructure, future-proof data centers, intelligent buildings, and intuitive homes. Anchored by our deep domain expertise, we provide integrated end-to-end lifecycle AI enabled Industrial IoT solutions with connected products, automation, software and services, delivering digital twins to enable profitable growth for our customers. We are a people company with an ecosystem of 150,000 colleagues and more than a million partners operating in over 100 countries to ensure proximity to our customers and stakeholders. We embrace diversity and inclusion in everything we do, guided by our meaningful purpose of a sustainable future for all. www.se.com Legal Notice and Terms of Use This product is provided subject to this Notification ( https://www.cisa.gov/notification ) and this Privacy & Use policy ( https://www.cisa.gov/privacy-policy ). Recommended Practices CISA recommends users take defensive measures to minimize the exploitation risk of these vulnerabilities. Minimize network exposure for all control system devices and/or systems, and ensure they are not accessible from the internet. Locate control system networks and remote devices behind firewalls and isolate them from business networks. When remote access is required, use more secure methods, such as Virtual Private Networks (VPNs), recognizing VPNs may have vulnerabilities and should be updated to the most recent version available. Also recognize VPN is only as secure as its connected devices. CISA reminds organizations to perform proper impact analysis and risk assessment prior to deploying defensive measures. CISA also provides a section for control systems security recommended practices on the ICS webpage on cisa.gov. Several CISA products detailing cyber defense best practices are available for reading and download, including Improving Industrial Control Systems Cybersecurity with Defense-in-Depth Strategies. CISA encourages organizations to implement recommended cybersecurity strategies for proactive defense of ICS assets. Additional mitigation guidance and recommended practices are publicly available on the ICS webpage at cisa.gov in the technical information paper, ICS-TIP-12-146-01B--Targeted Cyber Intrusion Detection and Mitigation Strategies. Organizations observing suspected malicious activity should follow established internal procedures and report findings to CISA for tracking and correlation against other incidents. Advisory Conversion Disclaimer This ICSA is a verbatim republication of Schneider Electric CPCERT SEVD-2025-224-05 from a direct conversion of the vendor's Common Security Advisory Framework (CSAF) advisory. This is republished to CISA's website as a means of increasing visibility and is provided "as-is" for informational purposes only. CISA is not responsible for the editorial or technical accuracy of republished advisories and provides no warranties of any kind regarding any information contained within this advisory. Further, CISA does not endorse any commercial product or service. Please contact Schneider Electric CPCERT directly for any questions regarding this advisory. Revision History Initial Release Date: 2025-08-12 Date Revision Summary 2025-08-12 1 Original Release 2026-04-14 2 Remediation is available for Modicon M340 2026-08-11 3 Remediation is available for BMXNOR0200H. 2026-09-17 4 Initial CISA Republication of Schneider Electric CPCERT SEVD-2025-224-05 advisory Legal Notice and Terms of Use

Fix: Review CISA guidance and apply vendor security updates immediately.

Bransys ELD Important CISA Advisory
2026-09-17 CISA Advisory

Bransys ELD

View CSAF Summary Successful exploitation of these vulnerabilities could allow unauthorized access to telemetry data and firmware. The following versions of Bransys ELD are affected: Android iOS CVSS Vendor Equipment Vulnerabilities v3 7.5 Bransys Bransys ELD Use of Hard-coded Credentials, Cleartext Transmission of Sensitive Information Background Critical Infrastructure Sectors: Transportation Systems Countries/Areas Deployed: United States Company Headquarters Location: United States Vulnerabilities Expand All + CVE-2026-86520 The affected product is shipped with hardcoded MQTT credentials, which will grant read access to real-time data for every active device across a subset of carriers that were connected to the affected MQTT broker. View CVE Details Affected Products Bransys ELD Vendor: Bransys Product Version: Bransys Android: Product Status: known_affected Remediations Vendor fix Bransys recommends that users update their system through the app store. Android users should be on version 11.00.00 or newer. iOS users should be on version 1.1.54 or newer. Relevant CWE: CWE-798 Use of Hard-coded Credentials Metrics CVSS Version Base Score Base Severity Vector String 3.1 7.5 HIGH CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N 4.0 8.7 HIGH CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:H/VI:N/VA:N/SC:N/SI:N/SA:N CVE-2026-86689 The affected product is susceptible to cleartext transmission of sensitive information, which could allow an attacker to connect to the broker and read all data. View CVE Details Affected Products Bransys ELD Vendor: Bransys Product Version: Bransys Android: Product Status: known_affected Remediations Vendor fix Bransys recommends that users update their system through the app store. Android users should be on version 11.00.00 or newer. iOS users should be on version 1.1.54 or newer. Relevant CWE: CWE-319 Cleartext Transmission of Sensitive Information Metrics CVSS Version Base Score Base Severity Vector String 3.1 5.9 MEDIUM CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:N/A:N 4.0 8.2 HIGH CVSS:4.0/AV:N/AC:H/AT:P/PR:N/UI:N/VC:H/VI:N/VA:N/SC:N/SI:N/SA:N CVE-2026-77960 The affected product ships with hardcoded FTP credentials which could allow an attacker to connect to the server and read data. View CVE Details Affected Products Bransys ELD Vendor: Bransys Product Version: Bransys Android: Product Status: known_affected Remediations Vendor fix Bransys recommends that users update their system through the app store. Android users should be on version 11.00.00 or newer. iOS users should be on version 1.1.54 or newer. Relevant CWE: CWE-798 Use of Hard-coded Credentials Metrics CVSS Version Base Score Base Severity Vector String 3.1 5.3 MEDIUM CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:N/A:N 4.0 6.9 MEDIUM CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:L/VI:N/VA:N/SC:N/SI:N/SA:N Acknowledgments Jaime Lightfoot reported these vulnerabilities to CISA. Legal Notice and Terms of Use This product is provided subject to this Notification ( https://www.cisa.gov/notification ) and this Privacy & Use policy ( https://www.cisa.gov/privacy-policy ). Recommended Practices CISA recommends users take defensive measures to minimize the risk of exploitation of these vulnerabilities. Minimize network exposure for all control system devices and/or systems, ensuring they are not accessible from the internet. Locate control system networks and remote devices behind firewalls and isolating them from business networks. When remote access is required, use more secure methods, such as Virtual Private Networks (VPNs), recognizing VPNs may have vulnerabilities and should be updated to the most current version available. Also recognize VPN is only as secure as the connected devices. CISA reminds organizations to perform proper impact analysis and risk assessment prior to deploying defensive measures. CISA also provides a section for control systems security recommended practices on the ICS webpage on cisa.gov/ics. Several CISA products detailing cyber defense best practices are available for reading and download, including Improving Industrial Control Systems Cybersecurity with Defense-in-Depth Strategies. CISA encourages organizations to implement recommended cybersecurity strategies for proactive defense of ICS assets. Additional mitigation guidance and recommended practices are publicly available on the ICS webpage at cisa.gov/ics in the technical information paper, ICS-TIP-12-146-01B--Targeted Cyber Intrusion Detection and Mitigation Strategies. Organizations observing suspected malicious activity should follow established internal procedures and report findings to CISA for tracking and correlation against other incidents. CISA also recommends users take the following measures to protect themselves from social engineering attacks: Do not click web links or open attachments in unsolicited email messages. Refer to Recognizing and Avoiding Email Scams for more information on avoiding email scams. Refer to Avoiding Social Engineering and Phishing Attacks for more information on social engineering attacks. No known public exploitation specifically targeting these vulnerabilities has been reported to CISA at this time. Revision History Initial Release Date: 2026-09-17 Date Revision Summary 2026-09-17 1 Initial Publication Legal Notice and Terms of Use

Fix: Review CISA guidance and apply vendor security updates immediately.
Mitsubishi Electric GX Works3 and Motion Control Setting Important CISA Advisory
2026-09-17 CISA Advisory

Mitsubishi Electric GX Works3 and Motion Control Setting

View CSAF Summary Successful exploitation of this vulnerability could allow a local attacker to successfully authenticate even with an invalid block password by executing the affected product and modify part of the executable module in memory, and thereby allows the attacker to view, tamper with, destroy, or delete control programs. The following versions of Mitsubishi Electric GX Works3 and Motion Control Setting are affected: Mitsubishi Electric GX Works3 vers:all/* (CVE-2026-15688) Mitsubishi Electric Motion Control Setting (Software packaged with GX Works3) vers:all/* (CVE-2026-15688) CVSS Vendor Equipment Vulnerabilities v3 8.8 Mitsubishi Electric Mitsubishi Electric GX Works3 and Motion Control Setting Incorrect Implementation of Authentication Algorithm Background Critical Infrastructure Sectors: Critical Manufacturing Countries/Areas Deployed: Worldwide Company Headquarters Location: Japan Vulnerabilities Expand All + CVE-2026-15688 Incorrect Implementation of Authentication Algorithm (CWE-303) vulnerability in the affected products allows a local attacker to successfully authenticate even with an invalid block password by executing the affected product and modify part of the executable module in memory, and thereby allows the attacker to view, tamper with, destroy, or delete control programs. View CVE Details Affected Products Mitsubishi Electric GX Works3 and Motion Control Setting Vendor: Mitsubishi Electric Product Version: Mitsubishi Electric GX Works3: vers:all/*, Mitsubishi Electric Motion Control Setting (Software packaged with GX Works3): vers:all/* Product Status: known_affected Remediations Workaround For customers using GX Works3, please download version 1.096A or later from the link https://www.mitsubishielectric.com/fa/download/software/detailsearch.page?mode=software&kisyu=/plceng&shiryoid=1000001411&lang=2&select=0&softid=1&infostatus=1_2_1&viewradio=0&viewstatus=&viewpos=, install it, and set the security version for projects to "2". Please refer to “15.9 Preventing Illegal Access to/Falsification of Data (Security Version)” in “GX Works3 Operating Manual” for details. For more information about the workaround, refer to the Mitsubishi Electric security advisory available at "https://www.mitsubishielectric.com/psirt/vulnerability/pdf/2026-007_en.pdf". https://www.mitsubishielectric.com/fa/download/software/detailsearch.page?mode=software&kisyu=/plceng&shiryoid=1000001411&lang=2&select=0&softid=1&infostatus=1_2_1&viewradio=0&viewstatus=&viewpos= Workaround For customers using Motion Control Setting (Software packaged with GX Works3), Please download version 1.070Y or later from the link "https://www.mitsubishielectric.com/fa/download/software/detailsearch.page?mode=software&kisyu=/ssc&shiryoid=1000000803&lang=2&select=0&softid=1&infostatus=1_8_1&viewradio=0&viewstatus=&viewpos=", install it, and set the security version for projects to "2". Please refer to “12.5 Preventing Illegal Access to/Falsification of Data (Security Version)” in “Motion Control Setting Function Help” for details. For more information about the workaround, refer to the Mitsubishi Electric security advisory at "https://www.mitsubishielectric.com/psirt/vulnerability/pdf/2026-007_en.pdf". https://www.mitsubishielectric.com/fa/download/software/detailsearch.page?mode=software&kisyu=/ssc&shiryoid=1000000803&lang=2&select=0&softid=1&infostatus=1_8_1&viewradio=0&viewstatus=&viewpos= Mitigation For customers of the affected products, Mitsubishi Electric recommends using a computer with the affected product within a LAN and blocking remote logins from untrusted networks, hosts, and users, to minimize the risk of exploiting this vulnerability. Mitigation For customers of the affected products, Mitsubishi Electric recommends using a firewall, virtual private network (VPN), etc., to prevent unauthorized access, and allowing remote login only to trusted users when connecting a computer with the affected product to the Internet, to minimize the risk of exploiting this vulnerability. Mitigation For customers of the affected products, Mitsubishi Electric recommends preventing the user from clicking on web links contained in emails or other messages from untrusted sources, or from opening attachments in untrusted emails, to minimize the risk of exploiting this vulnerability. Mitigation For customers of the affected products, Mitsubishi Electric recommends installing antivirus software on a computer running the affected product, to minimize the risk of exploiting this vulnerability. Mitigation For customers of the affected products, Mitsubishi Electric recommends restricting physical access to a computer on which the affected product is installed, as well as to computers and network devices that can communicate with it, to minimize the risk of exploiting this vulnerability. Relevant CWE: CWE-303 Incorrect Implementation of Authentication Algorithm Metrics CVSS Version Base Score Base Severity Vector String 3.1 8.8 HIGH CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:C/C:H/I:H/A:H 4.0 9.2 CRITICAL CVSS:4.0/AV:L/AC:L/AT:N/PR:L/UI:N/VC:H/VI:H/VA:N/SC:N/SI:H/SA:H Acknowledgments Mayeul Fargier, Erwan Cordier, and Noé Flatreaud reported this vulnerability to Mitsubishi Electric Legal Notice and Terms of Use This product is provided subject to this Notification (https://www.cisa.gov/notification) and this Privacy & Use policy (https://www.cisa.gov/privacy-policy). Recommended Practices CISA recommends users take defensive measures to minimize the exploitation risk of these vulnerabilities. Minimize network exposure for all control system devices and/or systems, and ensure they are not accessible from the internet. Locate control system networks and remote devices behind firewalls and isolate them from business networks. When remote access is required, use more secure methods, such as Virtual Private Networks (VPNs), recognizing VPNs may have vulnerabilities and should be updated to the most recent version available. Also recognize VPN is only as secure as its connected devices. CISA reminds organizations to perform proper impact analysis and risk assessment prior to deploying defensive measures. CISA also provides a section for control systems security recommended practices on the ICS webpage on cisa.gov. Several CISA products detailing cyber defense best practices are available for reading and download, including Improving Industrial Control Systems Cybersecurity with Defense-in-Depth Strategies. CISA encourages organizations to implement recommended cybersecurity strategies for proactive defense of ICS assets. Additional mitigation guidance and recommended practices are publicly available on the ICS webpage at cisa.gov in the technical information paper, ICS-TIP-12-146-01B--Targeted Cyber Intrusion Detection and Mitigation Strategies. Organizations observing suspected malicious activity should follow established internal procedures and report findings to CISA for tracking and correlation against other incidents. Advisory Conversion Disclaimer This ICSA is a verbatim republication of Mitsubishi Electric 2026-007 from a direct conversion of the vendor's Common Security Advisory Framework (CSAF) advisory. This is republished to CISA's website as a means of increasing visibility and is provided "as-is" for informational purposes only. CISA is not responsible for the editorial or technical accuracy of republished advisories and provides no warranties of any kind regarding any information contained within this advisory. Further, CISA does not endorse any commercial product or service. Please contact Mitsubishi Electric directly for any questions regarding this advisory. Revision History Initial Release Date: 2026-09-17 Date Revision Summary 2026-09-17 1 Initial Publication 2026-09-17 2 Initial CISA Republication of Mitsubishi Electric 2026-007 advisory Legal Notice and Terms of Use

Fix: Review CISA guidance and apply vendor security updates immediately.
Notification