Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 5,807 advisories
Page 158 of 242
eBook: Identity-First Threat Intelligence Moderate Help Net Security
2026-09-15 Help Net Security

eBook: Identity-First Threat Intelligence

Attackers increasingly bypass traditional defenses by logging in with credentials that have already been stolen, exposed, or sold on the Dark Web. As infostealer malware accelerates credential theft, organizations need greater visibility into identity risk across Active Directory, IAM, and authentication environments. Download the e-book to explore: How info…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Give every teammate and agent the right level of access to your Workers Moderate Cloudflare Security
2026-09-15 Cloudflare Security

Give every teammate and agent the right level of access to your Workers

As more teams — and now agents — build applications on Cloudflare's Developer Platform, having the right access controls is crucial to allow you to ship safely. After all, the last thing you want is for an agent to make a change in production, just because it was granted more access than it needs. Now, you can give a teammate or agent access to a specific Wo…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Have it both ways: stay discoverable in search while disallowing AI training Moderate Cloudflare Security
2026-09-15 Cloudflare Security

Have it both ways: stay discoverable in search while disallowing AI training

Without proper controls, website owners have long faced a difficult tradeoff: allow your content to be used for AI training, or risk losing discoverability in search. That tradeoff exists because some of the largest organizations on the Internet use mixed-use crawlers: a single crawler serving both search and AI training. Refuse one, and you refuse the other…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
China spy chief points at US AI models in cyber threat warning Moderate The Record by Recorded Future
2026-09-15 The Record by Recorded Future

China spy chief points at US AI models in cyber threat warning

China's spy chief identified Anthropic’s Claude Mythos and OpenAI’s GPT-5.5-Cyber as signs of what he called a “disruptive upgrade” in cyber capabilities, increasing the speed and potential weaponization of vulnerability discovery and malware development.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Manhattan DA takes down 12 AI deepfake porn sites Moderate The Record by Recorded Future
2026-09-15 The Record by Recorded Future

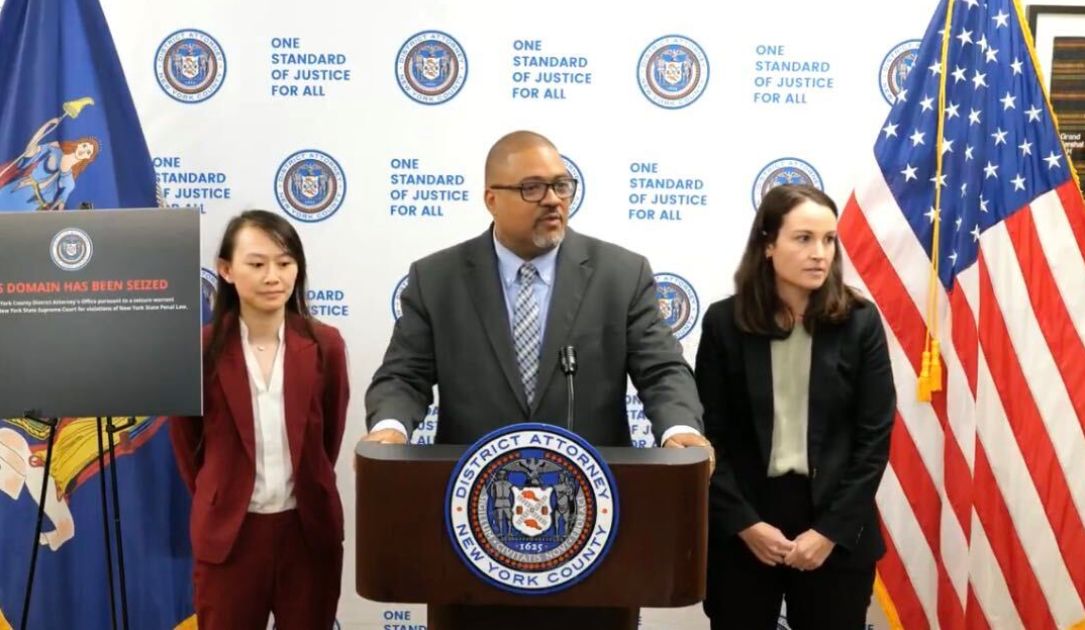
Manhattan DA takes down 12 AI deepfake porn sites

Manhattan District Attorney Alvin Bragg held a press conference on Monday touting the takedown of the sites, which hosted AI-generated videos of more than 1,200 people. The sites allowed users to use the faces and bodies of real people to create illegal pornography.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Uncensored AI sold on hacking forum as alternative to ChatGPT and Claude jailbreaks Moderate Help Net Security
2026-09-15 Help Net Security

Uncensored AI sold on hacking forum as alternative to ChatGPT and Claude jailbreaks

A new AI subscription service called Luciferus is being marketed on a hacking forum as an alternative to jailbreaking ChatGPT or Claude, Sophos found. The Counter Threat Unit (CTU) spotted the advertisement on August 24 on the Exploit forum, posted by a persona going by “Optimus_Prime.” The account joined the forum on April 18 and has since published 21 post…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CVE-2026-76461: Critical Cisco Secure Email Gateway Vulnerability Exploited in the Wild Critical CVE-2026-76461 Rapid7 Threat Research
2026-09-15 Rapid7 Threat Research

CVE-2026-76461: Critical Cisco Secure Email Gateway Vulnerability Exploited in the Wild

Overview On September 14, 2026, Cisco published a security advisory for CVE-2026-76461 , a critical SQL injection vulnerability affecting Cisco AsyncOS Software for Cisco Secure Email Gateway. The vulnerability has a reported CVSS v3.1 base score of 9.8 and could allow an unauthenticated, remote attacker to execute arbitrary commands with root privileges on …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Shared Hosting at Risk: LiteSpeed Enterprise Bug Can Grant Root from a Single Tenant Moderate CVE-2026-48172 SecurityAffairs
2026-09-15 SecurityAffairs

Shared Hosting at Risk: LiteSpeed Enterprise Bug Can Grant Root from a Single Tenant

Critical LiteSpeed Enterprise flaw lets one shared hosting account gain root, bypassing CageFS; patch now to 6.3.7 via forced update. cPanel warned that a critical flaw in LiteSpeed Enterprise can let a low‑privilege website user break out of their account and gain root on the whole server. On a box where dozens or hundreds of customers live side by side, th…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CISA: Critical VMware RCE flaw now exploited by ransomware gangs Critical BleepingComputer
2026-09-15 BleepingComputer

CISA: Critical VMware RCE flaw now exploited by ransomware gangs

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) warned security teams that ransomware gangs have now joined ongoing attacks exploiting a critical VMware vCenter vulnerability patched in July. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Siemens Reyrolle 7SR5 Important CISA Advisory
2026-09-15 CISA Advisory

Siemens Reyrolle 7SR5

View CSAF Summary Siemens Reyrolle 7SR5 Before V2.70 is affected by multiple vulnerabilities. Siemens has released a new version for Reyrolle 7SR5 and recommends to update to the latest version. The following versions of Siemens Reyrolle 7SR5 are affected: Reyrolle 7SR5 vers:intdot/ CVSS Vendor Equipment Vulnerabilities v3 9.8 Siemens Siemens Reyrolle 7SR5 Integer Overflow or Wraparound, Improper Neutralization of Delimiters, Use of Out-of-range Pointer Offset, Missing Authentication for Critical Function, Insufficient Entropy, Improper Input Validation, Out-of-bounds Write, Allocation of Resources Without Limits or Throttling, Authentication Bypass Using an Alternate Path or Channel, Insertion of Sensitive Information Into Debugging Code, Download of Code Without Integrity Check Background Critical Infrastructure Sectors: Energy Countries/Areas Deployed: Worldwide Company Headquarters Location: Germany Vulnerabilities Expand All + CVE-2024-42384 Integer Overflow or Wraparound vulnerability in Cesanta Mongoose Web Server v7.14 allows an attacker to send an unexpected TLS packet and produce a segmentation fault on the application. View CVE Details Affected Products Siemens Reyrolle 7SR5 Vendor: Siemens Product Version: Reyrolle 7SR5 Product Status: known_affected Remediations Vendor fix Update to V2.70 or later version https://support.industry.siemens.com/cs/ww/en/view/109772413/ Relevant CWE: CWE-190 Integer Overflow or Wraparound Metrics CVSS Version Base Score Base Severity Vector String 3.1 7.5 HIGH CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:H CVE-2024-42385 Improper Neutralization of Delimiters vulnerability in Cesanta Mongoose Web Server v7.14 allows to trigger an out-of-bound memory write if the PEM certificate contains unexpected characters. View CVE Details Affected Products Siemens Reyrolle 7SR5 Vendor: Siemens Product Version: Reyrolle 7SR5 Product Status: known_affected Remediations Vendor fix Update to V2.70 or later version https://support.industry.siemens.com/cs/ww/en/view/109772413/ Relevant CWE: CWE-140 Improper Neutralization of Delimiters Metrics CVSS Version Base Score Base Severity Vector String 3.1 4 MEDIUM CVSS:3.1/AV:L/AC:H/PR:H/UI:R/S:U/C:N/I:N/A:H CVE-2024-42386 Use of Out-of-range Pointer Offset vulnerability in Cesanta Mongoose Web Server v7.14 allows an attacker to send an unexpected TLS packet and produce a segmentation fault on the application. View CVE Details Affected Products Siemens Reyrolle 7SR5 Vendor: Siemens Product Version: Reyrolle 7SR5 Product Status: known_affected Remediations Vendor fix Update to V2.70 or later version https://support.industry.siemens.com/cs/ww/en/view/109772413/ Relevant CWE: CWE-823 Use of Out-of-range Pointer Offset Metrics CVSS Version Base Score Base Severity Vector String 3.1 8.2 HIGH CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:L/A:H CVE-2024-42391 Use of Out-of-range Pointer Offset vulnerability in Cesanta Mongoose Web Server v7.14 allows an attacker to send an unexpected TLS packet and force the application to read unintended heap memory space. View CVE Details Affected Products Siemens Reyrolle 7SR5 Vendor: Siemens Product Version: Reyrolle 7SR5 Product Status: known_affected Remediations Vendor fix Update to V2.70 or later version https://support.industry.siemens.com/cs/ww/en/view/109772413/ Relevant CWE: CWE-823 Use of Out-of-range Pointer Offset Metrics CVSS Version Base Score Base Severity Vector String 3.1 4.3 MEDIUM CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:U/C:L/I:N/A:N CVE-2024-42392 Improper Neutralization of Delimiters vulnerability in Cesanta Mongoose Web Server v7.14 allows to trigger an infinite loop bug if the input string contains unexpected characters. View CVE Details Affected Products Siemens Reyrolle 7SR5 Vendor: Siemens Product Version: Reyrolle 7SR5 Product Status: known_affected Remediations Vendor fix Update to V2.70 or later version https://support.industry.siemens.com/cs/ww/en/view/109772413/ Relevant CWE: CWE-140 Improper Neutralization of Delimiters Metrics CVSS Version Base Score Base Severity Vector String 3.1 4 MEDIUM CVSS:3.1/AV:L/AC:H/PR:H/UI:R/S:U/C:N/I:N/A:H CVE-2026-62645 Information is exposed through the web interface that can be used to calculate the current and past session ID numbers. This could allow an attacker to bypass the authentication and gain unauthorized access to the device. View CVE Details Affected Products Siemens Reyrolle 7SR5 Vendor: Siemens Product Version: Reyrolle 7SR5 Product Status: known_affected Remediations Vendor fix Update to V2.70 or later version https://support.industry.siemens.com/cs/ww/en/view/109772413/ Relevant CWE: CWE-306 Missing Authentication for Critical Function Metrics CVSS Version Base Score Base Severity Vector String 3.1 9.8 CRITICAL CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H CVE-2026-62646 A session identifier is generated using an algorithm with insufficient randomness, resulting in a token with low entropy that can be predicted or brute-forced within a feasible number of attempts. This could allow an unauthenticated remote attacker to derive valid session identifiers and bypass authentication. View CVE Details Affected Products Siemens Reyrolle 7SR5 Vendor: Siemens Product Version: Reyrolle 7SR5 Product Status: known_affected Remediations Vendor fix Update to V2.70 or later version https://support.industry.siemens.com/cs/ww/en/view/109772413/ Relevant CWE: CWE-331 Insufficient Entropy Metrics CVSS Version Base Score Base Severity Vector String 3.1 7.4 HIGH CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:N CVE-2026-62647 A random number generator is used to generate security-relevant values (such as session identifiers used for authentication purposes) that is not initialized with a True Random Number Generator (TRNG), resulting in a predictable sequence of generated values. This could allow an unauthenticated remote attacker to more easily predict the generated values and impersonate a legitimate authenticated user, potentially gaining unauthorized access to the device. View CVE Details Affected Products Siemens Reyrolle 7SR5 Vendor: Siemens Product Version: Reyrolle 7SR5 Product Status: known_affected Remediations Vendor fix Update to V2.70 or later version https://support.industry.siemens.com/cs/ww/en/view/109772413/ Relevant CWE: CWE-20 Improper Input Validation Metrics CVSS Version Base Score Base Severity Vector String 3.1 7.4 HIGH CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:N CVE-2026-62648 The length of the URL component contained in pre-authenticated HTTP messages is not properly validated before appending additional data to it, resulting in an out-of-bounds write condition in memory. This could allow an unauthenticated remote attacker to crash the affected device, causing a reboot and resulting in a denial-of-service condition. View CVE Details Affected Products Siemens Reyrolle 7SR5 Vendor: Siemens Product Version: Reyrolle 7SR5 Product Status: known_affected Remediations Vendor fix Update to V2.70 or later version https://support.industry.siemens.com/cs/ww/en/view/109772413/ Relevant CWE: CWE-787 Out-of-bounds Write Metrics CVSS Version Base Score Base Severity Vector String 3.1 7.5 HIGH CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:H CVE-2026-62649 The web server does not properly limit or manage system resources when processing a high volume of concurrent HTTP requests. This could allow an unauthenticated remote attacker to cause the entire device to crash and reboot, resulting in a denial-of-service condition. View CVE Details Affected Products Siemens Reyrolle 7SR5 Vendor: Siemens Product Version: Reyrolle 7SR5 Product Status: known_affected Remediations Vendor fix Update to V2.70 or later version https://support.industry.siemens.com/cs/ww/en/view/109772413/ Relevant CWE: CWE-770 Allocation of Resources Without Limits or Throttling Metrics CVSS Version Base Score Base Severity Vector String 3.1 7.5 HIGH CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:H CVE-2026-62650 Server-side authorization checks in the web-based management interface are not properly enforced, allowing role-based access control (RBAC) restrictions to be bypassed through manipulation of request data. This could allow an authenticated, low-privileged remote attacker to escalate privileges to an administrative level. View CVE Details Affected Products Siemens Reyrolle 7SR5 Vendor: Siemens Product Version: Reyrolle 7SR5 Product Status: known_affected Remediations Vendor fix Update to V2.70 or later version https://support.industry.siemens.com/cs/ww/en/view/109772413/ Relevant CWE: CWE-288 Authentication Bypass Using an Alternate Path or Channel Metrics CVSS Version Base Score Base Severity Vector String 3.1 8.8 HIGH CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H CVE-2026-62652 The device firmware contains binaries from which debugging symbols have not been removed. This could allow an unauthenticated attacker with access to the publicly available firmware update files to more easily reverse engineer the device's firmware, facilitating the identification of further vulnerabilities. View CVE Details Affected Products Siemens Reyrolle 7SR5 Vendor: Siemens Product Version: Reyrolle 7SR5 Product Status: known_affected Remediations Vendor fix Update to V2.70 or later version https://support.industry.siemens.com/cs/ww/en/view/109772413/ Relevant CWE: CWE-215 Insertion of Sensitive Information Into Debugging Code Metrics CVSS Version Base Score Base Severity Vector String 3.1 5.3 MEDIUM CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:N/A:N CVE-2026-62653 The input received over a proprietary communication protocol that is exposed when the device is placed into a special firmware-update mode is not properly validated, resulting in a memory corruption condition. This could allow an unauthenticated attacker with physical access to the device to cause a crash and potentially execute arbitrary code on the device. View CVE Details Affected Products Siemens Reyrolle 7SR5 Vendor: Siemens Product Version: Reyrolle 7SR5 Product Status: known_affected Remediations Vendor fix Update to V2.70 or later version https://support.industry.siemens.com/cs/ww/en/view/109772413/ Relevant CWE: CWE-787 Out-of-bounds Write Metrics CVSS Version Base Score Base Severity Vector String 3.1 6.8 MEDIUM CVSS:3.1/AV:P/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H CVE-2026-62654 A special maintenance mode can be activated via a physical key sequence during device boot, in which the device downloads and executes program code from a network server without verifying its authenticity or integrity. This could allow an attacker with physical access to the device to upload and execute arbitrary, unsigned code. View CVE Details Affected Products Siemens Reyrolle 7SR5 Vendor: Siemens Product Version: Reyrolle 7SR5 Product Status: known_affected Remediations Vendor fix Update to V2.70 or later version https://support.industry.siemens.com/cs/ww/en/view/109772413/ Relevant CWE: CWE-494 Download of Code Without Integrity Check Metrics CVSS Version Base Score Base Severity Vector String 3.1 6.8 MEDIUM CVSS:3.1/AV:P/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H Acknowledgments Siemens ProductCERT reported these vulnerabilities to CISA. General Recommendations Operators of critical power systems (e.g. TSOs or DSOs) worldwide are usually required by regulations to build resilience into the power grids by applying multi-level redundant secondary protection schemes. It is therefore recommended that the operators check whether appropriate resilient protection measures are in place. The risk of cyber incidents impacting the grid's reliability can thus be minimized by virtue of the grid design. Siemens strongly recommends applying the provided security updates using the corresponding tooling and documented procedures made available with the product. If supported by the product, an automated means to apply the security updates across multiple product instances may be used. Siemens strongly recommends prior validation of any security update before being applied, and supervision by trained staff of the update process in the target environment. As a general security measure Siemens strongly recommends protecting network access with appropriate mechanisms (e.g. firewalls, segmentation, VPN). It is advised to configure the environment according to our operational guidelines in order to run the devices in a protected IT environment. Recommended security guidelines can be found at: https://www.siemens.com/gridsecurity Additional Resources For further inquiries on security vulnerabilities in Siemens products and solutions, please contact the Siemens ProductCERT: https://www.siemens.com/cert/advisories Additional information on industrial security by Siemens can be found on the Siemens industrial security webpage For more information see the associated Siemens security advisory SSA-142885 in HTML and CSAF . Terms of Use The use of Siemens Security Advisories is subject to the terms and conditions listed on: https://www.siemens.com/productcert/terms-of-use . Legal Notice and Terms of Use This product is provided subject to this Notification ( https://www.cisa.gov/notification ) and this Privacy & Use policy ( https://www.cisa.gov/privacy-policy ). Recommended Practices CISA recommends users take defensive measures to minimize the exploitation risk of this vulnerability. Minimize network exposure for all control system devices and/or systems, and ensure they are not accessible from the internet. Locate control system networks and remote devices behind firewalls and isolate them from business networks. When remote access is required, use more secure methods, such as Virtual Private Networks (VPNs), recognizing VPNs may have vulnerabilities and should be updated to the most recent version available. Also recognize VPN is only as secure as its connected devices. CISA reminds organizations to perform proper impact analysis and risk assessment prior to deploying defensive measures. CISA also provides a section for control systems security recommended practices on the ICS webpage on cisa.gov. Several CISA products detailing cyber defense best practices are available for reading and download, including Improving Industrial Control Systems Cybersecurity with Defense-in-Depth Strategies. CISA encourages organizations to implement recommended cybersecurity strategies for proactive defense of ICS assets. Additional mitigation guidance and recommended practices are publicly available on the ICS webpage at cisa.gov in the technical information paper, ICS-TIP-12-146-01B--Targeted Cyber Intrusion Detection and Mitigation Strategies. Organizations observing suspected malicious activity should follow established internal procedures and report findings to CISA for tracking and correlation against other incidents. Advisory Conversion Disclaimer This ICSA is a verbatim republication of Siemens ProductCERT SSA-142885 from a direct conversion of the vendor's Common Security Advisory Framework (CSAF) advisory. This is republished to CISA's website as a means of increasing visibility and is provided "as-is" for informational purposes only. CISA is not responsible for the editorial or technical accuracy of republished advisories and provides no warranties of any kind regarding any information contained within this advisory. Further, CISA does not endorse any commercial product or service. Please contact Siemens ProductCERT directly for any questions regarding this advisory. Revision History Initial Release Date: 2026-09-08 Date Revision Summary 2026-09-08 1 Publication Date 2026-09-15 2 Initial CISA Republication of Siemens ProductCERT SSA-142885 advisory Legal Notice and Terms of Use

Fix: Review CISA guidance and apply vendor security updates immediately.

Schneider Electric SCADAPack x70 Products Important CISA Advisory
2026-09-15 CISA Advisory

Schneider Electric SCADAPack x70 Products

View CSAF Summary Schneider Electric is aware of a vulnerability in its SCADAPack x70 products. The SCADAPack 47x, SCADAPack 47xi, SCADAPack 47xd, SCADAPack 470R and SCADAPack 57x products are Remote Terminal Units that provide communication capabilities for remote monitoring and control. Failure to apply the mitigations provided below may increase the risk of unauthorized access to RTU configuration through the Secure Lock functionality, potentially resulting in a loss of confidentiality. The following versions of Schneider Electric SCADAPack x70 Products are affected: SCADAPack 47x vers:all/* (CVE-2026-81861) SCADAPack 47xi vers:all/* (CVE-2026-81861) SCADAPack 47xd vers:all/* (CVE-2026-81861) SCADAPack 470R vers:all/* (CVE-2026-81861) SCADAPack 57x vers:all/* (CVE-2026-81861) SCADAPack 3xx vers:all/* (CVE-2026-81861) SCADAPack 32 vers:all/* (CVE-2026-81861) CVSS Vendor Equipment Vulnerabilities v3 6.5 Schneider Electric Schneider Electric SCADAPack x70 Products Insufficiently Protected Credentials Background Critical Infrastructure Sectors: Critical Manufacturing, Energy Countries/Areas Deployed: Worldwide Company Headquarters Location: France Vulnerabilities Expand All + CVE-2026-81861 There is an insufficiently protected credentials vulnerability that could result in exposure of authentication information and unauthorized access to RTU functionality. View CVE Details Affected Products Schneider Electric SCADAPack x70 Products Vendor: Schneider Electric Product Version: SCADAPack 47x, SCADAPack 47xi, SCADAPack 47xd, SCADAPack 470R, SCADAPack 57x, SCADAPack 3xx, SCADAPack 32 Product Status: known_affected Remediations Mitigation Implement the Role-Based Access Control (RBAC) feature and follow the SCADAPack documentation sections Security Guidelines for Administrators and Working with Role-Based Access Control. RBAC is the recommended access control mechanism for SCADAPack 47x devices and should be used in place of the Secure Lock feature. The Secure Lock feature is legacy functionality retained for backward compatibility with existing deployments and should only be used where required to support legacy system requirements. Consult the SCADAPack Cybersecurity Guide, including the SCADAPack Hardening and Secured Communication sections. In addition, apply the following standard practices to reduce the risk of exploitation: Configure network segmentation to restrict access between trusted and untrusted networks. Enable and implement the RTU firewall service to restrict unauthorized access to device services and reduce the attack surface. Documentation available in RemoteConnect and SCADAPack x70 Utilities | Schneider Electric https://www.se.com/ww/en/download/document/RemoteConnect/ Mitigation Ensure setup of network segmentation to restrict access between trusted and untrusted networks and implementation of the RTU Firewall Service to restrict unauthorized access to services. Consult the SCADAPack Cybersecurity Guide, including the SCADAPack Hardening and Secured Communication sections. In addition, implement all best practices referenced in the SCADAPack Cybersecurity Guide. Documentation available in RemoteConnect and SCADAPack x70 Utilities | Schneider Electric https://www.se.com/ww/en/download/document/RemoteConnect/ Mitigation For more information see the associated Schneider Electric security advisory SEVD-2026-251-03 Insufficiently Protected Credentials vulnerability on SCADAPack x70 Products PDF Version , CSAF Version . Relevant CWE: CWE-522 Insufficiently Protected Credentials Metrics CVSS Version Base Score Base Severity Vector String 3.1 6.5 MEDIUM CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:U/C:H/I:N/A:N Acknowledgments Abhinav Agarwal reported this vulnerability to CISA. General Security Recommendations Schneider Electric strongly recommends the following industry cybersecurity best practices: Locate control and safety system networks and remote devices behind firewalls and isolate them from the business network. Install physical controls so no unauthorized personnel can access your industrial control and safety systems, components, peripheral equipment, and networks. Place all controllers in locked cabinets and never leave them in the “Program” mode. Never connect programming software to any network other than the network intended for that device. Scan all methods of mobile data exchange with the isolated network such as CDs, USB drives, etc. before use in the terminals or any node connected to these networks. Never allow mobile devices that have connected to any other network besides the intended network to connect to the safety or control networks without proper sanitation. Minimize network exposure for all control system devices and systems and ensure that they are not accessible from the Internet. When remote access is required, use secure methods, such as virtual private networks (VPNs). Recognize that VPNs may have vulnerabilities and should be updated to the most current version available. Also, understand that VPNs are only as secure as the connected devices. For more information refer to the Schneider Electric Recommended Cybersecurity Best Practices document. For More Information This document provides an overview of the identified vulnerability or vulnerabilities and actions required to mitigate. For more details and assistance on how to protect your installation, contact your local Schneider Electric representative or Schneider Electric Industrial Cybersecurity Services: https://www.se.com/ww/en/work/solutions/cybersecurity/ . These organizations will be fully aware of this situation and can support you through the process. For further information related to cybersecurity in Schneider Electric's products, visit the company's cybersecurity support portal page: https://www.se.com/ww/en/work/support/cybersecurity/overview.js p LEGAL DISCLAIMER THIS NOTIFICATION DOCUMENT, THE INFORMATION CONTAINED HEREIN, AND ANY MATERIALS LINKED FROM IT (COLLECTIVELY, THIS “NOTIFICATION”) ARE INTENDED TO HELP PROVIDE AN OVERVIEW OF THE IDENTIFIED SITUATION AND SUGGESTED MITIGATION ACTIONS, REMEDIATION, FIX, AND/OR GENERAL SECURITY RECOMMENDATIONS AND IS PROVIDED ON AN “AS-IS” BASIS WITHOUT WARRANTY OR GUARANTEE OF ANY KIND. SCHNEIDER ELECTRIC DISCLAIMS ALL WARRANTIES RELATING TO THIS NOTIFICATION, EITHER EXPRESS OR IMPLIED, INCLUDING WARRANTIES OF MERCHANTABILITY OR FITNESS FOR A PARTICULAR PURPOSE. SCHNEIDER ELECTRIC MAKES NO WARRANTY THAT THE NOTIFICATION WILL RESOLVE THE IDENTIFIED SITUATION. IN NO EVENT SHALL SCHNEIDER ELECTRIC BE LIABLE FOR ANY DAMAGES OR LOSSES WHATSOEVER IN CONNECTION WITH THIS NOTIFICATION, INCLUDING DIRECT, INDIRECT, INCIDENTAL, CONSEQUENTIAL, LOSS OF BUSINESS PROFITS OR SPECIAL DAMAGES, EVEN IF SCHNEIDER ELECTRIC HAS BEEN ADVISED OF THE POSSIBILITY OF SUCH DAMAGES. YOUR USE OF THIS NOTIFICATION IS AT YOUR OWN RISK, AND YOU ARE SOLELY LIABLE FOR ANY DAMAGES TO YOUR SYSTEMS OR ASSETS OR OTHER LOSSES THAT MAY RESULT FROM YOUR USE OF THIS NOTIFICATION. SCHNEIDER ELECTRIC RESERVES THE RIGHT TO UPDATE OR CHANGE THIS NOTIFICATION AT ANY TIME AND IN ITS SOLE DISCRETION About Schneider Electric Schneider's purpose is to create Impact by empowering all to make the most of our energy and resources, bridging progress and sustainability for all. We call this Life Is On. Our mission is to be the trusted partner in Sustainability and Efficiency. We are a global industrial technology leader bringing world-leading expertise in electrification, automation and digitization to smart industries, resilient infrastructure, future-proof data centers, intelligent buildings, and intuitive homes. Anchored by our deep domain expertise, we provide integrated end-to-end lifecycle AI enabled Industrial IoT solutions with connected products, automation, software and services, delivering digital twins to enable profitable growth for our customers. We are a people company with an ecosystem of 150,000 colleagues and more than a million partners operating in over 100 countries to ensure proximity to our customers and stakeholders. We embrace diversity and inclusion in everything we do, guided by our meaningful purpose of a sustainable future for all. www.se.com Legal Notice and Terms of Use This product is provided subject to this Notification ( https://www.cisa.gov/notification ) and this Privacy & Use policy ( https://www.cisa.gov/privacy-policy ). Recommended Practices CISA recommends users take defensive measures to minimize the exploitation risk of these vulnerabilities. Minimize network exposure for all control system devices and/or systems, and ensure they are not accessible from the internet. Locate control system networks and remote devices behind firewalls and isolate them from business networks. When remote access is required, use more secure methods, such as virtual private networks (VPNs), recognizing VPNs may have vulnerabilities and should be updated to the most recent version available. Also recognize VPN is only as secure as its connected devices. CISA reminds organizations to perform proper impact analysis and risk assessment prior to deploying defensive measures. CISA also provides a section for control systems security recommended practices on the ICS webpage on cisa.gov. Several CISA products detailing cyber defense best practices are available for reading and download, including Improving Industrial Control Systems Cybersecurity with Defense-in-Depth Strategies. CISA encourages organizations to implement recommended cybersecurity strategies for proactive defense of ICS assets. Additional mitigation guidance and recommended practices are publicly available on the ICS webpage at cisa.gov in the technical information paper, ICS-TIP-12-146-01B--Targeted Cyber Intrusion Detection and Mitigation Strategies. Organizations observing suspected malicious activity should follow established internal procedures and report findings to CISA for tracking and correlation against other incidents. Advisory Conversion Disclaimer This ICSA is a verbatim republication of Schneider Electric CPCERT SEVD-2026-251-03 from a direct conversion of the vendor's Common Security Advisory Framework (CSAF) advisory. This is republished to CISA's website as a means of increasing visibility and is provided "as-is" for informational purposes only. CISA is not responsible for the editorial or technical accuracy of republished advisories and provides no warranties of any kind regarding any information contained within this advisory. Further, CISA does not endorse any commercial product or service. Please contact Schneider Electric CPCERT directly for any questions regarding this advisory. Revision History Initial Release Date: 2026-09-08 Date Revision Summary 2026-09-08 1 Original Release 2026-09-15 2 Initial CISA Republication of Schneider Electric SEVD-2026-251-03 advisory Legal Notice and Terms of Use

Fix: Review CISA guidance and apply vendor security updates immediately.
Digital Watchdog VMAX DVR and NVR Product Lineups Important CISA Advisory
2026-09-15 CISA Advisory

Digital Watchdog VMAX DVR and NVR Product Lineups

View CSAF Summary Successful exploitation of these vulnerabilities could grant full administrative control of the device, allowing an attacker to view live and recorded surveillance, alter device configurations, and use the device as a network pivot point. The following versions of Digital Watchdog VMAX DVR and NVR Product Lineups are affected: VMAX A1 G4 DVRs vers:all/* (CVE-2026-68953, CVE-2026-66890, CVE-2026-68070, CVE-2026-68950, CVE-2026-66887, CVE-2026-66372) VMAX IP G4 NVRs vers:all/* (CVE-2026-68953, CVE-2026-66890, CVE-2026-68070, CVE-2026-68950, CVE-2026-66887, CVE-2026-66372) VMAX A1 PLUS vers:all/* (CVE-2026-68953, CVE-2026-66890, CVE-2026-68070, CVE-2026-68950, CVE-2026-66887, CVE-2026-66372) VA1G4 Recorder vers:all/* (CVE-2026-68953, CVE-2026-66890, CVE-2026-68070, CVE-2026-68950, CVE-2026-66887, CVE-2026-66372) VG4 Recorder vers:all/* (CVE-2026-68953, CVE-2026-66890, CVE-2026-68070, CVE-2026-68950, CVE-2026-66887, CVE-2026-66372) CVSS Vendor Equipment Vulnerabilities v3 9.6 Digital Watchdog Digital Watchdog VMAX DVR and NVR Product Lineups Missing Authentication for Critical Function, Use of Hard-coded Credentials, Missing Authorization, Predictable Seed in Pseudo-Random Number Generator (PRNG) Background Critical Infrastructure Sectors: Commercial Facilities, Government Services and Facilities, Healthcare and Public Health, Transportation Systems Countries/Areas Deployed: Worldwide Company Headquarters Location: United States Vulnerabilities Expand All + CVE-2026-68953 The affected products are vulnerable to an authentication bypass that allows unauthenticated remote attackers to disclose sensitive device information, including administrator credentials in plaintext, by sending crafted HTTP(S) requests. View CVE Details Affected Products Digital Watchdog VMAX DVR and NVR Product Lineups Vendor: Digital Watchdog Product Version: Digital Watchdog VMAX A1 G4 DVRs: vers:all/*, Digital Watchdog VMAX IP G4 NVRs: vers:all/*, Digital Watchdog VMAX A1 PLUS: vers:all/*, Digital Watchdog VA1G4 Recorder: vers:all/*, Digital Watchdog VG4 Recorder: vers:all/* Product Status: known_affected Remediations Mitigation Digital Watchdog has released updated firmware for the affected products. Users should download and install the updated firmware for their model at: https://digital-watchdog.com/downloads/ Relevant CWE: CWE-306 Missing Authentication for Critical Function Metrics CVSS Version Base Score Base Severity Vector String 3.1 6.5 MEDIUM CVSS:3.1/AV:A/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N 4.0 7.1 HIGH CVSS:4.0/AV:A/AC:L/AT:N/PR:N/UI:N/VC:H/VI:N/VA:N/SC:N/SI:N/SA:N CVE-2026-66890 The affected products use hard-coded credentials, which could allow remote access to files with root privileges where FTP is reachable. View CVE Details Affected Products Digital Watchdog VMAX DVR and NVR Product Lineups Vendor: Digital Watchdog Product Version: Digital Watchdog VMAX A1 G4 DVRs: vers:all/*, Digital Watchdog VMAX IP G4 NVRs: vers:all/*, Digital Watchdog VMAX A1 PLUS: vers:all/*, Digital Watchdog VA1G4 Recorder: vers:all/*, Digital Watchdog VG4 Recorder: vers:all/* Product Status: known_affected Remediations Mitigation Digital Watchdog has released updated firmware for the affected products. Users should download and install the updated firmware for their model at: https://digital-watchdog.com/downloads/ Relevant CWE: CWE-798 Use of Hard-coded Credentials Metrics CVSS Version Base Score Base Severity Vector String 3.1 9.6 CRITICAL CVSS:3.1/AV:A/AC:L/PR:N/UI:N/S:C/C:H/I:H/A:H 4.0 9.4 CRITICAL CVSS:4.0/AV:A/AC:L/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H/SC:H/SI:H/SA:H CVE-2026-68070 The affected products are missing authentication for a critical function, which could allow an attacker to run as root and pass received bytes directly to a system command. View CVE Details Affected Products Digital Watchdog VMAX DVR and NVR Product Lineups Vendor: Digital Watchdog Product Version: Digital Watchdog VMAX A1 G4 DVRs: vers:all/*, Digital Watchdog VMAX IP G4 NVRs: vers:all/*, Digital Watchdog VMAX A1 PLUS: vers:all/*, Digital Watchdog VA1G4 Recorder: vers:all/*, Digital Watchdog VG4 Recorder: vers:all/* Product Status: known_affected Remediations Mitigation Digital Watchdog has released updated firmware for the affected products. Users should download and install the updated firmware for their model at: https://digital-watchdog.com/downloads/ Relevant CWE: CWE-306 Missing Authentication for Critical Function Metrics CVSS Version Base Score Base Severity Vector String 3.1 8.8 HIGH CVSS:3.1/AV:A/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H 4.0 8.7 HIGH CVSS:4.0/AV:A/AC:L/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N CVE-2026-68950 The affected products use hard-coded credentials, which could allow an attacker to run the ftpd service as root, providing remote root file access where FTP is reachable. View CVE Details Affected Products Digital Watchdog VMAX DVR and NVR Product Lineups Vendor: Digital Watchdog Product Version: Digital Watchdog VMAX A1 G4 DVRs: vers:all/*, Digital Watchdog VMAX IP G4 NVRs: vers:all/*, Digital Watchdog VMAX A1 PLUS: vers:all/*, Digital Watchdog VA1G4 Recorder: vers:all/*, Digital Watchdog VG4 Recorder: vers:all/* Product Status: known_affected Remediations Mitigation Digital Watchdog has released updated firmware for the affected products. Users should download and install the updated firmware for their model at: https://digital-watchdog.com/downloads/ Relevant CWE: CWE-798 Use of Hard-coded Credentials Metrics CVSS Version Base Score Base Severity Vector String 3.1 8.8 HIGH CVSS:3.1/AV:A/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H 4.0 8.7 HIGH CVSS:4.0/AV:A/AC:L/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N CVE-2026-66887 The affected products are missing authorization on state-changing CGIs and session checks are not performed. View CVE Details Affected Products Digital Watchdog VMAX DVR and NVR Product Lineups Vendor: Digital Watchdog Product Version: Digital Watchdog VMAX A1 G4 DVRs: vers:all/*, Digital Watchdog VMAX IP G4 NVRs: vers:all/*, Digital Watchdog VMAX A1 PLUS: vers:all/*, Digital Watchdog VA1G4 Recorder: vers:all/*, Digital Watchdog VG4 Recorder: vers:all/* Product Status: known_affected Remediations Mitigation Digital Watchdog has released updated firmware for the affected products. Users should download and install the updated firmware for their model at: https://digital-watchdog.com/downloads/ Relevant CWE: CWE-862 Missing Authorization Metrics CVSS Version Base Score Base Severity Vector String 3.1 9.6 CRITICAL CVSS:3.1/AV:A/AC:L/PR:N/UI:N/S:C/C:H/I:H/A:H 4.0 9.4 CRITICAL CVSS:4.0/AV:A/AC:L/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H/SC:H/SI:H/SA:H CVE-2026-66372 The affected products use insufficiently random values, which allows web session tokens to be predictable, bounding token entropy to the seed space. View CVE Details Affected Products Digital Watchdog VMAX DVR and NVR Product Lineups Vendor: Digital Watchdog Product Version: Digital Watchdog VMAX A1 G4 DVRs: vers:all/*, Digital Watchdog VMAX IP G4 NVRs: vers:all/*, Digital Watchdog VMAX A1 PLUS: vers:all/*, Digital Watchdog VA1G4 Recorder: vers:all/*, Digital Watchdog VG4 Recorder: vers:all/* Product Status: known_affected Remediations Mitigation Digital Watchdog has released updated firmware for the affected products. Users should download and install the updated firmware for their model at: https://digital-watchdog.com/downloads/ Relevant CWE: CWE-337 Predictable Seed in Pseudo-Random Number Generator (PRNG) Metrics CVSS Version Base Score Base Severity Vector String 3.1 6.8 MEDIUM CVSS:3.1/AV:A/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:N 4.0 7.6 HIGH CVSS:4.0/AV:A/AC:H/AT:N/PR:N/UI:N/VC:H/VI:H/VA:N/SC:N/SI:N/SA:N Acknowledgments Scot Berner of TrustedSec reported these vulnerabilities to CISA. Legal Notice and Terms of Use This product is provided subject to this Notification ( https://www.cisa.gov/notification ) and this Privacy & Use policy ( https://www.cisa.gov/privacy-policy ). Recommended Practices CISA recommends users take defensive measures to minimize the risk of exploitation of these vulnerabilities. Minimize network exposure for all control system devices and/or systems, ensuring they are not accessible from the Internet. Locate control system networks and remote devices behind firewalls and isolating them from business networks. When remote access is required, use more secure methods, such as Virtual Private Networks (VPNs), recognizing VPNs may have vulnerabilities and should be updated to the most current version available. Also recognize VPN is only as secure as the connected devices. CISA reminds organizations to perform proper impact analysis and risk assessment prior to deploying defensive measures. CISA also provides a section for control systems security recommended practices on the ICS webpage on cisa.gov/ics. Several CISA products detailing cyber defense best practices are available for reading and download, including Improving Industrial Control Systems Cybersecurity with Defense-in-Depth Strategies. CISA encourages organizations to implement recommended cybersecurity strategies for proactive defense of ICS assets. Additional mitigation guidance and recommended practices are publicly available on the ICS webpage at cisa.gov/ics in the technical information paper, ICS-TIP-12-146-01B--Targeted Cyber Intrusion Detection and Mitigation Strategies. Organizations observing suspected malicious activity should follow established internal procedures and report findings to CISA for tracking and correlation against other incidents. CISA also recommends users take the following measures to protect themselves from social engineering attacks: Do not click web links or open attachments in unsolicited email messages. Refer to Recognizing and Avoiding Email Scams for more information on avoiding email scams. Refer to Avoiding Social Engineering and Phishing Attacks for more information on social engineering attacks. No known public exploitation specifically targeting these vulnerabilities has been reported to CISA at this time. These vulnerabilities are not exploitable remotely. Revision History Initial Release Date: 2026-09-15 Date Revision Summary 2026-09-15 1 Initial Publication Legal Notice and Terms of Use

Fix: Review CISA guidance and apply vendor security updates immediately.
Siemens Teamcenter Important CISA Advisory
2026-09-15 CISA Advisory

Siemens Teamcenter

View CSAF Summary A reflected cross site scripting vulnerability in the authentication redirect flow (/auth/) of Teamcenter allows an unauthenticated remote attacker to inject JavaScript into an authenticated user's session by crafting a malicious URL. Successful exploitation may enable the attacker to read data or perform actions within the victim's Teamcenter session. Siemens has released new versions for the affected products and recommends to update to the latest versions. The following versions of Siemens Teamcenter are affected: Teamcenter V2412 vers:intdot/ Teamcenter V2506 vers:intdot/ Teamcenter V2512 vers:intdot/ Teamcenter V2606 vers:intdot/ CVSS Vendor Equipment Vulnerabilities v3 6.1 Siemens Siemens Teamcenter Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') Background Critical Infrastructure Sectors: Critical Manufacturing, Information Technology Countries/Areas Deployed: Worldwide Company Headquarters Location: Germany Vulnerabilities Expand All + CVE-2026-58113 Affected applications do not properly encode user-supplied input reflected into HTML attribute contexts within the authentication redirect flow (/auth/ endpoint). This could allow an unauthenticated remote attacker to inject arbitrary JavaScript into the browser of an authenticated user who loads a crafted URL, enabling the attacker to perform actions within the victim's Teamcenter session. View CVE Details Affected Products Siemens Teamcenter Vendor: Siemens Product Version: Teamcenter V2412 Product Status: known_affected Remediations Vendor fix Update to V2412.0013 or later version https://support.sw.siemens.com/product/282219420/ Vendor fix Update to V2506.0010 or later version https://support.sw.siemens.com/product/282219420/ Vendor fix Update to V2512.2607 or later version https://support.sw.siemens.com/product/282219420/ Vendor fix Update to V2606.2607 or later version https://support.sw.siemens.com/product/282219420/ Relevant CWE: CWE-79 Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') Metrics CVSS Version Base Score Base Severity Vector String 3.1 6.1 MEDIUM CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N Acknowledgments Enzo Alvarez from Bishop Fox reported this vulnerability to Siemens. General Recommendations As a general security measure, Siemens recommends protecting network access to devices with appropriate mechanisms. To operate the devices in a protected IT environment, Siemens recommends configuring the environment according to Siemens' operational guidelines for industrial security and following recommendations in the product manuals. Additional information on Industrial Security by Siemens can be found at: https://www.siemens.com/industrialsecurity Additional Resources For further inquiries on security vulnerabilities in Siemens products and solutions, please contact the Siemens ProductCERT: https://www.siemens.com/cert/advisories Additional information on industrial security by Siemens can be found on the Siemens industrial security webpage For more information see the associated Siemens security advisory SSA-157465 in HTML and CSAF . Terms of Use The use of Siemens Security Advisories is subject to the terms and conditions listed on: https://www.siemens.com/productcert/terms-of-use . Legal Notice and Terms of Use This product is provided subject to this Notification ( https://www.cisa.gov/notification ) and this Privacy & Use policy ( https://www.cisa.gov/privacy-policy ). Recommended Practices CISA recommends users take defensive measures to minimize the exploitation risk of these vulnerabilities. Minimize network exposure for all control system devices and/or systems, and ensure they are not accessible from the internet. Locate control system networks and remote devices behind firewalls and isolate them from business networks. When remote access is required, use more secure methods, such as Virtual Private Networks (VPNs), recognizing VPNs may have vulnerabilities and should be updated to the most recent version available. Also recognize VPN is only as secure as its connected devices. CISA reminds organizations to perform proper impact analysis and risk assessment prior to deploying defensive measures. CISA also provides a section for control systems security recommended practices on the ICS webpage on cisa.gov. Several CISA products detailing cyber defense best practices are available for reading and download, including Improving Industrial Control Systems Cybersecurity with Defense-in-Depth Strategies. CISA encourages organizations to implement recommended cybersecurity strategies for proactive defense of ICS assets. Additional mitigation guidance and recommended practices are publicly available on the ICS webpage at cisa.gov in the technical information paper, ICS-TIP-12-146-01B--Targeted Cyber Intrusion Detection and Mitigation Strategies. Organizations observing suspected malicious activity should follow established internal procedures and report findings to CISA for tracking and correlation against other incidents. Advisory Conversion Disclaimer This ICSA is a verbatim republication of Siemens ProductCERT SSA-157465 from a direct conversion of the vendor's Common Security Advisory Framework (CSAF) advisory. This is republished to CISA's website as a means of increasing visibility and is provided "as-is" for informational purposes only. CISA is not responsible for the editorial or technical accuracy of republished advisories and provides no warranties of any kind regarding any information contained within this advisory. Further, CISA does not endorse any commercial product or service. Please contact Siemens ProductCERT directly for any questions regarding this advisory. Revision History Initial Release Date: 2026-09-08 Date Revision Summary 2026-09-08 1 Publication Date 2026-09-15 2 Initial CISA Republication of Siemens ProductCERT SSA-157465 advisory Legal Notice and Terms of Use

Fix: Review CISA guidance and apply vendor security updates immediately.
CareCam CM2507 Important CISA Advisory
2026-09-15 CISA Advisory

CareCam CM2507

View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to access live video and sensitive device information, enable unauthorized services, execute arbitrary code, modify device operation, and recover stored credentials. The following versions of CareCam CM2507 are affected: HMT.CM2507 Firmware v251211.1507 (CVE-2026-88259, CVE-2026-84398, CVE-2026-84400, CVE-2026-81305, CVE-2026-85478, CVE-2026-85497, CVE-2026-81321) CVSS Vendor Equipment Vulnerabilities v3 7.5 CareCam CareCam CM2507 Missing Authentication for Critical Function, Empty Password in Configuration File, Inclusion of Functionality from Untrusted Control Sphere, Use of Password Hash With Insufficient Computational Effort, Cleartext Storage of Sensitive Information Background Critical Infrastructure Sectors: Commercial Facilities Countries/Areas Deployed: Worldwide Company Headquarters Location: China Vulnerabilities Expand All + CVE-2026-88259 CareCam CM2507 IP cameras do not require authentication for access to its network video streaming service. An unauthenticated attacker with network access to the affected device could retrieve live camera video. View CVE Details Affected Products CareCam CM2507 Vendor: CareCam Product Version: CareCam HMT.CM2507 Firmware: v251211.1507 Product Status: known_affected Remediations Mitigation CareCam has not responded to CISA's attempts to coordinate. Users are encouraged to reach out to CareCam for more information. Relevant CWE: CWE-306 Missing Authentication for Critical Function Metrics CVSS Version Base Score Base Severity Vector String 3.1 7.5 HIGH CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N 4.0 8.7 HIGH CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:H/VI:N/VA:N/SC:N/SI:N/SA:N CVE-2026-84398 CM2507 IP cameras accept an empty password for a privileged account exposed through its ONVIF management service. An attacker with network access to the affected device could access privileged management functions and obtain device, user, media-profile, and stream configuration information. View CVE Details Affected Products CareCam CM2507 Vendor: CareCam Product Version: CareCam HMT.CM2507 Firmware: v251211.1507 Product Status: known_affected Remediations Mitigation CareCam has not responded to CISA's attempts to coordinate. Users are encouraged to reach out to CareCam for more information. Relevant CWE: CWE-258 Empty Password in Configuration File Metrics CVSS Version Base Score Base Severity Vector String 3.1 7.5 HIGH CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N 4.0 8.7 HIGH CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:H/VI:N/VA:N/SC:N/SI:N/SA:N CVE-2026-84400 CareCam CM2507 IP cameras contain an insufficiently protected network maintenance mechanism that can activate a remote debugging service. An attacker on the same local network who satisfies certain device state conditions could make the service remotely accessible, increasing the risk of unauthorized administrative access. View CVE Details Affected Products CareCam CM2507 Vendor: CareCam Product Version: CareCam HMT.CM2507 Firmware: v251211.1507 Product Status: known_affected Remediations Mitigation CareCam has not responded to CISA's attempts to coordinate. Users are encouraged to reach out to CareCam for more information. Relevant CWE: CWE-306 Missing Authentication for Critical Function Metrics CVSS Version Base Score Base Severity Vector String 3.1 3.1 LOW CVSS:3.1/AV:A/AC:H/PR:N/UI:N/S:U/C:N/I:L/A:N 4.0 2.3 LOW CVSS:4.0/AV:A/AC:L/AT:P/PR:N/UI:N/VC:N/VI:L/VA:N/SC:N/SI:N/SA:N CVE-2026-81305 CM2507 IP cameras automatically execute a predetermined script from removable media without verifying its authenticity or integrity. An attacker with physical access to the device could supply a malicious script and execute arbitrary code in the security context of the affected device. View CVE Details Affected Products CareCam CM2507 Vendor: CareCam Product Version: CareCam HMT.CM2507 Firmware: v251211.1507 Product Status: known_affected Remediations Mitigation CareCam has not responded to CISA's attempts to coordinate. Users are encouraged to reach out to CareCam for more information. Relevant CWE: CWE-829 Inclusion of Functionality from Untrusted Control Sphere Metrics CVSS Version Base Score Base Severity Vector String 3.1 6.8 MEDIUM CVSS:3.1/AV:P/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H 4.0 7 HIGH CVSS:4.0/AV:P/AC:L/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N CVE-2026-85478 A CM2507 IP camera running firmware version HMT.CM2507 v251211.1507 exposes an interactive bootloader through a physical debug interface without requiring authentication. An attacker with physical access could interrupt the normal boot process and access functionality that permits inspection or modification of boot configuration, firmware data, and software loaded by the device. View CVE Details Affected Products CareCam CM2507 Vendor: CareCam Product Version: CareCam HMT.CM2507 Firmware: v251211.1507 Product Status: known_affected Remediations Mitigation CareCam has not responded to CISA's attempts to coordinate. Users are encouraged to reach out to CareCam for more information. Relevant CWE: CWE-306 Missing Authentication for Critical Function Metrics CVSS Version Base Score Base Severity Vector String 3.1 3.5 LOW CVSS:3.1/AV:P/AC:L/PR:N/UI:N/S:U/C:L/I:L/A:N 4.0 2.4 LOW CVSS:4.0/AV:P/AC:L/AT:N/PR:N/UI:N/VC:L/VI:L/VA:N/SC:N/SI:N/SA:N CVE-2026-85497 CareCam CM2507 IP cameras store the device's root-account password using a fixed legacy password hash that provides insufficient resistance to offline cracking. An attacker who obtains the firmware image or password database could recover the associated credential, which may also be reusable across other devices running the same firmware. View CVE Details Affected Products CareCam CM2507 Vendor: CareCam Product Version: CareCam HMT.CM2507 Firmware: v251211.1507 Product Status: known_affected Remediations Mitigation CareCam has not responded to CISA's attempts to coordinate. Users are encouraged to reach out to CareCam for more information. Relevant CWE: CWE-916 Use of Password Hash With Insufficient Computational Effort Metrics CVSS Version Base Score Base Severity Vector String 3.1 7.5 HIGH CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:H 4.0 9.3 CRITICAL CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N CVE-2026-81321 CM2507 IP cameras store configured wireless network credentials in cleartext within the device filesystem. An attacker who obtains filesystem access through physical access, a debugging interface, or another vulnerability could recover the configured network identifier and pre-shared key. View CVE Details Affected Products CareCam CM2507 Vendor: CareCam Product Version: CareCam HMT.CM2507 Firmware: v251211.1507 Product Status: known_affected Remediations Mitigation CareCam has not responded to CISA's attempts to coordinate. Users are encouraged to reach out to CareCam for more information. Relevant CWE: CWE-312 Cleartext Storage of Sensitive Information Metrics CVSS Version Base Score Base Severity Vector String 3.1 7.5 HIGH CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:H 4.0 9.3 CRITICAL CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N Acknowledgments Ben Law reported these vulnerabilities to CISA. Legal Notice and Terms of Use This product is provided subject to this Notification ( https://www.cisa.gov/notification ) and this Privacy & Use policy ( https://www.cisa.gov/privacy-policy ). Recommended Practices CISA recommends users take defensive measures to minimize the risk of exploitation of these vulnerabilities. Minimize network exposure for all control system devices and/or systems, ensuring they are not accessible from the internet. Locate control system networks and remote devices behind firewalls and isolating them from business networks. When remote access is required, use more secure methods, such as Virtual Private Networks (VPNs), recognizing VPNs may have vulnerabilities and should be updated to the most current version available. Also recognize VPN is only as secure as the connected devices. CISA reminds organizations to perform proper impact analysis and risk assessment prior to deploying defensive measures. CISA also provides a section for control systems security recommended practices on the ICS webpage on cisa.gov/ics. Several CISA products detailing cyber defense best practices are available for reading and download, including Improving Industrial Control Systems Cybersecurity with Defense-in-Depth Strategies. CISA encourages organizations to implement recommended cybersecurity strategies for proactive defense of ICS assets. Additional mitigation guidance and recommended practices are publicly available on the ICS webpage at cisa.gov/ics in the technical information paper, ICS-TIP-12-146-01B--Targeted Cyber Intrusion Detection and Mitigation Strategies. Organizations observing suspected malicious activity should follow established internal procedures and report findings to CISA for tracking and correlation against other incidents. CISA also recommends users take the following measures to protect themselves from social engineering attacks: Do not click web links or open attachments in unsolicited email messages. Refer to Recognizing and Avoiding Email Scams for more information on avoiding email scams. Refer to Avoiding Social Engineering and Phishing Attacks for more information on social engineering attacks. No known public exploitation specifically targeting these vulnerabilities has been reported to CISA at this time. Revision History Initial Release Date: 2026-09-15 Date Revision Summary 2026-09-15 1 Initial Publication Legal Notice and Terms of Use

Fix: Review CISA guidance and apply vendor security updates immediately.
Protecting Tokens and Assertions from Forgery, Theft, and Misuse: Implementation Recommendations for Agencies and Cloud Service Providers Important CISA Advisory
2026-09-15 CISA Advisory

Protecting Tokens and Assertions from Forgery, Theft, and Misuse: Implementation Recommendations for Agencies and Cloud Service Providers

Developed by the National Institute of Standards and Technology (NIST) and CISA, this interagency report provides federal agencies and cloud service providers with guidelines to protect the identity assertions, access tokens, and cryptographic mechanisms that support modern authentication and authorization. As agencies adopt hybrid and multi-cloud environments, single sign-on, federation, and application programming interface (API)-based access increasingly depend on signed tokens and assertions that adversaries may target for forgery, theft, and misuse to move laterally across enterprise networks and access sensitive data. This final report updates the initial public draft and incorporates feedback on token validation, secrets management, and detection at scale, as well as input from government and industry experts that CISA gathered through its Joint Cyber Defense Collaborative. The report expands on NIST Special Publication Security and Privacy Controls for Information Systems and Organizations and supports Executive Order 14306 on secure software development practices. It provides architectural considerations and emphasizes the importance of Secure by Design principles for interoperable defense across cloud environments.

Fix: Review CISA guidance and apply vendor security updates immediately.
Siemens Mendix SAML Important CISA Advisory
2026-09-15 CISA Advisory

Siemens Mendix SAML

View CSAF Summary Mendix SAML module contains a vulnerability that could allow unauthenticated remote attackers to hijack an account in specific SSO configurations. Mendix has provided fix releases for the Mendix SAML module and recommends to update to the latest version. The following versions of Siemens Mendix SAML are affected: Mendix SAML (Mendix 10 compatible) vers:intdot/ Mendix SAML (Mendix 11 compatible) vers:intdot/ Mendix SAML (Mendix 9.24 compatible) vers:intdot/ CVSS Vendor Equipment Vulnerabilities v3 8.7 Siemens Siemens Mendix SAML Improper Verification of Cryptographic Signature Background Critical Infrastructure Sectors: Critical Manufacturing, Information Technology Countries/Areas Deployed: Worldwide Company Headquarters Location: Germany Vulnerabilities Expand All + CVE-2026-80465 Affected versions of the module do not properly validate the SAML response signature. This could allow unauthenticated remote attackers to hijack an account (session) in specific SSO configurations. View CVE Details Affected Products Siemens Mendix SAML Vendor: Siemens Product Version: Mendix SAML (Mendix 10 compatible) Product Status: known_affected Remediations Vendor fix Update to V3.6.27 or later version https://marketplace.mendix.com/link/component/1174 Vendor fix Update to V4.2.3 or later version https://marketplace.mendix.com/link/component/1174 Vendor fix Update to V4.2.3 or later version https://marketplace.mendix.com/link/component/1174 Relevant CWE: CWE-347 Improper Verification of Cryptographic Signature Metrics CVSS Version Base Score Base Severity Vector String 3.1 8.7 HIGH CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:C/C:H/I:H/A:N Acknowledgments Siemens ProductCERT reported this vulnerability to CISA. General Recommendations As a general security measure, Siemens strongly recommends protecting network access to devices with appropriate mechanisms. In order to operate the devices in a protected IT environment, Siemens recommends configuring the environment according to Siemens' operational guidelines for Industrial Security , and following the recommendations in the product manuals. Additional information on Industrial Security by Siemens can be found at: https://www.siemens.com/industrialsecurity Additional Resources For further inquiries on security vulnerabilities in Siemens products and solutions, please contact the Siemens ProductCERT: https://www.siemens.com/cert/advisories For more information see the associated Siemens security advisory SSA-887643 in HTML and CSAF . Terms of Use The use of Siemens Security Advisories is subject to the terms and conditions listed on: https://www.siemens.com/productcert/terms-of-use . Legal Notice and Terms of Use This product is provided subject to this Notification ( https://www.cisa.gov/notification ) and this Privacy & Use policy ( https://www.cisa.gov/privacy-policy ). Recommended Practices CISA recommends users take defensive measures to minimize the exploitation risk of these vulnerabilities. Minimize network exposure for all control system devices and/or systems, and ensure they are not accessible from the internet. Locate control system networks and remote devices behind firewalls and isolate them from business networks. When remote access is required, use more secure methods, such as Virtual Private Networks (VPNs), recognizing VPNs may have vulnerabilities and should be updated to the most recent version available. Also recognize VPN is only as secure as its connected devices. CISA reminds organizations to perform proper impact analysis and risk assessment prior to deploying defensive measures. CISA also provides a section for control systems security recommended practices on the ICS webpage on cisa.gov. Several CISA products detailing cyber defense best practices are available for reading and download, including Improving Industrial Control Systems Cybersecurity with Defense-in-Depth Strategies. CISA encourages organizations to implement recommended cybersecurity strategies for proactive defense of ICS assets. Additional mitigation guidance and recommended practices are publicly available on the ICS webpage at cisa.gov in the technical information paper, ICS-TIP-12-146-01B--Targeted Cyber Intrusion Detection and Mitigation Strategies. Organizations observing suspected malicious activity should follow established internal procedures and report findings to CISA for tracking and correlation against other incidents. Advisory Conversion Disclaimer This ICSA is a verbatim republication of Siemens ProductCERT SSA-887643 from a direct conversion of the vendor's Common Security Advisory Framework (CSAF) advisory. This is republished to CISA's website as a means of increasing visibility and is provided "as-is" for informational purposes only. CISA is not responsible for the editorial or technical accuracy of republished advisories and provides no warranties of any kind regarding any information contained within this advisory. Further, CISA does not endorse any commercial product or service. Please contact Siemens ProductCERT directly for any questions regarding this advisory. Revision History Initial Release Date: 2026-09-03 Date Revision Summary 2026-09-03 1 Publication Date 2026-09-15 2 Initial CISA Republication of Siemens ProductCERT SSA-887643 advisory Legal Notice and Terms of Use

Fix: Review CISA guidance and apply vendor security updates immediately.
mySCADA myPRO Manager Important CISA Advisory
2026-09-15 CISA Advisory

mySCADA myPRO Manager

View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to access privileged management functions or send arbitrary SMS messages through the connected GSM modem. The following versions of mySCADA myPRO Manager are affected: mySCADA myPRO Manager CVSS Vendor Equipment Vulnerabilities v3 9.8 mySCADA Technologies mySCADA myPRO Manager Missing Authorization, Missing Authentication for Critical Function Background Critical Infrastructure Sectors: Critical Manufacturing, Energy, Food and Agriculture, Transportation Systems, Water and Wastewater Countries/Areas Deployed: Worldwide Company Headquarters Location: Czechia Vulnerabilities Expand All + CVE-2026-73807 The mySCADA myPRO Manager command API does not properly enforce authentication for privileged functions. An unauthenticated attacker with network access to the affected API could exploit this vulnerability to access privileged management functions. View CVE Details Affected Products mySCADA myPRO Manager Vendor: mySCADA Technologies Product Version: mySCADA Technologies mySCADA myPRO Manager: Product Status: known_affected Remediations Mitigation mySCADA Technologies has addressed these issues in Version 2.2 and recommends that users update to the latest version. Users are notified in mySCADA Pro Manager about the availability of a new version if the device is connected to the internet. Otherwise, users can download the mySCADA Pro Manager from the webpage. https://www.myscada.org/downloads/mySCADAPROManager/ Relevant CWE: CWE-862 Missing Authorization Metrics CVSS Version Base Score Base Severity Vector String 3.1 9.8 CRITICAL CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H 4.0 9.3 CRITICAL CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N CVE-2026-82567 The myPRO Manager notification gateway exposes an unauthenticated HTTP endpoint used to send SMS messages through a connected GSM modem. The endpoint is accessible over the network and does not require authentication before accepting a phone number and message from a request and sending the specified SMS message. An unauthenticated attacker with network access to the notification gateway could exploit this vulnerability to send arbitrary SMS messages through the connected modem. View CVE Details Affected Products mySCADA myPRO Manager Vendor: mySCADA Technologies Product Version: mySCADA Technologies mySCADA myPRO Manager: Product Status: known_affected Remediations Mitigation mySCADA Technologies has addressed these issues in Version 2.2 and recommends that users update to the latest version. Users are notified in mySCADA Pro Manager about the availability of a new version if the device is connected to the internet. Otherwise, users can download the mySCADA Pro Manager from the webpage. https://www.myscada.org/downloads/mySCADAPROManager/ Relevant CWE: CWE-306 Missing Authentication for Critical Function Metrics CVSS Version Base Score Base Severity Vector String 3.1 6.3 MEDIUM CVSS:3.1/AV:A/AC:L/PR:N/UI:N/S:U/C:L/I:L/A:L 4.0 5.3 MEDIUM CVSS:4.0/AV:A/AC:L/AT:N/PR:N/UI:N/VC:L/VI:L/VA:L/SC:N/SI:N/SA:N Acknowledgments Shirshak Secnora OÜ reported these vulnerabilities to CISA. Legal Notice and Terms of Use This product is provided subject to this Notification ( https://www.cisa.gov/notification ) and this Privacy & Use policy ( https://www.cisa.gov/privacy-policy ). Recommended Practices CISA recommends users take defensive measures to minimize the risk of exploitation of these vulnerabilities. Minimize network exposure for all control system devices and/or systems, ensuring they are not accessible from the internet. Locate control system networks and remote devices behind firewalls and isolating them from business networks. When remote access is required, use more secure methods, such as virtual private networks (VPNs), recognizing VPNs may have vulnerabilities and should be updated to the most current version available. Also recognize VPN is only as secure as the connected devices. CISA reminds organizations to perform proper impact analysis and risk assessment prior to deploying defensive measures. CISA also provides a section for control systems security recommended practices on the ICS webpage on cisa.gov/ics. Several CISA products detailing cyber defense best practices are available for reading and download, including Improving Industrial Control Systems Cybersecurity with Defense-in-Depth Strategies. CISA encourages organizations to implement recommended cybersecurity strategies for proactive defense of ICS assets. Additional mitigation guidance and recommended practices are publicly available on the ICS webpage at cisa.gov/ics in the technical information paper, ICS-TIP-12-146-01B--Targeted Cyber Intrusion Detection and Mitigation Strategies. Organizations observing suspected malicious activity should follow established internal procedures and report findings to CISA for tracking and correlation against other incidents. CISA also recommends users take the following measures to protect themselves from social engineering attacks: Do not click web links or open attachments in unsolicited email messages. Refer to Recognizing and Avoiding Email Scams for more information on avoiding email scams. Refer to Avoiding Social Engineering and Phishing Attacks for more information on social engineering attacks. No known public exploitation specifically targeting these vulnerabilities has been reported to CISA at this time. Revision History Initial Release Date: 2026-09-15 Date Revision Summary 2026-09-15 1 Initial Publication Legal Notice and Terms of Use

Fix: Review CISA guidance and apply vendor security updates immediately.

Wärtsilä FOS-Onboard Important CISA Advisory
2026-09-15 CISA Advisory

Wärtsilä FOS-Onboard

View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to deliver an unauthorized update, execute code, or extract credentials to allow the attacker to impersonate a privileged client. The following versions of Wärtsilä FOS-Onboard are affected: FOS-Onboard 5.07.0923.01 (CVE-2026-78225, CVE-2026-81855) CVSS Vendor Equipment Vulnerabilities v3 9.1 Wärtsilä Wärtsilä FOS-Onboard Use of Hard-coded Cryptographic Key Background Critical Infrastructure Sectors: Transportation Systems Countries/Areas Deployed: Worldwide Company Headquarters Location: Finland Vulnerabilities Expand All + CVE-2026-78225 A hardcoded cryptographic server key vulnerability exists in the deployer-ng Update Controller component of Wärtsilä FOS-Onboard. View CVE Details Affected Products Wärtsilä FOS-Onboard Vendor: Wärtsilä Product Version: Wärtsilä FOS-Onboard: 5.07.0923.01 Product Status: known_affected Remediations Mitigation Wärtsilä states that the vulnerabilities are not exploitable when the product is installed as recommended, and has developed a security patch. Users are also directed to contact Wärtsilä to obtain and install the patch. To obtain and install the latest patch, contact Wärtsilä: https://www.wartsila.com/services-catalogue/engine-services-4-stroke/wartsila-ics-patch-deployment#contact Relevant CWE: CWE-321 Use of Hard-coded Cryptographic Key Metrics CVSS Version Base Score Base Severity Vector String 3.1 9 CRITICAL CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:C/C:H/I:H/A:H 4.0 9.5 CRITICAL CVSS:4.0/AV:N/AC:H/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H/SC:H/SI:H/SA:H CVE-2026-81855 A hardcoded cryptographic client authentication key vulnerability exists in the robot testing framework component of Wärtsilä FOS-Onboard. View CVE Details Affected Products Wärtsilä FOS-Onboard Vendor: Wärtsilä Product Version: Wärtsilä FOS-Onboard: 5.07.0923.01 Product Status: known_affected Remediations Mitigation Wärtsilä states that the vulnerabilities are not exploitable when the product is installed as recommended, and has developed a security patch. Users are also directed to contact Wärtsilä to obtain and install the patch. To obtain and install the latest patch, contact Wärtsilä: https://www.wartsila.com/services-catalogue/engine-services-4-stroke/wartsila-ics-patch-deployment#contact Relevant CWE: CWE-321 Use of Hard-coded Cryptographic Key Metrics CVSS Version Base Score Base Severity Vector String 3.1 9.1 CRITICAL CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:N 4.0 9.3 CRITICAL CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:H/VI:H/VA:N/SC:N/SI:N/SA:N Acknowledgments Cydome Security Ltd reported these vulnerabilities to Wärtsilä and CISA Legal Notice and Terms of Use This product is provided subject to this Notification ( https://www.cisa.gov/notification ) and this Privacy & Use policy ( https://www.cisa.gov/privacy-policy ). Recommended Practices CISA recommends users take defensive measures to minimize the risk of exploitation of these vulnerabilities. Minimize network exposure for all control system devices and/or systems, ensuring they are not accessible from the internet. Locate control system networks and remote devices behind firewalls and isolating them from business networks. When remote access is required, use more secure methods, such as virtual private networks (VPNs), recognizing VPNs may have vulnerabilities and should be updated to the most current version available. Also recognize VPN is only as secure as the connected devices. CISA reminds organizations to perform proper impact analysis and risk assessment prior to deploying defensive measures. CISA also provides a section for control systems security recommended practices on the ICS webpage on cisa.gov/ics. Several CISA products detailing cyber defense best practices are available for reading and download, including Improving Industrial Control Systems Cybersecurity with Defense-in-Depth Strategies. CISA encourages organizations to implement recommended cybersecurity strategies for proactive defense of ICS assets. Additional mitigation guidance and recommended practices are publicly available on the ICS webpage at cisa.gov/ics in the technical information paper, ICS-TIP-12-146-01B--Targeted Cyber Intrusion Detection and Mitigation Strategies. Organizations observing suspected malicious activity should follow established internal procedures and report findings to CISA for tracking and correlation against other incidents. CISA also recommends users take the following measures to protect themselves from social engineering attacks: Do not click web links or open attachments in unsolicited email messages. Refer to Recognizing and Avoiding Email Scams for more information on avoiding email scams. Refer to Avoiding Social Engineering and Phishing Attacks for more information on social engineering attacks. No known public exploitation specifically targeting these vulnerabilities has been reported to CISA at this time. Revision History Initial Release Date: 2026-09-15 Date Revision Summary 2026-09-15 1 Initial Publication Legal Notice and Terms of Use

Fix: Review CISA guidance and apply vendor security updates immediately.

Human Attacker Exploits Marimo RCE, Reaches SSH Bastion in Eight Seconds Critical The Hacker News
2026-09-15 The Hacker News

Human Attacker Exploits Marimo RCE, Reaches SSH Bastion in Eight Seconds

With artificial intelligence (AI) shrinking the window between vulnerability discovery and exploitation and lowering the barrier to entry for bad actors, new findings from Sysdig show that skilled human operators can move just as swiftly after gaining initial access. In one instance highlighted by the cloud security company, the threat actor pivoted from a v…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
HBO Max’s verified Reddit account hijacked to spread malware Important Malwarebytes Labs
2026-09-15 Malwarebytes Labs

HBO Max’s verified Reddit account hijacked to spread malware

Researchers at Hudson Rock found that cybercriminals hijacked HBO Max’s verified Reddit account and used it to run 108 malicious ads over roughly 48 hours. The ads used HBO Max’s trusted corporate account to promote fake AI tools, developer software, and macOS utilities, lowering potential victims’ guards. Some ads directed users to convincing HBO lookalike …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Attack Chains, Not Just Attack Surfaces: Why Testing Individual Techniques Misses the Point Important The Hacker News
2026-09-15 The Hacker News

Attack Chains, Not Just Attack Surfaces: Why Testing Individual Techniques Misses the Point

Introduction Security teams have gotten pretty good at testing against what can hurt them. Can this EDR agent catch this payload? Will my organization fail the phishing simulation? Does this SIEM rule fire on this particular technique? And, in more mature organizations, this testing happens continuously rather than as a one-off exercise. But no matter how mu…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Mass-Scanning Campaign Exploits Vite Flaw to Extract Cloud Credentials From Exposed Dev Servers Important The Hacker News
2026-09-15 The Hacker News

Mass-Scanning Campaign Exploits Vite Flaw to Extract Cloud Credentials From Exposed Dev Servers

Cybersecurity researchers have disclosed details of a mass-scanning campaign that has targeted Vite deployments siphon sensitive data. The first is an automated effort aimed at internet-exposed Vite development servers that's designed to steal cloud credentials, configurations from Amazon Web Services (AWS) and Microsoft Azure instances, and infrastructure s…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Cisco patches actively exploited email gateway zero-day (CVE-2026-76461) Critical CVE-2026-76461 Help Net Security
2026-09-15 Help Net Security

Cisco patches actively exploited email gateway zero-day (CVE-2026-76461)

Attackers have leveraged a zero-day SQL injection vulnerability (CVE-2026-76461) to compromise Cisco Secure Email Gateway appliances, Cisco confirmed on Monday. The vendor’s Product Security Incident Response Team became aware of active exploitation of this vulnerability in September 2025, and has shared indicators of compromise that organizations can look f…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification