
Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 5,807 advisories
Page 159 of 242
Microsoft sets security and safety rules for its AI models Moderate Help Net Security
2026-09-15 Help Net Security

Microsoft sets security and safety rules for its AI models

Microsoft AI has published the first draft of its Humanist AI Code of Conduct, a training manual outlining how it develops AI models and intends them to behave during deployment. The draft is open for public consultation for six weeks. The company plans to review the feedback, revise the document, and publish an updated version later this year. That version …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
One Exploit Chain, Two Espionage Campaigns: Chrome and Windows Under Fire Critical CVE-2026-85046 SecurityAffairs
2026-09-15 SecurityAffairs

One Exploit Chain, Two Espionage Campaigns: Chrome and Windows Under Fire

Two China-linked groups ran identical Chrome/Windows zero-day exploits against NGOs, before Chrome’s patch shipped, deploying different backdoors each. Two China-linked threat actors used the same Chrome/Windows zero-day against NGOs starting September 1, 2026, Volexity’s new report lays out the whole chain in detail. On September 1, Volexity detected a spea…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Attackers hijack HBO Max’s Reddit account for 48-hour malvertising blitz Important Help Net Security
2026-09-15 Help Net Security

Attackers hijack HBO Max’s Reddit account for 48-hour malvertising blitz

Attackers compromised the verified official HBO Max Reddit account, u/hbomax, and used its trusted advertising status to launch a ClickFix campaign targeting macOS and Windows devices with information-stealing malware. Screenshot of the fraudulent ad (Source: Alex Cutts) ClickFix has been rising in popularity among cybercriminals. It’s a social engineering t…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Suspected Black Axe gang leaders face cybercrime charges in the US Moderate BleepingComputer
2026-09-15 BleepingComputer

Suspected Black Axe gang leaders face cybercrime charges in the US

Five alleged leaders of the Black Axe cybercrime syndicate, known for its involvement in global-scale cyber-enabled financial fraud, have been extradited to the United States to face wire fraud and money laundering charges. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Meta AI builds detailed profiles of children from years of family posts Moderate Malwarebytes Labs
2026-09-15 Malwarebytes Labs

Meta AI builds detailed profiles of children from years of family posts

If you’re still OK with posting pictures of your kids on social media, take a minute to hear from mother of two Kalie Robins. At the start of September, she did something that hundreds of thousands of parents do every day. She posted a video of her young daughter on Facebook. Under the video of Robins and her daughter singing in a car, Facebook’s Meta AI sys…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Former AT&T store worker jailed after moonlighting as a SIM-swap gang’s inside man Moderate Graham Cluley Security
2026-09-15 Graham Cluley Security

Former AT&T store worker jailed after moonlighting as a SIM-swap gang’s inside man

44-year-old Kenneth Carter from Portland, Oregon, used to work in an AT&T retail store. But now he has been sentenced to 16 months in a federal prison. That should be plenty of time for him to rue the day he agreed to increase his monthly income by helping a SIM swap gang in their attempt to steal over half a million dollars. Read more in my article on the H…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
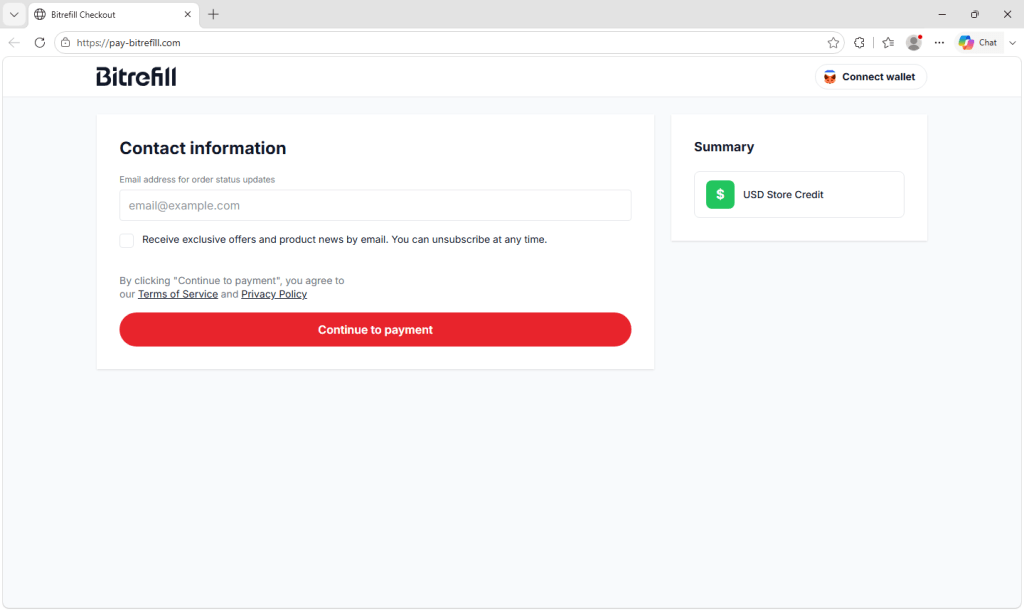
Search results are sending people to fake Bitrefill checkouts Moderate Malwarebytes Labs
2026-09-15 Malwarebytes Labs

Search results are sending people to fake Bitrefill checkouts

Bitrefill is a legitimate company that sells gift cards for popular stores like Amazon, Deliveroo, Apple, Nintendo, and thousands of others. They also sell eSIMs, and mobile top-ups. You can pay on their website for all of these with cryptocurrency. The scam is designed to catch people searching for Bitrefill or something it sells, like a gift card. Victims …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft confirms KB5002914 Excel update breaks copy and paste Moderate BleepingComputer
2026-09-15 BleepingComputer

Microsoft confirms KB5002914 Excel update breaks copy and paste

Microsoft has confirmed that copy and paste may silently fail for some Excel users after installing the September 2026 KB5002914 security update. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft Releases Emergency Patch to Fix RDS Vulnerability Important Infosecurity Magazine
2026-09-15 Infosecurity Magazine

Microsoft Releases Emergency Patch to Fix RDS Vulnerability

Microsoft has been forced to issue an out-of-band fix for several issues stemming from this month’s Patch Tuesday

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Akuity gives AI agents operational context to safely ship software Moderate Help Net Security
2026-09-15 Help Net Security

Akuity gives AI agents operational context to safely ship software

Akuity has introduced its Agentic Control Plane and MCP Server. Akuity’s Agentic Control Plane lets AI agents accelerate software delivery by giving them the operational context and permissions to act, all governed by the same controls Akuity already enforces across the pipeline. That governance is what gives engineering leadership the confidence to let agen…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Traefik Labs brings independent verification to AI agent governance Moderate Help Net Security
2026-09-15 Help Net Security

Traefik Labs brings independent verification to AI agent governance

Traefik Labs has introduced the Sovereign Trust Plane (STP), a set of capabilities in Traefik Hub that brings verifiable evidence to AI agent governance, with general availability planned by September 30, 2026. STP connects delegated access, policy enforcement and protected records of what the gateway allowed and refused across model, tool and API traffic. A…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Telegram Desktop Flaw Could Turn Old Chat Exports Into Data Theft Traps Important SecurityAffairs
2026-09-15 SecurityAffairs

Telegram Desktop Flaw Could Turn Old Chat Exports Into Data Theft Traps

A Telegram Desktop flaw let bots inject JavaScript into exported chats, enabling data theft and page manipulation. Old HTML exports remain unsafe. A vulnerability in Telegram Desktop could have turned an ordinary chat export into a serious data leak. Security researchers Denis and Aleksander Rostilov of ExPatch found a stored cross-site scripting flaw in the…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Cisco patches Secure Email Gateway zero-day exploited in attacks Critical BleepingComputer
2026-09-15 BleepingComputer

Cisco patches Secure Email Gateway zero-day exploited in attacks

Cisco warned customers to patch a critical Secure Email Gateway zero-day security flaw that threat actors have been exploiting in attacks. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Non-Zero-Day VPN Flaw Left Japan ‘s Government Shared Network Platform Exposed: 246,000 Records at Risk Critical SecurityAffairs
2026-09-15 SecurityAffairs

Non-Zero-Day VPN Flaw Left Japan ‘s Government Shared Network Platform Exposed: 246,000 Records at Risk

Japan ‘s Digital Agency disclosed a VPN breach exposing 246,000 government employee records across 23 ministries. Detected June 25, publicly disclosed September 11. Japan ‘s Digital Agency disclosed that attackers exploited a vulnerability in a VPN device to access its Government Solution Service (GSS), potentially leaking personal information belonging to a…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
LiteSpeed Enterprise Flaw Could Let One Hosting Account Gain Root Access on a Shared Server Important The Hacker News
2026-09-15 The Hacker News

LiteSpeed Enterprise Flaw Could Let One Hosting Account Gain Root Access on a Shared Server

A critical vulnerability in LiteSpeed Web Server Enterprise could let a low-privilege website user gain root access on a shared-hosting server, cPanel warned in an advisory published on September 14. On such servers, many customers' sites run on a single machine, and an attacker with one of those hosting accounts could exploit the flaw to access or alter oth…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Cisco Secure Email Gateway Flaw Exploited in the Wild, Enables Root Command Execution Critical CVE-2026-76461 The Hacker News
2026-09-15 The Hacker News

Cisco Secure Email Gateway Flaw Exploited in the Wild, Enables Root Command Execution

Cisco has warned that a new critical vulnerability impacting AsyncOS Software for Cisco Secure Email Gateway has come under active exploitation in the wild. The vulnerability, tracked as CVE-2026-76461, carries a CVSS score of 9.8 out of a maximum of 10.0. It has been described as a case of insufficient validation in the email parsing logic that could allow …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
China-Linked Hackers Exploit Chrome-Windows Zero-Day Chain to Deploy GRIMWEDGE Critical The Hacker News
2026-09-15 The Hacker News

China-Linked Hackers Exploit Chrome-Windows Zero-Day Chain to Deploy GRIMWEDGE

A Chinese threat actor has been attributed to a spear-phishing campaign that exploits recently patched security flaws in Google Chrome and Microsoft Windows to deliver a malicious JavaScript backdoor called GRIMWEDGE. Volexity, which is tracking the threat cluster under the moniker UTA0560, said the activity targeted multiple non-governmental organizations (…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Product showcase: mSecure makes one vault do more than remember passwords Moderate Help Net Security
2026-09-15 Help Net Security

Product showcase: mSecure makes one vault do more than remember passwords

mSecure is a password manager and data vault for storing credentials and other sensitive information. It is available for iOS, Android, macOS, and Windows, with data synchronization across supported devices. The app uses AES-256 encryption and a zero-knowledge architecture. The company does not store the account password or account key on its servers. Users …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Your employees are already using AI tools you never approved Moderate Help Net Security
2026-09-15 Help Net Security

Your employees are already using AI tools you never approved

Seventy-four percent of respondents report departmental or scaled AI adoption at their organizations, including within individual teams or departments, across business functions, and as part of processes and operations, according to the latest OneTrust 2026 AI-Ready Governance Report. The remaining respondents are planning, evaluating, or experimenting with …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Most chief audit executives can’t tell you what AI is worth yet Moderate Help Net Security
2026-09-15 Help Net Security

Most chief audit executives can’t tell you what AI is worth yet

Auditors are using AI in their daily work, and their departments have mostly left them to figure it out alone. 93% of audit leaders and auditors report some level of AI use, while 15% say their department has deployed formal use cases and runs them routinely in audits, according to Gartner. Chief audit executives (CAE) have to defend that arrangement to stak…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Chromium CVE-2026-87658: Information leak in Extensions Moderate CVE-2026-87658 Microsoft MSRC
2026-09-14 Microsoft MSRC

Chromium CVE-2026-87658: Information leak in Extensions

This CVE was assigned by Chrome. Microsoft Edge (Chromium-based) ingests Chromium, which addresses this vulnerability. Please see [Google Chrome Releases](https://chromereleases.googleblog.com/2026) for more information.

Fix: Deploy cumulative update via Windows Update or Microsoft Update Catalog.
Chromium CVE-2026-87657: Use after free in V8 Moderate CVE-2026-87657 Microsoft MSRC
2026-09-14 Microsoft MSRC

Chromium CVE-2026-87657: Use after free in V8

This CVE was assigned by Chrome. Microsoft Edge (Chromium-based) ingests Chromium, which addresses this vulnerability. Please see [Google Chrome Releases](https://chromereleases.googleblog.com/2026) for more information.

Fix: Deploy cumulative update via Windows Update or Microsoft Update Catalog.
Chromium CVE-2026-87656: Improper state validation in Safebrowsing Moderate CVE-2026-87656 Microsoft MSRC
2026-09-14 Microsoft MSRC

Chromium CVE-2026-87656: Improper state validation in Safebrowsing

This CVE was assigned by Chrome. Microsoft Edge (Chromium-based) ingests Chromium, which addresses this vulnerability. Please see [Google Chrome Releases](https://chromereleases.googleblog.com/2026) for more information.

Fix: Deploy cumulative update via Windows Update or Microsoft Update Catalog.
Notification