CRPx0 ransomware: what you need to know
CRPx0 is a cybercrime operation that started off operating a scam before pivoting into a fully-blown ransomware and cryptocurrency business. Read more in my article on the Fortra blog.
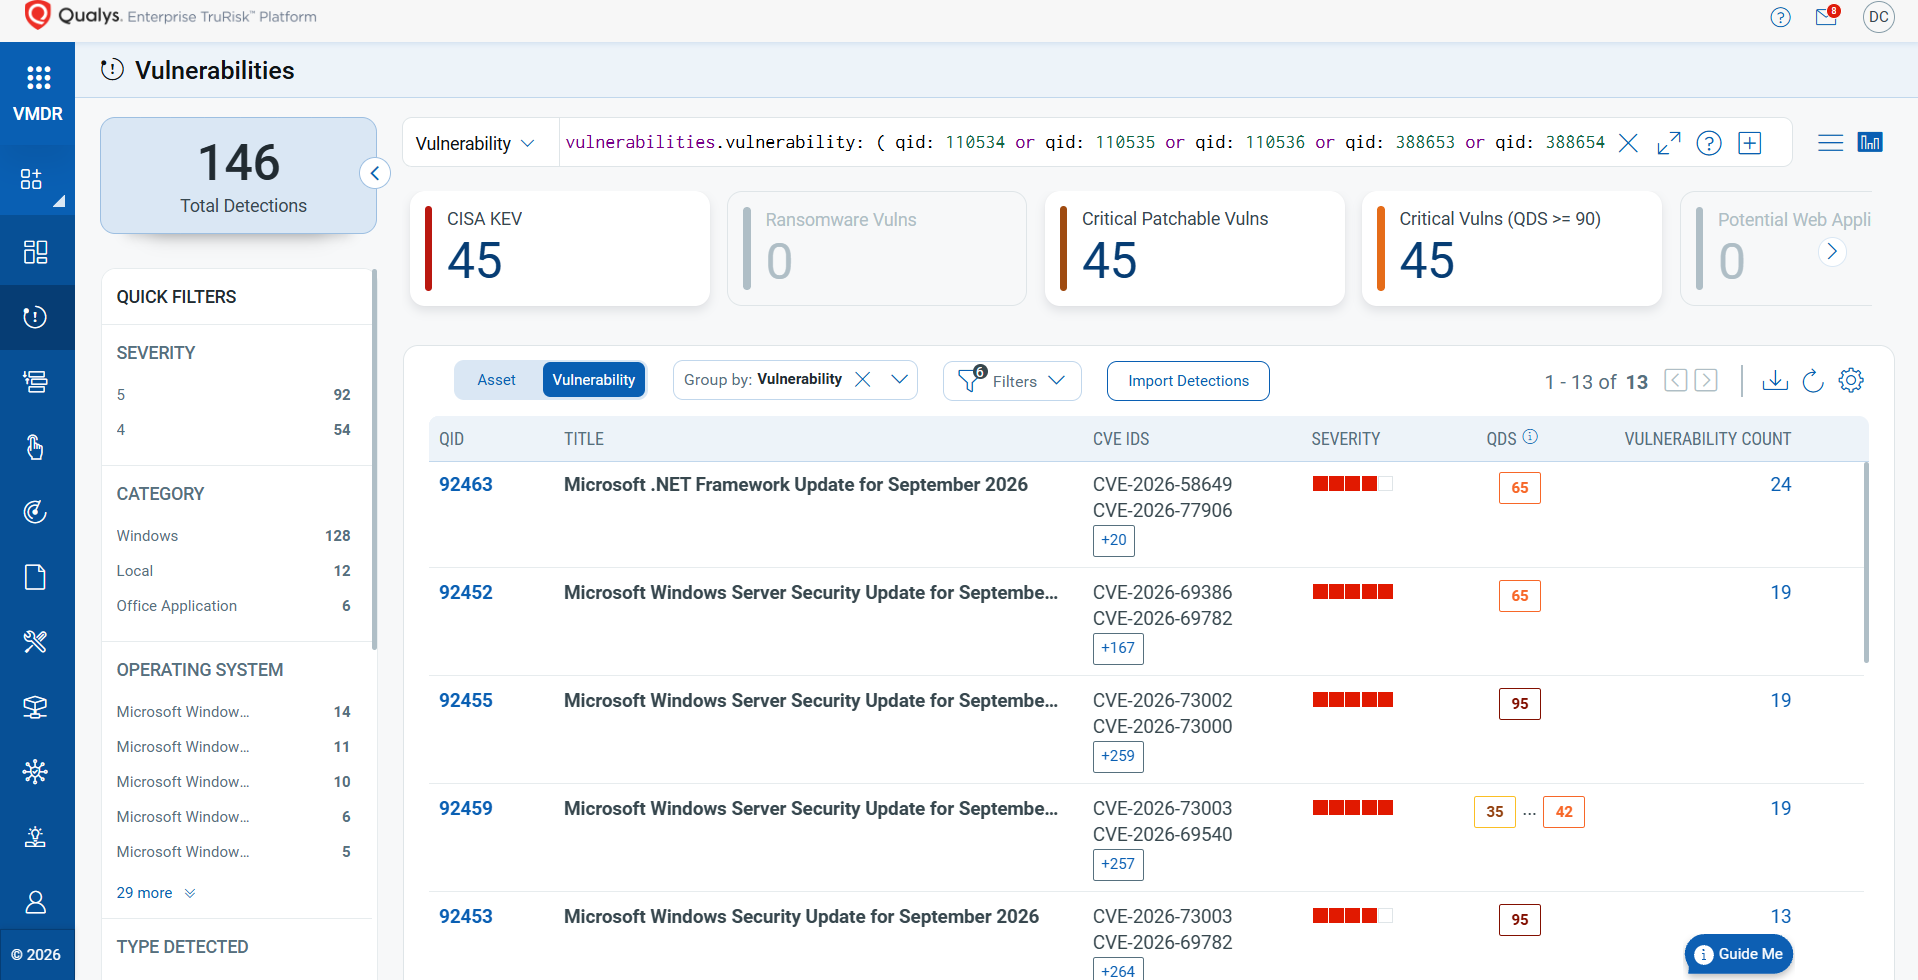
Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.
CRPx0 is a cybercrime operation that started off operating a scam before pivoting into a fully-blown ransomware and cryptocurrency business. Read more in my article on the Fortra blog.
Remember when social media was filled only with posts from your friends, rather than what an algorithm decided you wanted to see? So does the Australian government, and it wants that internet back. Yesterday, the government released draft legislation outlining a Digital Duty of Care. The proposal includes a measure that Prime Minister Anthony Albanese labele…
Onapsis urges SAP customers to patch “Overpass” vulnerability, which has a CVSS score of 10.0
Latest threat intelligence analysis from SANS Internet Storm Center: ISC Stormcast For Wednesday, September 9th, 2026 https://isc.sans.edu/podcastdetail/10086, (Wed, Sep 9th).
Microsoft has released its monthly security update for September 2026, which includes 973 vulnerabilities affecting a range of products, including 113 that Microsoft marked as "critical." Microsoft notes that 2 of the vulnerabilities disclosed this month have been exploited in the wild: CVE-2026-81963 affects Windows Update Stack. CVE-2026-81963 is a elevati…
Microsoft Corp. today issued updates to plug at least 974 security holes in its Windows operating systems and other software, by far its biggest single patch batch ever. Microsoft says artificial intelligence is helping to speed the discovery of vulnerabilities, but security experts warn that many organizations already are struggling to prioritize the more human-intensive endeavor of testing and d...
Microsoft is publishing 974 own-product vulnerabilities on September 2026 Patch Tuesday , including 723 vulnerabilities in Windows. Along with Microsoft fixes for 25 non-Microsoft CVEs, that brings the total number of vulnerabilities on the table today to 999. Whether this is the biggest Patch Tuesday ever depends on how we count, but this is by far the most…
Attackers are actively exploiting two of the vulnerabilities, and another 58 are more likely to be exploited, according to Microsoft.
Threat actors are abusing multiple Google services to evade detection, ultimately harvesting credentials or installing ScreenConnect remote access.
Researchers and OpenAI disagree on whether an earlier incident involving DseWiki, which the company did not disclose, was a “hack."
This month, Microsoft released patches for a record-breaking 973 vulnerabilities, including 113 rated critical. It is by far the largest Patch Tuesday to date, well ahead of the previous high of 664 set in July 2026. Two vulnerabilities are listed as exploited in the wild, while none were publicly disclosed before Patch Tuesday. Notable fixes include Windows…
Microsoft kicks off September with its monthly Patch Tuesday release, delivering fixes for security vulnerabilities affecting its products. The security updates are packed with security fixes, providing organizations with important updates to help protect their environments from emerging threats. This Patch Tuesday is Microsoft’s largest security update ever…
Whelp, here we are. Deep into the new normal. With nearly 1,000 CVEs coming out from Microsoft and a healthy release from Adobe as well, there’s a phrase from my military days that comes to mind: embrace the suck. Take an extended break from your regularly scheduled activities as we take a look at the latest security patches from Adobe and Microsoft. If you’…
Two separate attacks demonstrate how threat actors are finding new ways to compromise organizations by using the popular social engineering tactic.
Executive Summary Exposure management platforms are increasingly evaluated based on post-detection actions rather than detection itself. This piece sets out four questions to ask when evaluating one: whether it narrows vulnerabilities to the exploitable using environment context rather than severity scores; whether it validates exploitability continuously ra…
Location data sold by the ad industry has reportedly helped adversaries target US troops. The Pentagon has responded by switching off ad tracking on its devices - and you can do the same on yours. Read more in my article on the Hot for Security blog.
After a major cyber-attack targeted France's national tax authority, the Prime Minister called for the establishment of a new dedicated cyber incident response capability
Use after free in Windows Kernel allows an authorized attacker to elevate privileges locally.
Missing authorization in Entra ID allows an authorized attacker to elevate privileges over a network.
Heap-based buffer overflow in SQL Server allows an unauthorized attacker to execute code over a network.
Use after free in Windows Modern Execution Server allows an authorized attacker to elevate privileges locally.
Heap-based buffer overflow in Windows USB Video Driver allows an authorized attacker to elevate privileges locally.
Double free in Windows Credential Guard allows an authorized attacker to elevate privileges locally.
Relative path traversal in Windows DNS allows an authorized attacker to elevate privileges locally.