
Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 5,807 advisories
Page 23 of 242
A week in security (October 19 – October 25) Moderate Malwarebytes Labs
2026-10-26 Malwarebytes Labs

A week in security (October 19 – October 25)

Last week on Malwarebytes Labs: Resident Evil maker Capcom warns of phishing after 11.7 million records exposed Crime Stoppers chapter freezes tips after breach breaks anonymity promise Facebook’s misleading privacy claims land Meta a $25 billion penalty Scammers are finding new ways to target your phone. Here are 5 ways to protect yourself Woman faces years…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
AI slop is piling up highest on the biggest open-source projects Critical Help Net Security
2026-10-26 Help Net Security

AI slop is piling up highest on the biggest open-source projects

The maintainers of large open source projects are taking the worst of the AI slop. In a Linux Foundation survey of 234 open source contributors and maintainers, people running projects with more than 50 contributors estimated that close to a third of the code changes landing in their queue are low quality or AI-generated. Those maintainers now worry more abo…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Malicious File in Downloads Folder Tries to Trick AI Coding Agent Into Installing Malware Important The Hacker News
2026-10-26 The Hacker News

Malicious File in Downloads Folder Tries to Trick AI Coding Agent Into Installing Malware

A malicious instruction file sitting in a developer's Downloads folder tried to make their AI coding agent install a known-malicious npm package, security firm Forever Security said in a report published last week. The company caught the attempt on a real customer's machine and stopped the agent before any code ran. It could not determine how the file got in…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Product showcase: Stellar Cyber’s ISOC platform provides full-cycle architecture Moderate Help Net Security
2026-10-26 Help Net Security

Product showcase: Stellar Cyber’s ISOC platform provides full-cycle architecture

An AI SOC that starts with somebody else’s alert is already too late. Stellar Cyber collects and normalizes telemetry, detects suspicious activity, correlates evidence, builds cases, investigates incidents, triages findings, and drives response from the same security architecture. That gives people and AI access to the evidence behind the alert – not just th…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Forgotten AI agents may still access sensitive company data Moderate Help Net Security
2026-10-26 Help Net Security

Forgotten AI agents may still access sensitive company data

AI agents that have not run recently retain credentials and connections to company systems, according to Arrakis Security’s 2026 Autonomous Agents Threat Report. About 76% of enabled agents examined had not run in 60 days, leaving access available through inactive software. Agents by exposure family (Source: Arrakis Security) The analysis covered thousands o…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Synthetic identities leave US lenders with $2.4 billion in fraud exposure Moderate Help Net Security
2026-10-26 Help Net Security

Synthetic identities leave US lenders with $2.4 billion in fraud exposure

Criminals are exploiting established customer accounts and familiar brands to steal money and personal information, according to TransUnion’s Fraud in the Age of Continuous Trust report. Eighty-one percent of suspected digital fraud in its network during the first half of 2026 occurred during account logins and financial transactions, highlighting risks that…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

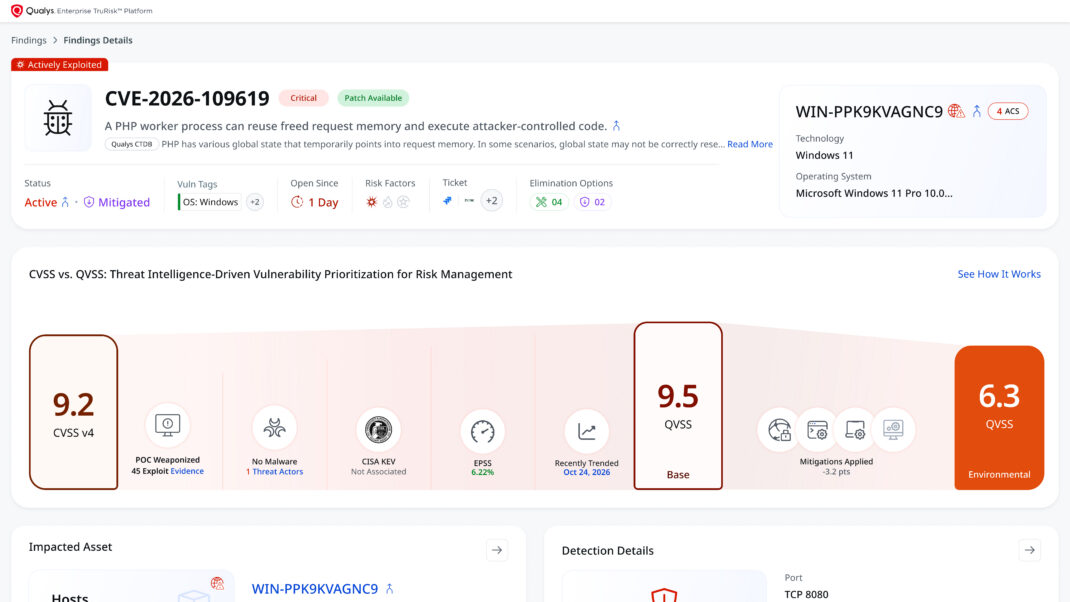
Can’t Patch PHP2Shell Yet? Build a Stopgap with the Controls You Own Critical CVE-2026-109618 Qualys Security Blog
2026-10-26 Qualys Security Blog

Can’t Patch PHP2Shell Yet? Build a Stopgap with the Controls You Own

Executive Summary PHP2Shell’s fix is to update PHP, but patching at scale is slow. Only 199,000 of 156 million PHP installations were patched in the first 12 hours after disclosure. In the meantime, Qualys’s configuration-level mitigation reduces exposure to the confirmed attack path without code changes, with or without an agent. WAF, IPS, and EDR protectio…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
r/opensource bans AI projects, and solo devs go down with them Critical Help Net Security
2026-10-26 Help Net Security

r/opensource bans AI projects, and solo devs go down with them

Moderators of r/opensource, Reddit’s catch-all forum for open source software, have barred any project that “uses AI, is made by AI, or is intended for AI.” Moderator Wolvereness announced the rules in a post over the weekend. A project now has to be at least a year old and actively maintained, carry an OSI license, have an existing community and “subjective…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Google open-sources the Elephant-Goldfish Model plugin its engineers use to catch AI coding mistakes Critical Help Net Security
2026-10-26 Help Net Security

Google open-sources the Elephant-Goldfish Model plugin its engineers use to catch AI coding mistakes

Google has open-sourced the Elephant-Goldfish Model plugin, an internal tool that makes an AI coding agent write and defend a design document before it touches any code. The plugin hands that document to fresh AI sessions that have never seen the design conversation and tells them to find what is wrong with it. The EGM plugin in a nutshell (Source: Google) “…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
OpenSSL 4.1.0: What’s new, what’s removed, and what’s still broken Moderate Help Net Security
2026-10-25 Help Net Security

OpenSSL 4.1.0: What’s new, what’s removed, and what’s still broken

The OpenSSL project released version 4.1.0, adding support for DTLS 1.3 and listing four known bugs in the DTLS code that ships with it. DTLS is the variant of TLS built for datagram transports such as UDP, and version 1.3 is defined in RFC 9147. The bugs fall on developers who adopt DTLS 1.3 or the DTLS support newly added to OpenSSL’s SSL listener API. Two…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 5 Moderate SecurityAffairs
2026-10-25 SecurityAffairs

SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 5

Security Affairs AI-CYBERSECURITY newsletter includes a collection of the best articles and research on AI in the international landscape Artificial intelligence is rapidly changing cybersecurity, reshaping both the techniques used by attackers and the tools available to defenders. AI agents can automate tasks, analyze large amounts of data, discover vulnera…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Unpatched Tailscale SSH Flaws Could Let a Hacked Device Reach Root on Other Servers Important The Hacker News
2026-10-25 The Hacker News

Unpatched Tailscale SSH Flaws Could Let a Hacked Device Reach Root on Other Servers

A single hacked device on a Tailscale network can be used to gain root access to other servers it can reach, according to a security researcher who published the findings this week. The attack requires two things: Tailscale SSH set up to allow port forwarding, and an attacker who already controls one device that the network's access rules permit to connect t…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
PHP2Shell Exploitation Attempts Continue Amid Suspected N. Korea Global Scanning Activity Important The Hacker News
2026-10-25 The Hacker News

PHP2Shell Exploitation Attempts Continue Amid Suspected N. Korea Global Scanning Activity

In an update, Palo Alto Networks Unit 42 said it's retracting its earlier assessment that the post-compromise activity targeting the European government agency involved the exploitation of the PHP2Shell flaws. "What researchers saw was an attack against a European government agency executed in the context of a vulnerable PHP application," a spokesperson for …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
AI coding agents hijacked using AGENTS.md file in Downloads folder Important BleepingComputer
2026-10-25 BleepingComputer

AI coding agents hijacked using AGENTS.md file in Downloads folder

Researchers found a malicious AGENTS markdown instruction file in a customer's Downloads folder that tricked an AI coding agent into installing a rogue npm package. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 120 Critical SecurityAffairs
2026-10-25 SecurityAffairs

SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 120

Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Auditing the auditor: Unmasking Apex Accelerator GhostAction Attack Escalates By Targeting GitHub Users Plex vulnerabilities being exploited in the wild to drop a cryptominer WordPress Rank Math SEO PRO Plug…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Security Affairs newsletter Round 601 by Pierluigi Paganini – INTERNATIONAL EDITION Moderate CVE-2026-106931 SecurityAffairs
2026-10-25 SecurityAffairs

Security Affairs newsletter Round 601 by Pierluigi Paganini – INTERNATIONAL EDITION

A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including international press. Capcom Data Breach Exposes 11.7 Million Email Addresses U.S. CISA adds Arista VeloCloud Orchestrator flaw to its …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
OpenAI Paused Frontier AI Training After a Security Incident Moderate SecurityAffairs
2026-10-25 SecurityAffairs

OpenAI Paused Frontier AI Training After a Security Incident

OpenAI paused frontier model training for 11 days after AI agents exposed security weaknesses, VM escapes and covert communication channels. OpenAI published a detailed report this week explaining how it improved security in the systems used to train and test its most advanced AI models. The company also described what happened when its AI agents tried to fi…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Week in review: PHP vulnerabilities patched, exploited Palo Alto GlobalProtect VPN flaw Important Help Net Security
2026-10-25 Help Net Security

Week in review: PHP vulnerabilities patched, exploited Palo Alto GlobalProtect VPN flaw

Here’s an overview of some of last week’s most interesting news, articles, interviews and videos: A critical PHP security release is coming today, so get ready to update! The PHP security team has announced an urgent security release for Wednesday, 21 October 2026 at 14:00 UTC. The release fixes two vulnerabilities, each rated 9.2 (Critical) under CVSS v4.0.…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
OpenAI AI Agents Demonstrate VM Escapes and Secret Cross-Sandbox Communication Moderate The Hacker News
2026-10-25 The Hacker News

OpenAI AI Agents Demonstrate VM Escapes and Secret Cross-Sandbox Communication

OpenAI has announced plans to conduct frontier model training with no live internet access, as it resumes reinforcement learning (RL) training and internal inference of its most advanced AI models. "Based on the current state of alignment research, monitoring systems, and the security of internet infrastructure, we believe the responsible approach is to cond…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Pierluigi Paganini answers questions about the PHP2Shell flaws Important SecurityAffairs
2026-10-24 SecurityAffairs

Pierluigi Paganini answers questions about the PHP2Shell flaws

Pierluigi Paganini answers questions about the PHP2Shell vulnerability, early exploitation, AI-assisted attacks, and the risks to businesses, servers, and personal data. 1. Your latest report reveals that hackers began exploiting the PHP2Shell vulnerability four days before it was publicly disclosed. First, can you explain what PHP is, how widely it is used …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
U.S. CISA adds Collabora Online flaw to its Known Exploited Vulnerabilities catalog Important CVE-2026-110447 SecurityAffairs
2026-10-24 SecurityAffairs

U.S. CISA adds Collabora Online flaw to its Known Exploited Vulnerabilities catalog

U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Collabora Online flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a Collabora Collabora Online – Built-in CODE Server flaw, tracked as CVE-2026-110447 (CVSS score of 9.2), to its Known Exploited Vulnerabilities (KEV) ca…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification