
Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 5,807 advisories
Page 25 of 242
You gave your AI agent access, but who is giving it orders? Moderate BleepingComputer
2026-10-23 BleepingComputer

You gave your AI agent access, but who is giving it orders?

AI agents can be manipulated through malicious emails, websites, and plugins into executing commands, stealing data, or deleting files using their legitimate permissions. Gen Digital explains how its Agent Trust Hub helps protect agents through skill verification, secure connectivity, and runtime controls that intercept dangerous act [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CVE-2026-83862 Windows Network Load Balancing Remote Code Execution Vulnerability Critical CVE-2026-83862 Microsoft MSRC
2026-10-23 Microsoft MSRC

CVE-2026-83862 Windows Network Load Balancing Remote Code Execution Vulnerability

Corrected the CVSS Attack Vector metric from Network (AV:N) to Adjacent (AV:A) to reflect the requirement for Layer 2 network adjacency. The CVSS base score has decreased from 9.8 to 8.8. This is an informational change only. Customers who have successfully installed the update do not need to take any further action.

Fix: Deploy cumulative update via Windows Update or Microsoft Update Catalog.
Hackers Breach Enterprise Firewalls and VPNs, Exposing Over 70,000 Credentials Critical The Hacker News
2026-10-23 The Hacker News

Hackers Breach Enterprise Firewalls and VPNs, Exposing Over 70,000 Credentials

Cybersecurity researchers have disclosed details of a large-scale campaign that has targeted exposed network edge devices such as Fortinet FortiGate and Palo Alto Networks GlobalProtect firewalls. "Artifacts from this investigation also indicate that operators in this campaign have obtained access to numerous organizations worldwide, and have attempted to fu…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

PHP Vulnerability Wrap-Up, (Fri, Oct 23rd) Important SANS Internet Storm Center
2026-10-23 SANS Internet Storm Center

PHP Vulnerability Wrap-Up, (Fri, Oct 23rd)

This morning, we returned to Infocon Green. As usual, we are raising the Infocon to alert you to emerging situations requiring immediate attention. PHP fit that description. By now, you either know about it, or you probably never will, so it is time to go back to "business as usual".

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Cyber Insurance's New Reality: Underwriting Isn't Enough Moderate Dark Reading
2026-10-23 Dark Reading

Cyber Insurance's New Reality: Underwriting Isn't Enough

Rising AI, social engineering, and cloud risks are pushing carriers beyond risk transfer and deeper into cybersecurity itself.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
UK proposes 14-year prison terms for undersea cable sabotage Moderate The Record by Recorded Future
2026-10-23 The Record by Recorded Future

UK proposes 14-year prison terms for undersea cable sabotage

In an era of hybrid threats, the British government wants to update the Submarine Telegraph Act 1885, which carries a maximum fine of £1,000 and five years’ imprisonment in cases of deliberate damage.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Resident Evil maker Capcom warns of phishing after 11.7 million records exposed Important Malwarebytes Labs
2026-10-23 Malwarebytes Labs

Resident Evil maker Capcom warns of phishing after 11.7 million records exposed

.kadence-column480618_38f885-ca > .kt-inside-inner-col{padding-top:20px;padding-right:20px;padding-bottom:10px;padding-left:20px;}.kadence-column480618_38f885-ca > .kt-inside-inner-col{column-gap:var(--global-kb-gap-sm, 1rem);}.kadence-column480618_38f885-ca > .kt-inside-inner-col{flex-direction:column;}.kadence-column480618_38f885-ca > .kt-inside-inner-col …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Infostealer riding the AI Train Critical Check Point Research
2026-10-23 Check Point Research

Infostealer riding the AI Train

Key Points Aokigahara , a newly observed infostealer, has been spotted in the wild. An earlier version may have been known as Kamidere or Stygian . The malware includes traditional data theft capabilities targeting browsers, VPN clients, cryptocurrency wallets, FTP/SFTP clients, password managers, and email applications, among other targets. AI applications …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Node.js Patches Brotli Remote Code Execution Flaw: Find Vulnerable Runtimes Before Attackers Do Critical CVE-2026-111497 Qualys Security Blog
2026-10-23 Qualys Security Blog

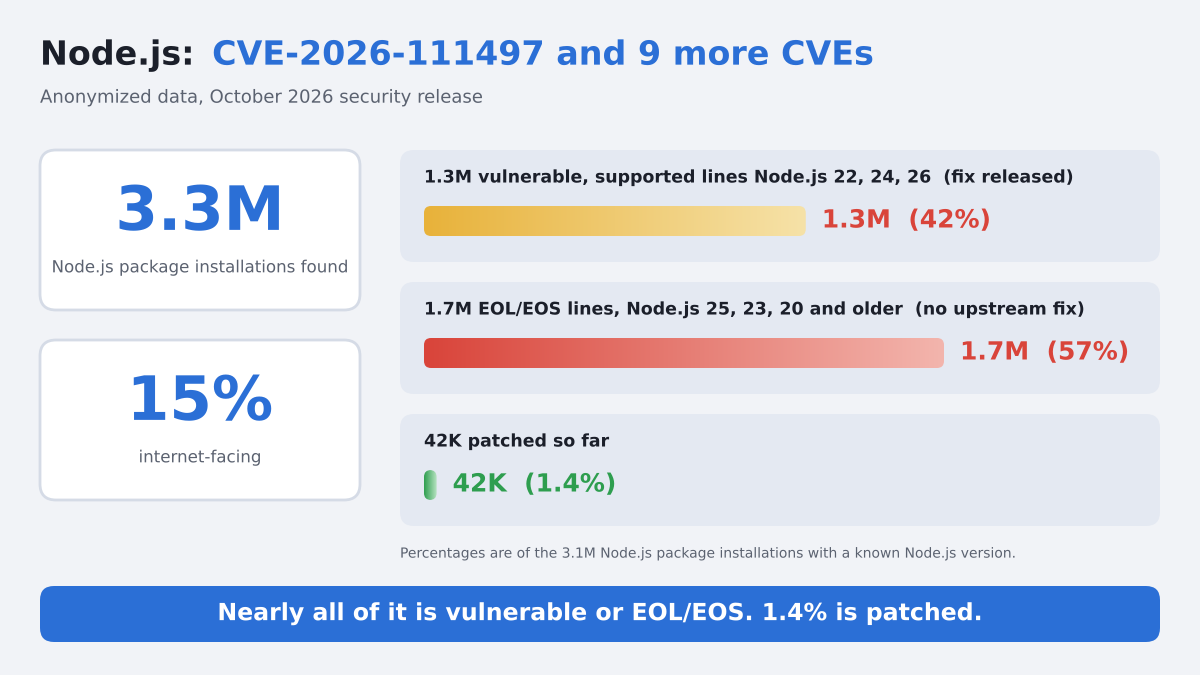
Node.js Patches Brotli Remote Code Execution Flaw: Find Vulnerable Runtimes Before Attackers Do

Executive Summary On October 21, 2026, Node.js released fixes for 10 vulnerabilities across its three supported release lines: 22.x, 24.x, and 26.x. Four are rated High. The most severe, CVE-2026-111497, is an out-of-bounds write in the bundled Brotli decoder that Node.js says permits remote code execution. These flaws live in the Node.js runtime itself, not…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
HPE patches eight max severity RCE and auth bypass AOS flaws Critical BleepingComputer
2026-10-23 BleepingComputer

HPE patches eight max severity RCE and auth bypass AOS flaws

Hewlett Packard Enterprise (HPE) released security updates to patch 72 vulnerabilities in the Aruba Operating System (ArubaOS), including eight maximum-severity authentication bypass and code execution issues. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

UK proposes 14-year jail terms for subsea cable saboteurs Moderate Help Net Security
2026-10-23 Help Net Security

UK proposes 14-year jail terms for subsea cable saboteurs

Damaging a cable on the seabed off the UK coast could soon cost someone 14 years of their life behind bars, under plans the British government published this week. The proposal comes from a White Paper by the Department for Digital, Culture, Media and Sport that would update laws protecting undersea cables and pipelines, some of which date back 140 years. Th…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Hacker leaks 281 GB of data from Germany’s far-right AfD party Moderate Graham Cluley Security
2026-10-23 Graham Cluley Security

Hacker leaks 281 GB of data from Germany’s far-right AfD party

The AfD has confirmed that hackers breached its hosting provider. A leak site now claims to offer 421,179 of the party’s internal emails, and shows AI-written summaries rather than the emails themselves. Read more in my article on the Hot for Security blog.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CISA Adds One Known Exploited Vulnerability to Catalog Critical CISA Advisory
2026-10-23 CISA Advisory

CISA Adds One Known Exploited Vulnerability to Catalog

CISA has added one new vulnerability to its Known Exploited Vulnerabilities (KEV) Catalog , based on evidence of active exploitation. CVE-2026-110447 Collabora Online – Built-in CODE Server OS Command Injection Vulnerability This type of vulnerability is a frequent attack vector for malicious cyber actors and poses significant risks to the federal enterprise. Binding Operational Directive (BOD) 26-04: Prioritizing Security Updates Based on Risk establishes vulnerability management requirements for Federal Civilian Executive Branch (FCEB) agencies. BOD 26-04 reinforces the importance of the KEV Catalog and requires federal agencies to prioritize rapid remediation of high-risk vulnerabilities, specifically those identified by Common Vulnerabilities and Exposures (CVEs) listed in CISA’s KEV Catalog on publicly exposed assets that grant total control of the asset post-exploitation, while deferring action for lower-risk vulnerabilities. BOD 26-04 further establishes basic expectations for when agencies must check whether threat actors compromised the system before the patch was applied. While BOD 26-04 applies only to FCEB agencies, CISA encourages all organizations to adopt risk-based vulnerability management and prioritize remediation of KEV Catalog vulnerabilities . CISA will continue to add vulnerabilities to the catalog that meet the specified criteria . Aware of an exploited vulnerability not currently listed in the KEV Catalog? Submit it for potential addition through CISA’s KEV Nomination Form . Potential KEV additions must have a CVE ID, evidence of exploitation, and clear mitigation guidance.

Fix: Review CISA guidance and apply vendor security updates immediately.
CISA Adds One Known Exploited Vulnerability to Catalog Critical CISA Advisory
2026-10-23 CISA Advisory

CISA Adds One Known Exploited Vulnerability to Catalog

CISA has added one new vulnerability to its Known Exploited Vulnerabilities (KEV) Catalog , based on evidence of active exploitation. CVE-2026-114625 Arista VeloCloud Orchestrator SQL Injection Vulnerability This type of vulnerability is a frequent attack vector for malicious cyber actors and poses significant risks to the federal enterprise. Binding Operational Directive (BOD) 26-04: Prioritizing Security Updates Based on Risk establishes vulnerability management requirements for Federal Civilian Executive Branch (FCEB) agencies. BOD 26-04 reinforces the importance of the KEV Catalog and requires federal agencies to prioritize rapid remediation of high-risk vulnerabilities, specifically those identified by Common Vulnerabilities and Exposures (CVEs) listed in CISA’s KEV Catalog on publicly exposed assets that grant total control of the asset post-exploitation, while deferring action for lower-risk vulnerabilities. BOD 26-04 further establishes basic expectations for when agencies must check whether threat actors compromised the system before the patch was applied. While BOD 26-04 applies only to FCEB agencies, CISA encourages all organizations to adopt risk-based vulnerability management and prioritize remediation of KEV Catalog vulnerabilities . CISA will continue to add vulnerabilities to the catalog that meet the specified criteria . Aware of an exploited vulnerability not currently listed in the KEV Catalog? Submit it for potential addition through CISA’s KEV Nomination Form . Potential KEV additions must have a CVE ID, evidence of exploitation, and clear mitigation guidance.

Fix: Review CISA guidance and apply vendor security updates immediately.
Microsoft 365 accounts compromised at 79 organizations, no passwords needed Moderate Help Net Security
2026-10-23 Help Net Security

Microsoft 365 accounts compromised at 79 organizations, no passwords needed

An attacker who spent ten weeks replaying stolen Microsoft 365 sign-in sessions broke into email accounts at 79 organizations and used hidden inbox rules to keep victims from seeing parts of their own mail, according to Huntress. The researchers tracked the campaign between July 14 and September 22, 2026, counting 497 successful sign-ins and more than 200,00…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Meta Faces $25 Billion Penalty Linked to Cambridge Analytica Scandal Moderate SecurityAffairs
2026-10-23 SecurityAffairs

Meta Faces $25 Billion Penalty Linked to Cambridge Analytica Scandal

A New Mexico judge ordered Meta to pay $25 billion for misleading users about privacy, setting a record penalty. Meta plans to appeal. This week a New Mexico judge ordered Meta to pay the state $25 billion. The order follows a jury finding that the company deceived Facebook users about their privacy, and it’s the biggest fine ever imposed on Meta. State Dist…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
PHP Warns of Another Unpatched RCE Risk Two Days After Emergency PHP2Shell Patches Critical CVE-2026-115560 The Hacker News
2026-10-23 The Hacker News

PHP Warns of Another Unpatched RCE Risk Two Days After Emergency PHP2Shell Patches

PHP has warned of another way an attacker could run code on a web server, two days after it shipped emergency fixes for the critical PHP2Shell flaws. The new issue, assigned CVE-2026-115560, affects only web applications configured in an unusual way, and PHP considers it an unlikely risk.The project is not issuing an emergency fix for it. Instead, it recomme…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Russia-Linked Hackers Used New Mesh Network Backdoor in Destructive Ukraine Attack Important The Hacker News
2026-10-23 The Hacker News

Russia-Linked Hackers Used New Mesh Network Backdoor in Destructive Ukraine Attack

The Russian state-sponsored hacking group Sandworm teamed up with another threat actor to carry out a destructive wiping attack targeting a Ukrainian logistics company last year. According to ESET, the attack involved UAC-0099 (aka Earth Sirrush) obtaining initial access to the target on July 16, 2025, via a spear-phishing email bearing a malware-laced attac…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
PHP2Shell: Millions of Attacks, No Confirmed Successful Exploits Yet Important CVE-2026-109618 SecurityAffairs
2026-10-23 SecurityAffairs

PHP2Shell: Millions of Attacks, No Confirmed Successful Exploits Yet

PHP2Shell attacks have surged into the millions, but no successful exploitation is confirmed. Patch it immediately. On October 21, PHP released emergency patches for two critical vulnerabilities tracked as CVE-2026-109618 and CVE-2026-109619 (CVSS score of 9.2), affecting every PHP version that handles web requests. The bug code dates back to PHP 5.4 from 20…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification