Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 2,629 advisories
Page 31 of 110
Cisco Warns of Active Attacks Exploiting New Critical Secure Email Gateway Vulnerability Critical The Hacker News
2026-10-15 The Hacker News

Cisco Warns of Active Attacks Exploiting New Critical Secure Email Gateway Vulnerability

Attackers are exploiting a critical flaw in Cisco Secure Email Gateway that lets a sender with no login write files to the appliance's operating system, Cisco said in an advisory on Wednesday. The attacker sends an email with a crafted attachment through the gateway and, if it succeeds, could then run commands as root. The appliance filters an organization's…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Ledger asks sellers across Asia to halt sales after supply-chain attack Important BleepingComputer
2026-10-14 BleepingComputer

Ledger asks sellers across Asia to halt sales after supply-chain attack

Ledger has asked resellers and distributors of its wallets in Indonesia, Singapore, Thailand, the Philippines, Vietnam, Malaysia, and Hong Kong to suspend device sales and remove products from shelves while it investigates device tampering. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Hackers Backdoor Nextcloud Servers Through Critical Flaw in Collabora’s Built-in CODE App Critical The Hacker News
2026-10-14 The Hacker News

Hackers Backdoor Nextcloud Servers Through Critical Flaw in Collabora’s Built-in CODE App

Attackers exploited a flaw in an optional Nextcloud app, Collabora Online - Built-in CODE Server, to plant web shells on Nextcloud servers. Three administrators reported the issue on GitHub, with the first logged attack on September 10. A web shell is a small file that executes any command an attacker sends via a web request, with the rights of the web serve…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Cisco patches new Secure Email Gateway zero-day exploited in attacks Critical BleepingComputer
2026-10-14 BleepingComputer

Cisco patches new Secure Email Gateway zero-day exploited in attacks

Cisco has patched another actively exploited zero-day flaw in its Secure Email Gateway (SEG) that lets remote unauthenticated attackers execute commands with root privileges. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft Disrupts 3 Phishing Kits Linked to Over 1 Billion Scam Messages Important The Hacker News
2026-10-14 The Hacker News

Microsoft Disrupts 3 Phishing Kits Linked to Over 1 Billion Scam Messages

Microsoft and Health-ISAC, along with the Japan Cybercrime Control Center (JC3) and a coalition of private sector companies, such as Resecurity, Cloudflare, Oracle, Proofpoint, and TRM Labs, announced the disruption of three phishing kits, CoGUI (aka NX or FA), Haozi (aka Phoenix), and Iron Man System. "Since January 2026, the threat actors behind these kits…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Spyware manufacturer had access to data harvested by former Polish government, current PM says Important The Record by Recorded Future
2026-10-14 The Record by Recorded Future

Spyware manufacturer had access to data harvested by former Polish government, current PM says

Prime Minister Donald Tusk, who ordered the investigation, on Monday called the sprawling spyware operation spearheaded by the country’s previous ruling party “one of the biggest scandals in Polish history since the fall of communism.”

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
AI worms could spread across your smart devices, Anthropic warns Moderate Malwarebytes Labs
2026-10-14 Malwarebytes Labs

AI worms could spread across your smart devices, Anthropic warns

Your streaming box might not look like much of a computer. But connect enough inexpensive devices together, and they can run an AI model. Researchers at Anthropic demonstrated this by running a Google Gemma model across 15 off-brand Android TV boxes. They warn that small models could soon spread across vulnerable internet-of-things (IoT) devices, including s…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

U.S. Shuts Down Over 40 Laptop Farms, Charges 14 in North Korean IT Worker Fraud Moderate The Hacker News
2026-10-14 The Hacker News

U.S. Shuts Down Over 40 Laptop Farms, Charges 14 in North Korean IT Worker Fraud

The U.S. Department of Justice (DoJ) on Tuesday charged 14 people and seized about 187 computers and KVM devices as part of its ongoing efforts to disrupt North Korea's fraudulent remote IT worker (ITW) scheme. The indictment charges a mix of U.S. citizens and Chinese nationals for their roles in an IT worker conspiracy affecting more than 70 U.S. companies,…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft fixes VPN issues caused by September Windows updates Moderate BleepingComputer
2026-10-14 BleepingComputer

Microsoft fixes VPN issues caused by September Windows updates

Microsoft has resolved a known issue that caused Always On VPN connection issues after installing the September 2026 Windows 11 security updates. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft Patch Tuesday Sets New Record with 1,415 CVEs in October 2026 Updates Critical CVE-2026-96951 SecurityAffairs
2026-10-14 SecurityAffairs

Microsoft Patch Tuesday Sets New Record with 1,415 CVEs in October 2026 Updates

Microsoft Patch Tuesday security updates for October 2026 address a record 1,415 vulnerabilities. Prioritize the exploited zero-day, critical bugs and potentially wormable vulnerabilities. Microsoft just shattered every patch record in the book. October 2026 brought us a staggering 1,415 new CVEs from Microsoft alone. “Well, it’s a new record release from Mi…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The Blind Spots of Agentic Pentesting and How to Close Them Moderate BleepingComputer
2026-10-14 BleepingComputer

The Blind Spots of Agentic Pentesting and How to Close Them

AI-powered penetration testing can uncover complex attack paths, but safety restrictions and network limitations leave many assets and vulnerabilities untested. Picus Security explains how combining agentic pentesting with exposure validation and breach simulation can help close these gaps. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Break the silence: Kazakhstan-nexus UAT-6275 targets CIS government organizations Moderate CVE-2025-8088 Cisco Talos Intelligence
2026-10-14 Cisco Talos Intelligence

Break the silence: Kazakhstan-nexus UAT-6275 targets CIS government organizations

This research was conducted jointly with Julian-Ferdinand Vögele of Recorded Future’s Insikt Group. Details of the joint research and presentation are available here . Cisco Talos identified UAT-6275 ( TAG-193 by Recorded Future) activity targeting government organizations across the Commonwealth of Independent States (CIS). Recovered artifacts show addition…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft takes down 3 major phishing platforms used by Chinese cybercriminals Important The Record by Recorded Future
2026-10-14 The Record by Recorded Future

Microsoft takes down 3 major phishing platforms used by Chinese cybercriminals

The tech giant worked with Japan’s National Police Agency and healthcare cybersecurity organization Health-ISAC to obtain a U.S. court order seizing and redirecting domains that were part of the infrastructure underlying YAM Store, CoGUI and Iron Man.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Global takedown hits network behind 1 billion phishing messages Important BleepingComputer
2026-10-14 BleepingComputer

Global takedown hits network behind 1 billion phishing messages

A massive cybercriminal ecosystem facilitating more than a billion malicious messages targeting over 75,000 organizations across 150 countries has been disrupted by law enforcement agencies and partners worldwide. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Russian travel booking platform suspends reservations after cyberattack Important The Record by Recorded Future
2026-10-14 The Record by Recorded Future

Russian travel booking platform suspends reservations after cyberattack

Customers of Russian travel website Anywayanyday were unable to book tickets or hotel rooms as the company responded to a cyberattack.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
FBI raids 40+ laptop farms helping North Korea pocket US tech salaries Moderate Help Net Security
2026-10-14 Help Net Security

FBI raids 40+ laptop farms helping North Korea pocket US tech salaries

North Korean IT workers used stolen and fabricated identities to land remote jobs at more than 70 US companies, with help from Americans who allegedly kept company-issued laptops running from their homes, according to the US Department of Justice. Arrests in Ohio, raids in Texas Michael James Bostelle of Pennsylvania and Juan Cecilio Pena Carrillo of Texas w…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Download: The IT and security field guide to AI adoption Moderate Help Net Security
2026-10-14 Help Net Security

Download: The IT and security field guide to AI adoption

Security and IT teams are under pressure to adopt AI, but many are seeing the opposite of what was promised. Tools that demo well don’t hold up in real workflows. Complexity increases. Trust breaks down. And instead of reducing workload, AI can introduce new risks and oversight burdens. This guide breaks down why AI adoption fails in practice and gives teams…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Russian Influence Operation Widely Targets Latin America Moderate Dark Reading
2026-10-14 Dark Reading

Russian Influence Operation Widely Targets Latin America

The AI-enabled operation used spoofed emails, fake government documents, and the creation of a local organization to target schools in Peru and Ecuador, among other efforts.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CISA warns admins to immediately fix Ivanti flaw exploited as zero-day Critical BleepingComputer
2026-10-14 BleepingComputer

CISA warns admins to immediately fix Ivanti flaw exploited as zero-day

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) urged security teams to immediately patch an Ivanti Connect Secure (ICS) flaw exploited in zero-day attacks since at least October 1st. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
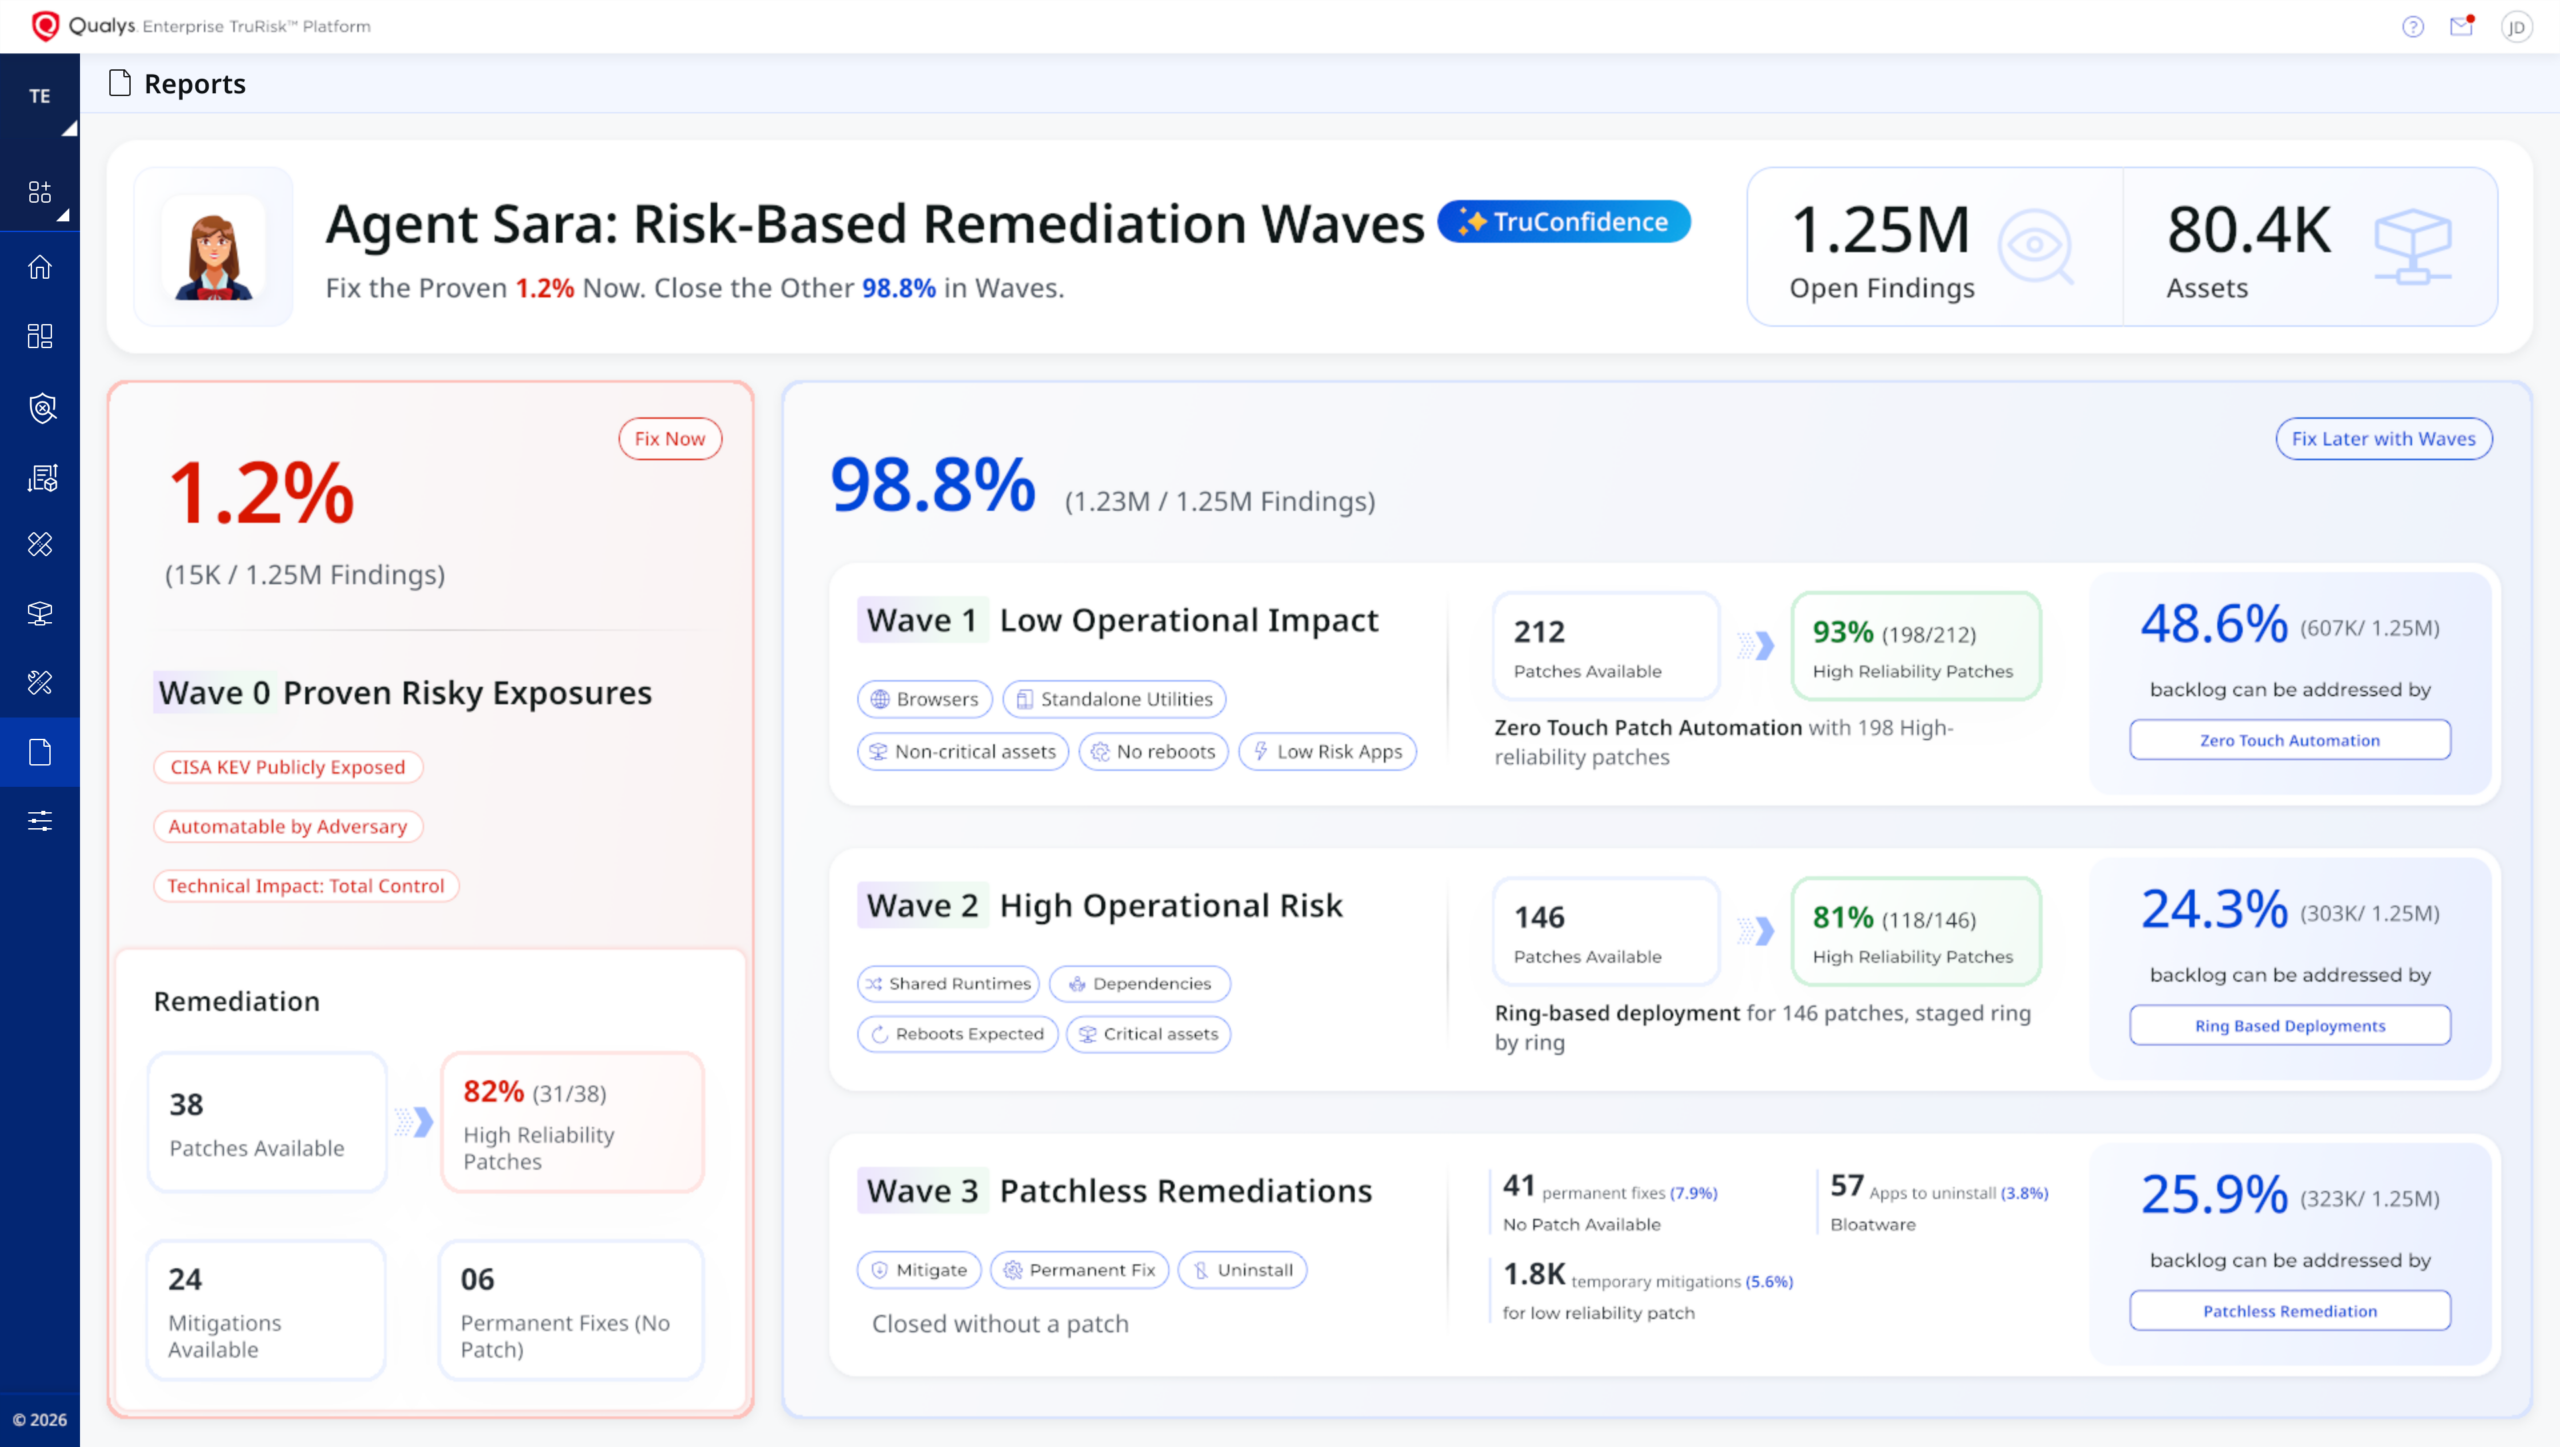
TruConfidence: Why Your Patch Automation Can Finally Be Autonomous Critical Qualys Security Blog
2026-10-14 Qualys Security Blog

TruConfidence: Why Your Patch Automation Can Finally Be Autonomous

TruConfidence: The AI-Powered Remediation Intelligence & Orchestration engine powering TruRisk Eliminate 2.0 delivers autonomous remediation at scale with proof at every step. Executive Summary Vulnerabilities are now discovered faster than enterprises can remediate them. Patch automation has been around for years, but vulnerability backlogs are still growin…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Congressional probe faults Match Group for failing to rein in dating app scams Moderate The Record by Recorded Future
2026-10-14 The Record by Recorded Future

Congressional probe faults Match Group for failing to rein in dating app scams

The Joint Economic Committee on Tuesday released the results of a year-long investigation into Tinder, Hinge, Match, Plenty of Fish and several other dating sites owned by Match Group.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CISA Urges Immediate Ivanti Connect Secure Updates as Honeypots Log 105 Exploit Attempts Critical CVE-2026-104935 The Hacker News
2026-10-14 The Hacker News

CISA Urges Immediate Ivanti Connect Secure Updates as Honeypots Log 105 Exploit Attempts

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday urged organizations to take steps to immediately update their Ivanti Connect Secure (ICS) appliances and deployments to the latest version following the disclosure of an actively exploited vulnerability. The security flaw, tracked as CVE-2026-104935 (CVSS score: 8.6), is a case of au…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification